
- blog
- 5+ Note
- Focus
- OSCP · Red Team
- Structure
- Recon → Exploit
Subdomain Enumeration blog
Filters
 guides-resources
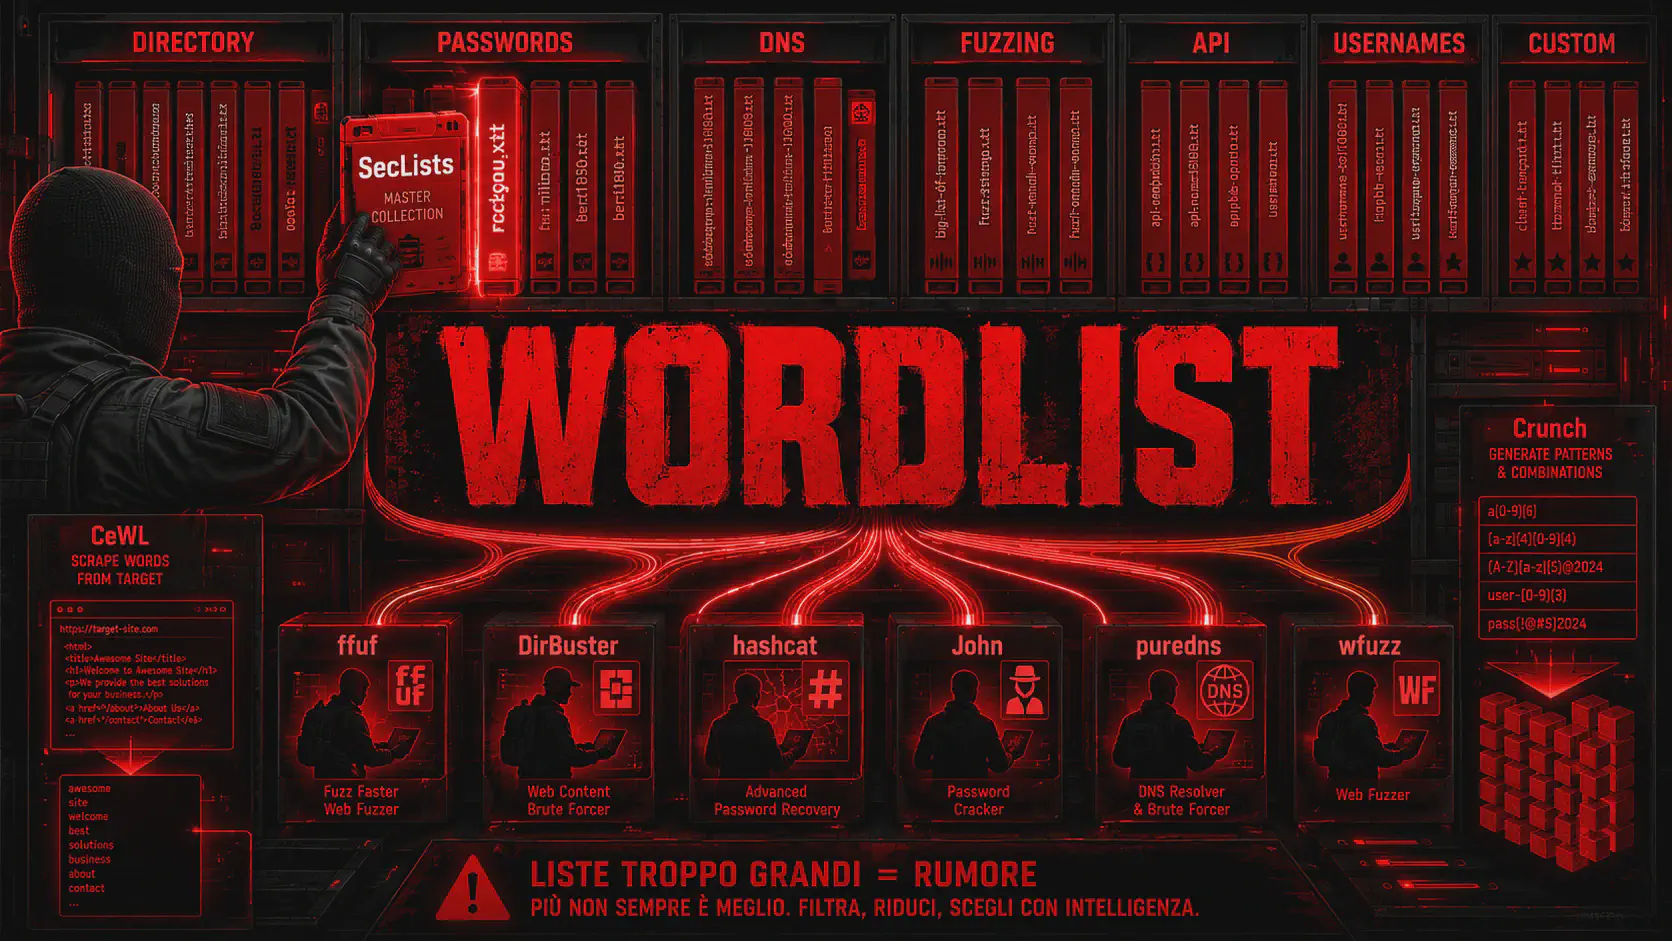
Wordlists for Pentesting: SecLists, RockYou, CeWL and Crunch
Learn which SecLists wordlists to use for directory fuzzing, password cracking, DNS and API, with paths on Kali Linux and custom lists created with CeWL and Crunch.
Discover more Discover more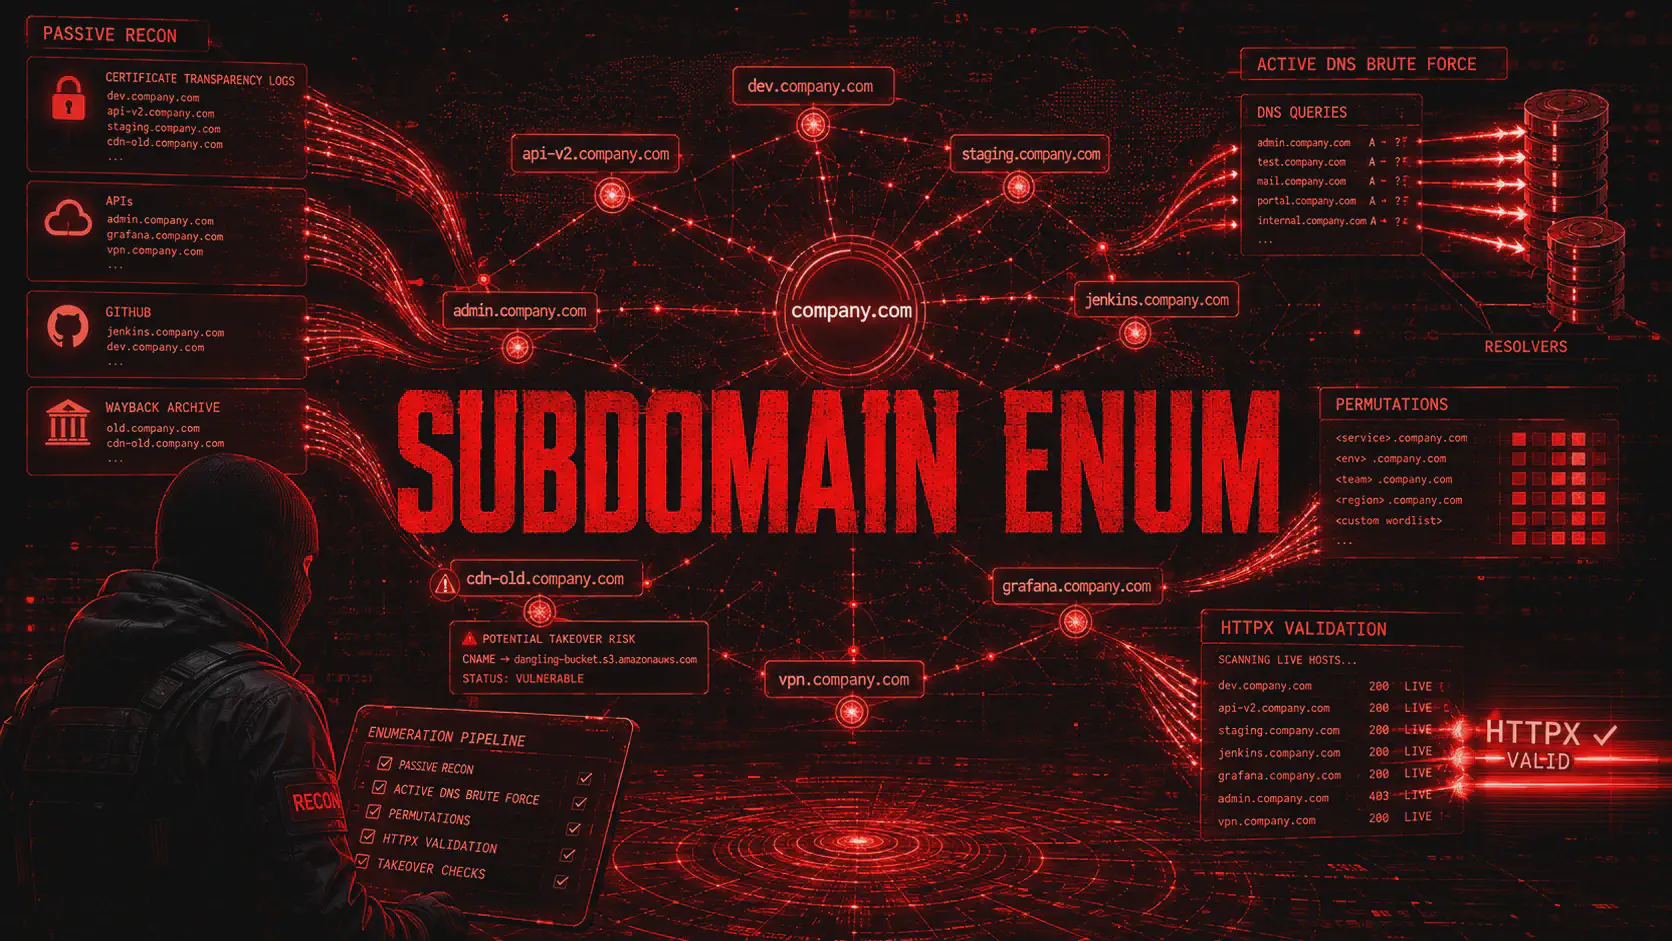 web hacking
Subdomain Enumeration with subfinder, puredns and httpx
Subdomain enumeration pipeline: passive recon with subfinder, brute force with puredns, Alterx permutations, httpx validation and subdomain takeover check.
Discover more Discover more tools
Subfinder: Complete guide to passive subdomain enumeration with ProjectDiscovery
Learn how to use Subfinder to find valid subdomains from passive sources, speed up web reconnaissance, and build a more effective recon pipeline with the ProjectDiscovery tool optimized for speed and stealth.
Discover more Discover more web hacking
Aquatone: Visual Recon and Automatic Screenshots for Subdomain Enumeration
Aquatone is a visual reconnaissance tool that automatically captures screenshots of hosts and subdomains discovered during the recon phase. It's ideal for quickly mapping web surfaces in penetration tests.
Discover more Discover more tools
Assetfinder: Rapid Subdomain Enumeration for Attack Surface Mapping
Assetfinder is an OSINT tool for enumerating subdomains from public sources during the reconnaissance phase. It's ideal for quickly mapping a domain's attack surface during penetration testing.
Discover more Discover more