
- blog
- 4+ Note
- Focus
- OSCP · Red Team
- Structure
- Recon → Exploit
SSRF blog
Filters
No results found.
 web hacking
XXE Injection (XML External Entity): file read, SSRF and RCE
XXE (XML External Entity) in pentesting: payload for file read, SSRF, Blind XXE OOB and RCE, testing with Burp Suite and Nuclei, prevention in XML parsers.
Discover more Discover more walkthroughs
HTB Love Walkthrough: SSRF, SQLi Time-Based and Privesc
Write-Up HTB Love, Easy VM: SQLi time-based, NTLM attempt on Responder, SSRF towards 5000, and privesc with AlwaysInstallElevated. Every dead end explained.
Discover more Discover more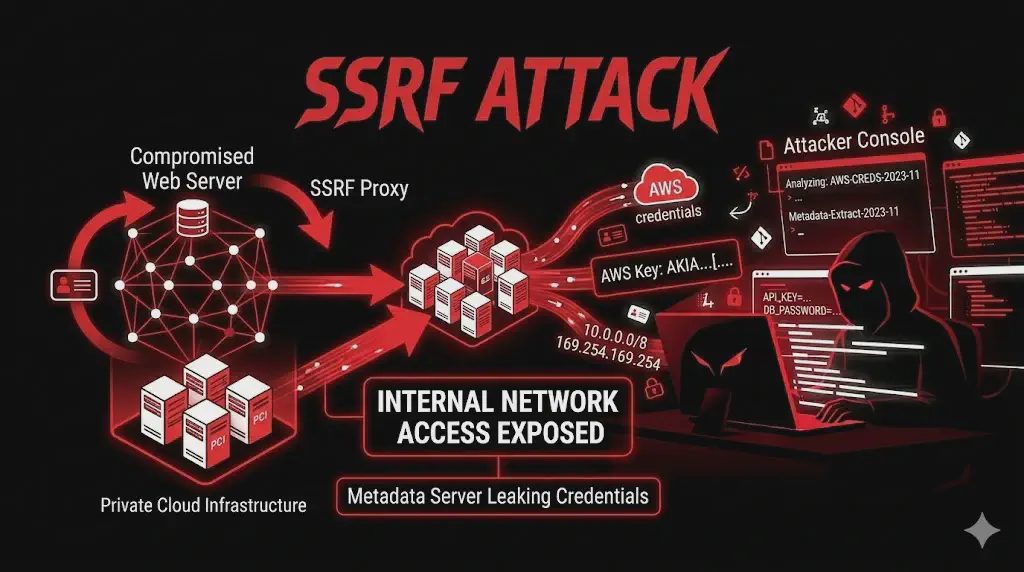 web hacking
SSRF Attack: Server-Side Request Forgery, Cloud Metadata and AWS Credential Theft
The Complete Guide to SSRF: How to Find Server-Side Request Forgery, Bypass IP Filters, Read AWS Metadata, and Get Cloud Credentials.
Discover more Discover more web hacking
Open Redirect: What It Is, How to Use It, and Chain with OAuth and SSRF
Open Redirect in Web Pentesting: Detection, URL and Chain Validation Bypass with OAuth Token Theft, SSRF Bypass, and Credible Phishing. A Practical Guide.
Discover more Discover more