
- blog
- 4+ Note
- Focus
- OSCP · Red Team
- Structure
- Recon → Exploit
Privilege Escalation blog
Filters
No results found.
 windows
Windows Filesystem: NTFS, Folders, and Registry for Pentesting
A practical guide to the Windows file system for pentesting: NTFS, system folders, the registry, ACLs, enumeration commands, privilege escalation, and detection.
Discover more Discover more windows
Windows Privilege Escalation: Techniques and Tools to Obtain SYSTEM
A guide to privilege escalation on Windows: enumeration, vulnerable services, token impersonation, DLL hijacking, UAC bypass, detection, and mitigations.
Discover more Discover more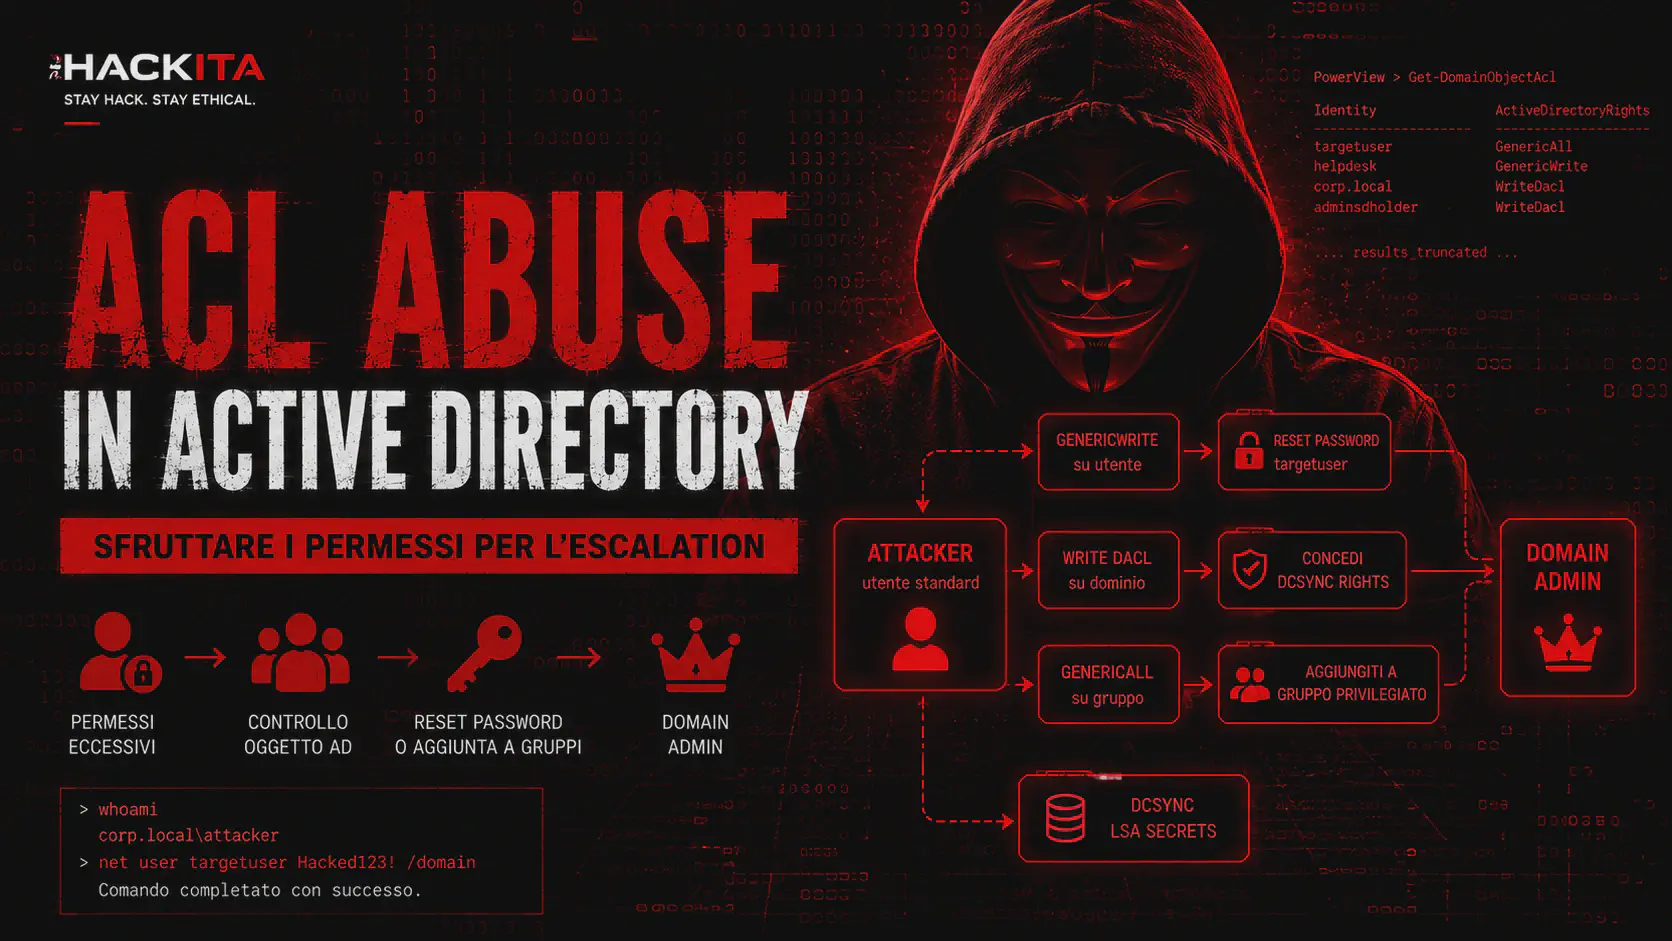 windows
ACL Abuse Active Directory: GenericAll, WriteDACL and DCSync
Guide to ACL abuse in Active Directory: GenericAll, WriteDACL, reset password, RBCD and DCSync with BloodHound, PowerView, bloodyAD and Impacket.
Discover more Discover more windows
SeRestorePrivilege: From Backup Operator to SYSTEM in 3 Steps
How to abuse SeRestorePrivilege to overwrite system binaries and gain SYSTEM shell. ImagePath hijacking, DLL sideloading, persistent backdoor. Red Team technique.
Discover more Discover more