
- blog
- 11+ Note
- Focus
- OSCP · Red Team
- Structure
- Recon → Exploit
OSINT blog
Filters
 web hacking
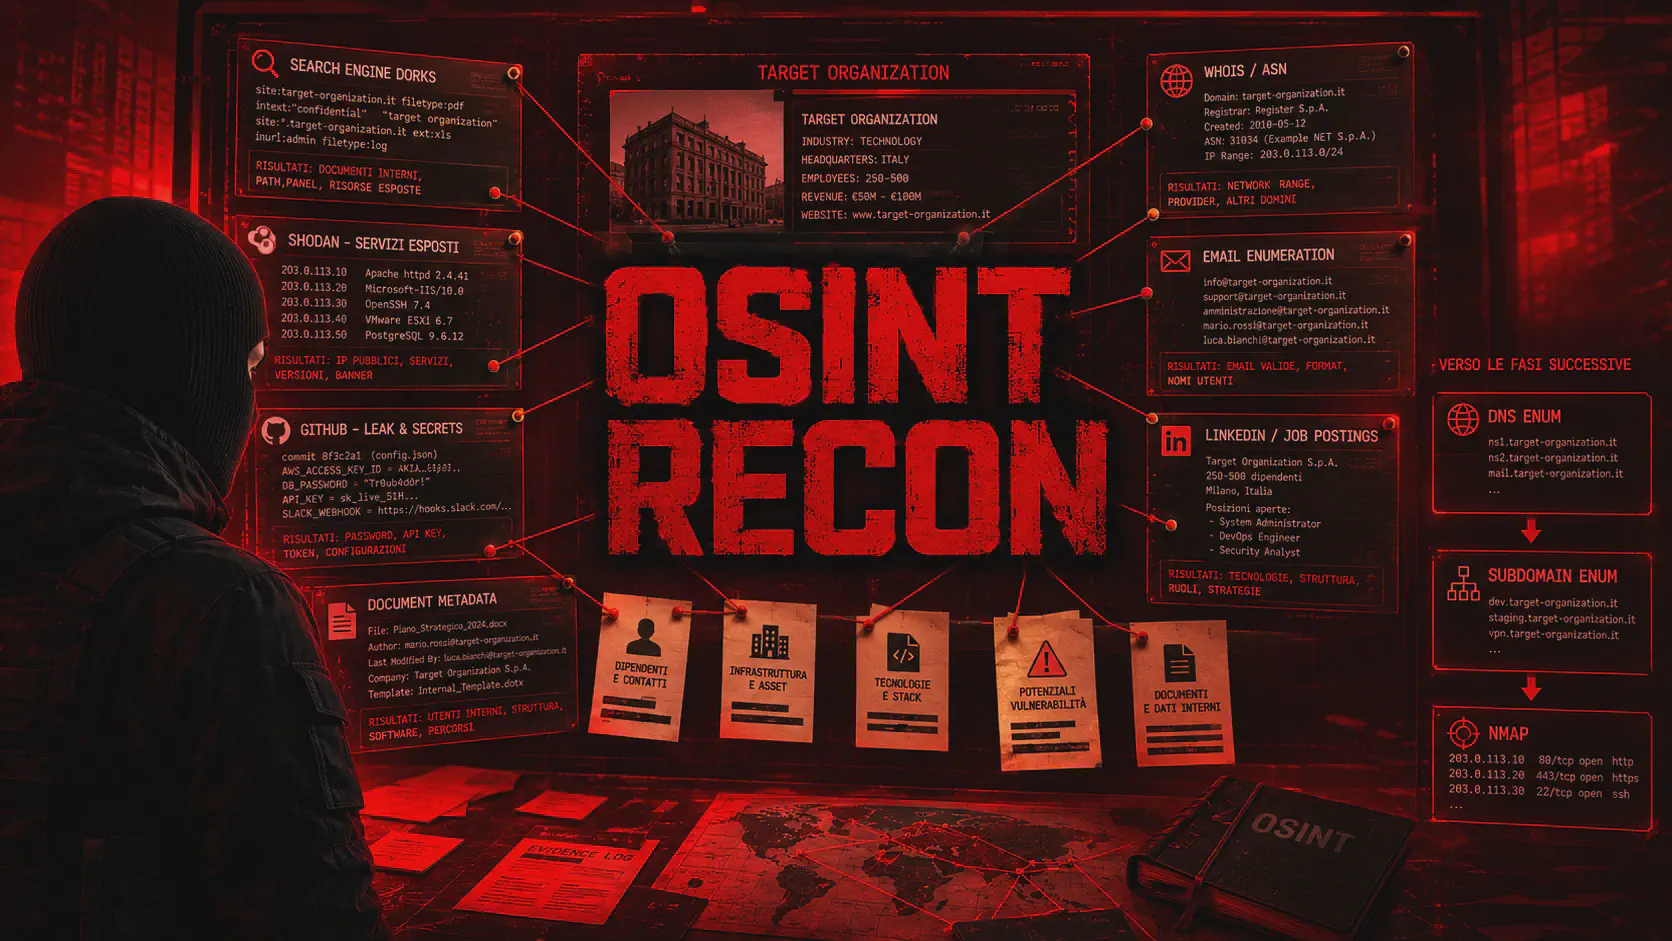
Recon OSINT: Tool, theHarvester, Shodan and Google Dorks.
Passive OSINT reconnaissance for pentesters: Collect emails, subdomains, exposed devices, and metadata with theHarvester, Google Dorks, Shodan, and Metagoofil.
Discover more Discover more web hacking
Recon Pipeline: OSINT Automation for Bug Bounty and Pentesting
Automated recon pipeline guide: subdomain enumeration, DNS, port scanning, fingerprinting, Nuclei, and secret scanning for bug bounty and pentesting.
Discover more Discover more networking
Port 43 WHOIS: OSINT on Domains, IPs and Name Servers
WHOIS port 43 allows passive queries on domains, IPs, and ASNs to gather registrars, name servers, contacts, and expiration dates for reconnaissance and OSINT.
Discover more Discover more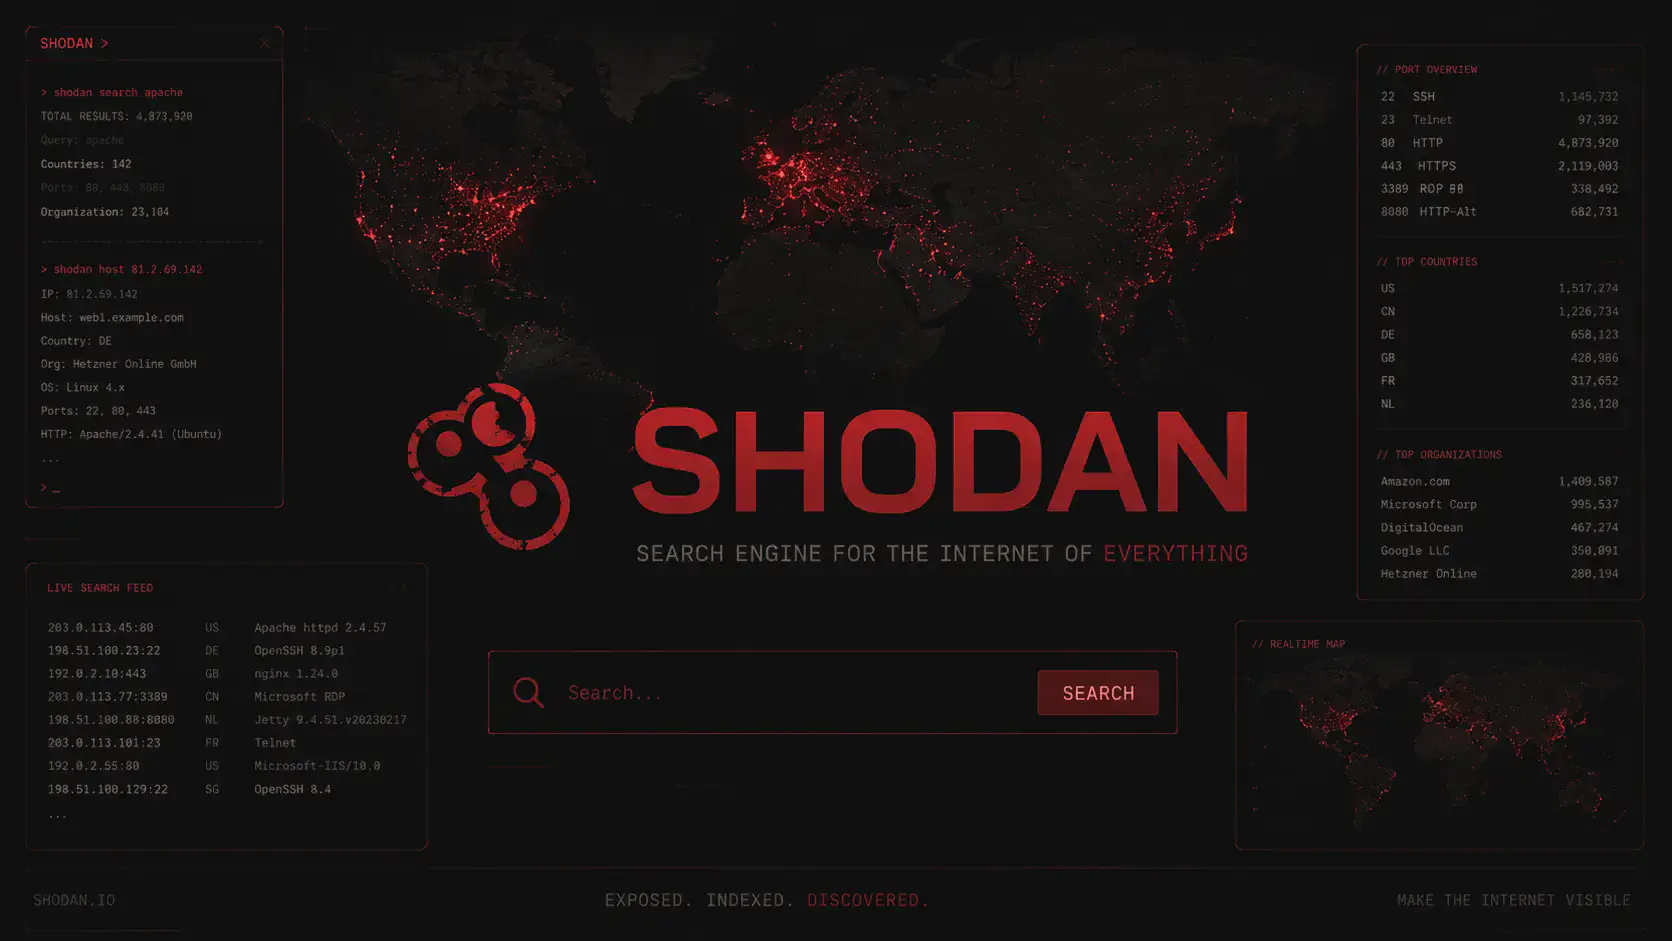 networking
Shodan: A Guide to Dork, Advanced Queries and Filters (2026)
Shodan: Practical dorks for MongoDB, IoT, ICS and CVE, advanced filters, CLI, API, InternetDB and complete cheat sheet for passive reconnaissance and pentesting (2026).
Discover more Discover more web hacking
Recon-ng: Modular OSINT Framework for Advanced Reconnaissance
Recon-ng is a modular OSINT framework with a Metasploit-like interface. Ideal for automated collection of domains, emails, and external assets.
Discover more Discover more web hacking
ReconSpider for Kali: Web Recon and Automated OSINT
ReconSpider is an OSINT tool for automating web reconnaissance and intelligence gathering on domains, IPs, emails, metadata, and other public sources.
Discover more Discover more tools
HostRecon: Automatic OSINT Reconnaissance on Single Targets
HostRecon automates single-domain OSINT and reconnaissance: DNS, whois, subdomain, breach data, and exposure mapping in a single command.
Discover more Discover more web hacking
Amass: Advanced Subdomain Enumeration for Reconnaissance and Attack Surface Mapping
Amass is an OSINT and active reconnaissance tool for enumerating subdomains, mapping external assets, and analyzing DNS relationships. A practical guide to its use during attack surface discovery during a penetration test.
Discover more Discover more tools
Assetfinder: Rapid Subdomain Enumeration for Attack Surface Mapping
Assetfinder is an OSINT tool for enumerating subdomains from public sources during the reconnaissance phase. It's ideal for quickly mapping a domain's attack surface during penetration testing.
Discover more Discover more tools
Maltego: What It Is and How to Use It for OSINT and Transform (2026)
How to Install Maltego for OSINT and Reconnaissance: Use Entity, Transform, Pivot, and Graph Analysis to Correlate Domains, IPs, Emails, People, and Infrastructure.
Discover more Discover more tools
TheHarvester: Rapid Email Enumeration and Subdomain Discovery for Initial Reconnaissance
TheHarvester is an OSINT tool for enumerating emails, subdomains, hosts, and public information from search engines and external data sources. A practical guide to its use in reconnaissance and penetration testing.
Discover more Discover more