
- blog
- 2+ Note
- Focus
- OSCP · Red Team
- Structure
- Recon → Exploit
Network Discovery blog
Filters
No results found.
 tools
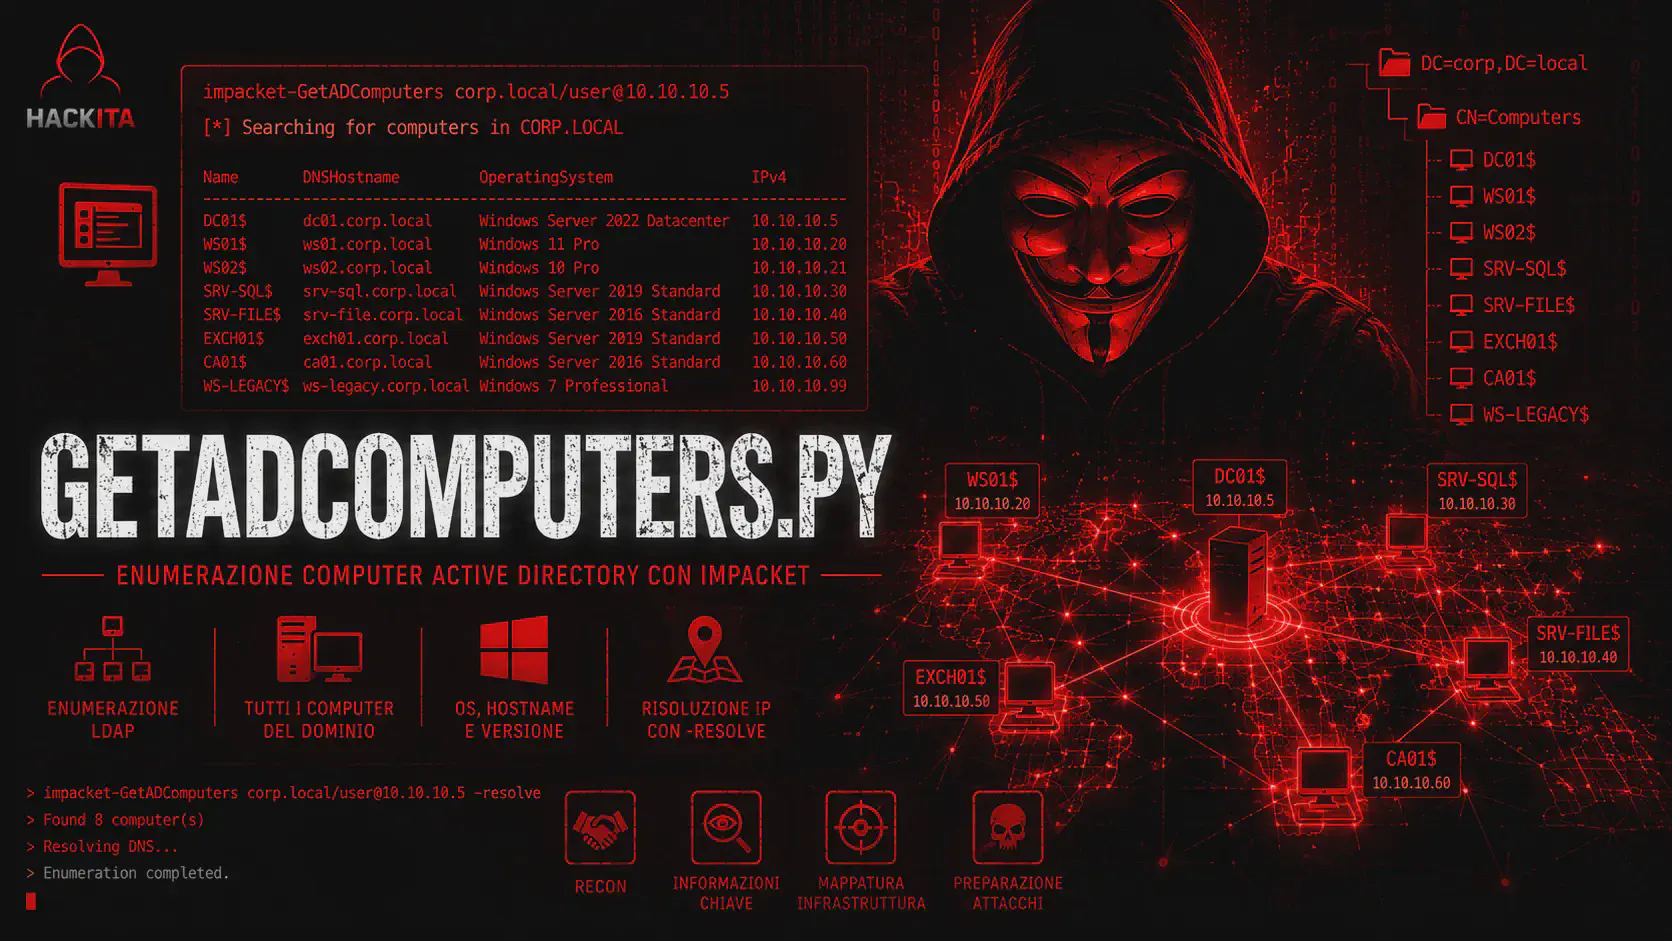
GetADComputers.py — Enumerate Active Directory Computers with Impacket
How to use impacket-GetADComputers to enumerate Active Directory computers via LDAP, -resolveIP ,auth with password, NTLM hash, Kerberos, ccache or AES keys.
Discover more Discover more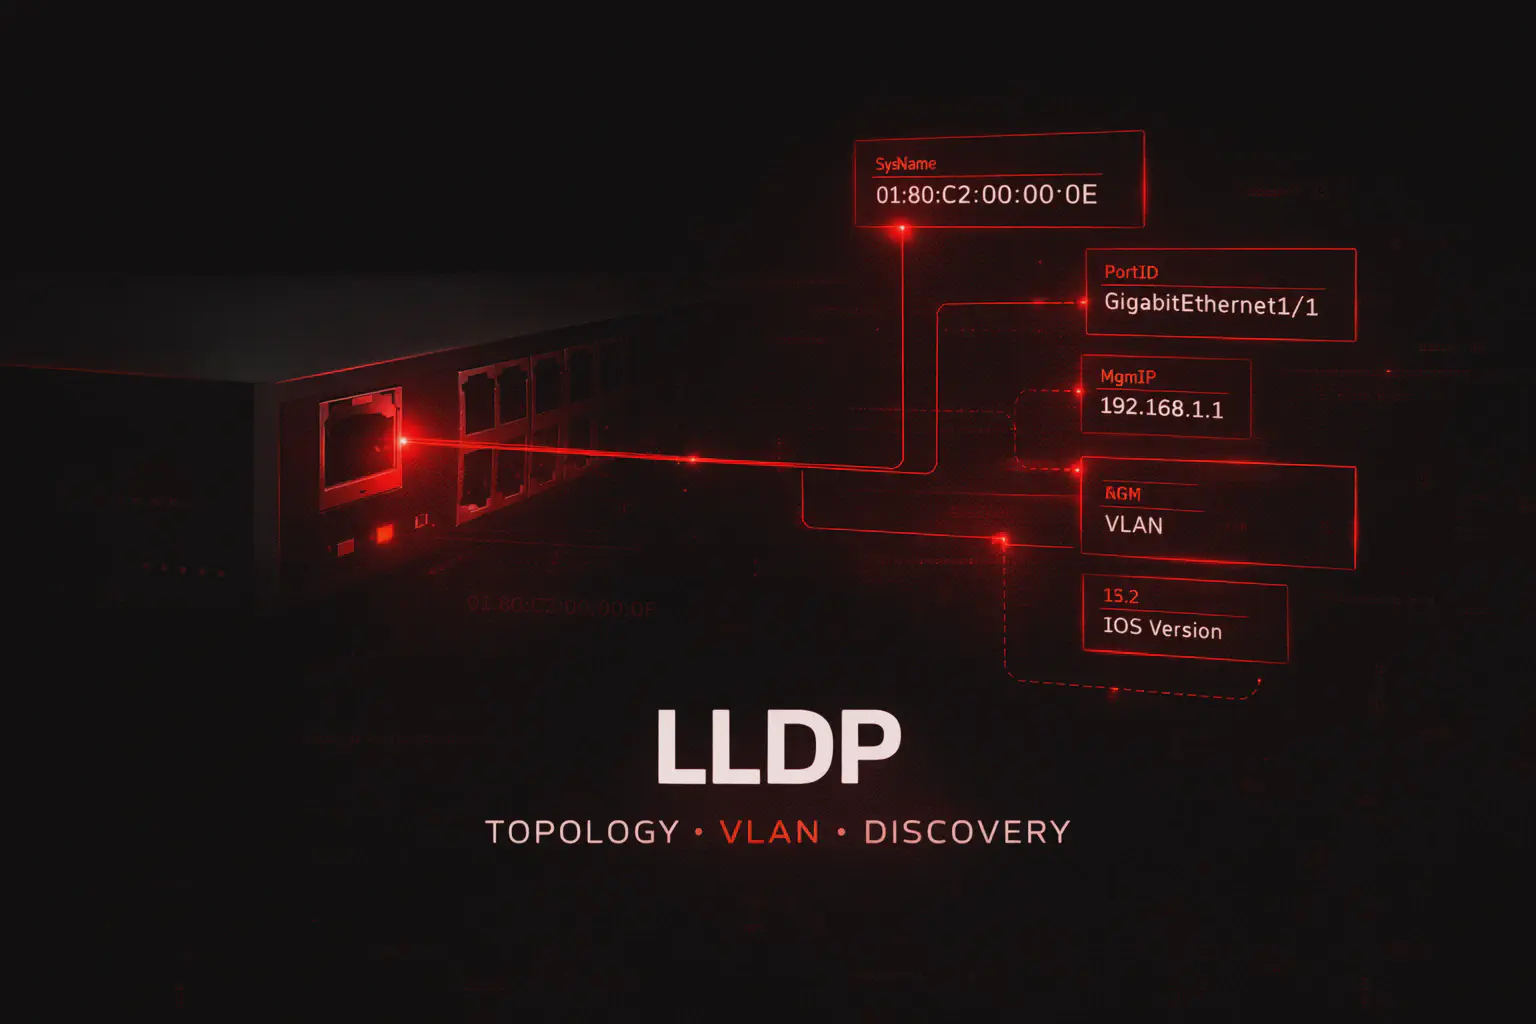 networking
LLDP: The Protocol That Reveals Switches, VLANs, and Network Topology
Learn what LLDP is, how it works, and why it's useful in pentesting: passive discovery, neighbor tables, VLANs, IP management, LLDP-MED, spoofing, and defenses.
Discover more Discover more