
- blog
- 12+ Note
- Focus
- OSCP · Red Team
- Structure
- Recon → Exploit
Kerberos blog
Filters
 tools
ticketer.py: Golden and Silver Ticket Kerberos with Impacket
Impacket-ticketer guide to forge Golden and Silver Kerberos Tickets with NTLM hashes or AES keys, customize PAC, and save ticket ccache.
Discover more Discover more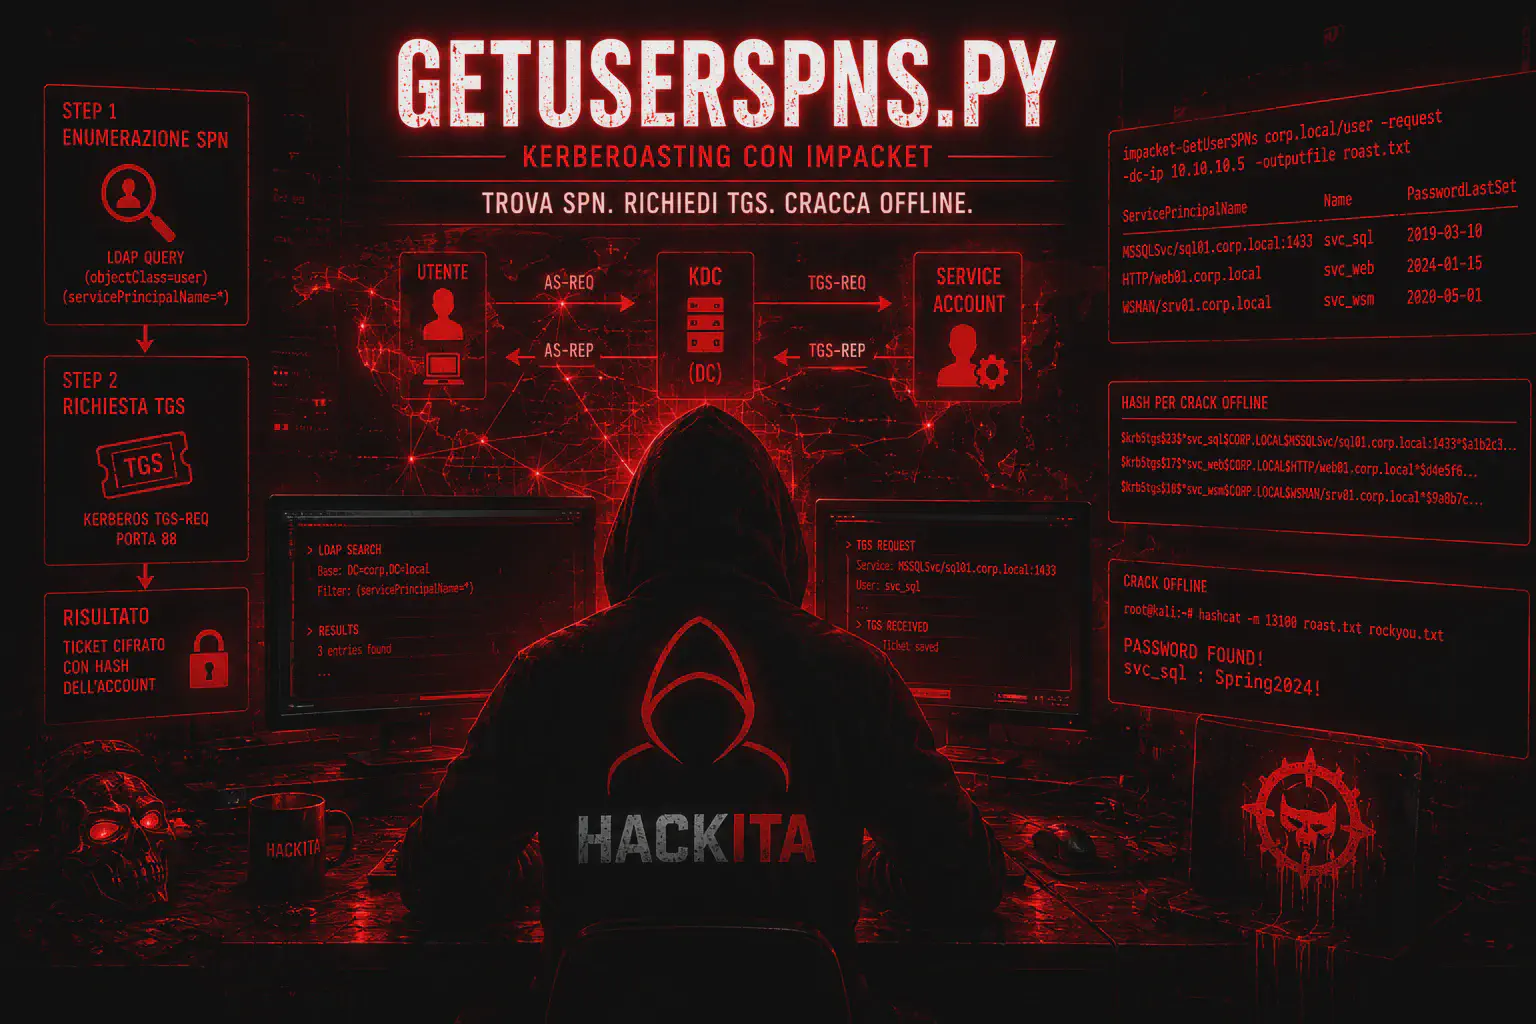 tools
GetUserSPNs.py: Kerberoasting and TGS with Impacket
How to use impacket-GetUserSPNs to enumerate accounts with SPNs and request Kerberos TGS with passwords, NTLM hashes, caches, or AES keys for Windows Active Directory
Discover more Discover more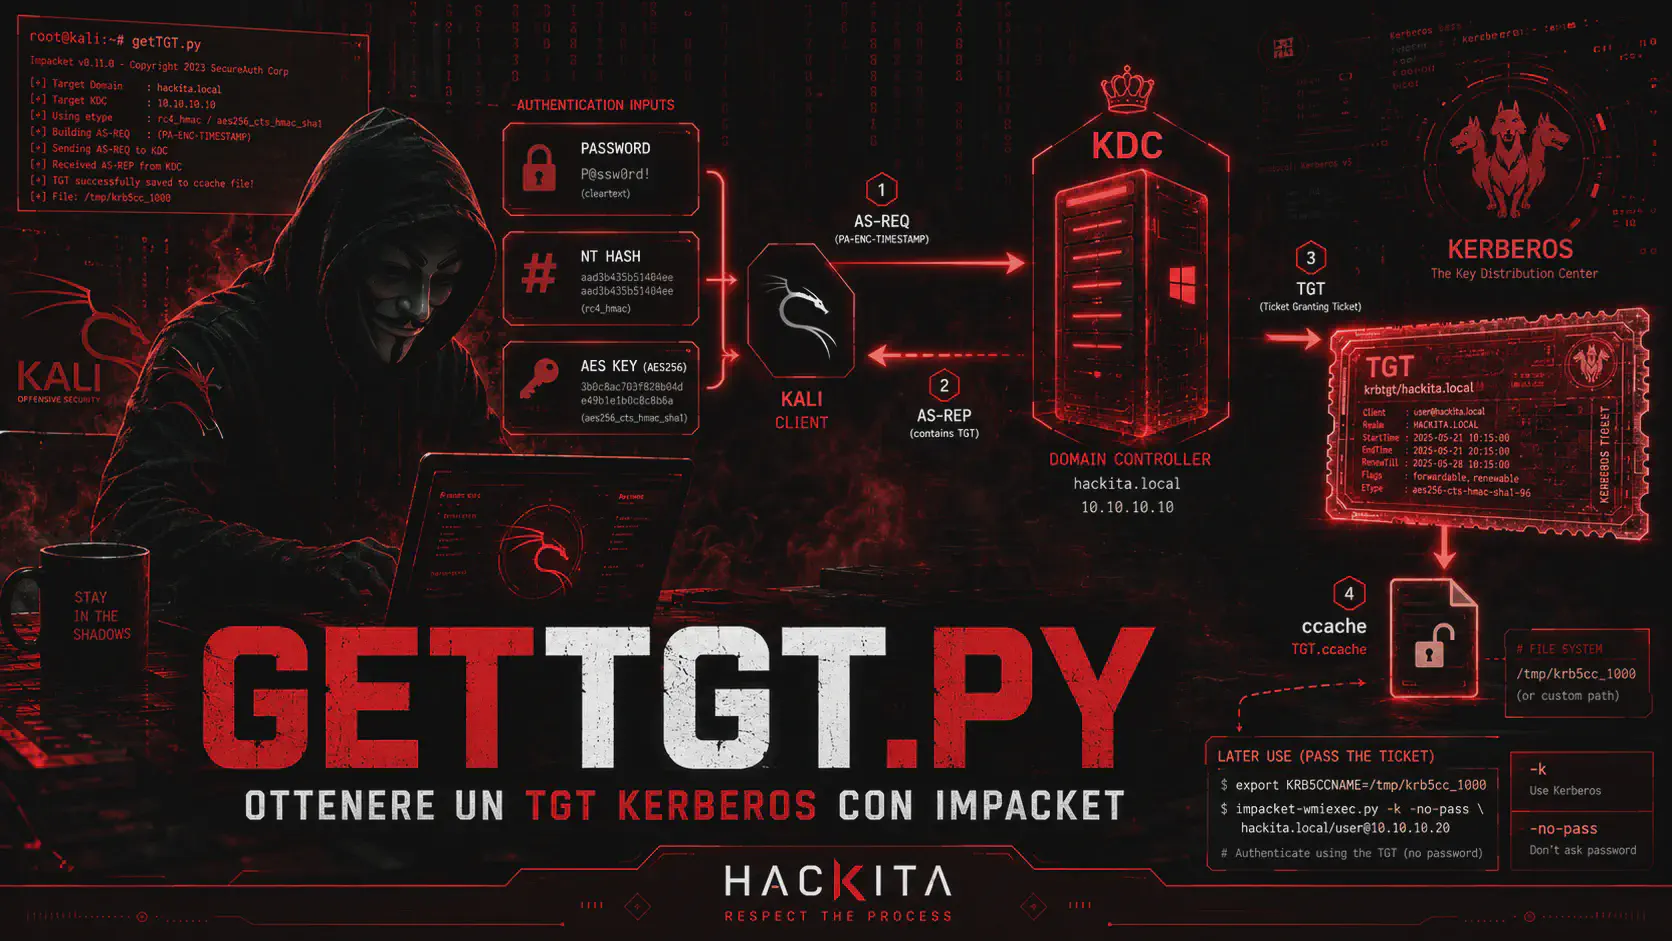 tools
getTGT.py: Getting a Kerberos TGT with Hash or AES
How to use impacket-getTGT to request a Kerberos TGT and save it in ccache format using a password, NTLM hash, or AES key in Active Directory.
Discover more Discover more tools
GetLAPSPassword.py: Recover LAPS Passwords with Impacket
Impacket's GetLAPSPassword.py guide for recovering encrypted Legacy LAPS and Windows LAPS passwords from Active Directory with passwords, NTLM hashes, or Kerberos.
Discover more Discover more tools
GetADUsers.py Inpacket: Enumerate Active Directory Users
Impacket's GetADUsers.py guide to enumerate Active Directory users via LDAP with password, NTLM hash, AES or Kerberos key and parse pwdLastSet and lastLogon.
Discover more Discover more windows
AS-REP Roasting: Cracking Kerberos Hashes Without Credentials
AS-REP Roasting in Active Directory: Extract Kerberos hashes without credentials and crack them offline with Impacket, Rubeus, and Hashcat. A complete technical guide.
Discover more Discover more windows
Sapphire Ticket: Kerberos Stealth S4U2Self+U2U Ticket
Sapphire Ticket: The stealthiest Kerberos ticket. Combines S4U2Self + U2U for the authentic KDC PAC. Impacket impersonation guide, differences from Golden/Diamond, detection, and mitigation.
Discover more Discover more windows
Diamond Ticket Attack: The Stealth Evolution of the Golden Ticket
Diamond Ticket: A stealth variant of the Golden Ticket with a real TGT to bypass MDI. Rubeus /ldap /opsec guide, Impacket, detection, and KRBTGT reset.
Discover more Discover more windows
ESC13 AD CS: Privesc with Issuance Policy OID and Certipy
Privilege escalation in Active Directory via ESC13: Certipy detects Issuance Policy OIDs linked to AD groups and explains privilege abuse via Kerberos TGT.
Discover more Discover more windows
Active Directory Pentesting 2026: Complete Guide to Kerberos, NTLM and Privilege Escalation
Active Directory Pentesting operationally explained: AD architecture, Kerberos vs NTLM, BloodHound, Kerberoasting, AS-REP Roasting, NTLM Relay, ACL abuse, AD CS, DCSync, Golden Ticket, Shadow Credentials and real defenses.
Discover more Discover more windows
Kerberos: What It Is, Authentication, Port 88, Active Directory
How Kerberos Works on Windows: KDC, TGT and TGS Tickets, TCP/UDP Port 88, Kerberos vs. NTLM and LDAP. Configuration, Errors, Security, and Command-Line Attacks
Discover more Discover more windows
Rubeus: Kerberos Attacks in Active Directory (2026)
Rubeus is the reference C# tool for attacking Kerberos in AD. Discover Kerberoasting, AS-REP Roasting, Pass-the-Ticket, and S4U with real-world detection.
Discover more Discover more