
- blog
- 2+ Note
- Focus
- OSCP · Red Team
- Structure
- Recon → Exploit
Http blog
Filters
No results found.
 networking
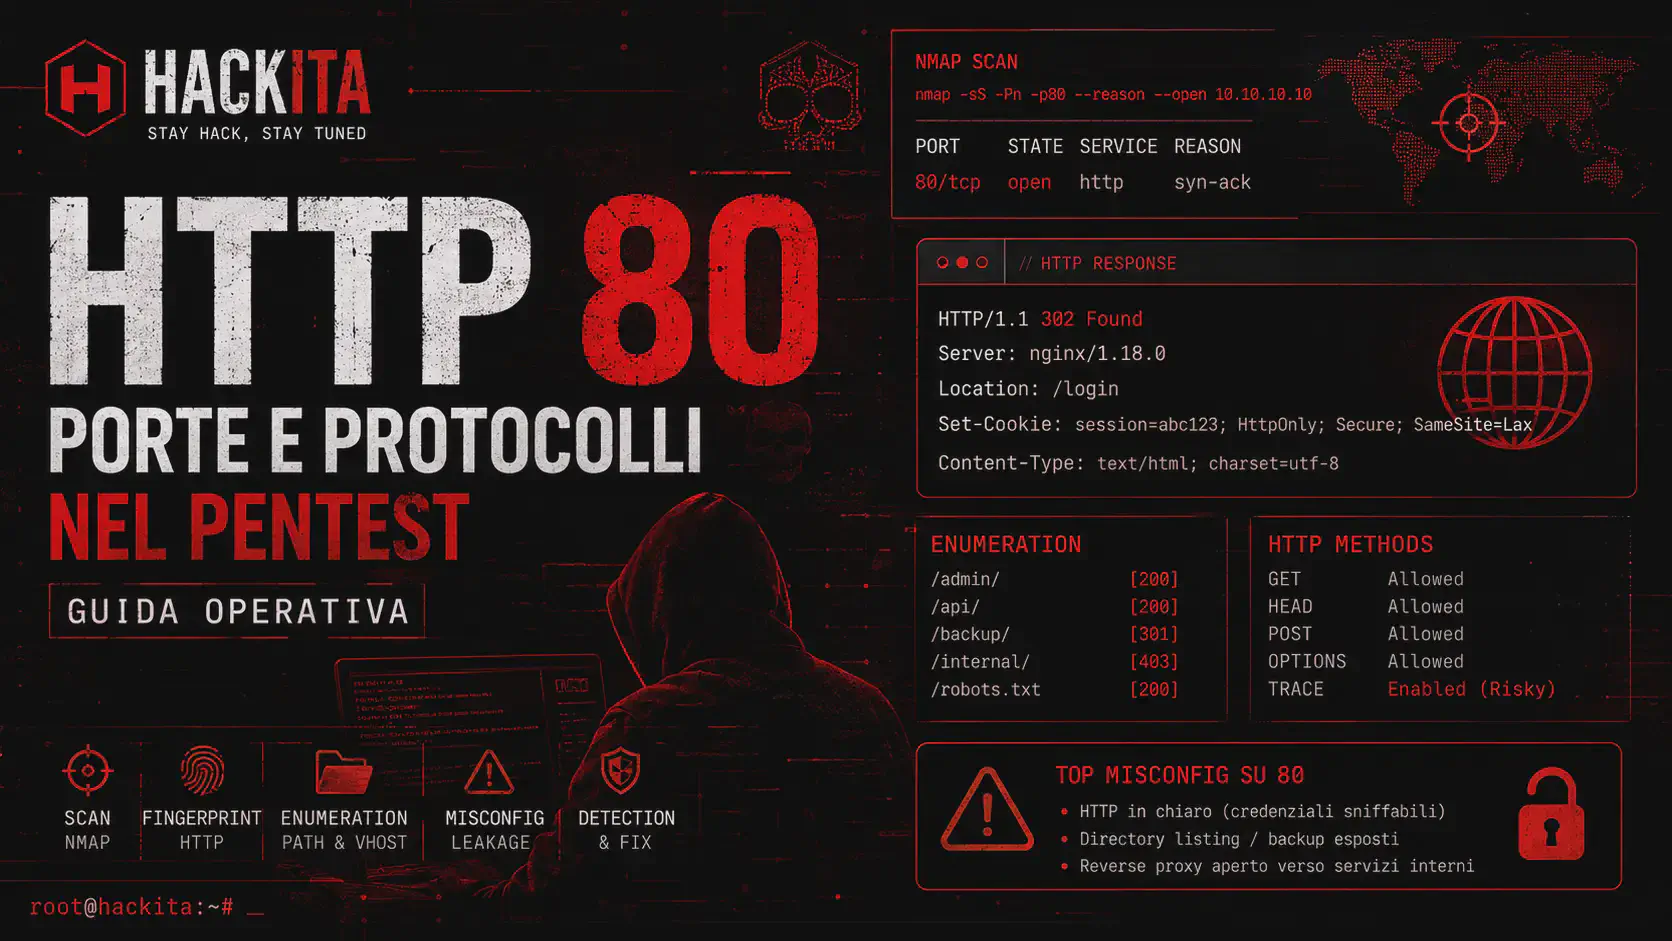
HTTP Port 80: Operational Guide (Ports/Protocols) in Pentesting
Port 80 in pentest lab: scan, HTTP fingerprint, vhost enum, directory brute force, misconfig and detection. Workflow with Nmap/ffuf/curl.
Discover more Discover more networking
HTTP and HTTPS: What They Are, How They Work, and How to Use Them in a Pentest
Learn what HTTP is, how HTTPS works, and why it's essential in web pentesting: methods, headers, cookies, status codes, fingerprinting, enumeration, and real-world attacks.
Discover more Discover more