
- blog
- 3+ Note
- Focus
- OSCP · Red Team
- Structure
- Recon → Exploit
File upload blog
Filters
No results found.
 web hacking
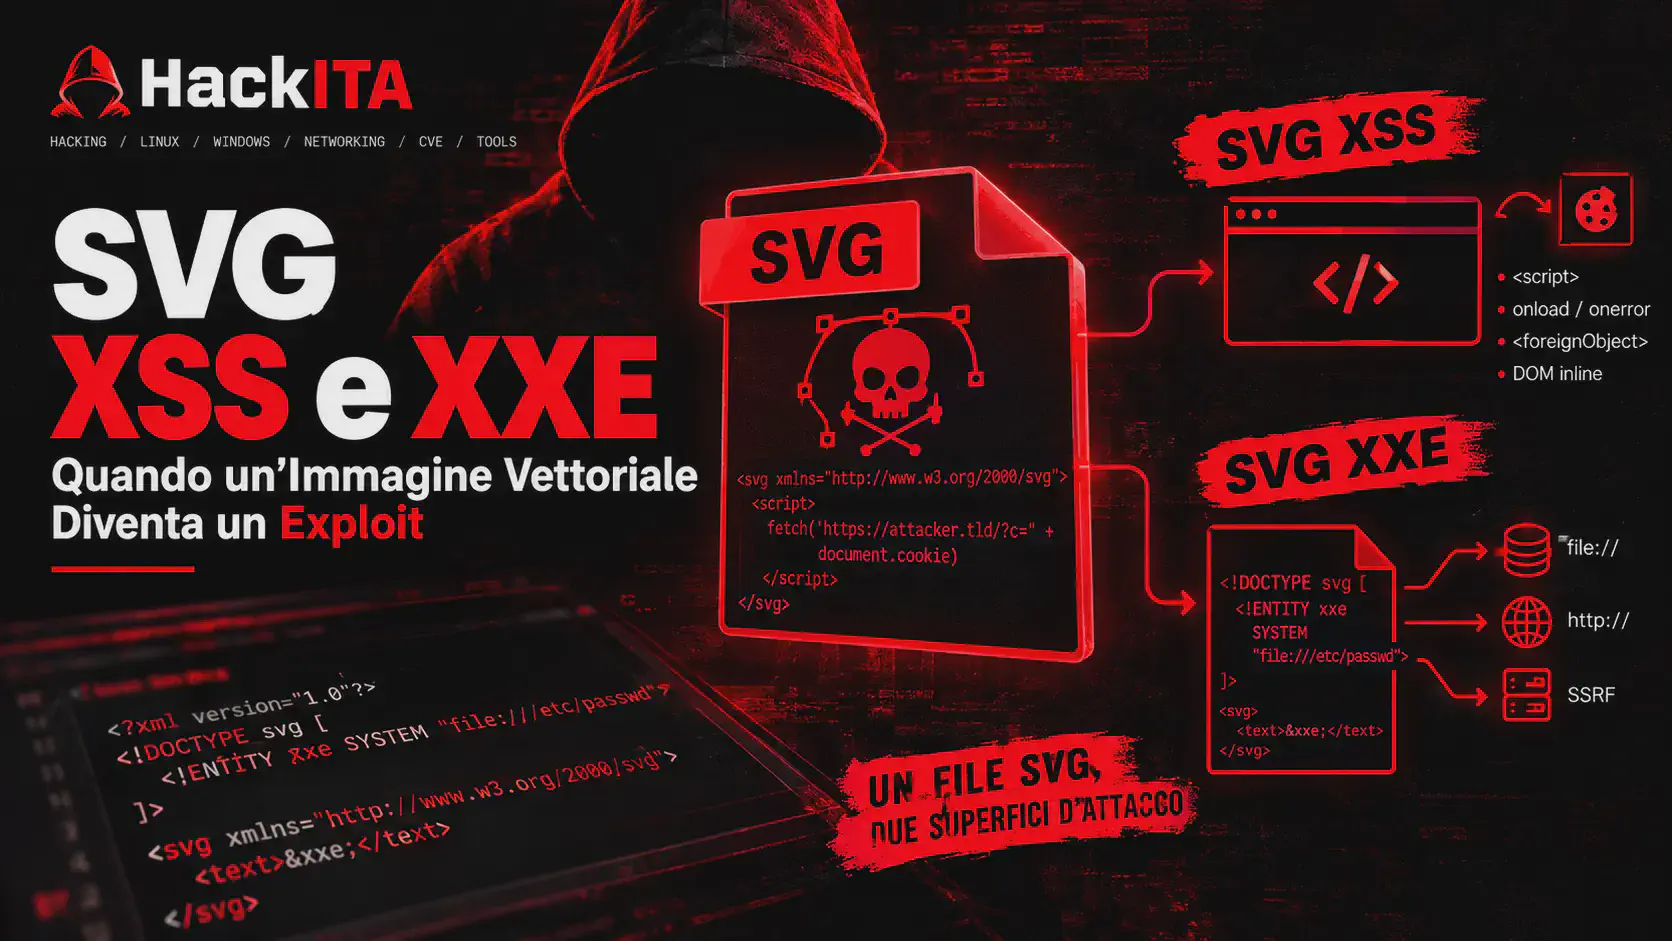
SVG XSS and XXE: Attack via Image Upload
An uploaded SVG can execute scripts or read local files. A practical guide to XSS and XXE via SVG: real-world payloads, attack vectors, and mitigations for developers.
Discover more Discover more walkthroughs
HTB Help Walkthrough: GraphQL and File Upload HelpDeskZ
Complete Hack The Box: Help write-up. GraphQL enumeration, bypass file upload to HelpDeskZ with vulnerable PHP code analysis, privesc kernel to root.
Discover more Discover more walkthroughs
HTB Falafel Walkthrough: SQLi, PHP Type Juggling and Privesc
Hack The Box's Falafel Machine Write-Up: User Enumeration, Blind SQL Injection, PHP Login Bypass, RCE Upload, and Linux Privilege Escalation.
Discover more Discover more