
- blog
- 2+ Note
- Focus
- OSCP · Red Team
- Structure
- Recon → Exploit
Content-Security-Policy blog
Filters
No results found.
 web hacking
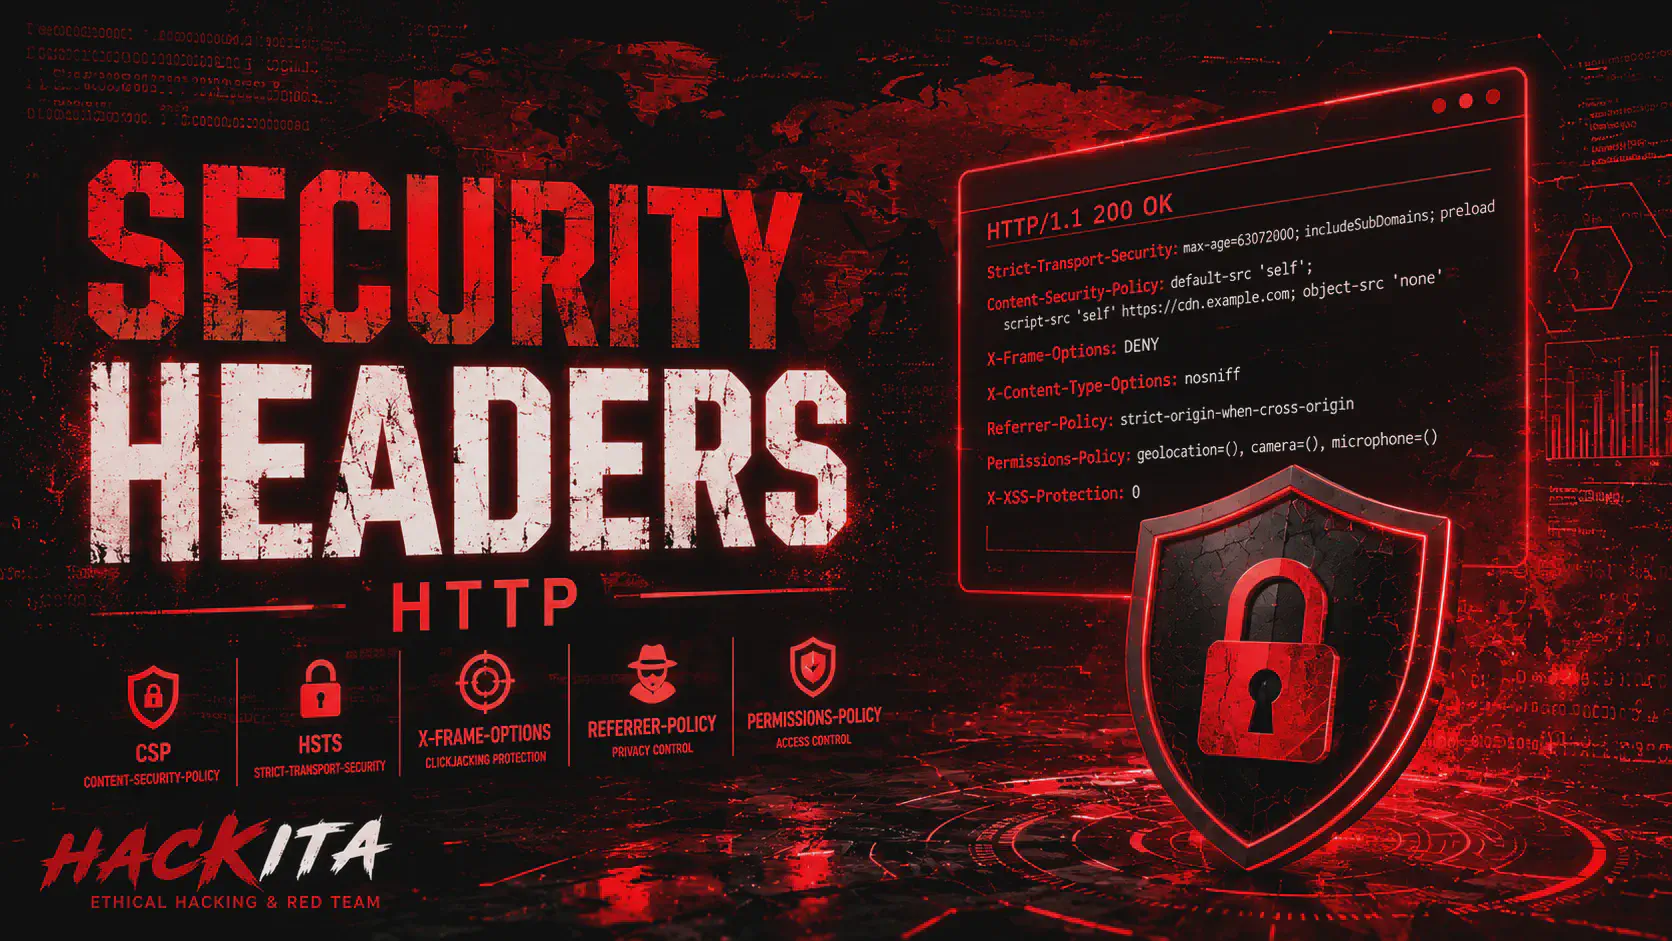
HTTP Security Headers: Guide to CSP, HSTS and Bypass
Learn how to test and configure HTTP security headers: CSP, HSTS, X-Frame-Options, Referrer-Policy and bypass techniques in web pentests.
Discover more Discover more web hacking
CSP Bypass: How to bypass Content Security Policy in XSS tests
A practical guide to CSP bypass: unsafe-inline, weak nonces, base-uri, object-src, JSONP, AngularJS, dangling markup, and real-world techniques for bypassing Content Security Policy.
Discover more Discover more