
- blog
- 5+ Note
- Focus
- OSCP · Red Team
- Structure
- Recon → Exploit
command injection blog
Filters
 web hacking
Command Injection: Payload, Bypass and How to Defend Yourself
Learn what Command Injection is, how it works, where it is found, and how to test for it with Burp Suite and Commix: blind techniques, OOB, filter bypass, and defense.
Discover more Discover more web hacking
RCE (Remote Code Execution): What it is, Vectors and Exploits
RCE in pentesting: Learn the vectors that lead to Remote Code Execution, how to verify them, get a shell, and initiate post-exploitation.
Discover more Discover more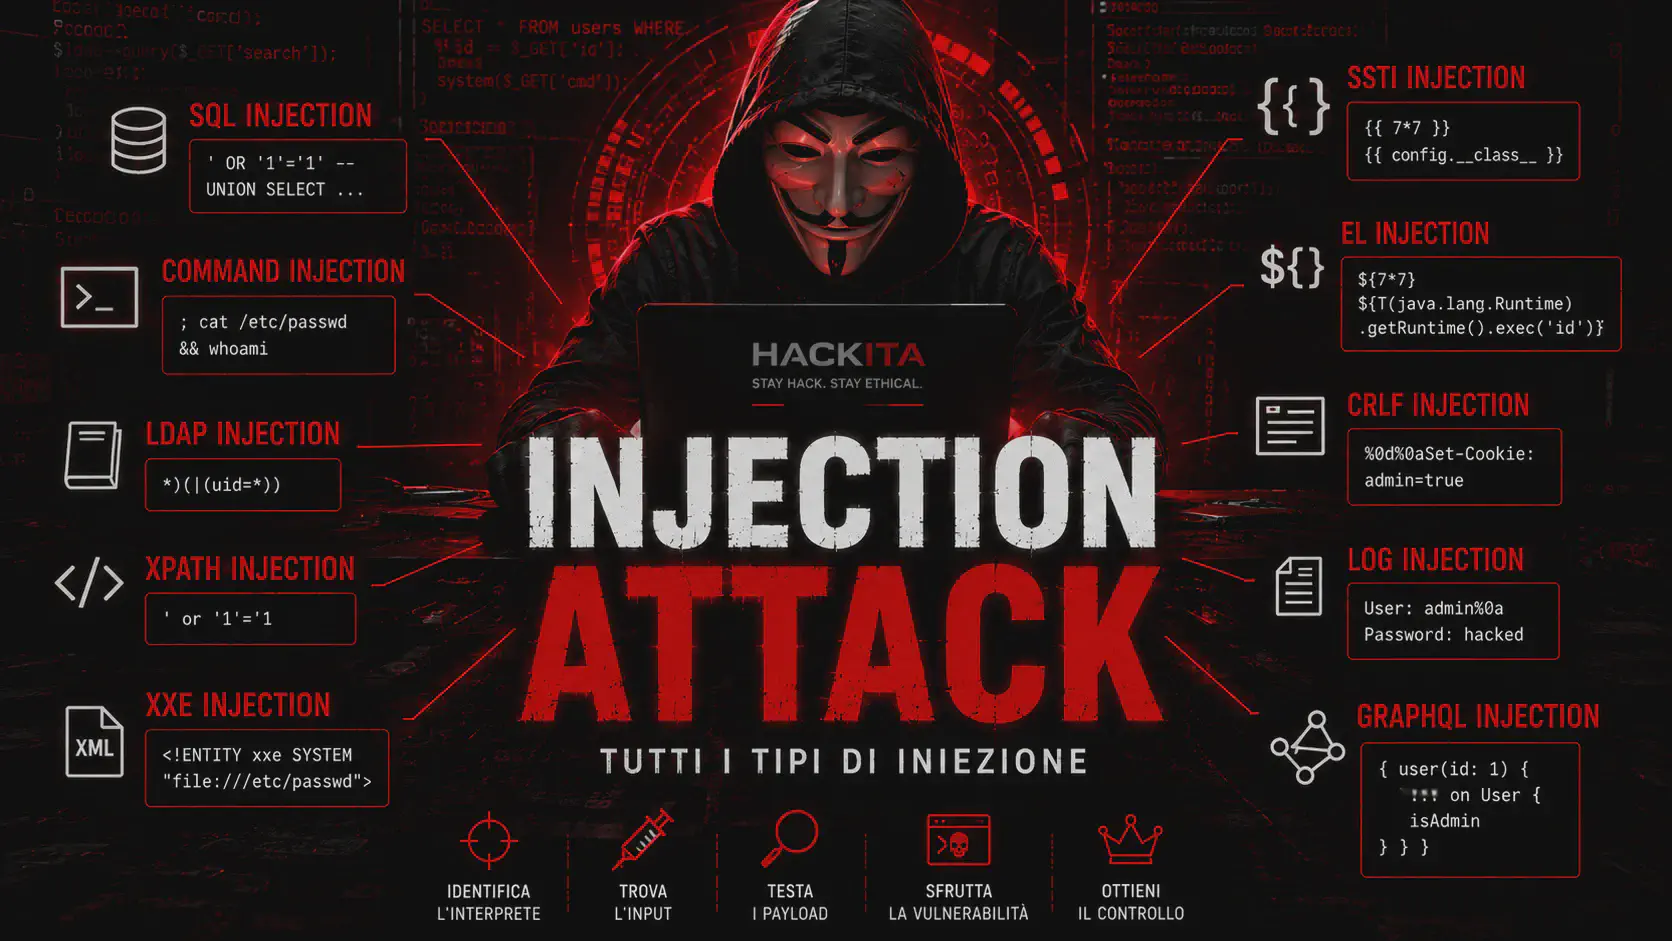 web hacking
Injection Attack: A Complete Guide to Web Injections
A complete guide to injection attacks: SQL injection, command injection, SSTI, XXE, LDAP, NoSQL, and other techniques, with examples, testing, and prevention.
Discover more Discover more web hacking
OS Command Injection: What is it, Argument Injection and RCE on Linux and Windows
OS Command Injection in pentesting: separators, argument injection, exploits on Linux and Windows (curl, tar, ffmpeg, Git, ImageMagick) and post-exploitation.
Discover more Discover more tools
Commix: Automated Command Injection Exploitation Tool
Commix is an automated tool for identifying and exploiting command injection vulnerabilities in web applications. It supports blind, time-based, and file-based techniques to obtain RCE during penetration testing.
Discover more Discover more