
- blog
- 5+ Note
- Focus
- OSCP · Red Team
- Structure
- Recon → Exploit
Burp Suite blog
Filters
 Recon & mapping
Tools
nmap, ffuf, Burp, Python: configurations, aliases, and scripts you'll actually use every time you attack a machine.
Discover more Discover more web hacking
Command Injection: Payload, Bypass and How to Defend Yourself
Learn what Command Injection is, how it works, where it is found, and how to test for it with Burp Suite and Commix: blind techniques, OOB, filter bypass, and defense.
Discover more Discover more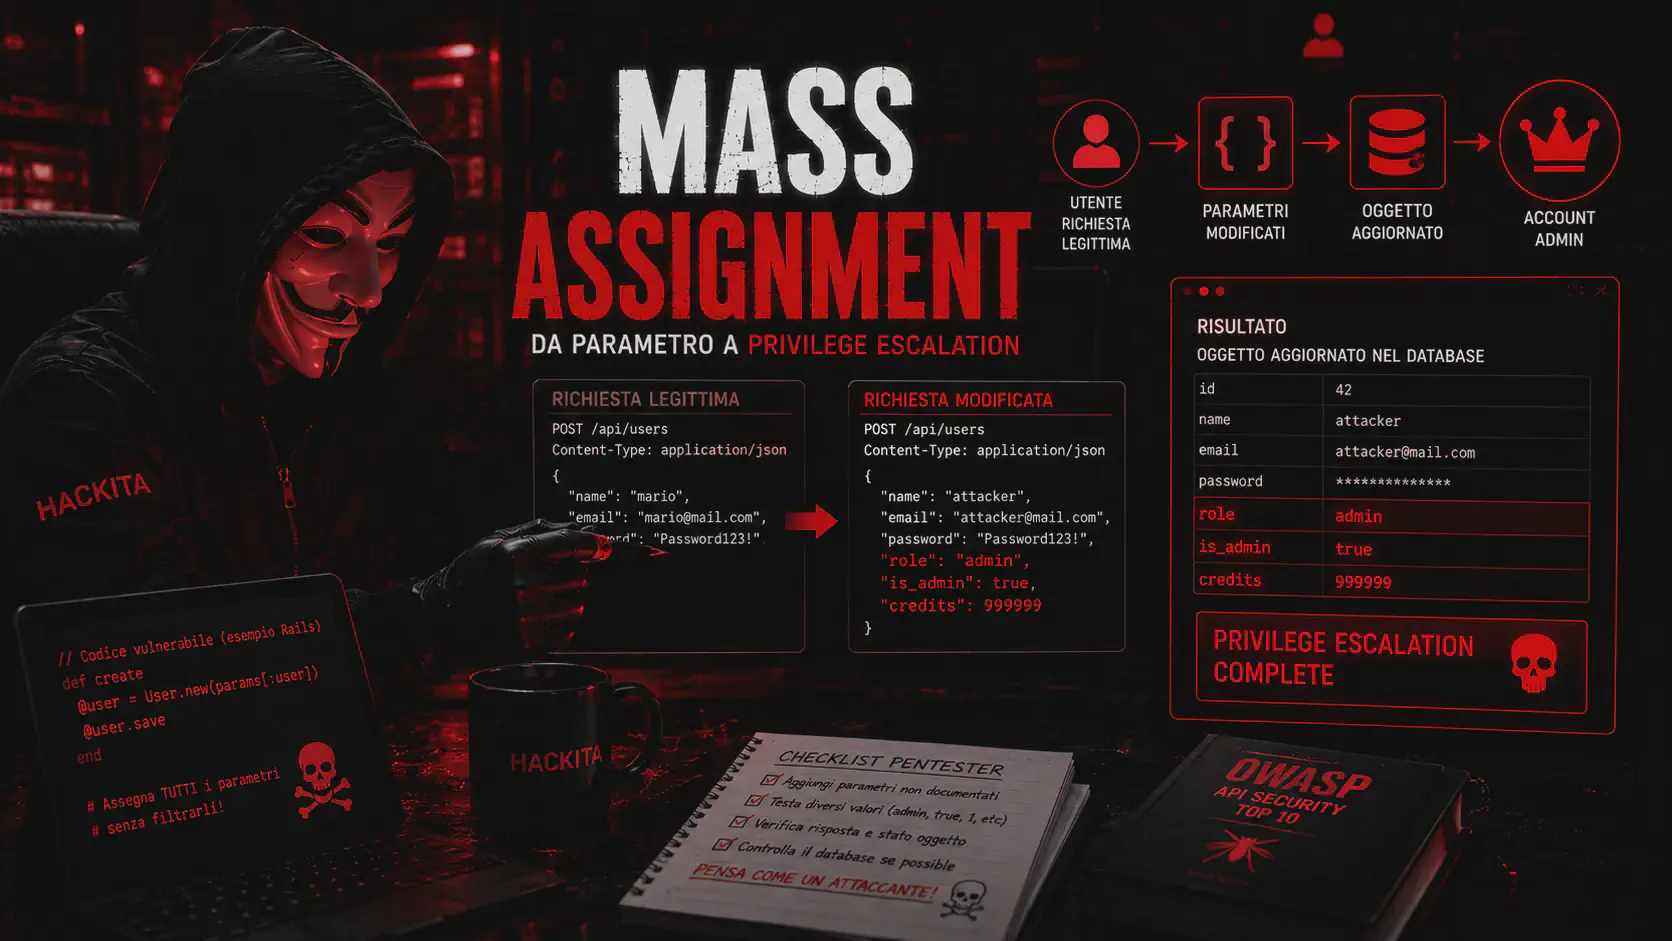 web hacking
Mass Assignment: How to Find and Use It in APIs
Learn what mass assignment is, how to identify it, and how to leverage it in REST APIs, with practical examples for Rails, Laravel, Django, Node.js, and Burp Suite.
Discover more Discover more web hacking
Web Cache Poisoning: Testing, Cache Keys, and Bypass Techniques
Practical guide to Web Cache Poisoning in pentesting: analyze cache keys and unkeyed inputs, test headers and fat GETs with Burp, and apply useful detection and mitigations.
Discover more Discover more web hacking
Burp Suite: Guide to Web Application Penetration Testing
Burp Suite: How to use it in web penetration testing: discover Proxy, Repeater, Intruder and Scanner and how to test SQLi, XSS, CSRF, API, authentication and secrets.
Discover more Discover more