
- blog
- 7+ Note
- Focus
- OSCP · Red Team
- Structure
- Recon → Exploit
Api blog
Filters
 walkthroughs
HTB Help Walkthrough: GraphQL and File Upload HelpDeskZ
Complete Hack The Box: Help write-up. GraphQL enumeration, bypass file upload to HelpDeskZ with vulnerable PHP code analysis, privesc kernel to root.
Discover more Discover more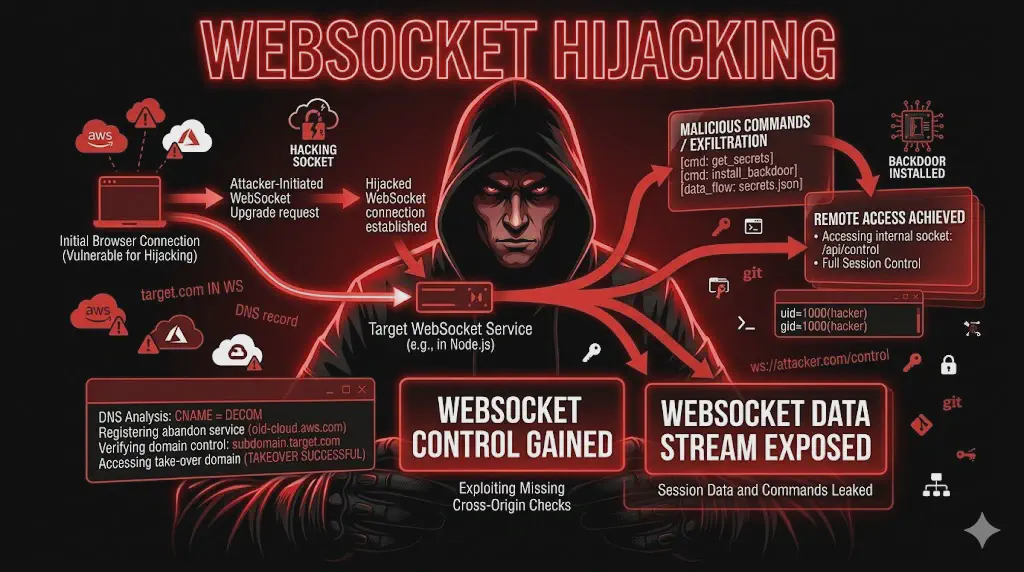 web hacking
WebSocket Hijacking (CSWSH): Cross-Site WebSocket Hijacking and Real-Time Data Theft
WebSocket Hijacking Explained: CSWSH, Vulnerable Handshake, Missing Origin Check, and Real-Time Data Theft from Chats, Notifications, and Dashboards.
Discover more Discover more web hacking
GraphQL Attacks: Introspection, Batching and Data Breach
Find out how to test GraphQL in web pentesting: introspection, batching, authorization bypass, IDOR, brute force and data leak via query.
Discover more Discover more web hacking
CORS Misconfiguration: Complete Guide to Exploit, Bypass and Data Theft in APIs
CORS Misconfiguration in APIs: Learn how to identify, exploit, and demonstrate data theft with origin reflection, null origin, common bypasses, and real-world PoCs with curl and JavaScript.
Discover more Discover more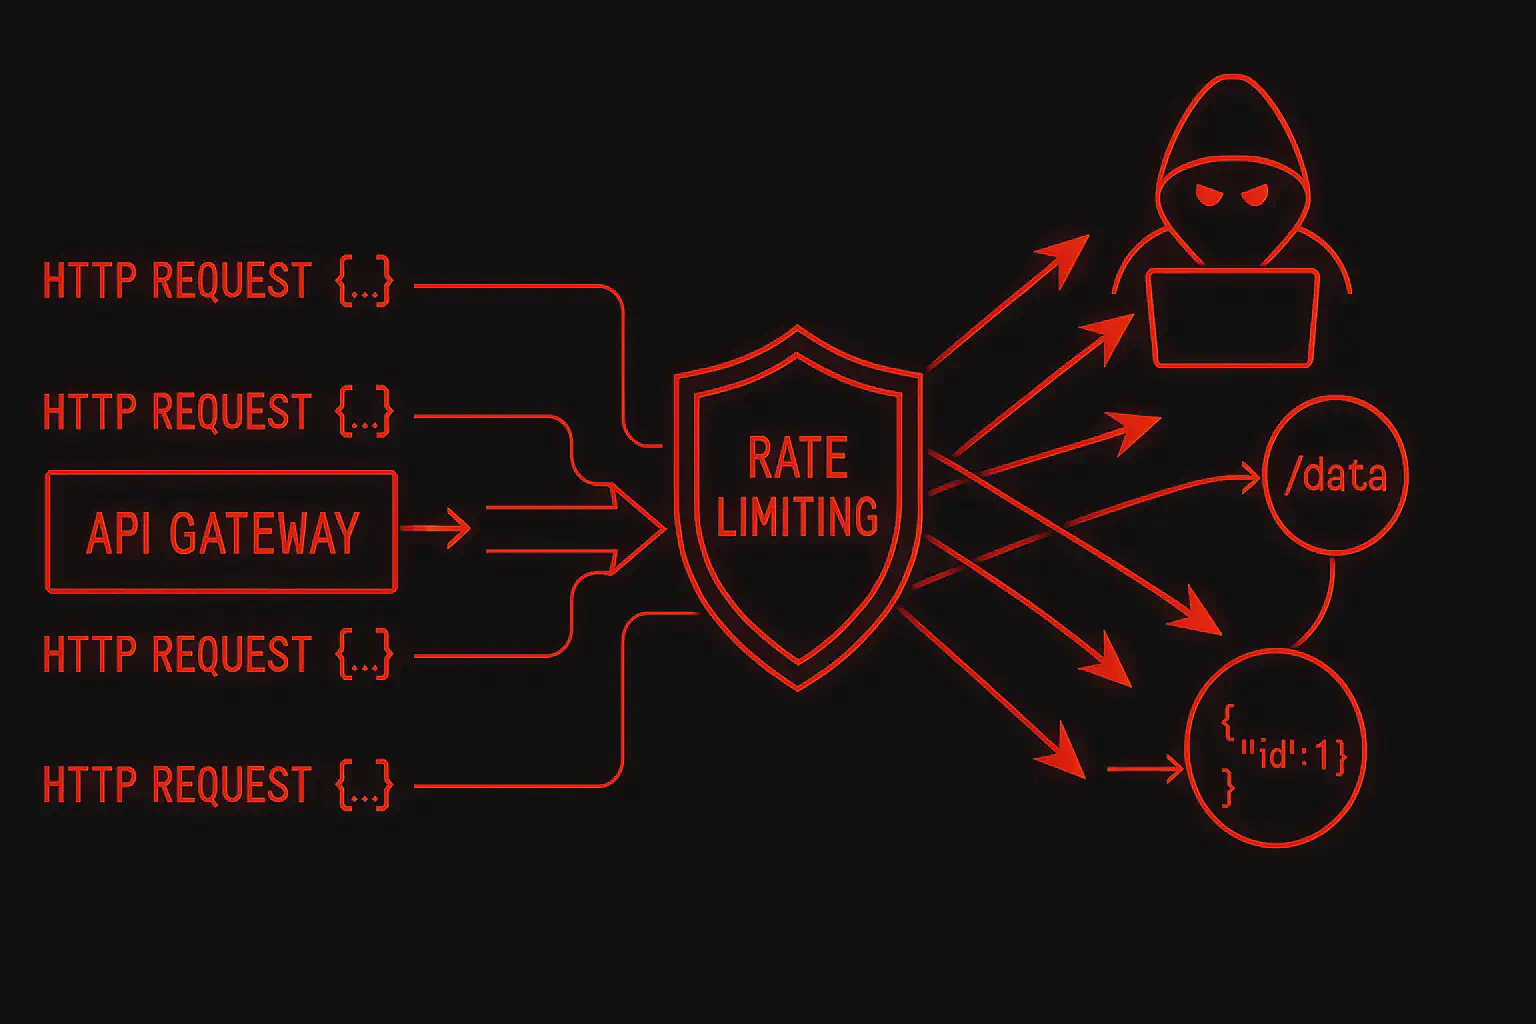 web hacking
API Rate Limit Bypass: Pentesting Techniques to Bypass Throttling (2026)
Rate Limit Bypass API explained operationally: header rotation with X-Forwarded-For, endpoint switching, HTTP method tampering, Unicode bypass, race conditions and GraphQL batching.
Discover more Discover more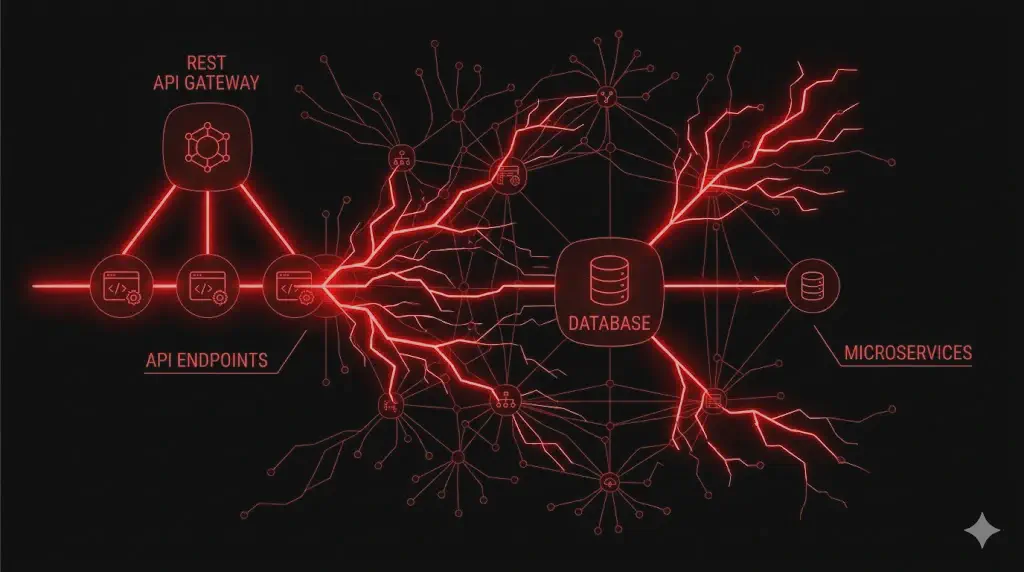 web hacking
API Security: A Complete Guide to API Attacks and Pentesting (SSRF, GraphQL, BOLA, CORS)
API security and penetration testing of modern APIs: SSRF, GraphQL attacks, BOLA/IDOR, CORS misconfiguration, mass assignment, and rate limit bypass. A comprehensive guide with real-world payloads and techniques.
Discover more Discover more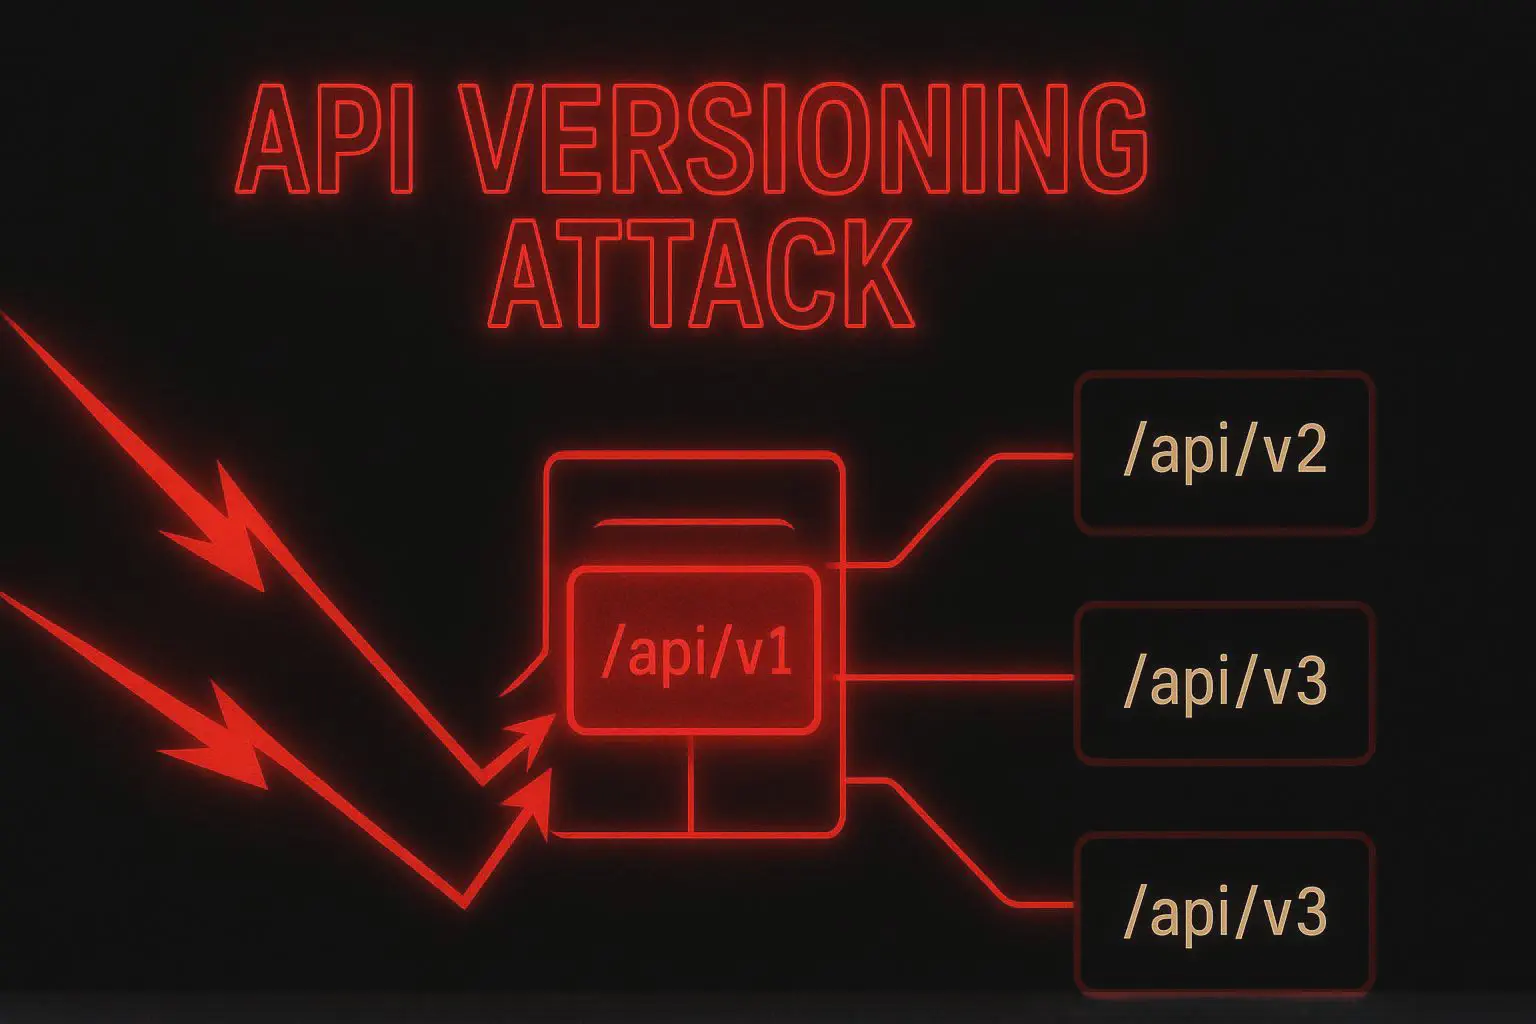 web hacking
API Versioning Attack: Exploiting Forgotten v1 Endpoints in API Pentesting (2026)
API Versioning Attack Operationally Explained: How to find legacy v1 API endpoints, bypass rate limits and authentication, and exploit deprecated APIs during a penetration test.
Discover more Discover more