
- blog
- 32+ Note
- Focus
- OSCP · Red Team
- Structure
- Recon → Exploit
Active Directory blog
Filters
 tools
renameMachine.py: NoPac and sAMAccountName Spoofing
Guide to impacket-renameMachine to change the sAMAccountName of account computers and understand the NoPac chain with CVE-2021-42278 and CVE-2021-42287.
Discover more Discover more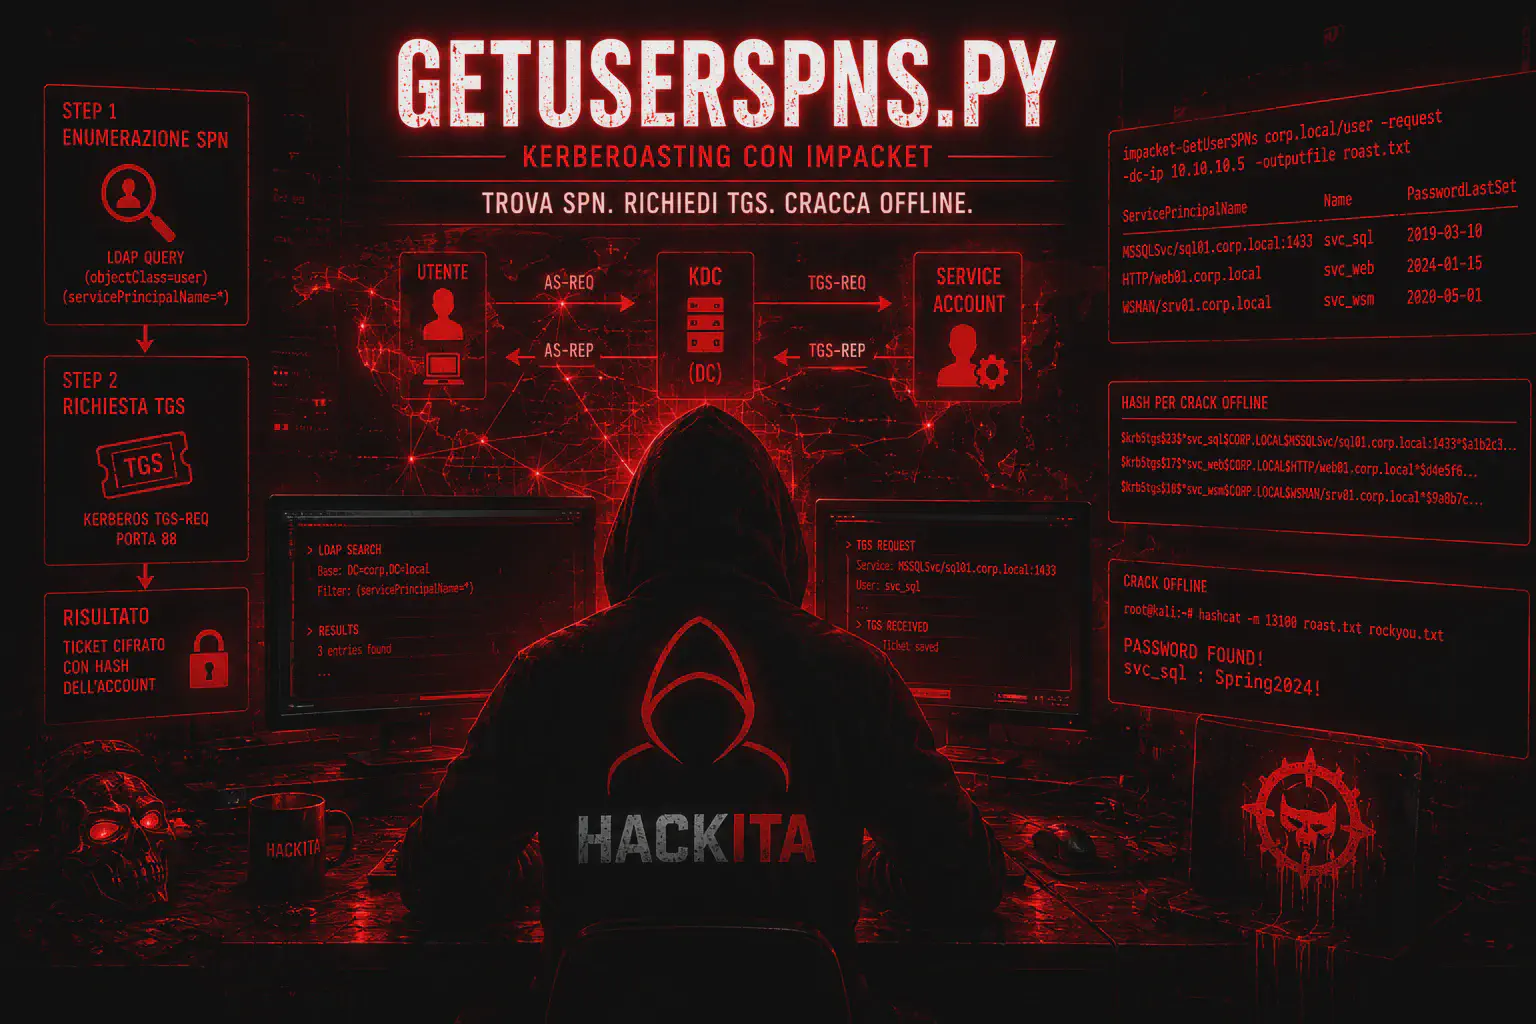 tools
GetUserSPNs.py: Kerberoasting and TGS with Impacket
How to use impacket-GetUserSPNs to enumerate accounts with SPNs and request Kerberos TGS with passwords, NTLM hashes, caches, or AES keys for Windows Active Directory
Discover more Discover more tools
addcomputer.py Impacket: Create Computer Account for RBCD
Impacket's addcomputer.py guide for creating Active Directory computer accounts via SAMR or LDAPS, verifying MachineAccountQuota, and using them in RBCD chains.
Discover more Discover more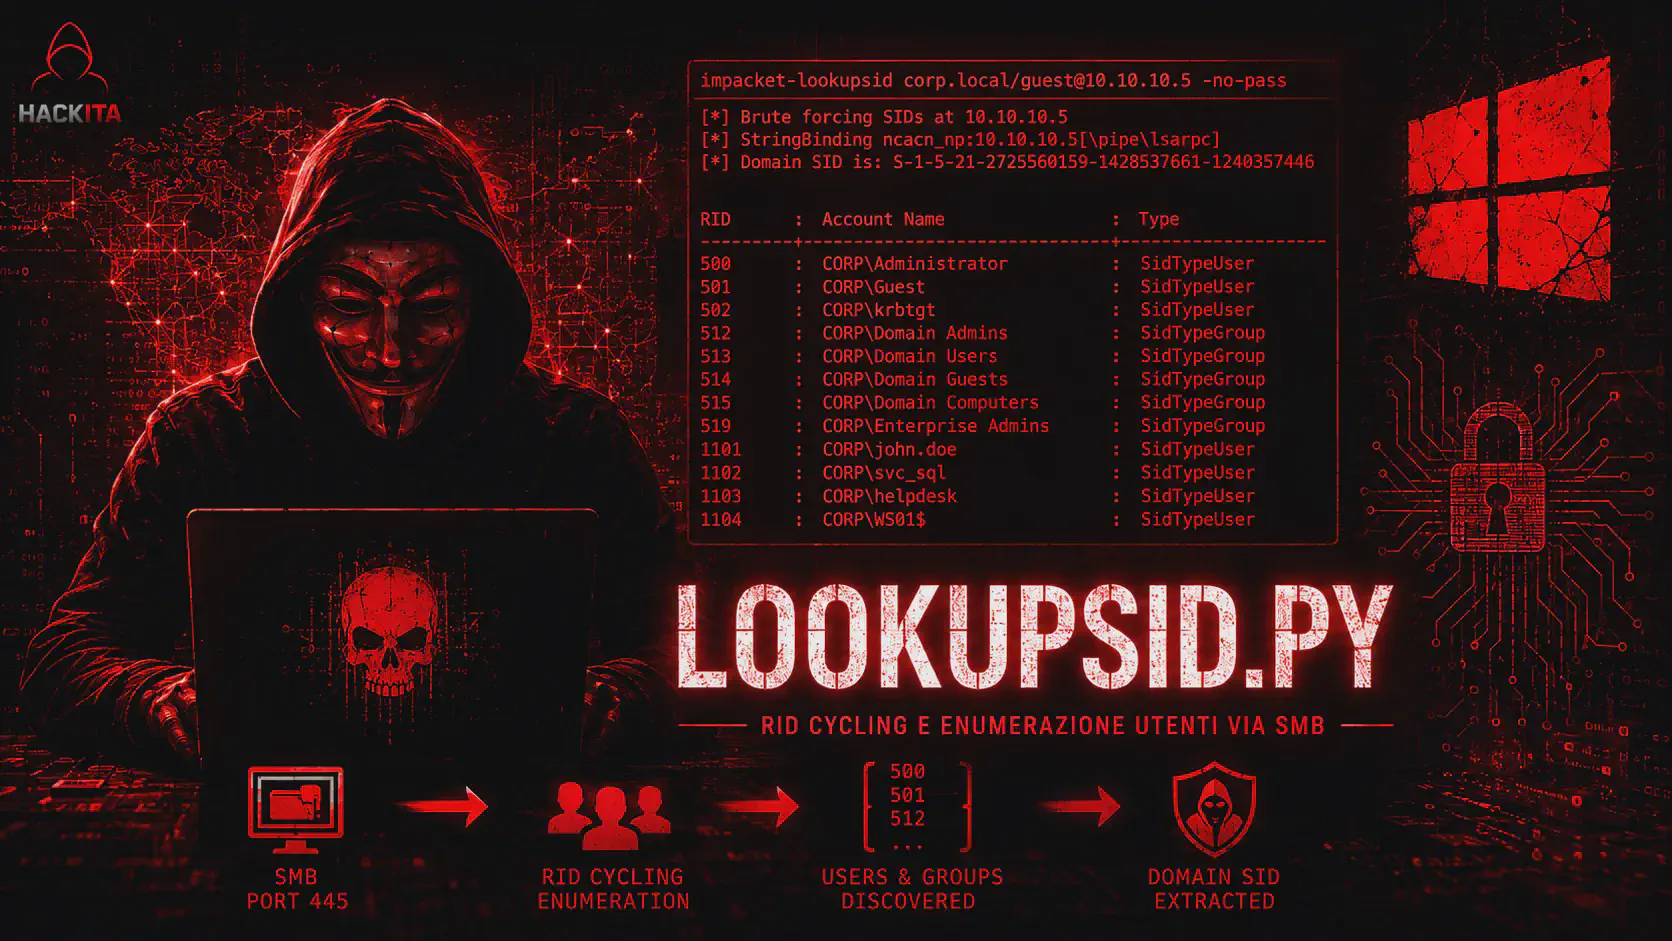 tools
lookupsid.py: Enumerate Users and SIDs via RID Cycling SMB
Guide to impacket-lookupsid to enumerate users, groups, and SIDs via MS-LSAT over SMB, using passwords, NTLM hashes, Kerberos, or anonymous sessions when allowed.
Discover more Discover more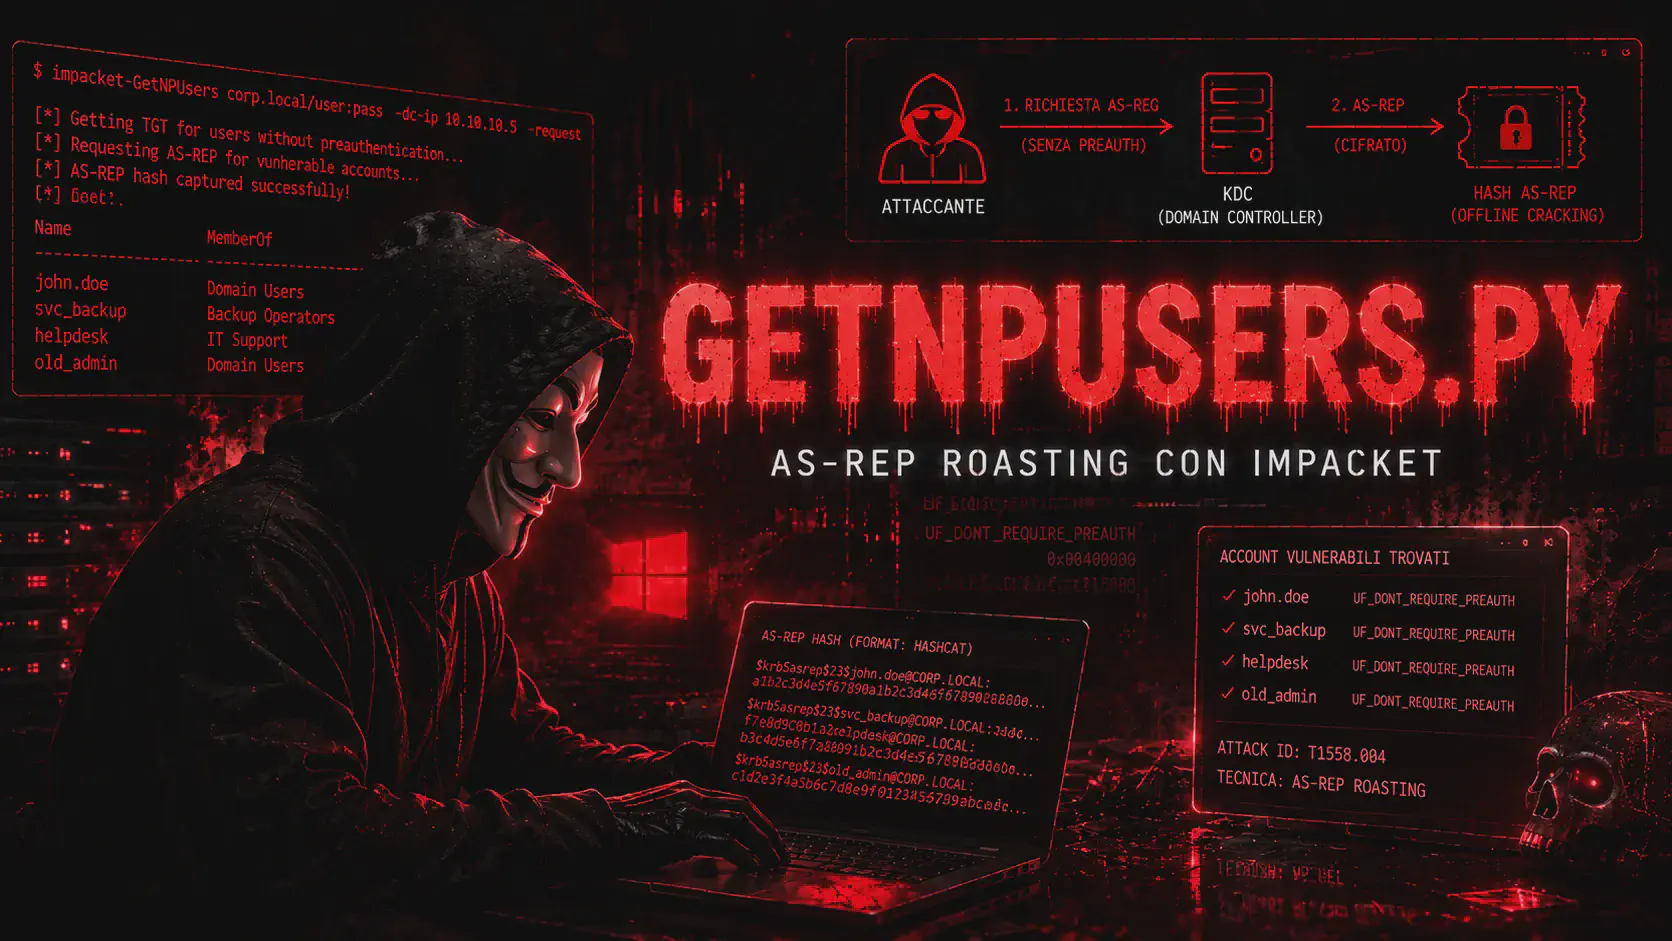 tools
GetNPUsers.py: AS-REP Roasting with Impacket
Impacket's GetNPUsers.py guide for finding accounts without Kerberos pre-authentication, extracting AS-REP hashes, and cracking them offline with Hashcat.
Discover more Discover more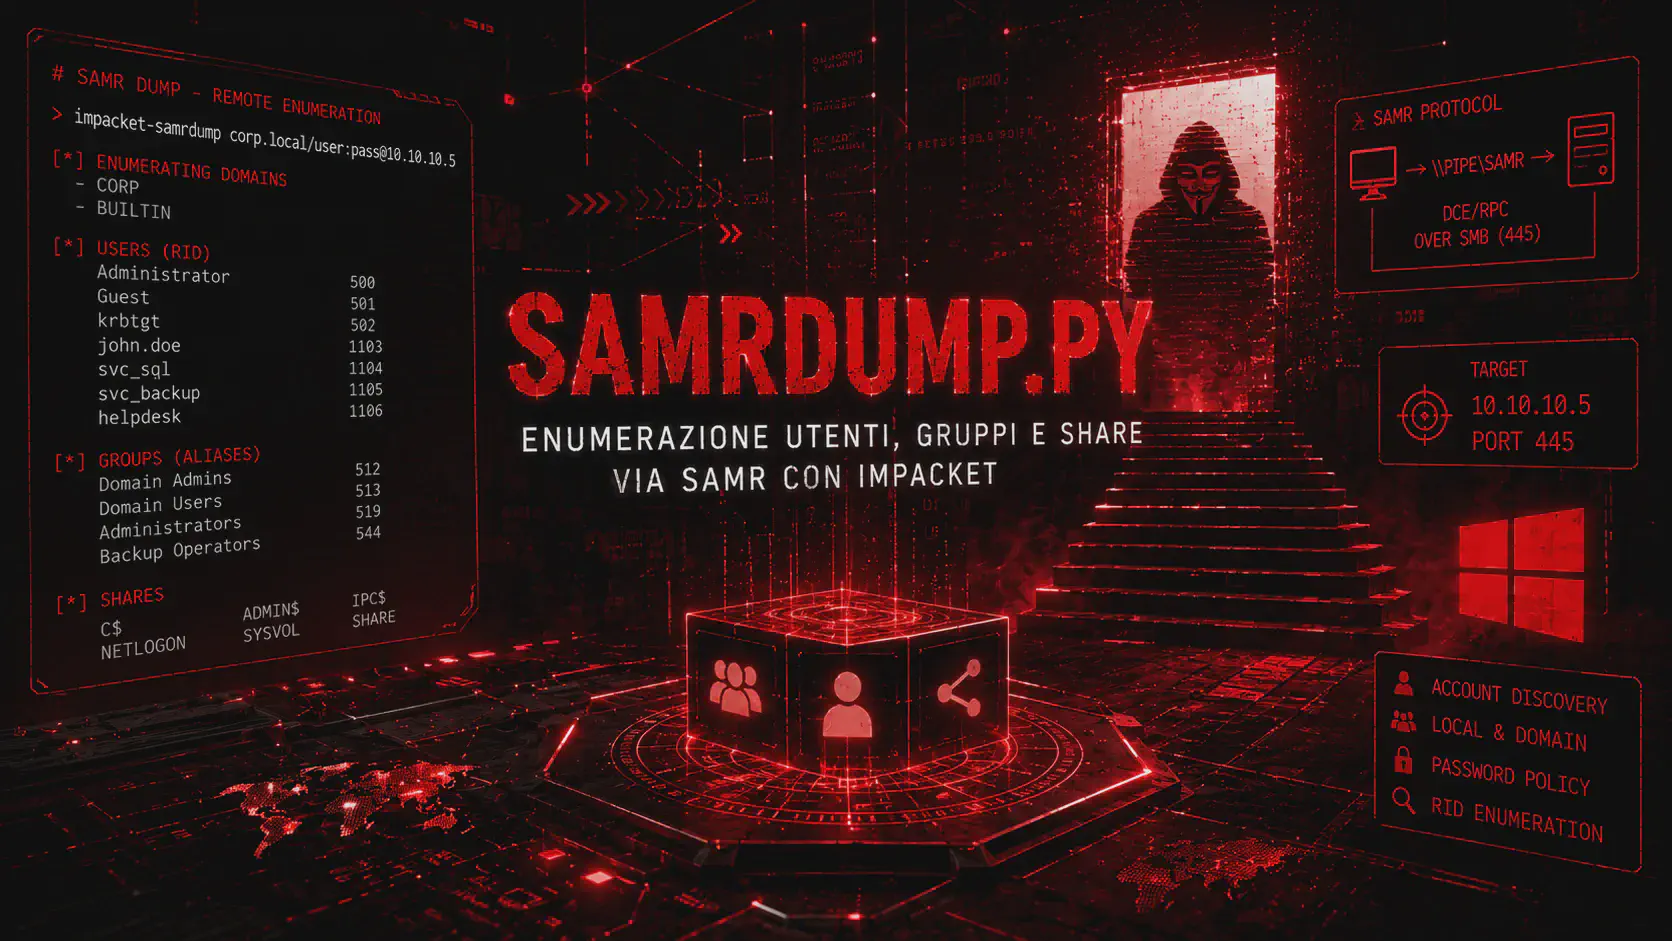 tools
samrdump.py Impacket: Enumerate Windows Users via SAMR
Impacket's samrdump.py guide to enumerate Windows users via MS-SAMR over SMB, get RID and account attributes with passwords, NTLM or Kerberos hashes.
Discover more Discover more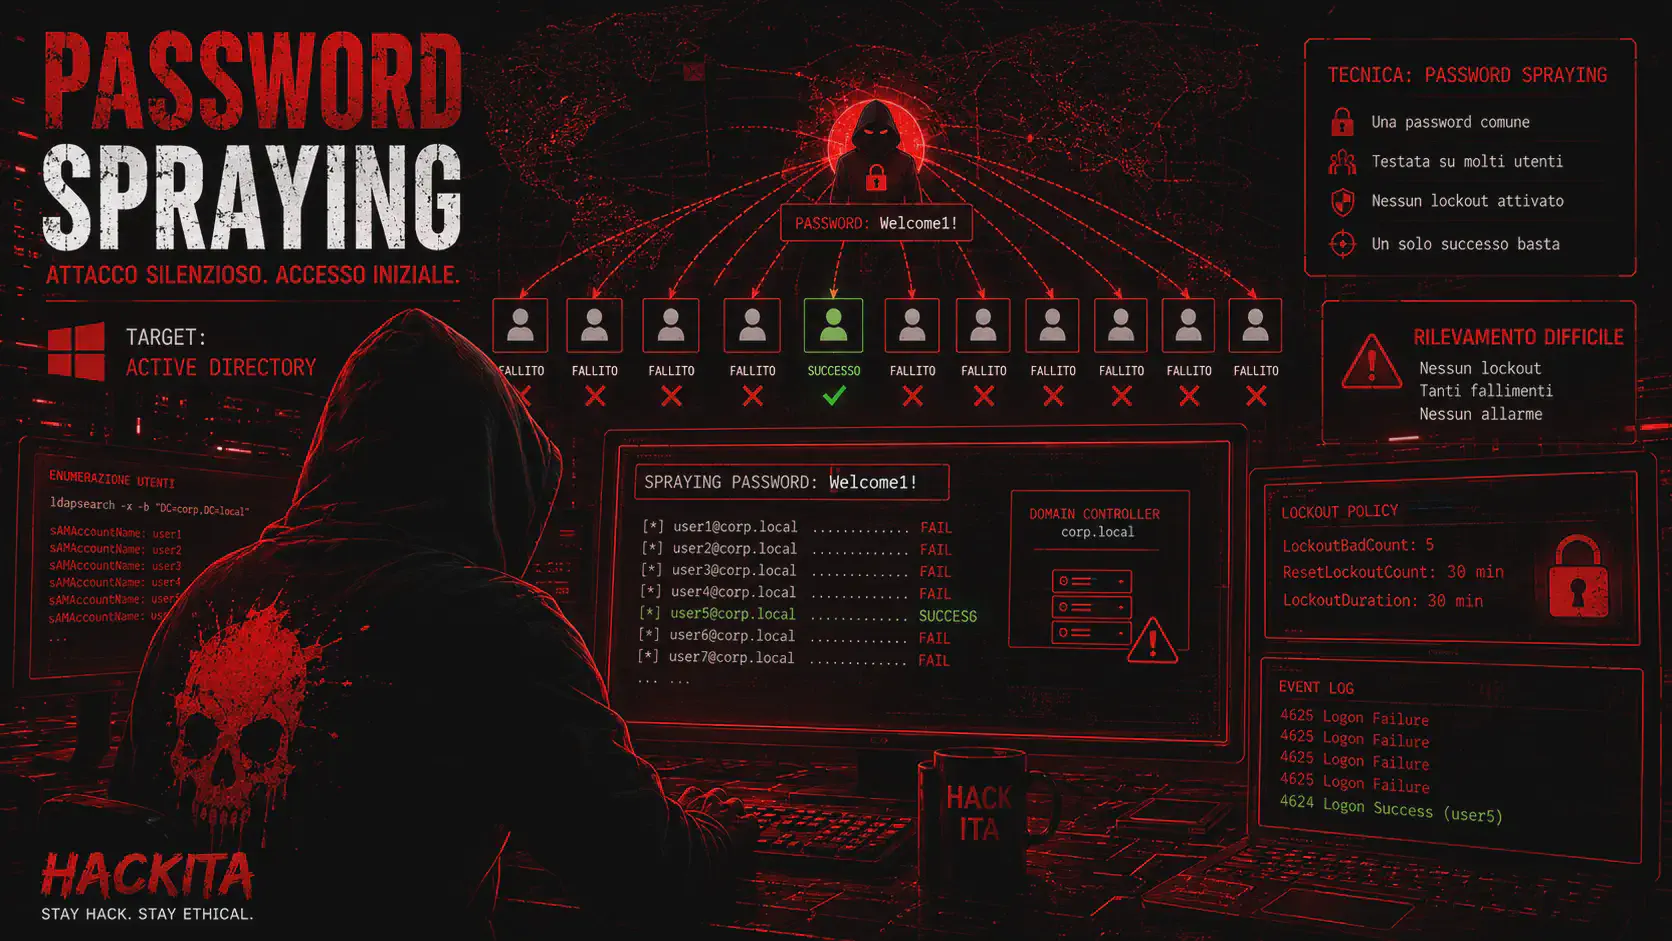 windows
Password Spraying: A Complete Guide to AD, AD FS, and Entra ID
Learn about Active Directory password spraying: techniques, authorized pentesting tools, detection, and defenses against weak password access.
Discover more Discover more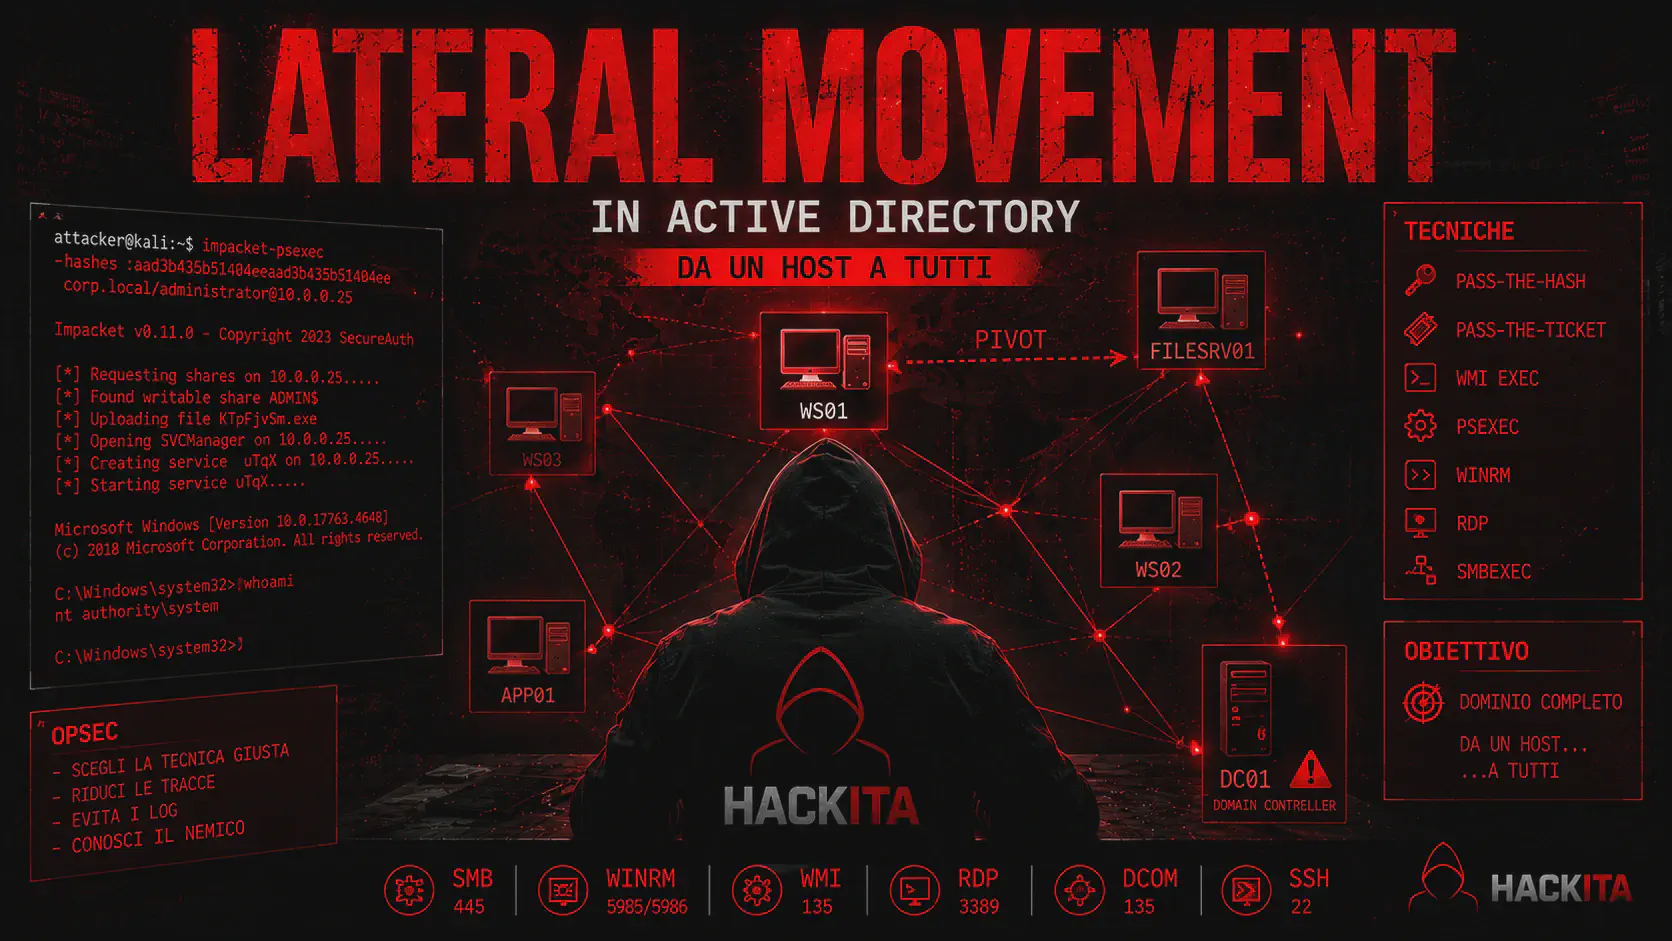 windows
Lateral Movement in Active Directory: Techniques, Tools and OPSEC
A guide to lateral movement in Active Directory: Pass-the-Hash, Kerberos, SMB, WMI, WinRM, and RDP with prerequisites, artifacts, detection, and mitigations.
Discover more Discover more walkthroughs
Voleur HTB: Writeup with Kerberoasting, DPAPI and WSL Privesc
Voleur's full walkthrough of Hack The Box: targeted Kerberoasting, AD Recycle Bin abuse, DPAPI chaining, and privilege escalation via WSL to Administrator.
Discover more Discover more windows
Golden Ticket Attack: What It Is, How It Works, and How to Defend Yourself in Active Directory
The Golden Ticket is the most dangerous attack on Active Directory. Learn how it works, how to forge a TGT with the krbtgt hash, how to detect it, and how to defend yourself with double reset. A complete guide.
Discover more Discover more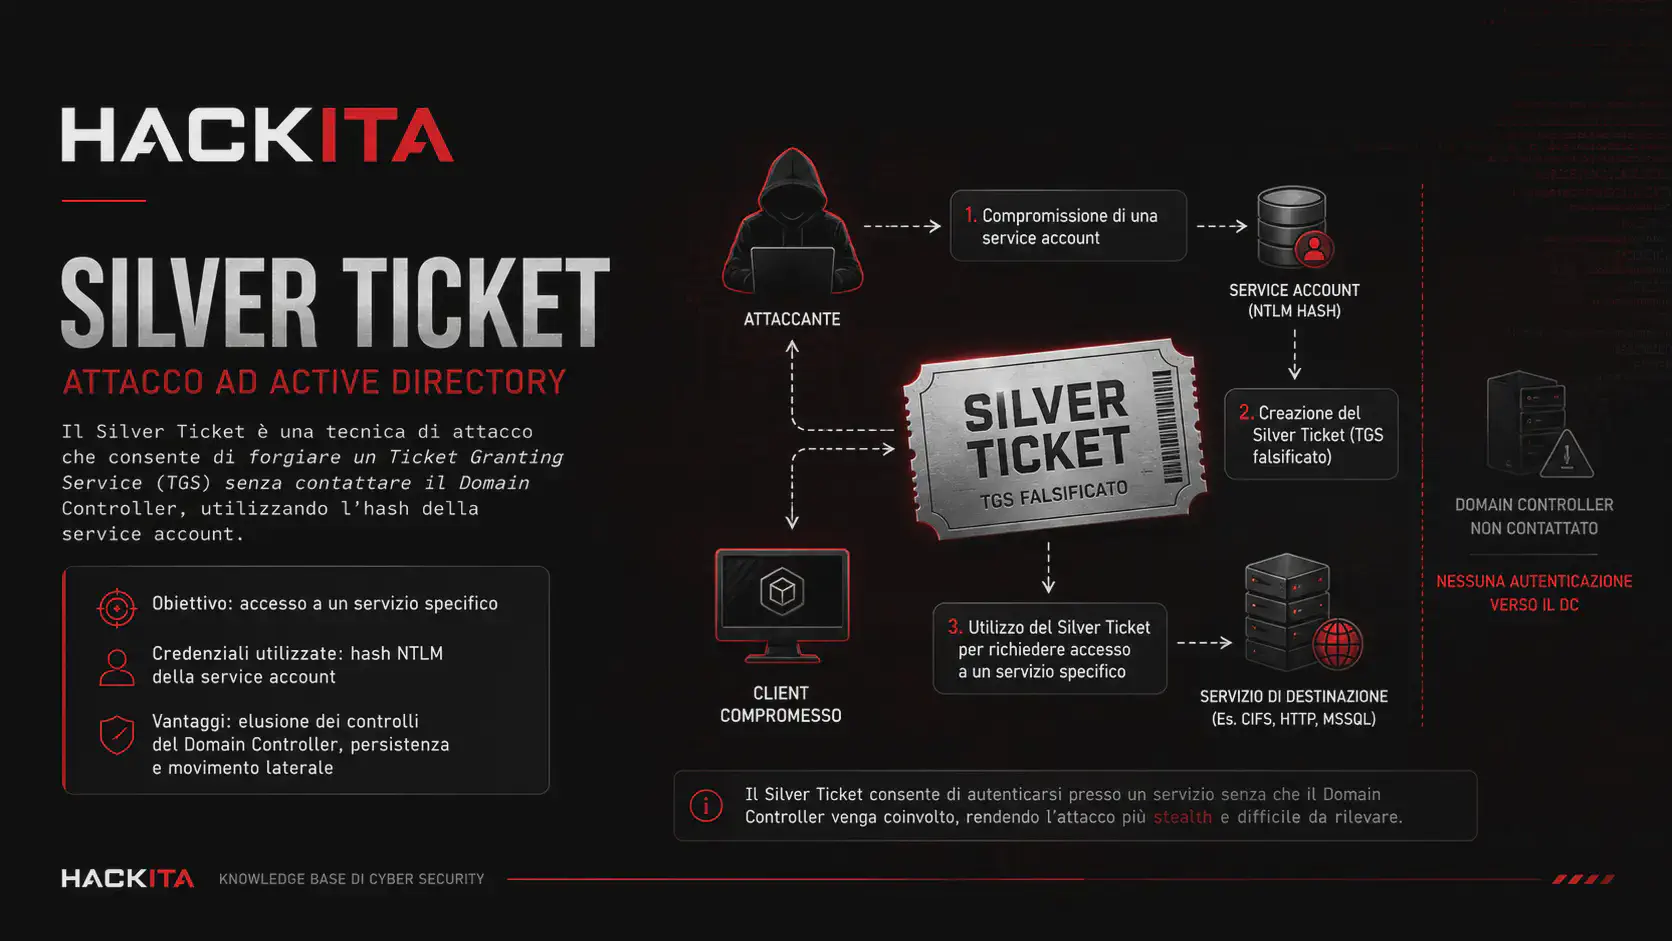 windows
Silver Ticket Attack: What It Is, How It Works, and How to Defend Yourself in AD
The Silver Ticket forges a Kerberos TGS using a service account hash, completely bypassing the KDC. A complete guide: how to obtain it, forge it with Mimikatz, Rubeus, and Impacket, scenarios for CIFS, LDAP, MSSQL, HTTP, and how to detect it.
Discover more Discover more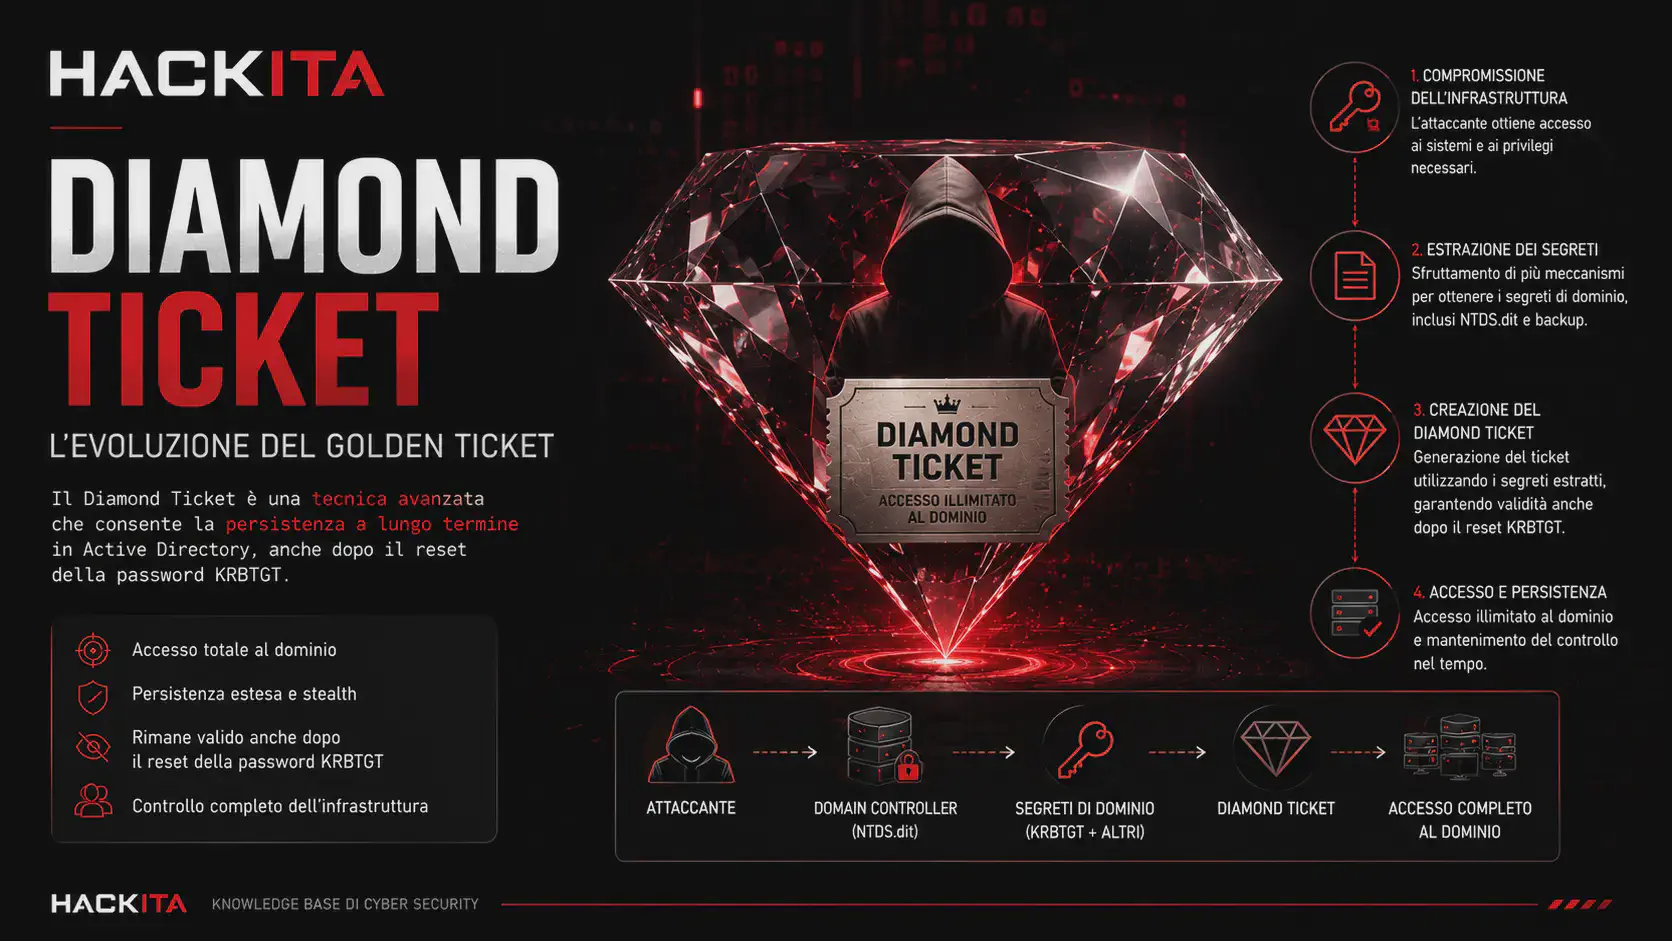 windows
Diamond Ticket Attack: The Stealth Evolution of the Golden Ticket
Diamond Ticket: A stealth variant of the Golden Ticket with a real TGT to bypass MDI. Rubeus /ldap /opsec guide, Impacket, detection, and KRBTGT reset.
Discover more Discover more windows
Logon Type Windows: Guide for Pentester, Red Teamer and SOC Analyst
Windows Logon Type: A practical guide to the 13 logon types, from Interactive to CachedUnlock. Real-world examples and relevance for penetration testing and security audits.
Discover more Discover more windows
EKU OID in ADCS: A Complete Guide to Active Directory Penetration Testing
All Active Directory certificate EKU OIDs explained from an offensive perspective: which ones to exploit in ESC1–ESC16, PKINIT attack flow, Event ID detection, FAQ and complete table with offensive relevance.
Discover more Discover more tools
Tool Penetration Testing: A Complete Guide to the Attack Phase"
All offensive penetration testing tools organized by attack phase: recon, exploitation, post-exploitation, pivoting, AD. With real attack chains for CTF, OSCP, OSEP, and red teams.
Discover more Discover more walkthroughs
HTB Sekhmet Walkthrough: Node.js Deserialization, WAF Bypass and DPAPI
HTB Sekhmet Insane,WriteUp Complete: insecure deserialization in node-serialize, bypass ModSecurity with Unicode encoding, ZipCrypto, Kerberos on Linux and DPAPI on Active Directory.
Discover more Discover more windows
SeBackupPrivilege: Hash dump and full domain with SAM, SYSTEM and NTDS.dit
PrivEsc with SeBackupPrivilege on Windows and Active Directory: SAM, SYSTEM, and SECURITY extraction, offline dump with secretsdump, access to NTDS.dit, and real-world impact on compromised domains.
Discover more Discover more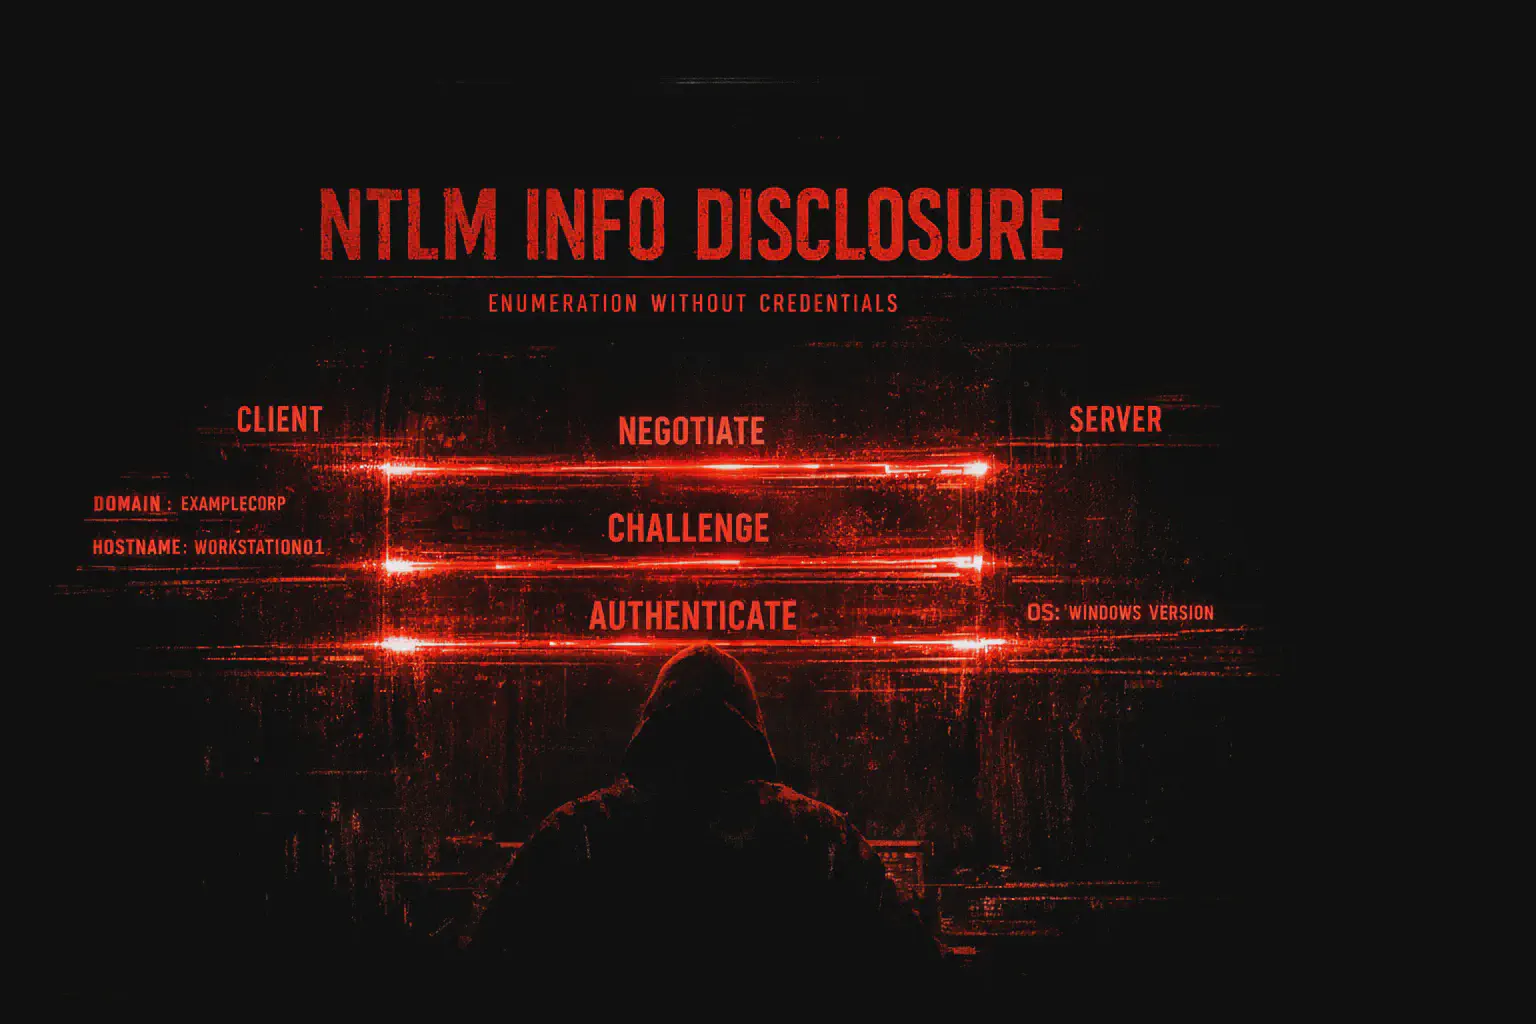 windows
NTLM Information Disclosure: Enumerate Domain, Hostname, and OS Without Credentials
NTLM authentication over HTTP reveals AD domain, NetBIOS name, hostname, and OS version with a single GET, without credentials. This is an essential recon technique for Exchange and IIS red teams. Learn curl, Nmap, Burp, and defenses.
Discover more Discover more networking
Port 50000 SAP NetWeaver: from SAP* Default to RCE on ERP Enterprise
SAP Management Console on 50000 without auth: Enumerate versions, exploit RECON (CVSS 10), abuse RFC with SAP*/06071992 and get OS command execution on all ERP data.
Discover more Discover more windows
ESC11 AD CS: NTLM Relay RPC, Certipy & Privilege Escalation
A CA vulnerable to ESC11 can accept NTLM relay via RPC. How to recognize the configuration, privesc, assess the impact on certificates, and prevent abuse.
Discover more Discover more windows
ESC13 AD CS: Privesc with Issuance Policy OID and Certipy
Privilege escalation in Active Directory via ESC13: Certipy detects Issuance Policy OIDs linked to AD groups and explains privilege abuse via Kerberos TGT.
Discover more Discover more windows
ESC14 AD CS: Privesc with altSecurityIdentities and Certipy
Privilege escalation in Active Directory: ESC14 exploits weak X.509 mappings in altSecurityIdentities to impersonate Windows accounts via certificates.
Discover more Discover more windows
ESC1 AD CS: Exploit and Privilege Escalation with Certipy
A practical guide to ESC1 in Active Directory: analyzing vulnerable templates with Certipy, Kerberos authentication, detection, privesc, and security mitigations.
Discover more Discover more windows
ESC2 AD CS: Any Purpose EKU, Enrollment Agent and Certipy
ESC2 in Active Directory Certificate Services: Windows privilege escalation with Any Purpose EKU template, exploits with Certipy and mitigations for secure AD CS.
Discover more Discover more windows
Kerberos Active Directory Attacks: Kerberoasting, AS-REP, Golden Ticket
Port 88 Kerberos: Complete guide to Active Directory penetration testing. Learn about Kerberoasting, AS-REP Roasting, Golden Ticket, Silver Ticket and Pass-the-Ticket for privilege escalation and lateral movement.
Discover more Discover more tools
Evil-WinRM: Remote Access and Post-Exploitation on Windows via WinRM
Evil-WinRM: Remote PowerShell shell via WinRM for Windows post-exploitation. Pass-the-hash, Kerberos ticket, AMSI bypass, in-memory execution .NET assembly for lateral movement enterprise.
Discover more Discover more tools
KeeThief: Master Key and Credential Dump from KeePass
KeeThief: How to extract master keys and credentials from KeePass during an authorized pentest. Memory dumps, .kdbx files, operational limitations, detection, and post-exploitation.
Discover more Discover more windows
LDAP Port 389: Enumeration and Pentesting in Active Directory
LDAP 389 PORT: Null bind, users, groups and SPNs, exposed credentials, LDAP relay and injection: enumeration techniques and misconfigurations in Active Directory.
Discover more Discover more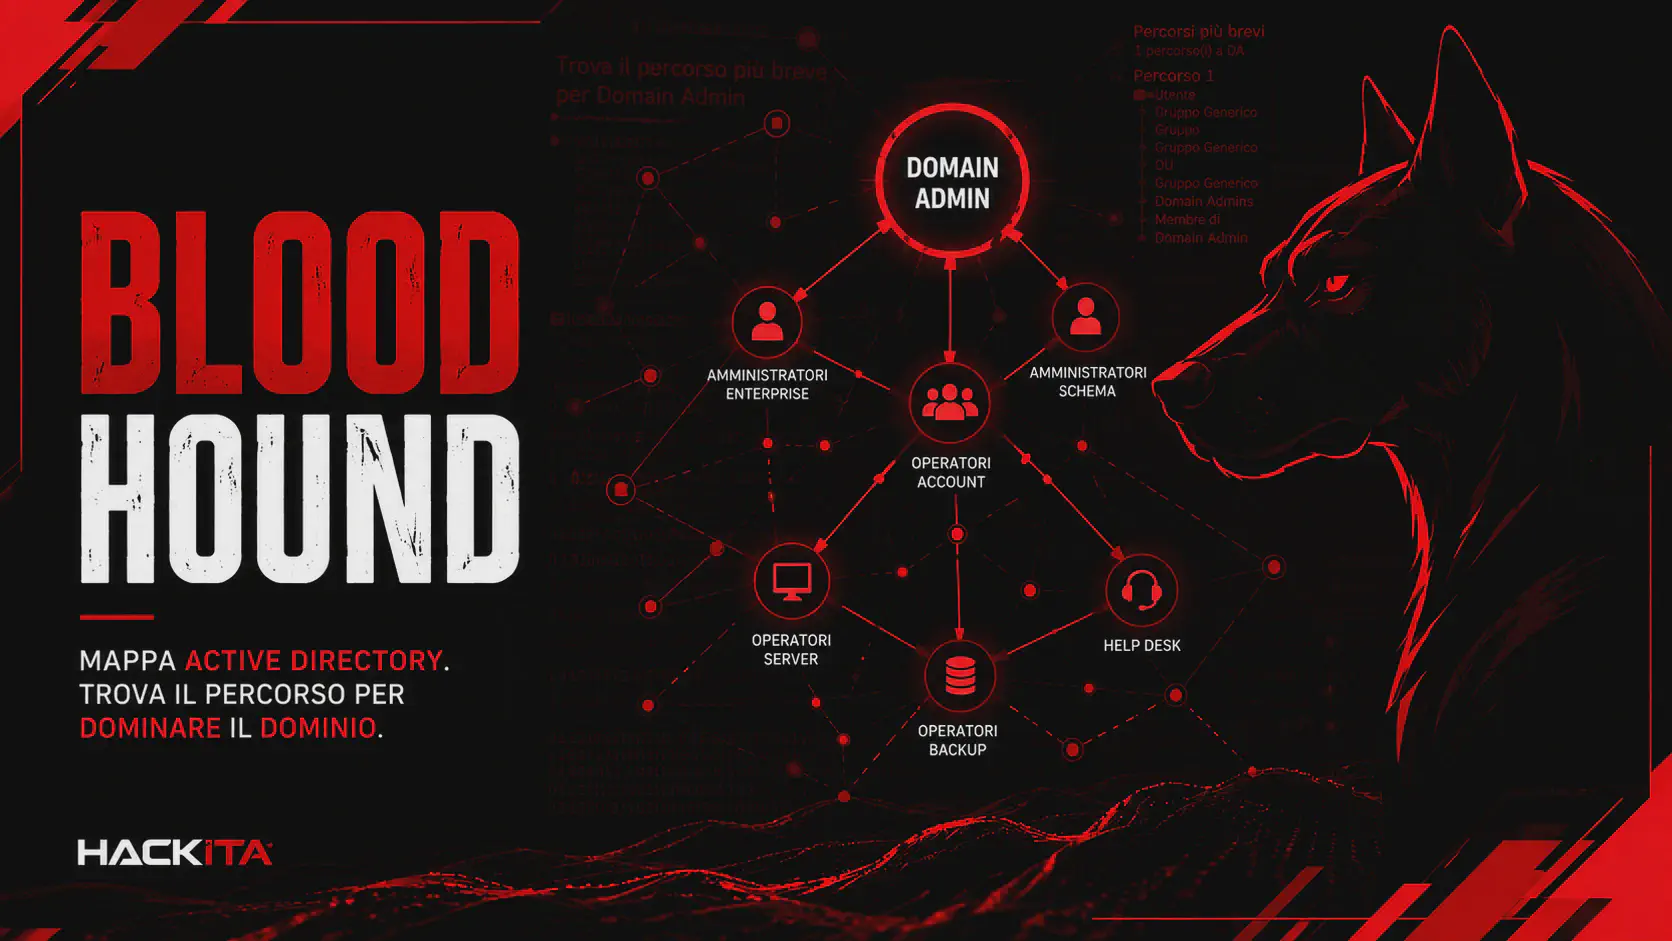 tools
BloodHound Pentest AD: Privilege Escalation and Domain Admin
BloodHound for privilege escalation on Active Directory: SharpHound, edge abuse, Shadow Credentials and ADCS. Italian guide to AD pentest towards Domain Admin.
Discover more Discover more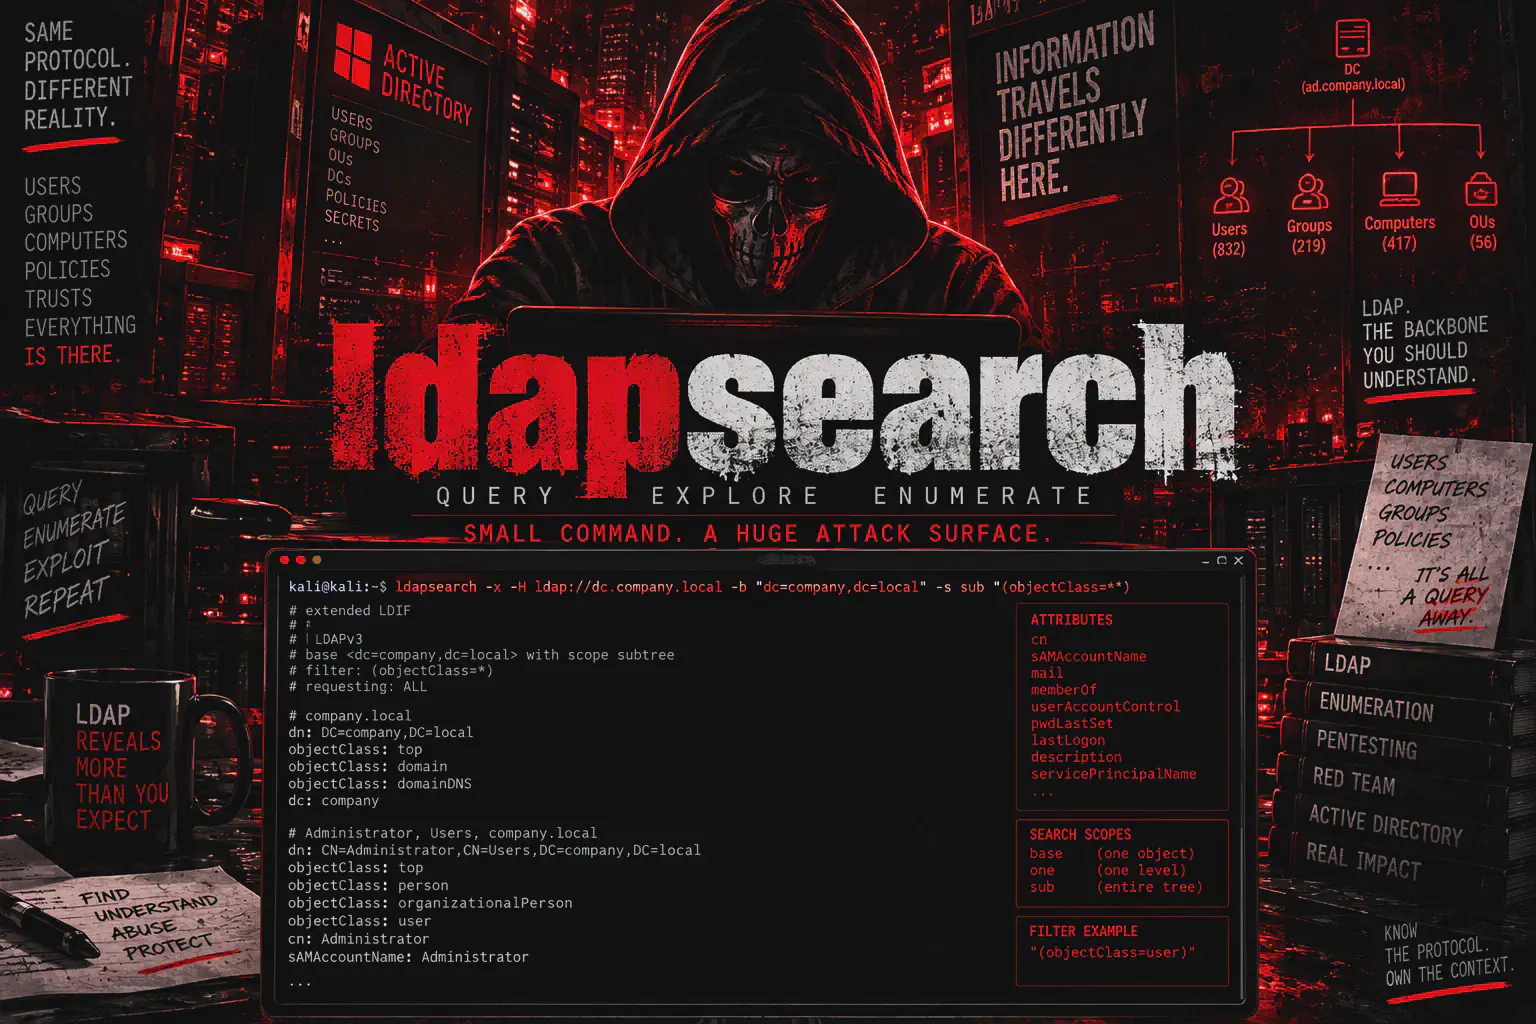 tools
ldapsearch: LDAP Commands to Enumerate Users, Groups and ADs
ldapsearch for pentest: RootDSE, Base DN, LDAP bindings, users, groups, computers, SPN, LDAPS and Active Directory enumeration troubleshooting and cheat sheets
Discover more Discover more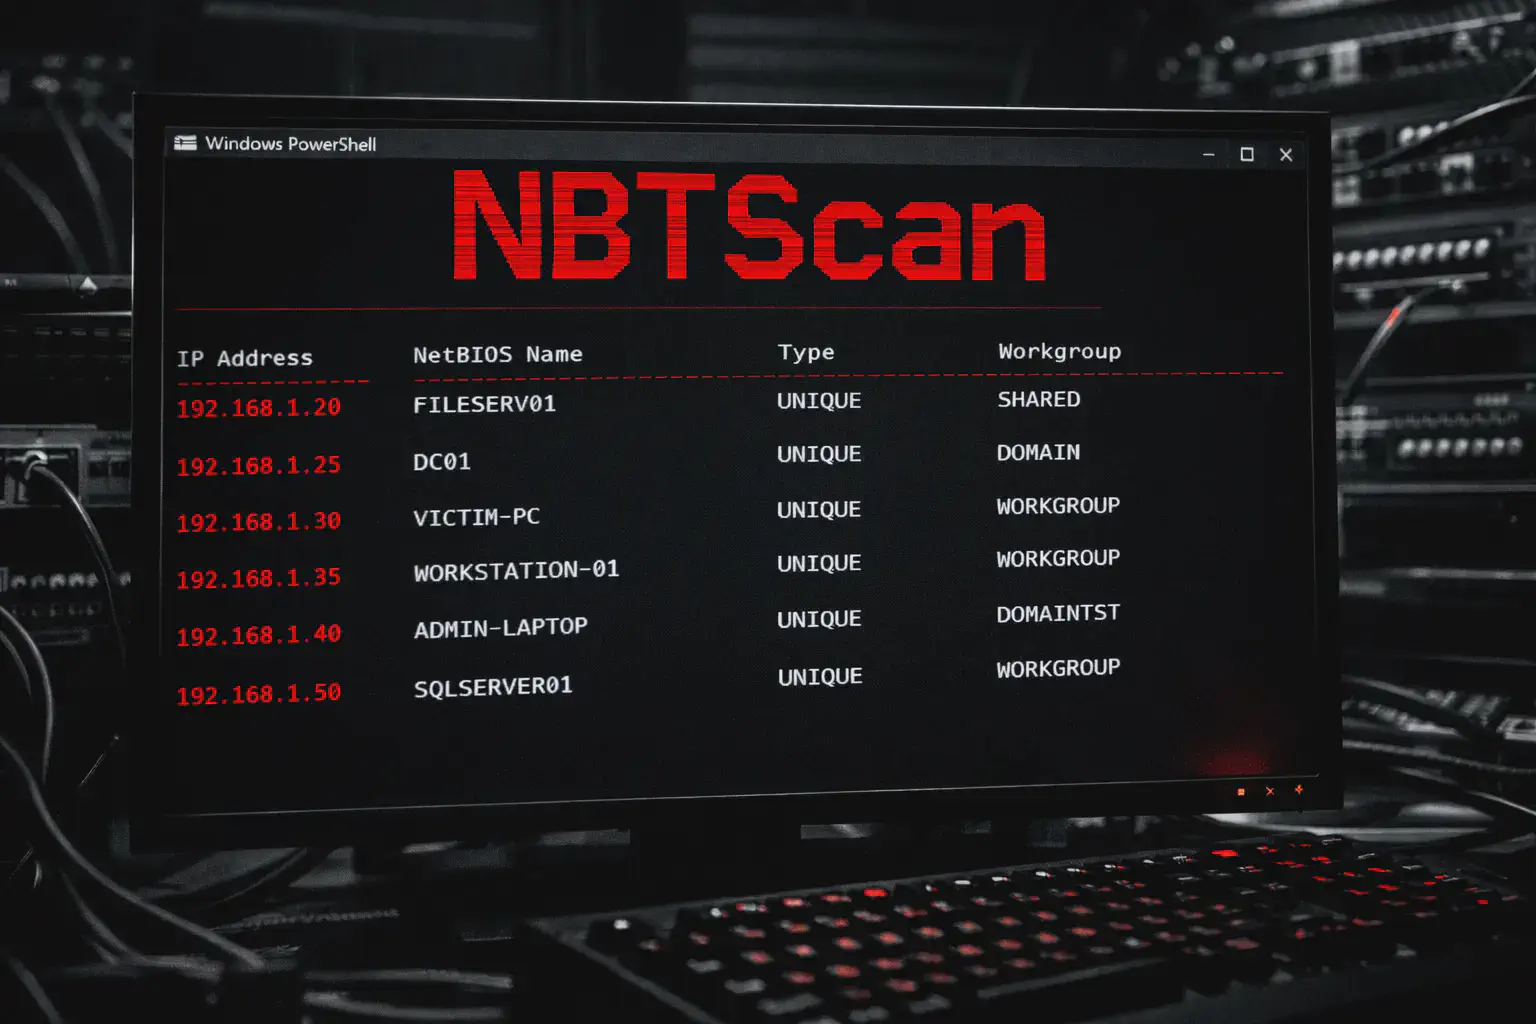 tools
NBTScan: NetBIOS Scanning on Linux for the Recon Windows
NBTScan on Linux: Learn how to scan Windows hosts, identify NetBIOS names, domains, workgroups, and useful information for network reconnaissance.
Discover more Discover more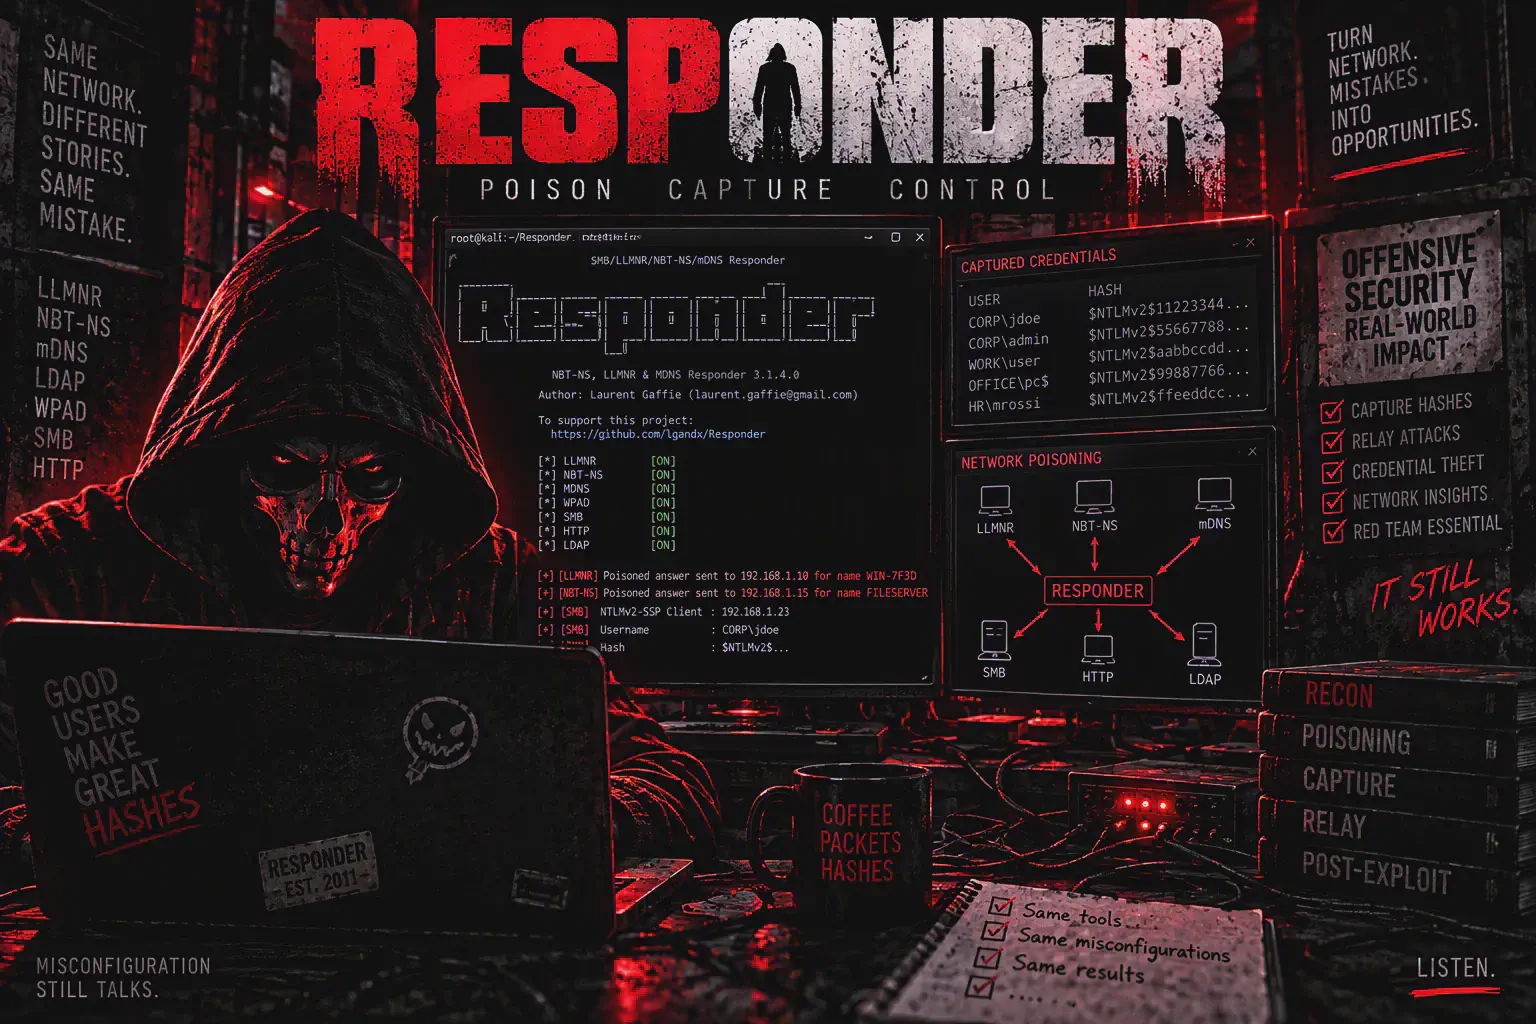 tools
Responder: Capture NTLM Hash on Linux, LLMNR, NBT-NS and Relay
Responder for Linux: How to capture NTLM/NetNTLMv2 hashes with LLMNR, NBT-NS, and WPAD, crack and relay NTLM in penetration tests and secure Windows labs
Discover more Discover more