
- blog
- 47+ Note
- Focus
- OSCP · Red Team
- Structure
- Recon → Exploit
Recon blog
Filters
 Recon & mapping
Web Hacking
Recon, fingerprinting, OWASP Top 10, and real-world exploit chains: everything you need to destroy lab-style web apps and exams.
Discover more Discover more web hacking
Recon OSINT: Tool, theHarvester, Shodan and Google Dorks.
Passive OSINT reconnaissance for pentesters: Collect emails, subdomains, exposed devices, and metadata with theHarvester, Google Dorks, Shodan, and Metagoofil.
Discover more Discover more web hacking
Subdomain Enumeration with subfinder, puredns and httpx
Subdomain enumeration pipeline: passive recon with subfinder, brute force with puredns, Alterx permutations, httpx validation and subdomain takeover check.
Discover more Discover more web hacking
Wfuzz: Web fuzzing of directories, parameters, headers, and VHosts
Wfuzz for web fuzzing: directory and parameter commands, VHost discovery, headers, cookies, filters, SecLists, encoders, and WAF bypass techniques.
Discover more Discover more web hacking
Recon Pipeline: OSINT Automation for Bug Bounty and Pentesting
Automated recon pipeline guide: subdomain enumeration, DNS, port scanning, fingerprinting, Nuclei, and secret scanning for bug bounty and pentesting.
Discover more Discover more web hacking
S3Scanner: Enumeration and Misconfiguration Detection on Amazon S3
S3Scanner: Enumeration and Misconfiguration Detection on Amazon S3
Discover more Discover more web hacking
Recon-ng: Modular OSINT Framework for Advanced Reconnaissance
Recon-ng is a modular OSINT framework with a Metasploit-like interface. Ideal for automated collection of domains, emails, and external assets.
Discover more Discover more web hacking
ReconSpider for Kali: Web Recon and Automated OSINT
ReconSpider is an OSINT tool for automating web reconnaissance and intelligence gathering on domains, IPs, emails, metadata, and other public sources.
Discover more Discover more web hacking
Nuclei: High-Speed Template-Based Vulnerability Scanner
Nuclei: High-Speed Template-Based Vulnerability Scanner
Discover more Discover more web hacking
Nikto: Web Server Vulnerability and Misconfiguration Scanner
Nikto is a web scanner for finding known vulnerabilities, sensitive files, misconfigurations, and outdated software on HTTP/HTTPS servers.
Discover more Discover more web hacking
Eyewitness: Visual Recon and Screenshot Automation for Large-Scale Web Triage
Eyewitness automates screenshots and analysis of web and RDP services. Rapid visual recon identifies admin panels and exposed attack surfaces.
Discover more Discover more web hacking
Feroxbuster: Fast and Recursive Directory Bruteforcing for Web Hacking
Feroxbuster is a high-performance directory and content discovery tool. It features recursive bruteforce, multi-threading, and proxy support for advanced web testing.
Discover more Discover more web hacking
FOCA: Metadata Extraction and OSINT on Documents for Information Gathering
FOCA is an OSINT tool for extracting metadata from public documents, mapping internal infrastructure, and identifying exposed users, servers, and paths.
Discover more Discover more web hacking
Gitrob: OSINT and Secret Discovery on GitHub Repository
Gitrob scans GitHub repositories to identify sensitive files and exposed credentials. A useful tool for reconnaissance and secret hunting.
Discover more Discover more web hacking
Amass: Advanced Subdomain Enumeration for Reconnaissance and Attack Surface Mapping
Amass is an OSINT and active reconnaissance tool for enumerating subdomains, mapping external assets, and analyzing DNS relationships. A practical guide to its use during attack surface discovery during a penetration test.
Discover more Discover more web hacking
Aquatone: Visual Recon and Automatic Screenshots for Subdomain Enumeration
Aquatone is a visual reconnaissance tool that automatically captures screenshots of hosts and subdomains discovered during the recon phase. It's ideal for quickly mapping web surfaces in penetration tests.
Discover more Discover more web hacking
Dirsearch: Directory and File Enumeration for Web Application Testing
Dirsearch is a tool for enumerating hidden directories and files on web applications using custom wordlists. A practical guide to its use during web reconnaissance during a penetration test.
Discover more Discover more web hacking
Gobuster: Directory, DNS and Virtual Host Bruteforcing for Web Enumeration
Gobuster is a fast tool for brute-forcing directories, DNS, and virtual hosts. A practical guide to using it for web enumeration during a penetration test.
Discover more Discover more tools
Maltego: What It Is and How to Use It for OSINT and Transform (2026)
How to Install Maltego for OSINT and Reconnaissance: Use Entity, Transform, Pivot, and Graph Analysis to Correlate Domains, IPs, Emails, People, and Infrastructure.
Discover more Discover more tools
Masscan: Ultra-Fast Port Scanner for Large-Scale Network Enumeration
Masscan is a high-speed port scanner capable of analyzing millions of IP addresses in minutes. A practical guide to its use during reconnaissance and infrastructure mapping during penetration testing.
Discover more Discover more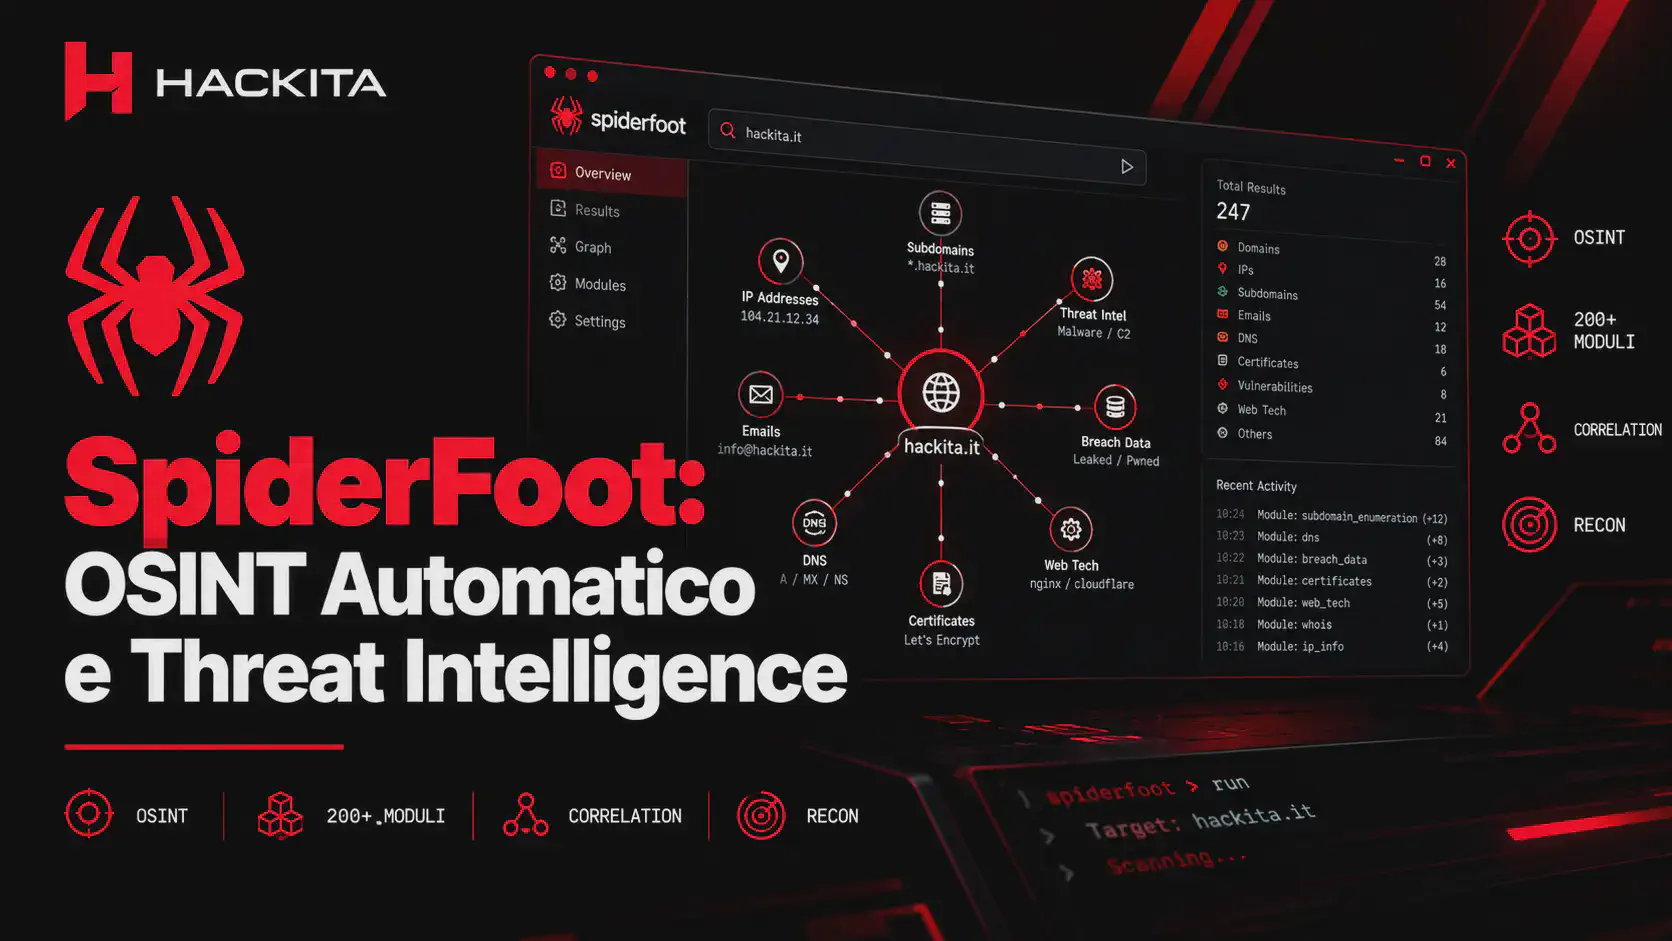 tools
SpiderFoot: OSINT Automation, Reconnaissance and Attack Surface
Discover SpiderFoot to automate OSINT and reconnaissance: modules, correlation, subdomain, IP, email, threat intelligence, and attack surface mapping.
Discover more Discover more web hacking
Burp Suite: Guide to Web Application Penetration Testing
Burp Suite: How to use it in web penetration testing: discover Proxy, Repeater, Intruder and Scanner and how to test SQLi, XSS, CSRF, API, authentication and secrets.
Discover more Discover more tools
FFUF: A Guide to Web Fuzzing for Directories, VHosts, and APIs (Pentesting and CTF)
FFUF is a fast Go web fuzzer for directory, vhost, and API testing. A practical guide with wordlists, filters, and pentest techniques.
Discover more Discover more tools
CrackMapExec vs. NetExec: CME Commands and Migration to NXC
CrackMapExec (cme) to NetExec (nxc) Migration Guide: Translate CME commands to NXC, manage Kerberos, forms, file transfer, and see what's changing today.
Discover more Discover more tools
ARP-Scan Kali Linux: ARP Scan and Host Discovery
ARP-Scan guide on Kali Linux to discover hosts on your local network: ARP scanning, IP, MAC, vendor, subnet, output, and network reconnaissance workflow.
Discover more Discover more tools
Netdiscover: Discover Hidden Devices and IPs on Your LAN
Netdiscover is an essential tool for identifying active devices on the local network. It's ideal for silent recon via ARP in environments without DNS or DHCP.
Discover more Discover more tools
Ping and ICMP Techniques and Active Scans for Recon
Analyze network behavior with ping, fping, and hping3. ICMP reconnaissance, host discovery, and firewall testing techniques used in pentests.
Discover more Discover more tools
Rpcinfo: Enumerating RPC Services in Unix Environments
Rpcinfo allows you to identify active RPC services on Unix/Linux hosts. It's essential for reconnaissance and analysis of potential remote attack vectors.
Discover more Discover more tools
Showmount: Discover exposed NFS shares on the network.
Showmount is the perfect tool for enumerating NFS shares. It's used in recons to identify accessible resources and entry points in Unix/Linux environments.
Discover more Discover more tools
SnmpCheck: Device and Service Enumeration via SNMP v1/v2
Snmp-check allows you to extract information from network devices using SNMP. Perfect for low-noise attacks, silent enumeration, and footprinting.
Discover more Discover more tools
Snmpwalk: Massive SNMP Enumeration on Exposed Networks
Snmpwalk is the ideal tool for querying SNMP agents and gathering detailed information about network devices. It's used for low-noise recon and targeted attacks.
Discover more Discover more tools
enum4linux-ng: SMB and Active Directory enumeration
Complete guide to enum4linux-ng for SMB and Active Directory enumeration: users, groups, shares, policies, SID/RID, authentication, and practical commands.
Discover more Discover more tools
NetExec (NXC): Complete Guide to CrackMapExec's Successor
Complete Operation Guide to NetExec (nxc): SMB, LDAP, WinRM, RDP, advanced modules, credential dumping, vulnerability scan and lateral movement in Active Directory
Discover more Discover more tools
Smbclient: Accessing and Attacking Windows Shares
With smbclient, you can access, read, and write files to SMB shares. Learn how to use it for pentesting, internal attacks, enumeration, and pivoting in AD.
Discover more Discover more tools
BloodHound Pentest AD: Privilege Escalation and Domain Admin
BloodHound for privilege escalation on Active Directory: SharpHound, edge abuse, Shadow Credentials and ADCS. Italian guide to AD pentest towards Domain Admin.
Discover more Discover more tools
ldapsearch: LDAP Commands to Enumerate Users, Groups and ADs
ldapsearch for pentest: RootDSE, Base DN, LDAP bindings, users, groups, computers, SPN, LDAPS and Active Directory enumeration troubleshooting and cheat sheets
Discover more Discover more tools
rpcclient Kali Linux: SMB, AD, and SID/RID Enumeration
Guide to rpcclient on Kali Linux to enumerate users, groups, SIDs/RIDs, trusts, password policies, and SMB shares via SAMR, LSARPC, and SRVSVC, with practical commands.
Discover more Discover more tools
Inveigh: LLMNR, NBNS, and WPAD to Capture NTLM Hashes
What is Inveigh and how does it work? A guide to LLMNR, NBNS, and WPAD for capturing NetNTLM in Windows labs, using PowerShell, relay, troubleshooting, and detection.
Discover more Discover more tools
Mitmproxy: Intercept and Analyze HTTP/HTTPS Traffic
A practical guide to mitmproxy: configure the proxy, intercept HTTPS, install the CA, filter and modify flows, save sessions, and troubleshoot common issues.
Discover more Discover more tools
NBTScan: NetBIOS Scanning on Linux for the Recon Windows
NBTScan on Linux: Learn how to scan Windows hosts, identify NetBIOS names, domains, workgroups, and useful information for network reconnaissance.
Discover more Discover more tools
Netcat (nc): Commands, Port Scanning, and File Transfer
Learn how to use Netcat (nc) on Linux and Windows: practical commands, TCP/UDP listeners, port scanning, banner grabbing, file transfer, and reverse shell.
Discover more Discover more tools
Responder: Capture NTLM Hash on Linux, LLMNR, NBT-NS and Relay
Responder for Linux: How to capture NTLM/NetNTLMv2 hashes with LLMNR, NBT-NS, and WPAD, crack and relay NTLM in penetration tests and secure Windows labs
Discover more Discover more tools
Bettercap: What It Is, MITM, ARP Spoofing, and Sniffing on Kali Linux
What is Bettercap and how does it work? Discover the framework for network hacking and MITM: tutorials on Kali Linux, ARP spoofing, sniffing, network recon, PCAP, and proxies.
Discover more Discover more tools
Ettercap: MITM Tutorial, ARP Spoofing and Sniffing on Kali Linux
What is Ettercap and how does it work? A practical guide to MITM, ARP spoofing, and sniffing on Kali Linux, including installation, filters, packet capture, and commands.
Discover more Discover more tools
Tcpdump: Network Traffic Sniffing and Analysis Tutorial
What is tcpdump and how does it work? A guide to terminal network sniffing with packet capture, BPF filters, PCAP analysis, and pentesting commands.
Discover more Discover more tools
TShark: Network Traffic Sniffing and Analysis Tutorial
What is TShark and how is it used? A guide to terminal network sniffing with packet capture, filters, PCAP analysis, statistics, and pentesting commands.
Discover more Discover more tools
Wireshark for Pentesting: Filters, NTLM, DNS and TCP Stream
Wireshark for ethical hacking: advanced filters, NTLM, DNS, and TCP Stream. Learn how to isolate traffic, read sessions, and find useful indicators in labs and HTBs.
Discover more Discover more