
- blog
- 48+ Note
- Focus
- OSCP · Red Team
- Structure
- Recon → Exploit
Expoit blog
Filters
 web hacking
SQL Injection MySQL: Payload, Cheat Sheet and Techniques
SQL injection on MySQL: cheat sheet with UNION payloads, error-based, blind, time-based, DIOS, RCE via UDF, OOB, WAF bypass and sqlmap commands for pentesting.
Discover more Discover more web hacking
Command Injection: Payload, Bypass and How to Defend Yourself
Learn what Command Injection is, how it works, where it is found, and how to test for it with Burp Suite and Commix: blind techniques, OOB, filter bypass, and defense.
Discover more Discover more tools
JTAG: What It Is, How It Works, and How to Use It in Hardware Pentesting
What is JTAG and how does it work? Learn about pins, JTAGulator, OpenOCD, firmware dumps, and the risks of an exposed JTAG interface in hardware pentesting.
Discover more Discover more web hacking
OAuth 2.0: Tokens, Scope, and Risks of Third-Party Tools | HackITA
How OAuth 2.0 works, what scope and access tokens are, and how to protect your company's social media accounts from token theft in third-party tools.
Discover more Discover more web hacking
SVG XSS and XXE: Attack via Image Upload
An uploaded SVG can execute scripts or read local files. A practical guide to XSS and XXE via SVG: real-world payloads, attack vectors, and mitigations for developers.
Discover more Discover more web hacking
RCE (Remote Code Execution): What it is, Vectors and Exploits
RCE in pentesting: Learn the vectors that lead to Remote Code Execution, how to verify them, get a shell, and initiate post-exploitation.
Discover more Discover more web hacking
XXE Injection (XML External Entity): file read, SSRF and RCE
XXE (XML External Entity) in pentesting: payload for file read, SSRF, Blind XXE OOB and RCE, testing with Burp Suite and Nuclei, prevention in XML parsers.
Discover more Discover more web hacking
Advanced XXE Injection: XML parser, XInclude, SOAP and bypass
Advanced XXE Injection: Identifies XML parsers, compares Java, PHP, Python, and .NET, tests SOAP, XInclude, content-type switching, and targeted bypasses.
Discover more Discover more tools
XSSer: XSS Scanner, Payload, Fuzzing and WAF Bypass
Practical guide to XSSer for testing XSS vulnerabilities: installation, GET/POST scanning, payload, fuzzing, encoding, WAF bypass and results reporting.
Discover more Discover more web hacking
Injection Attack: A Complete Guide to Web Injections
A complete guide to injection attacks: SQL injection, command injection, SSTI, XXE, LDAP, NoSQL, and other techniques, with examples, testing, and prevention.
Discover more Discover more web hacking
Password Reset Attack: Techniques, Exploits and Account Takeover
Password Reset Attack Guide: Host header poisoning, weak tokens, race conditions, leaks, and practical account takeover techniques for web pentests.
Discover more Discover more web hacking
Web Cache Poisoning: Testing, Cache Keys, and Bypass Techniques
Practical guide to Web Cache Poisoning in pentesting: analyze cache keys and unkeyed inputs, test headers and fat GETs with Burp, and apply useful detection and mitigations.
Discover more Discover more tools
renameMachine.py: NoPac and sAMAccountName Spoofing
Guide to impacket-renameMachine to change the sAMAccountName of account computers and understand the NoPac chain with CVE-2021-42278 and CVE-2021-42287.
Discover more Discover more tools
GetUserSPNs.py: Kerberoasting and TGS with Impacket
How to use impacket-GetUserSPNs to enumerate accounts with SPNs and request Kerberos TGS with passwords, NTLM hashes, caches, or AES keys for Windows Active Directory
Discover more Discover more tools
addcomputer.py Impacket: Create Computer Account for RBCD
Impacket's addcomputer.py guide for creating Active Directory computer accounts via SAMR or LDAPS, verifying MachineAccountQuota, and using them in RBCD chains.
Discover more Discover more tools
GetNPUsers.py: AS-REP Roasting with Impacket
Impacket's GetNPUsers.py guide for finding accounts without Kerberos pre-authentication, extracting AS-REP hashes, and cracking them offline with Hashcat.
Discover more Discover more tools
getST.py Impacket: S4U, RBCD and Constrained Delegation
Impacket's getST.py guide for obtaining Kerberos Service Tickets with S4U2Self, S4U2Proxy, RBCD, and constrained delegation. Payload and errors for AD pentests.
Discover more Discover more web hacking
Twig SSTI and Sandbox Bypass: RCE in Twig, CMS and PHP Filters
Twig SSTI ,detection, payload and RCE: fingerprint vs Jinja2, payload for Twig 2.x and 3.x, filter/map/reduce bypass, sandbox escape, Drupal/Craft CMS and mitigations
Discover more Discover more web hacking
SQL Injection MSSQL: UNION, Blind, Stacked, RCE, Payload
Pentest SQL Injection MSSQL: identify quotes, exploit UNION/blind/time-based/stacked/error-based, bypass WAF, RCE via xp_cmdshell, NTLM hash, linked server.
Discover more Discover more web hacking
2FA Bypass: Techniques, Payloads, and OTP Attacks for Pentesters
2FA bypass: response manipulation, OTP brute force, direct post-login link, SIM swapping, MFA phishing, backup code abuse. Payload for ethical pentesters and hackers
Discover more Discover more tools
Certipy: A Complete Guide to AD CS Enumeration and Abuse
Complete guide to Certipy 5.1 to enumerate AD CS, locate ESC1-ESC17, request certificates, use PKINIT, relay, Shadow Credentials and Golden Certificate.
Discover more Discover more web hacking
Deserialization Attack: What It Is, How to Find It, and How It Leads to RCE
Deserialization attack explained from the beginning: what serialization is, why it's dangerous, and how to exploit it in PHP, Java, Python, and .NET with ysoserial and phpggc. A step-by-step guide for beginners and pentesters.
Discover more Discover more web hacking
Evilginx 3: AiTM Phishing and MFA Bypass for Red Teams
Learn how Evilginx 3 enables AiTM phishing, captures post-MFA cookies, and helps red teams understand MFA-bypass risks in Microsoft 365.
Discover more Discover more web hacking
Account Takeover: Offensive Techniques for Pentesters (2026)
Learn Account Takeover (ATO) techniques for pentesters and red teams. Discover how to bypass MFA, steal tokens, and compromise accounts. Complete guide 2026.
Discover more Discover more web hacking
IDOR: What It Is, How to Find It, and How to Use It — A Complete Guide
IDOR (Insecure Direct Object Reference) explained from a pentester's perspective: how to identify it, how to enumerate it, and how to scale it to account takeovers and data breaches. With real-world examples and a practical checklist.
Discover more Discover more web hacking
Injection Attack: A Complete Guide to All Types of Injection
A complete guide to injection attacks: SQL injection, command injection, LDAP, XPath, SSTI, XXE, CRLF, log injection, EL, NoSQL, and GraphQL. What injection is, how it works, how to find it, and how to exploit it. A hub with links to all the specific guides.
Discover more Discover more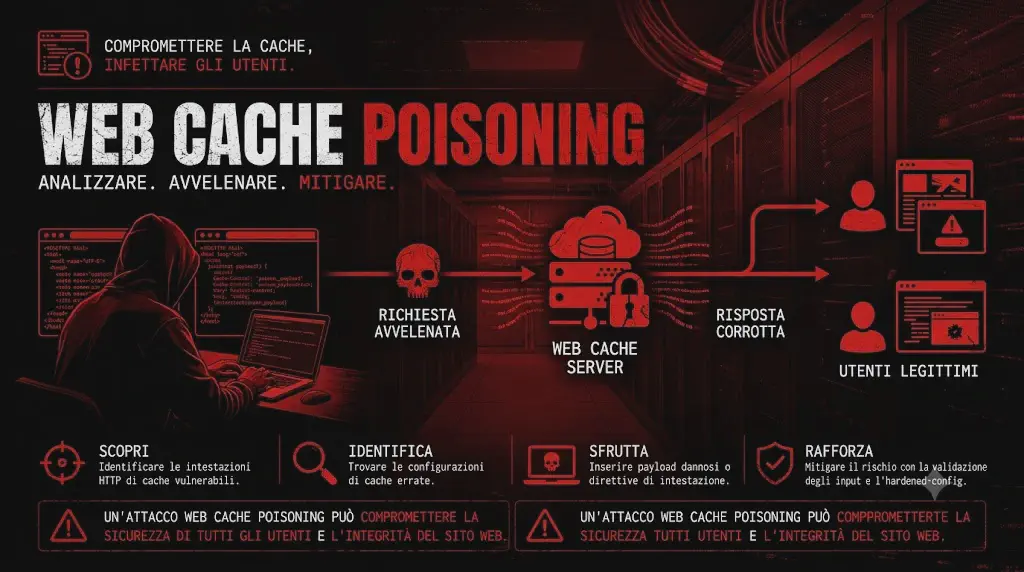 web hacking
Web Cache Poisoning: What It Is, How It Works, and How to Exploit It
A complete guide to web cache poisoning: discover what it is, how cache poisoning works, exploitation techniques (unkeyed inputs, CPDoS), and how to turn it into account takeover. Practical and CDN-specific examples.
Discover more Discover more tools
Certify: Enumerate and Abuse AD CS from Windows with C#
Certify is GhostPack's C# tool for enumerating and exploiting AD CS from Windows without Python dependencies. Learn how to use it to find vulnerable templates and request certificates for escalation to Domain Admin.
Discover more Discover more web hacking
SQL Injection on REST API and GraphQL: JSON Body, Header Injection and SQLMap (2026 Guide)
SQL Injection on REST API: JSON body injection, GraphQL SQLi, header injection and WAF bypass. Practical guide with SQLMap, API fuzzing and real exploitation.
Discover more Discover more web hacking
SQL Injection on ORM: Django, Laravel, Hibernate and Sequelize
SQL Injection on ORM: Vulnerabilities in Django, Laravel, Hibernate, and Sequelize. Raw queries, extra(), orderByRaw, and real-world exploitation with practical examples.
Discover more Discover more web hacking
Phishing: Techniques, Types, and Defenses in 2026
Phishing explained technically: spear phishing, credential harvesting, OAuth phishing, MFA bypass, and practical defenses for businesses and users.
Discover more Discover more tools
Social-Engineer Toolkit (SET): A Complete Guide to Social Engineering Attacks
SET is a framework for simulating social engineering in authorized environments: phishing, credential harvester, and client-side attacks.
Discover more Discover more tools
RouterSploit: Exploit Framework for Routers and IoT
RouterSploit is a framework for testing vulnerabilities on routers and IoT devices. It includes scanning, exploit, and brute-force modules.
Discover more Discover more tools
Patator: A Modular Brute-Force Authentication Testing Framework
Patator: A Modular Brute-Force Authentication Testing Framework
Discover more Discover more tools
MSFvenom Cheat Sheet: Commands, Payload, Shellcode & Bypass
MSFvenom exploit for lab and pentest: syntax, staged and stageless payload, EXE, ELF, PHP, WAR and MSI formats, shellcode with bad characters, handler and detection.
Discover more Discover more tools
Medusa: High-Speed Login Brute-Force Tool for Network Services
Medusa is a parallel tool for brute-forcing authentication over SSH, FTP, SMB, HTTP, and other services. Fast, scalable, and ideal for authorized password auditing.
Discover more Discover more tools
Metasploit Framework: Complete Guide to Exploits and Payloads
Metasploit Framework is the most widely used penetration testing platform for exploits, payloads, and post-exploitation. A complete offensive workflow guide.
Discover more Discover more tools
Hydra: Brute Force Login for Network Services
Hydra is a brute force tool for testing credentials over SSH, FTP, RDP, HTTP, and other services during authorized penetration tests.
Discover more Discover more tools
Impacket: Python Toolkit for SMB, Kerberos and Active Directory Attacks
Impacket is a Python suite for interacting with network protocols (SMB, LDAP, Kerberos, RPC) and conducting AD attacks such as DCSync and Pass-the-Hash.
Discover more Discover more tools
Invoke-Manipulation: PowerShell Obfuscation for Evasion AV
Invoke-Manipulation is a PowerShell module for obfuscating scripts and bypassing static checks during authorized red team operations.
Discover more Discover more web hacking
Gophish: Phishing Framework for Simulation and Red Team
Gophish is an open-source platform for phishing simulation and red team engagement. It offers centralized campaign management, tracking, and reporting.
Discover more Discover more tools
Evilginx2: Bypass 2FA with Phishing Proxy Man-in-the-Middle
Evilginx2's practical guide to bypassing 2FA authentication: man-in-the-middle phishing, session hijacking, and credential theft. Advanced attacks against MFA.
Discover more Discover more tools
Commix: Automated Command Injection Exploitation Tool
Commix is an automated tool for identifying and exploiting command injection vulnerabilities in web applications. It supports blind, time-based, and file-based techniques to obtain RCE during penetration testing.
Discover more Discover more tools
Searchsploit: Finding Local Exploits from Exploit-DB in Penetration Testing
Searchsploit is a terminal tool for searching for local exploits directly from the Exploit-DB database. A practical guide to identifying exploitable vulnerabilities during penetration testing.
Discover more Discover more web hacking
BeEF: Complete Guide to the Browser Exploitation Framework
BeEF's practical guide to browser exploitation: victim hooks, compromised browser control, and client-side post-exploitation. Transform XSS into persistent access.
Discover more Discover more web hacking
SQLMap: Complete Guide to SQL Injection Automation and Database Exploitation
Complete guide to SQLMap for SQL injection automation: detection, exploitation, database enumeration, WAF bypass and UNION, boolean and time-based techniques.
Discover more Discover more web hacking
XSS (Cross-Site Scripting): Exploits, Payloads and Bypasses
XSS (Cross-Site Scripting): complete guide to reflected, stored and DOM-based XSS, payloads, advanced filter bypasses, exploitation and defense of web applications.
Discover more Discover more web hacking
WordPress xmlrpc.php: Attacks & Exploits for Pentest (2026)
Learn how to verify xmlrpc.php in WordPress, analyze brute force and pingbacks, assess SSRF risks, and secure your endpoint during a pentest.
Discover more Discover more