
- blog
- 16+ Note
- Focus
- OSCP · Red Team
- Structure
- Recon → Exploit
Concepts blog
Filters
 Recon & mapping
Guides and Resources
Theoretical concepts, mindsets, checklists, and external links to organize your studies, plan your labs, and save time.
Discover more Discover more guides-resources
Basilicata Data Center: The Kraken Case and the Hacker Mystery
Basilicata data center down: technical failure, Russian pages, and Kraken. What happened and what we know about the alleged hacker attack on the region.
Discover more Discover more guides-resources
The 10 Most Famous and Powerful Hackers in the World (2026 Guide)
Who are the 10 most famous and powerful hackers in history? From Kevin Mitnick to Anonymous: true stories, famous attacks, secrets and curiosities, and what they do today.
Discover more Discover more guides-resources
Dark Web: What It Is, How to Access It, and How It Works
What is the dark web, how does it differ from the deep web and Tor, what criminal economy really operates there, and what's true about legends like the Red Rooms.
Discover more Discover more guides-resources
White Hat, Black Hat, and Grey Hat: Who They Are and What They Risk
What distinguishes white hat, black hat, and grey hat, the origin of the term hacker/cracker, the legal risks of each, and what responsible disclosure is.
Discover more Discover more guides-resources
Computer Virus: What It Is and How It's Different from Malware
What is a computer virus, how it spreads, the main types, how to recognize and remove it, and how it differs from malware, worms, Trojans, and ransomware.
Discover more Discover more guides-resources
Ethical Hacker: Who He Is, What He Does, and How Much He Earns
Who is an ethical hacker, what they do every day, what skills and tools they use, how much they earn in Italy, and how to become one step by step.
Discover more Discover more guides-resources
Hacker: Meaning, Types (White Hat, Black Hat), and Cracker
What is a hacker, the difference between a cracker and an ethical hacker, the types (white, black, grey hat), when hacking is a crime, and how to become an ethical hacker.
Discover more Discover more guides-resources
Thomson Reuters: SSN breached and files sealed
Thomson Reuters: C-Track platform breached in US and Canadian courts. SSNs, health data, and court records sealed in 24 courts.
Discover more Discover more guides-resources
Database Security: Hardening, Misconfigurations and Pentests
Database security for pentesters and defenders: misconfigurations, weak credentials, exposed services, and hardening of MSSQL, MySQL, and PostgreSQL.
Discover more Discover more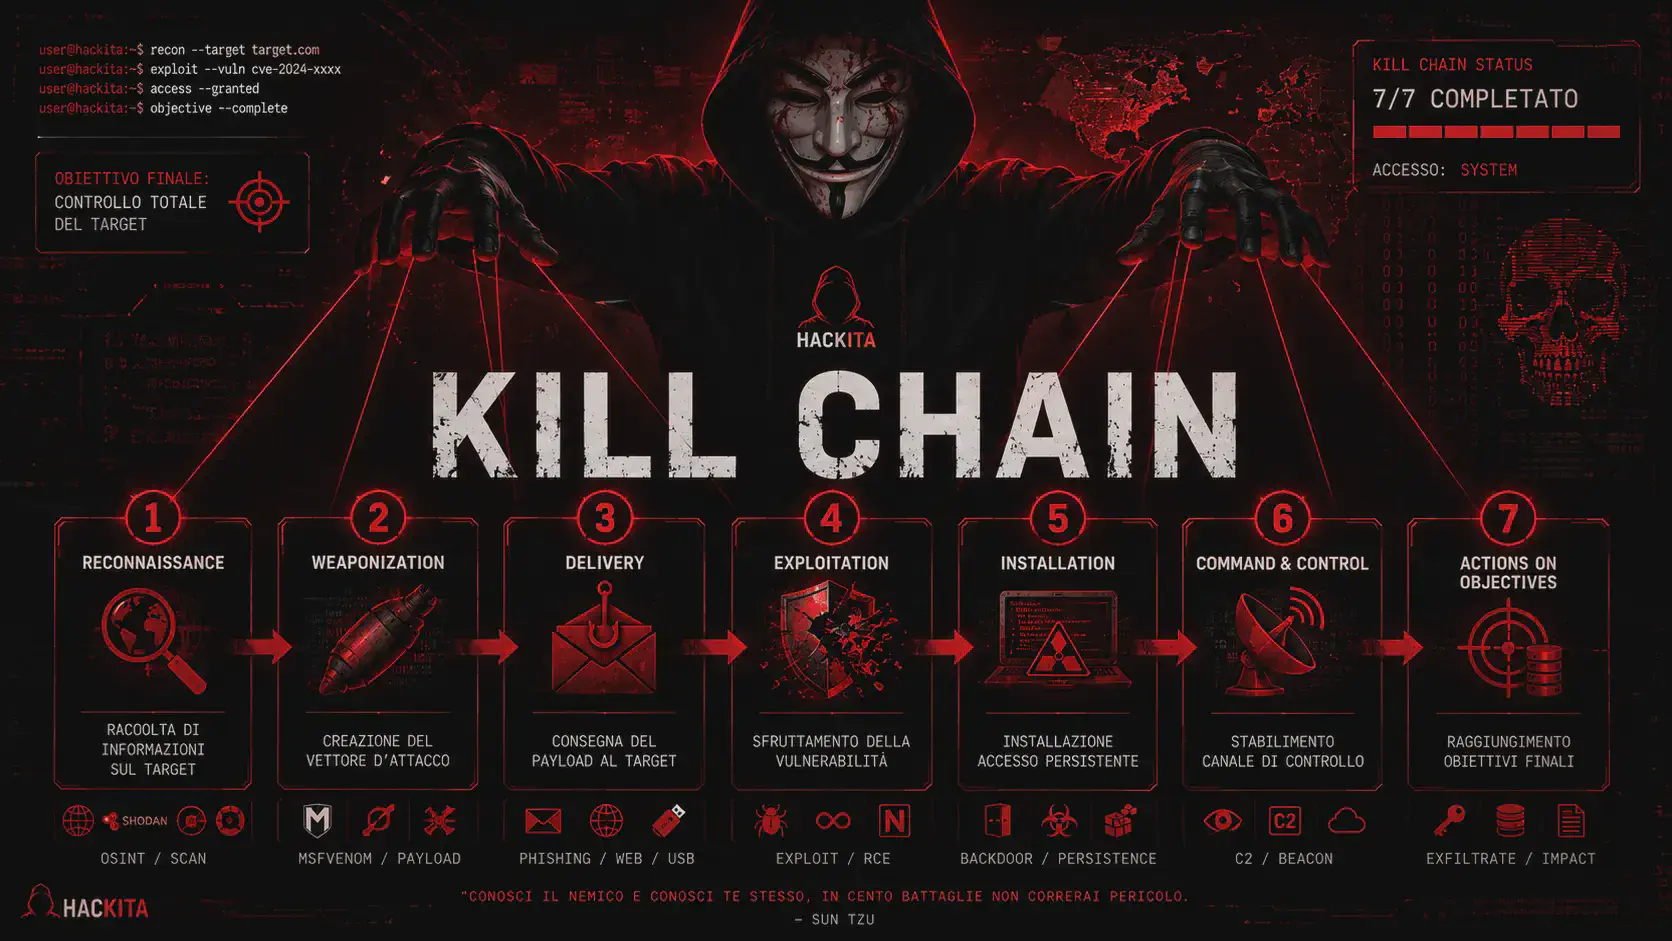 guides-resources
Cyber Kill Chain: What It Is, 7 Phases, and Pentesting Tools
Discover what the Cyber Kill Chain is: the 7 phases of an attack, pentesting and red team tools, MITRE ATT&CK mapping, and the Unified Kill Chain.
Discover more Discover more guides-resources
Ransomware 2026: A Complete Guide. What They Are and How to Protect Yourself
The Complete Guide to Ransomware 2026: What it is, how it works, historical attacks (WannaCry, LockBit), double extortion, RaaS, and best practices for defending against it with backups, MFA, and Zero Trust.
Discover more Discover more guides-resources
Vulnerability Exploitation: A Practical Framework for Moving from CVE to Shell
Discover the right method to transform a vulnerability into real access: discovery, validation, prioritization, exploit selection, weaponization, execution, and post-exploitation in penetration testing.
Discover more Discover more guides-resources
Man in the Middle (MITM): What it is and real-world techniques for intercepting traffic and credentials
The Complete Guide to Man in the Middle: ARP Spoofing, SSL Stripping, Session Hijacking, Rogue DHCP, Evil Twin, and Real-World MITM Techniques on Enterprise Networks and Wi-Fi.
Discover more Discover more guides-resources
Windows Buffer Overflow Exploit: ASLR and DEP Bypass with ROP Chain
Complete Guide to Windows Buffer Overflow Exploit: Format string leak to bypass ASLR, ROP chain to bypass DEP, VirtualAlloc, SEH, egg hunter.
Discover more Discover more guides-resources
AWS Privilege Escalation: 21+ Techniques for Escalating from Low-Priv to Admin in IAM
AWS Privilege Escalation is a set of techniques for gaining higher privileges by abusing IAM misconfigurations in cloud environments. Policy analysis, role assumption, and abuse of AWS services in authorized penetration testing contexts.
Discover more Discover more