
- blog
- 31+ Note
- Focus
- OSCP · Red Team
- Structure
- Recon → Exploit
Active Directory blog
Filters
 Recon & mapping
Windows
Abuse of services, registries, tokens, scheduled tasks and basic Active Directory knowledge to help you navigate enterprise environments.
Discover more Discover more windows
CredNinja: Validate SMB Credentials with NTLM Passwords and Hashes
Use CredNinja to validate passwords and NTLM hashes via SMB, find local admin, perform Pass-the-Hash and user hunting, and reduce lockouts with stripe and delay.
Discover more Discover more windows
TGS Kerberos: Kerberoasting, Silver Ticket and Service Ticket
Offensive Guide to Ticket-Granting Service (TGS) Kerberos: SPN, Kerberoasting with Rubeus and Impacket, Offline Crack, Pass-the-Ticket and Silver Ticket Windows AD
Discover more Discover more windows
Kerberos TGT: What It Is, How It Works, and How to Use It
Learn how Kerberos Ticket-Granting Ticket (TGT) works in Active Directory: Dumps with Rubeus, Pass-the-Ticket, Overpass-the-Hash, and Golden Ticket.
Discover more Discover more windows
Password Spraying: A Complete Guide to AD, AD FS, and Entra ID
Learn about Active Directory password spraying: techniques, authorized pentesting tools, detection, and defenses against weak password access.
Discover more Discover more windows
Windows Privilege Escalation: Techniques and Tools to Obtain SYSTEM
A guide to privilege escalation on Windows: enumeration, vulnerable services, token impersonation, DLL hijacking, UAC bypass, detection, and mitigations.
Discover more Discover more windows
Lateral Movement in Active Directory: Techniques, Tools and OPSEC
A guide to lateral movement in Active Directory: Pass-the-Hash, Kerberos, SMB, WMI, WinRM, and RDP with prerequisites, artifacts, detection, and mitigations.
Discover more Discover more windows
ACL Abuse Active Directory: GenericAll, WriteDACL and DCSync
Guide to ACL abuse in Active Directory: GenericAll, WriteDACL, reset password, RBCD and DCSync with BloodHound, PowerView, bloodyAD and Impacket.
Discover more Discover more windows
AS-REP Roasting: Cracking Kerberos Hashes Without Credentials
AS-REP Roasting in Active Directory: Extract Kerberos hashes without credentials and crack them offline with Impacket, Rubeus, and Hashcat. A complete technical guide.
Discover more Discover more windows
Golden Ticket Attack: What It Is, How It Works, and How to Defend Yourself in Active Directory
The Golden Ticket is the most dangerous attack on Active Directory. Learn how it works, how to forge a TGT with the krbtgt hash, how to detect it, and how to defend yourself with double reset. A complete guide.
Discover more Discover more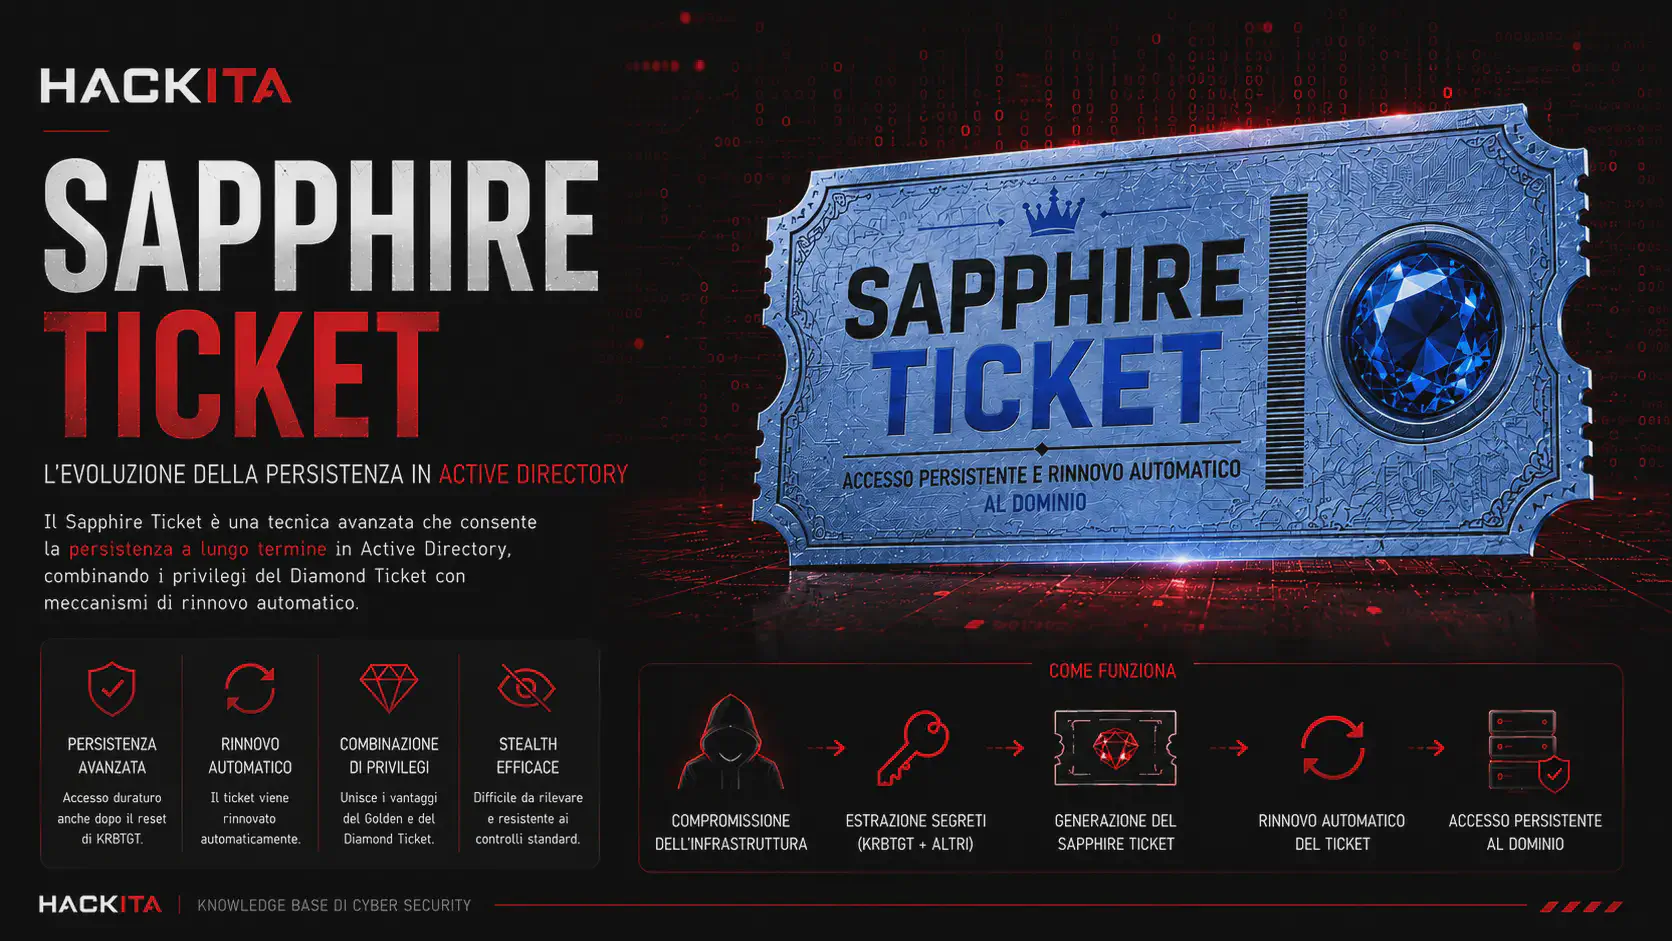 windows
Sapphire Ticket: Kerberos Stealth S4U2Self+U2U Ticket
Sapphire Ticket: The stealthiest Kerberos ticket. Combines S4U2Self + U2U for the authentic KDC PAC. Impacket impersonation guide, differences from Golden/Diamond, detection, and mitigation.
Discover more Discover more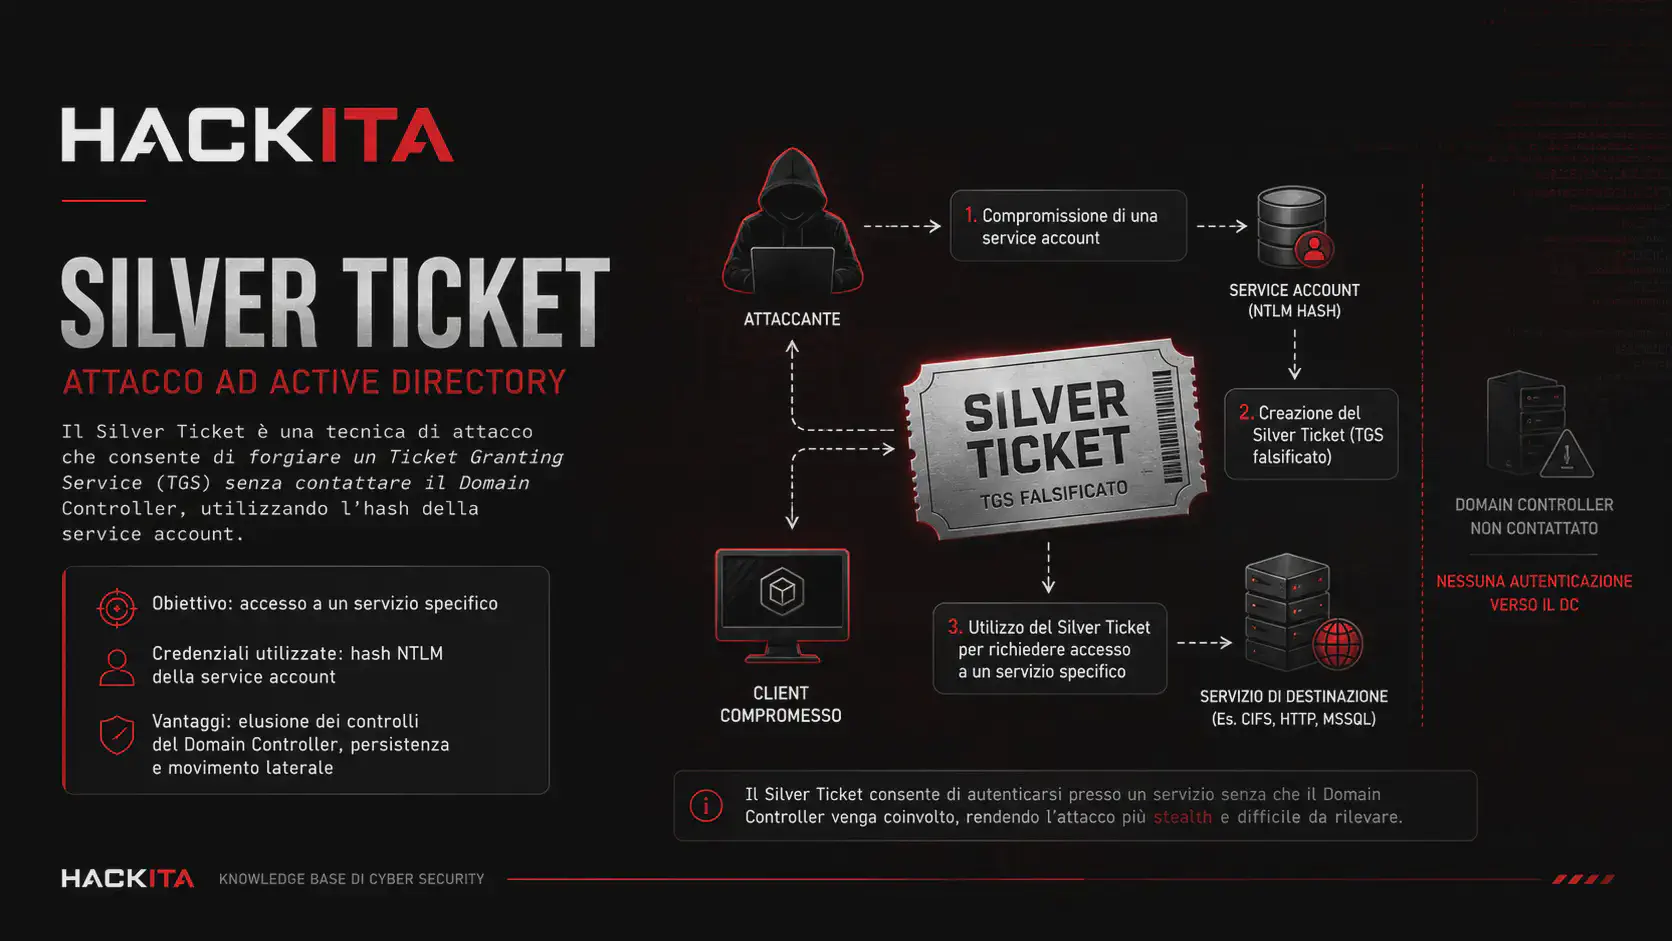 windows
Silver Ticket Attack: What It Is, How It Works, and How to Defend Yourself in AD
The Silver Ticket forges a Kerberos TGS using a service account hash, completely bypassing the KDC. A complete guide: how to obtain it, forge it with Mimikatz, Rubeus, and Impacket, scenarios for CIFS, LDAP, MSSQL, HTTP, and how to detect it.
Discover more Discover more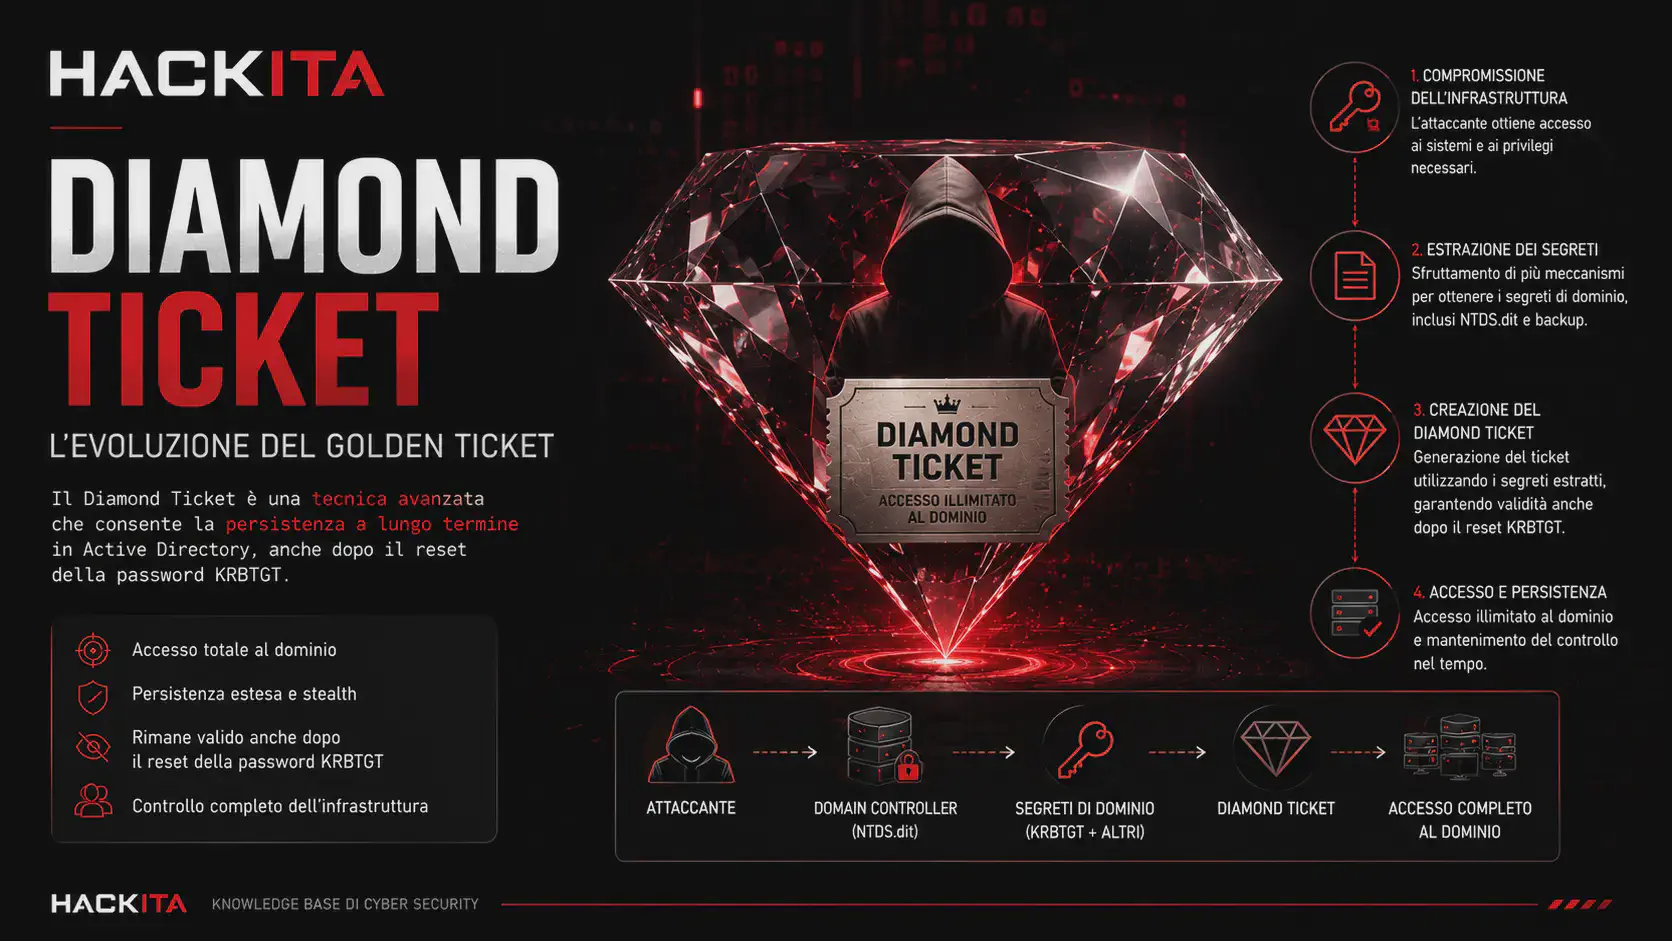 windows
Diamond Ticket Attack: The Stealth Evolution of the Golden Ticket
Diamond Ticket: A stealth variant of the Golden Ticket with a real TGT to bypass MDI. Rubeus /ldap /opsec guide, Impacket, detection, and KRBTGT reset.
Discover more Discover more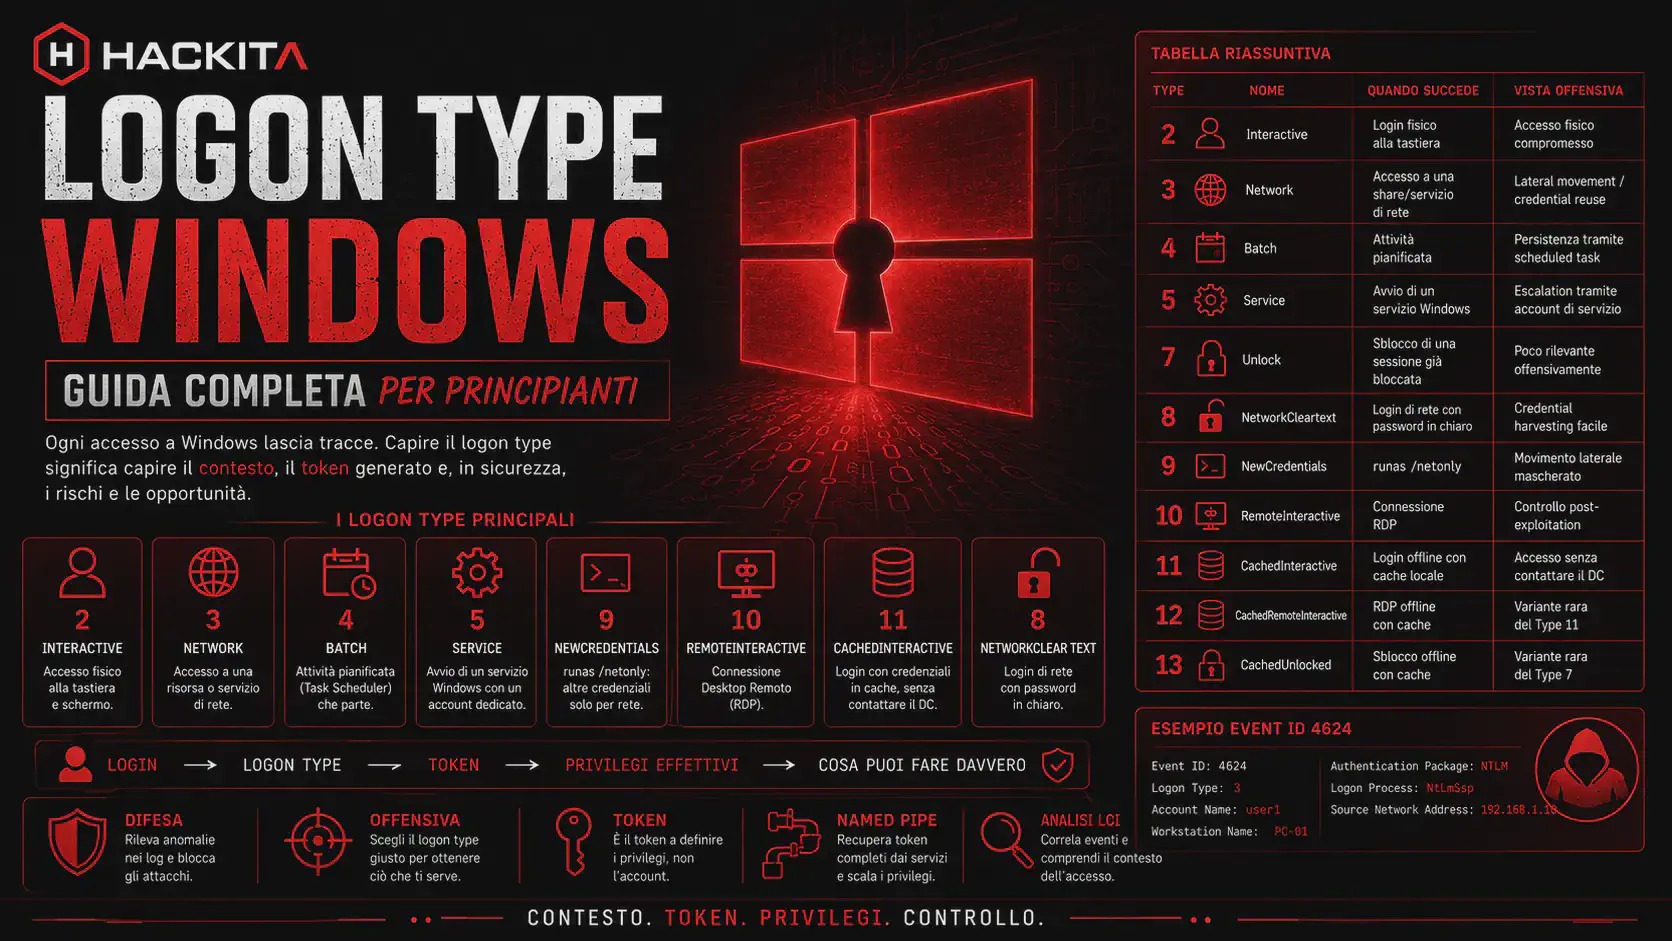 windows
Logon Type Windows: Guide for Pentester, Red Teamer and SOC Analyst
Windows Logon Type: A practical guide to the 13 logon types, from Interactive to CachedUnlock. Real-world examples and relevance for penetration testing and security audits.
Discover more Discover more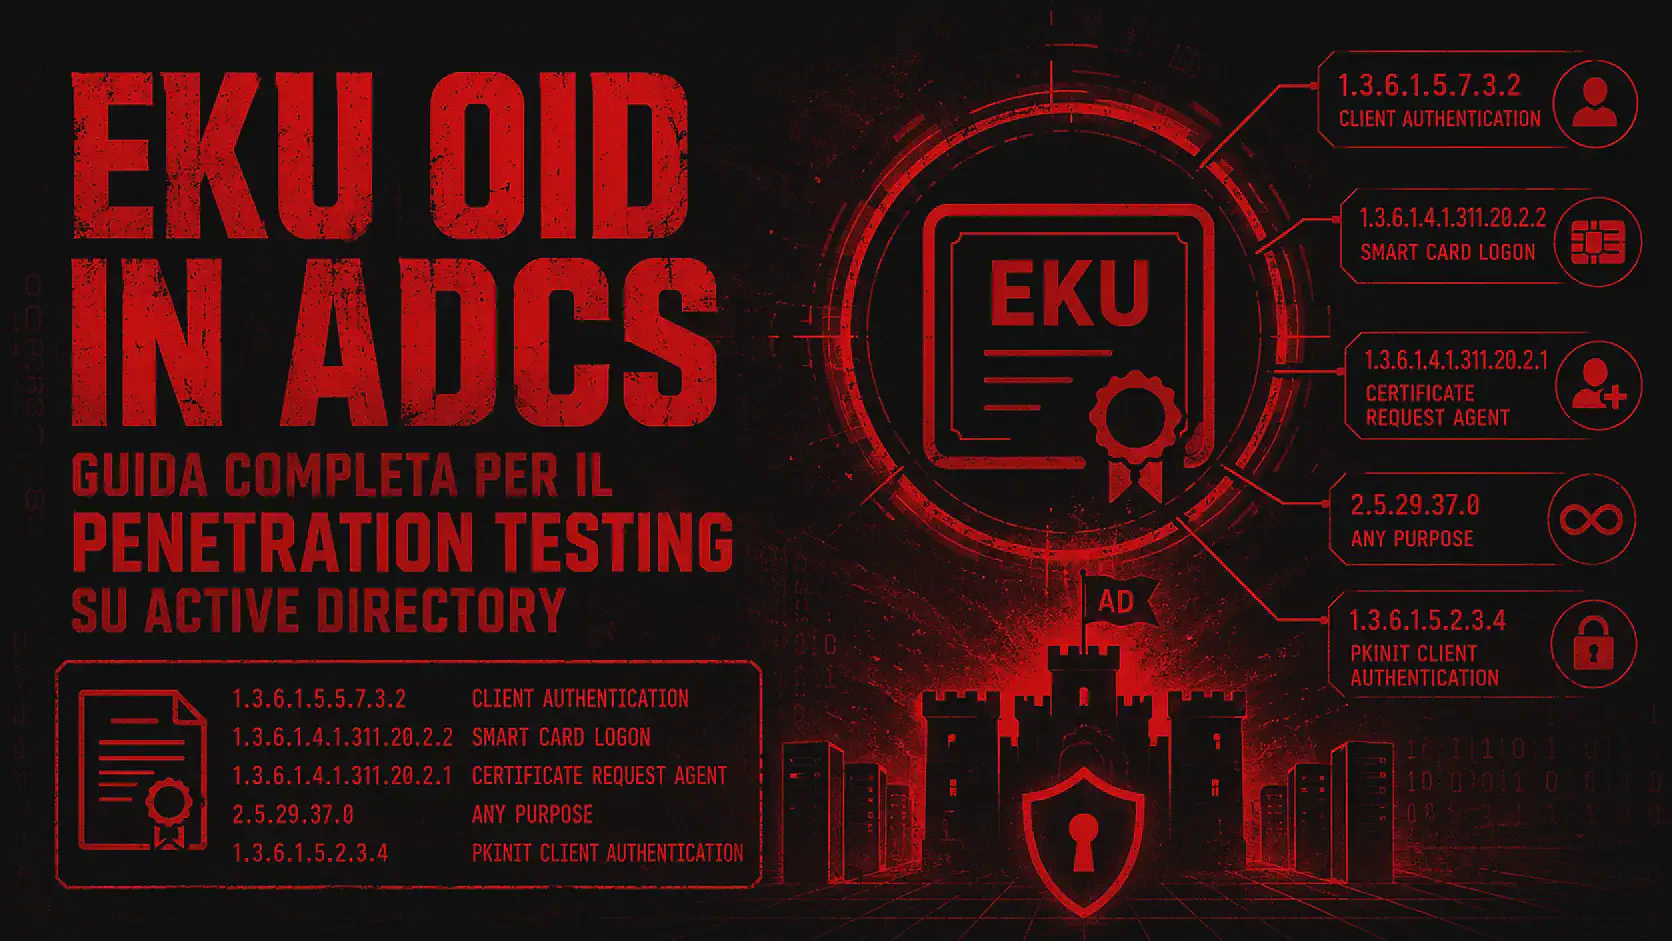 windows
EKU OID in ADCS: A Complete Guide to Active Directory Penetration Testing
All Active Directory certificate EKU OIDs explained from an offensive perspective: which ones to exploit in ESC1–ESC16, PKINIT attack flow, Event ID detection, FAQ and complete table with offensive relevance.
Discover more Discover more windows
Kerberoasting: Complete Guide — SPN, TGS Cracking and Domain Admin in 2026
Kerberoasting in Active Directory: SPN enumeration with GetUserSPNs and Rubeus, RC4 downgrade, hashcat, targeted kerberoasting, and real OPSEC. From domain user to privileged credentials.
Discover more Discover more windows
NTLM: Protocol, Hash Capture, Pass-the-Hash and Relay on Active Directory
NTLM explained from top to bottom: handshake, capture, NetNTLMv2 with Responder, Pass-the-Hash, coercion, and CVE 2026 enabled. NTLM vs. Kerberos decision point in the enterprise pentest.
Discover more Discover more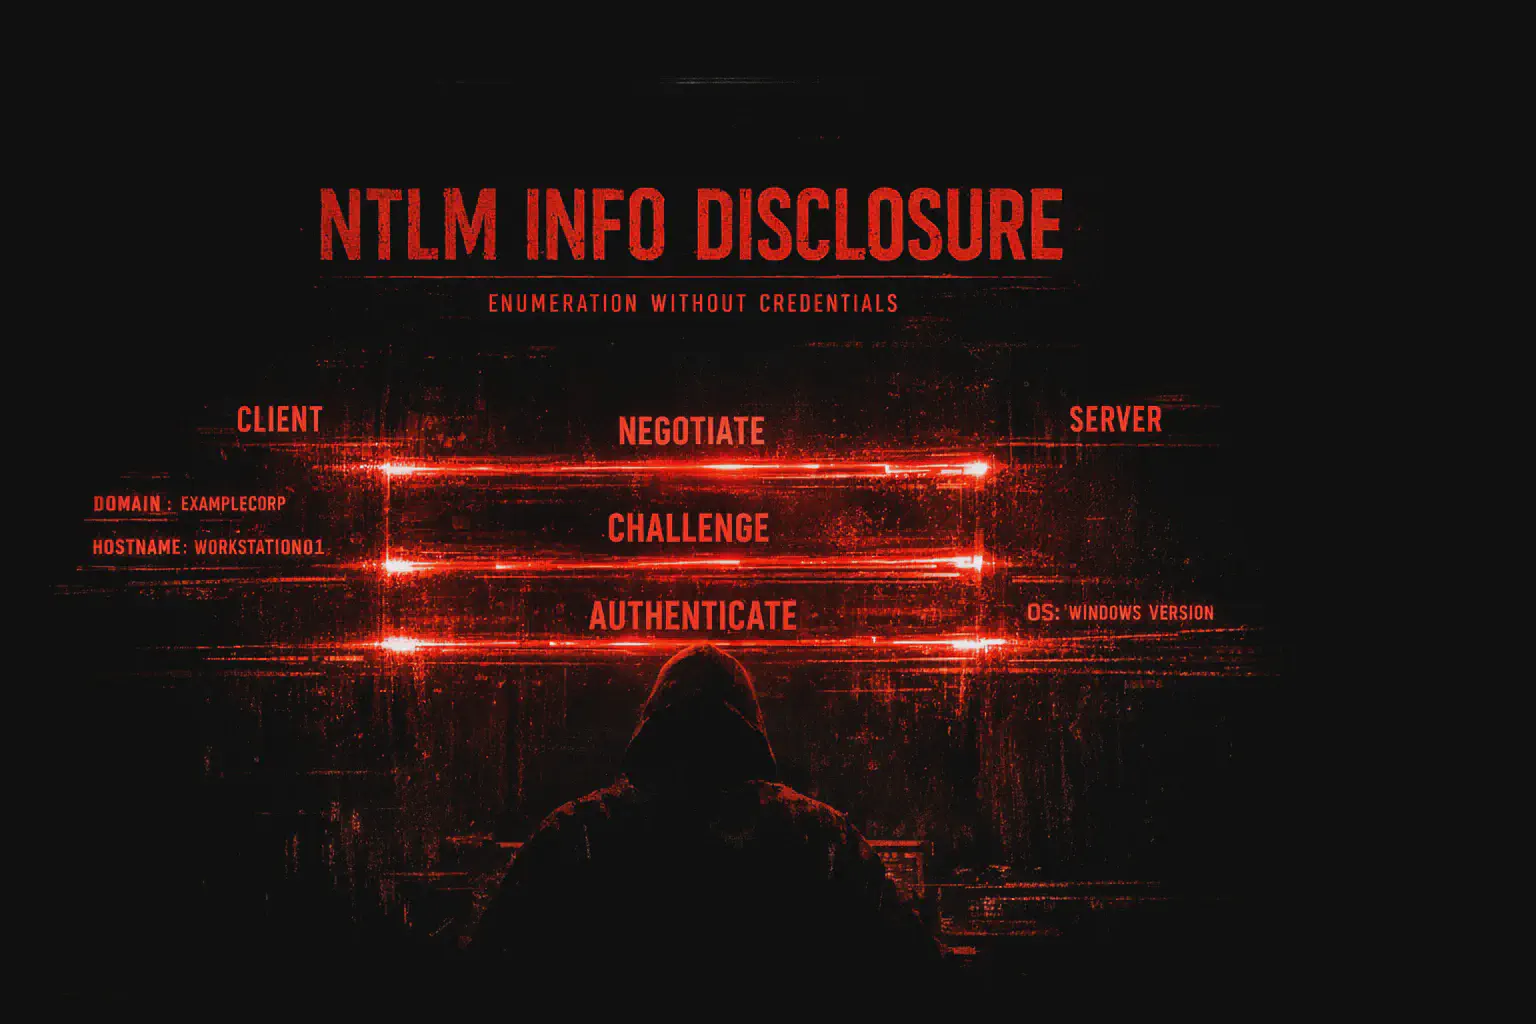 windows
NTLM Information Disclosure: Enumerate Domain, Hostname, and OS Without Credentials
NTLM authentication over HTTP reveals AD domain, NetBIOS name, hostname, and OS version with a single GET, without credentials. This is an essential recon technique for Exchange and IIS red teams. Learn curl, Nmap, Burp, and defenses.
Discover more Discover more windows
DPAPI Attack in Active Directory: Extract Encrypted Passwords and Masterkeys
Complete guide on DPAPI in an Active Directory pentest: masterkey, credential files, Chrome/Edge offline with pypykatz, LSASS dump LOLBin, DSInternals and DonPAPI.
Discover more Discover more windows
Active Directory Pentesting 2026: Complete Guide to Kerberos, NTLM and Privilege Escalation
Active Directory Pentesting operationally explained: AD architecture, Kerberos vs NTLM, BloodHound, Kerberoasting, AS-REP Roasting, NTLM Relay, ACL abuse, AD CS, DCSync, Golden Ticket, Shadow Credentials and real defenses.
Discover more Discover more windows
Kerberos Active Directory Attacks: Kerberoasting, AS-REP, Golden Ticket
Port 88 Kerberos: Complete guide to Active Directory penetration testing. Learn about Kerberoasting, AS-REP Roasting, Golden Ticket, Silver Ticket and Pass-the-Ticket for privilege escalation and lateral movement.
Discover more Discover more windows
Mimikatz: Complete Guide to Credential Dumping and Active Directory Attack
Mimikatz explained for pentesters: LSASS credential extraction, DCSync, Golden Ticket, pass-the-hash, and Active Directory attacks with practical examples.
Discover more Discover more windows
Smbexec: SMB Remote Execution and Lateral Movement in Active Directory
SMBExec: A Practical Guide to Windows Remote Execution: Stealthy Lateral Movement via SMB Without Disk Files. A Fileless Alternative to PsExec for AD Pentesting.
Discover more Discover more windows
Rubeus: Kerberos Attacks in Active Directory (2026)
Rubeus is the reference C# tool for attacking Kerberos in AD. Discover Kerberoasting, AS-REP Roasting, Pass-the-Ticket, and S4U with real-world detection.
Discover more Discover more windows
Windows Pass-the-Hash: Attack, Operation, and Passwordless Access
Learn Pass-the-Hash (PtH) on Windows: how it works, how to leverage NTLM hashes to gain passwordless access, and real-world lateral movement techniques.
Discover more Discover more windows
PsExec: Remote Command Execution via SMB in Windows Environments
PsExec allows remote command execution on Windows systems via SMB. A key tool for lateral movement and remote administration.
Discover more Discover more windows
DCSync: Active Directory Credential Dump via Replication Abuse
DCSync is an Active Directory technique that allows credential hash extraction by abusing the domain replication mechanism. It is used post-exploitation to obtain NTLM hashes of privileged users without direct access to the domain controller.
Discover more Discover more windows
Adfind: Advanced Active Directory Enumeration in Penetration Testing
AdFind is a tool for enumerating Active Directory objects via command-line LDAP queries. A practical guide to using it during domain enumeration during a penetration test.
Discover more Discover more windows
MSSQL Pentesting: Port 1433, Enumeration, Attack, and Payload
Learn how to enumerate and join MSSQL (port 1433): pentest for weak credentials, xp_dirtree for NTLM hashes, xp_cmdshell for RCE, and pivoting on linked servers
Discover more Discover more windows
LDAP Port 389: Enumeration and Pentesting in Active Directory
LDAP 389 PORT: Null bind, users, groups and SPNs, exposed credentials, LDAP relay and injection: enumeration techniques and misconfigurations in Active Directory.
Discover more Discover more windows
SMB Port 445: Enumeration and Attacks in a Pentest
SMB Port 445 on Windows Servers: Share enumeration, exploits, NTLM relay, Pass-the-Hash, remote execution, and lateral movement in Active Directory.
Discover more Discover more