
Abuse of services, registries, tokens, scheduled tasks and basic Active Directory knowledge to help you navigate enterprise environments.
- blog
- 73+ Note
- Focus
- OSCP · Red Team
- Structure
- Recon → Exploit
Windows blog
Filters
 windows
CredNinja: Validate SMB Credentials with NTLM Passwords and Hashes
Use CredNinja to validate passwords and NTLM hashes via SMB, find local admin, perform Pass-the-Hash and user hunting, and reduce lockouts with stripe and delay.
Discover more Discover more windows
Windows Filesystem: NTFS, Folders, and Registry for Pentesting
A practical guide to the Windows file system for pentesting: NTFS, system folders, the registry, ACLs, enumeration commands, privilege escalation, and detection.
Discover more Discover more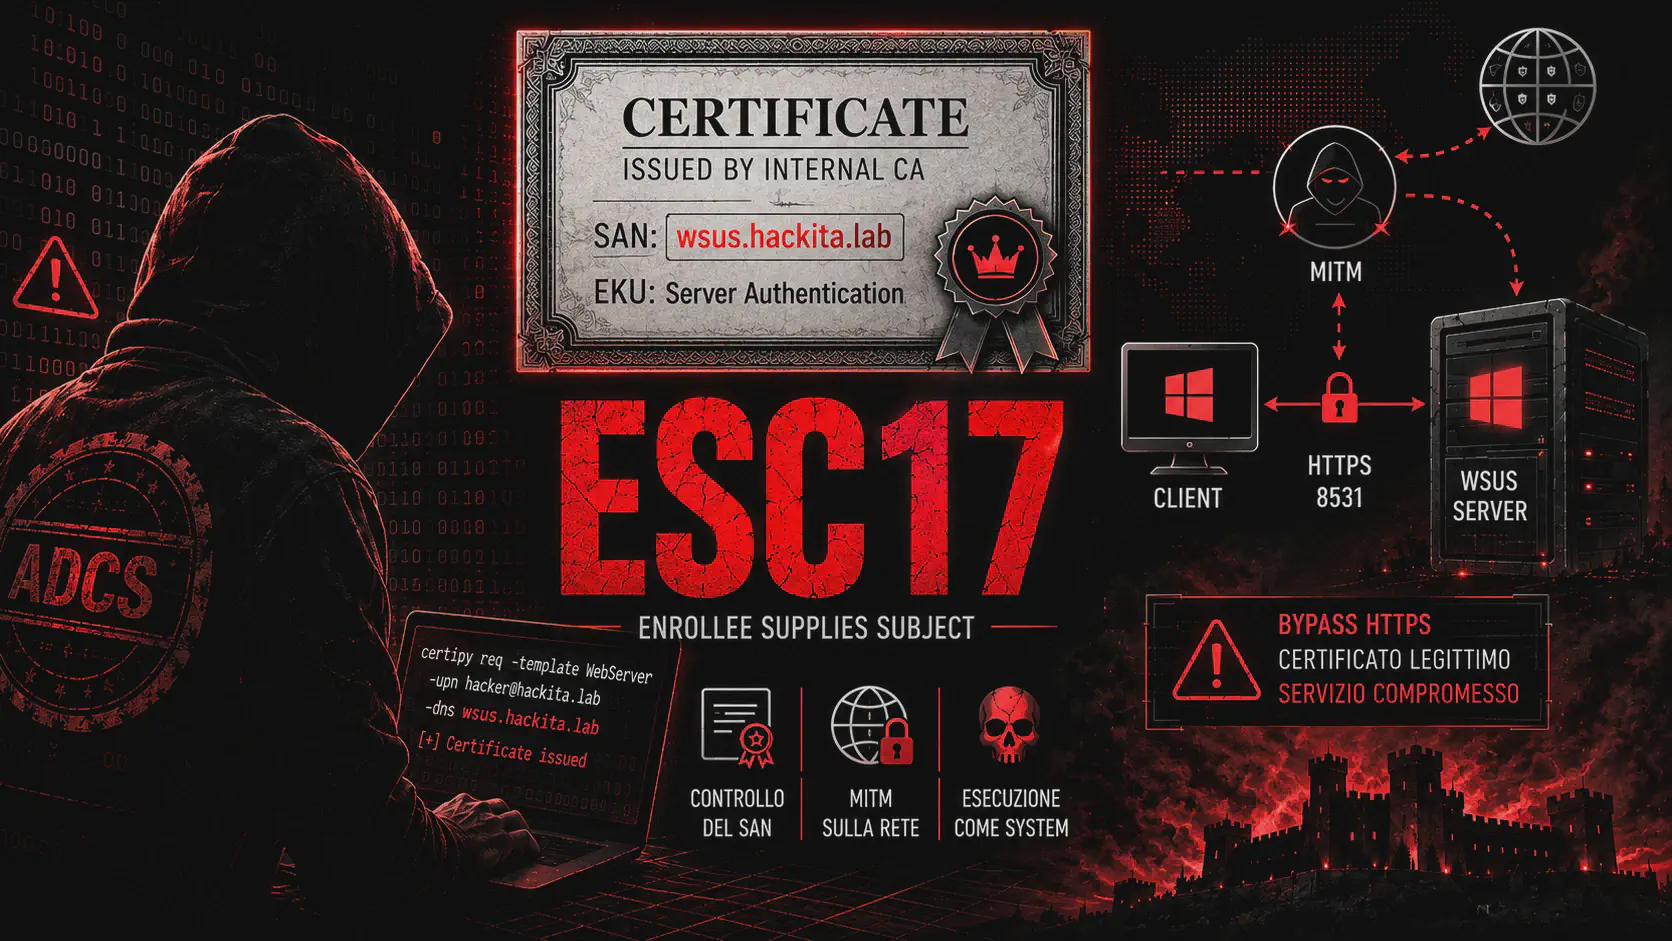 windows
ESC17 ADCS: MITM attack on WSUS clients over HTTPS
ESC17 ADCS uses controllable SANs to impersonate WSUS over HTTPS. Learn about certificate request with Certipy, MITM with wsuks, privesc, and detection.
Discover more Discover more windows
TGS Kerberos: Kerberoasting, Silver Ticket and Service Ticket
Offensive Guide to Ticket-Granting Service (TGS) Kerberos: SPN, Kerberoasting with Rubeus and Impacket, Offline Crack, Pass-the-Ticket and Silver Ticket Windows AD
Discover more Discover more windows
Kerberos TGT: What It Is, How It Works, and How to Use It
Learn how Kerberos Ticket-Granting Ticket (TGT) works in Active Directory: Dumps with Rubeus, Pass-the-Ticket, Overpass-the-Hash, and Golden Ticket.
Discover more Discover more windows
Password Spraying: A Complete Guide to AD, AD FS, and Entra ID
Learn about Active Directory password spraying: techniques, authorized pentesting tools, detection, and defenses against weak password access.
Discover more Discover more windows
Windows Privilege Escalation: Techniques and Tools to Obtain SYSTEM
A guide to privilege escalation on Windows: enumeration, vulnerable services, token impersonation, DLL hijacking, UAC bypass, detection, and mitigations.
Discover more Discover more windows
SeEnableDelegationPrivilege: Privisce AD, S4U and delegation
What is SeEnableDelegationPrivilege, privilege escalation, unconstrained/constrained/RBCD variants, S4U2Self-S4U2Proxy, errors, detection and defense.
Discover more Discover more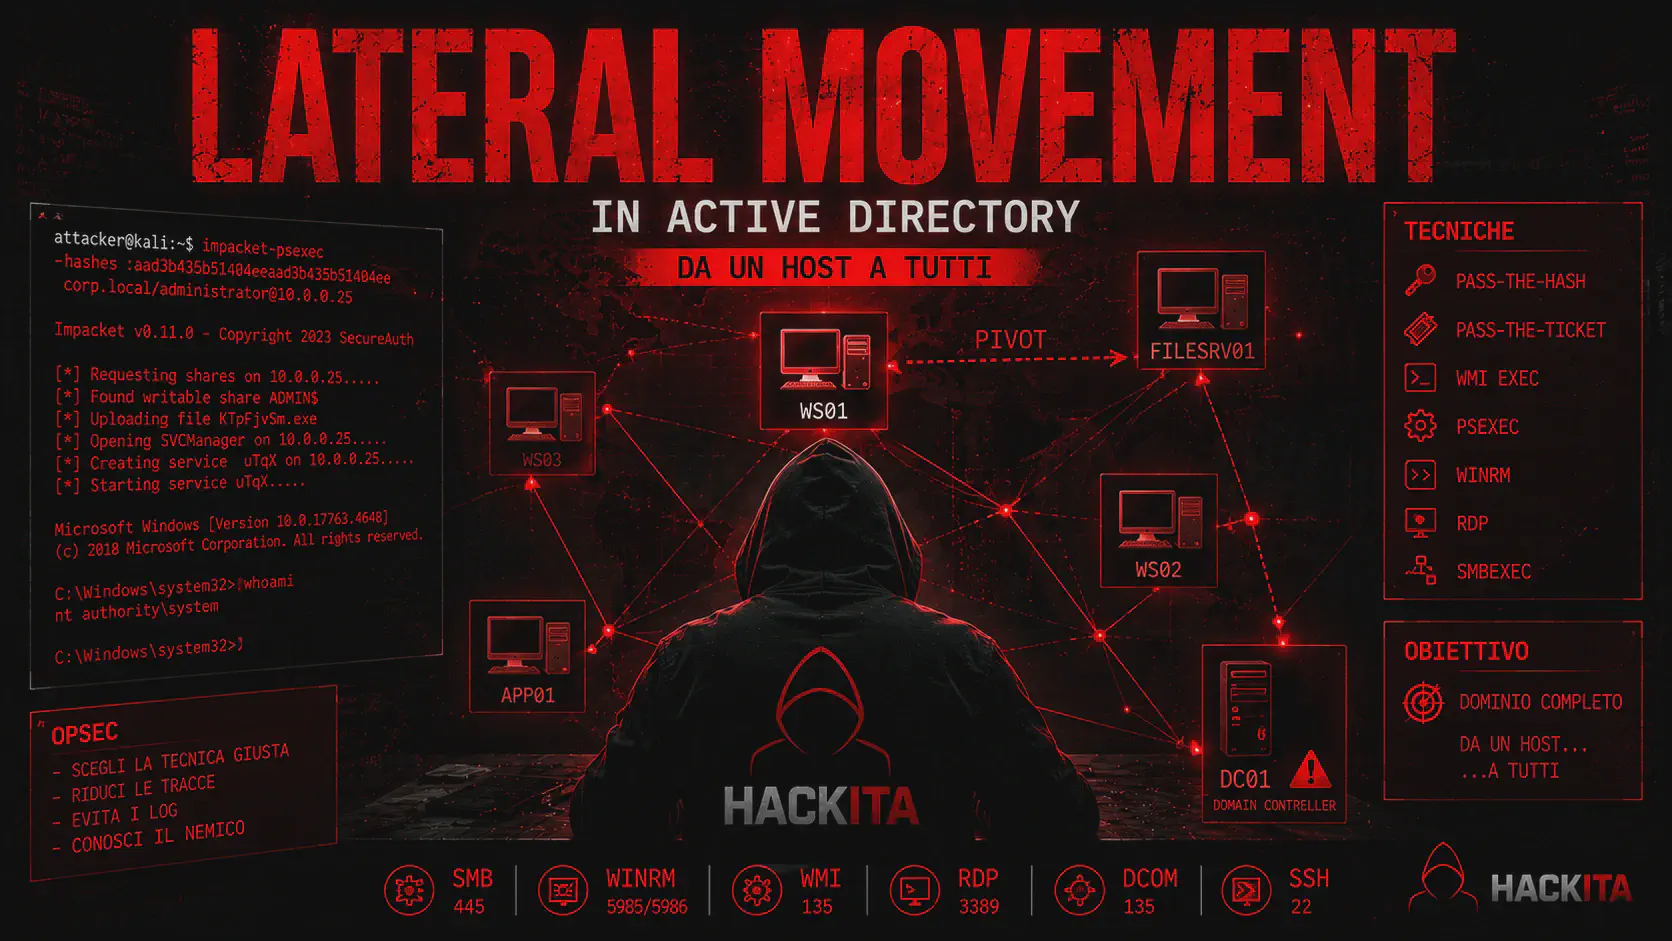 windows
Lateral Movement in Active Directory: Techniques, Tools and OPSEC
A guide to lateral movement in Active Directory: Pass-the-Hash, Kerberos, SMB, WMI, WinRM, and RDP with prerequisites, artifacts, detection, and mitigations.
Discover more Discover more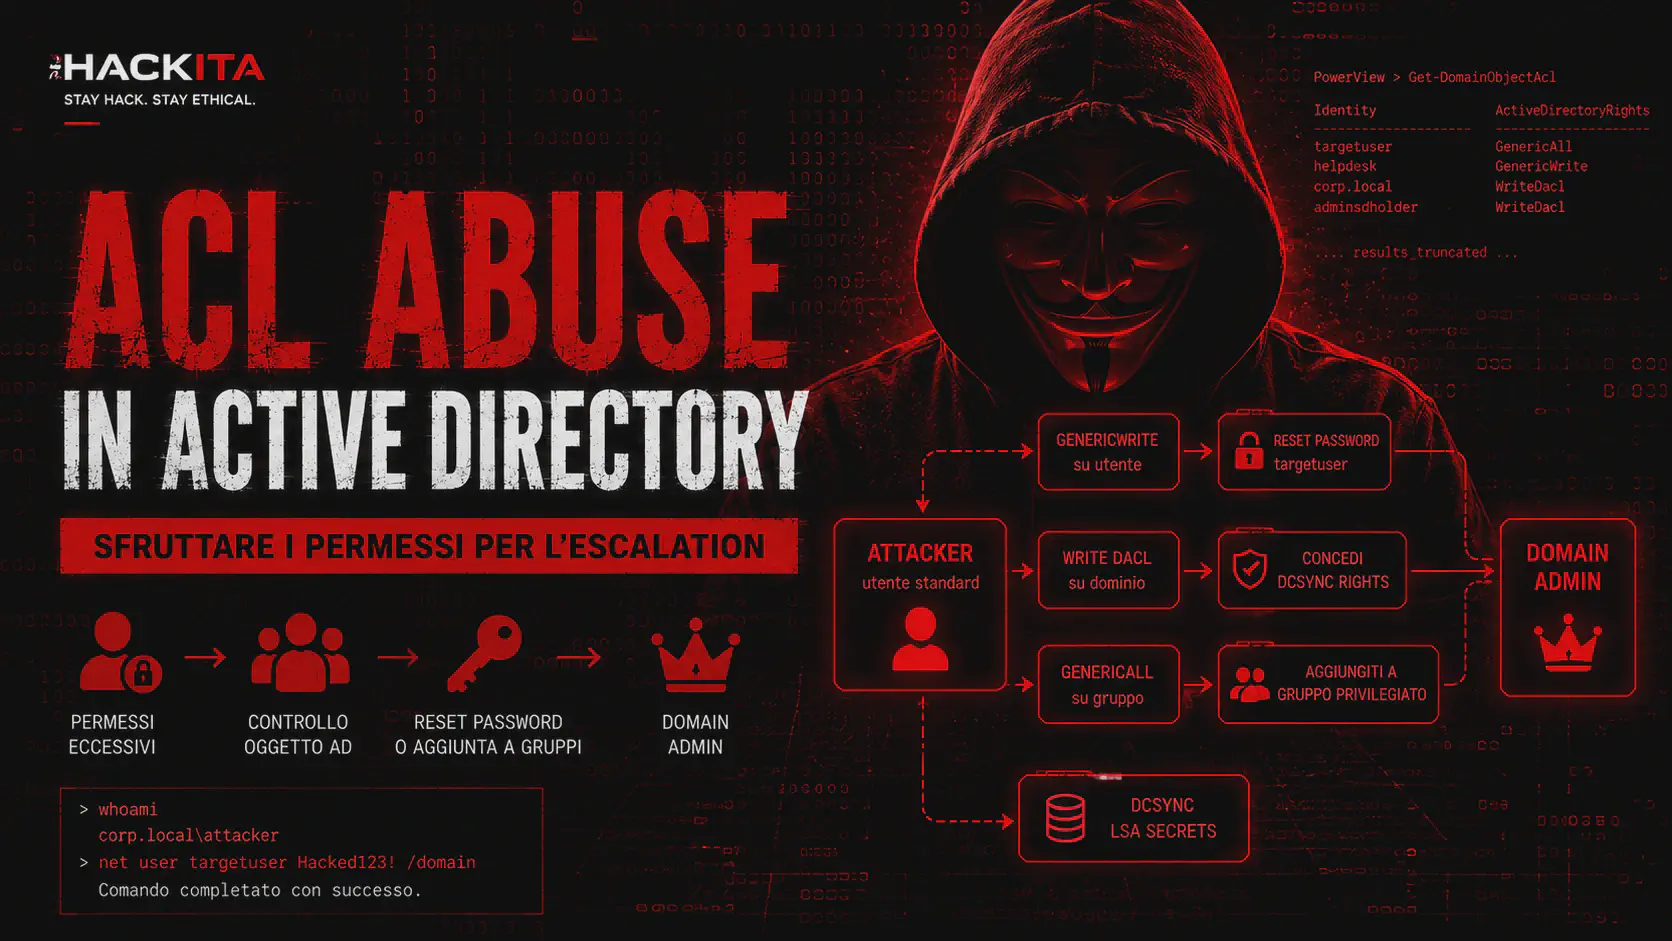 windows
ACL Abuse Active Directory: GenericAll, WriteDACL and DCSync
Guide to ACL abuse in Active Directory: GenericAll, WriteDACL, reset password, RBCD and DCSync with BloodHound, PowerView, bloodyAD and Impacket.
Discover more Discover more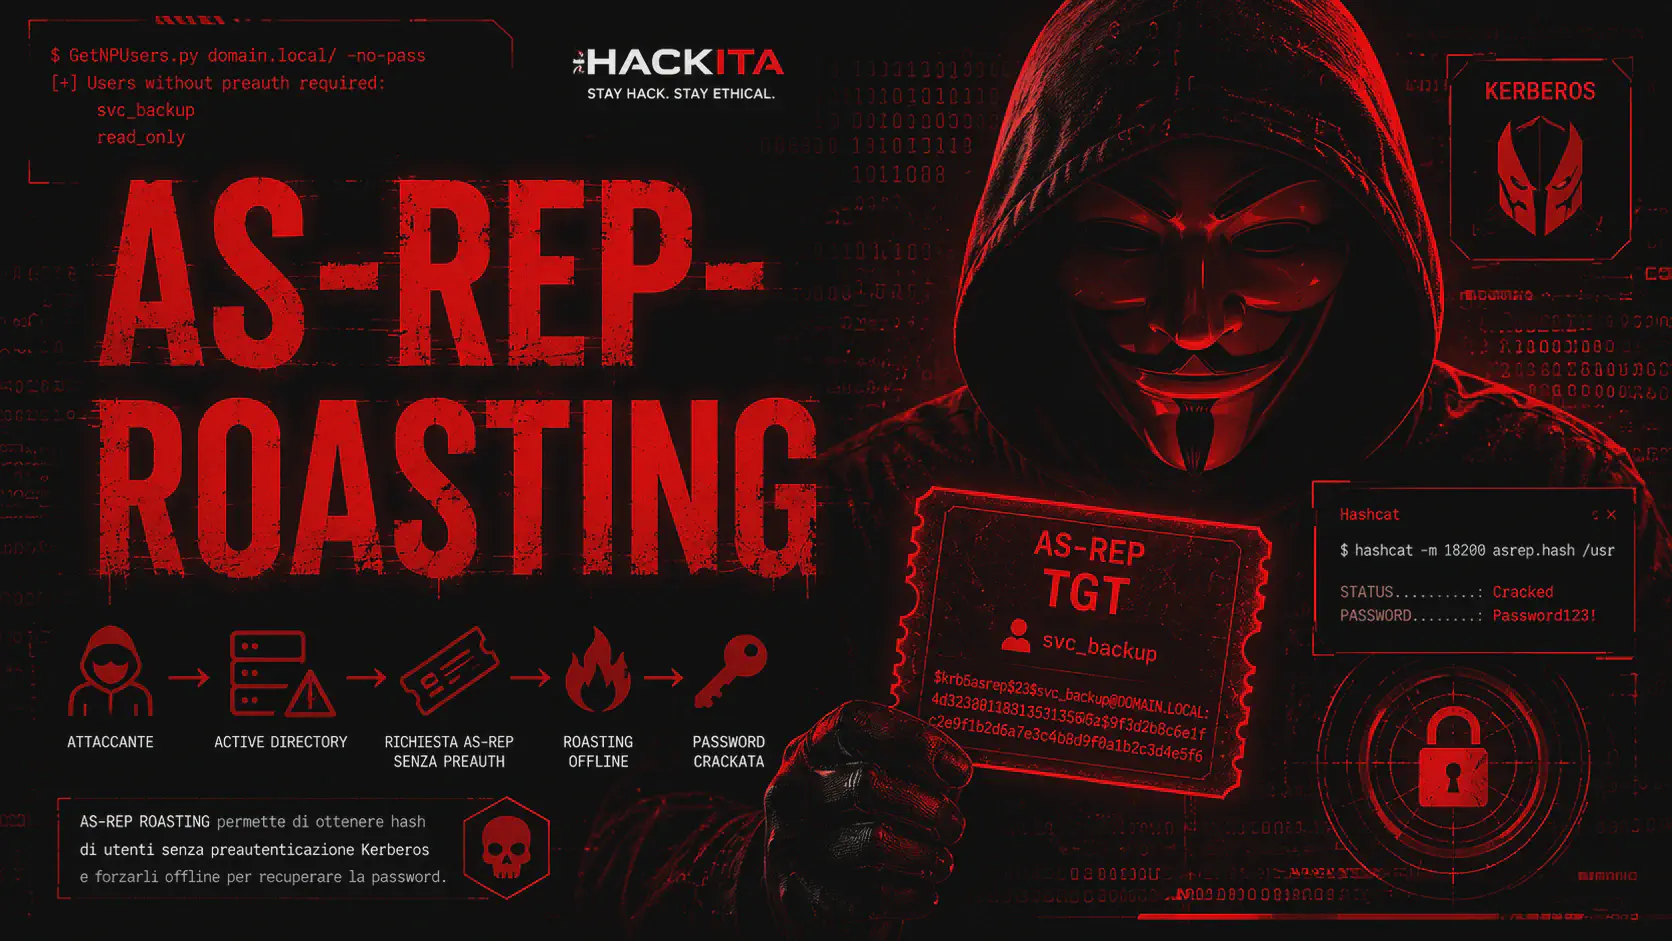 windows
AS-REP Roasting: Cracking Kerberos Hashes Without Credentials
AS-REP Roasting in Active Directory: Extract Kerberos hashes without credentials and crack them offline with Impacket, Rubeus, and Hashcat. A complete technical guide.
Discover more Discover more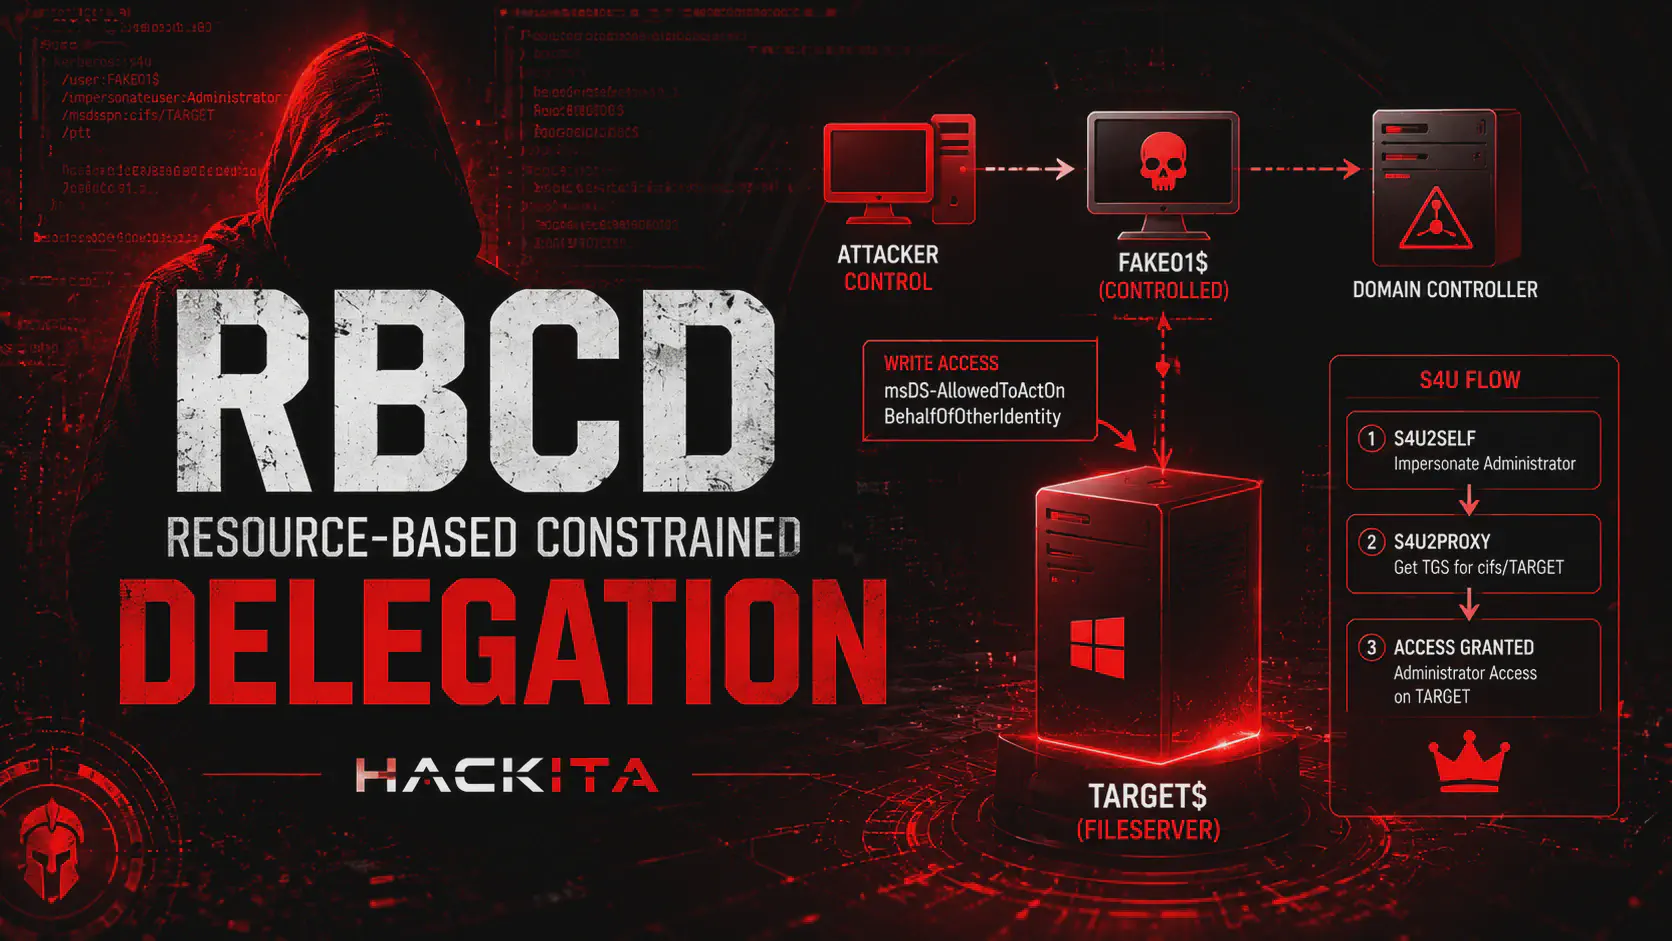 windows
RBCD Attack : Resource-Based Constrained Delegation PrivEsc
RBCD leverages write access on msDS-AllowedToActOnBehalfOfOtherIdentity for privilege escalation on active directory. Drive with Impacket, Rubeus and NTLM relay.
Discover more Discover more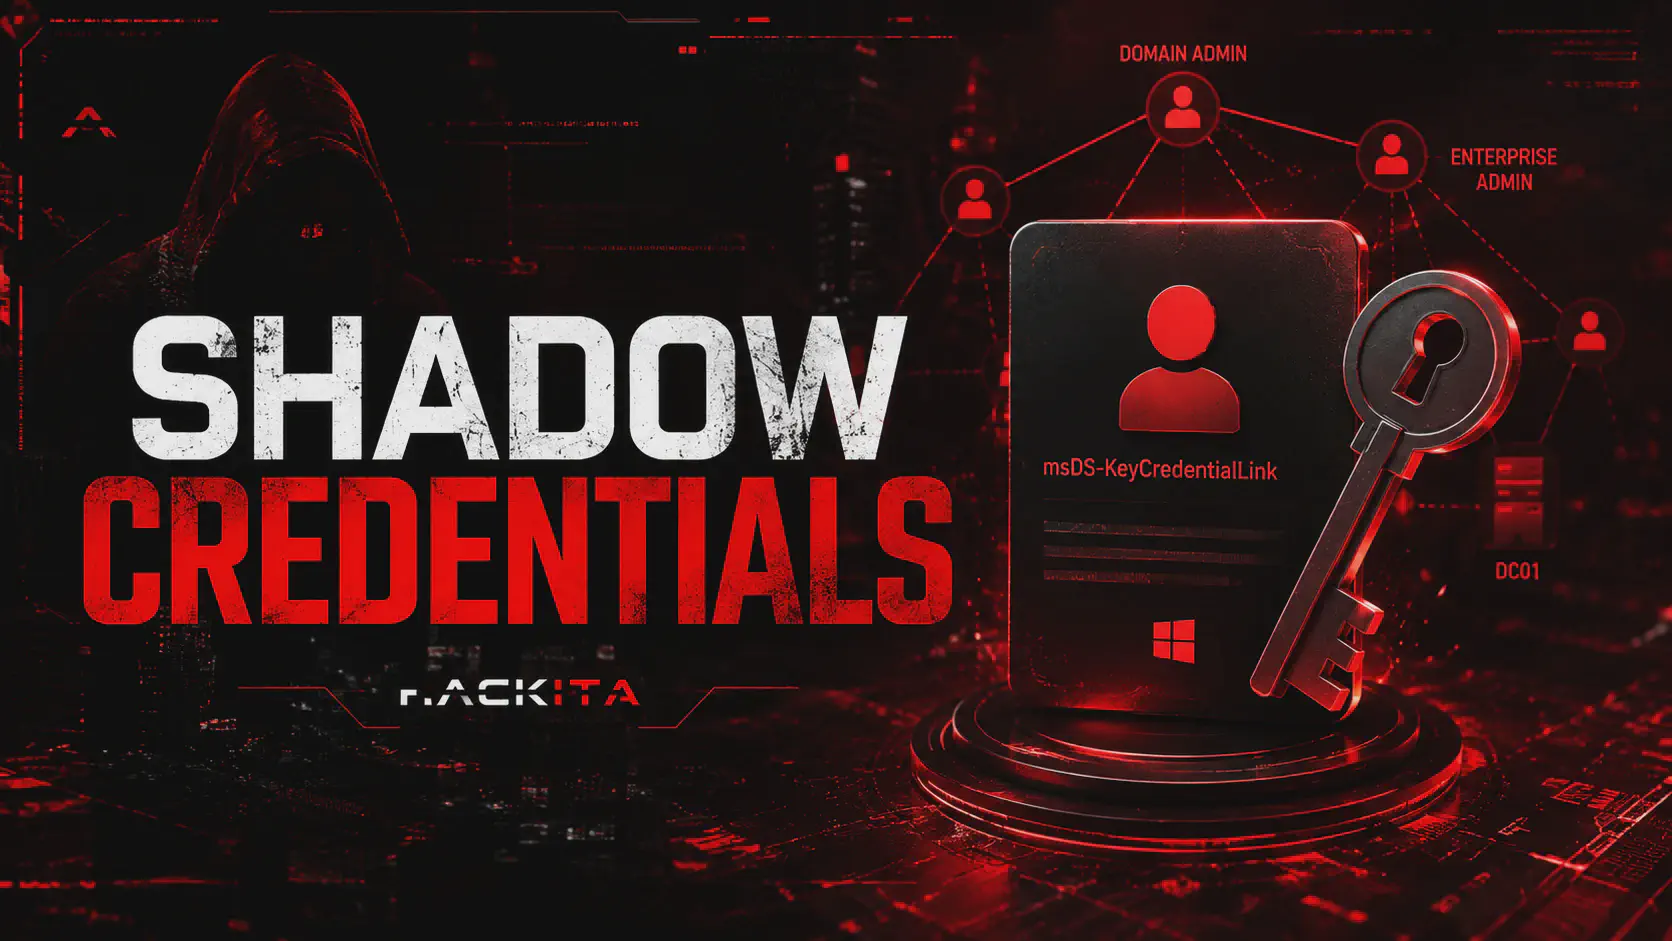 windows
Shadow Credentials AD: PrivEsc msDS-KeyCredentialLink
Shadow Credentials: Leverage msDS-KeyCredentialLink for passwordless AD account takeover. A practical guide with Whisker, pyWhisker, and Certipy for AD pentesting.
Discover more Discover more windows
Golden Ticket Attack: What It Is, How It Works, and How to Defend Yourself in Active Directory
The Golden Ticket is the most dangerous attack on Active Directory. Learn how it works, how to forge a TGT with the krbtgt hash, how to detect it, and how to defend yourself with double reset. A complete guide.
Discover more Discover more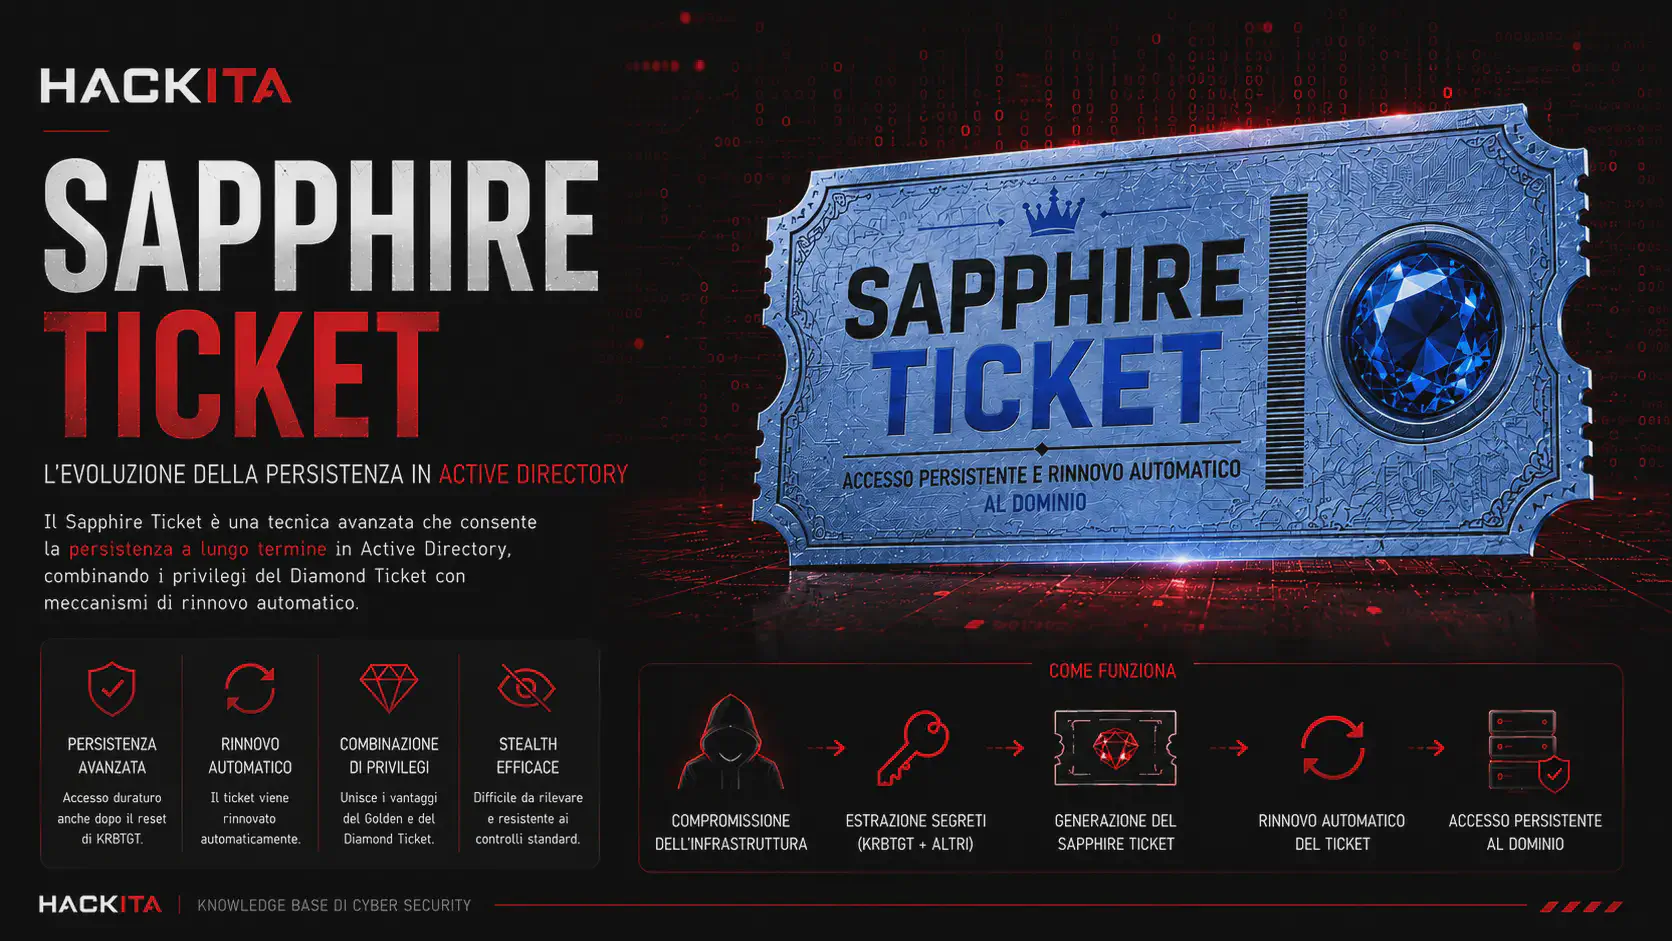 windows
Sapphire Ticket: Kerberos Stealth S4U2Self+U2U Ticket
Sapphire Ticket: The stealthiest Kerberos ticket. Combines S4U2Self + U2U for the authentic KDC PAC. Impacket impersonation guide, differences from Golden/Diamond, detection, and mitigation.
Discover more Discover more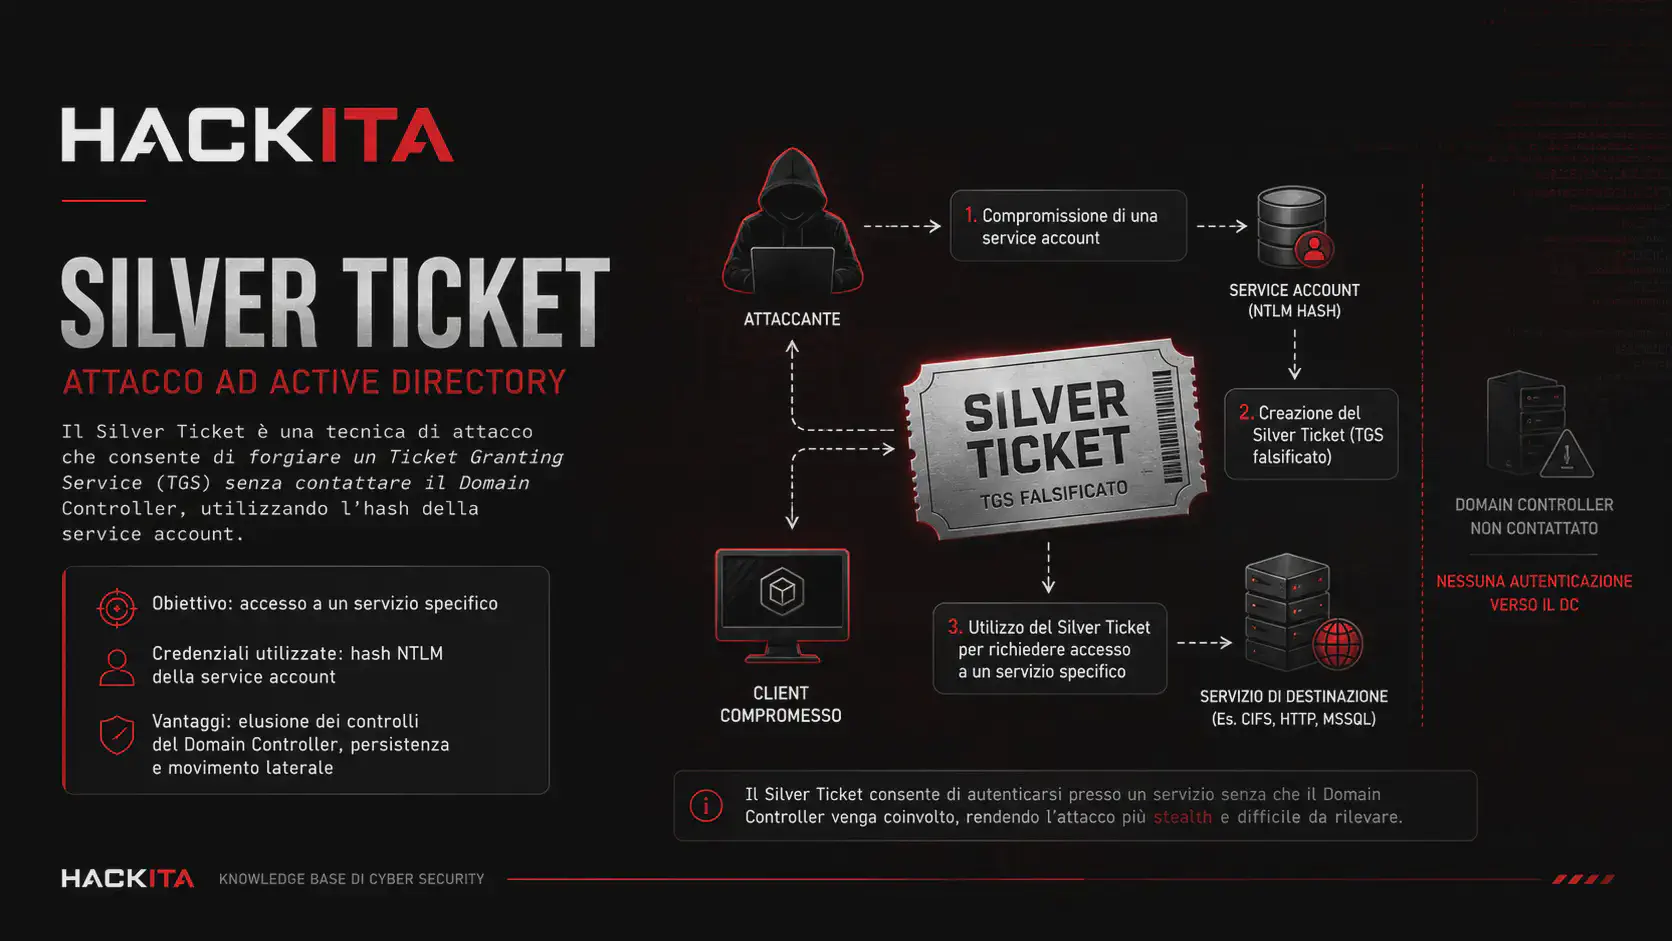 windows
Silver Ticket Attack: What It Is, How It Works, and How to Defend Yourself in AD
The Silver Ticket forges a Kerberos TGS using a service account hash, completely bypassing the KDC. A complete guide: how to obtain it, forge it with Mimikatz, Rubeus, and Impacket, scenarios for CIFS, LDAP, MSSQL, HTTP, and how to detect it.
Discover more Discover more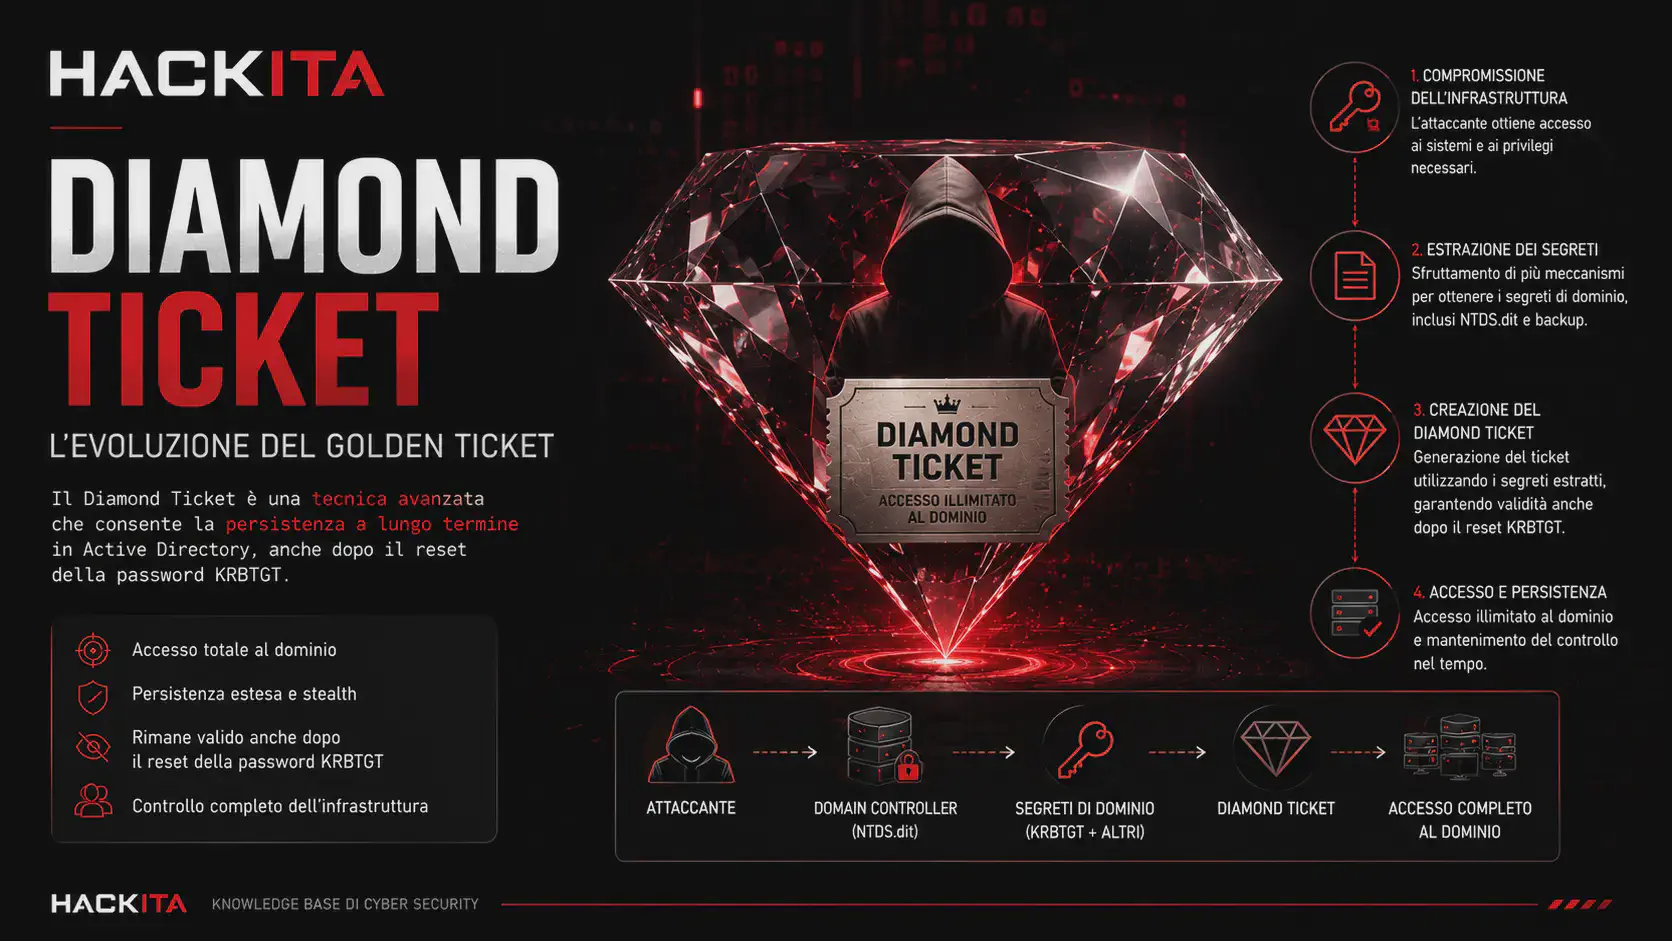 windows
Diamond Ticket Attack: The Stealth Evolution of the Golden Ticket
Diamond Ticket: A stealth variant of the Golden Ticket with a real TGT to bypass MDI. Rubeus /ldap /opsec guide, Impacket, detection, and KRBTGT reset.
Discover more Discover more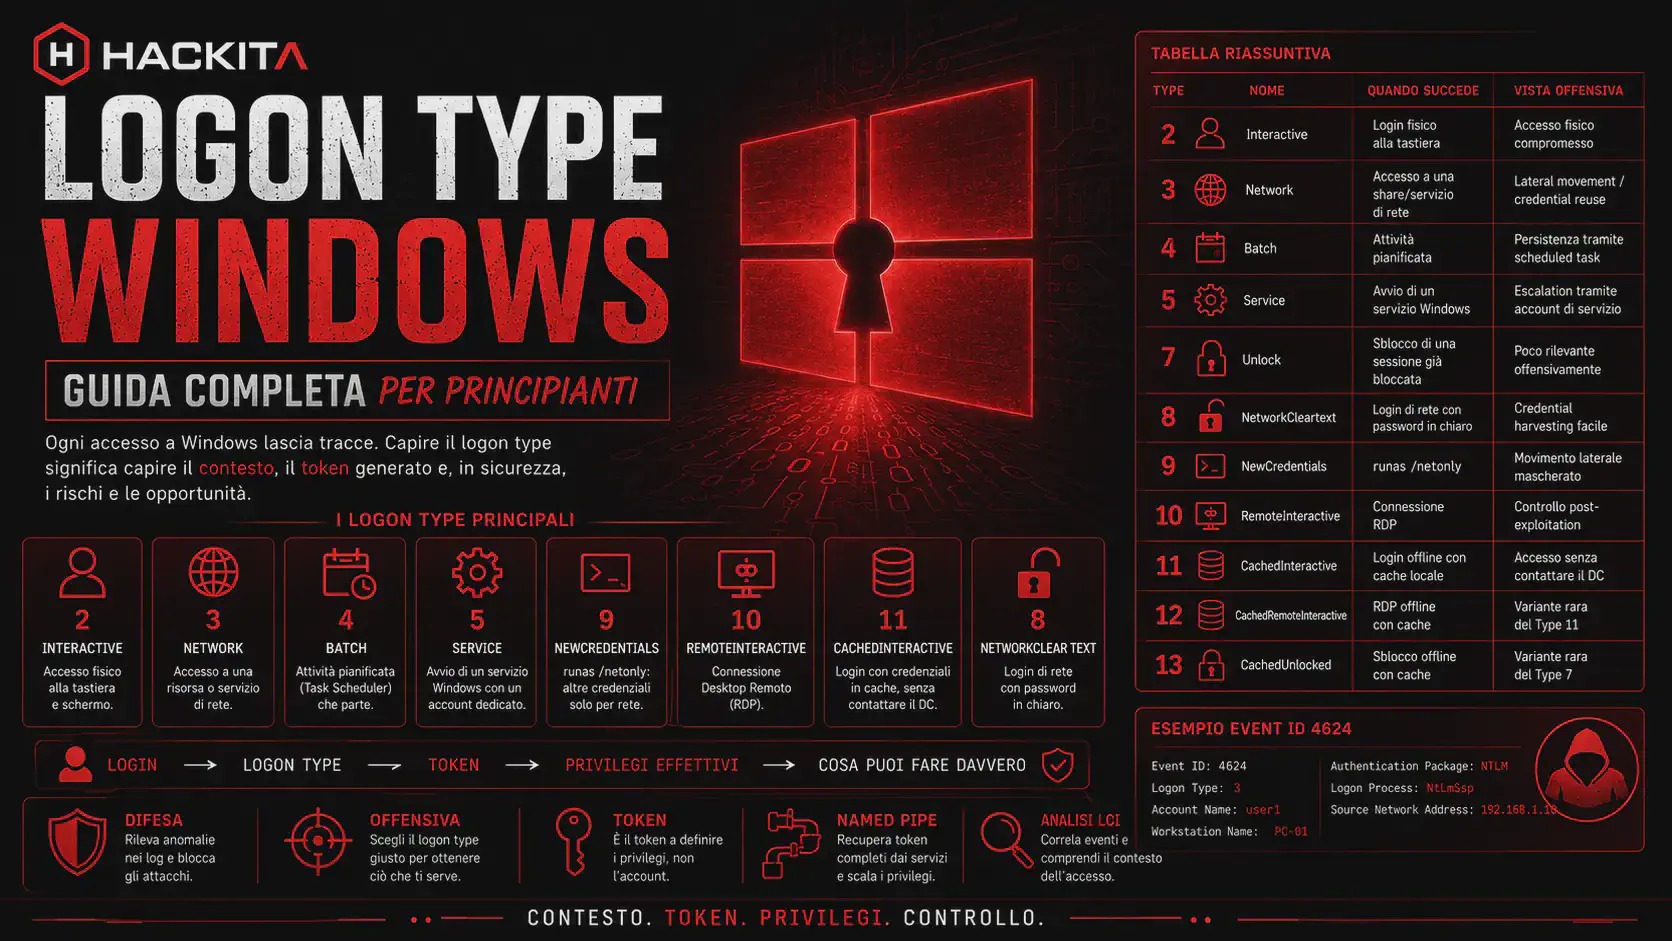 windows
Logon Type Windows: Guide for Pentester, Red Teamer and SOC Analyst
Windows Logon Type: A practical guide to the 13 logon types, from Interactive to CachedUnlock. Real-world examples and relevance for penetration testing and security audits.
Discover more Discover more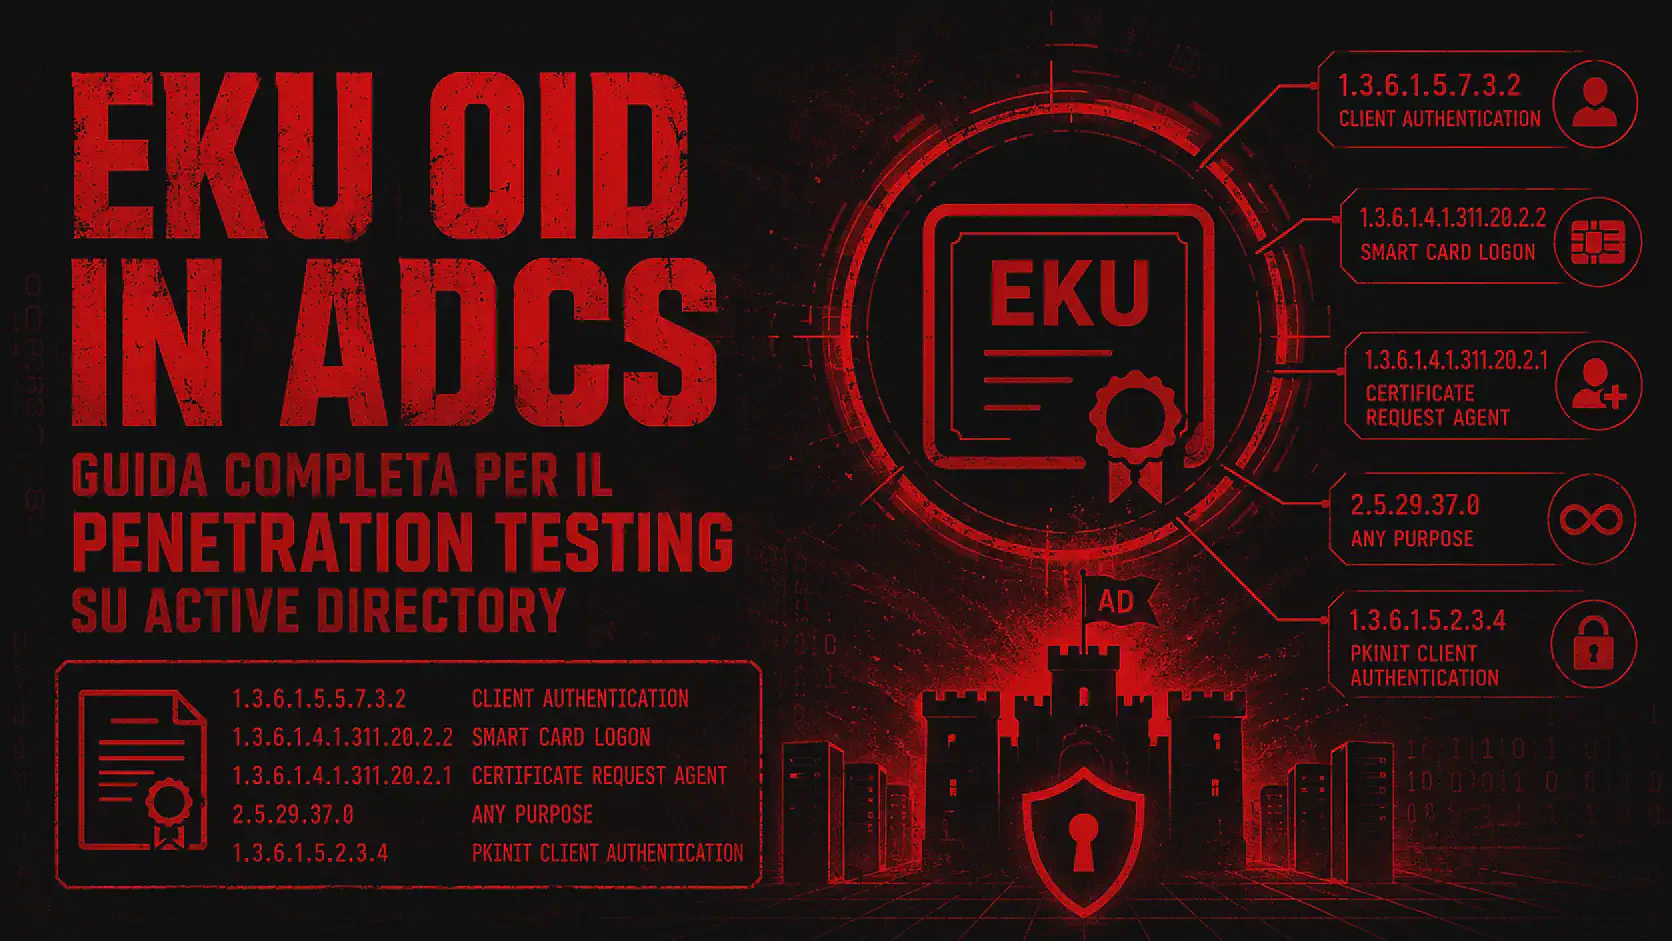 windows
EKU OID in ADCS: A Complete Guide to Active Directory Penetration Testing
All Active Directory certificate EKU OIDs explained from an offensive perspective: which ones to exploit in ESC1–ESC16, PKINIT attack flow, Event ID detection, FAQ and complete table with offensive relevance.
Discover more Discover more windows
SeMachineAccountQuota and RBCD: Privilege a Domain Admin in 5 Commands
From standard domain user to Domain Admin using MachineAccountQuota=10 and RBCD. Create computer account, S4U tickets, DCSync. Red Team AD guidance and privilege escalation.
Discover more Discover more windows
SeRelabelPrivilege: Bypass MIC and Write to File SYSTEM
Learn how to use SeRelabelPrivilege to lower the integrity level of files and directories, bypass Mandatory Integrity Control, and gain a SYSTEM shell.
Discover more Discover more windows
SeSecurityPrivilege: Clear Logs, SACLs, and SIEM Evasion
How to use SeSecurityPrivilege to read and delete the Security Log, remove SACLs, and operate invisibly on Windows. Red Team OpSec guide with SIEM verification.
Discover more Discover more windows
Kerberoasting: Complete Guide — SPN, TGS Cracking and Domain Admin in 2026
Kerberoasting in Active Directory: SPN enumeration with GetUserSPNs and Rubeus, RC4 downgrade, hashcat, targeted kerberoasting, and real OPSEC. From domain user to privileged credentials.
Discover more Discover more windows
SeTcbPrivilege: Arbitrary LSA Logon Session to SYSTEM
Found SeTcbPrivilege on a non-system account? Create LSA sessions with SID Domain Admins and get SYSTEM without external conditions. Red Team Technique.
Discover more Discover more windows
NTLM: Protocol, Hash Capture, Pass-the-Hash and Relay on Active Directory
NTLM explained from top to bottom: handshake, capture, NetNTLMv2 with Responder, Pass-the-Hash, coercion, and CVE 2026 enabled. NTLM vs. Kerberos decision point in the enterprise pentest.
Discover more Discover more windows
SeCreateTokenPrivilege: Token Forgery from Zero to SYSTEM
Found SeCreateTokenPrivilege on a non-system account? Create tokens with SID SYSTEM and Domain Admins from scratch. NtCreateToken for SYSTEM shell. Red Team technique.
Discover more Discover more windows
SeManageVolumePrivilege: Raw Disk for SAM and NTDS.dit without lock
How to use SeManageVolumePrivilege and RawCopy to extract SAM, SYSTEM, and NTDS.dit from the physical disk, bypassing locks and ACLs. Red Team technique with raw device access.
Discover more Discover more windows
SeCreateSymbolicLinkPrivilege: Symlink Attack on Windows from Shell
From simple user to SYSTEM by replacing system files with a symlink: what you can do with SeCreateSymbolicLinkPrivilege and mklink. Privilege escalation and the Red Team technique.
Discover more Discover more windows
SeTakeOwnershipPrivilege: From Admin to SYSTEM with 3 Commands
How to abuse SeTakeOwnershipPrivilege to take ownership of system binaries and gain the SYSTEM shell. takeown + icacls + binary replacement. Red Team technique.
Discover more Discover more windows
SeRestorePrivilege: From Backup Operator to SYSTEM in 3 Steps
How to abuse SeRestorePrivilege to overwrite system binaries and gain SYSTEM shell. ImagePath hijacking, DLL sideloading, persistent backdoor. Red Team technique.
Discover more Discover more windows
SeBackupPrivilege: Hash dump and full domain with SAM, SYSTEM and NTDS.dit
PrivEsc with SeBackupPrivilege on Windows and Active Directory: SAM, SYSTEM, and SECURITY extraction, offline dump with secretsdump, access to NTDS.dit, and real-world impact on compromised domains.
Discover more Discover more windows
SeAssignPrimaryTokenPrivilege: Bypassing Potato Attacks Even Without SeImpersonatePrivilege
Privilege escalation with SeAssignPrimaryTokenPrivilege and potato attack bypass on Windows: privilege verification, exploits with GodPotato, JuicyPotato, and SweetPotato, real-world scenarios, common pitfalls, and mitigations.
Discover more Discover more windows
SeLoadDriverPrivilege: Kernel Ring-0 with BYOVD in 3 Steps
SeLoadDriverPrivilege Enabled? Loads a vulnerable driver into the kernel, executes ring-0 code, disables EDR, and bypasses LSASS PPL. Help BYOVD with Capcom.sys and EDRSandBlast.
Discover more Discover more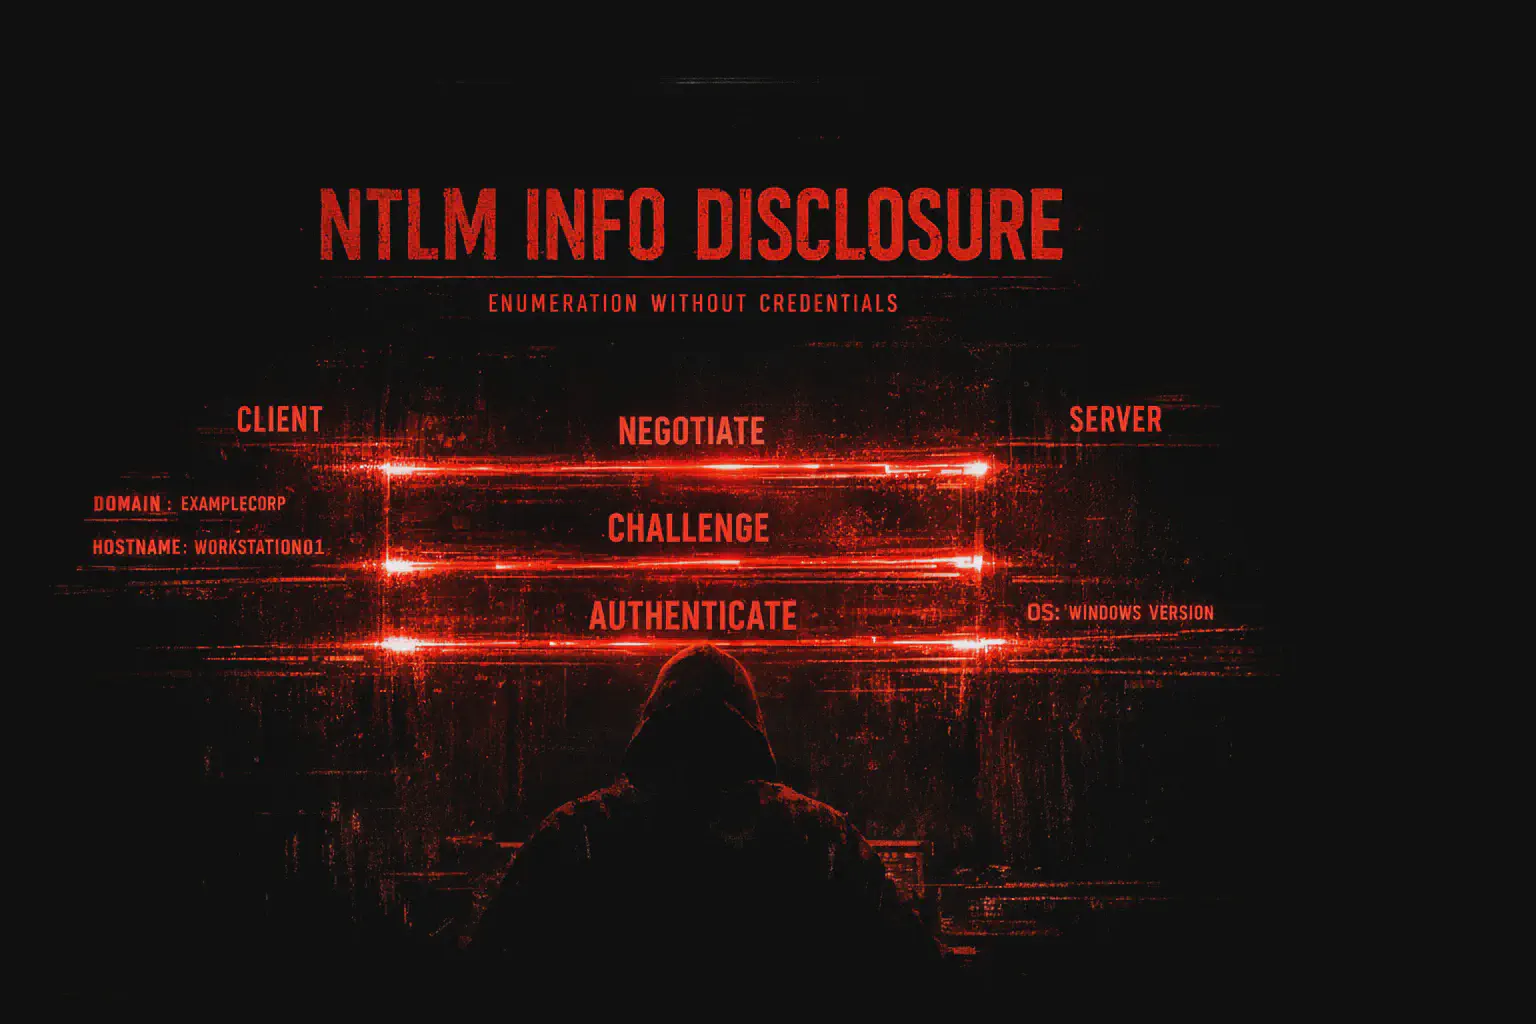 windows
NTLM Information Disclosure: Enumerate Domain, Hostname, and OS Without Credentials
NTLM authentication over HTTP reveals AD domain, NetBIOS name, hostname, and OS version with a single GET, without credentials. This is an essential recon technique for Exchange and IIS red teams. Learn curl, Nmap, Burp, and defenses.
Discover more Discover more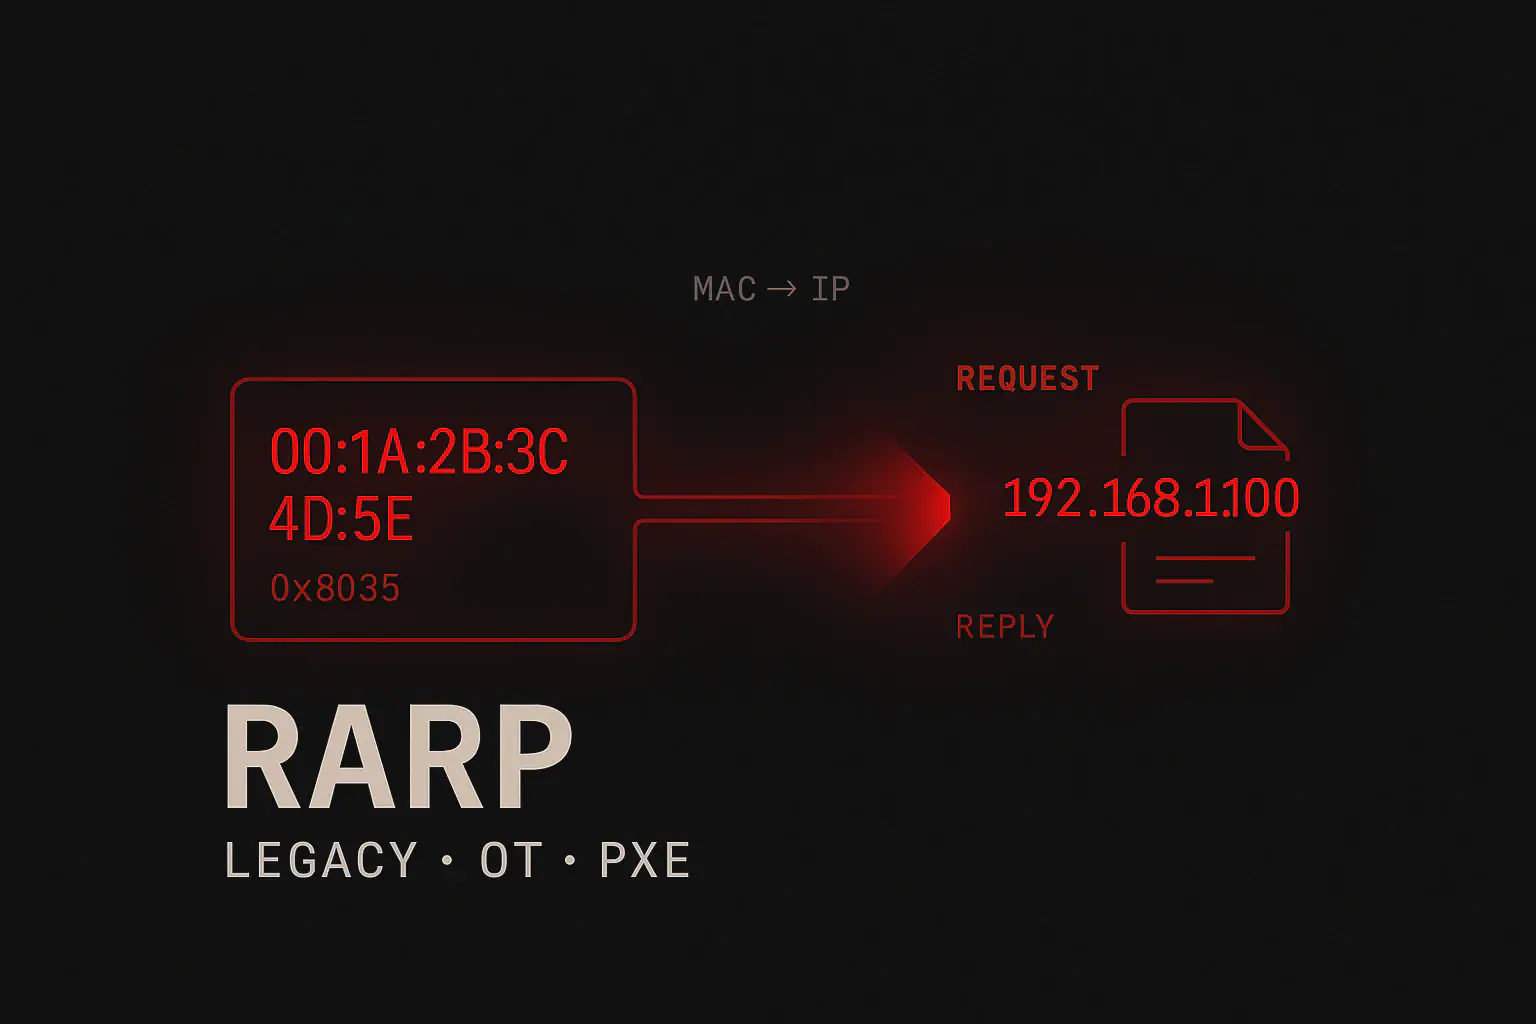 windows
RARP What is it: Reverse ARP that reveals legacy and OT networks
RARP: what it is, how it works, and why it still matters in pentests on legacy networks, OT/ICS, and PXE boot: request/reply, spoofing, boot hijacking, and the differences with ARP and DHCP.
Discover more Discover more windows
DPAPI Attack in Active Directory: Extract Encrypted Passwords and Masterkeys
Complete guide on DPAPI in an Active Directory pentest: masterkey, credential files, Chrome/Edge offline with pypykatz, LSASS dump LOLBin, DSInternals and DonPAPI.
Discover more Discover more windows
ESC15 ADCS (CVE-2024-49019): EKUwu ,PrivEsc & Injection
ESC15 allows privilege escalation in Active Directory via CVE-2024-49019: Application Policy injection in V1 templates alters certificate usages.
Discover more Discover more windows
ESC16 ADCS: CA Without SID Security Extension, Exploit and Fix
ESC16 in AD CS: The CA doesn't include the SID in the certificates. Learn about identification with Certipy, privesc, the ESC16+ESC6 chain, and the mitigation updated to 2026.
Discover more Discover more windows
ESC10 AD CS: PrivEsc, Weak Certificate Mapping in Schannel
ESC10 AD CS leverages Schannel's weak certificate mapping for privilege escalation via LDAPS. Guide with Certipy, UPN manipulation, detection, and mitigations.
Discover more Discover more windows
ESC11 AD CS: NTLM Relay RPC, Certipy & Privilege Escalation
A CA vulnerable to ESC11 can accept NTLM relay via RPC. How to recognize the configuration, privesc, assess the impact on certificates, and prevent abuse.
Discover more Discover more windows
ESC12 AD CS: Privesc via YubiHSM2 and Golden Certificates
ESC12 in AD CS is about YubiHSM2 KSP abuse on Windows CA: privilege escalation in Active Directory and use of Certipy after local compromise.
Discover more Discover more windows
ESC13 AD CS: Privesc with Issuance Policy OID and Certipy
Privilege escalation in Active Directory via ESC13: Certipy detects Issuance Policy OIDs linked to AD groups and explains privilege abuse via Kerberos TGT.
Discover more Discover more windows
ESC14 AD CS: Privesc with altSecurityIdentities and Certipy
Privilege escalation in Active Directory: ESC14 exploits weak X.509 mappings in altSecurityIdentities to impersonate Windows accounts via certificates.
Discover more Discover more windows
ESC8 AD CS: PrivEsc, NTLM Relay Attack with Certipy and PKINIT
ESC8 privilege escalation, leverages NTLM Relay against AD CS /certsrv/ endpoints to obtain privileged certificates. Guide to Certipy and NTLM coercion.
Discover more Discover more windows
ESC9 ADCS: Privilege Escalation via Template without SID Security Extension
ESC9 uses AD CS templates without the SID Security Extension to impersonate privileged users. A practical guide with Certipy and UPN manipulation.
Discover more Discover more windows
ESC3 AD CS: Enrollment Agent and Active Directory Privesc
A practical guide to ESC3 in AD CS: Enumerate templates with Certipy, analyze Enrollment Agent certificates, and dive into privilege escalation in Windows AD.
Discover more Discover more windows
ESC4 AD CS PrivEsc: Template Hijacking with Certipy
ESC4 ADCS Privilege Escalation: Detect weak ACLs on certificate templates, transform them into ESC1s with Certipy, and analyze the path to Domain Admin.
Discover more Discover more windows
ESC5 AD CS: ACL PKI, CA Compromise and Golden Certificate
Learn about ESC5 privilege escalation in Windows Active Directory (AD CS): Enumerate PKI ACLs with Certipy and PowerShell, verify NTAuthCertificates, and mitigations.
Discover more Discover more windows
ESC6 AD CS: SAN Injection with Certipy and Privilege Escalation
PrivEsc ESC6 in AD CS with Certipy: Check EDITF_ATTRIBUTESUBJECTALTNAME2, SAN injection, and differences between ESC9 and ESC16, with practical checks and mitigations.
Discover more Discover more windows
ESC7 AD CS: Certipy, Manage CA and Privilege Escalation
Discover ESC7 in AD CS: Leverage Manage CA permissions with Certipy and privesc, verify the SubCA path, and apply detection and mitigations in AD environments.
Discover more Discover more windows
AD CS Privilege Escalation: All ESC1–ESC16 Techniques with Certipy (Active Directory Attack Guide)
AD CS Privilege Escalation on Active Directory: A Complete Guide to ESC1–ESC16 Techniques with Certipy. Learn how to gain Domain Admin by exploiting misconfigured certificate templates and CAs.
Discover more Discover more windows
ESC1 AD CS: Exploit and Privilege Escalation with Certipy
A practical guide to ESC1 in Active Directory: analyzing vulnerable templates with Certipy, Kerberos authentication, detection, privesc, and security mitigations.
Discover more Discover more windows
ESC2 AD CS: Any Purpose EKU, Enrollment Agent and Certipy
ESC2 in Active Directory Certificate Services: Windows privilege escalation with Any Purpose EKU template, exploits with Certipy and mitigations for secure AD CS.
Discover more Discover more windows
Active Directory Pentesting 2026: Complete Guide to Kerberos, NTLM and Privilege Escalation
Active Directory Pentesting operationally explained: AD architecture, Kerberos vs NTLM, BloodHound, Kerberoasting, AS-REP Roasting, NTLM Relay, ACL abuse, AD CS, DCSync, Golden Ticket, Shadow Credentials and real defenses.
Discover more Discover more windows
Kerberos Active Directory Attacks: Kerberoasting, AS-REP, Golden Ticket
Port 88 Kerberos: Complete guide to Active Directory penetration testing. Learn about Kerberoasting, AS-REP Roasting, Golden Ticket, Silver Ticket and Pass-the-Ticket for privilege escalation and lateral movement.
Discover more Discover more windows
Mimikatz: Complete Guide to Credential Dumping and Active Directory Attack
Mimikatz explained for pentesters: LSASS credential extraction, DCSync, Golden Ticket, pass-the-hash, and Active Directory attacks with practical examples.
Discover more Discover more windows
Smbexec: SMB Remote Execution and Lateral Movement in Active Directory
SMBExec: A Practical Guide to Windows Remote Execution: Stealthy Lateral Movement via SMB Without Disk Files. A Fileless Alternative to PsExec for AD Pentesting.
Discover more Discover more windows
Seatbelt: Windows Enumeration for Post-Exploitation and Situational Awareness
Seatbelt is a Windows enumeration tool that collects system, user, privilege, and configuration information useful for privilege escalation.
Discover more Discover more windows
SharpChrome: Dump Browser Credentials from Windows (DPAPI Abuse)
SharpChrome: Dump Browser Credentials from Windows (DPAPI Abuse)
Discover more Discover more windows
SharpDPAPI: DPAPI Abuse to Decrypt Credentials on Windows
SharpDPAPI allows you to extract and decrypt DPAPI-protected credentials on Windows. This advanced tool is for credential access and lateral movement.
Discover more Discover more windows
SharpUp: Commands and Checks for Windows Privilege Escalation
SharpUp (GhostPack) Guide: Commands, real-world checks (ModifiableServices, AlwaysInstallElevated, DLL hijacking), and how to exploit them for privilege escalation on Windows.
Discover more Discover more windows
Sherlock: Automated Windows Privilege Escalation Checker
Sherlock identifies privilege escalation vulnerabilities on Windows by comparing installed patches and known CVEs. A quick tool for local privilege discovery.
Discover more Discover more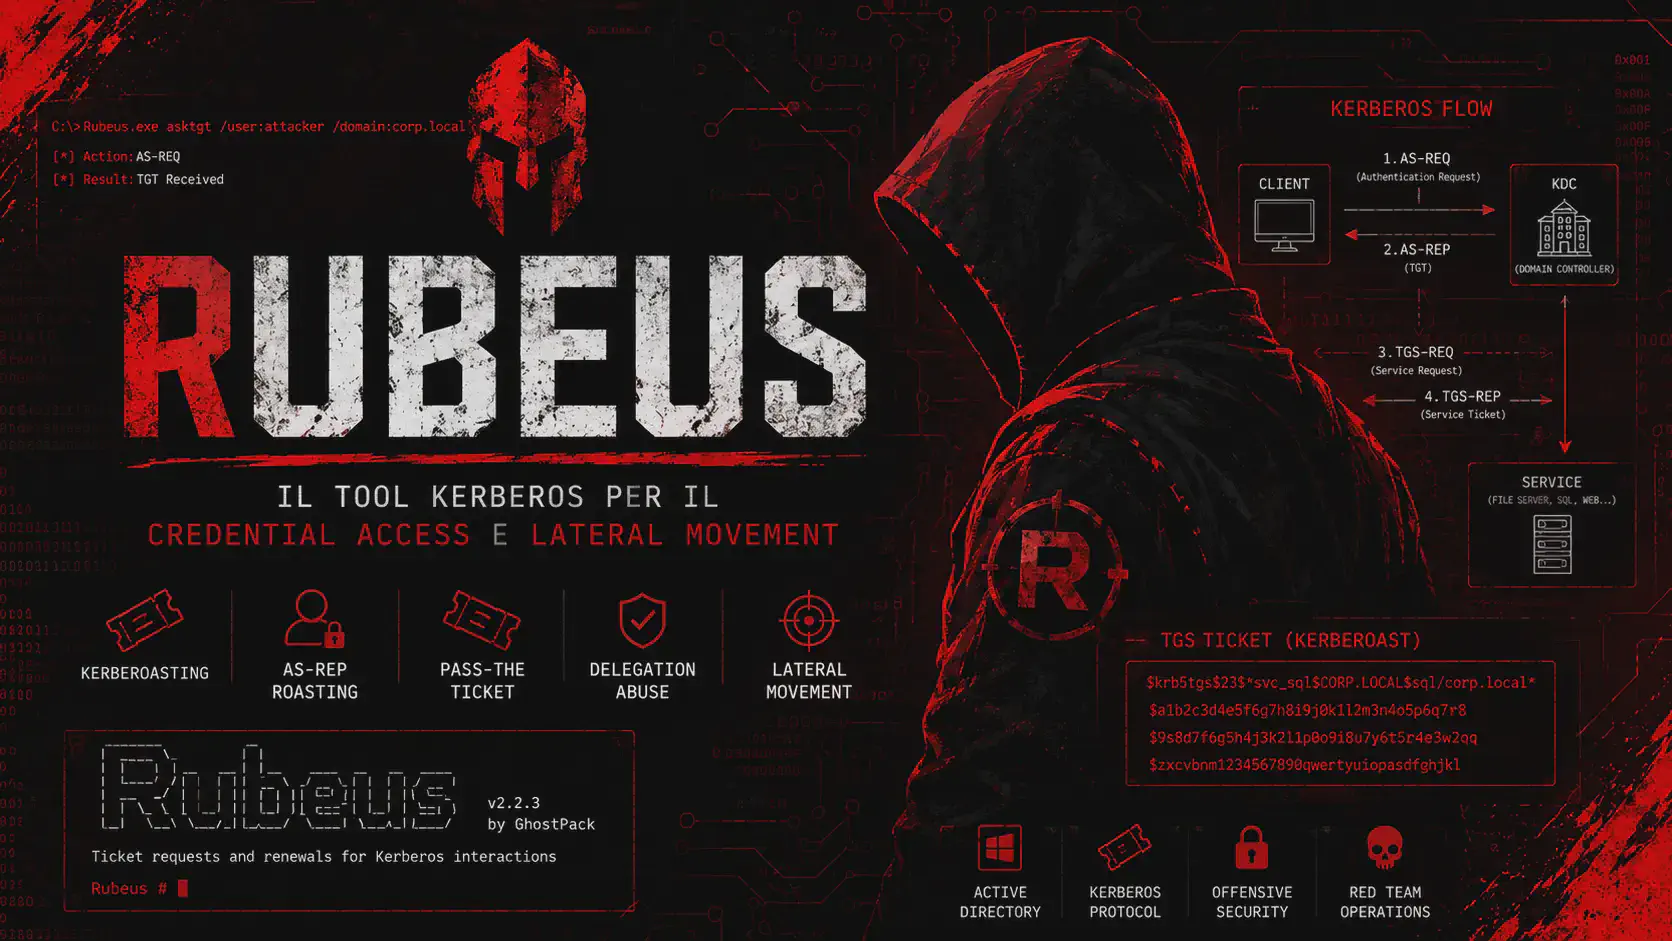 windows
Rubeus: Kerberos Attacks in Active Directory (2026)
Rubeus is the reference C# tool for attacking Kerberos in AD. Discover Kerberoasting, AS-REP Roasting, Pass-the-Ticket, and S4U with real-world detection.
Discover more Discover more windows
Windows Pass-the-Hash: Attack, Operation, and Passwordless Access
Learn Pass-the-Hash (PtH) on Windows: how it works, how to leverage NTLM hashes to gain passwordless access, and real-world lateral movement techniques.
Discover more Discover more windows
PsExec: Remote Command Execution via SMB in Windows Environments
PsExec allows remote command execution on Windows systems via SMB. A key tool for lateral movement and remote administration.
Discover more Discover more windows
JAWS: Windows Post-Exploitation Enumeration for Privilege Escalation
JAWS is a PowerShell script for automatic enumeration on compromised Windows hosts, useful for identifying misconfigurations and privilege escalation vectors.
Discover more Discover more windows
DCSync: Active Directory Credential Dump via Replication Abuse
DCSync is an Active Directory technique that allows credential hash extraction by abusing the domain replication mechanism. It is used post-exploitation to obtain NTLM hashes of privileged users without direct access to the domain controller.
Discover more Discover more windows
Adfind: Advanced Active Directory Enumeration in Penetration Testing
AdFind is a tool for enumerating Active Directory objects via command-line LDAP queries. A practical guide to using it during domain enumeration during a penetration test.
Discover more Discover more windows
Scheduled Task Backdoor: Windows Persistence with Scheduled Tasks in Pentest
Scheduled Task Backdoor: Persistence on Windows via Task Scheduler with schtasks and PowerShell. Stealth techniques, EDR evasion, log detection, and real-world Red Team scenarios.
Discover more Discover more windows
Certutil.exe: Download and Encoding for Living Off The Land on Windows
Practical guide Certutil.exe for Windows penetration testing: file download, Base64 encoding, hash verification and AV bypass. Living off the Land with native tool.
Discover more Discover more windows
MSSQL Pentesting: Port 1433, Enumeration, Attack, and Payload
Learn how to enumerate and join MSSQL (port 1433): pentest for weak credentials, xp_dirtree for NTLM hashes, xp_cmdshell for RCE, and pivoting on linked servers
Discover more Discover more windows
LDAP Port 389: Enumeration and Pentesting in Active Directory
LDAP 389 PORT: Null bind, users, groups and SPNs, exposed credentials, LDAP relay and injection: enumeration techniques and misconfigurations in Active Directory.
Discover more Discover more windows
SMB Port 445: Enumeration and Attacks in a Pentest
SMB Port 445 on Windows Servers: Share enumeration, exploits, NTLM relay, Pass-the-Hash, remote execution, and lateral movement in Active Directory.
Discover more Discover more