
Recon, fingerprinting, OWASP Top 10, and real-world exploit chains: everything you need to destroy lab-style web apps and exams.
- blog
- 107+ Note
- Focus
- OSCP · Red Team
- Structure
- Recon → Exploit
Web Hacking blog
Filters
 web hacking
SQL Injection MySQL: Payload, Cheat Sheet and Techniques
SQL injection on MySQL: cheat sheet with UNION payloads, error-based, blind, time-based, DIOS, RCE via UDF, OOB, WAF bypass and sqlmap commands for pentesting.
Discover more Discover more web hacking
Command Injection: Payload, Bypass and How to Defend Yourself
Learn what Command Injection is, how it works, where it is found, and how to test for it with Burp Suite and Commix: blind techniques, OOB, filter bypass, and defense.
Discover more Discover more web hacking
OAuth 2.0: Tokens, Scope, and Risks of Third-Party Tools | HackITA
How OAuth 2.0 works, what scope and access tokens are, and how to protect your company's social media accounts from token theft in third-party tools.
Discover more Discover more web hacking
SVG XSS and XXE: Attack via Image Upload
An uploaded SVG can execute scripts or read local files. A practical guide to XSS and XXE via SVG: real-world payloads, attack vectors, and mitigations for developers.
Discover more Discover more web hacking
NoSQL Injection: Guide to MongoDB, Payload, Bypass for Pentest
Learn what NoSQL Injection is on MongoDB: payload, authentication bypass, $regex, $where, blind injection, data extraction, and defense techniques.
Discover more Discover more web hacking
RCE (Remote Code Execution): What it is, Vectors and Exploits
RCE in pentesting: Learn the vectors that lead to Remote Code Execution, how to verify them, get a shell, and initiate post-exploitation.
Discover more Discover more web hacking
Recon OSINT: Tool, theHarvester, Shodan and Google Dorks.
Passive OSINT reconnaissance for pentesters: Collect emails, subdomains, exposed devices, and metadata with theHarvester, Google Dorks, Shodan, and Metagoofil.
Discover more Discover more web hacking
Subdomain Enumeration with subfinder, puredns and httpx
Subdomain enumeration pipeline: passive recon with subfinder, brute force with puredns, Alterx permutations, httpx validation and subdomain takeover check.
Discover more Discover more web hacking
Wfuzz: Web fuzzing of directories, parameters, headers, and VHosts
Wfuzz for web fuzzing: directory and parameter commands, VHost discovery, headers, cookies, filters, SecLists, encoders, and WAF bypass techniques.
Discover more Discover more web hacking
XXE Injection (XML External Entity): file read, SSRF and RCE
XXE (XML External Entity) in pentesting: payload for file read, SSRF, Blind XXE OOB and RCE, testing with Burp Suite and Nuclei, prevention in XML parsers.
Discover more Discover more web hacking
Advanced XXE Injection: XML parser, XInclude, SOAP and bypass
Advanced XXE Injection: Identifies XML parsers, compares Java, PHP, Python, and .NET, tests SOAP, XInclude, content-type switching, and targeted bypasses.
Discover more Discover more web hacking
HTTP Security Headers: Guide to CSP, HSTS and Bypass
Learn how to test and configure HTTP security headers: CSP, HSTS, X-Frame-Options, Referrer-Policy and bypass techniques in web pentests.
Discover more Discover more web hacking
Recon Pipeline: OSINT Automation for Bug Bounty and Pentesting
Automated recon pipeline guide: subdomain enumeration, DNS, port scanning, fingerprinting, Nuclei, and secret scanning for bug bounty and pentesting.
Discover more Discover more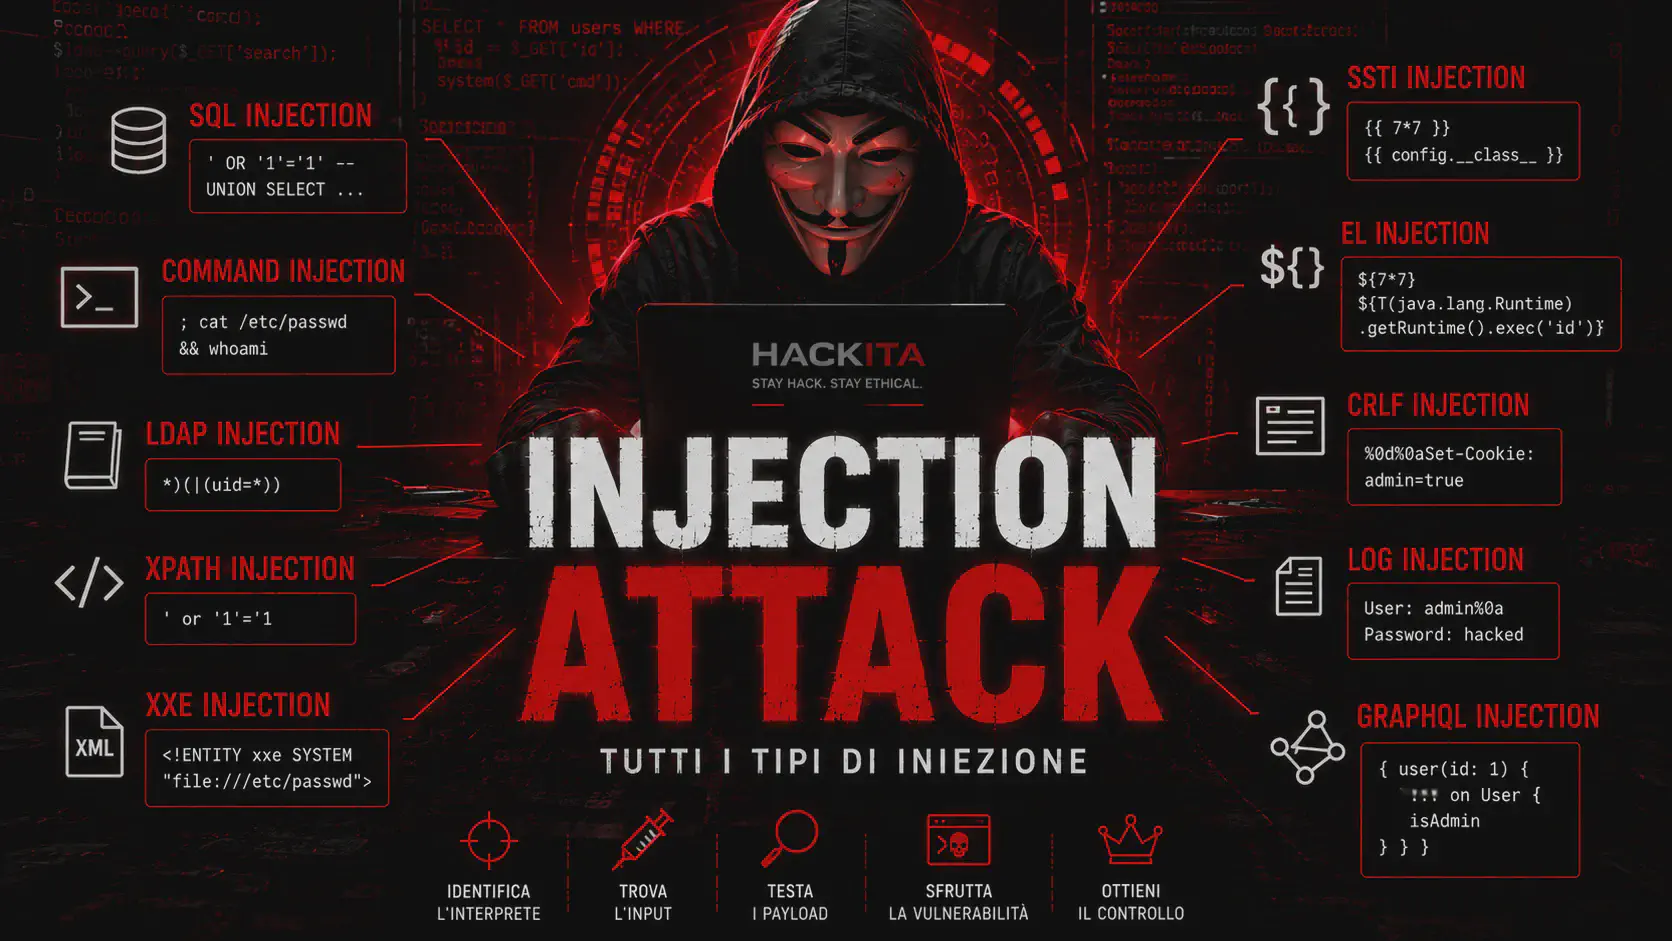 web hacking
Injection Attack: A Complete Guide to Web Injections
A complete guide to injection attacks: SQL injection, command injection, SSTI, XXE, LDAP, NoSQL, and other techniques, with examples, testing, and prevention.
Discover more Discover more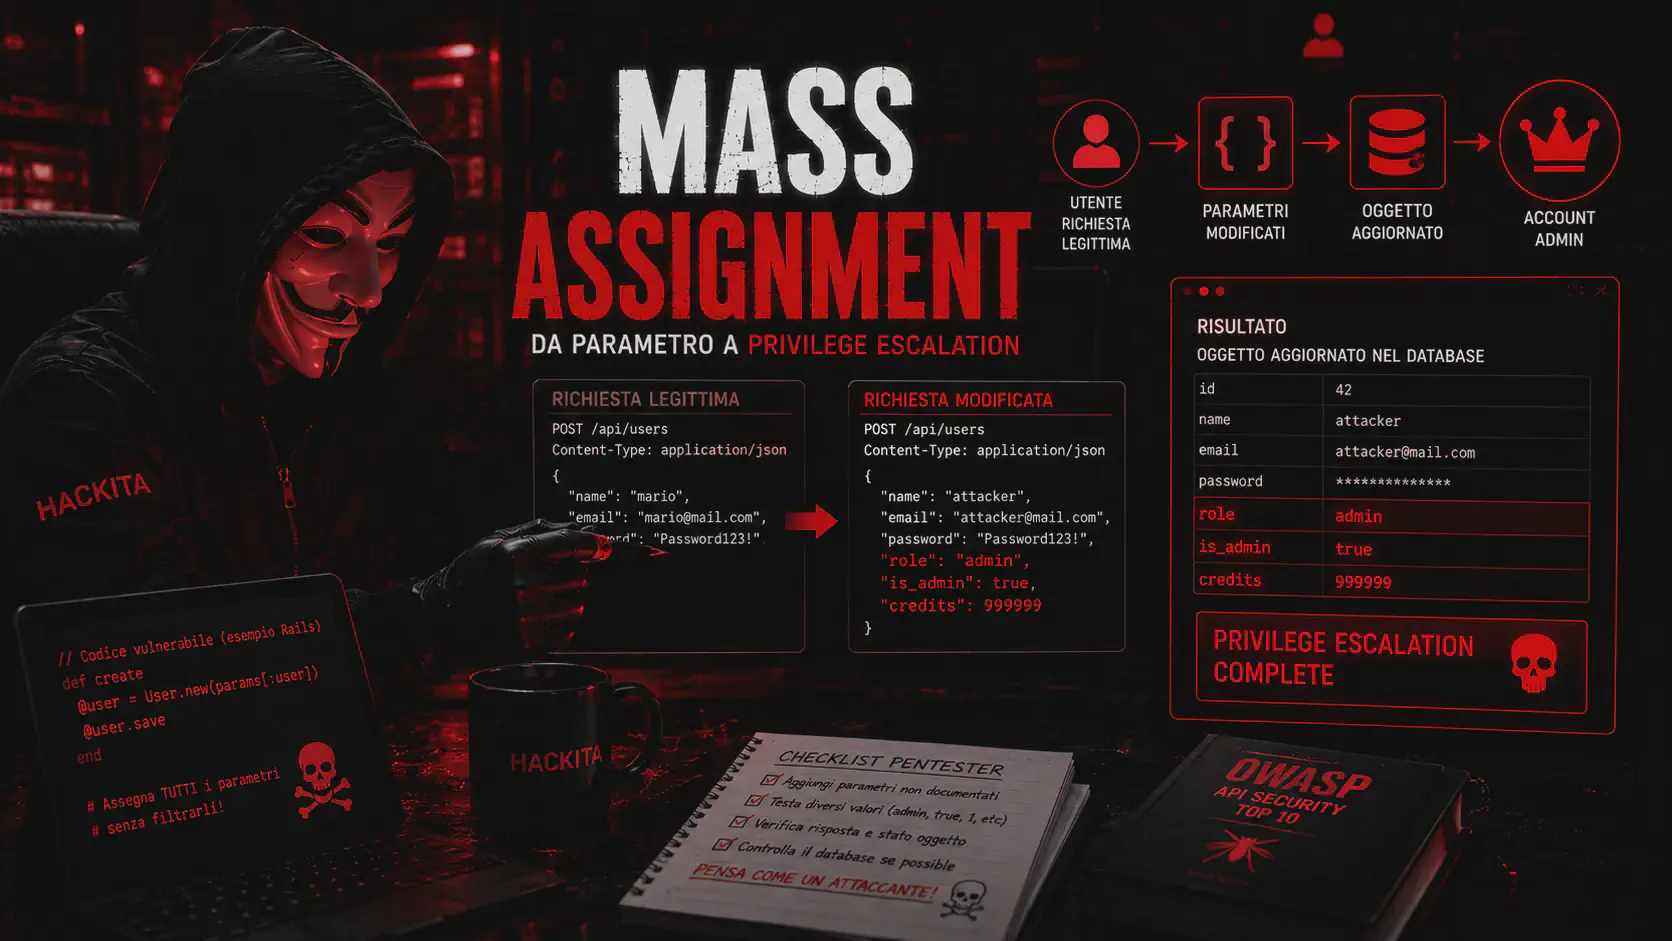 web hacking
Mass Assignment: How to Find and Use It in APIs
Learn what mass assignment is, how to identify it, and how to leverage it in REST APIs, with practical examples for Rails, Laravel, Django, Node.js, and Burp Suite.
Discover more Discover more web hacking
Password Reset Attack: Techniques, Exploits and Account Takeover
Password Reset Attack Guide: Host header poisoning, weak tokens, race conditions, leaks, and practical account takeover techniques for web pentests.
Discover more Discover more web hacking
Broken Authentication: Bypass Login, 2FA and Sessions
OWASP A07 Broken Authentication Guide: username enumeration, brute force, 2FA bypass, session fixation, password reset and credential stuffing for pentests.
Discover more Discover more web hacking
Web Cache Poisoning: Testing, Cache Keys, and Bypass Techniques
Practical guide to Web Cache Poisoning in pentesting: analyze cache keys and unkeyed inputs, test headers and fat GETs with Burp, and apply useful detection and mitigations.
Discover more Discover more web hacking
Broken Access Control: Tests, Examples and Bypass OWASP A01
Practical guide to Broken Access Control OWASP A01:2025: privilege escalation, IDOR and BOLA, force browsing, HTTP methods, header bypass and testing with Burp Suite.
Discover more Discover more web hacking
Twig SSTI and Sandbox Bypass: RCE in Twig, CMS and PHP Filters
Twig SSTI ,detection, payload and RCE: fingerprint vs Jinja2, payload for Twig 2.x and 3.x, filter/map/reduce bypass, sandbox escape, Drupal/Craft CMS and mitigations
Discover more Discover more web hacking
HasSession BloodHound: Session Enumeration and Abuse
HasSession BloodHound: Learn how to enumerate sessions with SharpHound and leverage tokens, credentials, and RDP, with Active Directory detection and mitigations.
Discover more Discover more web hacking
SQL Injection MSSQL: UNION, Blind, Stacked, RCE, Payload
Pentest SQL Injection MSSQL: identify quotes, exploit UNION/blind/time-based/stacked/error-based, bypass WAF, RCE via xp_cmdshell, NTLM hash, linked server.
Discover more Discover more web hacking
2FA Bypass: Techniques, Payloads, and OTP Attacks for Pentesters
2FA bypass: response manipulation, OTP brute force, direct post-login link, SIM swapping, MFA phishing, backup code abuse. Payload for ethical pentesters and hackers
Discover more Discover more web hacking
Deserialization Attack: What It Is, How to Find It, and How It Leads to RCE
Deserialization attack explained from the beginning: what serialization is, why it's dangerous, and how to exploit it in PHP, Java, Python, and .NET with ysoserial and phpggc. A step-by-step guide for beginners and pentesters.
Discover more Discover more web hacking
Windows Privilege Escalation 2026: A Complete Guide to Privilege Tokens (SE*)
A comprehensive map of exploitable Windows privilege tokens in a pentest. From whoami /priv to SYSTEM: cheat sheets, tables, workflows, and links to how-to guides.
Discover more Discover more web hacking
SeSystemEnvironmentPrivilege: PATH Hijacking and UEFI Persistence
Leverages SeSystemEnvironmentPrivilege for PATH hijacking and SYSTEM shell. UEFI persistence that survives disk wipes. Red Team guidance with registry, Process Monitor, and Chipsec.
Discover more Discover more web hacking
SeTrustedCredManAccessPrivilege: RDP Dump and Vault with Mimikatz
Extract RDP passwords and credentials from Credential Manager with SeTrustedCredManAccessPrivilege. Use cmdkey, mimikatz, and SharpDPAPI. Step-by-step Red Team guide.
Discover more Discover more web hacking
Evilginx 3: AiTM Phishing and MFA Bypass for Red Teams
Learn how Evilginx 3 enables AiTM phishing, captures post-MFA cookies, and helps red teams understand MFA-bypass risks in Microsoft 365.
Discover more Discover more web hacking
SeDelegateSessionUserImpersonatePrivilege: Cross-Session Token Stealing on RDS and Citrix
How to exploit SeDelegateSessionUserImpersonatePrivilege to impersonate users in active RDS sessions. Cross-session token stealing with NtObjectManager. Privesc and Red Team techniques.
Discover more Discover more web hacking
Account Takeover: Offensive Techniques for Pentesters (2026)
Learn Account Takeover (ATO) techniques for pentesters and red teams. Discover how to bypass MFA, steal tokens, and compromise accounts. Complete guide 2026.
Discover more Discover more web hacking
IDOR: What It Is, How to Find It, and How to Use It — A Complete Guide
IDOR (Insecure Direct Object Reference) explained from a pentester's perspective: how to identify it, how to enumerate it, and how to scale it to account takeovers and data breaches. With real-world examples and a practical checklist.
Discover more Discover more web hacking
Injection Attack: A Complete Guide to All Types of Injection
A complete guide to injection attacks: SQL injection, command injection, LDAP, XPath, SSTI, XXE, CRLF, log injection, EL, NoSQL, and GraphQL. What injection is, how it works, how to find it, and how to exploit it. A hub with links to all the specific guides.
Discover more Discover more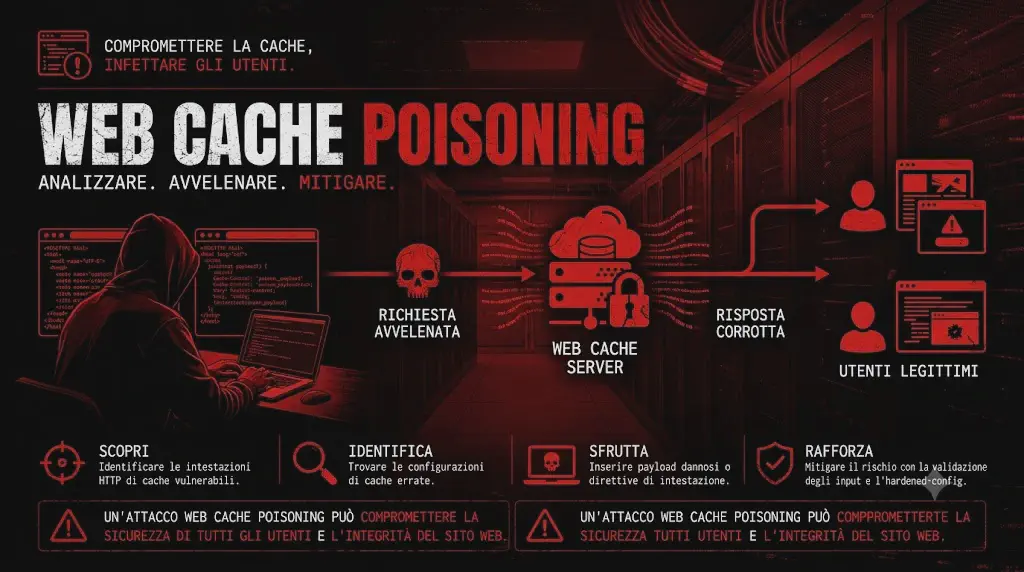 web hacking
Web Cache Poisoning: What It Is, How It Works, and How to Exploit It
A complete guide to web cache poisoning: discover what it is, how cache poisoning works, exploitation techniques (unkeyed inputs, CPDoS), and how to turn it into account takeover. Practical and CDN-specific examples.
Discover more Discover more web hacking
SeDebugPrivilege: Privilege Escalation with Dump LSASS with LOLBins
SeDebugPrivilege Enabled? Two commands to dump LSASS and get NTLM hashes. All with Windows' built-in comsvcs.dll, no disk mimikatz. Red Team technical guide.
Discover more Discover more web hacking
SeImpersonatePrivilege: Privesc and Potato Attack up to SYSTEM
SeImpersonatePrivilege explained with Potato attacks: from IIS or SQL Server to SYSTEM, privilege escalation windows with modern tools used in labs.
Discover more Discover more web hacking
CSP Bypass: How to bypass Content Security Policy in XSS tests
A practical guide to CSP bypass: unsafe-inline, weak nonces, base-uri, object-src, JSONP, AngularJS, dangling markup, and real-world techniques for bypassing Content Security Policy.
Discover more Discover more web hacking
XSS Payload List: Complete cheat sheet for context, bypass and blind XSS
Complete list of XSS payloads for HTML, attributes, JavaScript, DOM, Blind XSS and filter bypass: a practical cheat sheet for pentesters and bug bounties.
Discover more Discover more web hacking
XSS WAF Bypass: How to bypass Cloudflare, AWS WAF and ModSecurity
Practical guide to XSS bypass against real WAFs: Cloudflare, AWS WAF, ModSecurity CRS, encoding evasion, mutated payloads, origin bypass, and techniques used in pentests.
Discover more Discover more web hacking
DOM XSS: What It Is and How to Find Hidden Sources and Sinks in JavaScript
Practical guide to DOM
Discover more Discover more web hacking
Reflected XSS: How to Find It, Exploit It, and Execute the Payload
A complete guide to Reflected XSS: reflection points, context analysis, HTML and JavaScript payloads, link delivery, cookie stealing, dalfox, and real-world exploit techniques.
Discover more Discover more web hacking
XSS Filter Bypass: Payloads and Techniques for Bypassing Server-Side Filters
A practical guide to XSS bypasses: alternative tags, keyword obfuscation, encoding, regex bypass, HTML and JavaScript contexts, and real-world techniques for bypassing server-side filters.
Discover more Discover more web hacking
Stored XSS (Persistent XSS): Exploits, Cookie Theft and Web Worms
Stored XSS Explained: What It Is Cross-site scripting, persistent payloads stored in the database, cookie theft, account takeover, and self-replicating worms in web applications.
Discover more Discover more web hacking
Zip Slip Vulnerability: Path Traversal in ZIP/TAR and RCE via Archive Extraction
Zip Slip Explained: Path Traversal in ZIP and TAR Archives Leads to RCE, Web Shell, and Persistence During File Extraction
Discover more Discover more web hacking
WebSocket Hijacking (CSWSH): Cross-Site WebSocket Hijacking and Real-Time Data Theft
WebSocket Hijacking Explained: CSWSH, Vulnerable Handshake, Missing Origin Check, and Real-Time Data Theft from Chats, Notifications, and Dashboards.
Discover more Discover more web hacking
XPath Injection: Payload, Login Bypass and Blind Attack on XML
XPath Injection Guide: What it is, Pentesting, login bypass payloads, XML data extraction, and blind testing. Discover techniques, tools, secrets, and mitigations.
Discover more Discover more web hacking
Session Hijacking: Cookie Theft, XSS and Session Fixation in Web Apps
Session Hijacking in web pentesting: cookie theft via XSS, session fixation, HTTP sniffing and account takeover. HttpOnly, Secure and SameSite flag analysis.
Discover more Discover more web hacking
Source Code Disclosure: .git Exposed, Commit Credentials, and Git-Dumper
Source Code Disclosure in Pentesting: Exposed .git, git-dumper, credentials in git history, and trufflehog for secrets. From repository dump to cloud takeover.
Discover more Discover more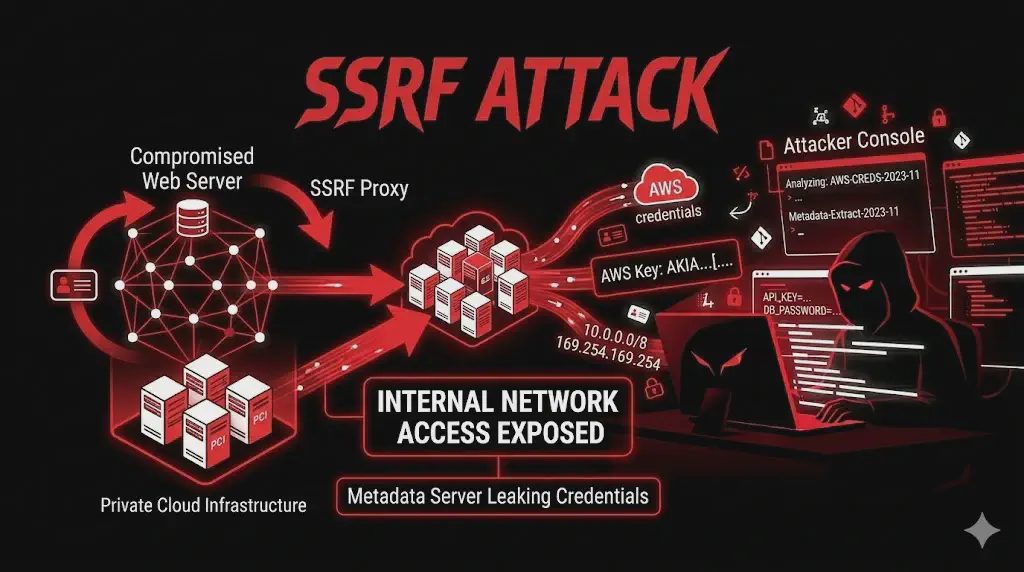 web hacking
SSRF Attack: Server-Side Request Forgery, Cloud Metadata and AWS Credential Theft
The Complete Guide to SSRF: How to Find Server-Side Request Forgery, Bypass IP Filters, Read AWS Metadata, and Get Cloud Credentials.
Discover more Discover more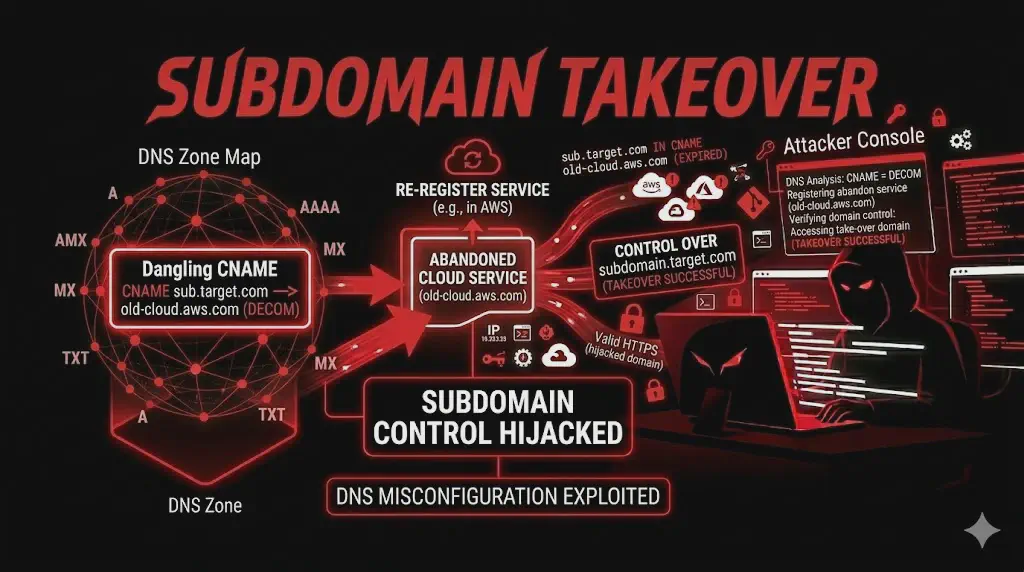 web hacking
Subdomain Takeover: CNAME Dangling, DNS Misconfiguration, and Account Takeover
The Complete Guide to Subdomain Takeover: CNAME Dangling, Defunct Cloud Services, and Subdomain Takeovers on AWS, Heroku, GitHub Pages, and Azure.
Discover more Discover more web hacking
Web Shell PHP: Upload Exploit, Reverse Shell and Persistence on the Server
Complete guide to Web Shells in pentesting: PHP shell upload, reverse shell, WAF bypass and persistence after file upload or LFI.
Discover more Discover more web hacking
Web Application Attacks: A Complete Guide to Vulnerabilities and Exploits
Discover the main web application attacks: SQL Injection, XSS, SSRF, IDOR, CSRF, SSTI, and API abuse. A complete guide for pentesters and red teams.
Discover more Discover more web hacking
Path Traversal: What it is, Payload, WAF Bypass and File Read in Pentesting
Path traversal in web pentesting: payload, WAF bypass, reading /etc/passwd, .env, and cloud credentials. A practical guide with fuzzing and exploitation.
Discover more Discover more web hacking
Web Privilege Escalation: Vertical, Horizontal, and Mass Assignment
Privilege escalation in web apps: mass assignment, role=admin, JWT manipulation, and multi-tenant bypass. Practical pentesting techniques for user-to-admin escalation.
Discover more Discover more web hacking
Race Condition Web: Double Spending, Coupon Abuse, and Parallel Request Attacks
Race Conditions in web apps: double spending, coupon abuse, and limit bypassing with parallel requests. Detection techniques with Turbo Intruder and real-world exploits.
Discover more Discover more web hacking
Remote File Inclusion (RFI): RCE via URL, Wrapper Bypass and SMB Attack
Remote File Inclusion (RFI): RCE via URL, Wrapper Bypass and SMB Attack
Discover more Discover more web hacking
Misc & Infrastructure Attacks: Subdomain Takeover, Race Condition, Request Smuggling
A comprehensive guide to the most underestimated vulnerabilities in web pentesting: Subdomain Takeover, HTTP Request Smuggling, Race Conditions, Deserialization, and Cache Poisoning. Real-world techniques, payloads, and enterprise attack chains.
Discover more Discover more web hacking
OAuth Attack: OAuth Vulnerabilities, Token Theft and Account Takeover
Learn how to exploit OAuth vulnerabilities: redirect_uri manipulation, stateless CSRF, referer token leak, and account takeover in web pentesting.
Discover more Discover more web hacking
Open Redirect: What It Is, How to Use It, and Chain with OAuth and SSRF
Open Redirect in Web Pentesting: Detection, URL and Chain Validation Bypass with OAuth Token Theft, SSRF Bypass, and Credible Phishing. A Practical Guide.
Discover more Discover more web hacking
OS Command Injection: What is it, Argument Injection and RCE on Linux and Windows
OS Command Injection in pentesting: separators, argument injection, exploits on Linux and Windows (curl, tar, ffmpeg, Git, ImageMagick) and post-exploitation.
Discover more Discover more web hacking
LDAP Injection: Bypassing Active Directory Authentication and User Enumeration
Learn how to exploit an LDAP injection in enterprise portals: bypass Active Directory authentication, enumerate users, and extract sensitive attributes from the corporate directory.
Discover more Discover more web hacking
Log Injection: Log Forging, Log Poisoning and RCE via LFI
Learn how to exploit a log injection in web pentesting: log forging for anti-forensics, log poisoning combined with LFI to achieve remote code execution, and the historical Log4Shell case study.
Discover more Discover more web hacking
File Upload Attack: Bypass, Polyglot and Web Shell
Learn how to exploit a file upload attack in web pentesting: extension bypass, Content-Type, magic bytes, polyglot, and RCE via web shell.
Discover more Discover more web hacking
GraphQL Attacks: Introspection, Batching and Data Breach
Find out how to test GraphQL in web pentesting: introspection, batching, authorization bypass, IDOR, brute force and data leak via query.
Discover more Discover more web hacking
HTTP Header Injection: Host Poisoning and X-Forwarded-For
Find out how to exploit HTTP Header Injection in web pentesting: Host Header Poisoning, X-Forwarded-For bypass, cache poisoning and reset password takeover.
Discover more Discover more web hacking
HTTP Request Smuggling: Desync, Cache Poisoning and Cookie Theft
Learn how to test HTTP Request Smuggling in web pentesting: CL.TE, TE.CL, proxy-backend desync, cache poisoning, and cookie theft.
Discover more Discover more web hacking
Local File Inclusion (LFI): Attacks, Payloads, RCE & Bypass
Learn how the LFI vulnerability works: file reading, PHP wrapper, filter chain, and log poisoning, with exploitation techniques and countermeasures in the pentest.
Discover more Discover more web hacking
SSTI (Server-Side Template Injection): Detection, Payload, Twig, Jinja2 and RCE
A practical guide to SSTI: detection, template engine fingerprinting, real payloads, Jinja2, Twig, FreeMarker, sandbox bypass, and RCE.
Discover more Discover more web hacking
CORS Misconfiguration: Complete Guide to Exploit, Bypass and Data Theft in APIs
CORS Misconfiguration in APIs: Learn how to identify, exploit, and demonstrate data theft with origin reflection, null origin, common bypasses, and real-world PoCs with curl and JavaScript.
Discover more Discover more web hacking
CRLF Injection: Header Injection, XSS and Cache Poisoning
Find out how to exploit a CRLF injection in web pentesting: header injection, HTTP response splitting, session fixation and cache poisoning.
Discover more Discover more web hacking
CSRF Attack: Real Token, SameSite and Bypass
Learn how to detect and test a CSRF attack in web pentesting: HTML PoC, token bypass, SameSite, JSON API, and account takeover.
Discover more Discover more web hacking
Expression Language Injection (EL): SpEL, OGNL, MVEL and RCE Java
Learn what Expression Language Injection is and how to leverage it in Java apps: SpEL, OGNL, Spring, Struts2, RCE, and real-world cases like Equifax.
Discover more Discover more web hacking
File & Path Attacks: LFI, Upload and Path Traversal
Guide to file & path attacks in web pentesting: path traversal, LFI, file upload, web shell, Zip Slip, backup exposure and file read.
Discover more Discover more web hacking
Auth & Access Control: A Complete Guide to Pentesting
A complete guide to authentication and access control in web pentesting: IDOR, JWT attacks, CSRF, 2FA bypass, password reset, and privilege escalation.
Discover more Discover more web hacking
Backup Exposure: SQL, .env and ZIP Dumps Exposed
Learn how to find exposed backup files in web pentesting: SQL dumps, .env, ZIP, and config.bak with feroxbuster, ffuf, and real-world techniques.
Discover more Discover more web hacking
Business Logic Flaw: What It Is and How to Find It
Learn what a business logic flaw is and how to spot it in web pentesting: negative pricing, coupon abuse, step bypass, and workflow flaws.
Discover more Discover more web hacking
Clickjacking: What It Is and How to Find It in Web Pentesting
Learn what clickjacking (UI Redressing) is and how to spot it in web pentesting: invisible iframes, X-Frame-Options, CSP frame-ancestors and real PoCs.
Discover more Discover more web hacking
Arbitrary File Read: Exploit, WAF Bypass and Cloud Takeover (2026 Pentesting Guide)
Arbitrary File Read exploit in pentesting: Read sensitive Linux and Windows files, bypass WAF, /proc/self/environ, cloud credentials, and escalate to cloud takeover.
Discover more Discover more web hacking
Brute Force Attack: Meaning, Techniques, Tools, Bypass
Brute Force attacks in penetration testing: password cracking, credential stuffing, wordlist, Hydra, Burp Intruder and bypass rate limit in systems with auth.
Discover more Discover more web hacking
API Rate Limit Bypass: Pentesting Techniques to Bypass Throttling (2026)
Rate Limit Bypass API explained operationally: header rotation with X-Forwarded-For, endpoint switching, HTTP method tampering, Unicode bypass, race conditions and GraphQL batching.
Discover more Discover more web hacking
API Security: A Complete Guide to API Attacks and Pentesting (SSRF, GraphQL, BOLA, CORS)
API security and penetration testing of modern APIs: SSRF, GraphQL attacks, BOLA/IDOR, CORS misconfiguration, mass assignment, and rate limit bypass. A comprehensive guide with real-world payloads and techniques.
Discover more Discover more web hacking
API Versioning Attack: Exploiting Forgotten v1 Endpoints in API Pentesting (2026)
API Versioning Attack Operationally Explained: How to find legacy v1 API endpoints, bypass rate limits and authentication, and exploit deprecated APIs during a penetration test.
Discover more Discover more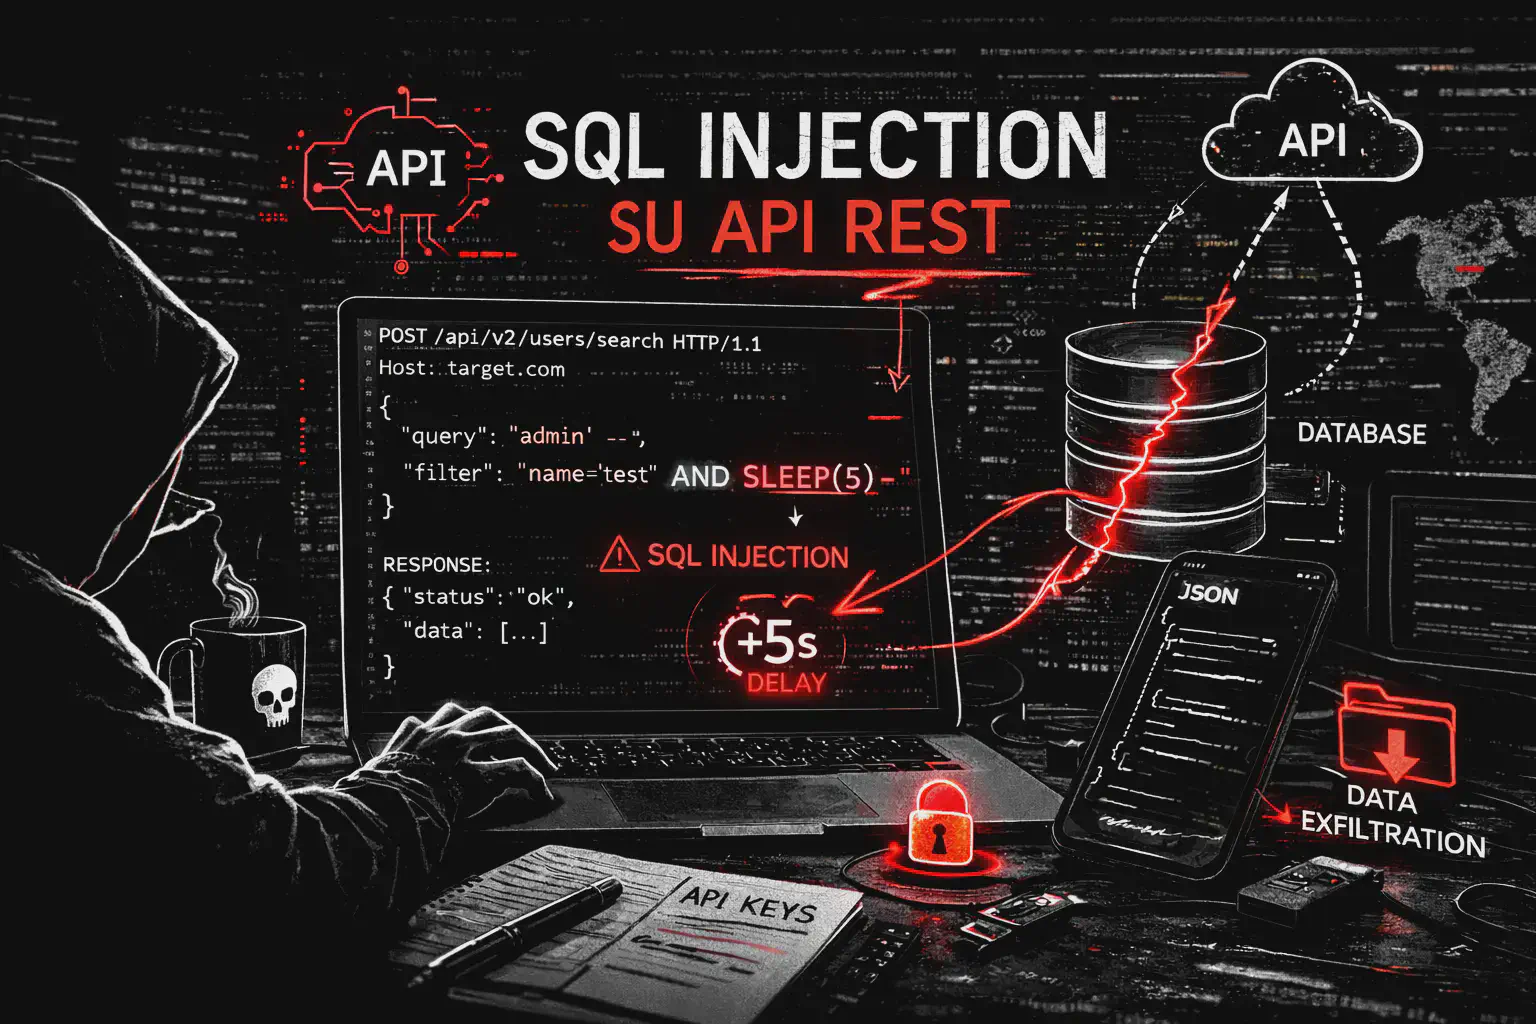 web hacking
SQL Injection on REST API and GraphQL: JSON Body, Header Injection and SQLMap (2026 Guide)
SQL Injection on REST API: JSON body injection, GraphQL SQLi, header injection and WAF bypass. Practical guide with SQLMap, API fuzzing and real exploitation.
Discover more Discover more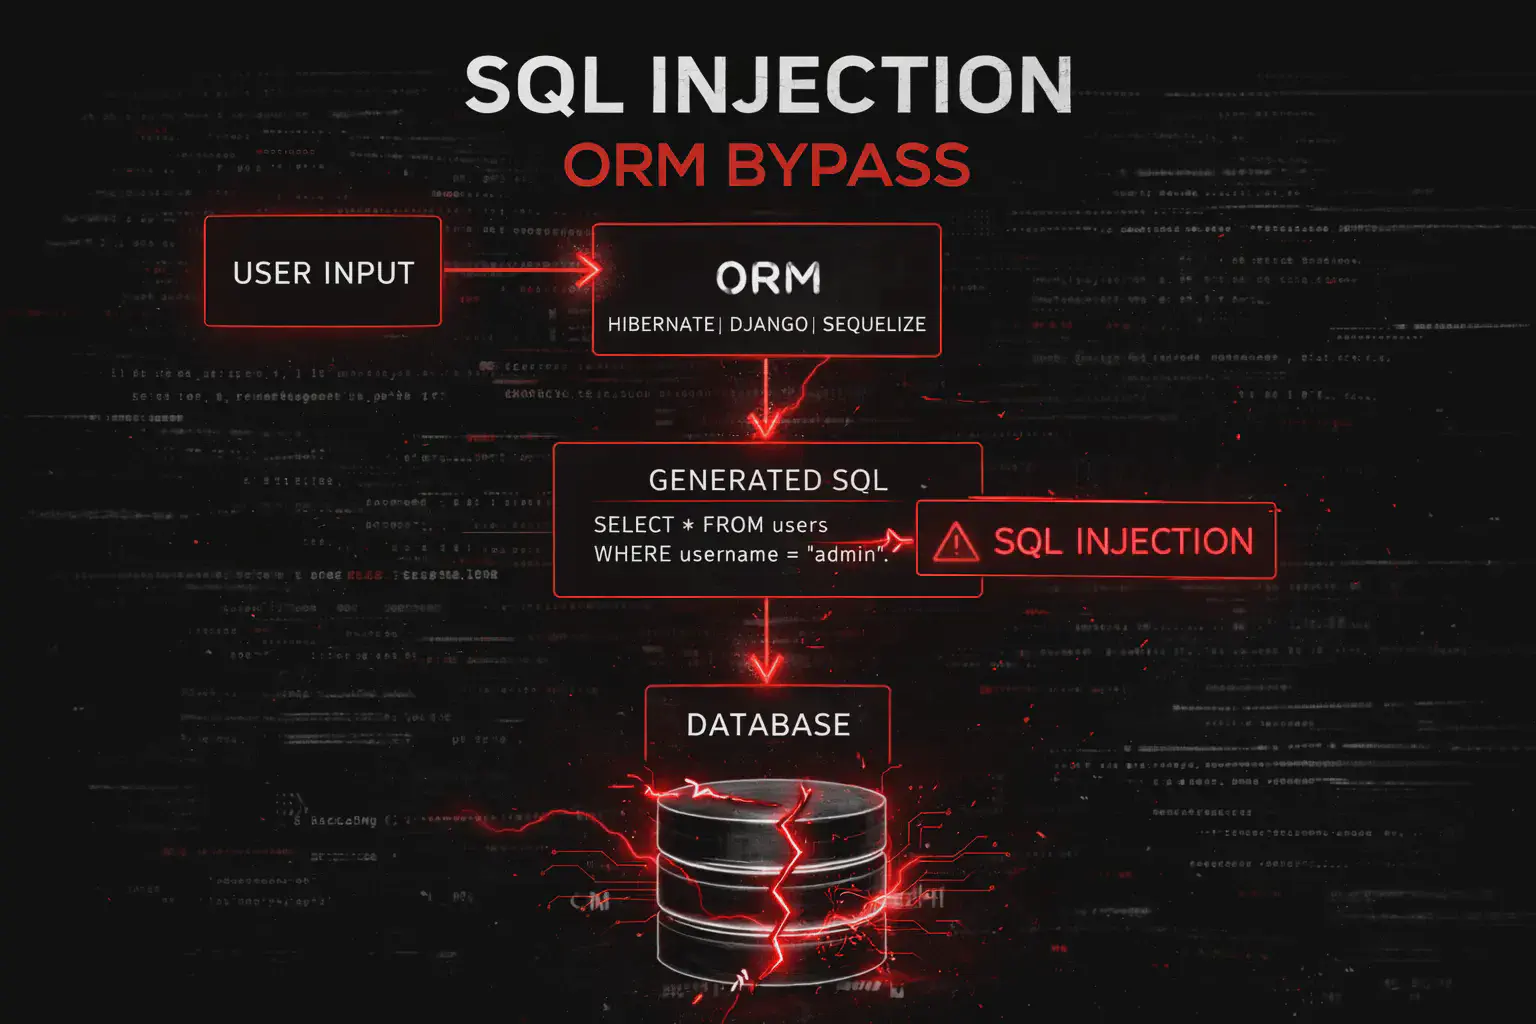 web hacking
SQL Injection on ORM: Django, Laravel, Hibernate and Sequelize
SQL Injection on ORM: Vulnerabilities in Django, Laravel, Hibernate, and Sequelize. Raw queries, extra(), orderByRaw, and real-world exploitation with practical examples.
Discover more Discover more web hacking
Time-Based SQL Injection: How to Extract Data Without Output
Time-Based SQL Injection explained with real payloads: SLEEP, pg_sleep, WAITFOR DELAY, heavy query, Python script and SQLMap. Complete exploitation guide 2026.
Discover more Discover more web hacking
Blind SQL Injection: Boolean-Based Extraction with SQLMap (2026 Guide)
Blind SQL Injection: boolean-based detection, extraction with SUBSTRING and ASCII, binary search and full automation with SQLMap for database dumps, credentials and escalation.
Discover more Discover more web hacking
Classic SQL Injection: UNION SELECT and Error-Based (2026 Operational Guide)
Classic SQL Injection (In-Band): practical guide to UNION SELECT and Error-Based with ORDER BY, data extraction, WAF bypass, SQLMap and complete step-by-step database dump.
Discover more Discover more web hacking
Phishing: Techniques, Types, and Defenses in 2026
Phishing explained technically: spear phishing, credential harvesting, OAuth phishing, MFA bypass, and practical defenses for businesses and users.
Discover more Discover more web hacking
S3Scanner: Enumeration and Misconfiguration Detection on Amazon S3
S3Scanner: Enumeration and Misconfiguration Detection on Amazon S3
Discover more Discover more web hacking
Recon-ng: Modular OSINT Framework for Advanced Reconnaissance
Recon-ng is a modular OSINT framework with a Metasploit-like interface. Ideal for automated collection of domains, emails, and external assets.
Discover more Discover more web hacking
ReconSpider for Kali: Web Recon and Automated OSINT
ReconSpider is an OSINT tool for automating web reconnaissance and intelligence gathering on domains, IPs, emails, metadata, and other public sources.
Discover more Discover more web hacking
Nuclei: High-Speed Template-Based Vulnerability Scanner
Nuclei: High-Speed Template-Based Vulnerability Scanner
Discover more Discover more web hacking
Nikto: Web Server Vulnerability and Misconfiguration Scanner
Nikto is a web scanner for finding known vulnerabilities, sensitive files, misconfigurations, and outdated software on HTTP/HTTPS servers.
Discover more Discover more web hacking
Eyewitness: Visual Recon and Screenshot Automation for Large-Scale Web Triage
Eyewitness automates screenshots and analysis of web and RDP services. Rapid visual recon identifies admin panels and exposed attack surfaces.
Discover more Discover more web hacking
Feroxbuster: Fast and Recursive Directory Bruteforcing for Web Hacking
Feroxbuster is a high-performance directory and content discovery tool. It features recursive bruteforce, multi-threading, and proxy support for advanced web testing.
Discover more Discover more web hacking
FOCA: Metadata Extraction and OSINT on Documents for Information Gathering
FOCA is an OSINT tool for extracting metadata from public documents, mapping internal infrastructure, and identifying exposed users, servers, and paths.
Discover more Discover more web hacking
Gitrob: OSINT and Secret Discovery on GitHub Repository
Gitrob scans GitHub repositories to identify sensitive files and exposed credentials. A useful tool for reconnaissance and secret hunting.
Discover more Discover more web hacking
Gophish: Phishing Framework for Simulation and Red Team
Gophish is an open-source platform for phishing simulation and red team engagement. It offers centralized campaign management, tracking, and reporting.
Discover more Discover more web hacking
Amass: Advanced Subdomain Enumeration for Reconnaissance and Attack Surface Mapping
Amass is an OSINT and active reconnaissance tool for enumerating subdomains, mapping external assets, and analyzing DNS relationships. A practical guide to its use during attack surface discovery during a penetration test.
Discover more Discover more web hacking
Aquatone: Visual Recon and Automatic Screenshots for Subdomain Enumeration
Aquatone is a visual reconnaissance tool that automatically captures screenshots of hosts and subdomains discovered during the recon phase. It's ideal for quickly mapping web surfaces in penetration tests.
Discover more Discover more web hacking
Dirsearch: Directory and File Enumeration for Web Application Testing
Dirsearch is a tool for enumerating hidden directories and files on web applications using custom wordlists. A practical guide to its use during web reconnaissance during a penetration test.
Discover more Discover more web hacking
Gobuster: Directory, DNS and Virtual Host Bruteforcing for Web Enumeration
Gobuster is a fast tool for brute-forcing directories, DNS, and virtual hosts. A practical guide to using it for web enumeration during a penetration test.
Discover more Discover more web hacking
BeEF: Complete Guide to the Browser Exploitation Framework
BeEF's practical guide to browser exploitation: victim hooks, compromised browser control, and client-side post-exploitation. Transform XSS into persistent access.
Discover more Discover more web hacking
Burp Suite: Guide to Web Application Penetration Testing
Burp Suite: How to use it in web penetration testing: discover Proxy, Repeater, Intruder and Scanner and how to test SQLi, XSS, CSRF, API, authentication and secrets.
Discover more Discover more web hacking
SQLMap: Complete Guide to SQL Injection Automation and Database Exploitation
Complete guide to SQLMap for SQL injection automation: detection, exploitation, database enumeration, WAF bypass and UNION, boolean and time-based techniques.
Discover more Discover more web hacking
XSS (Cross-Site Scripting): Exploits, Payloads and Bypasses
XSS (Cross-Site Scripting): complete guide to reflected, stored and DOM-based XSS, payloads, advanced filter bypasses, exploitation and defense of web applications.
Discover more Discover more web hacking
JWT Attacks: 10 Pentests, Vulnerabilities, and How to Defend Yourself
Practical guide to JWT attacks: alg none, weak HMAC keys, algorithm confusion, kid, jku and jwk, claim, refresh token, terminal tools and mitigations.
Discover more Discover more web hacking
WordPress xmlrpc.php: Attacks & Exploits for Pentest (2026)
Learn how to verify xmlrpc.php in WordPress, analyze brute force and pingbacks, assess SSRF risks, and secure your endpoint during a pentest.
Discover more Discover more