
nmap, ffuf, Burp, Python: configurations, aliases, and scripts you'll actually use every time you attack a machine.
- blog
- 114+ Note
- Focus
- OSCP · Red Team
- Structure
- Recon → Exploit
Tools blog
Filters
 tools
OpenSSL: Tools for TLS, Certificates, and Encryption
OpenSSL for TLS, X.509, RSA, and ECDSA certificates, PKI, s_client, and encryption. Practical commands for Linux, Windows, troubleshooting, and pentesting.
Discover more Discover more tools
Dradis Framework: Reporting, Findings, and Pentest Automation
Discover Dradis Framework: import findings from Nessus, Nmap, and Burp, organize evidence, and generate consistent pentest reports. A practical guide.
Discover more Discover more tools
JTAG: What It Is, How It Works, and How to Use It in Hardware Pentesting
What is JTAG and how does it work? Learn about pins, JTAGulator, OpenOCD, firmware dumps, and the risks of an exposed JTAG interface in hardware pentesting.
Discover more Discover more tools
Nessus: Complete Guide to Scanning, Installation, and Vulnerabilities
Nessus Guide: Installation, Nessus Essentials, vulnerability scans, credentialed scans, policies, tuning, and reporting. The complete vulnerability assessment workflow.
Discover more Discover more tools
Sliver C2: Guide to Listeners, Beacons, Implants and Armory
Configure Sliver C2 for Red Team: installation, mTLS/HTTP/DNS listener, implant, beacons and sessions, Armory, BOF, pivoting, OPSEC, detection and cleanup.
Discover more Discover more tools
Cobalt Strike: What It Is, How It Works, Beacon, and Malleable C2
Learn how Cobalt Strike works in the Red Team: Team Server architecture, Beacon, listener, Malleable C2, post-exploitation and main detection techniques.
Discover more Discover more tools
DirBuster on Kali: brute force directory with GUI and wordlist
Use DirBuster on Kali to find hidden directories and files: GUI and headless configuration, wordlist, recursion, soft-404, and comparison with ffuf and feroxbuster.
Discover more Discover more tools
ngrok Reverse Shell: TCP tunnels and Metasploit in the Pentest
Use ngrok in penetration testing to create TCP/HTTPS tunnels behind NATs and firewalls, receive reverse shells with Netcat or Metasploit, and evaluate OPSEC limits.
Discover more Discover more tools
XSSer: XSS Scanner, Payload, Fuzzing and WAF Bypass
Practical guide to XSSer for testing XSS vulnerabilities: installation, GET/POST scanning, payload, fuzzing, encoding, WAF bypass and results reporting.
Discover more Discover more tools
WPScan: WordPress Pentest, Enumeration and Vulnerabilities
A practical guide to WPScan for WordPress pentesting: installation, scanning, plugin, theme, and user enumeration, vulnerabilities, API tokens, and brute force.
Discover more Discover more tools
renameMachine.py: NoPac and sAMAccountName Spoofing
Guide to impacket-renameMachine to change the sAMAccountName of account computers and understand the NoPac chain with CVE-2021-42278 and CVE-2021-42287.
Discover more Discover more tools
ticketer.py: Golden and Silver Ticket Kerberos with Impacket
Impacket-ticketer guide to forge Golden and Silver Kerberos Tickets with NTLM hashes or AES keys, customize PAC, and save ticket ccache.
Discover more Discover more tools
smbserver.py: SMB Server for File Transfer and NTLM
A guide to impacket-smbserver for creating an SMB share on Kali, transferring files, registering NTLM authentication, and managing SMB2, logins, and logging.
Discover more Discover more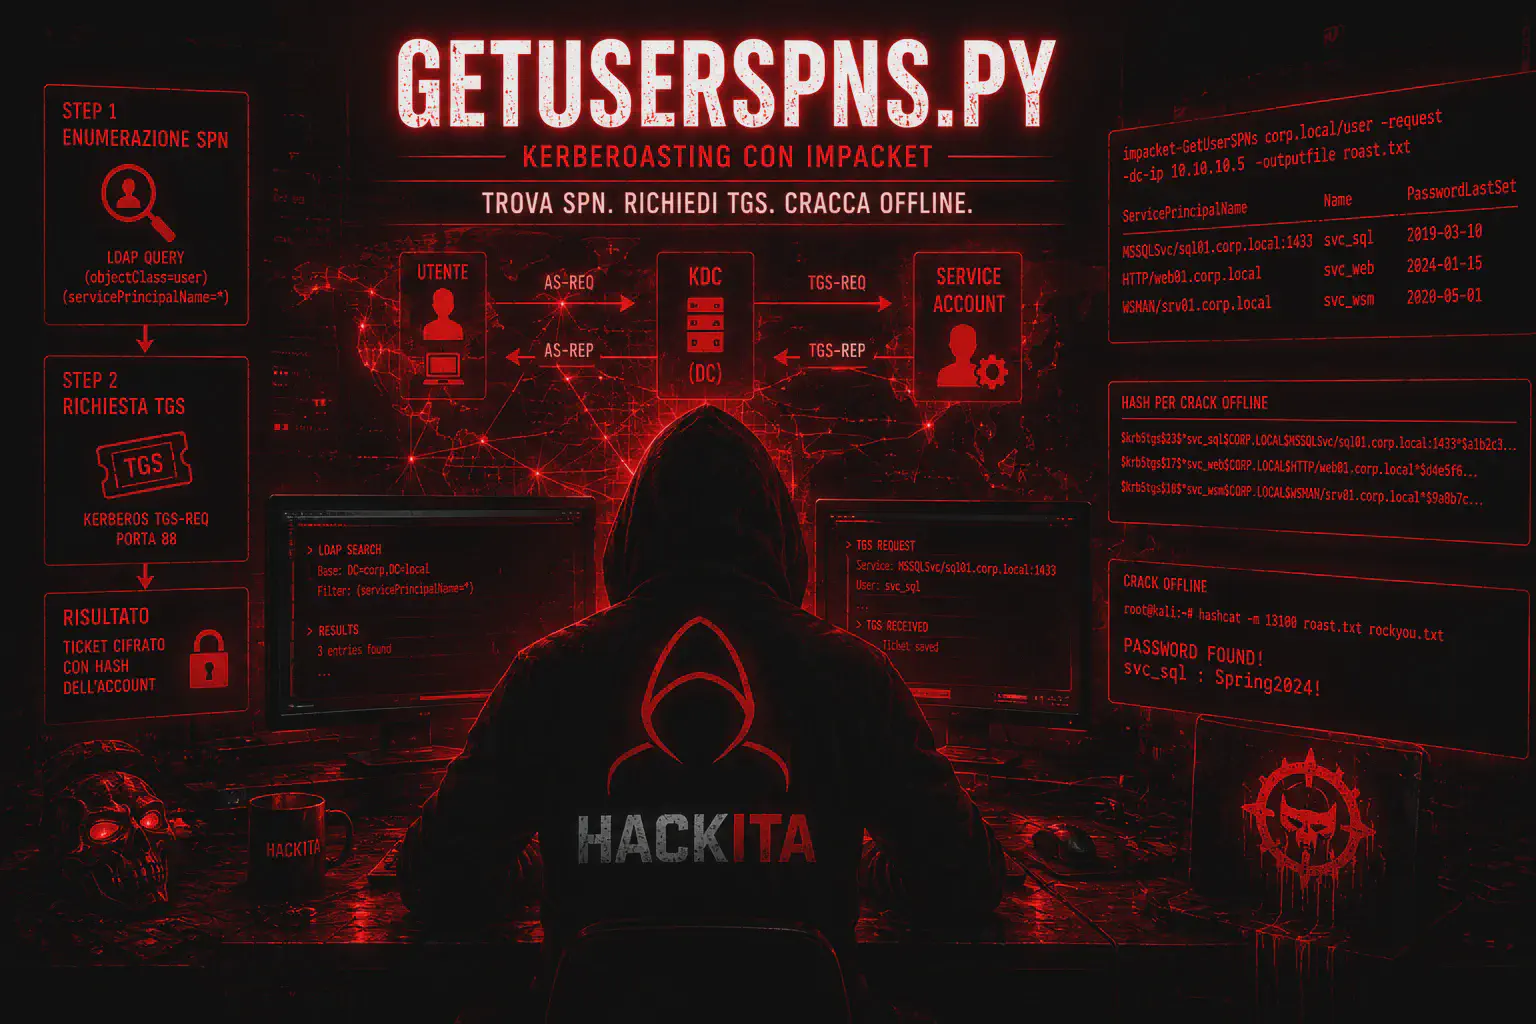 tools
GetUserSPNs.py: Kerberoasting and TGS with Impacket
How to use impacket-GetUserSPNs to enumerate accounts with SPNs and request Kerberos TGS with passwords, NTLM hashes, caches, or AES keys for Windows Active Directory
Discover more Discover more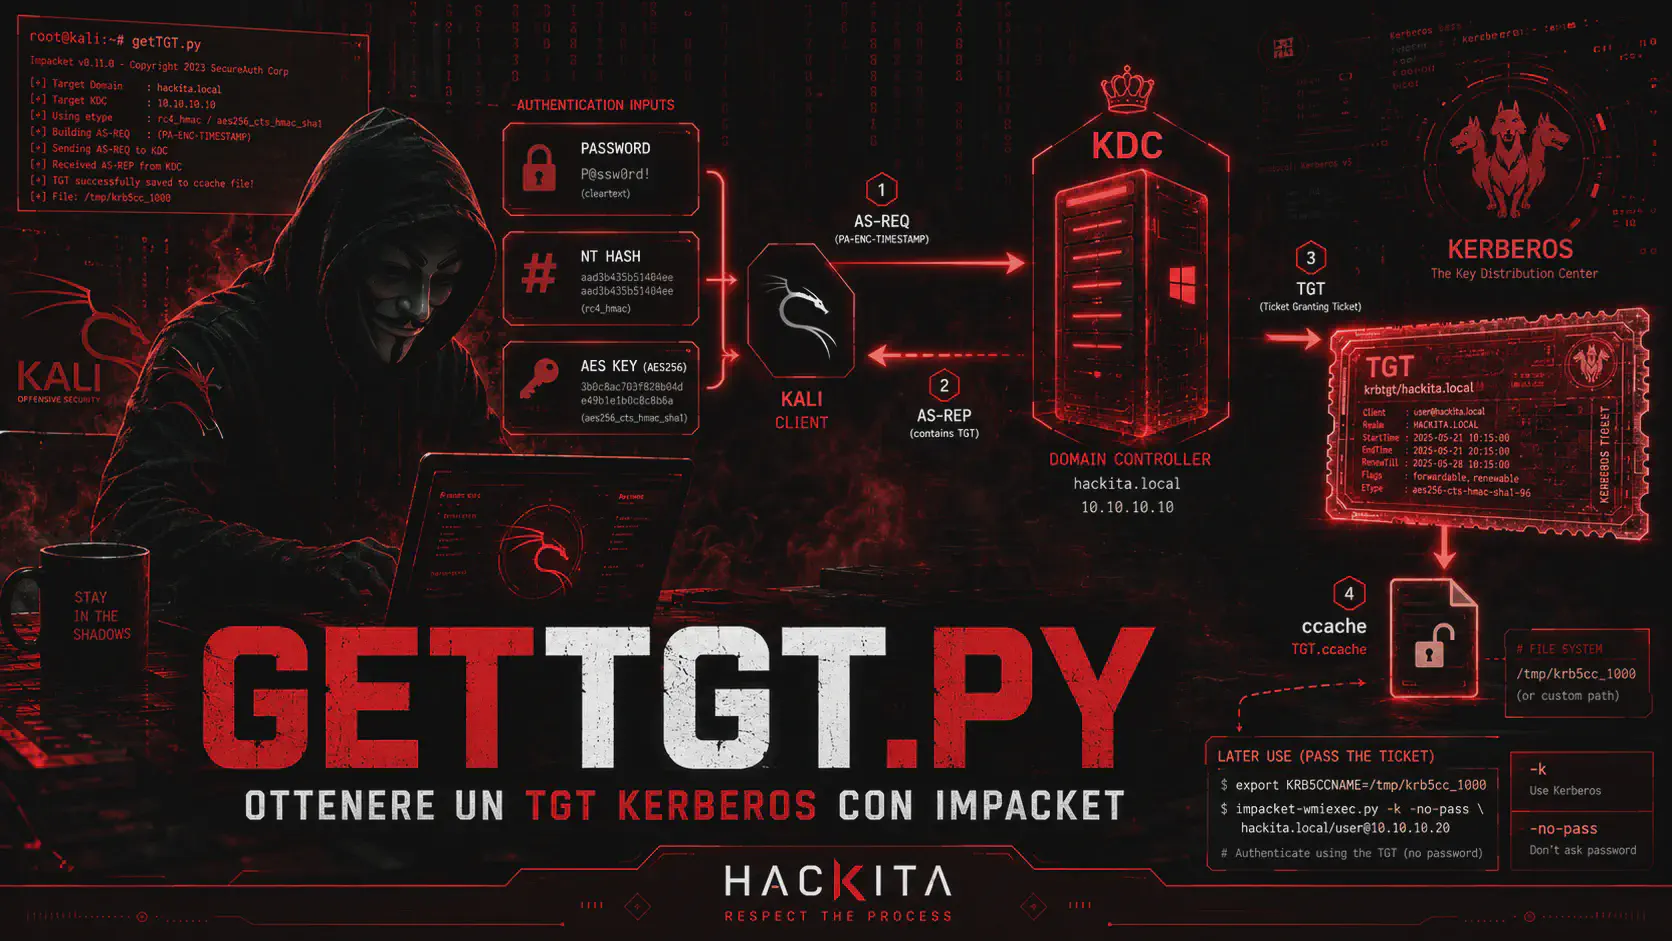 tools
getTGT.py: Getting a Kerberos TGT with Hash or AES
How to use impacket-getTGT to request a Kerberos TGT and save it in ccache format using a password, NTLM hash, or AES key in Active Directory.
Discover more Discover more tools
GetADComputers.py — Enumerate Active Directory Computers with Impacket
How to use impacket-GetADComputers to enumerate Active Directory computers via LDAP, -resolveIP ,auth with password, NTLM hash, Kerberos, ccache or AES keys.
Discover more Discover more tools
GetLAPSPassword.py: Recover LAPS Passwords with Impacket
Impacket's GetLAPSPassword.py guide for recovering encrypted Legacy LAPS and Windows LAPS passwords from Active Directory with passwords, NTLM hashes, or Kerberos.
Discover more Discover more tools
addcomputer.py Impacket: Create Computer Account for RBCD
Impacket's addcomputer.py guide for creating Active Directory computer accounts via SAMR or LDAPS, verifying MachineAccountQuota, and using them in RBCD chains.
Discover more Discover more tools
lookupsid.py: Enumerate Users and SIDs via RID Cycling SMB
Guide to impacket-lookupsid to enumerate users, groups, and SIDs via MS-LSAT over SMB, using passwords, NTLM hashes, Kerberos, or anonymous sessions when allowed.
Discover more Discover more tools
GetNPUsers.py: AS-REP Roasting with Impacket
Impacket's GetNPUsers.py guide for finding accounts without Kerberos pre-authentication, extracting AS-REP hashes, and cracking them offline with Hashcat.
Discover more Discover more tools
samrdump.py Impacket: Enumerate Windows Users via SAMR
Impacket's samrdump.py guide to enumerate Windows users via MS-SAMR over SMB, get RID and account attributes with passwords, NTLM or Kerberos hashes.
Discover more Discover more tools
GetADUsers.py Inpacket: Enumerate Active Directory Users
Impacket's GetADUsers.py guide to enumerate Active Directory users via LDAP with password, NTLM hash, AES or Kerberos key and parse pwdLastSet and lastLogon.
Discover more Discover more tools
getST.py Impacket: S4U, RBCD and Constrained Delegation
Impacket's getST.py guide for obtaining Kerberos Service Tickets with S4U2Self, S4U2Proxy, RBCD, and constrained delegation. Payload and errors for AD pentests.
Discover more Discover more tools
rpcdump.py Inpacket: RPC Endpoint, UUID and Named Pipe
A guide to Impacket's rpcdump.py for enumerating Windows RPC endpoints, UUIDs, named pipes, and dynamic ports. Practical commands and analysis for pentesting.
Discover more Discover more tools
dcomexec.py - Lateral Movement via DCOM with Impacket
impacket-dcomexec How-To Guide: Remote Windows Execution via DCOM with ShellWindows, ShellBrowserWindow, and MMC20 Using NTLM Passwords or Hashes.
Discover more Discover more tools
Impacket aexec: Remote Execution via Task Scheduler
A Guide to Impacket-atexec: Remote Execution on Windows via Task Scheduler RPC with Password, Pass-the-Hash, Kerberos, and Lateral Movement over SMB.
Discover more Discover more tools
pth-net: Guide to Pass-the-Hash with Samba over SMB/RPC
Use pth-net with NTLM hash to enumerate users, payloads, groups and shares via SMB/RPC in pentests, compare it with NetExec and Impacket and analyze PtH detection.
Discover more Discover more tools
impacket-secretsdump: Dump Windows Hashes and Credentials
How to impacket-secretsdump: Remote and offline dump of NTLM hashes, SAM, LSA secrets, Kerberos keys, and NTDS.dit in Windows and Active Directory.
Discover more Discover more tools
PowerView: Active Directory Enumeration with Commands and Examples
PowerView guide to enumerate Windows Active Directory: users, groups, computers, ACLs, sessions, GPOs, and trusts with PowerShell commands and practical examples.
Discover more Discover more tools
PowerShell for Penetration Testing: The Complete Offensive Guide
PowerShell for Windows Pentesters: Commands, Downloads, Remoting, Active Directory Enumeration, Logging, AMSI, CLM, and Post-Exploitation Techniques.
Discover more Discover more tools
SharpHound for BloodHound CE: AD Data Collection Guide
SharpHound for BloodHound CE: Active Directory data collection, key flags, stealth options, and import to map escalation paths.
Discover more Discover more tools
BloodyAD: Privilege Escalation in Active Directory (2026 Guide)
BloodyAD: PTH/PTT authentication, ACE abuse (GenericAll, WriteDACL, RBCD), Shadow Credentials, Bad Successor 2025 and autobloody.Pentest, payload, detection and bypass
Discover more Discover more tools
reg.py: All Registry Keys for Pentesting and Active Directory
Impacket reg.py: Query, add, delete, save, and backup the remote Windows registry via SMB/MS-RRP. SAM, LSA, WDigest, RDP, and WinRM keys for pentesting and hardening.
Discover more Discover more tools
Certipy: A Complete Guide to AD CS Enumeration and Abuse
Complete guide to Certipy 5.1 to enumerate AD CS, locate ESC1-ESC17, request certificates, use PKINIT, relay, Shadow Credentials and Golden Certificate.
Discover more Discover more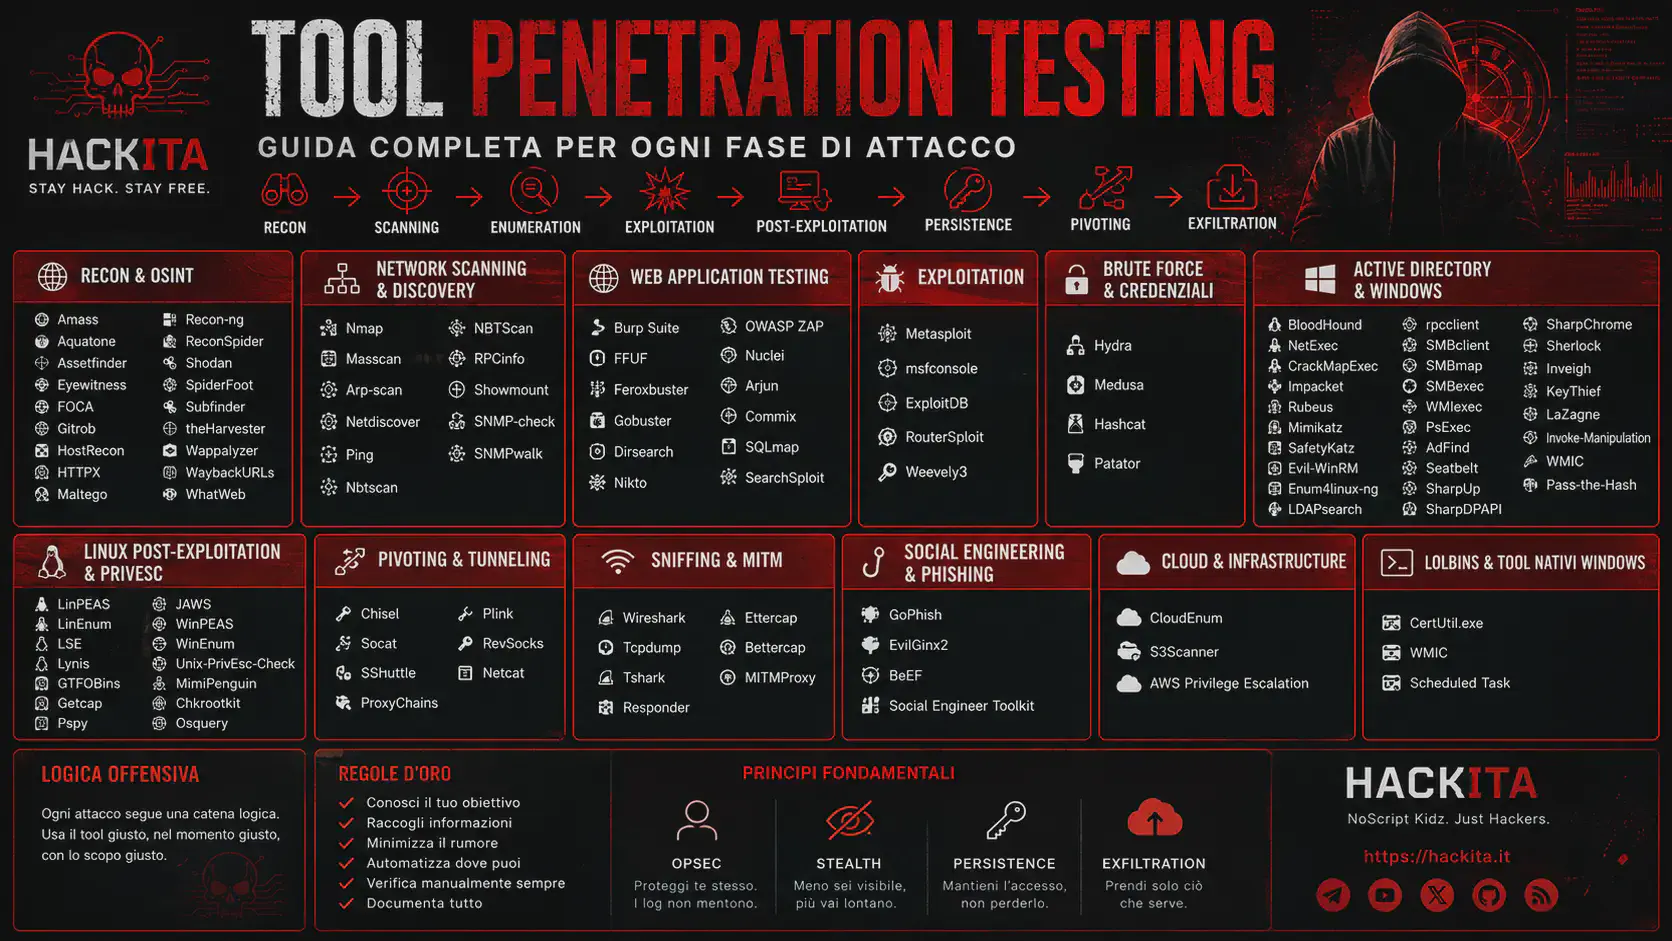 tools
Tool Penetration Testing: A Complete Guide to the Attack Phase"
All offensive penetration testing tools organized by attack phase: recon, exploitation, post-exploitation, pivoting, AD. With real attack chains for CTF, OSCP, OSEP, and red teams.
Discover more Discover more tools
Certify: Enumerate and Abuse AD CS from Windows with C#
Certify is GhostPack's C# tool for enumerating and exploiting AD CS from Windows without Python dependencies. Learn how to use it to find vulnerable templates and request certificates for escalation to Domain Admin.
Discover more Discover more tools
John the Ripper: Complete Guide to Password Cracking
Complete guide to John the Ripper (Jumbo): Extract hashes from ZIP, SSH, KeePass, PDF, and Office with *2john; crack with wordlist and rules. Comparison with hashcat and final cheat sheet.
Discover more Discover more tools
OWASP ZAP: Complete guide to proxies, spiders, active scan and fuzzing
Learn how to use OWASP ZAP to intercept HTTP/HTTPS traffic, map web applications with spiders and AJAX Spiders, perform active scans, fuzzing, and authenticated tests, even in CI/CD with Docker and APIs.
Discover more Discover more tools
WMIExec: Complete guide to lateral movement stealth with wmiexec.py
Learn how to use Impacket's WMIExec and wmiexec.py for lateral movement on Windows with passwords, Pass-the-Hash, and Kerberos, reducing artifacts compared to PsExec and improving OPSEC.
Discover more Discover more tools
Unix-PrivEsc-Check: privilege escalation auditing on Linux and legacy Unix
Learn how to use Unix-PrivEsc-Check to detect misconfigurations, weak permissions, sudo abuse, and privilege escalation vectors on Unix/Linux systems, including legacy environments where modern tools fail.
Discover more Discover more tools
Wappalyzer: How to Identify a Website's CMS, Framework, and Technologies
A guide to Wappalyzer for detecting CMS, framework, CDN, analytics, and website versioning clues to guide targeted reconnaissance, fingerprinting, and scanning in pentesting.
Discover more Discover more tools
Wayback URLs: How to Find Historical URLs, Hidden Endpoints, and Sensitive Files
Learn how to use Waybackurls to extract a domain's historical URLs from the Wayback Machine, find forgotten paths, exposed backups, and old endpoints useful for passive reconnaissance.
Discover more Discover more tools
WhatWeb: A Complete Guide to Stealth and Aggressive Web Fingerprinting
Learn how to use WhatWeb to identify a website's CMS, framework, web server, JavaScript libraries, and technologies to guide reconnaissance, fingerprinting, and targeted vulnerability scanning.
Discover more Discover more tools
WinEnum: Windows enumeration for privilege escalation and comparison with WinPEAS
Complete guide to WinEnum for post-exploitation enumeration on Windows: PowerShell and Batch variants, privilege escalation checks, OPSEC, differences with WinPEAS, PowerUp, SharpUp, and Seatbelt.
Discover more Discover more tools
WinPEAS: Commands and Privilege Escalation on Windows
WinPEAS for Windows privesc: Commands, enumeration, and output to detect vulnerable services, exposed credentials, and misconfigured privilege escalation.
Discover more Discover more tools
WMIC: Offensive Commands, Lateral Movement, and Persistence on Windows
Learn how to use WMIC for enumeration, remote execution, lateral movement, and WMI persistence on Windows. This includes the current status of the tool, practical commands, detection, hardening, and a comparison with PowerShell, CIM, and WinRM.
Discover more Discover more tools
Ssh-audit: How to Analyze Weak Ciphers, CVEs, and SSH Misconfigurations
Learn how to use ssh-audit to verify SSH server and client configurations, identify weak algorithms, outdated ciphers, vulnerable versions, and find useful findings for authorized hardening or penetration testing.
Discover more Discover more tools
SSH-KeyHunter: Find Private SSH Keys and Pivot on Linux
SSH-KeyHunter automates the search for private SSH keys on Linux, detects unprotected files, owners, fingerprints, and targets from known_hosts: an ideal tool for post-exploitation and lateral movement in authorized pentests.
Discover more Discover more tools
Sshuttle: Transparent Pivoting and Tunneling via SSH to Internal Networks
A guide to Sshuttle for creating a transparent tunnel over SSH, reaching internal subnets, routing DNS, and using a compromised host as a pivot during lateral movement and post-exploitation in authorized pentests.
Discover more Discover more tools
Subfinder: Complete guide to passive subdomain enumeration with ProjectDiscovery
Learn how to use Subfinder to find valid subdomains from passive sources, speed up web reconnaissance, and build a more effective recon pipeline with the ProjectDiscovery tool optimized for speed and stealth.
Discover more Discover more tools
Smbmap: SMB Enumeration and Share Discovery on Windows
smbmap explained for pentests: SMB share enumeration, permissions, file access, and credential testing on Windows and Active Directory systems.
Discover more Discover more tools
SMBExec: Fileless Remote Execution on Windows via SMB
SMBExec is a remote command execution technique over SMB 445 without dropping persistent binaries. It's a stealthier alternative to PsExec in Active Directory environments.
Discover more Discover more tools
Social-Engineer Toolkit (SET): A Complete Guide to Social Engineering Attacks
SET is a framework for simulating social engineering in authorized environments: phishing, credential harvester, and client-side attacks.
Discover more Discover more tools
RouterSploit: Exploit Framework for Routers and IoT
RouterSploit is a framework for testing vulnerabilities on routers and IoT devices. It includes scanning, exploit, and brute-force modules.
Discover more Discover more tools
Osquery: SQL-Based Endpoint Monitoring for Linux, macOS and Windows
Osquery allows you to query operating systems with SQL queries to analyze processes, users, files, and configurations for security monitoring purposes.
Discover more Discover more tools
Patator: A Modular Brute-Force Authentication Testing Framework
Patator: A Modular Brute-Force Authentication Testing Framework
Discover more Discover more tools
Nmap for Pentesting: Port Scanning, Network Recon and NSE
Nmap for penetration testing and network recon: commands, host discovery, TCP/UDP port scanning, service detection, OS fingerprinting, NSE and enumeration.
Discover more Discover more tools
Ncat.exe on Windows: Download, Commands, and Reverse Shell
How to download and use ncat.exe on Windows: listeners, connections, file transfer, SSL, reverse shell with -e cmd.exe, antivirus false positives and detection.
Discover more Discover more tools
MSFvenom Cheat Sheet: Commands, Payload, Shellcode & Bypass
MSFvenom exploit for lab and pentest: syntax, staged and stageless payload, EXE, ELF, PHP, WAR and MSI formats, shellcode with bad characters, handler and detection.
Discover more Discover more tools
LSE (Linux Smart Enumeration): Automated Linux Privilege Escalation Checklist
LSE (Linux Smart Enumeration): Automated Linux Privilege Escalation Checklist
Discover more Discover more tools
Medusa: High-Speed Login Brute-Force Tool for Network Services
Medusa is a parallel tool for brute-forcing authentication over SSH, FTP, SMB, HTTP, and other services. Fast, scalable, and ideal for authorized password auditing.
Discover more Discover more tools
Metasploit Framework: Complete Guide to Exploits and Payloads
Metasploit Framework is the most widely used penetration testing platform for exploits, payloads, and post-exploitation. A complete offensive workflow guide.
Discover more Discover more tools
Mitmproxy: HTTP/HTTPS Traffic Interception and Manipulation
mitmproxy is an interactive proxy for analyzing and manipulating HTTP/HTTPS traffic. Ideal for API testing, debugging, and authorized security assessments.
Discover more Discover more tools
LaZagne: Password Extraction from Browsers and Applications
LaZagne is an open-source tool for recovering saved passwords on Windows and Linux from browsers, email clients, and local software post-exploitation.
Discover more Discover more tools
Ldapsearch: LDAP and Active Directory Enumeration from Linux
Ldapsearch is a CLI tool for querying LDAP and Active Directory from Linux. It's useful for enumerating users, groups, SPNs, and domain objects.
Discover more Discover more tools
Httpx: HTTP Probing and Large-Scale Web Analysis in Penetration Testing
httpx is the HTTP probing tool for filtering active hosts, detecting technologies, status codes and screenshots in pipelines with subdomain enumeration.
Discover more Discover more tools
Hydra: Brute Force Login for Network Services
Hydra is a brute force tool for testing credentials over SSH, FTP, RDP, HTTP, and other services during authorized penetration tests.
Discover more Discover more tools
Impacket: Python Toolkit for SMB, Kerberos and Active Directory Attacks
Impacket is a Python suite for interacting with network protocols (SMB, LDAP, Kerberos, RPC) and conducting AD attacks such as DCSync and Pass-the-Hash.
Discover more Discover more tools
Invoke-Manipulation: PowerShell Obfuscation for Evasion AV
Invoke-Manipulation is a PowerShell module for obfuscating scripts and bypassing static checks during authorized red team operations.
Discover more Discover more tools
HostRecon: Automatic OSINT Reconnaissance on Single Targets
HostRecon automates single-domain OSINT and reconnaissance: DNS, whois, subdomain, breach data, and exposure mapping in a single command.
Discover more Discover more tools
Evil-WinRM: Remote Access and Post-Exploitation on Windows via WinRM
Evil-WinRM: Remote PowerShell shell via WinRM for Windows post-exploitation. Pass-the-hash, Kerberos ticket, AMSI bypass, in-memory execution .NET assembly for lateral movement enterprise.
Discover more Discover more tools
Cloud_enum: Cloud Asset Enumeration for Recon on AWS, Azure, and GCP
Cloud_enum is an OSINT tool for enumerating publicly exposed cloud resources on AWS, Azure, and GCP. It's useful during reconnaissance to map buckets, storage accounts, and assets related to a target domain.
Discover more Discover more tools
Empire: post-exploitation C2 framework for red team operations
Empire 5.0: A Complete Guide to C2 PowerShell: Stager, AMSI Bypass, Post-Exploitation, Lateral Movement, and Evasion Techniques. Cheat sheet included.
Discover more Discover more tools
Evilginx2: Bypass 2FA with Phishing Proxy Man-in-the-Middle
Evilginx2's practical guide to bypassing 2FA authentication: man-in-the-middle phishing, session hijacking, and credential theft. Advanced attacks against MFA.
Discover more Discover more tools
Arjun: HTTP Parameter Discovery for Advanced Web Application Recon
Arjun is a tool for discovering hidden HTTP parameters in web applications during penetration testing. It automates the identification of undocumented GET and POST parameters useful for IDOR, XSS, and injection.
Discover more Discover more tools
Assetfinder: Rapid Subdomain Enumeration for Attack Surface Mapping
Assetfinder is an OSINT tool for enumerating subdomains from public sources during the reconnaissance phase. It's ideal for quickly mapping a domain's attack surface during penetration testing.
Discover more Discover more tools
Commix: Automated Command Injection Exploitation Tool
Commix is an automated tool for identifying and exploiting command injection vulnerabilities in web applications. It supports blind, time-based, and file-based techniques to obtain RCE during penetration testing.
Discover more Discover more tools
Plink: Port Forwarding and SSH Tunneling from the Command Line in Windows Environments
Plink is the command-line version of PuTTY that allows SSH tunneling, port forwarding, and pivoting from Windows systems. A practical guide to its use in penetration testing and red teams.
Discover more Discover more tools
Searchsploit: Finding Local Exploits from Exploit-DB in Penetration Testing
Searchsploit is a terminal tool for searching for local exploits directly from the Exploit-DB database. A practical guide to identifying exploitable vulnerabilities during penetration testing.
Discover more Discover more tools
Maltego: What It Is and How to Use It for OSINT and Transform (2026)
How to Install Maltego for OSINT and Reconnaissance: Use Entity, Transform, Pivot, and Graph Analysis to Correlate Domains, IPs, Emails, People, and Infrastructure.
Discover more Discover more tools
Masscan: Ultra-Fast Port Scanner for Large-Scale Network Enumeration
Masscan is a high-speed port scanner capable of analyzing millions of IP addresses in minutes. A practical guide to its use during reconnaissance and infrastructure mapping during penetration testing.
Discover more Discover more tools
SpiderFoot: OSINT Automation, Reconnaissance and Attack Surface
Discover SpiderFoot to automate OSINT and reconnaissance: modules, correlation, subdomain, IP, email, threat intelligence, and attack surface mapping.
Discover more Discover more tools
TheHarvester: SECRETS to OSINT, Email & Subdomains (2026)
Learn how to use TheHarvester to harvest emails and subdomains: installation, recon, OSINT sources, API keys, JSON/XML output, and verified troubleshooting.
Discover more Discover more tools
KeeThief: Master Key and Credential Dump from KeePass
KeeThief: How to extract master keys and credentials from KeePass during an authorized pentest. Memory dumps, .kdbx files, operational limitations, detection, and post-exploitation.
Discover more Discover more tools
Weevely3: PHP Stealth Web Shell for Post-Exploitation and Pivoting
Weevely3: A practical guide to generating and managing stealthy PHP web shells in penetration testing. Tunneling, evasion, and post-exploitation.
Discover more Discover more tools
Chisel: TCP Tunneling over HTTP for Pivoting and Post-Exploitation
Chisel's Practical Guide to Tunneling and Pivoting: TCP Tunneling over HTTP, SOCKS Proxy, and Port Forwarding Through Firewalls. Modern Pivoting for Pentesters.
Discover more Discover more tools
LaZagne: Post-Exploitation Tool for Application Credential Dumping and DPAPI
LaZagne: password recovery tool for 87+ applications. Browser, WiFi, email, database, sysadmin tools. DPAPI decryption, credential harvesting post-exploitation Windows/Linux/macOS.
Discover more Discover more tools
SafetyKatz: Mimikatz Memory-Only Wrapper for LSASS Credential Dumping and EDR Evasion
SafetyKatz is a Mimikatz wrapper for in-memory credential dumping from LSASS, without writing to disk. It supports EDR evasion, NTLM hash extraction, and integration with Cobalt Strike for post-exploitation in Active Directory.
Discover more Discover more tools
FFUF: A Guide to Web Fuzzing for Directories, VHosts, and APIs (Pentesting and CTF)
FFUF is a fast Go web fuzzer for directory, vhost, and API testing. A practical guide with wordlists, filters, and pentest techniques.
Discover more Discover more tools
Hashcat: Password Cracking with GPU, Hash, Modes and Rules
Hashcat: GPU password cracking practical guide for NTLM, MD5, SHA, bcrypt hashes. Attack modes, mask patterns, wordlist rules and real techniques from CTF and pentest.
Discover more Discover more tools
CrackMapExec vs. NetExec: CME Commands and Migration to NXC
CrackMapExec (cme) to NetExec (nxc) Migration Guide: Translate CME commands to NXC, manage Kerberos, forms, file transfer, and see what's changing today.
Discover more Discover more tools
ARP-Scan Kali Linux: ARP Scan and Host Discovery
ARP-Scan guide on Kali Linux to discover hosts on your local network: ARP scanning, IP, MAC, vendor, subnet, output, and network reconnaissance workflow.
Discover more Discover more tools
Netdiscover: Discover Hidden Devices and IPs on Your LAN
Netdiscover is an essential tool for identifying active devices on the local network. It's ideal for silent recon via ARP in environments without DNS or DHCP.
Discover more Discover more tools
Ping and ICMP Techniques and Active Scans for Recon
Analyze network behavior with ping, fping, and hping3. ICMP reconnaissance, host discovery, and firewall testing techniques used in pentests.
Discover more Discover more tools
Rpcinfo: Enumerating RPC Services in Unix Environments
Rpcinfo allows you to identify active RPC services on Unix/Linux hosts. It's essential for reconnaissance and analysis of potential remote attack vectors.
Discover more Discover more tools
Showmount: Discover exposed NFS shares on the network.
Showmount is the perfect tool for enumerating NFS shares. It's used in recons to identify accessible resources and entry points in Unix/Linux environments.
Discover more Discover more tools
SnmpCheck: Device and Service Enumeration via SNMP v1/v2
Snmp-check allows you to extract information from network devices using SNMP. Perfect for low-noise attacks, silent enumeration, and footprinting.
Discover more Discover more tools
Snmpwalk: Massive SNMP Enumeration on Exposed Networks
Snmpwalk is the ideal tool for querying SNMP agents and gathering detailed information about network devices. It's used for low-noise recon and targeted attacks.
Discover more Discover more tools
enum4linux-ng: SMB and Active Directory enumeration
Complete guide to enum4linux-ng for SMB and Active Directory enumeration: users, groups, shares, policies, SID/RID, authentication, and practical commands.
Discover more Discover more tools
NetExec (NXC): Complete Guide to CrackMapExec's Successor
Complete Operation Guide to NetExec (nxc): SMB, LDAP, WinRM, RDP, advanced modules, credential dumping, vulnerability scan and lateral movement in Active Directory
Discover more Discover more tools
Smbclient: Accessing and Attacking Windows Shares
With smbclient, you can access, read, and write files to SMB shares. Learn how to use it for pentesting, internal attacks, enumeration, and pivoting in AD.
Discover more Discover more tools
BloodHound Pentest AD: Privilege Escalation and Domain Admin
BloodHound for privilege escalation on Active Directory: SharpHound, edge abuse, Shadow Credentials and ADCS. Italian guide to AD pentest towards Domain Admin.
Discover more Discover more tools
ldapsearch: LDAP Commands to Enumerate Users, Groups and ADs
ldapsearch for pentest: RootDSE, Base DN, LDAP bindings, users, groups, computers, SPN, LDAPS and Active Directory enumeration troubleshooting and cheat sheets
Discover more Discover more tools
rpcclient Kali Linux: SMB, AD, and SID/RID Enumeration
Guide to rpcclient on Kali Linux to enumerate users, groups, SIDs/RIDs, trusts, password policies, and SMB shares via SAMR, LSARPC, and SRVSVC, with practical commands.
Discover more Discover more tools
Inveigh: LLMNR, NBNS, and WPAD to Capture NTLM Hashes
What is Inveigh and how does it work? A guide to LLMNR, NBNS, and WPAD for capturing NetNTLM in Windows labs, using PowerShell, relay, troubleshooting, and detection.
Discover more Discover more tools
Mitmproxy: Intercept and Analyze HTTP/HTTPS Traffic
A practical guide to mitmproxy: configure the proxy, intercept HTTPS, install the CA, filter and modify flows, save sessions, and troubleshoot common issues.
Discover more Discover more tools
NBTScan: NetBIOS Scanning on Linux for the Recon Windows
NBTScan on Linux: Learn how to scan Windows hosts, identify NetBIOS names, domains, workgroups, and useful information for network reconnaissance.
Discover more Discover more tools
Netcat (nc): Commands, Port Scanning, and File Transfer
Learn how to use Netcat (nc) on Linux and Windows: practical commands, TCP/UDP listeners, port scanning, banner grabbing, file transfer, and reverse shell.
Discover more Discover more tools
Responder: Capture NTLM Hash on Linux, LLMNR, NBT-NS and Relay
Responder for Linux: How to capture NTLM/NetNTLMv2 hashes with LLMNR, NBT-NS, and WPAD, crack and relay NTLM in penetration tests and secure Windows labs
Discover more Discover more tools
Bettercap: What It Is, MITM, ARP Spoofing, and Sniffing on Kali Linux
What is Bettercap and how does it work? Discover the framework for network hacking and MITM: tutorials on Kali Linux, ARP spoofing, sniffing, network recon, PCAP, and proxies.
Discover more Discover more tools
Ettercap: MITM Tutorial, ARP Spoofing and Sniffing on Kali Linux
What is Ettercap and how does it work? A practical guide to MITM, ARP spoofing, and sniffing on Kali Linux, including installation, filters, packet capture, and commands.
Discover more Discover more tools
Tcpdump: Network Traffic Sniffing and Analysis Tutorial
What is tcpdump and how does it work? A guide to terminal network sniffing with packet capture, BPF filters, PCAP analysis, and pentesting commands.
Discover more Discover more tools
TShark: Network Traffic Sniffing and Analysis Tutorial
What is TShark and how is it used? A guide to terminal network sniffing with packet capture, filters, PCAP analysis, statistics, and pentesting commands.
Discover more Discover more tools
Wireshark for Pentesting: Filters, NTLM, DNS and TCP Stream
Wireshark for ethical hacking: advanced filters, NTLM, DNS, and TCP Stream. Learn how to isolate traffic, read sessions, and find useful indicators in labs and HTBs.
Discover more Discover more