
Theoretical concepts, mindsets, checklists, and external links to organize your studies, plan your labs, and save time.
- blog
- 43+ Note
- Focus
- OSCP · Red Team
- Structure
- Recon → Exploit
Guides and Resources blog
Filters
 guides-resources
Data Breach: What It Is, Meaning, Examples, and What to Do (2026)
Data breach: how it works and what it is, causes, real-world examples, the 72-hour rule, costs in 2026, and what to do if your data is stolen.
Discover more Discover more guides-resources
Trojan Virus: What It Is, How It Works, and How to Recognize It
Trojans: how they spread, what damage they can cause, and how to recognize them. Comparison with viruses and worms, main types, and examples such as Zeus and Emotet.
Discover more Discover more guides-resources
Zero-Day: What It Is, How It Works, and How to Defend Yourself (2026)
What is a zero-day attack? Learn what zero-day vulnerabilities and exploits mean, the differences between n-day and CVE, real-world examples, and how to defend yourself in 2026.
Discover more Discover more guides-resources
GDPR: What It Is, Obligations, Rights, Sanctions, and DPO (2026 Guide)
GDPR: meaning, how it works and who it applies to, principles, rights, DPO, data breach in 72 hours and fines up to 20 million euros or 4% of turnover
Discover more Discover more guides-resources
Anonymous Hacker: Mask, Operations, and Current Events
Who are Anonymous, where the Guy Fawkes mask came from, their most famous operations (Chanology, Payback, Tunisia), and what they're still doing today in 2026.
Discover more Discover more guides-resources
The Deep Web: What It Is, How It Differs from the Dark Web, and How It Works
The deep web explained simply: what it is, how to access it and how it works, examples, differences between the surface web and the dark web, whether Tor is needed, and whether it's legal to browse it.
Discover more Discover more guides-resources
Kevin Mitnick: Hacker, Social Engineering, Arrest, and Career
Kevin David Mitnick, known as The Condor and The Darkside Hacker, was one of the most famous hackers: social engineering, arrest, career, and death in 2023.
Discover more Discover more guides-resources
Botnets: The Mirai Case and How to Recognize an Active One
What is a botnet, how a device becomes a remotely controlled zombie, how to recognize it, and the Mirai case that brought half the internet into crisis in 2016.
Discover more Discover more guides-resources
NIS2: What it is, Obligations, Requirements, and 2026 Deadlines
NIS2 explained simply: what the NIS 2 directive is, who it applies to, obligations, 24-hour incident reporting, fines up to €10 million, and 2026 deadlines.
Discover more Discover more guides-resources
Spyware: What It Is, How to Detect It, and the Pegasus Case
Learn how spyware works, the signs you can spot on your phone and PC, how it differs from stalkerware, how to remove it, and what the Pegasus case revealed.
Discover more Discover more guides-resources
Basilicata Data Center: The Kraken Case and the Hacker Mystery
Were data centers in Basilicata hacked? Russian pages and Kraken indicate a hacker attack: what happened to the Basilicata Region, healthcare system, and hospitals?
Discover more Discover more guides-resources
The 10 Most Famous and Powerful Hackers in the World (2026 Guide)
Who are the 10 most famous and powerful hackers in history? From Kevin Mitnick to Anonymous: true stories, famous attacks, secrets and curiosities, and what they do today.
Discover more Discover more guides-resources
Dark Web: What It Is, How to Access It, and How It Works
What is the dark web, how does it differ from the deep web and Tor, what criminal economy really operates there, and what's true about legends like the Red Rooms.
Discover more Discover more guides-resources
White Hat, Black Hat, and Grey Hat: Who They Are and What They Risk
What distinguishes white hat, black hat, and grey hat, the origin of the term hacker/cracker, the legal risks of each, and what responsible disclosure is.
Discover more Discover more guides-resources
Computer Virus: What It Is and How It's Different from Malware
What is a computer virus, how it spreads, the main types, how to recognize and remove it, and how it differs from malware, worms, Trojans, and ransomware.
Discover more Discover more guides-resources
Ethical Hacker: Who He Is, What He Does, and How Much He Earns
Who is an ethical hacker, what they do every day, what skills and tools they use, how much they earn in Italy, and how to become one step by step.
Discover more Discover more guides-resources
Hacker: Meaning, Types (White Hat, Black Hat), and Cracker
What is a hacker, the difference between a cracker and an ethical hacker, the types (white, black, grey hat), when hacking is a crime, and how to become an ethical hacker.
Discover more Discover more guides-resources
Revolut hacked? Data breach: passports, IBANs, and Bitcoin
Revolut confirms a data breach: fake government request, passports and Bitcoin histories exposed. Data published online, 10.000 BTC ransom demanded.
Discover more Discover more guides-resources
Thomson Reuters: SSN breached and files sealed
Thomson Reuters: C-Track platform breached in US and Canadian courts. SSNs, health data, and court records sealed in 24 courts.
Discover more Discover more guides-resources
Vodafone scam: "7415 Gold Starter points will expire today"
Vodafone 2026 scam: Did you receive the text message "Your 7415 Gold Starter points expire today"? Here's how to spot it, where the link goes, and what to do.
Discover more Discover more guides-resources
Secret Scanning: Gitleaks, TruffleHog and Pipeline CI/CD
Automate secret scanning with Gitleaks pre-commit and TruffleHog in CI/CD: lock API keys and tokens, verify leaks, and remove secrets from Git history.
Discover more Discover more guides-resources
AWS Pentesting: IAM, S3, EC2, IMDS, and Privilege Escalation
AWS Operational Pentesting: Enumerate IAM, S3, EC2, Lambda, and IMDS with AWS CLI, Pacu, ScoutSuite, and Prowler; find misconfigurations and privilege escalation paths.
Discover more Discover more guides-resources
Cloud Security Automation: Prowler, Checkov and AWS Config
Cloud security automation on AWS: Use Prowler, ScoutSuite, and AWS Config; integrate Checkov and tfsec into CI/CD; and detect drift and misconfiguration with EventBridge.
Discover more Discover more guides-resources
Wordlists for Pentesting: SecLists, RockYou, CeWL and Crunch
Learn which SecLists wordlists to use for directory fuzzing, password cracking, DNS and API, with paths on Kali Linux and custom lists created with CeWL and Crunch.
Discover more Discover more guides-resources
Database Security: Hardening, Misconfigurations and Pentests
Database security for pentesters and defenders: misconfigurations, weak credentials, exposed services, and hardening of MSSQL, MySQL, and PostgreSQL.
Discover more Discover more guides-resources
Database Privilege Escalation: From DB Access to RCE
Database Privilege Escalation Guide. Pentest for MSSQL, MySQL, PostgreSQL, and Oracle: Enumerate privileges and escalate from database access to RCE.
Discover more Discover more guides-resources
Cyber Kill Chain: What It Is, 7 Phases, and Pentesting Tools
Discover what the Cyber Kill Chain is: the 7 phases of an attack, pentesting and red team tools, MITRE ATT&CK mapping, and the Unified Kill Chain.
Discover more Discover more guides-resources
Credential Stuffing: What It Is, How It Works, and How to Protect Yourself
Credential stuffing: Learn how credential-stolen attacks work, how to detect them, and which defenses to use, including MFA, passkeys, and rate limiting.
Discover more Discover more guides-resources
Credential Harvesting: Techniques and Tools for Pentesting
Learn how credential harvesting works in pentesting: Responder, Evilginx2, LaZagne, AiTM phishing, browser theft, detection and mitigation.
Discover more Discover more guides-resources
Credential Dumping on Windows: LSASS, SAM, DPAPI and NTDS.dit
Credential dumping on Windows: NTLM hash and Kerberos tickets from LSASS, SAM, LSA Secrets, DPAPI and NTDS.dit with Mimikatz, ProcDump and secretsdump on Active Directory
Discover more Discover more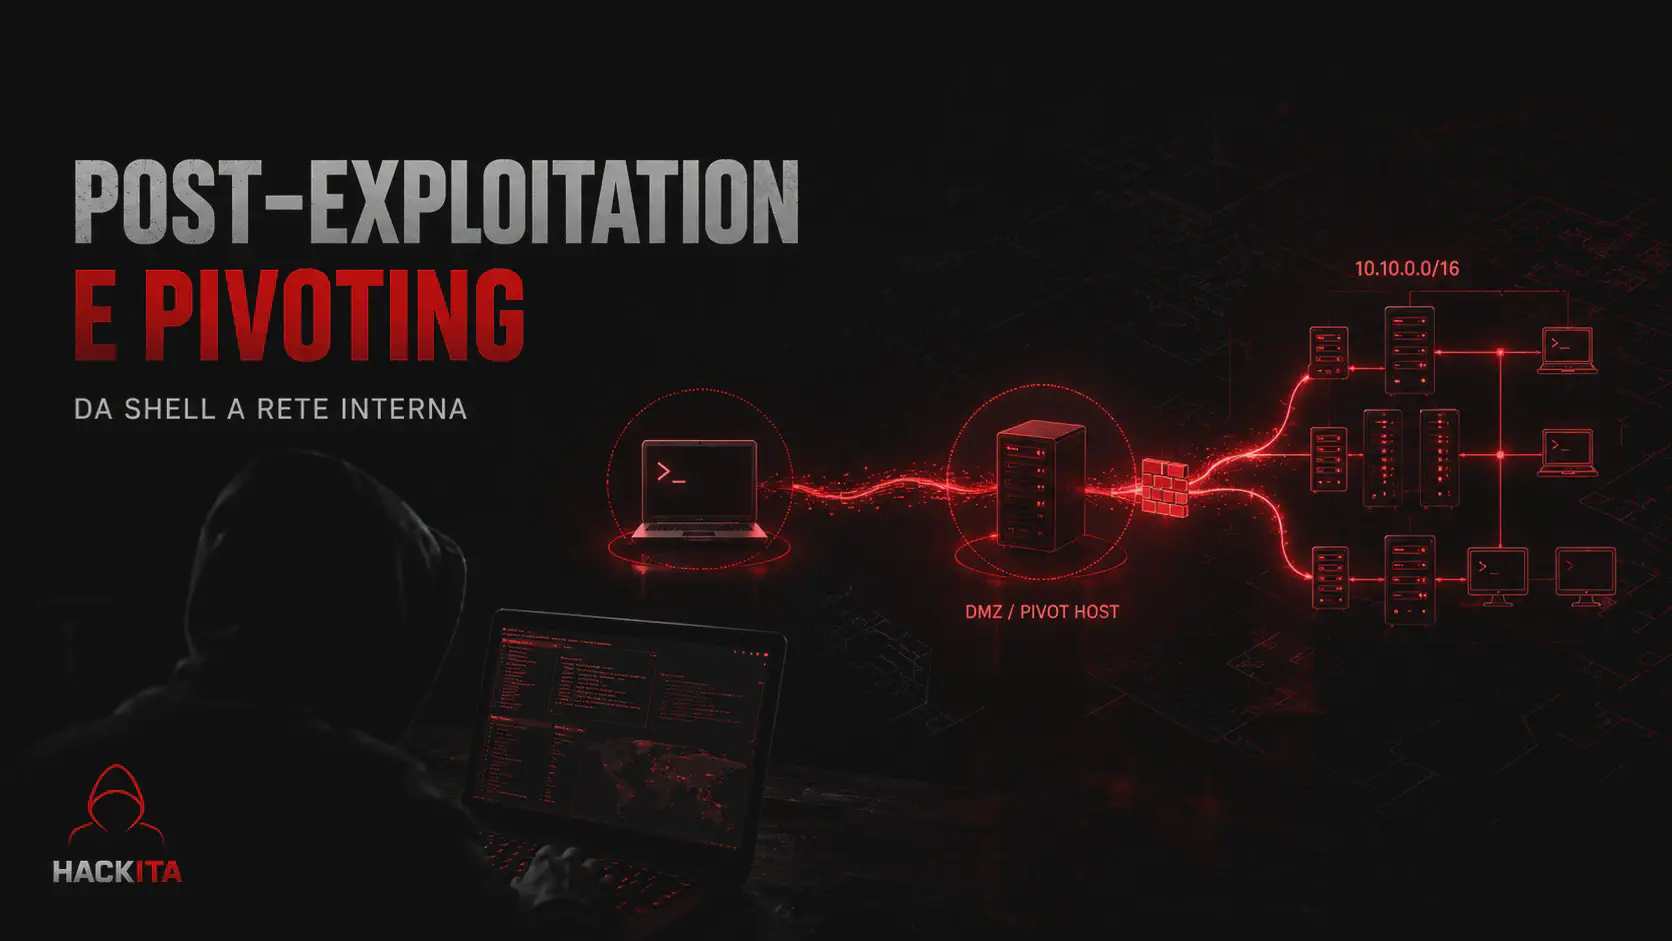 guides-resources
Pivoting in Pentesting: A Complete Guide with Ligolo-ng, Chisel, and SSH
Practical guide to pivoting and tunneling with SSH, Ligolo-ng, Chisel, sshuttle, and ProxyChains to reach internal networks and configure double pivots.
Discover more Discover more guides-resources
Post-Exploitation Windows and Active Directory: Complete Guide
Post-exploitation Windows and Active Directory: enumeration, privilege escalation, credential dumping, persistence, lateral movement and operational cleanup.
Discover more Discover more guides-resources
LOLBins, GTFOBins and LOOBins: The Complete Guide to Living Off the Land (2026)
Complete guide to Living Off the Land (LotL), LOLBins, GTFOBins, and LOOBins for Windows, Linux, and macOS in 2026. Commands, EDR evasion techniques, privilege escalation, lateral movement, and post-exploitation with native binaries and LOLBAS
Discover more Discover more guides-resources
Phishing Attack Vectors: A Red Team Technical Breakdown
Red team phishing techniques for authorized engagements: spear phishing with GoPhish, SET credential harvesting, quishing, HTML smuggling, SMTP infrastructure setup, and AiTM session capture.
Discover more Discover more guides-resources
Enumeration Penetration Testing: Network, AD & Web Guide
Offensive Enumeration 2026: host discovery, SMB, LDAP, Kerberos, BloodHound, web fuzzing and post-compromise. From zero to domain admin.
Discover more Discover more guides-resources
Ransomware 2026: A Complete Guide. What They Are and How to Protect Yourself
The Complete Guide to Ransomware 2026: What it is, how it works, historical attacks (WannaCry, LockBit), double extortion, RaaS, and best practices for defending against it with backups, MFA, and Zero Trust.
Discover more Discover more guides-resources
HackIta: The Italian blog for ethical hacking, pentesting, and offensive security
HackIta (not Ackita) is the Italian resource for ethical hacking, penetration testing, and CTF. 277+ technical articles on Windows/Linux privileges, Active Directory, web hacking, and red teams.
Discover more Discover more guides-resources
Vulnerability Exploitation: A Practical Framework for Moving from CVE to Shell
Discover the right method to transform a vulnerability into real access: discovery, validation, prioritization, exploit selection, weaponization, execution, and post-exploitation in penetration testing.
Discover more Discover more guides-resources
Man in the Middle: What Is a MITM Attack and How Does It Work?
The Complete Guide to Man in the Middle: ARP Spoofing, SSL Stripping, Session Hijacking, Rogue DHCP, Evil Twin, and Real-World MITM Techniques on Enterprise Networks and Wi-Fi.
Discover more Discover more guides-resources
Windows Buffer Overflow Exploit: ASLR and DEP Bypass with ROP Chain
Complete Guide to Windows Buffer Overflow Exploit: Format string leak to bypass ASLR, ROP chain to bypass DEP, VirtualAlloc, SEH, egg hunter.
Discover more Discover more guides-resources
Social Engineering: What It Is, Real Attacks, and Defenses in 2026
Social Engineering: What it is, its meaning, how it works, and the techniques it uses, including OSINT, pretexting, vishing, phishing, and impersonation.
Discover more Discover more guides-resources
Exploit-DB: Exploit and PoC Database for Penetration Testing
Exploit-DB is a public database of exploits and proofs of concept for vulnerability research and penetration testing. Search by CVE, software, and platform.
Discover more Discover more guides-resources
AWS Privilege Escalation: 21+ Techniques for Escalating from Low-Priv to Admin in IAM
AWS Privilege Escalation is a set of techniques for gaining higher privileges by abusing IAM misconfigurations in cloud environments. Policy analysis, role assumption, and abuse of AWS services in authorized penetration testing contexts.
Discover more Discover more