Wordlists for Pentesting: SecLists, RockYou, CeWL and Crunch

Learn which SecLists wordlists to use for directory fuzzing, password cracking, DNS and API, with paths on Kali Linux and custom lists created with CeWL and Crunch.
- Posted on 2026-08-19
- Reading time: 9 min
Wordlist Hacking and Pentesting: Guide to SecLists and Custom Wordlists #
Tools make noise, wordlists make the difference. You can have ffuf, feroxbuster, hashcat, john—without the right wordlist, you won't find anything. The choice of wordlist is what separates a 10-minute recon from hours of false negatives: a WordPress target scanned with a generic directory list misses all the WP-specific paths that a CMS-specific list finds in 30 seconds.
This guide covers every scenario: which wordlist to use for directory brute forcing, password auditing, DNS subdomain discovery, fuzzing, username enumeration, API discovery—and how to generate custom wordlists when generic ones aren't enough.
Prerequisites: Basic Linux knowledge and familiarity with at least one enumeration tool such as ffuf or gobuster. The password hash sections also require familiarity with hashcat or john the ripper.
What is a Wordlist in Pentesting? #
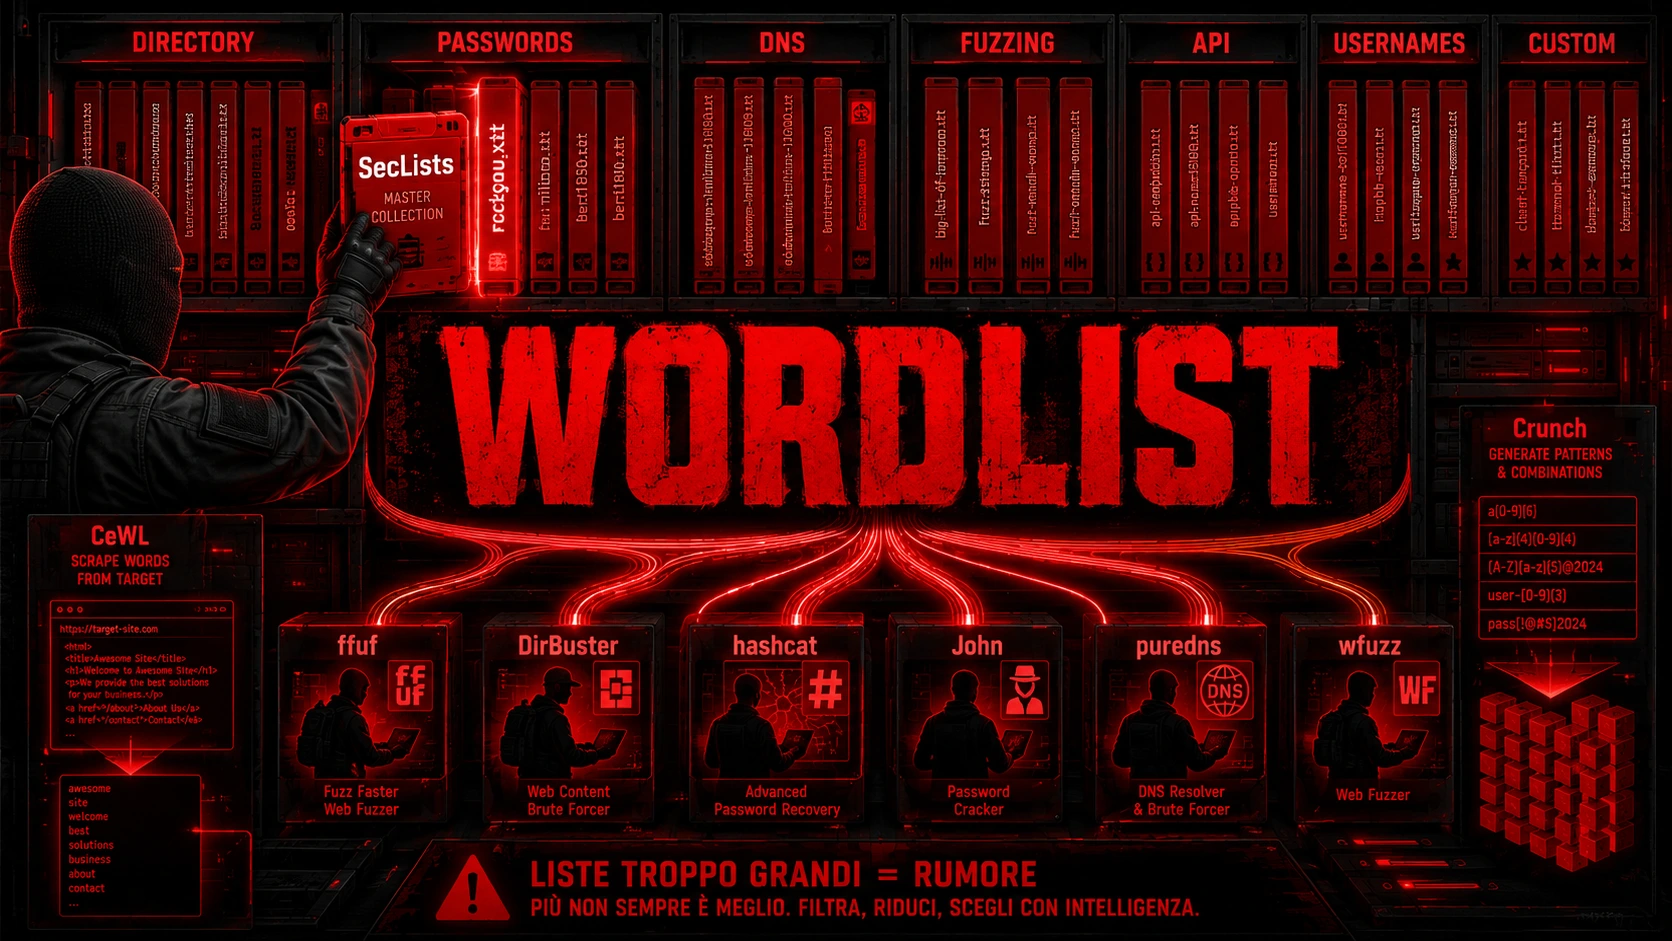
A wordlist is a file containing a collection of words, strings, paths, usernames, passwords, or payloads used by security tools to automate enumeration, fuzzing, and password auditing. SecLists is one of the most widely used collections because it organizes thousands of lists for web content discovery, DNS, passwords, usernames, and vulnerability testing.
Types of Wordlists #
| Type | Usage |
|---|---|
| Directory | Web directories and files |
| DNS | Subdomain discovery |
| Password | Password auditing |
| Username | Account enumeration |
| Fuzzing | Payload and input testing |
| API | Endpoint discovery |
| CMS | WordPress, Drupal, Joomla |
| Custom | Targeted enumeration on the specific target |
How to Choose a Wordlist #
The general rule: specificity over size . A small, technology-focused list almost always beats a huge, generic list.
Target generico → common.txt → raft-medium → lista specifica CMS/tecnologia → custom wordlist| Wordlist | Pro | Cons |
|---|---|---|
| Small | Very fast | Minor coverage |
| Media | Good balance | Most requested |
| Grande | High coverage | Slow, noisy |
| Technology specification | Very effective on target | Requires fingerprinting first |
| Custom | Highly targeted | It requires preparation |
Don't automatically start with the largest list: start with the most specific one for your target and increase coverage only if necessary.
Where Are Wordlists on Kali? #
# Directory wordlist principali
ls /usr/share/wordlists/           # rockyou.txt e poco altro
ls /usr/share/seclists/            # SecLists (dopo installazione)
ls /usr/share/dirbuster/wordlists/ # Liste directory DirBuster
ls /usr/share/dirb/wordlists/      # Liste dirb
ls /usr/share/wfuzz/wordlist/      # Liste wfuzz

# Decomprimi rockyou (compresso di default su Kali)
gunzip /usr/share/wordlists/rockyou.txt.gz
SecLists – The Main Collection #
SecLists (GitHub: danielmiessler/SecLists) is the most widely used wordlist collection in the industry. It's not a single list, but a scenario-based library with thousands of specialized files.
sudo apt install seclists -y
ls /usr/share/seclists//usr/share/seclists/
├── Discovery/
│ ├── Web-Content/ ← directory, file, API, CMS-specific
│ ├── DNS/ ← subdomain discovery
│ └── Infrastructure/ ← porte, servizi
├── Fuzzing/
│ ├── SQLi/ ← SQL injection payloads
│ ├── XSS/ ← Cross-site scripting
│ ├── LFI/ ← Local File Inclusion
│ └── Command-Injection/
├── Passwords/
│ ├── Common-Credentials/ ← top password lists
│ ├── Default-Credentials/ ← credenziali default per servizio
│ └── Leaked-Databases/ ← rockyou e altri breach
├── Usernames/ ← username lists
└── Web-Shells/ ← nomi file di web shell comuniWordlist for Directory Enumeration #
To find hidden directories and files on web servers. The choice depends on the available speed and the search depth. The entry numbers below are indicative and vary between package versions. Always check with your local service provider. wc -l on the file you are using.
Quick Wordlists (quick win) #
# common.txt – poche migliaia di entry, risultati in <30 secondi
# Usa sempre come primo check
/usr/share/seclists/Discovery/Web-Content/common.txt

ffuf -w /usr/share/seclists/Discovery/Web-Content/common.txt \
     -u http://target.com/FUZZ --hc 404
Wordlist Standard (normal assessment) #
# raft-medium-directories.txt – decine di migliaia di entry, bilanciato
/usr/share/seclists/Discovery/Web-Content/raft-medium-directories.txt

# raft-medium-files.txt – file specifici (non directory)
/usr/share/seclists/Discovery/Web-Content/raft-medium-files.txt

# directory-list-2.3-medium.txt – il default storico di DirBuster
/usr/share/dirbuster/wordlists/directory-list-2.3-medium.txt
In-Depth Wordlists (Full Engagement) #
# raft-large-directories.txt – da siti reali, molto più ampia della medium
/usr/share/seclists/Discovery/Web-Content/raft-large-directories.txt

# directory-list-2.3-big.txt – oltre un milione di entry, lenta, usa solo quando necessario
/usr/share/dirbuster/wordlists/directory-list-2.3-big.txt
Wordlist for Technology #
Fingerprint first, wordlist second. When identifying CMS or stacks (Wappalyzer, whatweb, headers), use the specific list—it finds what the generic ones miss.
# WordPress
/usr/share/seclists/Discovery/Web-Content/CMS/wordpress.txt

# Drupal
/usr/share/seclists/Discovery/Web-Content/CMS/drupal.txt

# Joomla
/usr/share/seclists/Discovery/Web-Content/CMS/joomla.txt

# Apache / IIS / Nginx
/usr/share/seclists/Discovery/Web-Content/apache.txt
/usr/share/seclists/Discovery/Web-Content/IIS.txt
/usr/share/seclists/Discovery/Web-Content/nginx.txt

# Esempio: target WordPress
ffuf -w /usr/share/seclists/Discovery/Web-Content/CMS/wordpress.txt \
     -u http://target.com/FUZZ \
     -e php,txt,bak --hc 404
Summary Table – Directory Fuzzing #
| Screenwriting | Wordlist | Swift |
|---|---|---|
| Initial quick win | common.txt | ★ ★ ★ ★ ★ |
| Standard Assessment | raft-medium-directories.txt | ★ ★ ★ ★ |
| In-depth scan | raft-large-directories.txt | ★★★ |
| Max coverage | directory-list-2.3-big.txt | ★ |
| Wordpress | CMS/wordpress.txt | ★ ★ ★ ★ |
| Sensitive files | raft-medium-files.txt | ★ ★ ★ ★ |
Wordlist for Offline Password Auditing #
Here the flow is hash → wordlist → hashcat/john: you already have a hash (from a dump, from a file, from a capture) and you try to crack it offline, with no rate limits.
RockYou – The Classic #
Real passwords leaked from a 2009 breach. Still effective because password habits don't change much over time.
# Location su Kali
/usr/share/wordlists/rockyou.txt
gunzip /usr/share/wordlists/rockyou.txt.gz  # se ancora compresso

# Con hashcat (NTLM)
hashcat -m 1000 hashes.txt /usr/share/wordlists/rockyou.txt

# Con john
john --wordlist=/usr/share/wordlists/rockyou.txt hashes.txt

# Con regole per aumentare la copertura
hashcat -m 1000 hashes.txt rockyou.txt -r /usr/share/hashcat/rules/best64.rule
rockyou.txt It is a good first choice for offline password auditing, but the success rate varies greatly depending on the organization's password policy, user population, hashing algorithm, and applied mutation rules—there is no universally reliable percentage.
Lists by Largest Volume #
# 10 milioni – per hash cracking dopo che rockyou non basta
/usr/share/seclists/Passwords/Common-Credentials/10-million-password-list-top-100000.txt
rockyou2024 #
# RockYou2024: raccolta molto più ampia (rilasciata luglio 2024)
# NON incluso in Kali — download separato, dimensione notevole da decompresso
# Usa solo per hash cracking offline su GPU potente
# Download: https://github.com/ohmybahgosh/RockYou2024.txt
Generate Variants with Rules #
Before moving on to a huge wordlist, try mutating the one you already have. The hashcat and john rules apply common transformations (capitalization, trailing digits, year, symbols) to every word in the list:
password → Password → password1 → Password1 → password2026 → Password2026!# hashcat con regole
hashcat -m 1000 hashes.txt rockyou.txt -r /usr/share/hashcat/rules/best64.rule
# john con regole custom (in john.conf) o predefinite
john --wordlist=rockyou.txt --rules hashes.txtIt makes sense to move to a much larger list only after you have exhausted the wordlist + rules on the base list.
Wordlist for Authentication Testing (Online) #
Here the flow is different: username + password list → login → rate limit/lockoutEvery attempt is a real request against a live service—that's why small, targeted lists are generally preferable to huge ones, especially when rate limits or account lockouts apply.
# Top password comuni – per attacchi rapidi su login web
/usr/share/seclists/Passwords/Common-Credentials/10k-most-common.txt

# Shortlist – primo tentativo, minimo rumore
/usr/share/seclists/Passwords/Common-Credentials/top-passwords-shortlist.txt
Default Credentials – Per Service #
/usr/share/seclists/Passwords/Default-Credentials/ftp-betterdefaultpasslist.txt
/usr/share/seclists/Passwords/Default-Credentials/ssh-betterdefaultpasslist.txt
/usr/share/seclists/Passwords/Default-Credentials/tomcat-betterdefaultpasslist.txt
/usr/share/seclists/Passwords/Default-Credentials/mssql-betterdefaultpasslist.txt
/usr/share/seclists/Passwords/Default-Credentials/telnet-betterdefaultpasslist.txt
For authorized authentication tests, always start with the smallest, service-specific list before scaling—less noise, less chance of lockouts during engagement.
Wordlist for DNS and Subdomain Discovery #
# Top 5.000 – quick check per target standard
/usr/share/seclists/Discovery/DNS/subdomains-top1million-5000.txt

# Top 20.000 – assessment standard
/usr/share/seclists/Discovery/DNS/subdomains-top1million-20000.txt

# Top 110.000 – engagement approfondito
/usr/share/seclists/Discovery/DNS/subdomains-top1million-110000.txt

# Esempio con gobuster
gobuster dns -d target.com \
  -w /usr/share/seclists/Discovery/DNS/subdomains-top1million-5000.txt \
  -t 50
n0kovo – Large Wordlist for Subdomain Discovery #
# n0kovo_subdomains: generata da SSL cert harvesting sull'intero IPv4
# Molto ampia, buona opzione quando le liste standard non bastano
# GitHub: https://github.com/n0kovo/n0kovo_subdomains

git clone https://github.com/n0kovo/n0kovo_subdomains
Wordlist for Fuzzing – SQLi, XSS, LFI, Command Injection #
Ready-to-use injection payloads, for use with ffuf or wfuzz.
# SQL Injection
/usr/share/seclists/Fuzzing/SQLi/Generic-SQLi.txt
/usr/share/seclists/Fuzzing/SQLi/Generic-BlindSQLi.fuzzdb.txt

# XSS
/usr/share/seclists/Fuzzing/XSS/XSS-Jhaddix.txt
/usr/share/seclists/Fuzzing/XSS/XSS-Bypass-Strings-BruteLogic.txt

# LFI / Path Traversal
/usr/share/seclists/Fuzzing/LFI/LFI-Jhaddix.txt
/usr/share/seclists/Fuzzing/LFI/LFI-gracefulsecurity-linux.txt
/usr/share/seclists/Fuzzing/LFI/LFI-gracefulsecurity-windows.txt

# Command Injection
/usr/share/seclists/Fuzzing/command-injection-commix.txt

# SSTI (Server-Side Template Injection)
/usr/share/seclists/Fuzzing/template-engines-special-vars.txt

# Polyglot (testa SQLi + XSS + SSTI in una sola lista)
/usr/share/seclists/Fuzzing/Polyglots/polyglots.txt
Wordlist for Username Enumeration and Parameter Discovery #
Username Lists #
/usr/share/seclists/Usernames/top-usernames-shortlist.txt
/usr/share/seclists/Usernames/Names/names.txt

# Username formato Active Directory (first.last, flast, ecc.)
git clone https://github.com/urbanadventurer/username-anarchy
cat names.txt | ./username-anarchy > ad_usernames.txt
Parameter Discovery #
# Nomi di parametri GET/POST comuni (da ricerca Burp Suite)
/usr/share/seclists/Discovery/Web-Content/burp-parameter-names.txt

ffuf -w /usr/share/seclists/Discovery/Web-Content/burp-parameter-names.txt \
     -u "http://target.com/search?FUZZ=test" --hh 0
Endpoint Discovery API #
/usr/share/seclists/Discovery/Web-Content/api/api-endpoints.txt
/usr/share/seclists/Discovery/Web-Content/api/api-endpoints-res.txt
/usr/share/seclists/Discovery/Web-Content/swagger.txt
/usr/share/seclists/Discovery/Web-Content/graphql.txt

ffuf -w /usr/share/seclists/Discovery/Web-Content/api/api-endpoints.txt \
     -u http://target.com/api/FUZZ \
     -H "Content-Type: application/json" --hc 404,401
Wordlist Custom – CeWL and Crunch #
When generic wordlists aren't enough, generate a target-specific list.
CeWL – Wordlist from the Target Site #
CeWL collects words from the accessible content of the site by crawling the pages—often product names, internal codes, and corporate terminology not found in any generic list. Therefore, it should be considered an active collection tool with respect to the target (it generates actual requests to the site), not a passive one, and should be used only when permitted by the scope.
sudo apt install cewl -y

# Genera wordlist dalle parole del sito (depth 2, min 5 caratteri)
cewl http://target.com -d 2 -m 5 -w custom_wordlist.txt

# Include anche email trovate nel sito
cewl http://target.com -e -w wordlist_with_emails.txt

# Con autenticazione Basic
cewl http://target.com --auth_type basic \
     --auth_user admin --auth_pass password123 \
     -w auth_wordlist.txt

wc -l custom_wordlist.txt
Crunch – Wordlist from Pattern #
Generate wordlists based on specific patterns — when you know the password structure but not the value.
sudo apt install crunch -y

# Tutte le combo alfanumeriche di 6 caratteri
crunch 6 6 abcdefghijklmnopqrstuvwxyz0123456789 -o wordlist_6char.txt

# Pattern specifico: 4 lettere + 2 cifre (tipo "admin12")
crunch 6 6 -t @@@@%% > pattern_wordlist.txt
# @ = lowercase, % = cifra, ^ = uppercase, , = simboli

# Anno in coda (password2026, admin2026, ecc.)
crunch 4 4 2026 | sed 's/^/password/' > password_with_year.txt

# PIN a 4 cifre (0000-9999)
crunch 4 4 0123456789 > pins.txt
Clean and Optimize a Wordlist #
Before launching a wordlist (especially one generated or merged from multiple sources), it's worth cleaning it up:
# Rimuovi duplicati
sort -u input.txt > unique.txt

# Rimuovi righe vuote
sed '/^$/d' input.txt > clean.txt

# Ordina
sort input.txt > sorted.txt

# Conta le entry
wc -l input.txt

# Filtra per lunghezza (es. tra 6 e 20 caratteri)
awk 'length >= 6 && length <= 20' input.txt > filtered.txt
Alternative Collections #
SecLists vs Assetnote #
| SecLists | Asset note | |
|---|---|---|
| Focus | General purpose collection | Datasets derived from real crawling |
| Updates | Community repository | Lists periodically regenerated |
| Directory | ✅ | ✅ |
| DNS | ✅ | ✅ |
| Parameters | ✅ | ✅ |
| Ideal use | Basic toolkit for most scenarios | Advanced coverage on important engagements |
# Download (scegli la lista giusta da wordlists.assetnote.io)
wget https://wordlists-cdn.assetnote.io/data/manual/best-dns-wordlist.txt
wget https://wordlists-cdn.assetnote.io/data/automated/httparchive_parameters_top_1m_2024_01_28.txt
FuzzDB #
FuzzDB is a collection of payloads and patterns for security testing, useful for web fuzzing, error discovery, predictable resources, and injection testing. Compared to SecLists—a large general-purpose collection—FuzzDB is more focused on payloads and patterns specific to web application testing.
OneListForAll #
Deduplicated merge of the best wordlists per directory — a single list designed to work well as a first scan on any target.
git clone https://github.com/six2dez/onelistforallmicro
ffuf -w onelistforallmicro.txt -u http://target.com/FUZZ --hc 404
Complete Table – Which Wordlist for Which Scenario #
| Screenwriting | Recommended Wordlist | Path |
|---|---|---|
| Say quick win | common.txt | /usr/share/seclists/Discovery/Web-Content/ |
| Standard dir | raft-medium-directories.txt | same saying |
| In-depth dir | raft-large-directories.txt | same saying |
| WordPress Dir | CMS/wordpress.txt | same saying |
| Sensitive files | raft-medium-files.txt | same saying |
| Quick offline password | 10k-most-common.txt | .../Passwords/Common-Credentials/ |
| Standard offline password | rockyou.txt | /usr/share/wordlists/ |
| Auth online | top-passwords-shortlist.txt | .../Passwords/Common-Credentials/ |
| Default credentials | <servizio>-betterdefaultpasslist.txt | .../Passwords/Default-Credentials/ |
| Subdomain quick | subdomains-top1million-5000.txt | .../Discovery/DNS/ |
| Subdomain deep | n0kovo_subdomains | GitHub |
| SQL injection | Generic-SQLi.txt | .../Fuzzing/SQLi/ |
| XSS | XSS-Jhaddix.txt | .../Fuzzing/XSS/ |
| LFI | LFI-Jhaddix.txt | .../Fuzzing/LFI/ |
| Parameter names | burp-parameter-names.txt | .../Discovery/Web-Content/ |
| API endpoints | api-endpoints.txt | .../Discovery/Web-Content/api/ |
| Username | top-usernames-shortlist.txt | .../Usernames/ |
| Custom from target | CeWL | cewl http://target.com -w custom.txt |
Recommended Operational Path #
1. PRIMA DI TUTTO: installa SecLists
   └─ sudo apt install seclists -y

2. RECON WEB – sempre in questo ordine:
   └─ common.txt (quick win)
   └─ raft-medium-directories.txt (standard)
   └─ Se identifichi CMS/tecnologia → lista specifica

3. PASSWORD AUDITING:
   └─ Offline: rockyou.txt + regole hashcat/john
   └─ Online: lista piccola e specifica, attenzione a rate limit/lockout

4. SUBDOMAIN:
   └─ subdomains-top1million-5000.txt (quick)
   └─ n0kovo per engagement approfondito

5. FUZZING INJECTION:
   └─ Identifica i parametri prima con burp-parameter-names.txt
   └─ Poi lancia payload specifici (SQLi, XSS, LFI)

6. CUSTOM WORDLIST:
   └─ cewl sul target (se consentito dallo scope) → merge con SecLists base
   └─ cat custom.txt seclists.txt | sort -u > merged.txt
Troubleshooting #
| Problem | Cause | Solution |
|---|---|---|
rockyou.txt: No such file | Still compressed | gunzip /usr/share/wordlists/rockyou.txt.gz |
| SecLists not installed | Missing package | sudo apt install seclists -y |
| Wordlist too large, slow scan | Wrong list for now | Start with common.txt, progressively scales |
| 0 results with huge list | Target uses soft-404 | Test path absurd, filter by response size |
| CeWL finds few words | JavaScript-heavy site | Use greater depth: cewl -d 3 |
| Crunch generates huge files | Charset too wide | Narrow charset or limit maximum length |
FAQ #
What is the best wordlist for pentesting?
There's no universally best list—it depends on the scenario. For a general initial check: common.txtFor offline passwords: rockyou.txtThe rule is to start specific, not from the largest list.
Which wordlist should I use with ffuf?
It depends on the target: common.txt for a quick check, raft-medium-directories.txt for a standard, a CMS-specific list if you have identified the technology.
Which wordlist should I use for WordPress?
Discovery/Web-Content/CMS/wordpress.txt SecLists — Find WP-specific paths that a generic list doesn't cover.
What's the difference between SecLists and RockYou? They're not alternatives, they're complementary. RockYou is a single list of real passwords for offline cracking. SecLists is an entire library that includes, among other things, RockYou.
Which wordlist should I use for subdomain enumeration?
Discovery/DNS/subdomains-top1million-5000.txt for a quick check, n0kovo_subdomains for broader coverage on in-depth engagements.
How do I create a custom wordlist? Use CeWL, if the scope allows, to extract real words from the target site, or use crunch when you know a specific pattern to generate.
How do I reduce a wordlist that is too large?
Filtering by length (awk 'length >= 6 && length <= 20'), or by applying mutation rules to a smaller base list instead of using a huge one.
How do I merge two wordlists?
cat lista1.txt lista2.txt | sort -u > merged.txt — merges and removes duplicates in one step.
Wordlist Selection Checklist #
[ ] Identificato il tipo di test (directory, password, DNS, fuzzing...)
[ ] Identificata la tecnologia/CMS del target
[ ] Scelta una lista specifica prima di una generica
[ ] Eseguito un quick scan
[ ] Verificati falsi positivi / soft-404
[ ] Scalato a una lista più ampia solo se necessario
[ ] Generata wordlist custom se le liste standard non bastano
[ ] Rimossi duplicati e righe vuote
[ ] Filtrata per lunghezza dove utile
[ ] Applicate regole di mutazione prima di liste enormi (per password)
[ ] Salvata la wordlist finale per riuso
Final Cheat Sheet #
=== INSTALLAZIONE ===
SecLists:    sudo apt install seclists -y
rockyou:     gunzip /usr/share/wordlists/rockyou.txt.gz

=== PATH PRINCIPALI ===
SecLists:    /usr/share/seclists/
rockyou:     /usr/share/wordlists/rockyou.txt
DirBuster:   /usr/share/dirbuster/wordlists/

=== DIRECTORY FUZZING ===
Quick:       /usr/share/seclists/Discovery/Web-Content/common.txt
Standard:    /usr/share/seclists/Discovery/Web-Content/raft-medium-directories.txt
Deep:        /usr/share/seclists/Discovery/Web-Content/raft-large-directories.txt
WordPress:   /usr/share/seclists/Discovery/Web-Content/CMS/wordpress.txt
File:        /usr/share/seclists/Discovery/Web-Content/raft-medium-files.txt

=== PASSWORD ===
Offline standard:  /usr/share/wordlists/rockyou.txt
Online rapida:     /usr/share/seclists/Passwords/Common-Credentials/10k-most-common.txt
Default:           /usr/share/seclists/Passwords/Default-Credentials/<service>-betterdefaultpasslist.txt
Regole hashcat:    hashcat ... -r /usr/share/hashcat/rules/best64.rule

=== SUBDOMAIN ===
Quick:       /usr/share/seclists/Discovery/DNS/subdomains-top1million-5000.txt
Standard:    /usr/share/seclists/Discovery/DNS/subdomains-top1million-20000.txt
Deep:        n0kovo_subdomains (GitHub)

=== FUZZING ===
SQLi:        /usr/share/seclists/Fuzzing/SQLi/Generic-SQLi.txt
XSS:         /usr/share/seclists/Fuzzing/XSS/XSS-Jhaddix.txt
LFI:         /usr/share/seclists/Fuzzing/LFI/LFI-Jhaddix.txt
CmdInj:      /usr/share/seclists/Fuzzing/command-injection-commix.txt
SSTI:        /usr/share/seclists/Fuzzing/template-engines-special-vars.txt

=== PARAMETRI E API ===
Params:      /usr/share/seclists/Discovery/Web-Content/burp-parameter-names.txt
API:         /usr/share/seclists/Discovery/Web-Content/api/api-endpoints.txt
Swagger:     /usr/share/seclists/Discovery/Web-Content/swagger.txt

=== USERNAME ===
Quick:       /usr/share/seclists/Usernames/top-usernames-shortlist.txt
Full:        /usr/share/seclists/Usernames/Names/names.txt

=== CUSTOM WORDLIST ===
CeWL:        cewl http://target.com -d 2 -m 5 -w custom.txt
Crunch PIN:  crunch 4 4 0123456789 > pins.txt
Crunch alfa: crunch 6 8 abcdefghijklmnopqrstuvwxyz -o alpha.txt

=== PULIZIA ===
Merge+dedup: cat lista1.txt lista2.txt | sort -u > merged.txt
No righe vuote: sed '/^$/d' input.txt > clean.txt
Filtra lunghezza: awk 'length >= 6 && length <= 20' input.txt > filtered.txt
Related guides on hackita.it:
- John the Ripper: Password Cracking Complete
- Hashcat: GPU Password Cracking
- SQL Injection: A Complete Guide
- DNS: Basics and Attacks