VLANs and 802.1Q: Network Segmentation, Trunks, and VLAN Hopping in a Pentest

Learn how VLANs and 802.1Q work, the difference between access and trunk, native VLANs, inter-VLAN routing, DTP, double tagging, and VLAN hopping techniques in pentests.
- Posted on 2026-03-26
- Reading time: 8 min
VLANs are the primary mechanism by which enterprise networks separate traffic. Understanding what a VLAN is and how 802.1Q works is essential for pentesters: VLAN segmentation is often the only boundary between a user network, the server network, and the management network. If that segmentation is poorly configured, everything collapses. VLAN hopping is one of the most underrated techniques in an internal network pentesting engagement.
What is a VLAN? #
A VLAN (Virtual Local Area Network) is a mechanism that allows you to create logically separate local networks within the same physical infrastructure. Two hosts in the same VLAN behave as if they were on the same physical segment; two hosts in different VLANs cannot communicate without passing through a router or Layer 3 switch, even if they are physically connected to the same switch.
The standard that defines VLAN tagging on Ethernet networks is IEEE 802.1Q , ratified in 1998 and subsequently updated several times.
Before VLANs, separating traffic required dedicated hardware: separate physical switches for each segment. VLANs make this separation virtual and software-manageable, while still maintaining robust logical isolation—if configured correctly.
How 802.1Q Works #
The VLAN tag in the Ethernet frame #
802.1Q works by inserting a 4-byte tag into the Ethernet frame, between the MAC Source field and the original EtherType/Length field.
802.1Q Tag Structure:
| Countryside | Size | Description |
|---|---|---|
| TPID (Tag Protocol Identifier) | 2 bytes | 0x8100 — identifies the frame as tagged |
| PCP (Priority Code Point) | 3 bit | QoS Priority (802.1p) |
| DEI (Drop Eligible Indicator) | 1 bit | Frame droppable in case of congestion |
| VID (VLAN Identifier) | 12 bit | VLAN ID (1–4094) |
With 12 bits for the VLAN ID, the standard supports up to 4094 VLANs (0 and 4095 are reserved).
Access and Trunk Doors #
802.1Q switches distinguish two types of ports:
Access port belongs to a single VLAN. Incoming and outgoing traffic is not tagged with a VLAN; the switch adds or removes the tag transparently. Hosts connected to access ports never see VLAN tags.
Trunk Port: Carries traffic from multiple VLANs simultaneously. Frames retain the 802.1Q tag that identifies the VLAN they belong to. Trunk ports connect switches to each other, switches to routers, and switches to servers that manage multiple VLANs (hypervisors, firewalls).
Native VLAN On a trunk port, the native VLAN is the one whose traffic passes untagged. This is a critical security concept: a misconfigured native VLAN is the basis of double-tagging attacks.
Inter-VLAN routing #
Two hosts in different VLANs cannot communicate directly: traffic must pass through a Layer 3 device. The options are:
- Router-on-a-stick: a router with a single trunk interface, with virtual sub-interfaces for each VLAN
- Layer 3 switch (SVI): a switch with Switch Virtual Interface for each VLAN, which manages routing internally
- Firewall as inter-VLAN gateway: common configuration in environments with stringent security policies
Where VLANs are used in networks #
VLANs are the basic segmentation tool in any enterprise network:
- Departmental separation: HR VLAN, Finance VLAN, IT VLAN, Guest VLAN
- VoIP Networks: Separate voice VLAN from data VLAN for QoS and security
- Management Network: Dedicated VLAN for access to switches, routers and infrastructure devices
- Virtual DMZ: VLAN for exposed servers separate from the internal network
- OT/ICS Production Environments: VLAN to isolate industrial systems from the corporate network
- Data center: VLAN to separate tenants, environments (dev/test/prod), and storage traffic
In almost every internal network pentesting engagement, VLAN segmentation is the first thing to analyze: understanding how it is structured reveals the topology of the entire network and identifies the paths to the most sensitive targets.
Why VLANs are important in cybersecurity #
VLANs create logical boundaries that limit the propagation of attacks. An attacker in a user VLAN shouldn't see server VLAN traffic or reach the management VLAN—ideally.
In practice, VLAN misconfigurations are common and often critical:
- Native VLAN configured on trunk port equal to data VLAN
- Dynamic Trunking Protocol (DTP) active on access ports
- Switch access port configured on the management VLAN
- VLAN 1 (default) used as data or management VLAN
Understanding 802.1Q allows you to identify and exploit these misconfigurations. Information about VLANs present in a network often emerges passively from LLDP and ARP . The physical layer at which 802.1Q frames operate is described in the IEEE 802.3 Ethernet article.
VLAN in a pentesting engagement #
Reconnaissance: Identify existing VLANs #
The first step is to understand how many VLANs exist and how they are configured. The main sources:
LLDP/CDP: Reveals the VLANs configured on the port you are connected to, and sometimes the complete list of infrastructure VLANs.
lldpcli show neighborsARP scanning for VLANs: If you can send tagged traffic, you can discover in VLANs other than the one you are in.
Passive traffic: Observing 802.1Q tags in captured traffic identifies active VLANs in the segment.
tcpdump -i eth0 -nn -e vlanPost-compromise on switches: If you gain access to the CLI of a switch:
show vlan brief
show interfaces trunk
show cdp neighbors detail
VLAN topology enumeration #
Mapping VLANs means understanding:
- What VLANs exist and their purpose
- Which IP subnets are associated with each VLAN
- Where is the management VLAN located?
- Which VLANs contain high-value systems (servers, DCs, firewalls)
Combined with Nmap for each identified subnet, you get a complete map of the infrastructure.
Attack surface: VLAN hopping #
VLAN hopping is the technique of escaping your own VLAN and accessing other VLANs without authorization. There are two main methods.
Method 1 — Switch Spoofing (DTP Exploitation)
DTP (Dynamic Trunking Protocol) is a Cisco protocol that allows automatic trunk port negotiation. If enabled on an access port (the default configuration on many Cisco switches), an attacker can negotiate a trunk and receive traffic from all VLANs.
With Scapy or yersinia :
yersinia dtp -attack 1 -interface eth0If the negotiation is successful, the attacker's interface becomes a trunk port. Tagged frames can then be sent and received for any VLAN.
Method 2 — Double Tagging
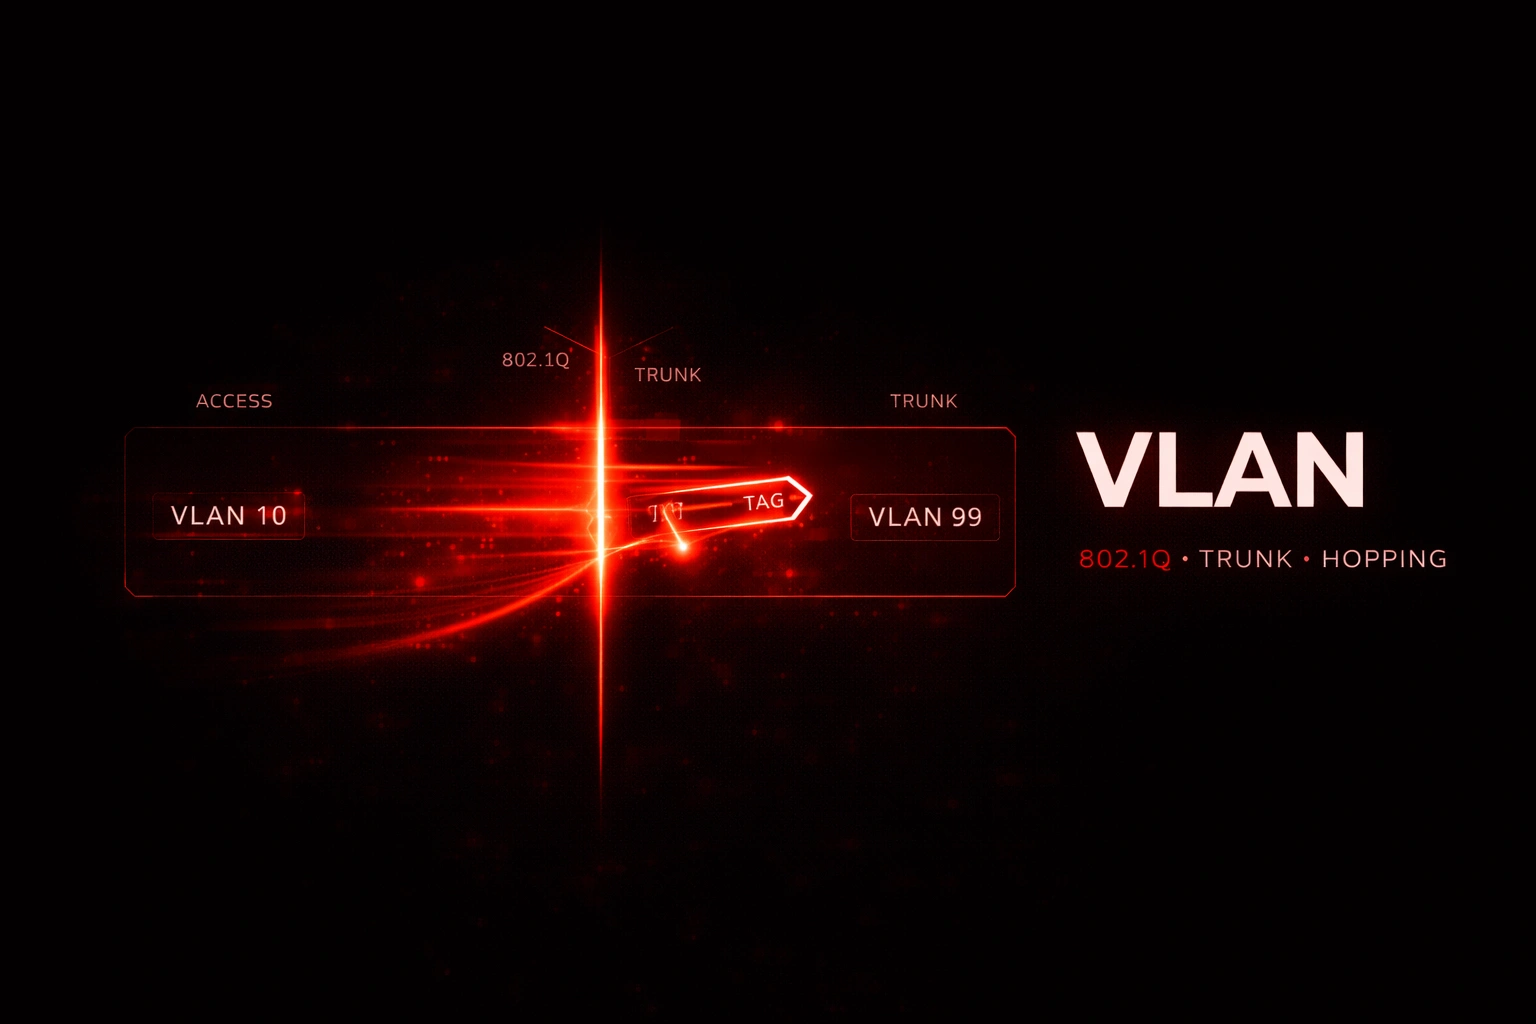
Double tagging exploits the native VLAN. The attacker constructs a frame with two nested 802.1Q tags:
- External tag: Native VLAN of the switch (e.g. VLAN 1)
- Internal tag: Target VLAN (e.g. VLAN 99 — management)
When the switch receives the frame, it removes the outer tag (native VLAN, untagged) and forwards the frame with the inner tag to another switch. The second switch sees the inner tag and routes the frame into the target VLAN.
Limitation: Double tagging is unidirectional. The frame arrives in the target VLAN, but responses return through normal routing—unless combined with man-in-the-middle techniques.
Pivoting across VLANs #
Once you have gained access to an additional VLAN (via hopping or rogue routing), you can:
- Access previously unreachable subnets
- Reach the management VLAN and attack the switches directly
- Move laterally to server VLANs or DMZs
- Intercept traffic from other VLANs with techniques sniffing
Possible attacks and abuses on VLANs #
Switch Spoofing via DTP #
As described: Negotiate a trunk using DTP enabled on access ports. This allows you to receive traffic from all VLANs on the trunk.
Double Tagging Attack #
Double-tagged 802.1Q frame to traverse the native VLAN and send traffic to other VLANs. Unidirectional but effective for reconnaissance.
VLAN 1 Abuse #
VLAN 1 is the default VLAN on virtually all switches. It's often used for management and STP traffic. If a host is in VLAN 1 or can access it, it has visibility into a lot of infrastructure traffic.
Rogue Switch #
Connect a rogue switch to the network and negotiate a trunk with DTP. The rogue switch receives traffic from all VLANs in the trunk, allowing for bulk sniffing.
Starvation of the CAM table combined with VLAN #
Combine a CAM table overflow attack with VLAN awareness to maximize visibility into traffic captured during switch flooding.
Practical examples with 802.1Q VLANs in the laboratory #
Configuring a VLAN-tagged interface on Linux #
ip link add link eth0 name eth0.10 type vlan id 10
ip link set eth0.10 up
ip addr add 192.168.10.100/24 dev eth0.10
You can now send and receive VLAN 10 tagged traffic from the interface eth0.10.
Sending double-tagged frames with Scapy #
from scapy.all import *

frame = Ether(dst="ff:ff:ff:ff:ff:ff") / \
        Dot1Q(vlan=1) / \
        Dot1Q(vlan=99) / \
        IP(dst="10.99.0.1") / \
        ICMP()

sendp(frame, iface="eth0")
VLAN Analysis with Wireshark #
View all tagged traffic:
vlanFilter by specific VLAN:
vlan.id == 99Identify double-tagged frames:
vlan && vlanEnumeration with yersinia #
yersinia is a tool for attacks on layer 2 protocols, including DTP:
yersinia -G  # interfaccia grafica
# oppure
yersinia dtp -attack 1 -interface eth0
802.1Q VLAN Detection and Defense #
A defender monitoring the network for VLAN attacks can detect:
- DTP frames on access ports: a switch should not receive DTP from user ports
- Doubly tagged 802.1Q frames: virtually never legitimate on gateways
- Sudden changes in the CAM table with abnormal tagged traffic: possible rogue switch
- Unexpected VLAN traffic from specific hosts: a user host sending tagged frames is suspicious
- Unauthorized trunk negotiation: log all port mode change events
VLAN Hardening and Mitigations #
Disable DTP on all access ports #
On Cisco switches, on each access port:
interface GigabitEthernet1/0/1
 switchport mode access
 switchport nonegotiate
switchport nonegotiate Disable DTP. Never leave ports in mode. dynamic auto o dynamic desirable.
Change the native VLAN on all trunks #
Never use VLAN 1 as the native VLAN on a trunk port. Assign a dedicated VLAN that isn't used elsewhere:
interface GigabitEthernet1/0/24
 switchport trunk native vlan 999
 switchport trunk allowed vlan 10,20,30,50
Do not use VLAN 1 for data or management traffic #
VLAN 1 should be empty or used only for STP control traffic. Never assign production hosts to VLAN 1.
Limit the VLANs allowed on each trunk #
Each trunk should carry only the VLANs that are absolutely necessary. Use switchport trunk allowed vlan to explicitly restrict.
802.1X on all access ports #
Authenticate devices before assigning them to a VLAN. When combined with a RADIUS server, it allows you to dynamically assign VLANs based on device identity.
Isolate the management VLAN #
The switch management VLAN should never be reachable from user VLANs. Inter-VLAN ACLs on Layer 3 switches or firewalls.
Common VLAN Mistakes #
“VLANs are a firewall.” No. VLANs provide logical separation of L2 traffic, but they don't enforce security policies. Inter-VLAN traffic passes through a router or L3 switch: if ACLs are absent or permissive, the separation is only apparent.
“VLAN 1 is safe if I don't use it” VLAN 1 is still present and active on all default ports. STP, CDP, VTP, and other control traffic often uses VLAN 1. Leaving hosts on VLAN 1 or not explicitly managing it is risky.
“VLAN hopping requires special hardware.” False. Any Linux PC running Scapy or Yersinia is sufficient to test DTP exploitation and double tagging.
“Changing the VLAN ID every now and then is protective” No. VLAN security depends on the correct configuration of the ports (access vs. trunk, DTP disabled, dedicated native VLAN), not on the secrecy of the VLAN IDs.
802.1Q VLAN FAQ #
What is a VLAN and what is it used for? A VLAN (Virtual Local Area Network) is a mechanism that allows you to logically separate network traffic on a shared physical infrastructure. Hosts in different VLANs cannot communicate without passing through a router, even if they are connected to the same physical switch.
What is VLAN hopping and how does it work? VLAN hopping is an attack technique that allows you to escape your own VLAN and send traffic to other VLANs without authorization. The main methods are switch spoofing via DTP and double tagging with nested 802.1Q frames.
Is VLAN segmentation enough to isolate networks? Not by itself. VLANs separate L2 traffic, but inter-VLAN traffic passes through a router or L3 switch. Without appropriate ACLs on that device, the separation is merely logistical, not security-related.
How do you check if DTP is enabled on a switch?
On Cisco: show dtp interface GigabitEthernet1/0/1. If the state is dynamic auto o dynamic desirable, DTP is active and the port is vulnerable to switch spoofing.
How many VLANs can you create with 802.1Q? The 802.1Q standard uses 12 bits for the VLAN ID, allowing for 4094 distinct VLANs (IDs 0 and 4095 are reserved). In practice, most switches support a few hundred to a few thousand simultaneously active VLANs.
Conclusion on 802.1Q VLANs #
VLANs are the backbone of segmentation in enterprise networks. Understanding how they work means understanding where network boundaries are, how they're constructed, and where they can fail.
DTP enabled on access ports, misconfigured native VLAN, unmanaged VLAN 1: these are real misconfigurations, present in many enterprise networks, that allow an attacker to cross boundaries that should be impermeable.
In an internal network pentesting engagement, VLAN reconnaissance is one of the first steps after initial positioning. Identifying the infrastructure's VLAN structure completely changes the view of the available attack surface.
Learn more about related protocols and techniques:
- Ethernet IEEE 802.3: frame and datalink layer
- ARP: discovery and spoofing
- LLDP: Passive Infrastructure Discovery
- STP and RSTP: Spanning Tree and Security
- Sniffing on local networks
- Man in the Middle: techniques and tools
- Nmap: port scanning and service detection
Official reference: IEEE 802.1Q — Bridges and Bridged Networks
Want to verify whether your infrastructure's VLAN segmentation can withstand an attack? A professional penetration test can make the difference before anyone else does. Contact us at hackita.it/servizi.
If HackITA helps you grow in the world of offensive security, you can support it here: hackita.it/supporto