rpcdump.py Inpacket: RPC Endpoint, UUID and Named Pipe

A guide to Impacket's rpcdump.py for enumerating Windows RPC endpoints, UUIDs, named pipes, and dynamic ports. Practical commands and analysis for pentesting.
- Posted on 2026-07-23
- Reading time: 8 min
rpcdump.py: Enumerate RPC Endpoints, UUIDs and Named Pipes on Windows #
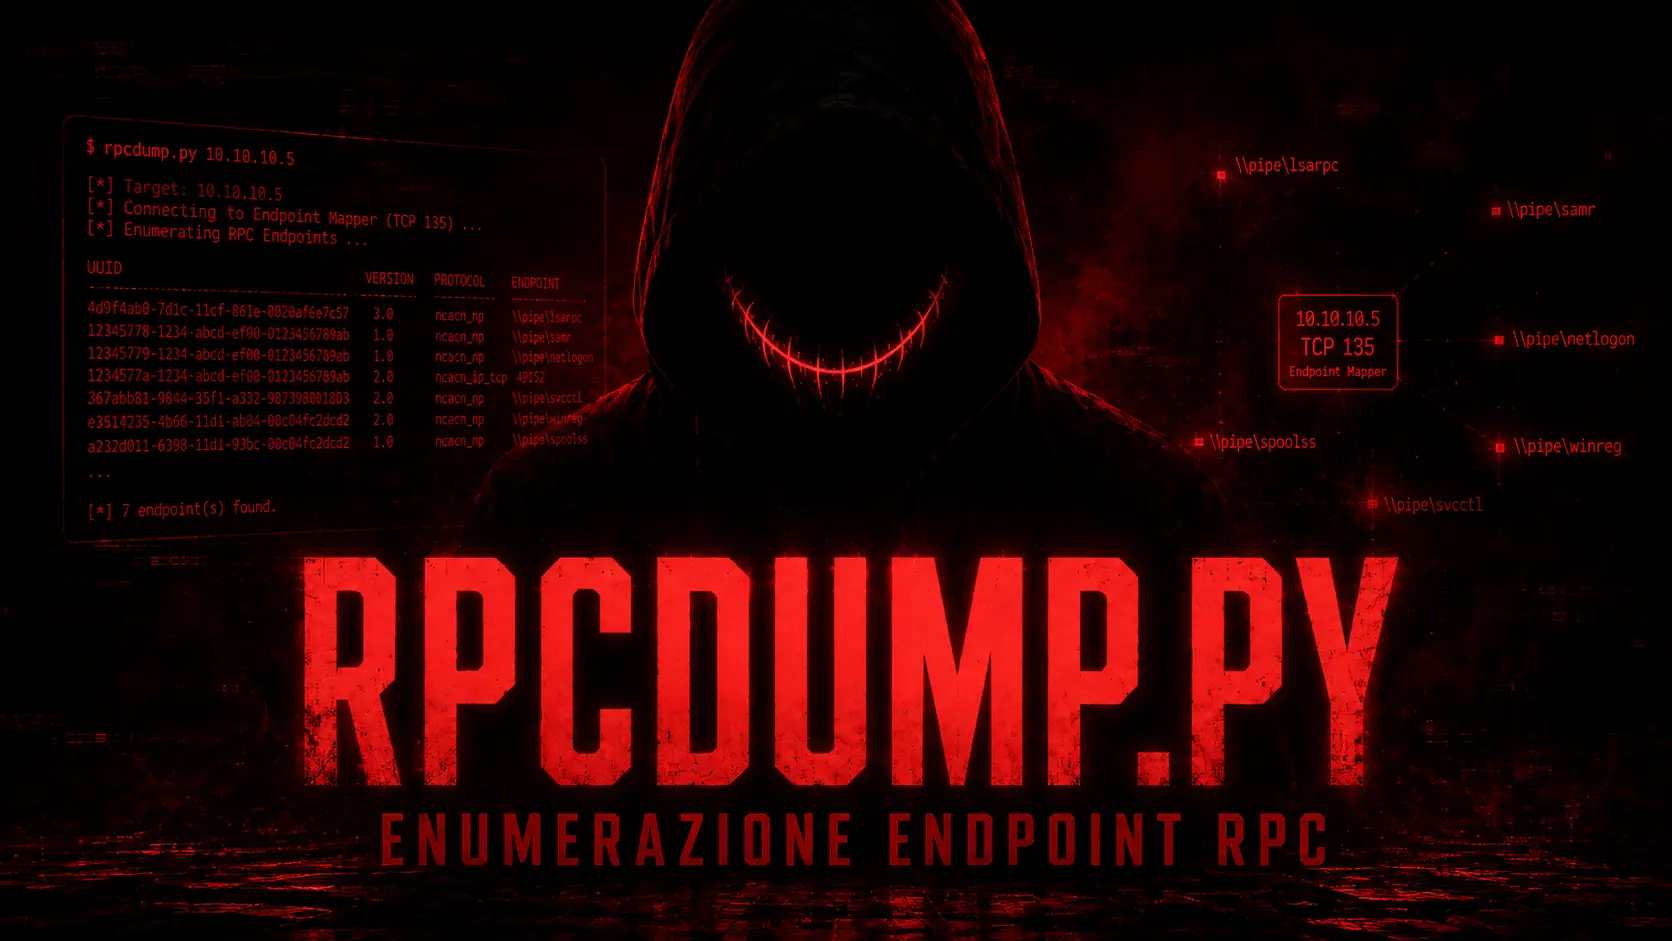
rpcdump.py is part of Packet and questions theEndpoint Mapper of Windows (gate 135) to return a list of all RPC interfaces registered on the host: UUID, protocol, binding (dynamic port or named pipe). It doesn't execute commands on the target — it's pure enumeration, complementary to what you do with rpcclient on the same named pipes. The result is a map of what's running on the host and on which channels it can be reached.
Attention right away: The presence of an interface in the output does not constitute a vulnerability. It only demonstrates that the interface is registered with the Endpoint Mapper. For it to be truly exploitable, other conditions must be met: the binding must be remotely reachable (ncacn_ip_tcp o ncacn_np, Not ncalrpc (which is local only), the RPC bind must complete, the user must have the required privileges, and the service must have a weak configuration or an applicable vulnerability.
Official reference: fortra/impacket — rpcdump.py Protocol documentation: MS-RPCE — Microsoft RPC Protocol
What is rpcdump.py used for? #
The Endpoint Mapper (TCP/135 port) is the Windows service that maps RPC clients to registered services. When an RPC service starts, it registers itself by communicating its UUID (interface identifier), the protocol (ncacn_ip_tcp, ncacn_np, ncalrpc) and the port or named pipe on which he listens.
rpcdump.py queries this registry and returns everything, then attempts to match each UUID to a known service to make it readable. This is typically used during enumeration, after identifying port 135 open with Nmap, to understand which services (Task Scheduler, SAM, Service Control Manager, WMI) are exposed and therefore potentially attackable — with the reservation seen above on the difference between presence and exploitability.
Does rpcdump require credentials? #
It depends on the port. Looking at the current source code:
- Door 135 and 593: no authentication — the Endpoint Mapper responds without credentials on these two channels
- Door 139 and 445: the credentials (password or Pass the Hash) are applied for SMB authentication, which is required to reach the Endpoint Mapper via
\pipe\epmapper - port 443: The credentials are only used for authentication at the RPC (RPC-over-HTTP) proxy, not at the MSRPC level.
rpcdump.py does not implement Kerberos —there are no flags -k o -no-pass in this version of the tool.
Syntax and options #
impacket-rpcdump [opzioni] [dominio/utente:password@]target| Option | Description |
|---|---|
-target-ip IP | Target IP — useful if the name doesn't resolve via DNS |
-port {135,139,443,445,593} | Port to connect to (default: 135) |
-hashes LM:NT | Pass-the-Hash — only applies to port 139/445 |
-debug | Verbose output for troubleshooting |
-ts | Adds timestamp to each log line |
What ports does rpcdump.py use? #
# Anonymous su 135 (default) — nessuna credenziale possibile né richiesta
impacket-rpcdump 10.10.10.5

# Con credenziali di dominio — autenticazione SMB su porta 445
impacket-rpcdump -port 445 corp.local/user:Password123@10.10.10.5

# Pass-the-Hash su porta 445
impacket-rpcdump -hashes :NThash -port 445 corp.local/administrator@10.10.10.5

# Via RPC over HTTP (593) — credenziali solo per il proxy
impacket-rpcdump -port 593 corp.local/user:pass@10.10.10.5

# IP separato dal nome (NetBIOS senza DNS)
impacket-rpcdump -target-ip 10.10.10.5 corp.local/user:pass@DC01
When 135 is filtered: rpcdump specifically reaches the Endpoint Mapper through \pipe\epmapper via SMB (port 445), authenticating with NTLMThis does not automatically make all other RPC interfaces on the host reachable — each service still has its own binding (dynamic or to a specific named pipe) that must be verified separately.
Output and how to read it #
Protocol: [MS-SAMR]: Security Account Manager (SAM) Remote Protocol
Provider: samsrv.dll
UUID    : 12345778-1234-ABCD-EF00-0123456789AC
Bindings:
          ncacn_np:\\DC01[\pipe\samr]
          ncacn_ip_tcp:10.10.10.5[49155]

Protocol: [MS-SCMR]: Service Control Manager Remote Protocol
Provider: services.exe
UUID    : 367ABB81-9844-35F1-AD32-98F038001003
Bindings:
          ncacn_np:\\DC01[\pipe\svcctl]
A binding ncalrpc (often seen by interfaces like modern Task Scheduler) indicates RPC communication local —it alone is not a surface reachable by the network. Search instead ncacn_ip_tcp o ncacn_np to understand what is really exposed remotely.
IOXIDResolver — Enumerate network interfaces without authentication #
Among the interfaces that rpcdump.py list there is often IObjectExporter (DCOM). His method ServerAlive2 responds without requiring any authentication and returns all the machine's network interfaces, including those on internal or IPv6 networks that aren't visible to a simple scan. This is the technique that made the HTB "APT" box famous: querying this method revealed an otherwise invisible IPv6 address.
# Con Impacket (script community IOXIDResolver.py, non incluso di default)
python3 IOXIDResolver.py -t 10.10.10.5

# Con rpcmap.py, forzando i binding numeri di opnum bassi sull'interfaccia DCOM
rpcmap.py -brute-opnums -opnum-max 5 ncacn_ip_tcp:10.10.10.5
Useful in two scenarios: when the host has multiple network cards (pivoting to segments that nmap doesn't see from the outside) or when there is an IPv6 configuration that the attacker didn't know about.
Which RPC UUIDs are most important during a pentest? #
During an authorized penetration test, the highest priority endpoints to check are those related to lateral movement, authentication coercion, and AD replication.
High priority offensive interfaces #
| UUID | Interface | Typical binding | Relevance | What it does NOT prove |
|---|---|---|---|---|
E3514235-4B06-11D1-AB04-00C04FC2DCD2 | MS-DRSR / DRSUAPI | Dynamic TCP (no named pipes) | AD replication, path DCSync | It does not demonstrate possession of the rights of reply |
91AE6020-9E3C-11CF-8D7C-00AA00C091BE | MS-ICPR / ICertPassage | \pipe\cert or dynamic TCP | RPC interface of a CA AD CS, which can then be verified with Certipy | It does not prove that relays or ESCs are usable |
367ABB81-9844-35F1-AD32-98F038001003 | MS-SCMR | \pipe\svcctl or TCP | Remote Service Management — psexec.py, smbexec.py | Does not demonstrate administrative privileges |
86D35949-83C9-4044-B424-DB363231FD0C | MS-TSCH/ITaskSchedulerService (modern) | Dynamic TCP | Modern Task Scheduler, used by atexec.py even away \pipe\atsvc on SMB | Does not demonstrate the right to create or start tasks |
1FF70682-0A51-30E8-076D-740BE8CEE98B | MS-TSCH / ATSvc legacy | \pipe\atsvc | Legacy Task Scheduler (AT command), used only by at.exe | Does not indicate that the system still supports legacy operations |
378E52B0-C0A9-11CF-822D-00AA0051E40F | MS-TSCH / SASec | \pipe\atsvc | Legacy Task Security Management | Does not demonstrate administrative access |
12345678-1234-ABCD-EF00-0123456789AB | MS-RPRN (Print Spooler) | \pipe\spoolss | Coercion Surface — PrinterBug/SpoolSample | It does not prove that PrintNightmare is present |
76F03F96-CDFD-44FC-A22C-64950A001209 | MS-PAR (asynchronous, same pipe spoolss) | \pipe\spoolss or dynamic TCP | Asynchronous print system interface, also used in PrintNightmare | Not to be confused with the MS-RPRN primary UUID |
C681D488-D850-11D0-8C52-00C04FD90F7E / DF1941C5-FE89-4E79-BF10-463657ACF44D | MS-EFSR / EFSRPC | \pipe\efsrpc (also via lsarpc, samr, lsass, netlogon) | Authentication coercion — PetitPotam technique | It does not demonstrate that the required RPC method is accepted |
4FC742E0-4A10-11CF-8273-00AA004AE673 | MS-DFSNM | \pipe\netdfs | DFS Management — DFSCoerce Surface | It does not demonstrate that the coercive call is authorized |
12345678-1234-ABCD-EF00-01234567CFFB | MS-NRPC / Netlogon | \pipe\netlogon or dynamic TCP | Secure channel, Zerologon (CVE-2020-1472) | Does not demonstrate vulnerabilities on patched systems |
Useful interfaces for enumeration and post-exploitation #
| UUID | Interface | Endpoint | Tools |
|---|---|---|---|
338CD001-2244-31F1-AAAA-900038001003 | MS-RRP (Remote Registry) | \pipe\winreg | Remote read/modify registry with appropriate permissions |
3DDE7C30-165D-11D1-AB8F-00805F14DB40 | MS-BKRP (BackupKey) | \pipe\protected_storage, \pipe\ntsvcs | Domain DPAPI Backup Keys |
12345778-1234-ABCD-EF00-0123456789AC | MS-SAMR | \pipe\samr or TCP | Enumerate users, groups, aliases |
12345778-1234-ABCD-EF00-0123456789AB | MS-LSAT / MS-LSAD | \pipe\lsarpc | SID-name translation, LSA policy, trust |
4B324FC8-1670-01D3-1278-5A47BF6EE188 | MS-SRVS (Server Service) | \pipe\srvsvc | Share, sessions, connections |
6BFFD098-A112-3610-9833-46C3F87E345A | MS-WKST (Workstation Service) | \pipe\wkssvc | Info about workstations, domains, and connected users |
82273FDC-E32A-18C3-3F78-827929DC23EA | MS-EVEN (Eventlog Remoting) | \pipe\eventlog | Remote reading of event logs — useful for enumerating past user sessions (see the LogHunter community tool). Affected by CVE-2025-29969 (Arbitrary file writing via TOCTOU) |
9556DC99-828C-11CF-A37E-00AA003240C7 | MS-WMI / IWbemServices | DCOM, dynamic TCP | WMI Query and Remote Management — is the interface used by wmiexec.py |
F309AD18-D86A-11D0-A075-00C04FB68820 | MS-WMI / IWbemLevel1Login | DCOM, dynamic TCP | Login and initialize WMI sessions |
Note on WMI: 8BC3F05E-D86B-11D0-A075-00C04FB68820 that you often see quoted is not the UUID of the interface IWbemServices — is the CLSID used for WMI activation via DCOM (WbemLevel1Login). The interface that actually executes the queries is IWbemServices, UUID 9556DC99-828C-11CF-A37E-00AA003240C7.
UUIDs are easy to confuse #
A single wrong digit completely changes the identified protocol:
| UUID | Protocol |
|---|---|
12345678-1234-ABCD-EF00-0123456789AB | MS-RPRN (Print Spooler) |
12345778-1234-ABCD-EF00-0123456789AB | MS-LSAT/MS-LSAD |
12345778-1234-ABCD-EF00-0123456789AC | MS-SAMR |
12345678-1234-ABCD-EF00-01234567CFFB | MS-NRPC (Netlogon) |
Grep to filter the output #
# Trova solo named pipe
impacket-rpcdump corp.local/user:pass@10.10.10.5 | grep "pipe\\"

# Cerca Print Spooler (coercizione)
impacket-rpcdump corp.local/user:pass@10.10.10.5 | grep -i "spool\|12345678-1234-ABCD-EF00-0123456789AB"

# Cerca NTDS Replication (percorso DCSync)
impacket-rpcdump corp.local/user:pass@10.10.10.5 | grep "E3514235"

# Cerca Netlogon (Zerologon)
impacket-rpcdump corp.local/user:pass@10.10.10.5 | grep "12345678-1234-ABCD-EF00-01234567CFFB"

# Export completo per analisi
impacket-rpcdump corp.local/user:pass@10.10.10.5 > rpcdump_output.txt
grep -E "Protocol:|UUID|ncacn_np|ncacn_ip_tcp" rpcdump_output.txt
What is the difference between rpcdump.py and rpcmap.py? #
rpcmap.py This complements rpcdump: it tests direct bindings on specific interfaces without going through the Endpoint Mapper. It's useful when the epmapper is filtered but you already know of an open high port (found with Nmap) or you want to verify a specific named pipe binding.
# Enumera interfacce sulla porta 135
rpcmap.py ncacn_ip_tcp:10.10.10.5[135]

# Su porta alta specifica (trovata con nmap)
rpcmap.py ncacn_ip_tcp:10.10.10.5[49155]

# Via named pipe, con autenticazione SMB (transport) diversa dall'auth RPC
rpcmap.py -auth-transport corp.local/user:pass 'ncacn_np:10.10.10.5[\pipe\samr]'

# Pass-the-Hash sia a livello RPC che di trasporto
rpcmap.py -hashes-rpc :NThash -hashes-transport :NThash ncacn_ip_tcp:10.10.10.5[135]
When the server requires authenticated clients (policy “Restrict Unauthenticated RPC Clients”), the standard enumeration call (MGMT) fails. In that case rpcmap.py It has an internal database of known UUIDs and tries to bind each one individually to figure out which interfaces actually exist:
# Forza il tentativo di bind su ogni UUID noto, ignorando l'MGMT bloccato
rpcmap.py -auth-level 1 ncacn_ip_tcp:10.10.10.5[135]

# Con livello di autenticazione più alto e credenziali
rpcmap.py -auth-level 6 -auth-rpc corp.local/user:pass ncacn_ip_tcp:10.10.10.5[135]
rpcdump in an enumeration workflow #
1. nmap -sV -p 135 10.10.10.0/24 → identifica host con RPC esposto
2. rpcdump.py → mappa i servizi esposti e le named pipe
3. rpcclient -U '' -N target → prova sessione null diretta sulle pipe trovate (samr, lsarpc)
4. Identifica vettori da approfondire (verificando SEMPRE binding e privilegi reali):
   \pipe\samr → enumerazione SAM
   \pipe\svcctl → psexec/smbexec (se hai creds admin)
   \pipe\atsvc → atexec.py
   \pipe\spoolss → verifica coercizione (PrinterBug/SpoolSample)
   E3514235 (DRSUAPI) → percorso DCSync, se sei DA
5. rpcmap.py → approfondimento su porte/pipe specifiche, o bypass se l'MGMT è bloccato
6. IObjectExporter / ServerAlive2 → se serve scoprire altre interfacce di rete (IPv6, altre schede)
Detection: What your monitors really see #
What is an opnum, in a nutshell: Each RPC interface exposes several functions (e.g., "create service," "read registry"); the opnum is simply the number that identifies WHICH function you called—sort of like the number of an option in a phone menu. Knowing the opnum tells you exactly what action you performed, not just which service you spoke to.
Knowing not only which UUID triggers an alert, but which opnum does so, tells you exactly what makes one tool noisy compared to another—useful for understanding OPSEC choices, not just for the blue team.
| Interface | UUID | Critical Opnum | What does it mean? |
|---|---|---|---|
| MS-SCMR | 367ABB81-9844-35F1-AD32-98F038001003 | 0xC (RCreateServiceW) / 0x18 (RCreateServiceA) | Creating Remote Service — psexec.py |
| MS-TSCH | 86D35949-83C9-4044-B424-DB363231FD0C | 0x1 (SchRpcRegisterTask) | Task Recording — atexec.py |
| MS-EFSR | C681D488-D850-11D0-8C52-00C04FD90F7E | 0x0 / 0x4 | PetitPotam calls coercion |
| MS-RRP | 338CD001-2244-31F1-AAAA-900038001003 | — (the entire interface is responsive) | Remote access to the registry |
In practice: a tool that only calls SchRpcRegisterTask generates a specific, recognizable event regardless of the task name (random or not) — the signature is on the opnum, not on the superficial details.
What defenders use to block, not just log: In addition to native Event IDs, there are solutions such as RPC firewall (Zero Networks) that inject themselves into the RPC server process and allow blocking by UUID+opnum+source IP — for example blocking 367ABB81-... From any host other than an authorized jump box, this disables psexec/smbexec without affecting the rest of the service. Knowing this exists helps explain an abnormal failure (access denied even with correct credentials) during an assessment.
On the other side, researchers on these interfaces use tools like MS-RPC-Fuzzer (based on NtObjectManager) to bombard each RPC procedure with mutated input and discover crashes or anomalous behavior—a complementary approach to rpcdump, geared toward finding vulnerabilities rather than enumerating existing surface areas.
Common mistakes #
| Error | Cause | Solution |
|---|---|---|
Connection refused | Port 135 filtered | Try it now -port 445 |
MSRPC SessionError: access_denied | SMB authentication failed or denied | Verify credentials, try another user |
DCE/RPC connection failed | Firewall blocks high dynamic ports | Usa -port 445 to switch from SMB |
| Empty output | Host does not have Endpoint Mapper active | Check with nmap that 135/445 are open |
| No useful interface on updated targets | Null sessions disabled (default from Windows 10 Anniversary onwards) | Try with even minimal valid credentials, or verify \pipe\samr with rpcclient |
FAQ #
What is rpcdump.py used for? It lists all RPC services registered on a Windows host via the Endpoint Mapper (port 135), displaying the UUID, protocol, and binding (port or named pipe) for each. It doesn't execute commands, just enumeration.
Does rpcdump.py require credentials? Only on ports 139/445 (SMB authentication) and partially on 443 (only for RPC proxy). On 135 and 593, it works without credentials; no authentication is required.
What ports does rpcdump.py use?
135 (default), 139, 443, 445, 593. When 135 is filtered, it passes through 445 reaching the Endpoint Mapper via \pipe\epmapper.
Does the presence of a UUID mean the service is vulnerable? No. It just proves that the interface is registered. You then need to verify that the binding is remotely reachable, that the RPC binding is successful, that you have the correct privileges, and that the service has a weak or vulnerable configuration.
What's the difference between rpcdump.py and rpcmap.py? rpcdump queries the Endpoint Mapper and returns the complete list. rpcmap tests a specific binding you already know (port or pipe), useful when the epmapper is filtered or when MGMT is blocked by policy.
Why does rpcdump show an ncalrpc binding?
ncalrpc It's local-only RPC communication, on the same machine — it's not reachable from the network. If you only see ncalrpc for an interface, that is not a remote attack surface.
Cheat sheet #
# Base (anonymous su 135, nessuna credenziale possibile)
impacket-rpcdump 10.10.10.5

# Con credenziali (autenticazione SMB su 445)
impacket-rpcdump -port 445 corp.local/user:pass@10.10.10.5

# Pass-the-Hash (solo su 139/445)
impacket-rpcdump -hashes :NThash -port 445 corp.local/user@10.10.10.5

# Via RPC over HTTP
impacket-rpcdump -port 593 corp.local/user:pass@10.10.10.5

# Filtra named pipe
impacket-rpcdump corp.local/user:pass@10.10.10.5 | grep "pipe\\"

# Cerca Print Spooler (coercizione)
impacket-rpcdump corp.local/user:pass@10.10.10.5 | grep -i "spool\|12345678-1234-ABCD-EF00-0123456789AB"

# Cerca DRSUAPI (percorso DCSync)
impacket-rpcdump corp.local/user:pass@10.10.10.5 | grep "E3514235"

# Cerca Netlogon (Zerologon)
impacket-rpcdump corp.local/user:pass@10.10.10.5 | grep "12345678-1234-ABCD-EF00-01234567CFFB"

# rpcmap su porta o pipe specifica
rpcmap.py ncacn_ip_tcp:10.10.10.5[49155]
rpcmap.py 'ncacn_np:10.10.10.5[\pipe\samr]'
For use in authorized environments only.