Recon OSINT: Tool, theHarvester, Shodan and Google Dorks.

Passive OSINT reconnaissance for pentesters: Collect emails, subdomains, exposed devices, and metadata with theHarvester, Google Dorks, Shodan, and Metagoofil.
- Posted on 2026-08-18
- Reading time: 11 min
Reconnaissance in Pentesting: Passive Recon and OSINT #
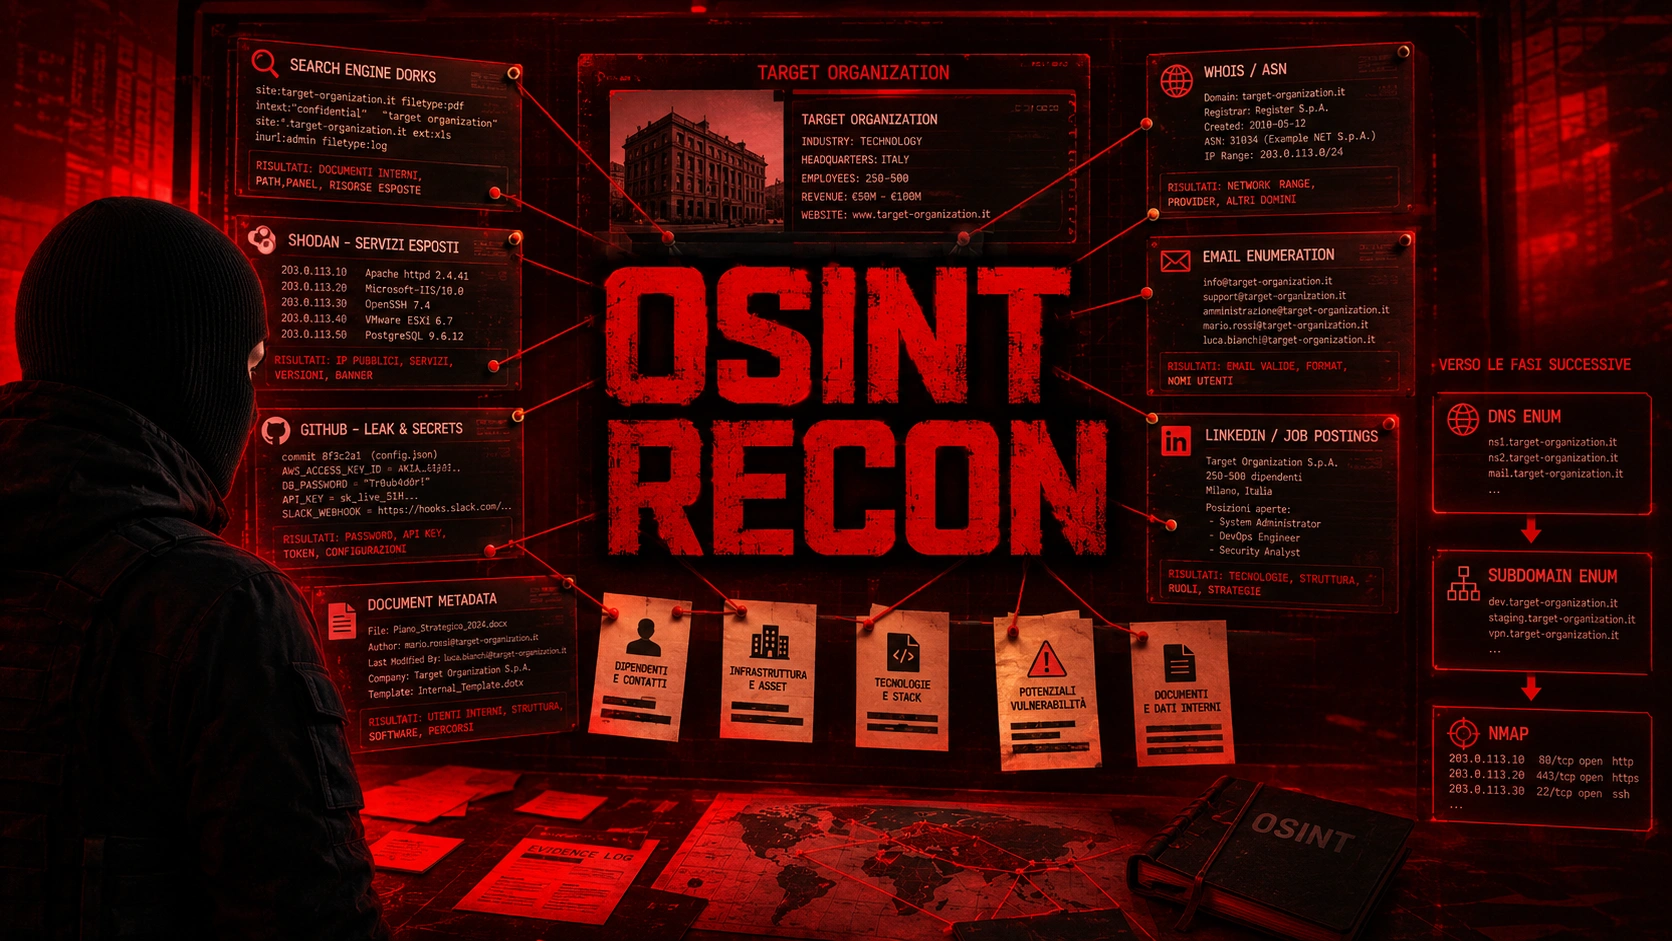
Reconnaissance in pentesting is the process of gathering information about a target before enumeration and scanning. Passive reconnaissance uses public sources—search engines, WHOIS, Shodan, GitHub, social media—without sending direct requests to the target's infrastructure. Build a complete profile of the target—employee emails, technology stack, exposed documents, internet-accessible devices, leaked credentials—before opening nmap.
A well read target in reconnaissance is worth more than hours of aggressive scanning: you can identify company addresses, roles and naming conventions useful for evaluating the attack surface and simulating authorized social engineering scenarios, identifying an exposed VPN gateway on Shodan, a .sql Google-indexed backup, or credentials in a public GitHub repo.
Prerequisites: None — this is the first step in any engagement. The results feed DNS , subdomain enumeration, nmap , and all subsequent steps.
What is Reconnaissance in Pentesting? #
Reconnaissance is the systematic collection of information about a target before directly interacting with its infrastructure. It is divided into two categories with very different implications for OPSEC.
Passive vs Active Reconnaissance #
| Type | Interaction with the target | Examples |
|---|---|---|
| passive | No live broadcast | Google, Shodan, WHOIS, crt.sh, GitHub, VirusTotal |
| Active | Chain drive | DNS queries to target nameservers, port scan, banner grabbing |
Most of this article covers passive reconnaissance: you query pre-populated databases and sources (Google, Shodan, WHOIS, Certificate Transparency), without touching the target's servers. The exceptions are commands dig/host for reverse resolution and, further down the pipeline, nmap scanning — those do generate observable traffic to the target infrastructure, and are active, not passive, reconnaissance/enumeration.
Reconnaissance vs. Enumeration #
- Recognition → What can I learn about the target from public sources before touching it?
- Enumeration → What services, hosts, and accounts actually exist and are verified directly?
- Scanning → Which ports and services are accessible now?
These are sequential phases: reconnaissance feeds enumeration, which feeds targeted scanning.
Order of Operations #
RECON (questo articolo)          → DNS/SUBDOMAIN ENUM → PORT SCAN → EXPLOITATION
theHarvester, Shodan, Dorks         dig, puredns           nmap
Email, documenti, tech stack        AXFR                   service detection
Recon fuels everything: knowing that the target uses Cisco ASA (found on Shodan) tells you to look for Cisco CVEs. Knowing that an employee is named Mario Rossi tells you to try m.rossi@, mario.rossi@, mrossi@ as a username pattern — useful for password spraying or brute force against Active DirectoryKnowing that the target uses AWS (from a LinkedIn job posting) tells you to look for exposed S3 buckets.
theHarvester – Email, Subdomain, IP from Public Sources #
theHarvester queries search engines, DNS databases, LinkedIn, and other sources to collect emails, subdomains, and IP addresses associated with the target domain, without directly touching its servers.
# Se non è già installato
sudo apt install theharvester -y
theHarvester --help

# Scan base con Google
theHarvester -d target.com -b google

# Scan con Bing (a volte indicizza più cose di Google)
theHarvester -d target.com -b bing

# LinkedIn – trova nomi di dipendenti
theHarvester -d target.com -b linkedin

# Combina più fonti
theHarvester -d target.com -b google,bing,linkedin,dnsdumpster

# Tutto quello che ha
theHarvester -d target.com -b all -l 500

# Salva output in file XML e HTML
theHarvester -d target.com -b all -f recon_output

# Con proxy Burp Suite (per vedere le query che fa)
theHarvester -d target.com -b google --proxy 127.0.0.1:8080[*] Emails found:
mario.rossi@target.com
info@target.com
helpdesk@target.com
admin@target.com
[*] Hosts found:
mail.target.com:203.0.113.20
vpn.target.com:203.0.113.40
dev.target.com:10.0.0.50
[*] IPs found:
203.0.113.10
203.0.113.20
203.0.113.40What to do with the results:
- Email: formulates the naming pattern (
nome.cognome@,ncognome@) → use for username enumeration on authentication services, or for authorized phishing simulations - Subdomain: add to list for DNS enumeration and active subdomain enumeration
- IP: switch to Shodan to see what runs on those IPs, then to Nmap for the complete port scan
Typical mistake: blindly trusting theHarvester's results. Some emails are false positives extracted from the wrong context. Always check the naming pattern on 2-3 emails found before using them.
Google Dorks – Find What Shouldn't Be Indexed #
Google Dorks are advanced queries that use special operators to find specific information indexed by Google—sensitive files, admin panels, exposed directories, backups, credentials.
Fundamental Operators #
| Operator | What does he do | Example |
|---|---|---|
site: | Restrict to domain | site:target.com |
filetype: | File type | filetype:pdf site:target.com |
intitle: | Word in the title | intitle:"index of" site:target.com |
inurl: | Word in URL | inurl:admin site:target.com |
intext: | Word in text | intext:"password" site:target.com |
ext: | File extension | ext:env site:target.com |
- | Exclude | site:target.com -www |
"..." | Exact string | "mario.rossi" target.com |
Dork for Sensitive Files #
# File di configurazione e backup
site:target.com ext:env
site:target.com ext:conf
site:target.com ext:cfg
site:target.com ext:ini
site:target.com ext:bak
site:target.com ext:sql
site:target.com ext:log

# Documenti con info potenzialmente sensibili
site:target.com filetype:pdf
site:target.com filetype:xlsx
site:target.com filetype:xls "password"
site:target.com filetype:doc "confidential"
site:target.com filetype:pptx "internal only"

# File .env e credenziali (sviluppatori) — poi testa i parametri trovati con SQL injection
site:github.com "target.com" ext:env
site:github.com "target.com" "api_key"
site:github.com "target.com" "password"
site:github.com "target.com" "secret"
Dork for Admin Panels and Login #
# Pannelli di amministrazione — trovato un /admin? Testalo con Burp Suite e directory fuzzing
inurl:admin site:target.com
inurl:login site:target.com
inurl:wp-admin site:target.com
inurl:phpmyadmin site:target.com
inurl:cpanel site:target.com
inurl:webmail site:target.com
intitle:"admin panel" site:target.com
intitle:"login" inurl:admin site:target.com
Dork for Exposed Directories #
# Directory listing aperte
intitle:"index of" site:target.com
intitle:"index of" "backup" site:target.com
intitle:"index of" ".git" site:target.com
intitle:"index of" "/uploads" site:target.com
Dork for Technology Stack #
# Identifica tech usata (utile prima di cercare CVE specifici)
site:target.com "Powered by WordPress"
site:target.com "Apache/2"
site:target.com "nginx/"
site:target.com "IIS"
site:target.com intext:"Django" OR intext:"Laravel" OR intext:"Spring Boot"
Dork on GitHub #
# Cerca nel codice sorgente su GitHub
site:github.com "target.com" "password"
site:github.com "target.com" "api_key" OR "apikey" OR "api-key"
site:github.com "target.com" "secret" OR "token"
site:github.com org:targetorg "internal"
site:github.com "@target.com" password
Google may display CAPTCHAs or temporarily limit queries if you send too many in a row—this isn't a hard and fast rule, but it happens often. Use a regular browser, pause between searches, or alternate with Bing, which often indexes different things.
Shodan – Devices Exposed on the Internet #
Shodan indexes internet-connected devices (servers, routers, IoT, ICS, cameras) with banners for each open port. The Shodan database search is passive with respect to the target—you don't touch it; Shodan has already scanned it with its own infrastructure.
# Installa CLI Shodan
pip install shodan
shodan init TUA_API_KEY

# Cerca per dominio
shodan domain target.com

# Cerca per IP specifico
shodan host 203.0.113.10

# Cerca per hostname
shodan search "hostname:target.com"

# Cerca per certificato SSL (trova tutti i host con cert per target.com)
shodan search "ssl.cert.subject.cn:target.com"

# Cerca per organizzazione (trova tutto l'ASN)
shodan search "org:\"Target Corporation\""

# Cerca tecnologie specifiche esposte
shodan search "hostname:target.com product:Apache"
shodan search "hostname:target.com port:3389"   # RDP esposto
shodan search "hostname:target.com port:22"     # SSH esposto

# Cerca vulnerabilità note su host del target
shodan search "net:203.0.113.0/24 vuln:CVE-2021-44228"  # Log4Shell

# Trova dispositivi AD (utile prima di attaccare Active Directory)
shodan search "hostname:target.com port:88"   # Kerberos
shodan search "hostname:target.com port:389" # LDAP# Output shodan host 203.0.113.10
IP: 203.0.113.10
Organization: Target Corporation
OS: Windows Server 2019
Open ports:
80/tcp Apache httpd 2.4.51
443/tcp Apache httpd 2.4.51
3389/tcp Microsoft Terminal Services ← RDP esposto!
8443/tcp Apache Tomcat/9.0.54Shodan Dork Utili #
hostname:target.com http.title:"admin"
hostname:target.com http.title:"dashboard" 200
hostname:target.com port:3306   # MySQL
hostname:target.com port:5432   # PostgreSQL
hostname:target.com port:27017  # MongoDB
hostname:target.com port:6379   # Redis (spesso senza auth)
hostname:target.com port:9200 product:Elastic
Censys – Search Engine for Internet Assets #
Censys covers the same space as Shodan (devices and services exposed on the internet), but with a more focused focus on hosts and certificates rather than just service banners.
| Shodan | censys |
|---|---|
| Banner/service oriented | Host/certificate oriented |
| Great for identifying services and versions | Great for certificates and asset correlation |
| Quick door/product queries | Useful for mapping an organization's entire certified infrastructure |
# Ricerca via web UI: search.censys.io
# Query per organizzazione
services.tls.certificates.leaf_data.subject.organization: "Target Corporation"

# Query per hostname
services.tls.certificates.leaf_data.subject_dn: "target.com"
Use Shodan and Censys together: often a device missing from one appears in the other, especially for hosts with special TLS certificates.
Certificate Transparency and crt.sh #
Publicly issued TLS certificates end up in Certificate Transparency logs — freely searchable, often revealing subdomains, staging/dev environments, and forgotten infrastructure that doesn't appear anywhere else.
curl -s "https://crt.sh/?q=%.target.com&output=json" | \
  jq -r '.[].name_value' | \
  sed 's/\*\.//g' | \
  sort -u
The results feed directly into the subdomain enumeration phase — it's often the first place hosts like staging-old.target.com o dev-2019.target.com that no one remembers having exposed anymore.
WHOIS and ASN – Network Footprint #
WHOIS can reveal domain ownership and administrative contact information—but not always: privacy protections and regulations like the GDPR often obscure this data, especially for domains registered in Europe. The ASN reveals the IP ranges owned by the organization, which is important for understanding the full scope.
# WHOIS base
whois target.com
# Se non oscurato: registrar, admin email, name server, data di scadenza

# WHOIS su IP
whois 203.0.113.10
# Rivela: Organization, Country, Net Range, CIDR

# Trova ASN dell'organizzazione
whois -h whois.radb.net -- '-i origin AS12345'

# Tutti gli IP range di un ASN
# bgpview.io/asn/12345#prefixes

# Risoluzione inversa (IP → hostname)
dig -x 203.0.113.10 +short
host 203.0.113.10
VirusTotal – Passive DNS and Infrastructure Intelligence #
VirusTotal isn’t just a malware scanner: its “Relations” section correlates domains, subdomains, IPs, historical DNS records, and certificates—useful for finding infrastructure connected to the target that other sources don’t show.
# Via API (richiede API key gratuita)
curl -s "https://www.virustotal.com/api/v3/domains/target.com/subdomains" \
  -H "x-apikey: TUA_API_KEY" | jq -r '.data[].id'

# Passive DNS: IP storici associati al dominio
curl -s "https://www.virustotal.com/api/v3/domains/target.com" \
  -H "x-apikey: TUA_API_KEY" | jq '.data.attributes.last_dns_records'
Useful in combination with crt.sh: where crt.sh shows issued certificates, VirusTotal shows historical DNS relationships between assets.
Wayback Machine – Historical Reconnaissance #
The Internet Archive preserves historical snapshots of web pages—often revealing old subdomains, removed endpoints, forgotten files, and superseded but still referenced technologies.
# Tutti gli URL archiviati per un dominio
curl -s "http://web.archive.org/cdx/search/cdx?url=*.target.com/*&output=text&fl=original&collapse=urlkey" \
  | sort -u > wayback_urls.txt

# Filtra per estensioni interessanti
grep -E "\.(env|sql|bak|config|json)$" wayback_urls.txt

# Con gau (Wayback + Common Crawl + OTX insieme)
gau target.com | sort -u > gau_urls.txt
Particularly useful for finding old API endpoints that are still active but no longer linked, or parameters that reveal decommissioned application logic.
Email Enumeration – Find the Pattern and Verify #
Once theHarvester finds some emails, it extracts the naming pattern and finds other employees. This phase fuels username enumeration and, later in the engagement, authentication tests—not to be confused with credential dumping, which only occurs after access has already been gained.
# Hunter.io (API con piano gratuito limitato)
curl "https://api.hunter.io/v2/domain-search?domain=target.com&api_key=TUA_KEY" | \
  jq '.data.pattern'
# Output: "{first}.{last}" → mario.rossi@target.com

# Verifica se un indirizzo esiste (SMTP verify)
curl "https://api.hunter.io/v2/email-verifier?email=mario.rossi@target.com&api_key=TUA_KEY" | \
  jq '.data.result'
# Output: "deliverable" oppure "undeliverable"

# Estrai nomi dipendenti da LinkedIn (manuale nel browser → azienda → persone)

# Genera wordlist di email da lista di nomi con username-anarchy
git clone https://github.com/urbanadventurer/username-anarchy
cat nomi.txt | ./username-anarchy --input-format firstname_lastname \
  | sed 's/$/@target.com/' > email_list.txt
Document Metadata – Metagoofil #
PDF, Word, and Excel documents published on the target site contain metadata: author name, Windows username, software used, and internal filesystem paths.
# Installa
sudo apt install metagoofil -y

# Scarica e analizza tutti i PDF del sito
metagoofil -d target.com -t pdf -l 50 -o output_pdf/

# Analizza anche doc, xls, pptx
metagoofil -d target.com -t pdf,doc,xls,ppt,docx,xlsx -l 100 -o output_docs/# Analisi manuale di un PDF con exiftool
sudo apt install exiftool
exiftool documento.pdfWhat are you looking for in metadata:
- Username → try as an SSH, VPN, RDP username, or as a base for attacks against Active Directory
- Software versions → look up CVE for that version
- Internal path → reveal internal directory structure
- Email address → confirm the naming pattern
Social Media and GitHub Intelligence #
LinkedIn – Tech Stack and People #
# Ricerche manuali su LinkedIn:

# 1. Trova dipendenti IT/Security
# LinkedIn search → People → Company: Target → Department: IT

# 2. Analizza job posting per tech stack
# Job posting per "DevOps Engineer": "AWS, Kubernetes, Terraform, Jenkins"
# → Il target usa AWS + k8s + Terraform + Jenkins, cerca misconfigurazioni note

# 3. Estrai email dal pattern trovato
# Se Mario Rossi → mario.rossi@target.com (da hunter.io)
# Allora Giulia Bianchi → giulia.bianchi@target.com
GitHub – Credentials and Config Leak #
# Con trufflehog: cerca secret in repos pubblici dell'organizzazione
curl -sSfL https://raw.githubusercontent.com/trufflesecurity/trufflehog/main/scripts/install.sh | sh

trufflehog github --org=targetorg --only-verified
trufflehog git https://github.com/targetorg/repo --only-verified# Dork manuali su GitHub (nel browser):
target.com "api_key"
target.com "password" "BEGIN RSA"
target.com "mongodb+srv://"
target.com "s3.amazonaws.com" "access_key"Additional OSINT Sources #
| Pig iron | Information |
|---|---|
| crt.sh | TLS Certificates, Subdomains |
| VirusTotal | Passive DNS, relationships between infrastructures |
| censys | Hosts, certificates, internet assets |
| Wayback Machine | Old versions, decommissioned endpoints |
| GitHub | Source code, secrets exposed |
| Have I Been Pwned | Check if emails/domains appear in known breaches |
You don't need to use all of them on every engagement — they're tools to pull out when the main sources (theHarvester, Google, Shodan) aren't enough or when the target is large.
recon-ng – OSINT Automation Framework #
recon-ng is a framework with workspaces, modules, and an integrated database for organizing larger reconnaissances.
recon-ng

[recon-ng] > workspaces create target_com
[recon-ng][target_com] > db insert domains
> domain: target.com

[recon-ng][target_com] > marketplace install recon/domains-hosts/hackertarget
[recon-ng][target_com] > marketplace install recon/domains-contacts/whois_pocs
[recon-ng][target_com] > marketplace install recon/hosts-hosts/shodan_ip

[recon-ng][target_com] > modules load recon/domains-hosts/hackertarget
[recon-ng][target_com][hackertarget] > run

[recon-ng][target_com] > modules load recon/domains-contacts/whois_pocs
[recon-ng][target_com][whois_pocs] > run

[recon-ng][target_com] > marketplace install reporting/html
[recon-ng][target_com] > modules load reporting/html
[recon-ng][target_com][html] > set FILENAME /tmp/recon_report.html
[recon-ng][target_com][html] > run
SpiderFoot – Automatic OSINT #
SpiderFoot automates dozens of OSINT modules in a single run with a web interface.
pip install spiderfoot
spiderfoot -l 127.0.0.1:5001
# Apri browser su http://127.0.0.1:5001
# Nuovo Scan → Inserisci target.com → Seleziona moduli → Start
Useful modules in SpiderFoot: Shodan, Censys, VirusTotal for IP/host intelligence; Have I Been Pwned for email in breach; Hunter.io for email patterns; crt.sh for certificate transparency; DNS/WHOIS for network info; LinkedIn/GitHub for social and code recon.
Recommended Operational Path #
1. WHOIS + ASN
   └─ whois target.com → nameserver, contatti (se non oscurati), org
   └─ bgpview.io → IP range dell'organizzazione

2. THEHARVESTER
   └─ theHarvester -d target.com -b all -l 500
   └─ Raccogli: email, subdomain, IP

3. GOOGLE DORKS
   └─ File sensibili: ext:env, ext:sql, ext:bak
   └─ Admin panels: inurl:admin, intitle:"index of"
   └─ GitHub: site:github.com "target.com" "password"

4. SHODAN + CENSYS
   └─ shodan domain target.com
   └─ Porte, tecnologie, versioni software esposte

5. CERTIFICATE TRANSPARENCY + VIRUSTOTAL + WAYBACK
   └─ crt.sh per sottodomini da certificati
   └─ VirusTotal per passive DNS
   └─ Wayback per endpoint storici

6. LINKEDIN + JOB POSTING
   └─ Dipendenti IT/Security, tech stack, pattern email

7. METAGOOFIL
   └─ Username Windows, path interni, versioni software

8. GITHUB SCAN
   └─ trufflehog + dork manuali per credenziali

9. CONSOLIDA
   └─ Subdomain → DNS enumeration → subdomain enumeration attiva
   └─ IP → nmap port scan
   └─ Email/username → test di autenticazione, phishing simulation
   └─ Tech stack → tool specifici (WPScan per WordPress, ecc.)
Reconnaissance Checklist #
[ ] Target scope definito e autorizzato
[ ] Domini principali identificati
[ ] Sottodomini raccolti (theHarvester, crt.sh, VirusTotal)
[ ] ASN e CIDR identificati
[ ] IP correlati
[ ] Certificati analizzati (crt.sh, Censys)
[ ] Tecnologie identificate
[ ] Email pubbliche raccolte
[ ] Naming convention identificata
[ ] Documenti pubblici analizzati
[ ] Metadata estratti
[ ] GitHub analizzato
[ ] Leak pubblici verificati (Have I Been Pwned)
[ ] Asset Shodan/Censys correlati
[ ] Vecchi asset analizzati (Wayback Machine)
[ ] Risultati consolidati
[ ] Passaggio a enumeration attiva
Mistakes to Avoid in Passive Reconnaissance #
- Scan the target without explicit permission
- Manually verify ports or services during a declared passive phase
- Send test emails to found addresses
- Attempting to log in on uncovered panels
- Actively interact with passively identified services
- Download more data than necessary for engagement
- Using credentials found in public leaks without explicit authorization
- Confusing (potentially old) indexed data with the actual current state of the target
Troubleshooting #
| Problem | Cause | Solution |
|---|---|---|
| theHarvester finds 0 emails | Small or poorly indexed domain | Try it now -b bing e -b linkedin separately |
| Google displays CAPTCHA | Too many fast queries | Manual pause, use Bing as an alternative |
| Shodan requires API key | You need an account | Register on shodan.io, check the limits of your current plan |
| Metagoofil cannot find documents | Site with few public documents | Try Google manually: site:target.com filetype:pdf |
| very slow trufflehog | Lots of repos to scan | Usa --only-verified and limits the org |
| recon-ng modules not installing | Proxy or firewall | marketplace install requires direct internet connection |
| WHOIS does not show contacts | Privacy protection active | Normal with GDPR — try ASN/IP WHOIS or alternative sources |
FAQ #
What is passive reconnaissance? Collecting information about a target using only pre-populated public sources (search engines, WHOIS, Shodan, certified transparency), without sending direct requests to the target's infrastructure.
What's the difference between reconnaissance and enumeration? Reconnaissance collects what's publicly known about the target. Enumeration directly verifies, by interacting with the infrastructure, which services and accounts actually exist.
What tools are used for reconnaissance? theHarvester, Google Dorks, Shodan, Censys, WHOIS, crt.sh, VirusTotal, Wayback Machine, Metagoofil, recon-ng, and SpiderFoot cover most cases.
Is Shodan passive reconnaissance? Your search in the Shodan database does—it doesn't generate traffic to the target. Shodan itself, however, collects that data through its own active scanning activities across the internet.
What information can be collected during reconnaissance? Emails, subdomains, IP addresses, technologies used, public documents with metadata, employees and roles, leaked credentials, TLS certificates, and historical infrastructure.
What's the first step in reconnaissance? Usually, WHOIS and ASN to understand the network scope, followed by theHarvester for emails and subdomains.
Is passive reconnaissance legal? You're reading already indexed public data, without sending requests to the target. Always check the engagement rules before starting, and don't confuse passive recon with active actions (logins, tests, mass downloads).
How do I use the found emails? Identify the naming pattern, generate a list from employee names found on LinkedIn, verify with Hunter.io or SMTP, and use them for authentication tests or authorized phishing simulations—not for credential dumping, which is a later and different step.
Final Cheat Sheet #
=== THEHARVESTER ===
Singola fonte:     theHarvester -d target.com -b google
Multi-fonte:       theHarvester -d target.com -b google,bing,linkedin,dnsdumpster
Tutto:             theHarvester -d target.com -b all -l 500 -f output

=== GOOGLE DORKS ===
File sensibili:    site:target.com ext:env OR ext:sql OR ext:bak
Admin panels:      inurl:admin site:target.com
Dir listing:       intitle:"index of" site:target.com
GitHub leak:       site:github.com "target.com" "password" OR "api_key"
Documenti:         site:target.com filetype:pdf OR filetype:xlsx

=== SHODAN / CENSYS ===
Setup:             pip install shodan && shodan init API_KEY
Per dominio:       shodan domain target.com
Per IP:            shodan host IP
SSL cert:          shodan search "ssl.cert.subject.cn:target.com"
Censys:            search.censys.io → services.tls.certificates.leaf_data.subject.organization

=== CERTIFICATE TRANSPARENCY ===
crt.sh:            curl -s "https://crt.sh/?q=%.target.com&output=json" | jq -r '.[].name_value' | sort -u

=== WHOIS / ASN ===
WHOIS:             whois target.com
Reverse WHOIS:     whois 203.0.113.10
ASN IP ranges:     bgpview.io/asn/AS12345

=== VIRUSTOTAL / WAYBACK ===
VT subdomains:     curl -s ".../domains/target.com/subdomains" -H "x-apikey: KEY"
Wayback URLs:      curl -s "http://web.archive.org/cdx/search/cdx?url=*.target.com/*&output=text"

=== EMAIL ENUMERATION ===
theHarvester:      theHarvester -d target.com -b all
Pattern:           curl "https://api.hunter.io/v2/domain-search?domain=target.com&api_key=KEY"
Username gen:      cat nomi.txt | ./username-anarchy | sed 's/$/@target.com/'

=== METAGOOFIL ===
PDF:               metagoofil -d target.com -t pdf -l 50 -o out/
Tutti i tipi:      metagoofil -d target.com -t pdf,doc,xls,ppt,docx,xlsx -l 100 -o out/
Exiftool:          exiftool documento.pdf

=== GITHUB / TRUFFLEHOG ===
Org scan:          trufflehog github --org=targetorg --only-verified
Repo singolo:      trufflehog git https://github.com/org/repo --only-verified

=== RECON-NG ===
Start:             recon-ng
Workspace:         workspaces create target_com
Modulo:            marketplace install recon/domains-hosts/hackertarget → run
Report:            modules load reporting/html → run
Related guides on hackita.it:
- DNS: Basics and Attacks
- Nmap: Port Scanning and Service Detection
- SQL Injection: A Complete Guide
- Burp Suite: Intercept and Analyze HTTP Traffic
- Credential Dumping: How to Mine Hash
- John the Ripper: Password Cracking Complete
- Hashcat: GPU Password Cracking
- Responder: Hash Capture NTLM
- Active Directory: Complete Attack Paths
- Kerberoasting: Service Account Attacks
- Impacket: Tool Suite for AD
- Linux Privilege Escalation
References #
- OSINT Framework – osintframework.com
- Google Hacking Database (GHDB) – exploit-db.com/google-hacking-database
#tools #reconnaissance