OAuth 2.0: Tokens, Scope, and Risks of Third-Party Tools | HackITA

How OAuth 2.0 works, what scope and access tokens are, and how to protect your company's social media accounts from token theft in third-party tools.
- Posted on 2026-09-21
- Reading time: 4 min
OAuth 2.0: How It Works, Tokens, Scope, and Risks #
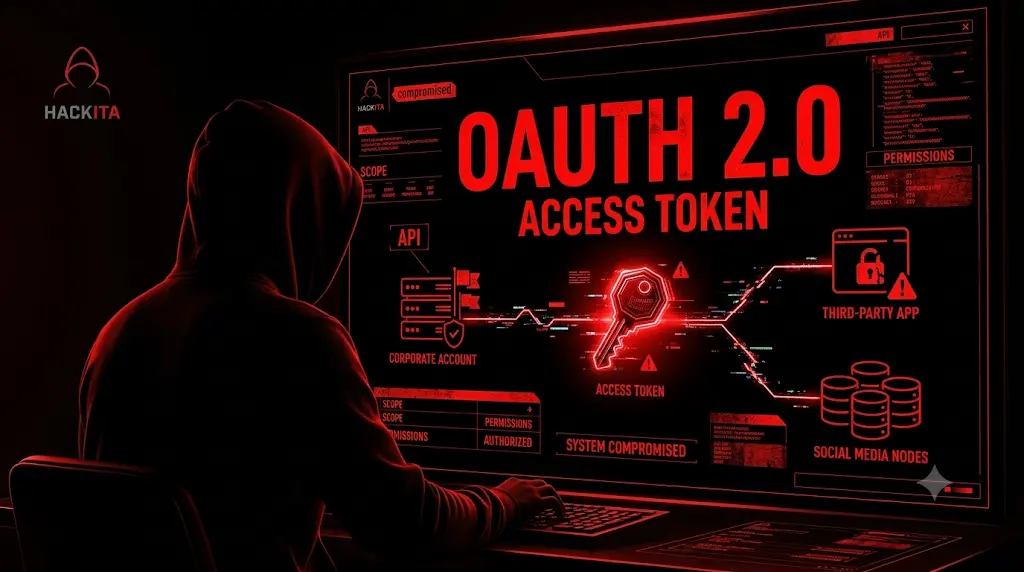
OAuth 2.0 is the protocol that comes into play whenever you connect an external tool to your LinkedIn, Facebook, or Instagram account. Authorizing it is much more than a simple confirmation click: you're granting an access token that, depending on the permissions requested, can allow sensitive account operations—often without having to re-authenticate each time.
In short : OAuth 2.0 allows an application to obtain delegated access to a user's resources without knowing their password. The access token represents this authorization, and its actual power depends on the scope, duration, and controls applied by the system that issues it and the APIs that accept it.
What is OAuth 2.0? #
OAuth 2.0 is the standard protocol that allows a third-party application to access resources on behalf of a user, without the user directly sharing their password with that application. Instead of a password, the app receives an access token with a defined scope (permissions).
How does OAuth work with social networks? #
The typical flow is:
Utente → autorizza l'app → Authorization Server (es. LinkedIn/Meta) → Access Token → chiamate API
| Element | Function |
|---|---|
| Resource Owner | The user granting access |
| Client | The third-party tool |
| Authorization Server | The platform (LinkedIn, Facebook, etc.) |
| Access Token | The credential used for API calls |
| Scope | Permits actually granted |
What are OAuth Scopes? #
Scopes define exactly what operations an app can perform on behalf of the user: reading profile, reading posts, publishing, managing pages, reading messages. Conceptually: read_profile, publish_posts, manage_pages (real names vary from platform to platform).
In general, the more privileges an access token is granted, the greater the impact of its compromise. The actual capabilities available, however, depend on the platform's specific APIs and permissions: OAuth 2.0 defines the delegation mechanism, not a universal set of scopes such as publish_posts o manage_pages.
Why are third-party tools a risk? #
Social media management and content automation tools often combine two factors: broad publishing permissions and the ability to connect to multiple accounts/platforms simultaneously from a single dashboard. This makes them an attractive target—compromising one can mean access to multiple company channels at once.
An example of this category is AI tools for generating social content, such as carousel generators for LinkedIn : tools that, depending on the integration, require publishing permissions on the linked company page.
What happens if an access token is stolen? #
Technical precision is needed here: an access token is not automatically equivalent to a password . Its actual impact depends on the scopes granted, its validity period, the possibility of revocation, and the APIs to which it grants access.
| Scope compromise | Possible impact |
|---|---|
| Profile reading | Information theft |
| Data reading | Data exposure |
| Publication | Malicious posts in the company's name |
| Messages | Phishing launched from the account |
| Page management | Compromising corporate presence |
How can an OAuth token be compromised? #
| Carrier | What happen |
|---|---|
| Token leakage | Token ends up in logs, URLs, or unprotected storage |
| Consent phishing | The user authorizes a malicious application thinking it is legitimate |
| Misconfigured redirect URI | Facilitates authorization code/token theft |
| Client compromise | The attacker gains access to the system that manages the tokens, a scenario close to a classic one session hijacking applied to OAuth tokens |
| Supply Chain | The tool provider itself is compromised |
For protocol-specific attack mechanisms, we've covered them in detail in our OAuth Attack deep dive.
OAuth token vs. password: what's the difference? #
| Credential | Feature |
|---|---|
| Password | Authenticate the user directly |
| API key | Identify/authorize an application |
| OAuth access token | Grants delegated and limited access to specific resources |
OAuth isn’t about “giving your password to an app” — it’s about delegating limited access without ever sharing it.
Compromise scenario #
ADMIN
  │ autorizza
  ▼
TOOL DI TERZE PARTI
  │ riceve access token
  ▼
LINKEDIN / META (API)
  │
  ▼
POST / MESSAGGI / DATI ESPOSTI- The administrator connects the tool to his social account
- The tool receives an access token with defined scopes
- The system storing the token is compromised (malware, vendor-side breach, stolen credentials)
- The attacker uses the token to interact with the APIs within the granted scopes
- The company notices the anomaly, revokes the token and removes the integration
This type of scenario generally concerns any tool with direct access to social media accounts and automatic publishing, such as a social media post generator connected to multiple platforms. The point isn't to avoid these tools, which are still useful, but to treat the authorization as access that should be monitored over time—much like a phishing attempt targeting a company account.
How to protect business accounts #
Quick checklist if you manage corporate accounts connected to OAuth tools:
- Check connected apps periodically: LinkedIn (Settings → Connected Apps), Facebook Business Settings → Integrations
- Revoke access to tools no longer in use: a forgotten token is a token that no one controls
- Limit scopes when connecting, when the platform allows it
- Use dedicated accounts for third-party tools, separate from the main administrator account
- Enable MFA on your primary account and monitor any anomalous activity
OAuth Security: Best Practices #
- Principle of least privilege on requested scopes
- Periodic revocation of unused tokens
- Token rotation where applicable
- Refresh token protection
- Using PKCE in public streams (apps without client secrets)
- Precisely configured redirect URIs, never wildcards
- Constant monitoring of authorized applications
These recommendations follow the guidance in IETF RFC 9700 (January 2025), the most up-to-date technical reference on OAuth 2.0 flow security.
FAQ: OAuth and Access Tokens #
What is an OAuth token? An OAuth access token is a credential that allows an application to access certain resources on behalf of the user, within the granted privileges (scope).
Is an OAuth token like a password? Not exactly. The token grants access without revealing the password, but if stolen, it can be used within the privileges and duration provided by the token itself.
Does OAuth bypass MFA? Not really. A valid token can allow API requests without re-authentication because login and consent have already occurred during the initial OAuth flow—MFA isn't "bypassed," it simply doesn't need to be re-done for every subsequent call to the token.
What happens if an access token is stolen? The impact depends on the scopes granted and the resources the token allows access to—it's not uniform or automatically total.
How can I protect my OAuth tokens? By limiting requested scopes, revoking unused permissions, and periodically monitoring the apps connected to your social media accounts.