Dradis Framework: Reporting, Findings, and Pentest Automation

Discover Dradis Framework: import findings from Nessus, Nmap, and Burp, organize evidence, and generate consistent pentest reports. A practical guide.
- Posted on 2026-09-23
- Reading time: 5 min
Dradis Framework: How to Centralize Pentest Findings #
A real pentest produces output from different tools— Nessus , Nmap, Burp Suite, manual notes, screenshots. At the end of the engagement, someone needs to collate it all into a coherent report. Doing it manually in Word is slow, error-prone, and each consultant writes their findings differently. Dradis solves exactly this: a central point where everything converges, with a uniform output format.
When to use it: Any pentest/red team with multiple tools and/or multiple people involved, where a consistent final report is needed. Coverage: Installation, import from external tools, Issue Library, report generation. Doesn't cover: The advanced features of the Professional Edition (Rules Engine, real-time results portal, Jira/ServiceNow integration)—here we focus on the free, open-source Community Edition.
Phase 0 — Understanding the logic before the commands #
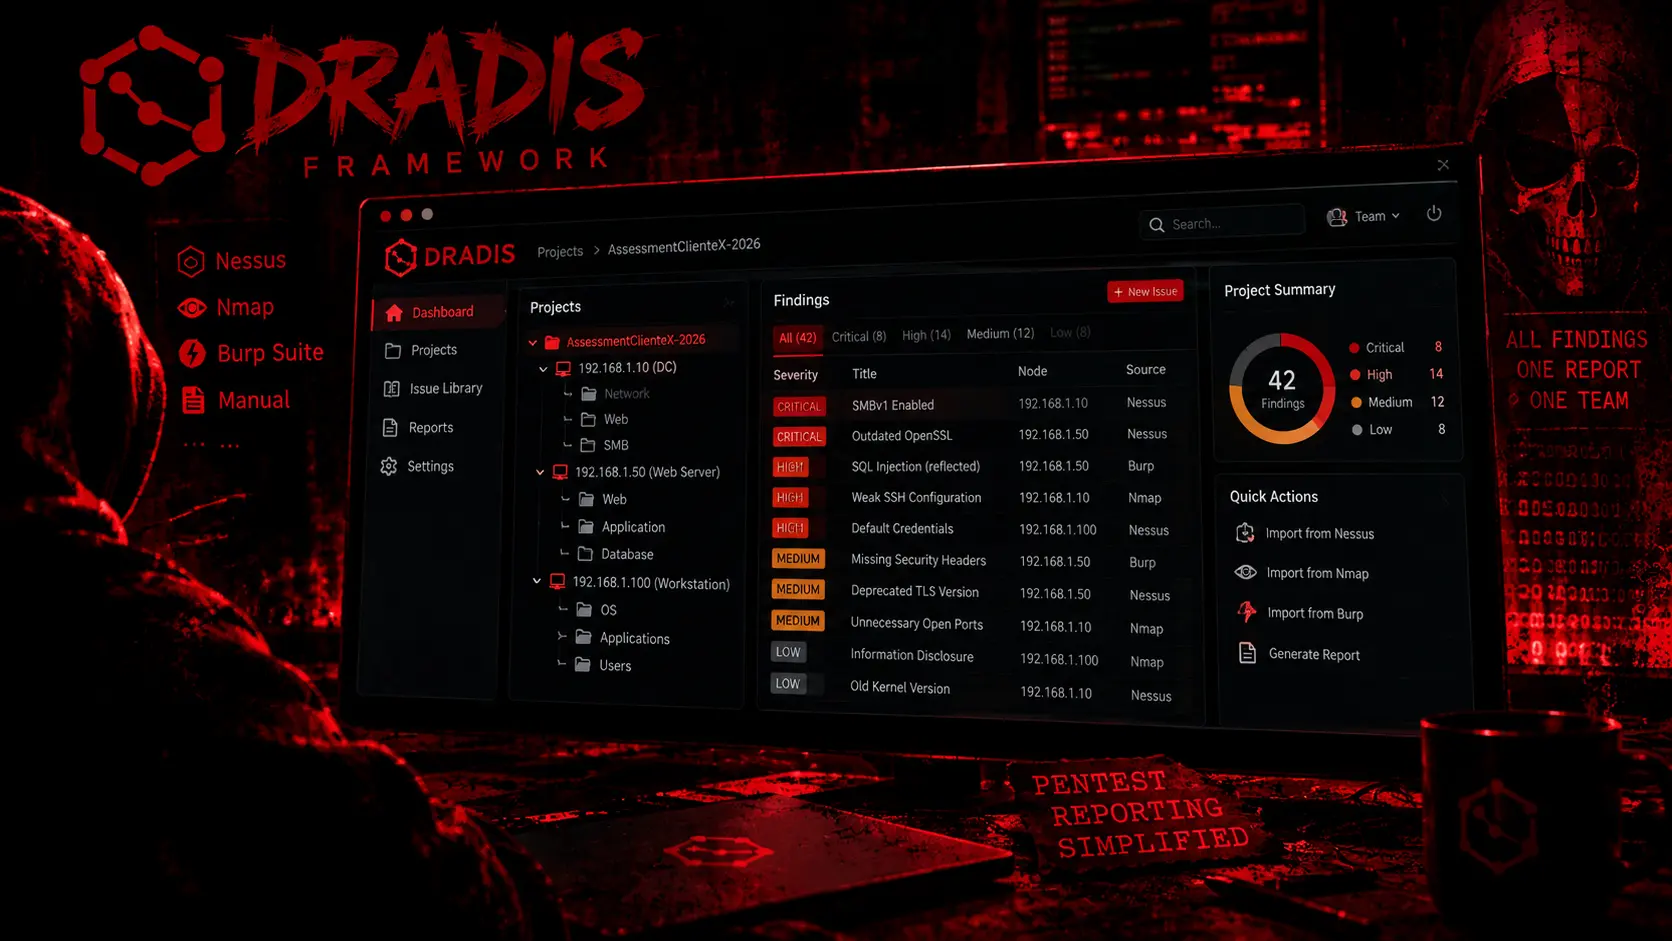
Dradis organizes everything around three concepts:
- Project — the specific engagement (a customer, a date, a scope)
- Node — a host/target within the project (tree structure)
- Issue — the actual finding, associated with one or more Nodes as evidence
The central idea: Instead of writing the same finding (“SMBv1 enabled”) from scratch every time, you write it once in the Issue Library and reuse it — even across projects.
Phase 1 — Installation #
Kali Linux (pre-installed) #
# Avvia il servizio
dradis-start

# Ferma il servizio
dradis-stop
On Kali the historical command dradis it is deprecated — use dradis-start/dradis-stop.
From source (other distros) #
git clone https://github.com/dradis/dradis-ce.git
cd dradis-ce

# Segui le istruzioni del repo per bundle install e setup del database
# (richiede Ruby on Rails, essendo Dradis un'applicazione Rails)
Admission #
http://127.0.0.1:3000or, depending on the configuration:
https://127.0.0.1:3004When you log in for the first time, set a shared password —unlike many tools, Dradis CE doesn't use individual user accounts, but a single team password for the project. The "Login" field is only used to label who did what, not for authentication.
Phase 2 — Create the Project and Structure #
After logging in, create the tree structure that represents your engagement:
1. Crea un "branch" (nodo) principale → rinominalo con il nome del progetto
   (es. "AssessmentClienteX-2026")

2. Click destro → "Add child" per creare la gerarchia
   Esempio struttura:
   AssessmentClienteX
   ├── 192.168.1.10 (DC)
   ├── 192.168.1.50 (Web Server)
   └── 192.168.1.100 (Workstation)
Think about your structure before you start importing data — reorganizing it later with hundreds of findings already imported is more laborious.
Phase 3 — Import from External Tools (the true value of Dradis) #
Dradis supports direct import from dozens of scanners — Nessus , Nmap, Burp Suite, Qualys, and many others.
Import output Nessus #
Menu → Import from file → Nessus

Carica il file .nessus esportato dal tuo scan
Every scanned host becomes a Node, every vulnerability an Issue — automatically, without copying anything by hand.
Import Nmap output #
Menu → Import from file → Nmap
Carica l'output XML (nmap -oX output.xml)
Import output Burp Suite #
Menu → Import from file → Burp
Carica l'export XML di Burp
⚠️ Practical note: Direct import populates the scanner's raw findings — manual review and triage are still required (same "found vs. exploitable" discussion applies to Nessus ). Dradis centralizes the data, it doesn't replace human analysis.
Phase 4 — Issue Library: Write Once, Reuse Always #
This is the piece that saves the most time in the long run.
Menu → Issue Library

Crea un nuovo Issue con:
- Titolo (es. "SMBv1 Enabled — EternalBlue Exposure")
- Descrizione standard
- Severity di default
- Raccomandazione di remediation standard
For the next project, instead of rewriting the same description for SMBv1, you import it from the library and associate it with the newly discovered vulnerable nodes. Over time, the library grows, and each new report requires less and less writing from scratch.
Best practice: After each engagement, take a few minutes to add the "good" findings written during the project to the library—those with the clearest explanations or the best-reasoned remediation. The next project will inherit them for free.
Step 5 — Add Manual Findings #
Not everything comes from a scanner — many vulnerabilities (business logic, specific misconfigurations, exploit chains) are written by hand.
Sul Node specifico → Add Issue

Campi tipici:
- Title
- Description
- Evidence (dove si trova la vulnerabilità)
- Proof of concept / screenshot
- Severity
- Remediation
You can attach screenshots directly as evidence — useful for documenting a successful exploit without having to manage separate files off-system.
Phase 6 — Team Collaboration #
If multiple people are working on the same project:
- Everyone shares the same project password
- Findings added by a consultant are immediately visible to others
- You can comment on other people's findings for review (internal QA before delivery)
Typical team workflow:
1. Consulente A testa host 192.168.1.10-50, aggiunge finding man mano
2. Consulente B testa host 192.168.1.51-100, in parallelo
3. Report writer (o uno dei due) fa la revisione finale di tutti i finding
4. Generazione report unico, coerente, da tutto il lavoro del team
Without a central tool, this step usually requires piecing together separate Word documents—with Dradis, everything is already in one place.
Phase 7 — Generating the Final Report #
Menu → Export → [formato desiderato]Formats available in Community Edition: HTML, plain text, and exportable templates (depending on your configuration).
For complex corporate report templates (Word with logo, customized section structure, tables formatted to your firm's standards), the Community Edition requires more manual adaptation work than the Professional Edition, which offers conversion of the existing template and direct output to .docx/.xlsx/.pdf.
What a generated report typically includes:
- executive summary
- Exclusive
- Findings grouped by severity
- Technical details for each finding (with attached evidence)
- Remediation recommendations
Common Mistakes #
| Error | Conseguenza | Fix |
|---|---|---|
| Import raw scans without triage | Report full of false positives delivered to the customer | Always manual review before final export |
| Don't structure Nodes before importing | Messy structure, difficult to navigate after | Plan your tree (by host, by subnet, by stage) before importing data |
| Do not feed the Issue Library over time | Each project starts from scratch, no accumulated time savings | Add top findings to your library after each engagement |
| Project password shared via insecure channels | Risk of unauthorized access to customer data | Share your password via an encrypted channel, not plain text email. |
| Forgetting to backup your project | Lose weeks of work if your server has a problem | Periodically export/backup your project, especially on long engagements |
Dradis in a Pentest Workflow #
DURANTE L'ENGAGEMENT
  Ogni tool (Nessus, Nmap, Burp) gira e produce output
  → Import continuo in Dradis, non solo alla fine

PARALLELO AL TESTING
  Note manuali, screenshot, PoC vengono aggiunti man mano
  → Non aspettare la fine per scrivere i finding, il dettaglio si perde

FINE ENGAGEMENT
  Triage e QA di tutti i finding (grezzi + manuali) in un posto solo

CONSEGNA
  Export nel formato richiesto dal cliente
  → Un solo punto di verità, non file sparsi tra consulenti diversi
Dradis's exact role: it doesn't replace analysis (that remains human), but it eliminates the mechanical work of assembling scattered data into a coherent final document. For an engagement with a single tester and a scan, the advantage is marginal. For a team of multiple people using multiple tools, the time savings become substantial.
Final Cheat Sheet #
| Operation | Command/Path |
|---|---|
| Start (Kali) | dradis-start |
| Stop (Kali) | dradis-stop |
| Web access | http://127.0.0.1:3000 |
| Create project | Add branch → rename |
| Add Host | Right click node → Add child |
| Import Nessus | Import from file → Nessus → load .nessus |
| Import Nmap | Import from file → Nmap → load XML |
| Import Burp | Import from file → Burp → load XML |
| Issue Library | Menu → Issue Library → New Issue |
| Add manual finding | On Node → Add Issue |
| Export report | Menu → Export → Format |
FAQ #
Does Dradis replace manual report writing? No. It automates aggregation and formatting, but the content (analysis, remediation, context) remains human work.
Is an account required for each consultant? No, in Community Edition the password is shared at the project level. The Login field is for information purposes only.
Can I import data from unofficially supported tools? Yes, via the extension/API interface. If a tool doesn't have a direct import, you can build a custom connector (the project is open source and extensible).
Is the Community Edition enough for a professional red team? To centralize findings and generate basic reports, yes. For complex business templates, real-time results reporting, and integration with Jira/ServiceNow, you need the Professional Edition.
What happens if I import the same scan twice? Duplicate risks—always check if a Node/Issue already exists before re-importing an updated scan on the same host.
References: Dradis Framework GitHub , Dradis Community Edition . To generate starting findings to import, see Nessus on HackIta . To centralize findings collected after a multi-host pivot, see Pivoting on HackIta.