Last article
Kevin Mitnick: Hacker, Social Engineering, Arrest, and Career
HackITA TV
kevin mitnick / guides-resources

Kevin David Mitnick, known as The Condor and The Darkside Hacker, was one of the most famous hackers: social engineering, arrest, career, and death in 2023.
Latest Web Hacking
SQL injection on MySQL: cheat sheet with UNION payloads, error-based, blind, time-based, DIOS, RCE via UDF, OOB, WAF bypass and sqlmap commands for pentesting.
Learn what Command Injection is, how it works, where it is found, and how to test for it with Burp Suite and Commix: blind techniques, OOB, filter bypass, and defense.
How OAuth 2.0 works, what scope and access tokens are, and how to protect your company's social media accounts from token theft in third-party tools.
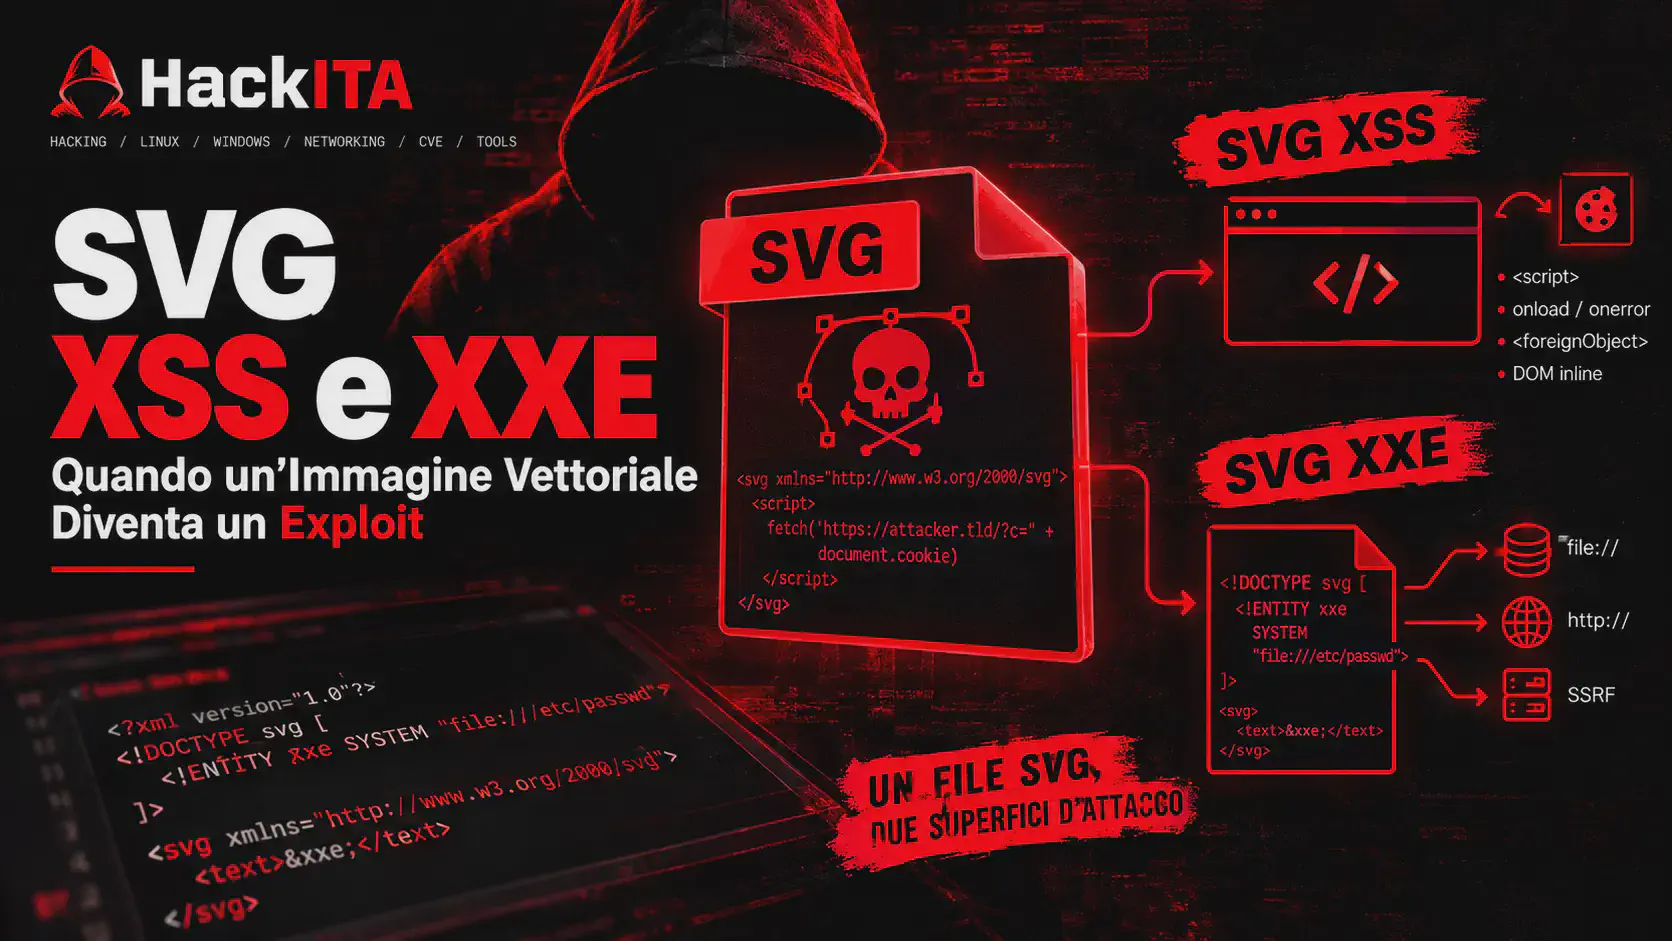
An uploaded SVG can execute scripts or read local files. A practical guide to XSS and XXE via SVG: real-world payloads, attack vectors, and mitigations for developers.
Learn what NoSQL Injection is on MongoDB: payload, authentication bypass, $regex, $where, blind injection, data extraction, and defense techniques.
RCE in pentesting: Learn the vectors that lead to Remote Code Execution, how to verify them, get a shell, and initiate post-exploitation.
Passive OSINT reconnaissance for pentesters: Collect emails, subdomains, exposed devices, and metadata with theHarvester, Google Dorks, Shodan, and Metagoofil.
Subdomain enumeration pipeline: passive recon with subfinder, brute force with puredns, Alterx permutations, httpx validation and subdomain takeover check.
Wfuzz for web fuzzing: directory and parameter commands, VHost discovery, headers, cookies, filters, SecLists, encoders, and WAF bypass techniques.
XXE (XML External Entity) in pentesting: payload for file read, SSRF, Blind XXE OOB and RCE, testing with Burp Suite and Nuclei, prevention in XML parsers.
Advanced XXE Injection: Identifies XML parsers, compares Java, PHP, Python, and .NET, tests SOAP, XInclude, content-type switching, and targeted bypasses.
Learn how to test and configure HTTP security headers: CSP, HSTS, X-Frame-Options, Referrer-Policy and bypass techniques in web pentests.
Automated recon pipeline guide: subdomain enumeration, DNS, port scanning, fingerprinting, Nuclei, and secret scanning for bug bounty and pentesting.
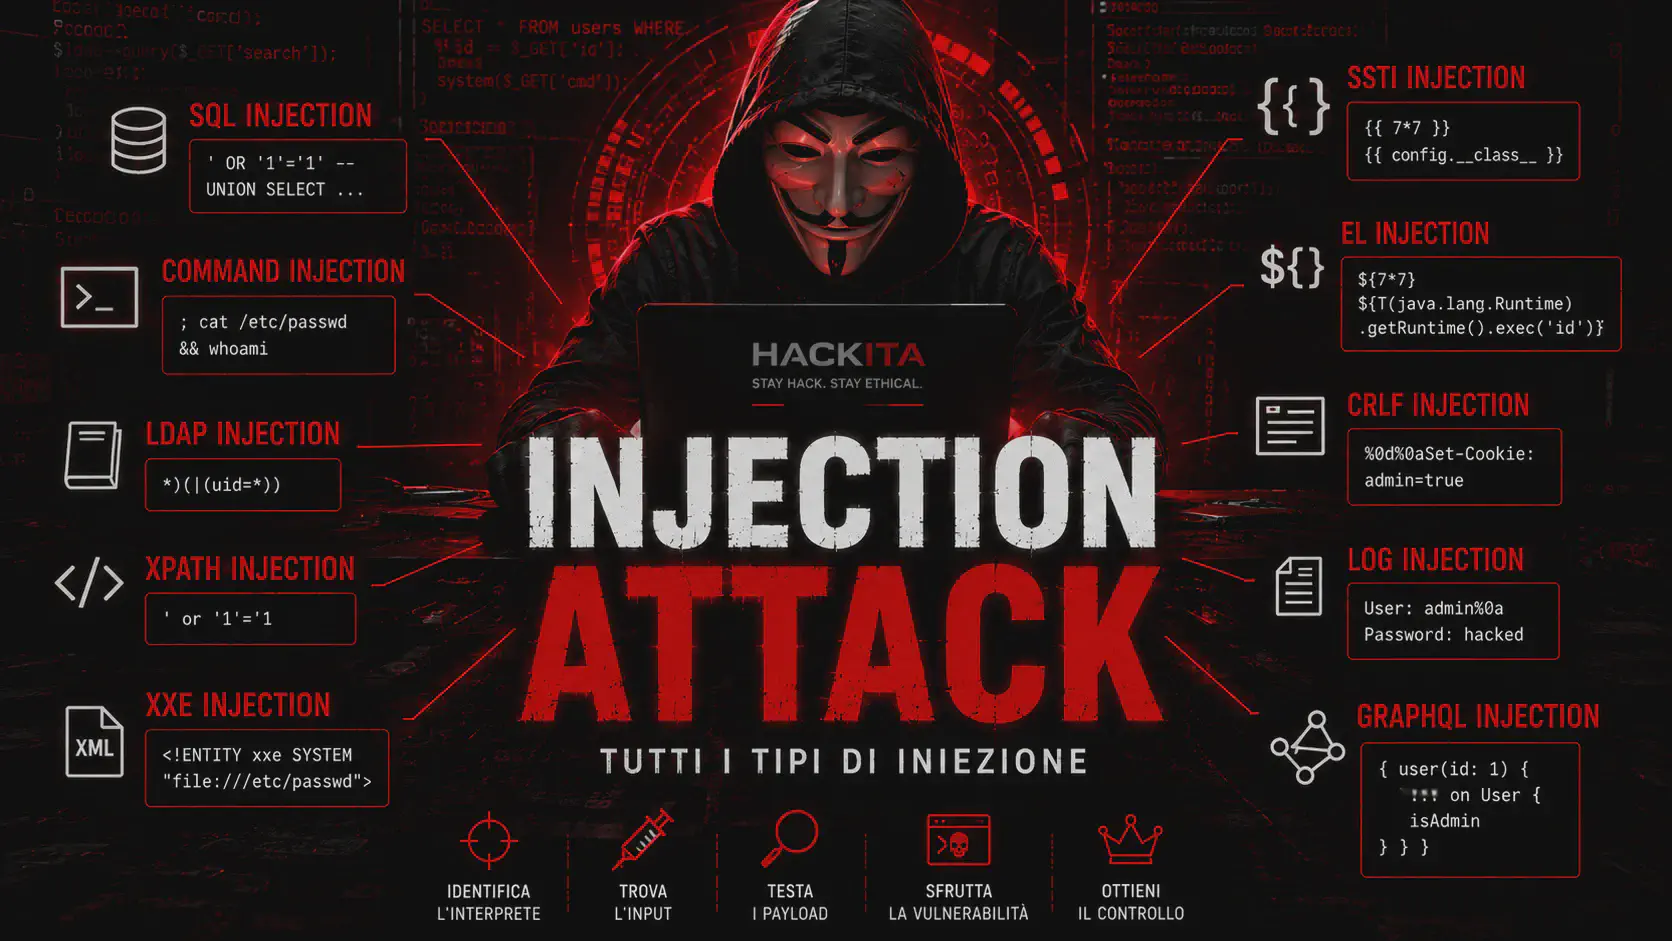
A complete guide to injection attacks: SQL injection, command injection, SSTI, XXE, LDAP, NoSQL, and other techniques, with examples, testing, and prevention.
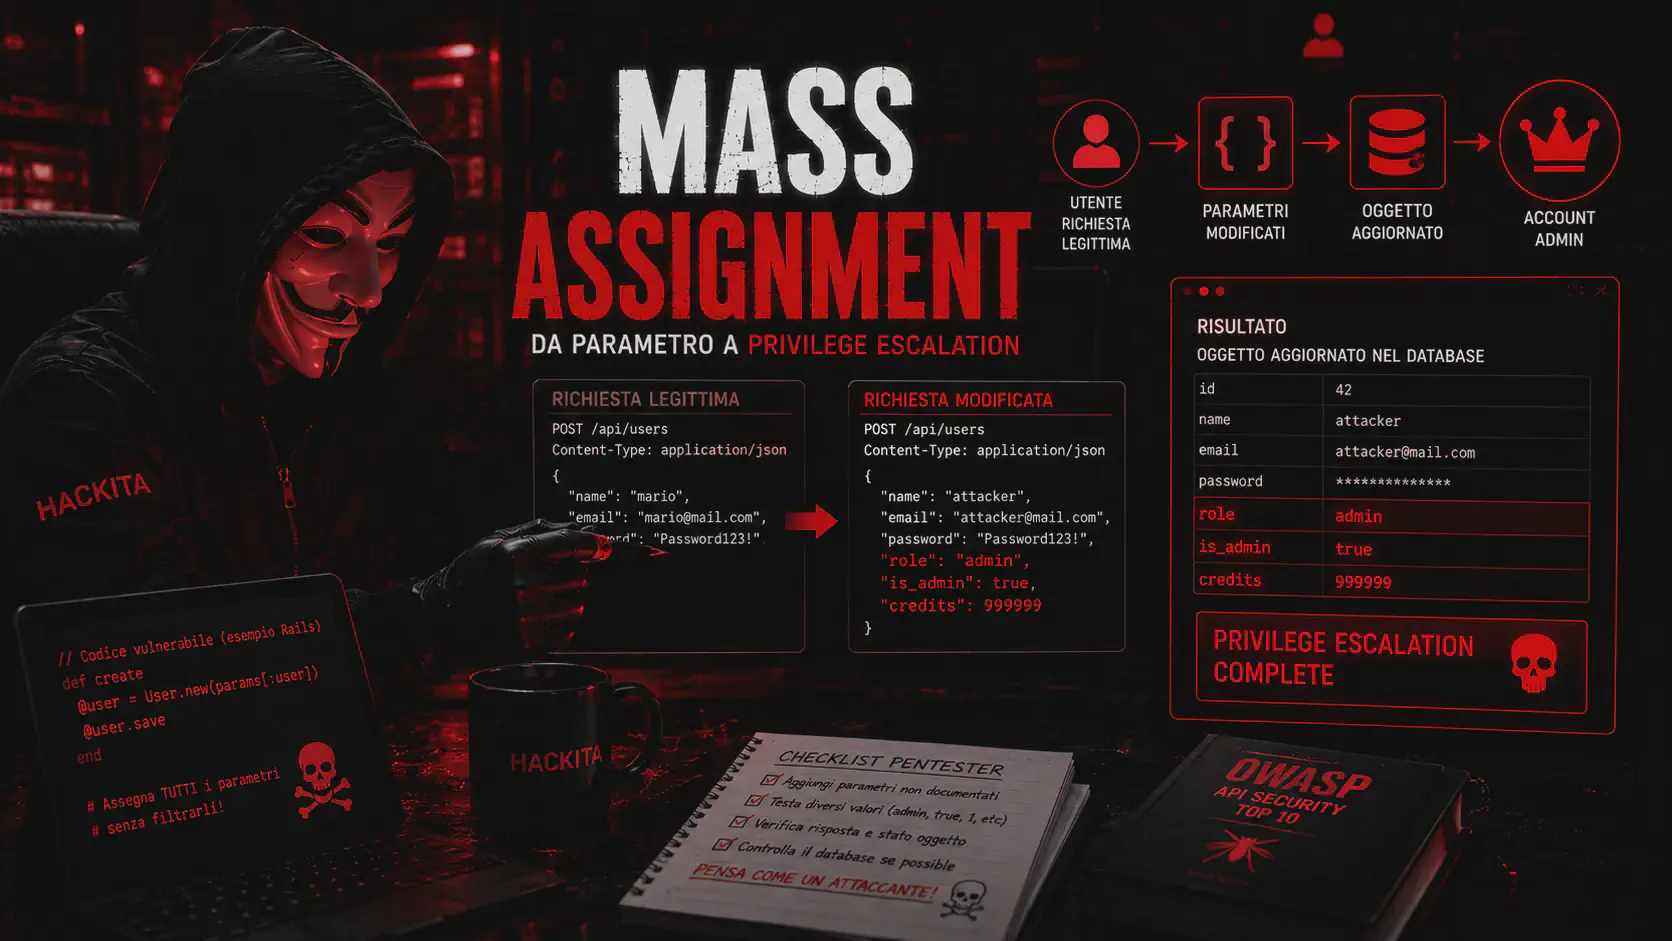
Learn what mass assignment is, how to identify it, and how to leverage it in REST APIs, with practical examples for Rails, Laravel, Django, Node.js, and Burp Suite.
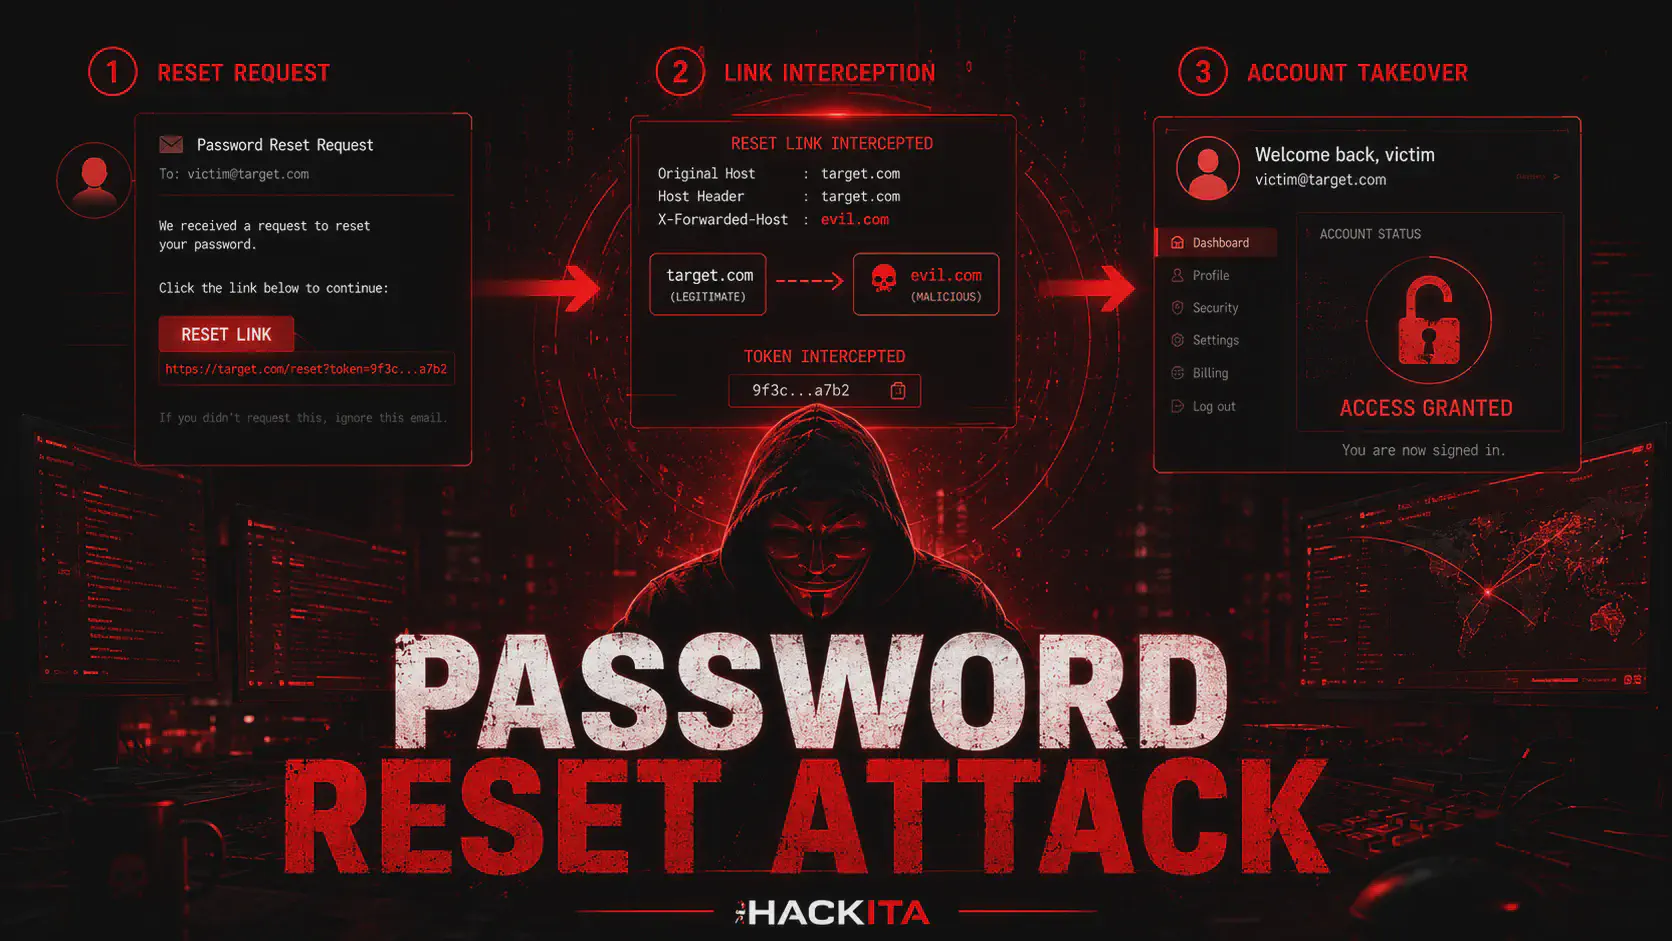
Password Reset Attack Guide: Host header poisoning, weak tokens, race conditions, leaks, and practical account takeover techniques for web pentests.
OWASP A07 Broken Authentication Guide: username enumeration, brute force, 2FA bypass, session fixation, password reset and credential stuffing for pentests.
Practical guide to Web Cache Poisoning in pentesting: analyze cache keys and unkeyed inputs, test headers and fat GETs with Burp, and apply useful detection and mitigations.
Practical guide to Broken Access Control OWASP A01:2025: privilege escalation, IDOR and BOLA, force browsing, HTTP methods, header bypass and testing with Burp Suite.
Twig SSTI ,detection, payload and RCE: fingerprint vs Jinja2, payload for Twig 2.x and 3.x, filter/map/reduce bypass, sandbox escape, Drupal/Craft CMS and mitigations
HasSession BloodHound: Learn how to enumerate sessions with SharpHound and leverage tokens, credentials, and RDP, with Active Directory detection and mitigations.
Pentest SQL Injection MSSQL: identify quotes, exploit UNION/blind/time-based/stacked/error-based, bypass WAF, RCE via xp_cmdshell, NTLM hash, linked server.
2FA bypass: response manipulation, OTP brute force, direct post-login link, SIM swapping, MFA phishing, backup code abuse. Payload for ethical pentesters and hackers
Deserialization attack explained from the beginning: what serialization is, why it's dangerous, and how to exploit it in PHP, Java, Python, and .NET with ysoserial and phpggc. A step-by-step guide for beginners and pentesters.
A comprehensive map of exploitable Windows privilege tokens in a pentest. From whoami /priv to SYSTEM: cheat sheets, tables, workflows, and links to how-to guides.
Leverages SeSystemEnvironmentPrivilege for PATH hijacking and SYSTEM shell. UEFI persistence that survives disk wipes. Red Team guidance with registry, Process Monitor, and Chipsec.
Extract RDP passwords and credentials from Credential Manager with SeTrustedCredManAccessPrivilege. Use cmdkey, mimikatz, and SharpDPAPI. Step-by-step Red Team guide.
Learn how Evilginx 3 enables AiTM phishing, captures post-MFA cookies, and helps red teams understand MFA-bypass risks in Microsoft 365.
How to exploit SeDelegateSessionUserImpersonatePrivilege to impersonate users in active RDS sessions. Cross-session token stealing with NtObjectManager. Privesc and Red Team techniques.
Learn Account Takeover (ATO) techniques for pentesters and red teams. Discover how to bypass MFA, steal tokens, and compromise accounts. Complete guide 2026.
IDOR (Insecure Direct Object Reference) explained from a pentester's perspective: how to identify it, how to enumerate it, and how to scale it to account takeovers and data breaches. With real-world examples and a practical checklist.
A complete guide to injection attacks: SQL injection, command injection, LDAP, XPath, SSTI, XXE, CRLF, log injection, EL, NoSQL, and GraphQL. What injection is, how it works, how to find it, and how to exploit it. A hub with links to all the specific guides.
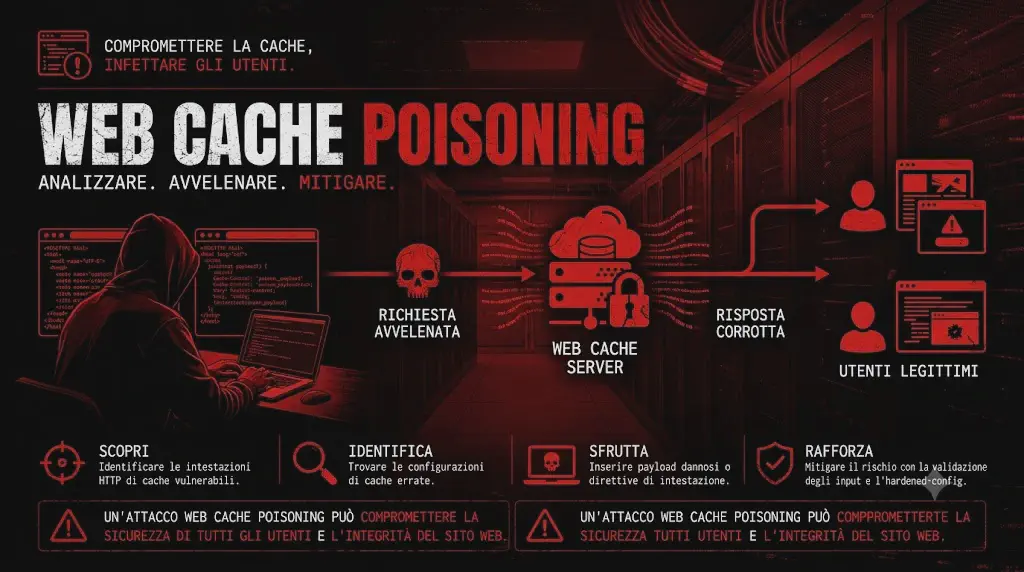
A complete guide to web cache poisoning: discover what it is, how cache poisoning works, exploitation techniques (unkeyed inputs, CPDoS), and how to turn it into account takeover. Practical and CDN-specific examples.
SeDebugPrivilege Enabled? Two commands to dump LSASS and get NTLM hashes. All with Windows' built-in comsvcs.dll, no disk mimikatz. Red Team technical guide.
SeImpersonatePrivilege explained with Potato attacks: from IIS or SQL Server to SYSTEM, privilege escalation windows with modern tools used in labs.
A practical guide to CSP bypass: unsafe-inline, weak nonces, base-uri, object-src, JSONP, AngularJS, dangling markup, and real-world techniques for bypassing Content Security Policy.
Complete list of XSS payloads for HTML, attributes, JavaScript, DOM, Blind XSS and filter bypass: a practical cheat sheet for pentesters and bug bounties.
Practical guide to XSS bypass against real WAFs: Cloudflare, AWS WAF, ModSecurity CRS, encoding evasion, mutated payloads, origin bypass, and techniques used in pentests.
Practical guide to DOM
A complete guide to Reflected XSS: reflection points, context analysis, HTML and JavaScript payloads, link delivery, cookie stealing, dalfox, and real-world exploit techniques.
A practical guide to XSS bypasses: alternative tags, keyword obfuscation, encoding, regex bypass, HTML and JavaScript contexts, and real-world techniques for bypassing server-side filters.
Stored XSS Explained: What It Is Cross-site scripting, persistent payloads stored in the database, cookie theft, account takeover, and self-replicating worms in web applications.
Zip Slip Explained: Path Traversal in ZIP and TAR Archives Leads to RCE, Web Shell, and Persistence During File Extraction
WebSocket Hijacking Explained: CSWSH, Vulnerable Handshake, Missing Origin Check, and Real-Time Data Theft from Chats, Notifications, and Dashboards.
XPath Injection Guide: What it is, Pentesting, login bypass payloads, XML data extraction, and blind testing. Discover techniques, tools, secrets, and mitigations.
Session Hijacking in web pentesting: cookie theft via XSS, session fixation, HTTP sniffing and account takeover. HttpOnly, Secure and SameSite flag analysis.
Source Code Disclosure in Pentesting: Exposed .git, git-dumper, credentials in git history, and trufflehog for secrets. From repository dump to cloud takeover.
The Complete Guide to SSRF: How to Find Server-Side Request Forgery, Bypass IP Filters, Read AWS Metadata, and Get Cloud Credentials.
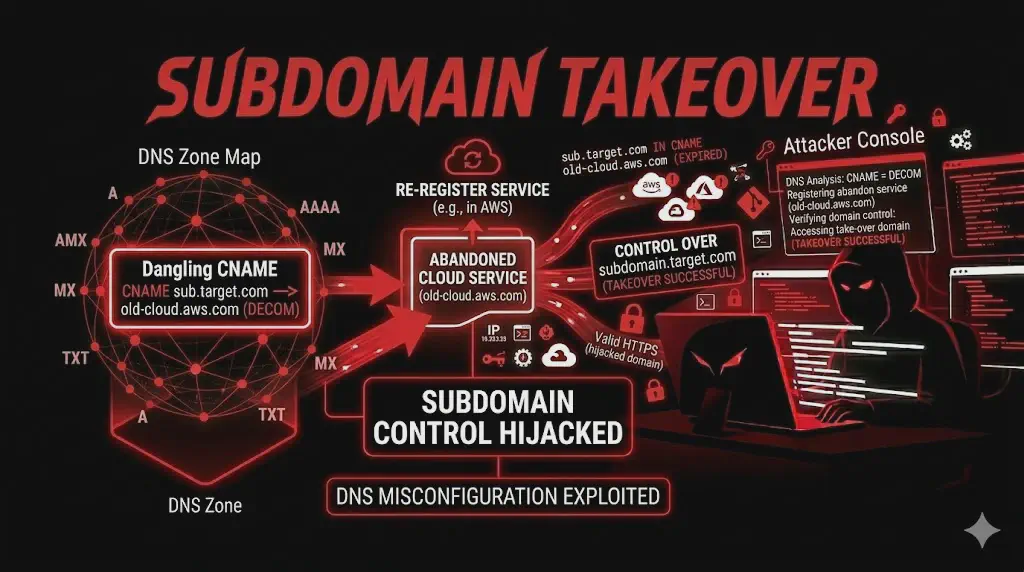
The Complete Guide to Subdomain Takeover: CNAME Dangling, Defunct Cloud Services, and Subdomain Takeovers on AWS, Heroku, GitHub Pages, and Azure.
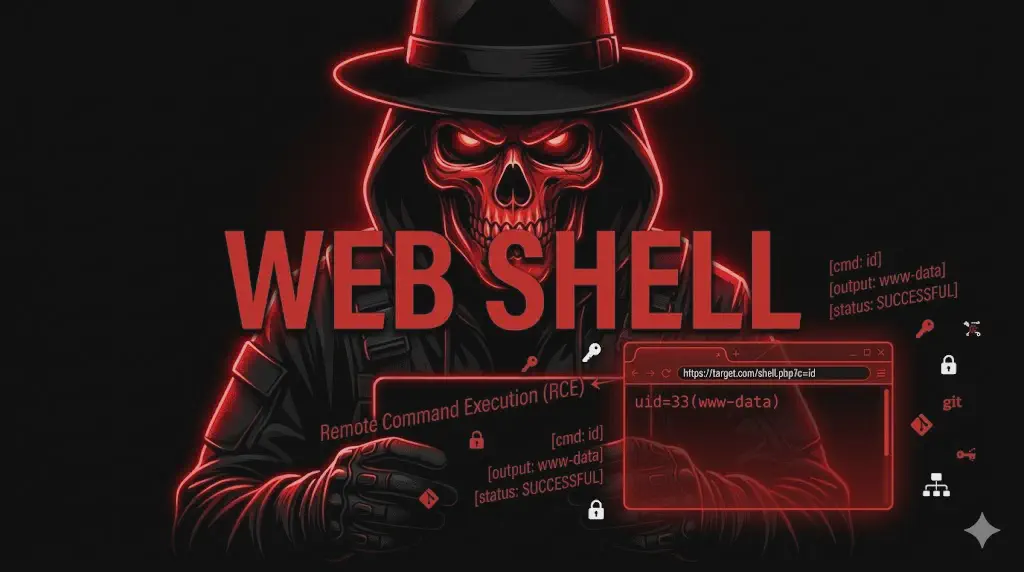
Complete guide to Web Shells in pentesting: PHP shell upload, reverse shell, WAF bypass and persistence after file upload or LFI.
Discover the main web application attacks: SQL Injection, XSS, SSRF, IDOR, CSRF, SSTI, and API abuse. A complete guide for pentesters and red teams.
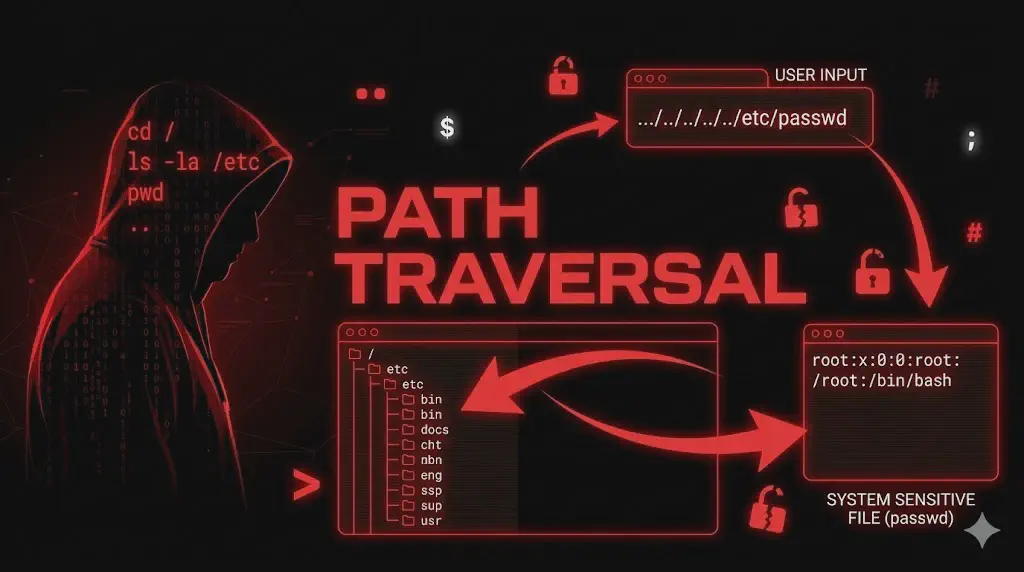
Path traversal in web pentesting: payload, WAF bypass, reading /etc/passwd, .env, and cloud credentials. A practical guide with fuzzing and exploitation.
Privilege escalation in web apps: mass assignment, role=admin, JWT manipulation, and multi-tenant bypass. Practical pentesting techniques for user-to-admin escalation.
Race Conditions in web apps: double spending, coupon abuse, and limit bypassing with parallel requests. Detection techniques with Turbo Intruder and real-world exploits.
Remote File Inclusion (RFI): RCE via URL, Wrapper Bypass and SMB Attack
A comprehensive guide to the most underestimated vulnerabilities in web pentesting: Subdomain Takeover, HTTP Request Smuggling, Race Conditions, Deserialization, and Cache Poisoning. Real-world techniques, payloads, and enterprise attack chains.
Learn how to exploit OAuth vulnerabilities: redirect_uri manipulation, stateless CSRF, referer token leak, and account takeover in web pentesting.
Open Redirect in Web Pentesting: Detection, URL and Chain Validation Bypass with OAuth Token Theft, SSRF Bypass, and Credible Phishing. A Practical Guide.
OS Command Injection in pentesting: separators, argument injection, exploits on Linux and Windows (curl, tar, ffmpeg, Git, ImageMagick) and post-exploitation.
Learn how to exploit an LDAP injection in enterprise portals: bypass Active Directory authentication, enumerate users, and extract sensitive attributes from the corporate directory.
Learn how to exploit a log injection in web pentesting: log forging for anti-forensics, log poisoning combined with LFI to achieve remote code execution, and the historical Log4Shell case study.
Learn how to exploit a file upload attack in web pentesting: extension bypass, Content-Type, magic bytes, polyglot, and RCE via web shell.
Find out how to test GraphQL in web pentesting: introspection, batching, authorization bypass, IDOR, brute force and data leak via query.
Find out how to exploit HTTP Header Injection in web pentesting: Host Header Poisoning, X-Forwarded-For bypass, cache poisoning and reset password takeover.
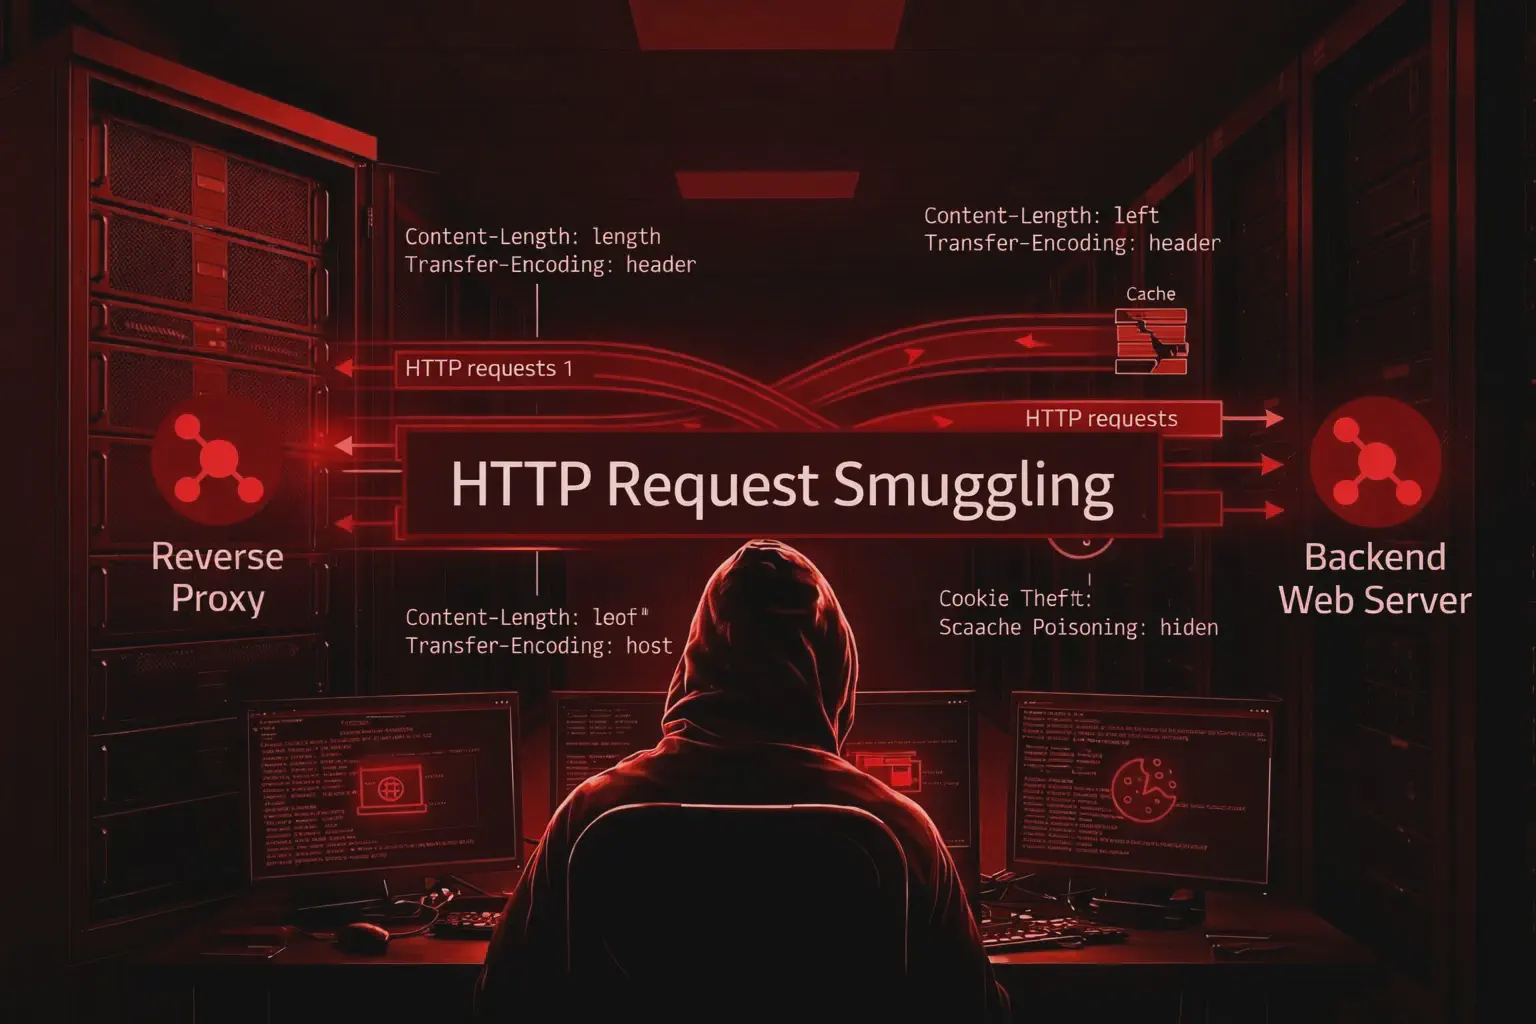
Learn how to test HTTP Request Smuggling in web pentesting: CL.TE, TE.CL, proxy-backend desync, cache poisoning, and cookie theft.
Learn how the LFI vulnerability works: file reading, PHP wrapper, filter chain, and log poisoning, with exploitation techniques and countermeasures in the pentest.
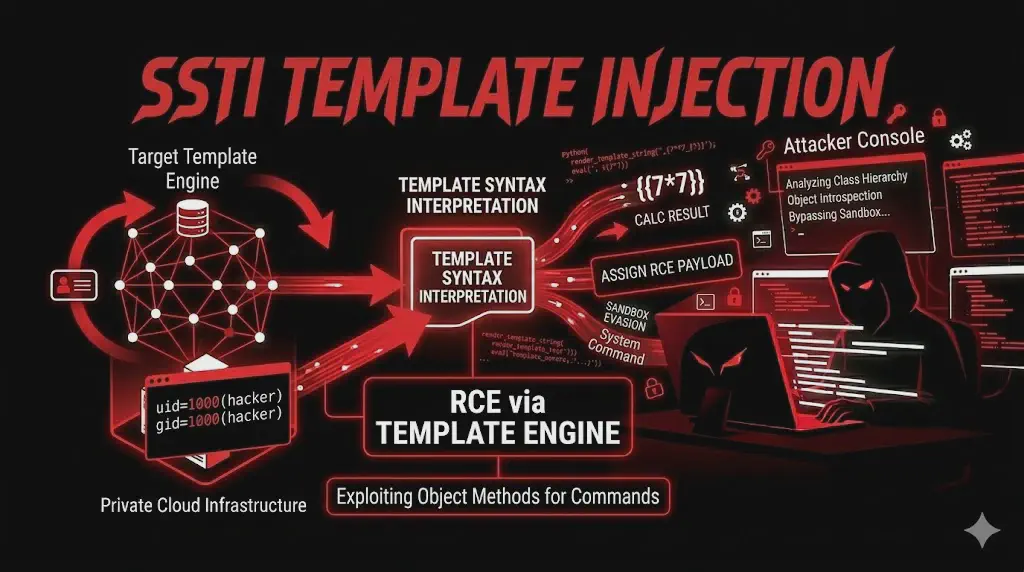
A practical guide to SSTI: detection, template engine fingerprinting, real payloads, Jinja2, Twig, FreeMarker, sandbox bypass, and RCE.
CORS Misconfiguration in APIs: Learn how to identify, exploit, and demonstrate data theft with origin reflection, null origin, common bypasses, and real-world PoCs with curl and JavaScript.
Find out how to exploit a CRLF injection in web pentesting: header injection, HTTP response splitting, session fixation and cache poisoning.
Learn how to detect and test a CSRF attack in web pentesting: HTML PoC, token bypass, SameSite, JSON API, and account takeover.
Learn what Expression Language Injection is and how to leverage it in Java apps: SpEL, OGNL, Spring, Struts2, RCE, and real-world cases like Equifax.
Guide to file & path attacks in web pentesting: path traversal, LFI, file upload, web shell, Zip Slip, backup exposure and file read.
A complete guide to authentication and access control in web pentesting: IDOR, JWT attacks, CSRF, 2FA bypass, password reset, and privilege escalation.
Learn how to find exposed backup files in web pentesting: SQL dumps, .env, ZIP, and config.bak with feroxbuster, ffuf, and real-world techniques.
Learn what a business logic flaw is and how to spot it in web pentesting: negative pricing, coupon abuse, step bypass, and workflow flaws.
Learn what clickjacking (UI Redressing) is and how to spot it in web pentesting: invisible iframes, X-Frame-Options, CSP frame-ancestors and real PoCs.
Arbitrary File Read exploit in pentesting: Read sensitive Linux and Windows files, bypass WAF, /proc/self/environ, cloud credentials, and escalate to cloud takeover.
Brute Force attacks in penetration testing: password cracking, credential stuffing, wordlist, Hydra, Burp Intruder and bypass rate limit in systems with auth.
Rate Limit Bypass API explained operationally: header rotation with X-Forwarded-For, endpoint switching, HTTP method tampering, Unicode bypass, race conditions and GraphQL batching.
API security and penetration testing of modern APIs: SSRF, GraphQL attacks, BOLA/IDOR, CORS misconfiguration, mass assignment, and rate limit bypass. A comprehensive guide with real-world payloads and techniques.
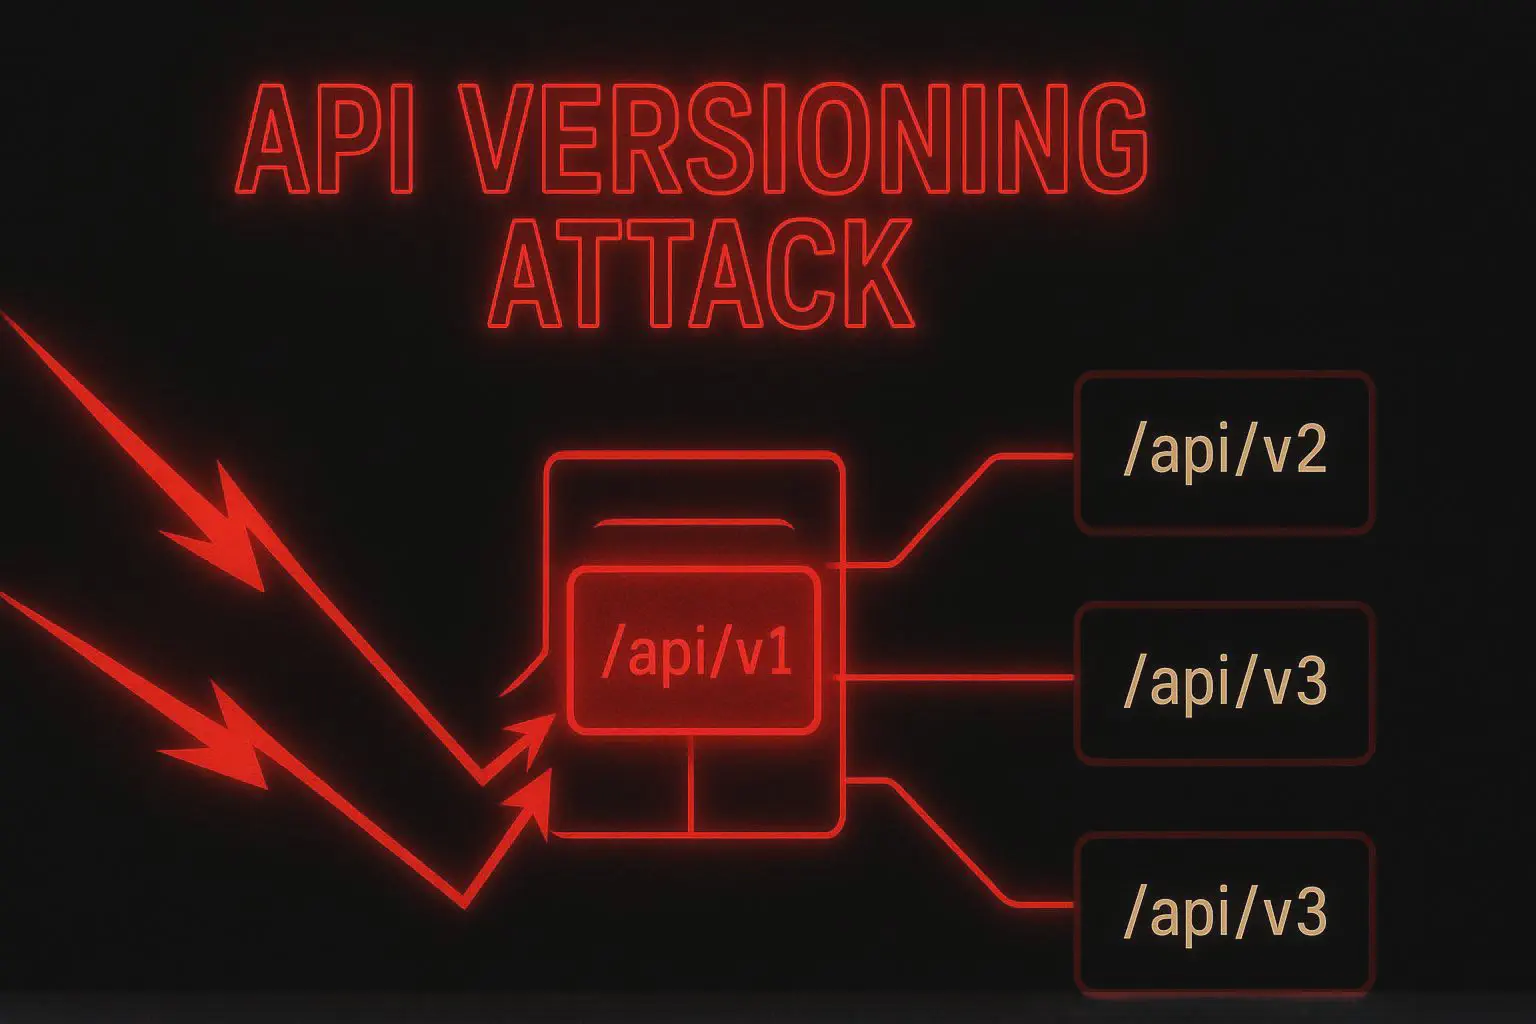
API Versioning Attack Operationally Explained: How to find legacy v1 API endpoints, bypass rate limits and authentication, and exploit deprecated APIs during a penetration test.
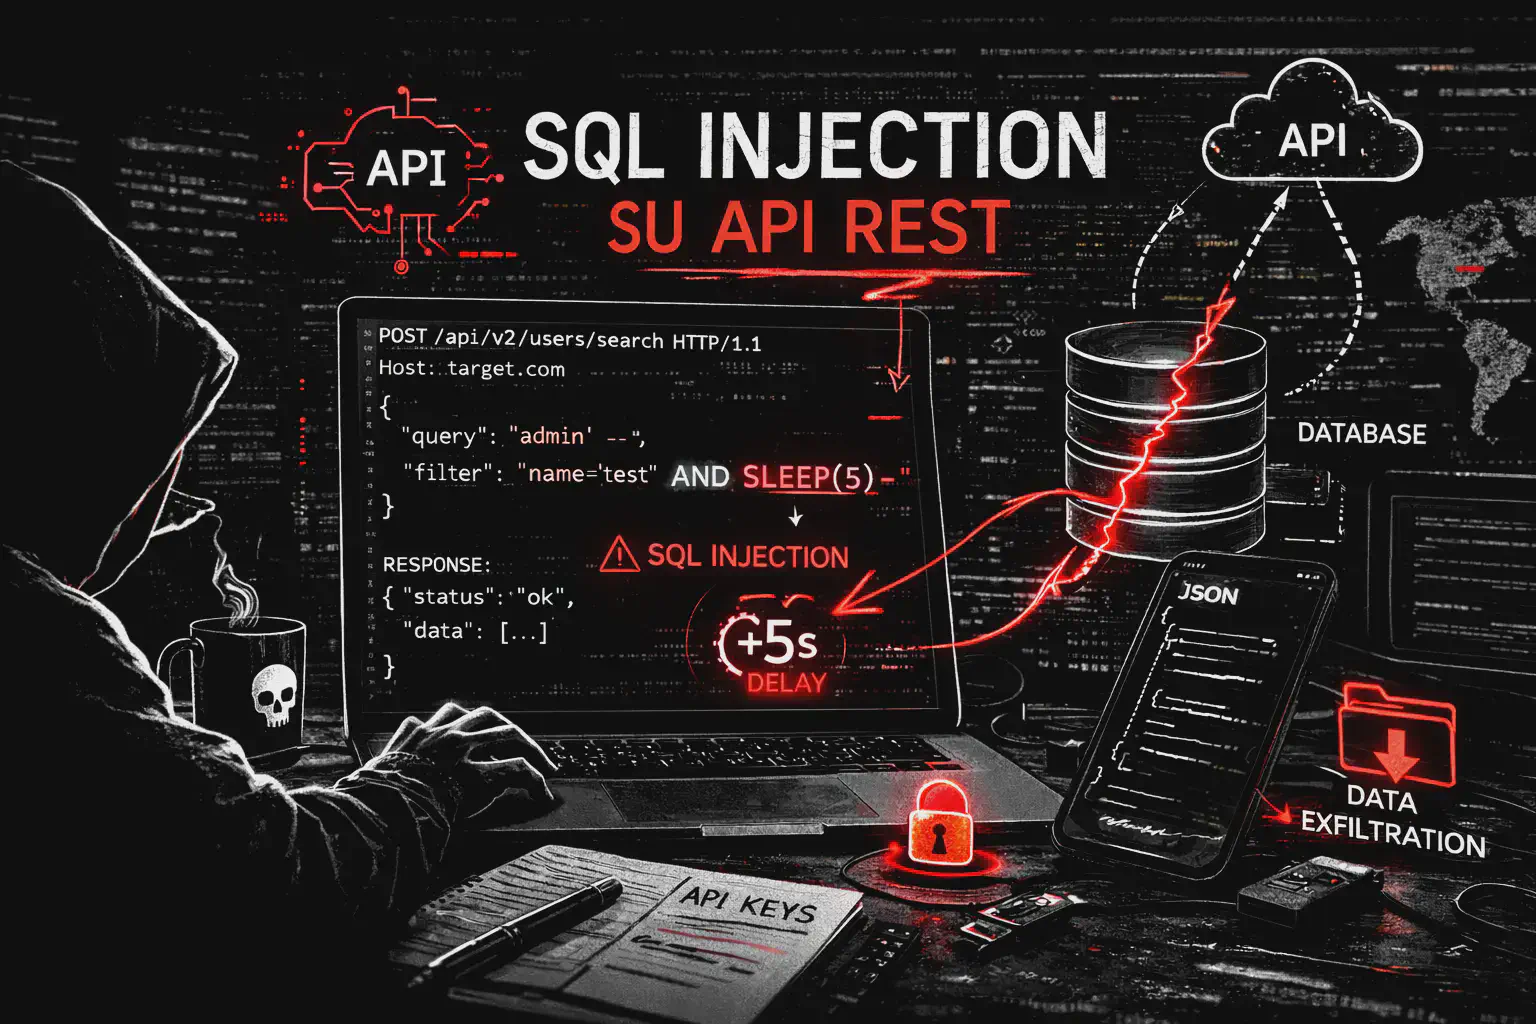
SQL Injection on REST API: JSON body injection, GraphQL SQLi, header injection and WAF bypass. Practical guide with SQLMap, API fuzzing and real exploitation.
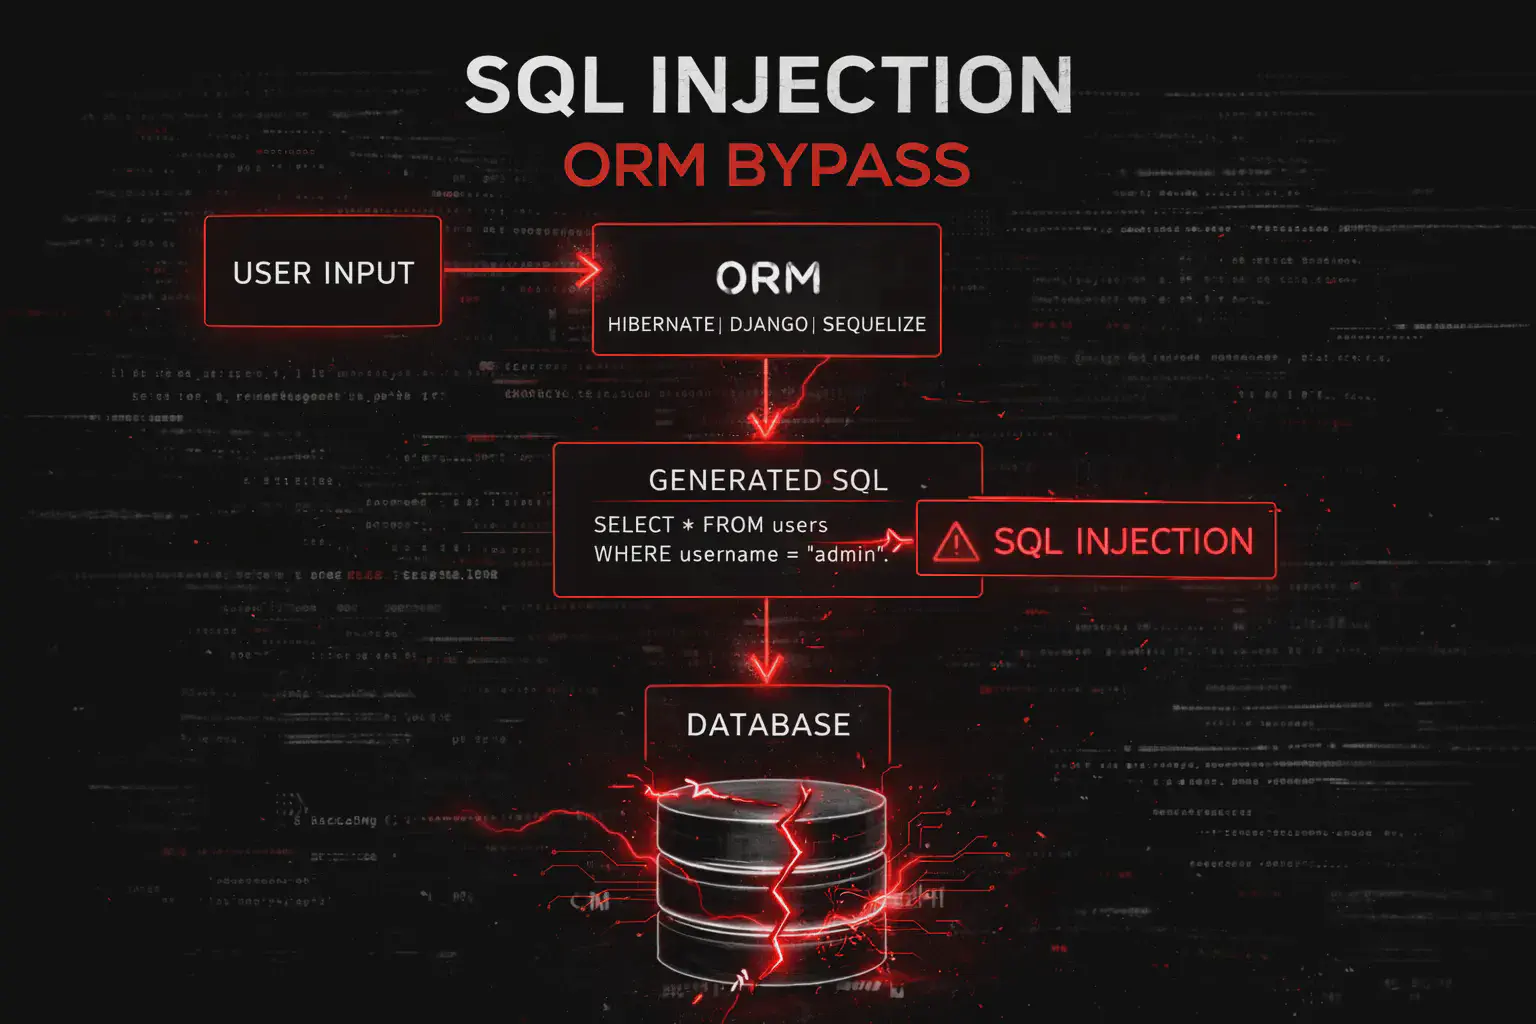
SQL Injection on ORM: Vulnerabilities in Django, Laravel, Hibernate, and Sequelize. Raw queries, extra(), orderByRaw, and real-world exploitation with practical examples.
Time-Based SQL Injection explained with real payloads: SLEEP, pg_sleep, WAITFOR DELAY, heavy query, Python script and SQLMap. Complete exploitation guide 2026.
Blind SQL Injection: boolean-based detection, extraction with SUBSTRING and ASCII, binary search and full automation with SQLMap for database dumps, credentials and escalation.
Classic SQL Injection (In-Band): practical guide to UNION SELECT and Error-Based with ORDER BY, data extraction, WAF bypass, SQLMap and complete step-by-step database dump.
Phishing explained technically: spear phishing, credential harvesting, OAuth phishing, MFA bypass, and practical defenses for businesses and users.
S3Scanner: Enumeration and Misconfiguration Detection on Amazon S3
Recon-ng is a modular OSINT framework with a Metasploit-like interface. Ideal for automated collection of domains, emails, and external assets.
ReconSpider is an OSINT tool for automating web reconnaissance and intelligence gathering on domains, IPs, emails, metadata, and other public sources.
Nuclei: High-Speed Template-Based Vulnerability Scanner
Nikto is a web scanner for finding known vulnerabilities, sensitive files, misconfigurations, and outdated software on HTTP/HTTPS servers.
Eyewitness automates screenshots and analysis of web and RDP services. Rapid visual recon identifies admin panels and exposed attack surfaces.
Feroxbuster is a high-performance directory and content discovery tool. It features recursive bruteforce, multi-threading, and proxy support for advanced web testing.
FOCA is an OSINT tool for extracting metadata from public documents, mapping internal infrastructure, and identifying exposed users, servers, and paths.
Gitrob scans GitHub repositories to identify sensitive files and exposed credentials. A useful tool for reconnaissance and secret hunting.
Gophish is an open-source platform for phishing simulation and red team engagement. It offers centralized campaign management, tracking, and reporting.
Amass is an OSINT and active reconnaissance tool for enumerating subdomains, mapping external assets, and analyzing DNS relationships. A practical guide to its use during attack surface discovery during a penetration test.
Aquatone is a visual reconnaissance tool that automatically captures screenshots of hosts and subdomains discovered during the recon phase. It's ideal for quickly mapping web surfaces in penetration tests.
Dirsearch is a tool for enumerating hidden directories and files on web applications using custom wordlists. A practical guide to its use during web reconnaissance during a penetration test.
Gobuster is a fast tool for brute-forcing directories, DNS, and virtual hosts. A practical guide to using it for web enumeration during a penetration test.
BeEF's practical guide to browser exploitation: victim hooks, compromised browser control, and client-side post-exploitation. Transform XSS into persistent access.
Burp Suite: How to use it in web penetration testing: discover Proxy, Repeater, Intruder and Scanner and how to test SQLi, XSS, CSRF, API, authentication and secrets.
Complete guide to SQLMap for SQL injection automation: detection, exploitation, database enumeration, WAF bypass and UNION, boolean and time-based techniques.
XSS (Cross-Site Scripting): complete guide to reflected, stored and DOM-based XSS, payloads, advanced filter bypasses, exploitation and defense of web applications.
Practical guide to JWT attacks: alg none, weak HMAC keys, algorithm confusion, kid, jku and jwk, claim, refresh token, terminal tools and mitigations.
Learn how to verify xmlrpc.php in WordPress, analyze brute force and pingbacks, assess SSRF risks, and secure your endpoint during a pentest.
Latest Linux
A Guide to Linux Post-Exploitation Persistence: Systemd, Cron, SSH, Udev, LKM, Capabilities, and Other Persistence Mechanisms on Linux.
Kubernetes pentest: How a stolen token in a Pod leads, via RBAC and nodes/proxies, to privilege escalation and root shell on the node, with kubectl and cheatsheet.
What is Bash and how does it work? Learn Bash commands, variables, pipes, permissions, and scripting with a practical, groundbreaking guide designed for Linux and cybersecurity.
SSH hardening on Linux: Configure sshd_config, Ed25519, Fail2Ban, UFW, and 2FA keys; verify algorithms and logins with ssh-audit; and create a jump host.
Linux enumeration step-by-step: Use manual commands, SUID, sudo, capabilities, cron, LinPEAS, LinEnum, and LSE to detect privilege escalation vectors.
Linux privilege escalation via 40+ Linux groups: disk, Docker, LXD, Incus, MicroK8s, libvirt, shadow, video, adm, input, ssl-cert, KVM, sudo/wheel, lpadmin.
Learn how to use LinPEAS for Linux privilege escalation enumeration: SUID, sudo, cron, capabilities, kernel exploits, PATH hijacking, and CTF scenarios with real command examples.
Learn how to exploit a Fail2Ban misconfiguration, what it is, and how to gain root on Linux: enumeration, exploit, ban triggers, detection, and hardening.
Top 100 Linux commands: a comprehensive and practical list for pentesters and sysadmins. Essential for enumeration, exploits, and post-exploitation.

Container Escape: Docker sockets, privileged containers, Linux capabilities, Kubernetes, kernel exploits, and IMDS. Privilege escape techniques, detection, and defense.
Kernel exploits: real-world privilege escalation techniques on Linux and Windows. From theory to practical lab exploits.
Pspy is a tool for observing processes and cron jobs running on Linux without root privileges. It's ideal for identifying privilege escalation vectors.
Lynis is an auditing tool for Unix/Linux systems that analyzes configurations, permissions, patches, and hardening. Ideal for penetration testers and blue teams.
Mimipenguin is a post-exploitation script for Linux that extracts cleartext passwords from the memory of processes such as SSH, sudo, and display managers.
LinEnum is a Bash script for automatic enumeration on Linux systems, useful for identifying privilege escalation vectors post-exploitation.
LinPEAS is an automatic enumeration script for Linux that identifies SUIDs, capabilities, exposed credentials, and privilege escalation vectors.
GTFOBins is the definitive database for exploiting legitimate Linux binaries to escalate privilege, bypass sudo, and escape shells in authorized labs.
Getcap allows you to detect files with Linux capabilities to identify privilege escalation vectors without SUID. This is a key post-exploitation technique.
Chkrootkit is a Linux tool for detecting rootkits and indicators of compromise on Unix-like systems. It is used in incident response and post-exploitation analysis to verify persistence and backdoors.
Crontab Backdoor: A practical guide to creating Linux persistence with cron jobs in penetration testing. Complete setup, evasion, and cleanup.
Latest Windows
Use CredNinja to validate passwords and NTLM hashes via SMB, find local admin, perform Pass-the-Hash and user hunting, and reduce lockouts with stripe and delay.
A practical guide to the Windows file system for pentesting: NTFS, system folders, the registry, ACLs, enumeration commands, privilege escalation, and detection.
ESC17 ADCS uses controllable SANs to impersonate WSUS over HTTPS. Learn about certificate request with Certipy, MITM with wsuks, privesc, and detection.
Offensive Guide to Ticket-Granting Service (TGS) Kerberos: SPN, Kerberoasting with Rubeus and Impacket, Offline Crack, Pass-the-Ticket and Silver Ticket Windows AD
Learn how Kerberos Ticket-Granting Ticket (TGT) works in Active Directory: Dumps with Rubeus, Pass-the-Ticket, Overpass-the-Hash, and Golden Ticket.
Learn about Active Directory password spraying: techniques, authorized pentesting tools, detection, and defenses against weak password access.
A guide to privilege escalation on Windows: enumeration, vulnerable services, token impersonation, DLL hijacking, UAC bypass, detection, and mitigations.
What is SeEnableDelegationPrivilege, privilege escalation, unconstrained/constrained/RBCD variants, S4U2Self-S4U2Proxy, errors, detection and defense.
A guide to lateral movement in Active Directory: Pass-the-Hash, Kerberos, SMB, WMI, WinRM, and RDP with prerequisites, artifacts, detection, and mitigations.
Guide to ACL abuse in Active Directory: GenericAll, WriteDACL, reset password, RBCD and DCSync with BloodHound, PowerView, bloodyAD and Impacket.
AS-REP Roasting in Active Directory: Extract Kerberos hashes without credentials and crack them offline with Impacket, Rubeus, and Hashcat. A complete technical guide.
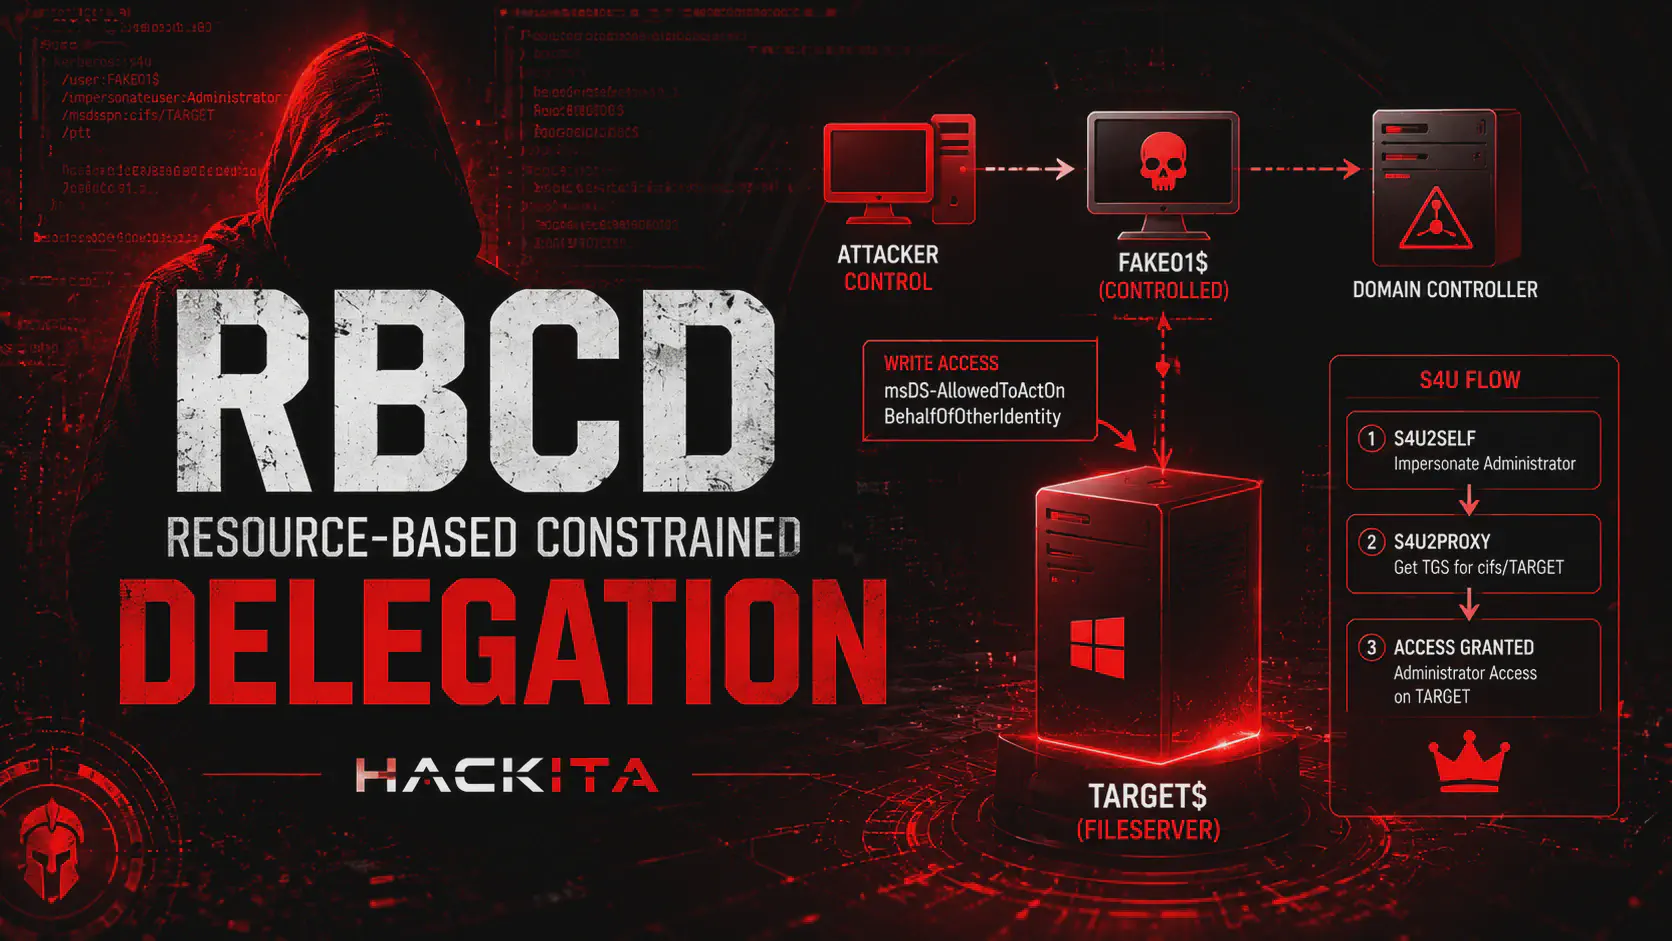
RBCD leverages write access on msDS-AllowedToActOnBehalfOfOtherIdentity for privilege escalation on active directory. Drive with Impacket, Rubeus and NTLM relay.
Shadow Credentials: Leverage msDS-KeyCredentialLink for passwordless AD account takeover. A practical guide with Whisker, pyWhisker, and Certipy for AD pentesting.
The Golden Ticket is the most dangerous attack on Active Directory. Learn how it works, how to forge a TGT with the krbtgt hash, how to detect it, and how to defend yourself with double reset. A complete guide.
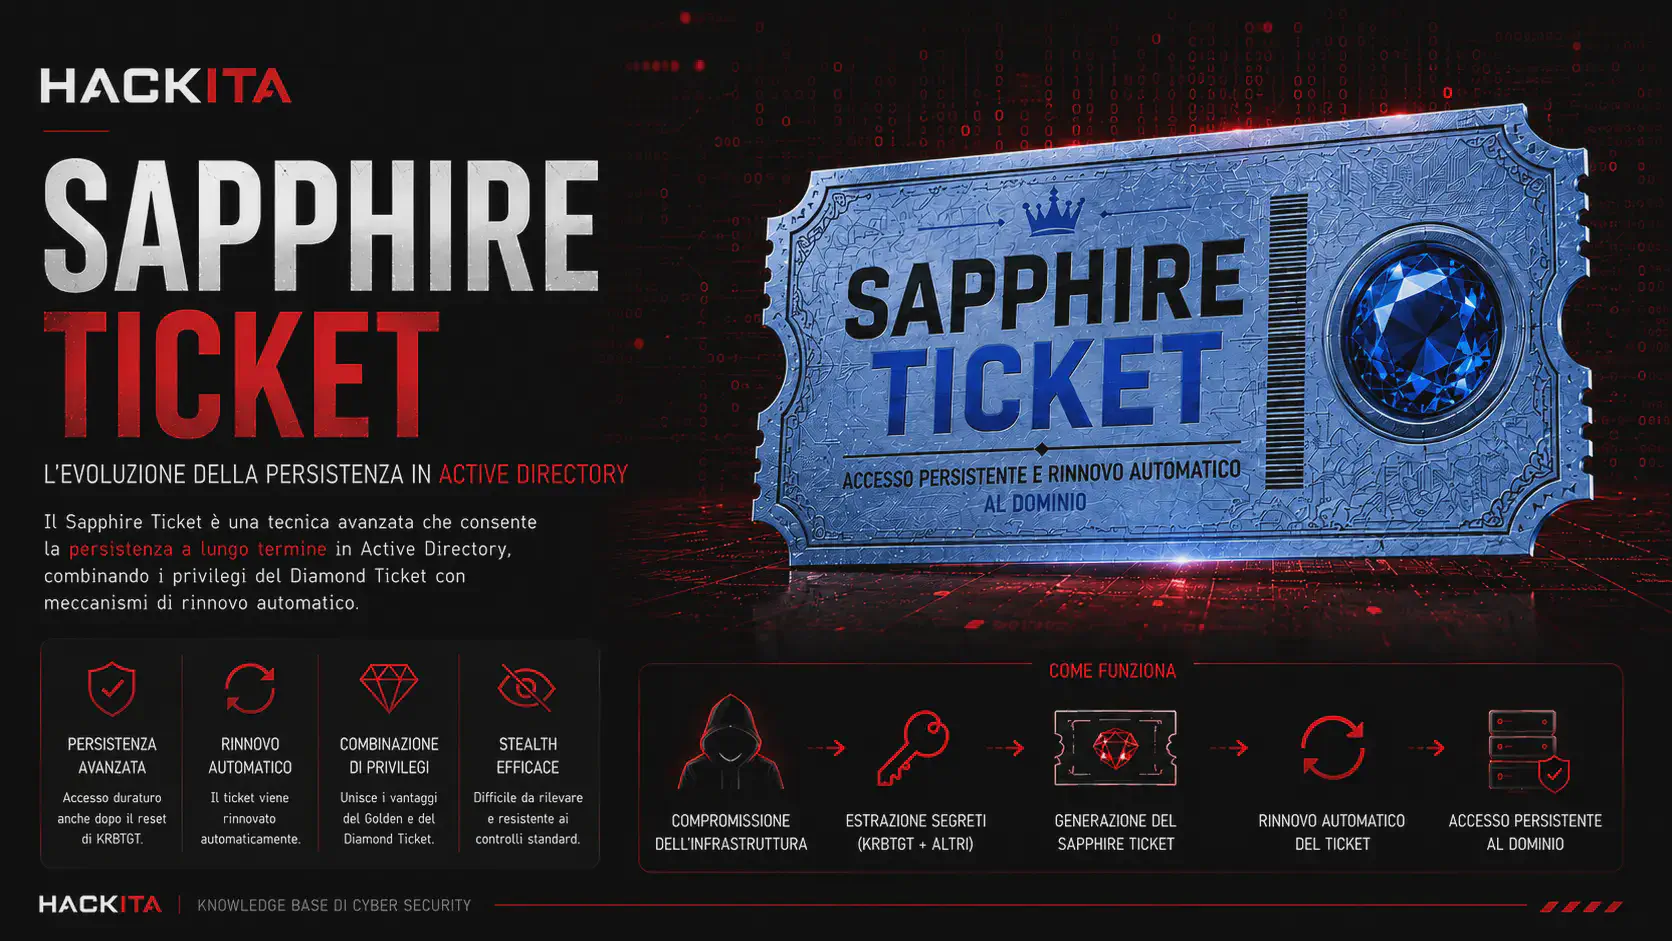
Sapphire Ticket: The stealthiest Kerberos ticket. Combines S4U2Self + U2U for the authentic KDC PAC. Impacket impersonation guide, differences from Golden/Diamond, detection, and mitigation.
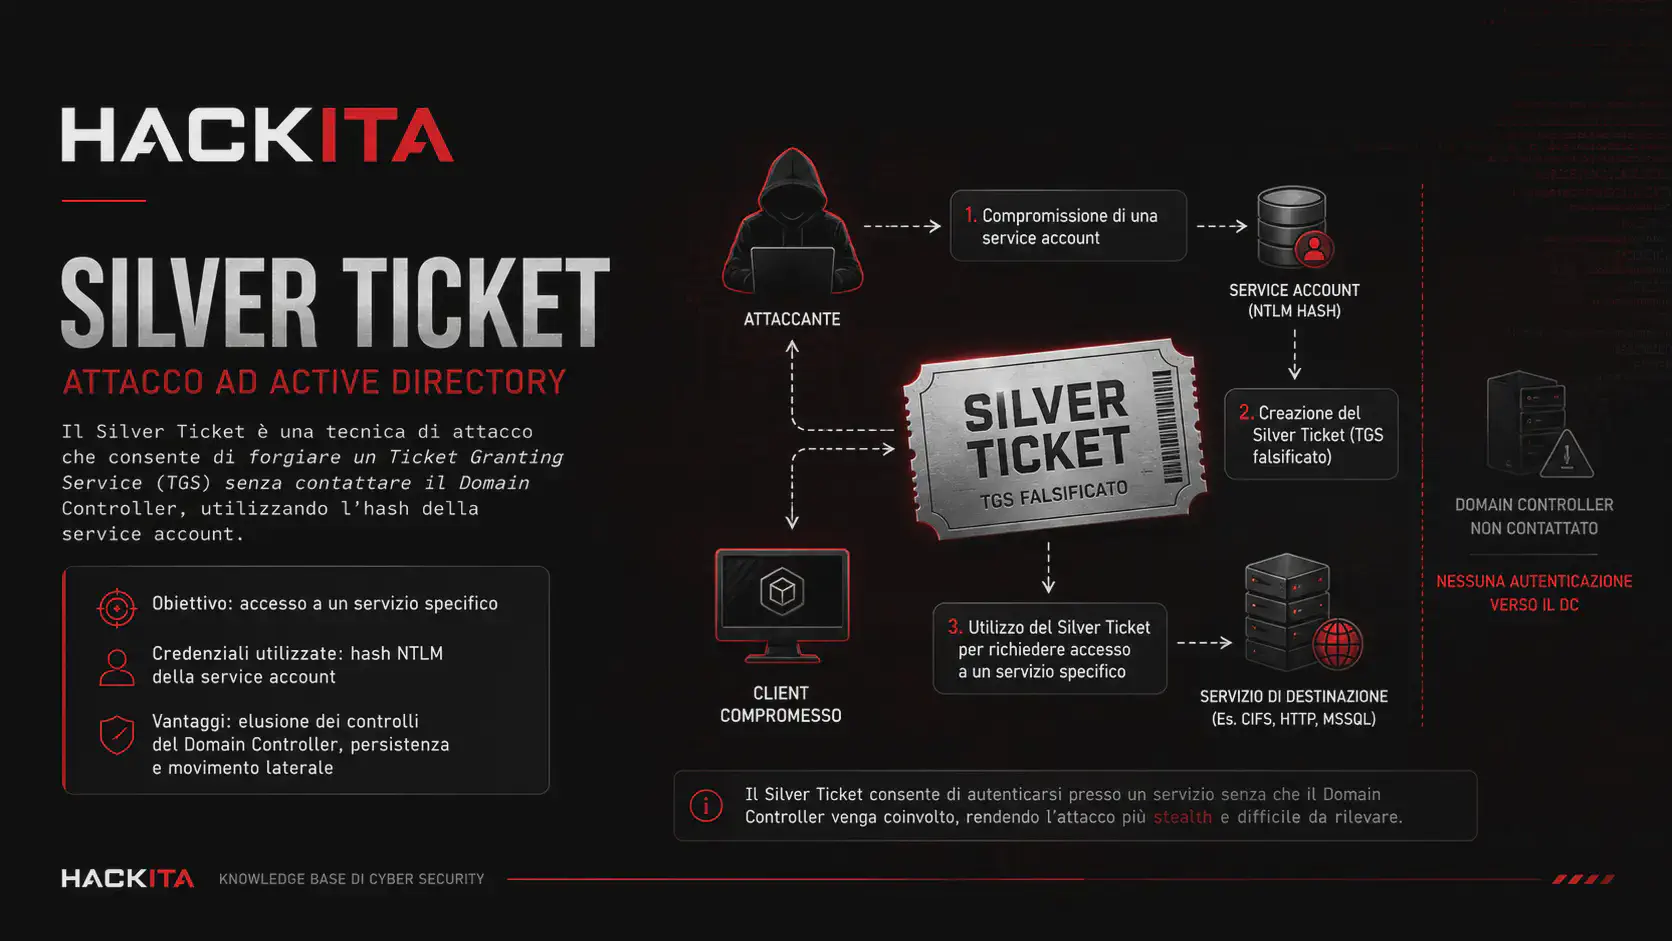
The Silver Ticket forges a Kerberos TGS using a service account hash, completely bypassing the KDC. A complete guide: how to obtain it, forge it with Mimikatz, Rubeus, and Impacket, scenarios for CIFS, LDAP, MSSQL, HTTP, and how to detect it.
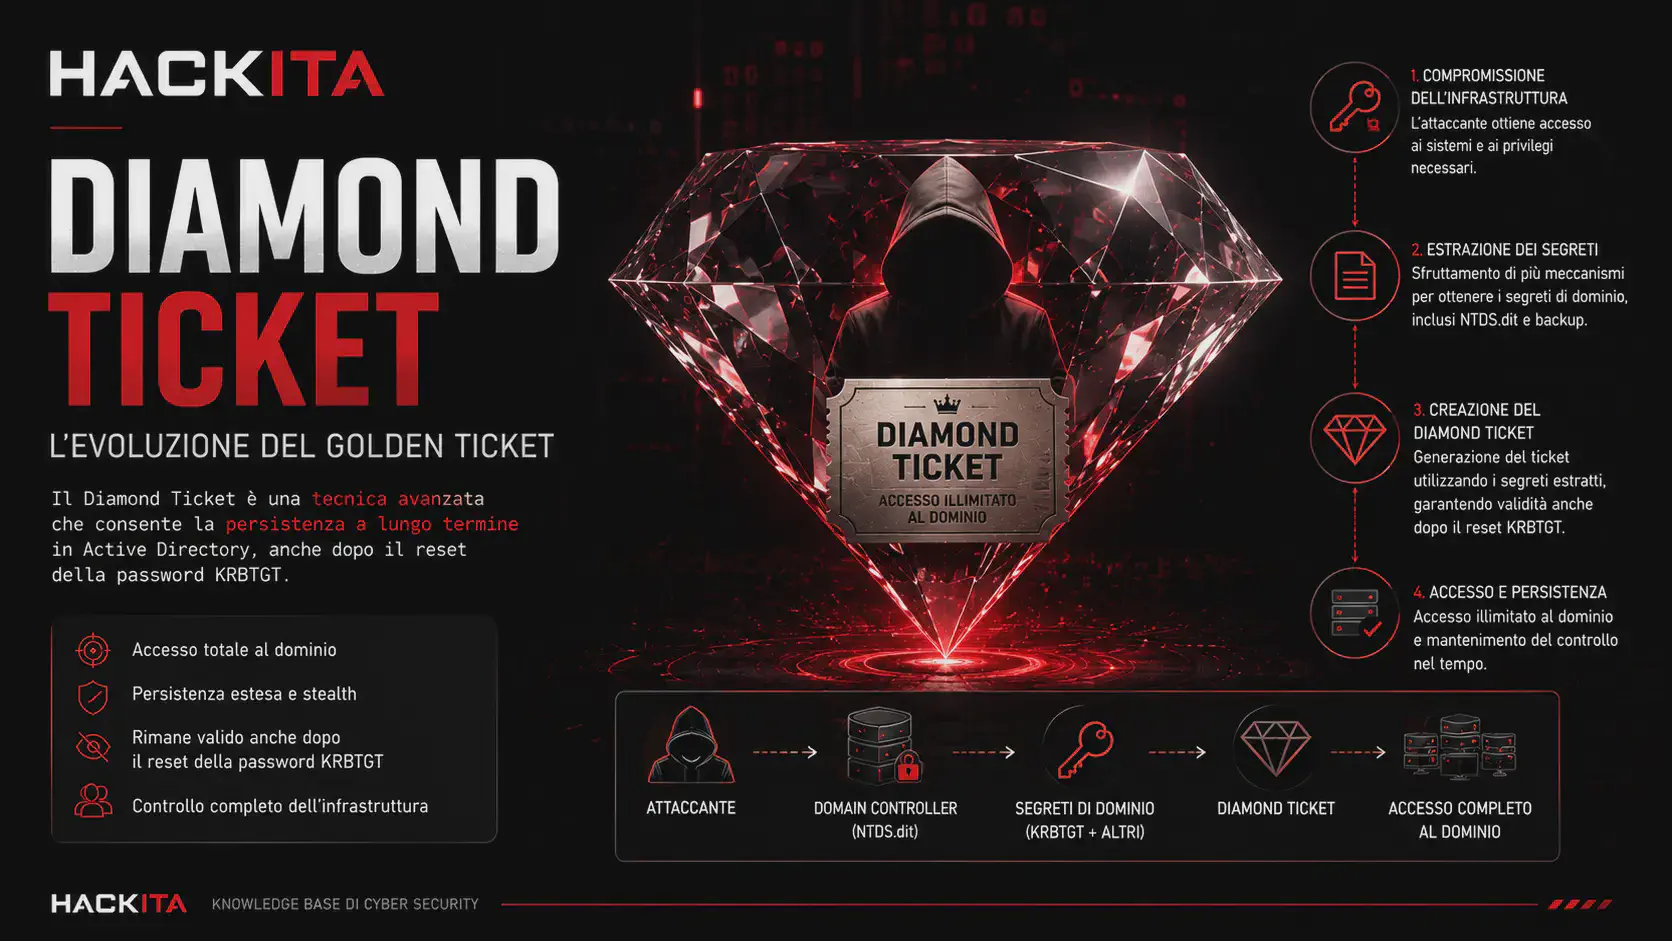
Diamond Ticket: A stealth variant of the Golden Ticket with a real TGT to bypass MDI. Rubeus /ldap /opsec guide, Impacket, detection, and KRBTGT reset.
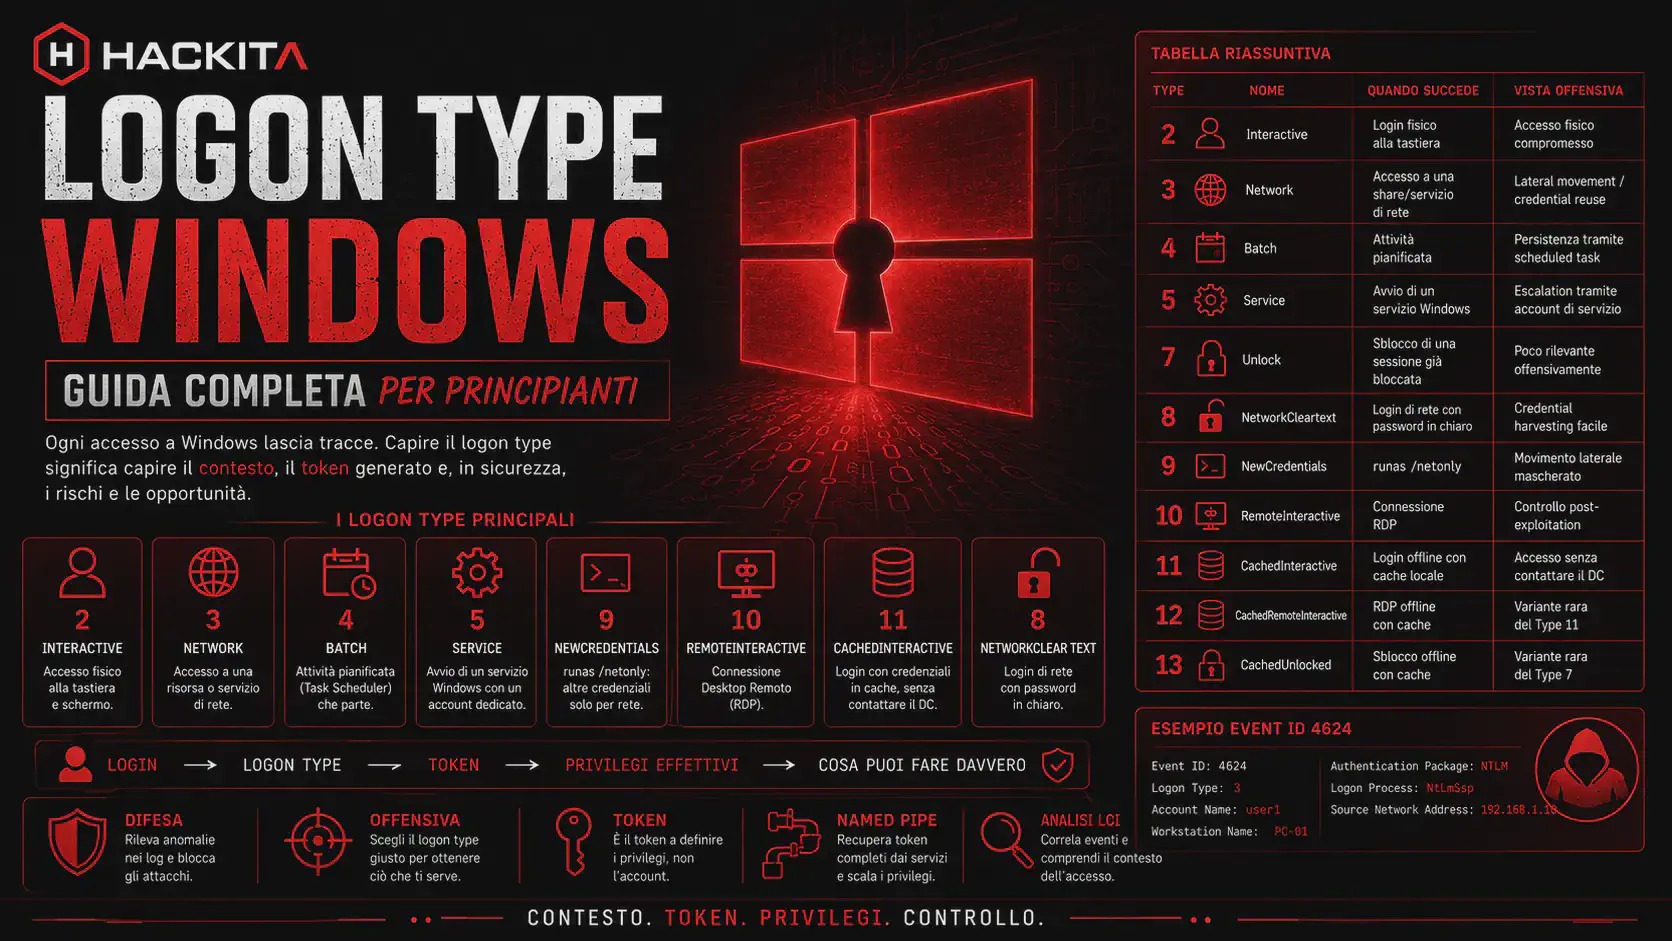
Windows Logon Type: A practical guide to the 13 logon types, from Interactive to CachedUnlock. Real-world examples and relevance for penetration testing and security audits.
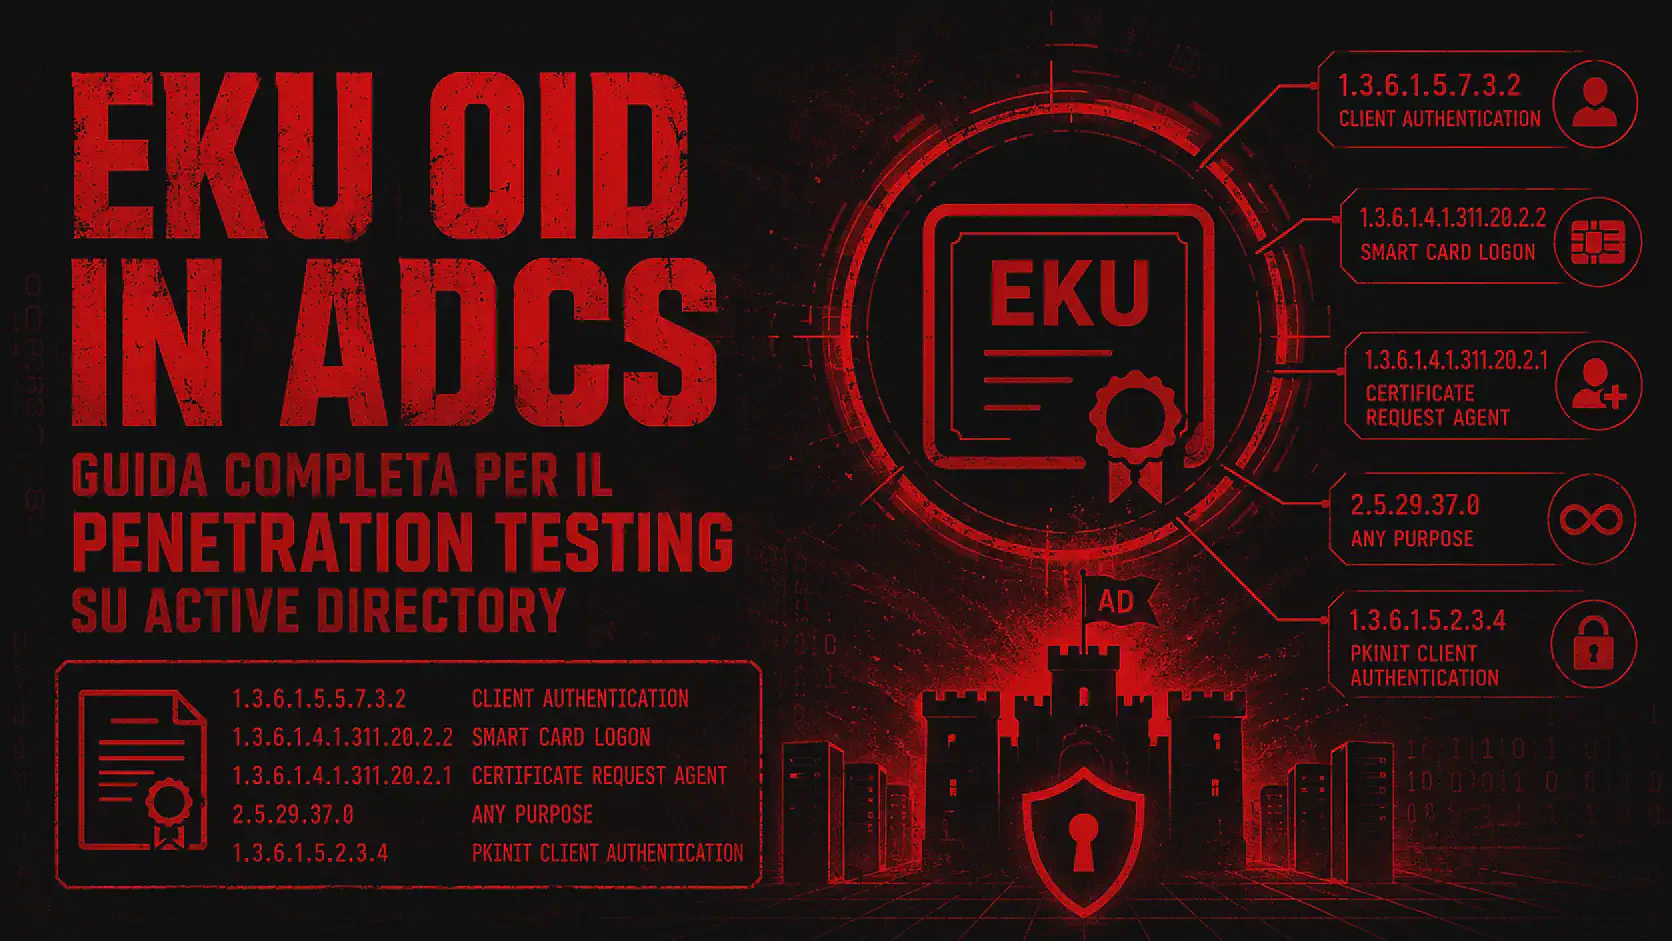
All Active Directory certificate EKU OIDs explained from an offensive perspective: which ones to exploit in ESC1–ESC16, PKINIT attack flow, Event ID detection, FAQ and complete table with offensive relevance.
From standard domain user to Domain Admin using MachineAccountQuota=10 and RBCD. Create computer account, S4U tickets, DCSync. Red Team AD guidance and privilege escalation.
Learn how to use SeRelabelPrivilege to lower the integrity level of files and directories, bypass Mandatory Integrity Control, and gain a SYSTEM shell.
How to use SeSecurityPrivilege to read and delete the Security Log, remove SACLs, and operate invisibly on Windows. Red Team OpSec guide with SIEM verification.
Kerberoasting in Active Directory: SPN enumeration with GetUserSPNs and Rubeus, RC4 downgrade, hashcat, targeted kerberoasting, and real OPSEC. From domain user to privileged credentials.
Found SeTcbPrivilege on a non-system account? Create LSA sessions with SID Domain Admins and get SYSTEM without external conditions. Red Team Technique.
NTLM explained from top to bottom: handshake, capture, NetNTLMv2 with Responder, Pass-the-Hash, coercion, and CVE 2026 enabled. NTLM vs. Kerberos decision point in the enterprise pentest.
Found SeCreateTokenPrivilege on a non-system account? Create tokens with SID SYSTEM and Domain Admins from scratch. NtCreateToken for SYSTEM shell. Red Team technique.
How to use SeManageVolumePrivilege and RawCopy to extract SAM, SYSTEM, and NTDS.dit from the physical disk, bypassing locks and ACLs. Red Team technique with raw device access.

From simple user to SYSTEM by replacing system files with a symlink: what you can do with SeCreateSymbolicLinkPrivilege and mklink. Privilege escalation and the Red Team technique.
How to abuse SeTakeOwnershipPrivilege to take ownership of system binaries and gain the SYSTEM shell. takeown + icacls + binary replacement. Red Team technique.
How to abuse SeRestorePrivilege to overwrite system binaries and gain SYSTEM shell. ImagePath hijacking, DLL sideloading, persistent backdoor. Red Team technique.
PrivEsc with SeBackupPrivilege on Windows and Active Directory: SAM, SYSTEM, and SECURITY extraction, offline dump with secretsdump, access to NTDS.dit, and real-world impact on compromised domains.
Privilege escalation with SeAssignPrimaryTokenPrivilege and potato attack bypass on Windows: privilege verification, exploits with GodPotato, JuicyPotato, and SweetPotato, real-world scenarios, common pitfalls, and mitigations.
SeLoadDriverPrivilege Enabled? Loads a vulnerable driver into the kernel, executes ring-0 code, disables EDR, and bypasses LSASS PPL. Help BYOVD with Capcom.sys and EDRSandBlast.
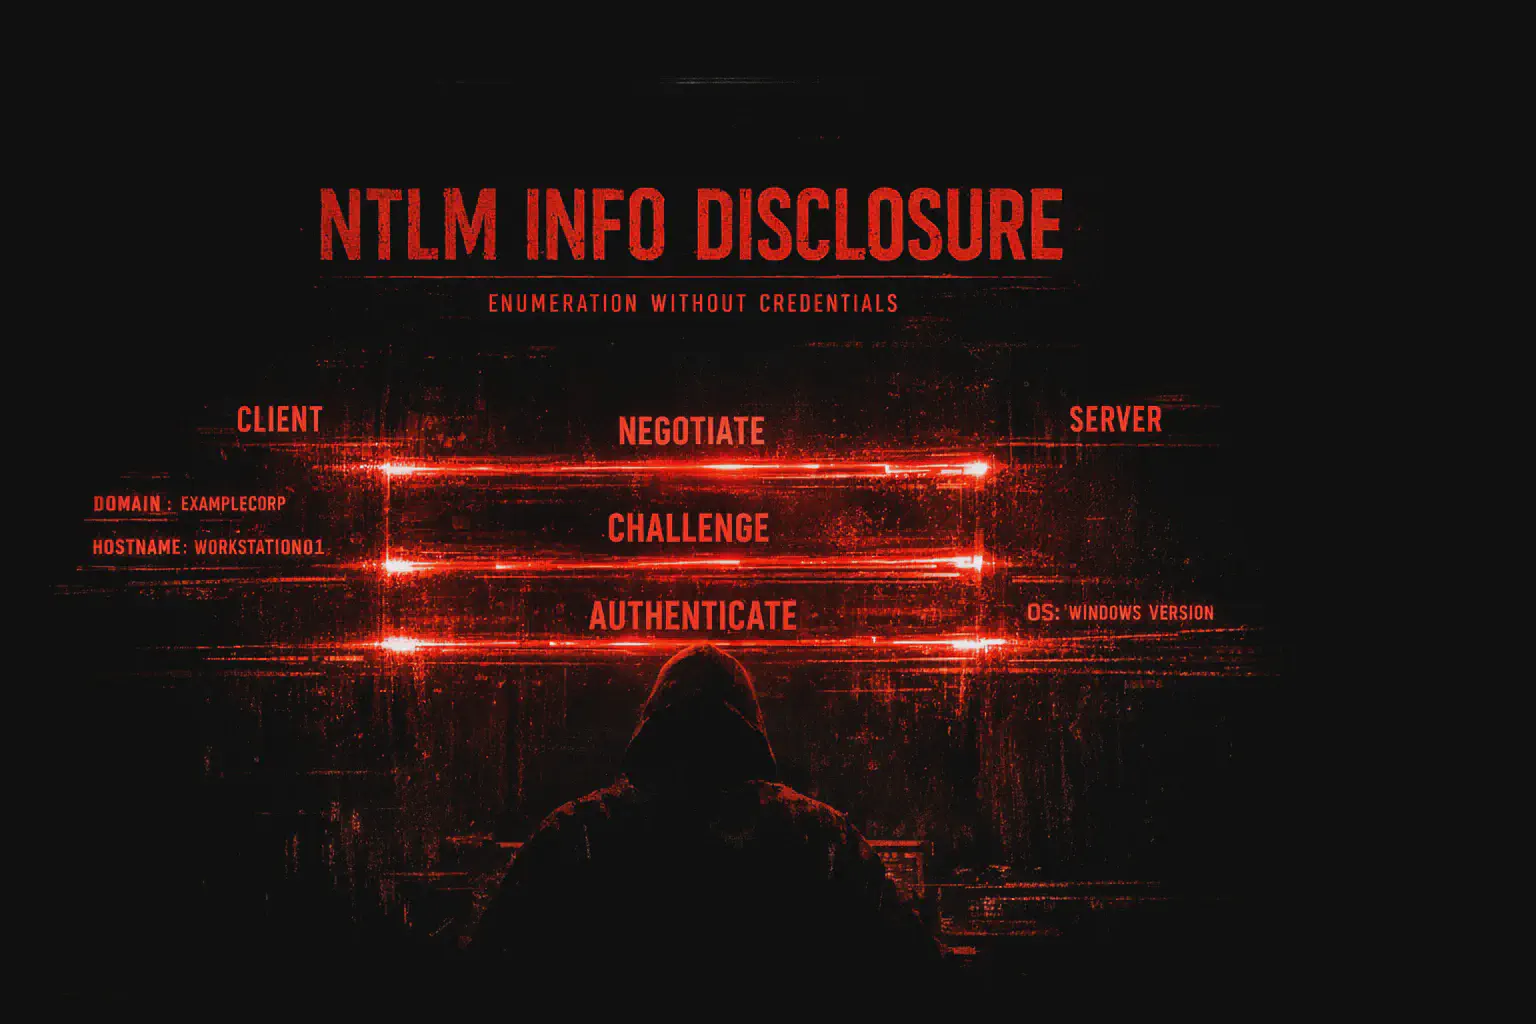
NTLM authentication over HTTP reveals AD domain, NetBIOS name, hostname, and OS version with a single GET, without credentials. This is an essential recon technique for Exchange and IIS red teams. Learn curl, Nmap, Burp, and defenses.
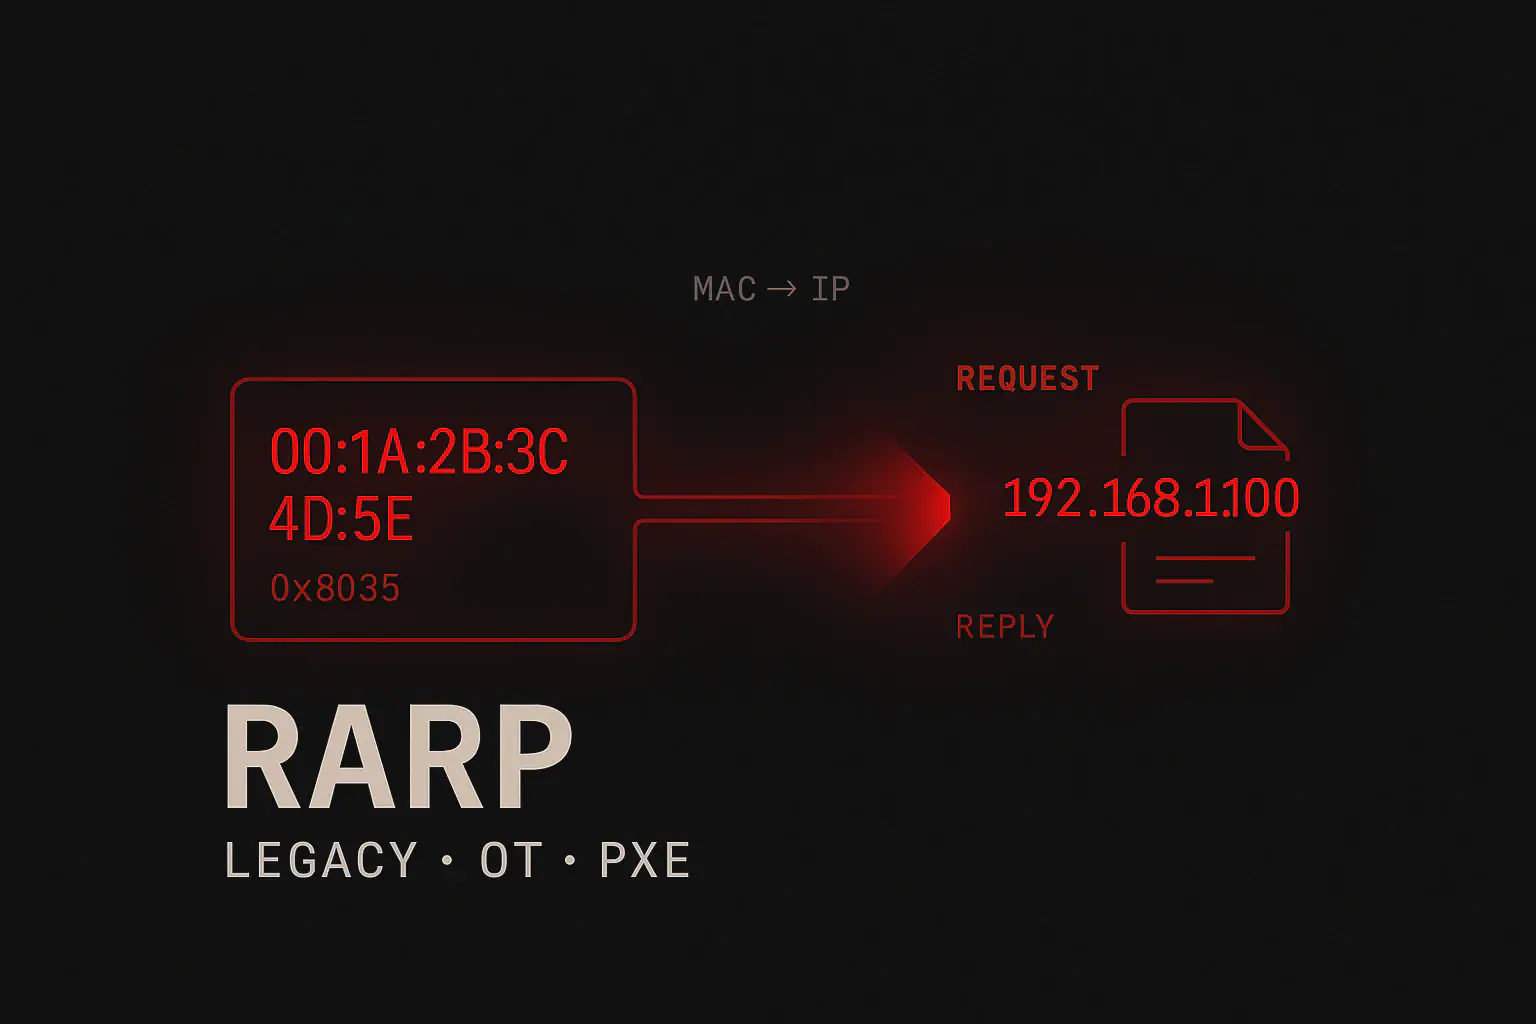
RARP: what it is, how it works, and why it still matters in pentests on legacy networks, OT/ICS, and PXE boot: request/reply, spoofing, boot hijacking, and the differences with ARP and DHCP.
Complete guide on DPAPI in an Active Directory pentest: masterkey, credential files, Chrome/Edge offline with pypykatz, LSASS dump LOLBin, DSInternals and DonPAPI.
ESC15 allows privilege escalation in Active Directory via CVE-2024-49019: Application Policy injection in V1 templates alters certificate usages.
ESC16 in AD CS: The CA doesn't include the SID in the certificates. Learn about identification with Certipy, privesc, the ESC16+ESC6 chain, and the mitigation updated to 2026.
ESC10 AD CS leverages Schannel's weak certificate mapping for privilege escalation via LDAPS. Guide with Certipy, UPN manipulation, detection, and mitigations.
A CA vulnerable to ESC11 can accept NTLM relay via RPC. How to recognize the configuration, privesc, assess the impact on certificates, and prevent abuse.
ESC12 in AD CS is about YubiHSM2 KSP abuse on Windows CA: privilege escalation in Active Directory and use of Certipy after local compromise.
Privilege escalation in Active Directory via ESC13: Certipy detects Issuance Policy OIDs linked to AD groups and explains privilege abuse via Kerberos TGT.
Privilege escalation in Active Directory: ESC14 exploits weak X.509 mappings in altSecurityIdentities to impersonate Windows accounts via certificates.
ESC8 privilege escalation, leverages NTLM Relay against AD CS /certsrv/ endpoints to obtain privileged certificates. Guide to Certipy and NTLM coercion.
ESC9 uses AD CS templates without the SID Security Extension to impersonate privileged users. A practical guide with Certipy and UPN manipulation.
A practical guide to ESC3 in AD CS: Enumerate templates with Certipy, analyze Enrollment Agent certificates, and dive into privilege escalation in Windows AD.
ESC4 ADCS Privilege Escalation: Detect weak ACLs on certificate templates, transform them into ESC1s with Certipy, and analyze the path to Domain Admin.
Learn about ESC5 privilege escalation in Windows Active Directory (AD CS): Enumerate PKI ACLs with Certipy and PowerShell, verify NTAuthCertificates, and mitigations.
PrivEsc ESC6 in AD CS with Certipy: Check EDITF_ATTRIBUTESUBJECTALTNAME2, SAN injection, and differences between ESC9 and ESC16, with practical checks and mitigations.
Discover ESC7 in AD CS: Leverage Manage CA permissions with Certipy and privesc, verify the SubCA path, and apply detection and mitigations in AD environments.

AD CS Privilege Escalation on Active Directory: A Complete Guide to ESC1–ESC16 Techniques with Certipy. Learn how to gain Domain Admin by exploiting misconfigured certificate templates and CAs.
A practical guide to ESC1 in Active Directory: analyzing vulnerable templates with Certipy, Kerberos authentication, detection, privesc, and security mitigations.
ESC2 in Active Directory Certificate Services: Windows privilege escalation with Any Purpose EKU template, exploits with Certipy and mitigations for secure AD CS.
Active Directory Pentesting operationally explained: AD architecture, Kerberos vs NTLM, BloodHound, Kerberoasting, AS-REP Roasting, NTLM Relay, ACL abuse, AD CS, DCSync, Golden Ticket, Shadow Credentials and real defenses.
Port 88 Kerberos: Complete guide to Active Directory penetration testing. Learn about Kerberoasting, AS-REP Roasting, Golden Ticket, Silver Ticket and Pass-the-Ticket for privilege escalation and lateral movement.
Mimikatz explained for pentesters: LSASS credential extraction, DCSync, Golden Ticket, pass-the-hash, and Active Directory attacks with practical examples.
SMBExec: A Practical Guide to Windows Remote Execution: Stealthy Lateral Movement via SMB Without Disk Files. A Fileless Alternative to PsExec for AD Pentesting.
Seatbelt is a Windows enumeration tool that collects system, user, privilege, and configuration information useful for privilege escalation.
SharpChrome: Dump Browser Credentials from Windows (DPAPI Abuse)
SharpDPAPI allows you to extract and decrypt DPAPI-protected credentials on Windows. This advanced tool is for credential access and lateral movement.
SharpUp (GhostPack) Guide: Commands, real-world checks (ModifiableServices, AlwaysInstallElevated, DLL hijacking), and how to exploit them for privilege escalation on Windows.
Sherlock identifies privilege escalation vulnerabilities on Windows by comparing installed patches and known CVEs. A quick tool for local privilege discovery.
Rubeus is the reference C# tool for attacking Kerberos in AD. Discover Kerberoasting, AS-REP Roasting, Pass-the-Ticket, and S4U with real-world detection.
Learn Pass-the-Hash (PtH) on Windows: how it works, how to leverage NTLM hashes to gain passwordless access, and real-world lateral movement techniques.
PsExec allows remote command execution on Windows systems via SMB. A key tool for lateral movement and remote administration.
JAWS is a PowerShell script for automatic enumeration on compromised Windows hosts, useful for identifying misconfigurations and privilege escalation vectors.
DCSync is an Active Directory technique that allows credential hash extraction by abusing the domain replication mechanism. It is used post-exploitation to obtain NTLM hashes of privileged users without direct access to the domain controller.
AdFind is a tool for enumerating Active Directory objects via command-line LDAP queries. A practical guide to using it during domain enumeration during a penetration test.
Scheduled Task Backdoor: Persistence on Windows via Task Scheduler with schtasks and PowerShell. Stealth techniques, EDR evasion, log detection, and real-world Red Team scenarios.
Practical guide Certutil.exe for Windows penetration testing: file download, Base64 encoding, hash verification and AV bypass. Living off the Land with native tool.
Learn how to enumerate and join MSSQL (port 1433): pentest for weak credentials, xp_dirtree for NTLM hashes, xp_cmdshell for RCE, and pivoting on linked servers
LDAP 389 PORT: Null bind, users, groups and SPNs, exposed credentials, LDAP relay and injection: enumeration techniques and misconfigurations in Active Directory.
SMB Port 445 on Windows Servers: Share enumeration, exploits, NTLM relay, Pass-the-Hash, remote execution, and lateral movement in Active Directory.
Latest Networking
TFTP over UDP 69: A Practical Guide to Enumeration, Files, Configurations, Vulnerabilities, Cleartext Traffic, and Risks in Internal Networks.
What is a DDoS attack and how does it work? Learn about DDoS types, attack techniques, authorized testing, and how to verify the effectiveness of your defenses.
WAN penetration testing guide: Analyze VPN, IPsec, MPLS, and SD-WAN, identify tunnel vulnerabilities, and verify WAN infrastructure security.
MS08-067: What it is, how it works, and why it's one of the most notorious Windows RCEs. Learn about Server Service, NetAPI, SMB, Metasploit, detection, and mitigations.
FTP Bounce Attack: What it is, how the PORT command works, why it can enable indirect port scanning, and how to detect and prevent it.
Learn Scapy with Python to create and parse TCP, UDP, ICMP, and ARP packets, perform SYN scans, sniffing, ARP spoofing, and test firewalls and IDSs.
Port 2375 Docker API pentest: Test unauthenticated access, get RCE and root on the host, and apply detection, TLS, firewall, and hardening.
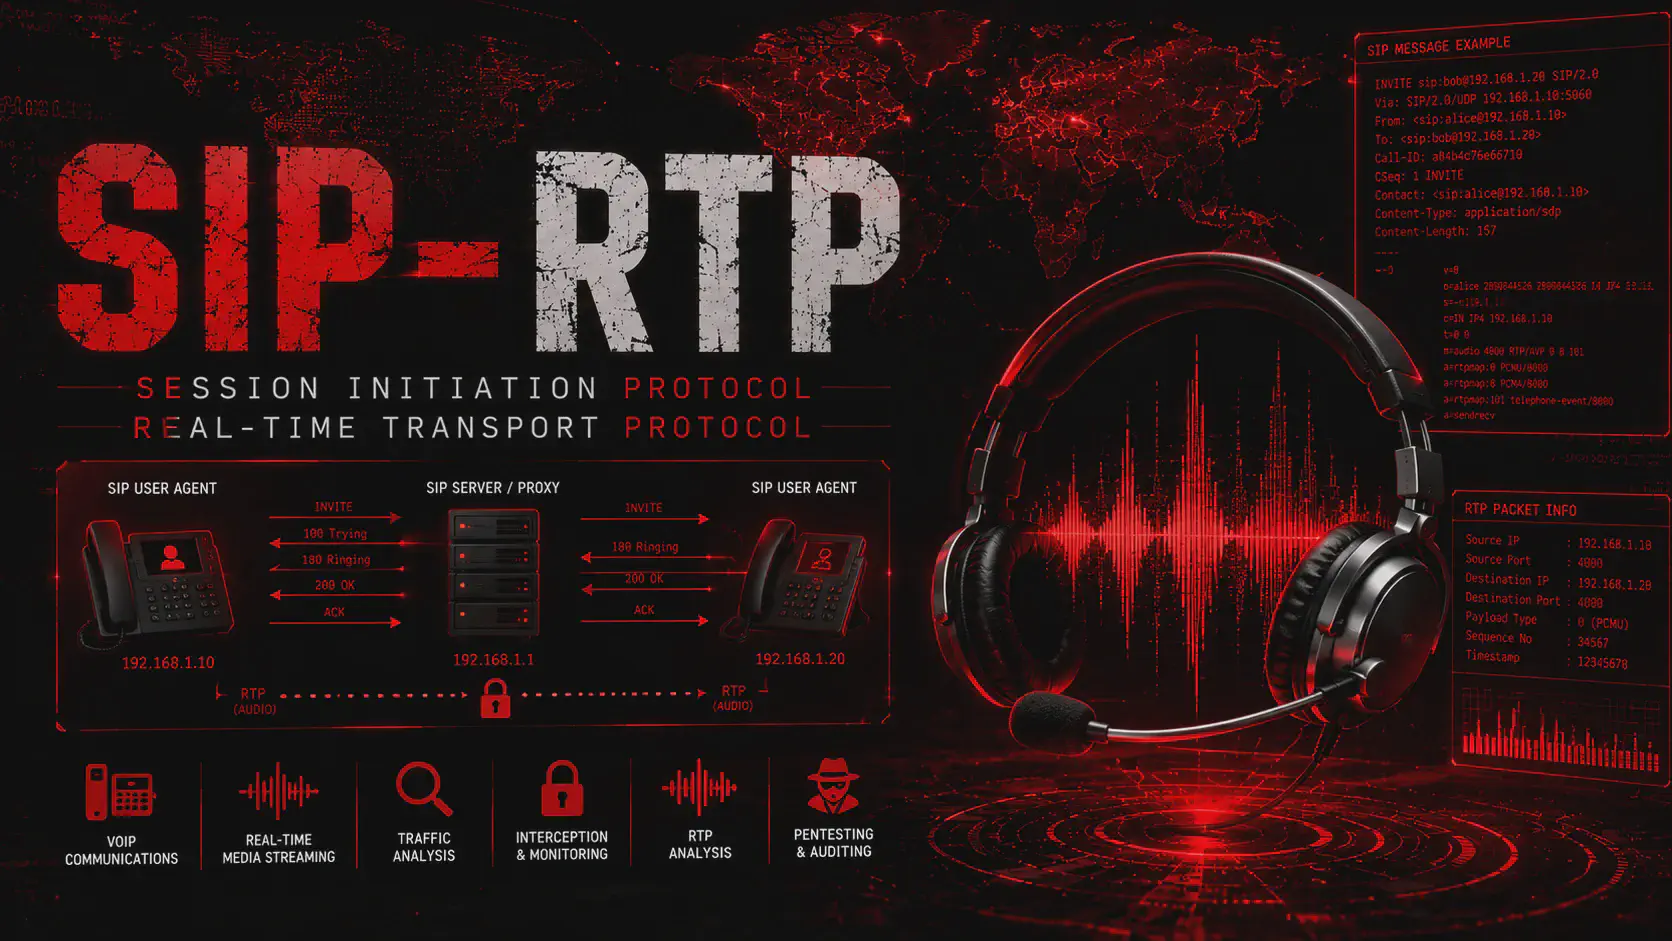
A practical guide to SIP and RTP pentesting: VoIP enumeration, authentication, traffic analysis, RTP injection, operational tools, and defenses with TLS and SRTP.
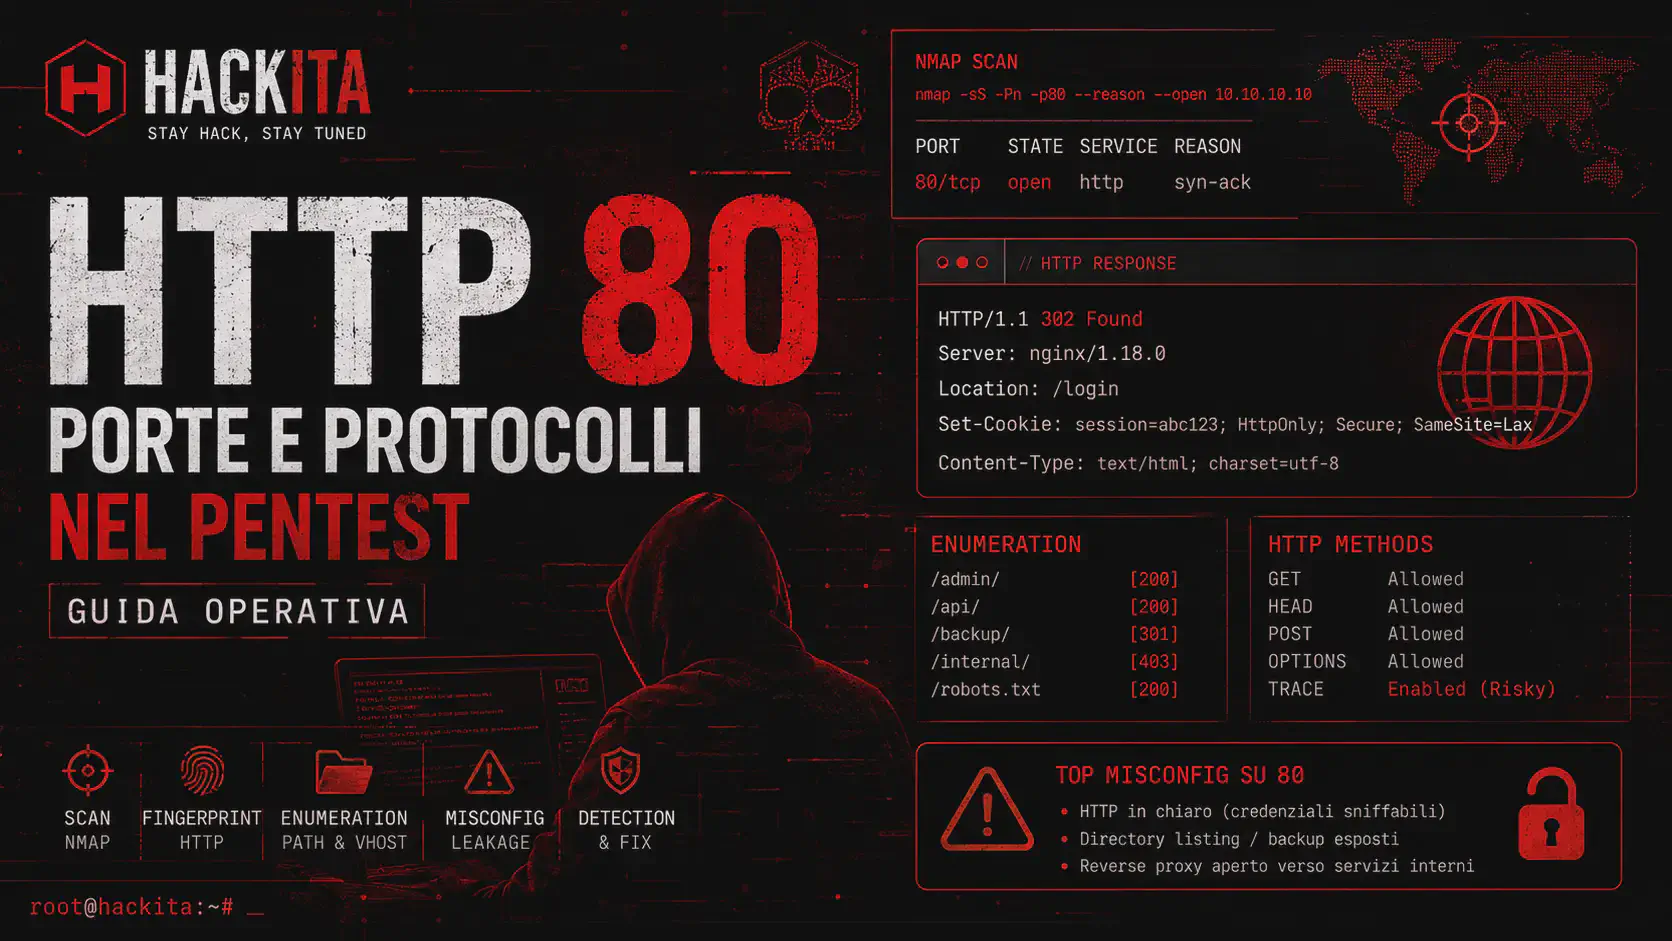
Port 80 in pentest lab: scan, HTTP fingerprint, vhost enum, directory brute force, misconfig and detection. Workflow with Nmap/ffuf/curl.
Learn how to pentest SSH from an offensive perspective: enumeration, brute force, port forwarding, SOCKS pivoting, file transfer, and agent hijacking for authorized red team engagements.
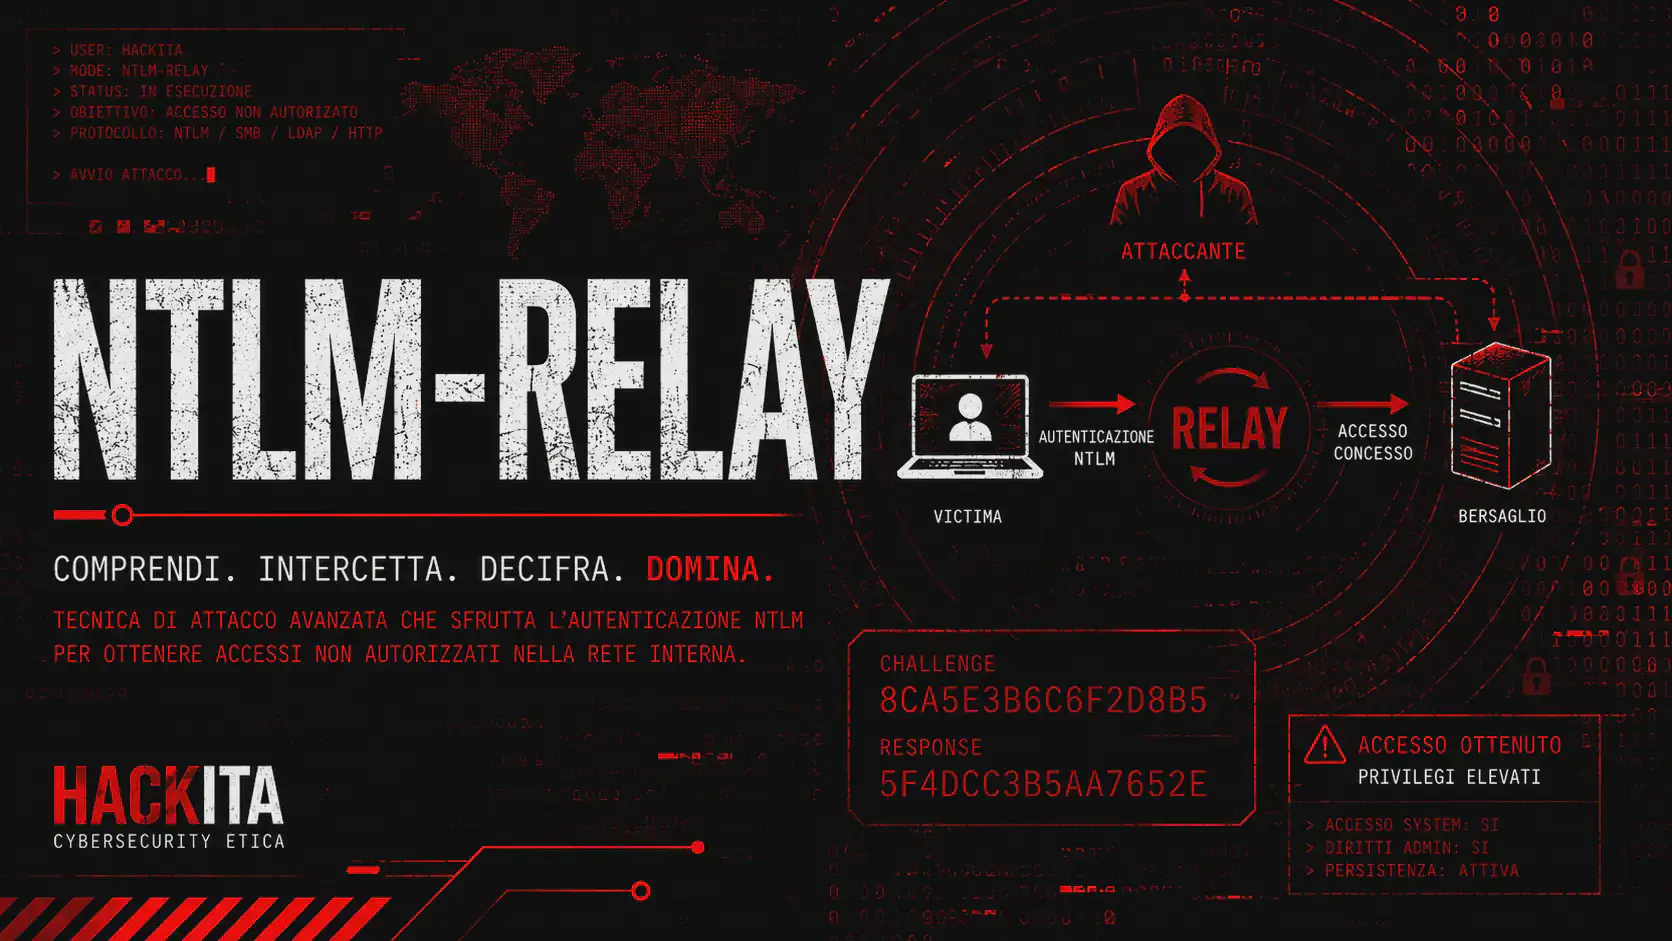
Complete guide to the NTLM Relay Attack with ntlmrelayx: coercion (PetitPotam, PrinterBug), SMB/LDAP/ADCS relay (ESC8), RBCD, Shadow Credentials, and DCSync. Internal network to Domain Admin workflow.
Complete guide to Splunk pentesting: Exploit CVE-2024-36991, recover credentials via splunk.secret, obtain RCE via malicious app, and scale to SYSTEM or root.
All TCP and UDP ports in penetration testing, organized by attack scenario: Active Directory, web, database, mail, DevOps. Attack vectors and complete technical guides for OSCP and red teams.
Complete guide to ICS/OT penetration testing: Modbus, S7, DNP3, BACnet, EtherNet/IP protocols. GRASSMARLIN tools, pymodbus, python-snap7, ISF, IndustrialXPL-Forge. CVE 2024-2025 and real attacks.
NetBIOS on port 137 enabled? Responder captures NTLMv2 hashes in minutes, ntlmrelayx executes commands without cracking. Chain from NBT-NS poisoning to Domain Admin for pentest.
Port 138 open? The attack surface is minimal in 2026, but it indicates NetBIOS is enabled. Focus on port 137 with Responder and 445 with SMB—those are the real vectors.
RPCbind on 111? Enumerate NFS and NIS with rpcinfo, mount anonymous shares, bypass root_squash with UID matching, and steal SSH keys or password hashes. Chain to root in minutes.
Port 113 open? Ident is nearly defunct, but it reveals usernames and points to vulnerable legacy systems. Learn how to enumerate and what to look for next.
Port 119 open? NNTP is nearly defunct, but it can expose newsgroups with cleartext credentials, usernames, and confidential data. Learn how to enumerate and exploit it.
Port 135 open? Enumerate users with null sessions and RID cycling, run commands via WMI/DCOM with Impacket, and reach Domain Admin in 42 minutes. Complete AD pentest guide.
Port 139 open? Enumerate users with null sessions, exploit MS17-010 over SMBv1, and use ntlmrelayx if signing is disabled. Chain a Domain Admin in 27 minutes.
Port 67 without DHCP snooping? Deploy a rogue server with dnsmasq, poison gateways and DNS, capture NTLMv2 hashes with Responder, and get to Domain Admin in 90 minutes.
Port 95 open during a scan? SUPDUP has been defunct since the 90s. Learn how to identify the real service: hidden web server, custom app, or honeypot.
TACACS+ on Route 49 with a weak shared secret? Bruteforce the key, decrypt the traffic with Wireshark, and take control of every router, switch, and firewall in the Cisco infrastructure.
Port 90 open during a scan? PointCast has been dead since 2001. Learn how to identify the real service, whether it's a hidden web server, proxy, or custom app.
Port 37 open? Time Protocol reveals OS (Windows Server 2003/2008, Cisco IOS), timestamp, and uptime. Immediate red flag for legacy technology—chain to EternalBlue in 15 minutes.
WINS on port 42 without authentication: enumerates domain controllers, file servers, and logged-in users via NetBIOS. Instant red flag for legacy Windows—chain to AD in 20 minutes.
Port 27018 exposed? Connect directly to the replica set secondaries, read the oplog with cleartext password, bypass the keyfile, and pivot into cluster nodes.
Port 28017 open? Read version, hostname, and logs without credentials, dump data via REST API, and pivot to 27017. Only on legacy MongoDB ≤ 3.4, often unpatched.
RDP moved to 33389? nmap -sV finds it in seconds. BlueKeep, Pass-the-Hash, and brute force work identically. Changing ports isn't security—it's a placebo.
SAP Management Console on 50000 without auth: Enumerate versions, exploit RECON (CVSS 10), abuse RFC with SAP*/06071992 and get OS command execution on all ERP data.
HDFS without Kerberos on 50070? Browse the filesystem, download CDRs and PIIs via WebHDFS with user.name=hdfs, then get a shell to the cluster via the YARN REST API.
Unpatched ActiveMQ on 61616? CVE-2023-46604 gives root shell in 8 seconds via OpenWire. Web console with admin:admin, messages with JDBC credentials, and lateral movement to Oracle.
Memcached opened without authentication: dump session token, credentials, and JWT with nc. 51.000x UDP amplification, cache poisoning, and hardening explained.
RabbitMQ management exposed on 15672? With guest:guest, read every message in the queue, dump hashes, and get RCE via Erlang cookies. Practical offensive guide.
HBase Master UI on 16010 without authentication: enumerate tables, dump data via REST API and Thrift, read tokens and CDRs. Full pentest with scan, Hadoop lateral movement.
MongoDB exposed on 27017? Login without authentication, bypass $ne login, dump credentials and MFA secret, and perform privilege escalation. Complete pentest with live payloads.
Port 10000 Webmin: CVE-2019-15107 pre-auth RCE root backdoor, CVE-2022-0824 file manager, CVE-2024-12828 CVSS 9.9, Metasploit modules, and post-exploitation with full root access.
Port 9200 Elasticsearch without authentication: Index dumps with credentials and PII, password lookup in logs, Groovy script RCE, CVE-2015-1427, elasticdump, and lateral movement from ELK stack.
Port 9000: Direct RCE via PHP-FPM FastCGI exposed, SonarQube admin:admin with hardcoded source code and credentials, Portainer without initial setup and container escape.
Port 9090: Authless Prometheus exposes entire infrastructure and credentials, Cockpit provides a Linux shell in the browser, and JBoss WAR deploys for RCE. Operational cheat sheet included.
Port 9092 Apache Kafka without authentication: topic list, real-time message interception, message injection, Kafka Connect credentials JDBC and full offensive chain.
Elasticsearch transport port 9300: Unauthorized cluster join, data replication to malicious node, Java deserialization RCE CVE-2015-5377, and operational differences from port 9200.
Port 9418: Authenticationless git daemon: Repository clone, credential extraction from commit history, truffleHog, gitleaks, web-exposed .git, and lateral movement from source code.
Port 9999: Abyss Web Server directory traversal and admin bypass, Icecast buffer overflow RCE CVE-2004-1561, Varnish admin exposed, unprotected server staging and backdoor detection.
Offensive guidance on Oracle HTTP Server port 7777: OHS enumeration, EBS and PeopleSoft default credentials, CVE-2022-21587, PL/SQL gateway injection, SSRF, and lateral movement.
Port 8000 offensive guide: Django DEBUG=True, Python http.server directory listing, Flask Werkzeug console, PHP built-in server and credential extraction. With cheat sheets.
Alternative HTTP port 8008: Grafana and Splunk default credentials, CVE-2021-43798 path traversalSpring Boot Actuator heapdump, internal REST APIs and credential extraction.
Port 8081: Nexus Repository default credentials, CVE-2019-7238 RCE, Traefik dashboard without auth, OWASP API Security Top 10 with operational payloads and supply chain attacks.
Alternative HTTPS port 8443: VMware vCenter CVE-2021-21972, pfSense RCE, UniFi Log4Shell, Cisco ASDM default credentials, certificate intelligence, and TLS hardening.
Port 8888 Authentication-free Jupyter Notebook: Direct code execution, token leak, integrated terminal, hardcoded credentials in notebooks, and real-world step-by-step attack chain.
Neo4j port 7474/7687 pentest: enumeration, default credentials, cypher injection, APOC RCE, hash dump, and API key. Complete guide 2026.
Port 7070 open? 2026 Pentest Guide: What is it, Helix/RealServer enumeration, RTSP exploits, directory traversal, AnyDesk, and Java app server.
Kibana Port 5601 in Pentest: Dev Tools Console, Elasticsearch Queries, Log Exposure, Internal Hosts, and Sensitive Credentials in Indexed Data
Port 5900 VNC in the pentest: remote desktop access, unauthenticated instances, password brute force, screenshots, and session hijacking.
WinRM HTTPS port 5986 in the pentest: client certificates, Evil-WinRM over TLS, ADCS abuse, and remote access via certificate-based authentication.
Port 6000 X11 in the pentest: exposed remote display, desktop screenshots, keylogging, input injection and session hijacking on Linux and Unix systems.
Redis port 6379 in pentest: unauthenticated login, key and session dumps, SSH key injection, malicious modules, and RCE.
Port 6443 Kubernetes APIs in the pentest: ServiceAccount token, secret extraction, pod access, escalation to cluster-admin, and cluster compromise.
IRC port 6667 in the pentest: server and channel enumeration, user and hostname info leak, C2 botnet, UnrealIRCd, and hijacking risks.
WebLogic port 7001 in pentest: T3 protocol, admin console, CVE RCE pre-auth, SSRF, and Oracle WebLogic Server access exposed.
WebLogic SSL Port 7002 in Pentest: HTTPS Console, T3S, TLS Certificates, Pre-Auth CVEs, and Attacks on Encrypted Oracle WebLogic Server.
Bring 3690 SVN to the pentest: exposed repositories, anonymous checkout, commit history, source code disclosure, and recoverable credentials.
Bring 4040 Spark UI to pentest: environment leak, worker discovery, exposed credentials, and pivot to 6066 REST API and big data cluster.
Port 4500 IPsec NAT-T in the pentest: IKE, NAT traversal, aggressive mode, PSK cracking and exposed VPN surface analysis.
Port 5000 in pentest: Docker Registry exposed with downloadable images and secrets, or Flask debug with console tool and RCE from the browser.
RabbitMQ port 5672 to the pentest: AMQP queues and messages, exposed credentials, Management API 15672, injection and Erlang cookie risk.
Port 2082 cPanel in the pentest: unencrypted HTTP login, credential reuse, upload via File Manager, database access, email, and backups.
Port 2083 cPanel SSL in pentest: HTTPS login, TLS enumeration, cPanel API, file upload, post-auth automation, and cPHulk checks.
Port 2181 ZooKeeper into the pentest: four-letter commands, dump configurations, cluster enumeration, and sensitive metadata.
Port 2376 Docker TLS API in pentest: TLS enumeration, mutual TLS, client certificate theft, misconfigurations, and remote daemon access
Oracle DB Port 2483 in Pentest: TNS Listener, SID and Service Name Enumeration, Credential Brute Force, DBA Escalation, and System Access Techniques
Oracle TCPS port 2484 in pentest: Encrypted TNS Listener, certificates and Oracle Wallet, TLS enumeration and differences with 2483.
Port 2701 TVersity in the pentest: media server with exposed web UI, shared file disclosure and access surface analysis.
Bringing the 3260 iSCSI to the pentest: target and LUN discovery, storage volume access, CHAP, remote disk mounts, and exposed data analysis.
Port 3478 STUN/TURN in pentest: NAT traversal, IP leak, NAT type, TURN relay abuse and misconfigurations in WebRTC and VoIP infrastructures.
DistCC Port 3632 in Pentest: distccd exposed, RCE without authentication via CVE-2004-2687, Nmap NSE verification, and immediate impact
cPanel and WHM Pentest Guide: 2083, 2087, and Webmail 2096 Panels, Account Enumeration, APIs, Hosting Exposure, and Critical Misconfigurations
MSSQL Pentest on port 1434/UDP: SQL Server Browser enumeration, named instance, version, dynamic ports, and SQL instance discovery in lab.
Citrix Pentest on port 1604/UDP: ICA Browser enumeration, published apps, StoreFront, 1494/2598 services, and access to Citrix Virtual Apps environments in lab.
PPTP Pentest on Port 1723: What it is, Control Channel Fingerprinting, MS-CHAPv2 Analysis, Legacy VPN Credentials, GRE, and Internal Network Access Risk.
RADIUS Pentest on Port 1812/UDP: Test Shared Secret, EAP Authentication, AD/LDAP Backend, RADIUS Accounting, and Network Access Control in the Lab.
Pentest RADIUS Accounting on port 1813/UDP: session tracking, Framed-IP, Accounting-Request, correlation with 1812 and visibility into network sessions in the lab.
Port 1883 MQTT in IoT pentest: topic enumeration, anonymous subscription, message injection, and clear text credentials on exposed brokers.
Port 1900 SSDP/UPnP in pentest: device discovery, port mapping abuse, SSRF via CallStranger, and exposed services analysis.
Port 1947 HASP in the pentest: Sentinel Admin Control Center, dongle enumeration and active licenses, version check and License Manager RCE risks.
Brings 1984 Xymon and BigBrother to the pentest: agent monitoring, host data disclosure, exposed services, and infrastructure dashboard accessible without adequate controls.
Port 1990 UPnP in the pentest: SOAP action, port mapping abuse, device control and analysis of IGD services exposed on the router.
Bring 1993 SNMP into the pentest: SNMP Inform, trap correlation, community string, alternative collectors and information disclosure on monitoring servers.
Port 2049 NFS in the pentest: export enumeration, remote mount, UID spoofing, no_root_squash, SSH key injection, and privesc Linux.
PostgreSQL pentest on port 5432: enumeration, brute force, pg_shadow, file read/write, COPY PROGRAM, RCE and privilege escalation in lab.
Port 110 exposes POP3, the protocol used to download email from the server to the client. A practical guide to enumeration, brute force, cleartext credential sniffing, message downloading, and mail server hardening.
OpenVPN pentest on port 1194: UDP/TCP fingerprinting, .ovpn file analysis, credential testing, client certificates, and internal network access in the lab.
Lotus Notes/Domino pentest on port 1352: NRPC enums, names.nsf, Domino Directory, NSF databases, WebAdmin, and weak logins in legacy environments.
Port 143 exposes IMAP, the protocol used to access and synchronize email and folders directly on the server. A practical guide to enumeration, login testing, mailbox discovery, and mail server hardening.
Oracle Pentest 1521: TNS Listener enumeration, payload, SID, and service name, weak credential testing, SQL injection, escalation to DBA, and lateral movement in the lab.
SMTP port 25 can expose user enumeration via VRFY and RCPT TO, open relay, email spoofing, and brute force on SMTP AUTH. A practical guide to mail server enumeration, exploits, detection, and hardening.
WHOIS port 43 allows passive queries on domains, IPs, and ASNs to gather registrars, name servers, contacts, and expiration dates for reconnaissance and OSINT.
Bring 5000 into the pentest: recognize Docker Registry, Flask debug, UPnP or Synology DSM. Enumeration, image pull, RCE Werkzeug and SOAP abuse in lab.
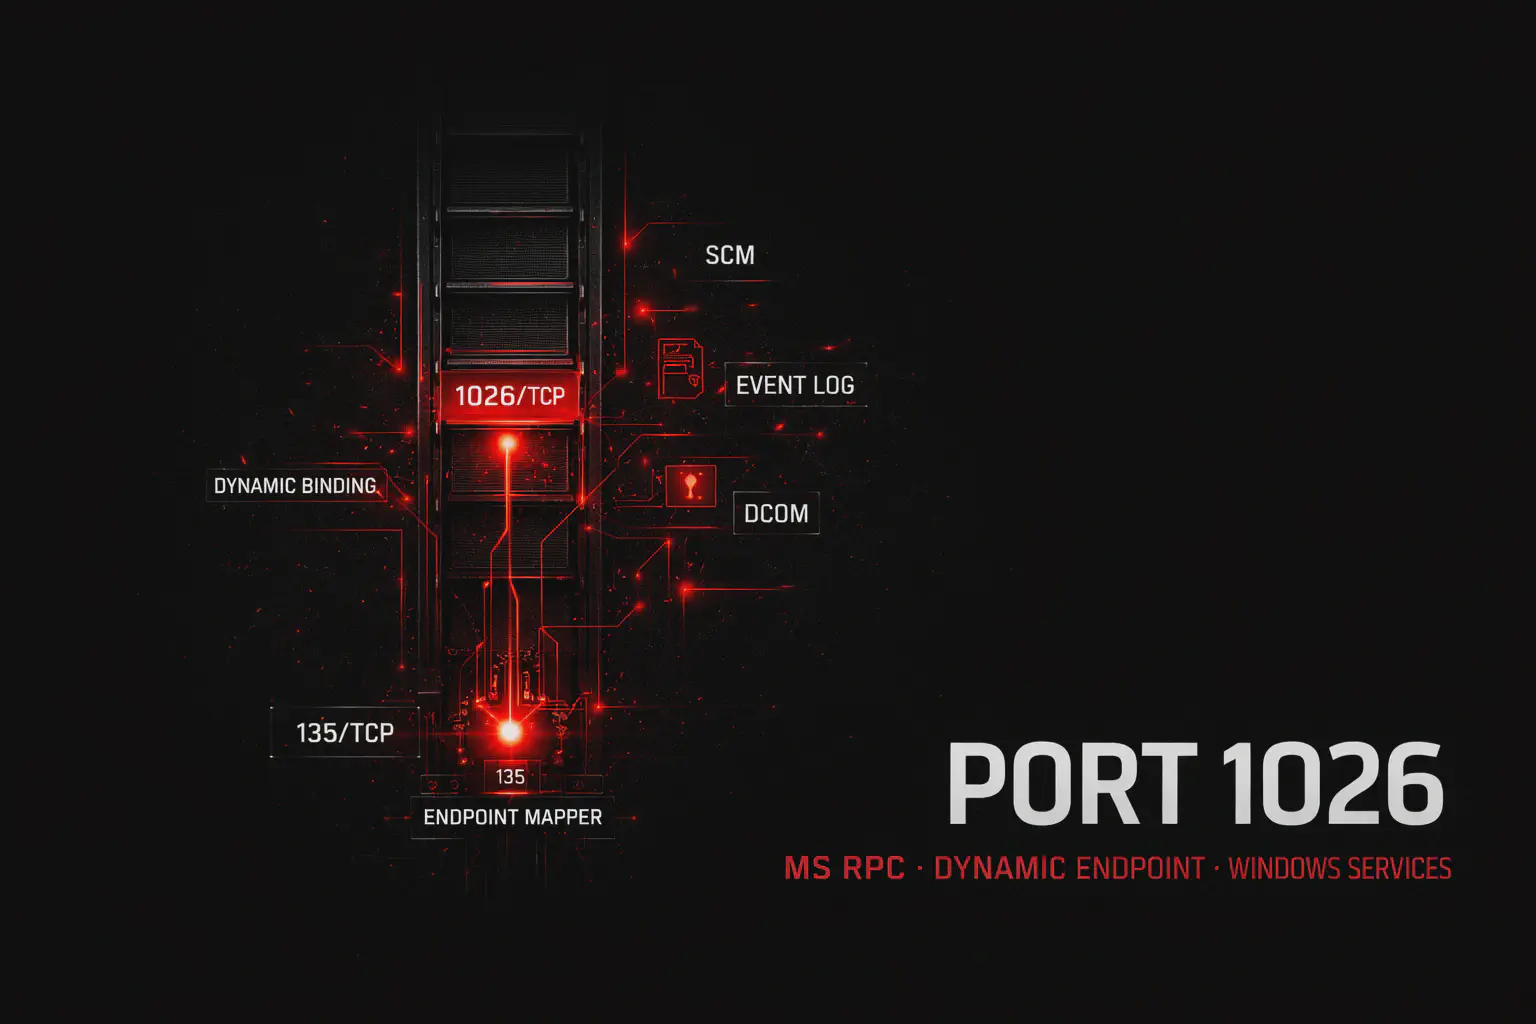
Learn what port 1026 is in MS RPC, why it correlates with the endpoint mapper on 135, and how dynamic RPC ports change between legacy and modern Windows systems, impacting enumeration, firewalling, and lateral movement.
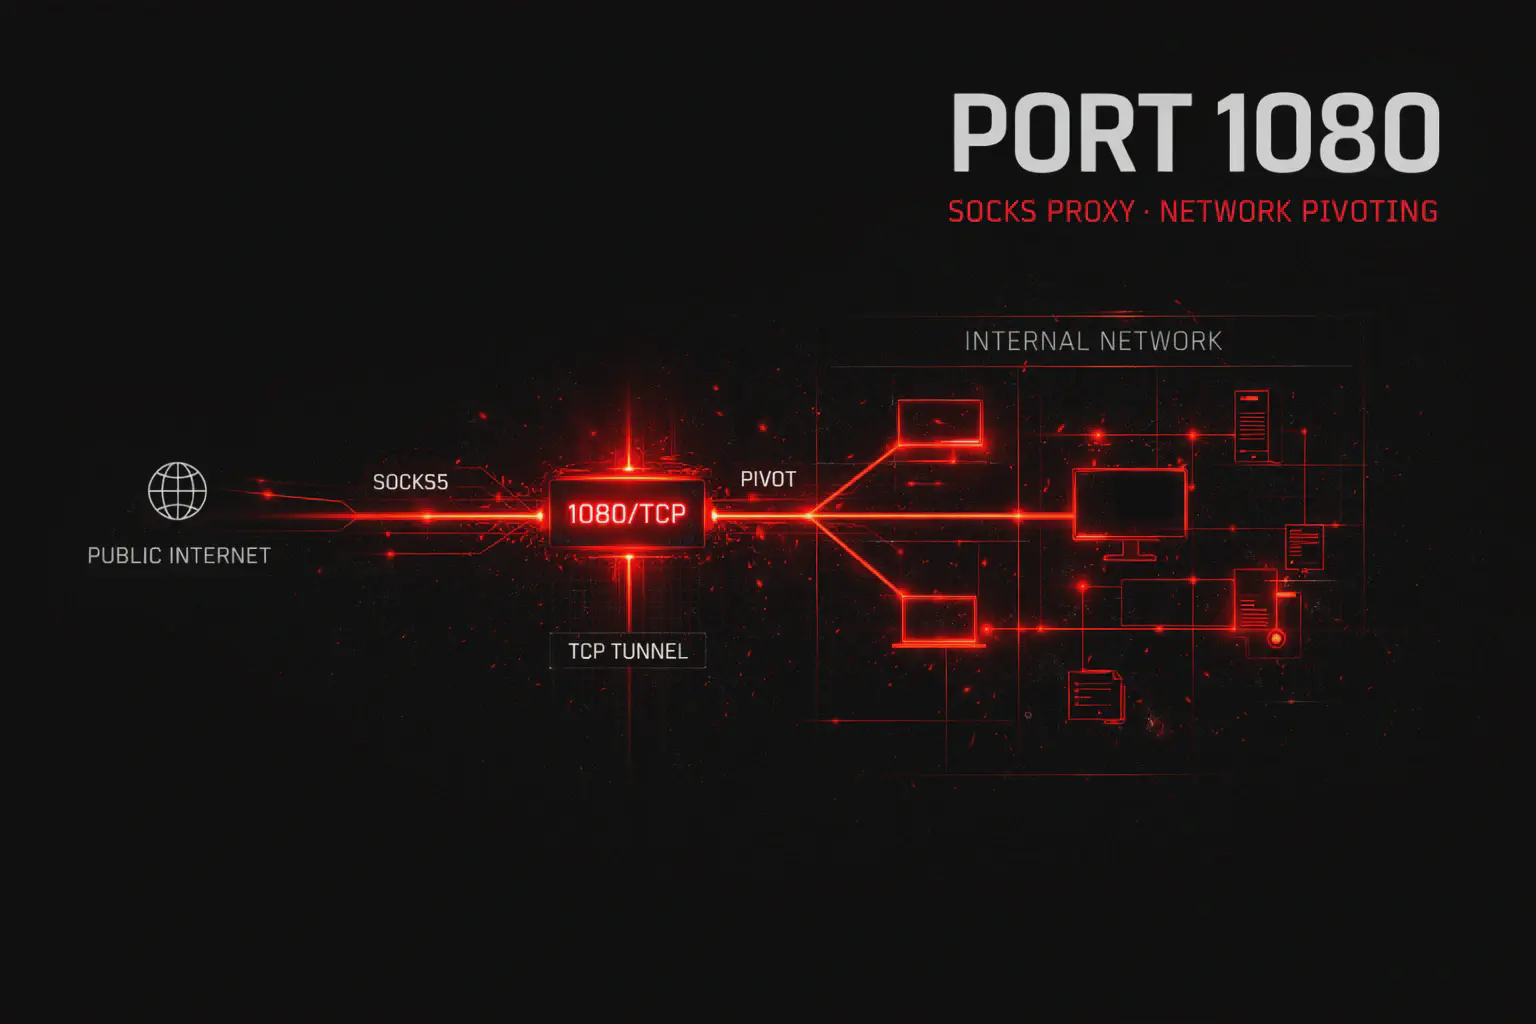
Port 1080 can expose an open SOCKS proxy that can be used for pivoting, tunneling, and internal network access. Learn how to identify, test, and exploit it in authorized pentests.
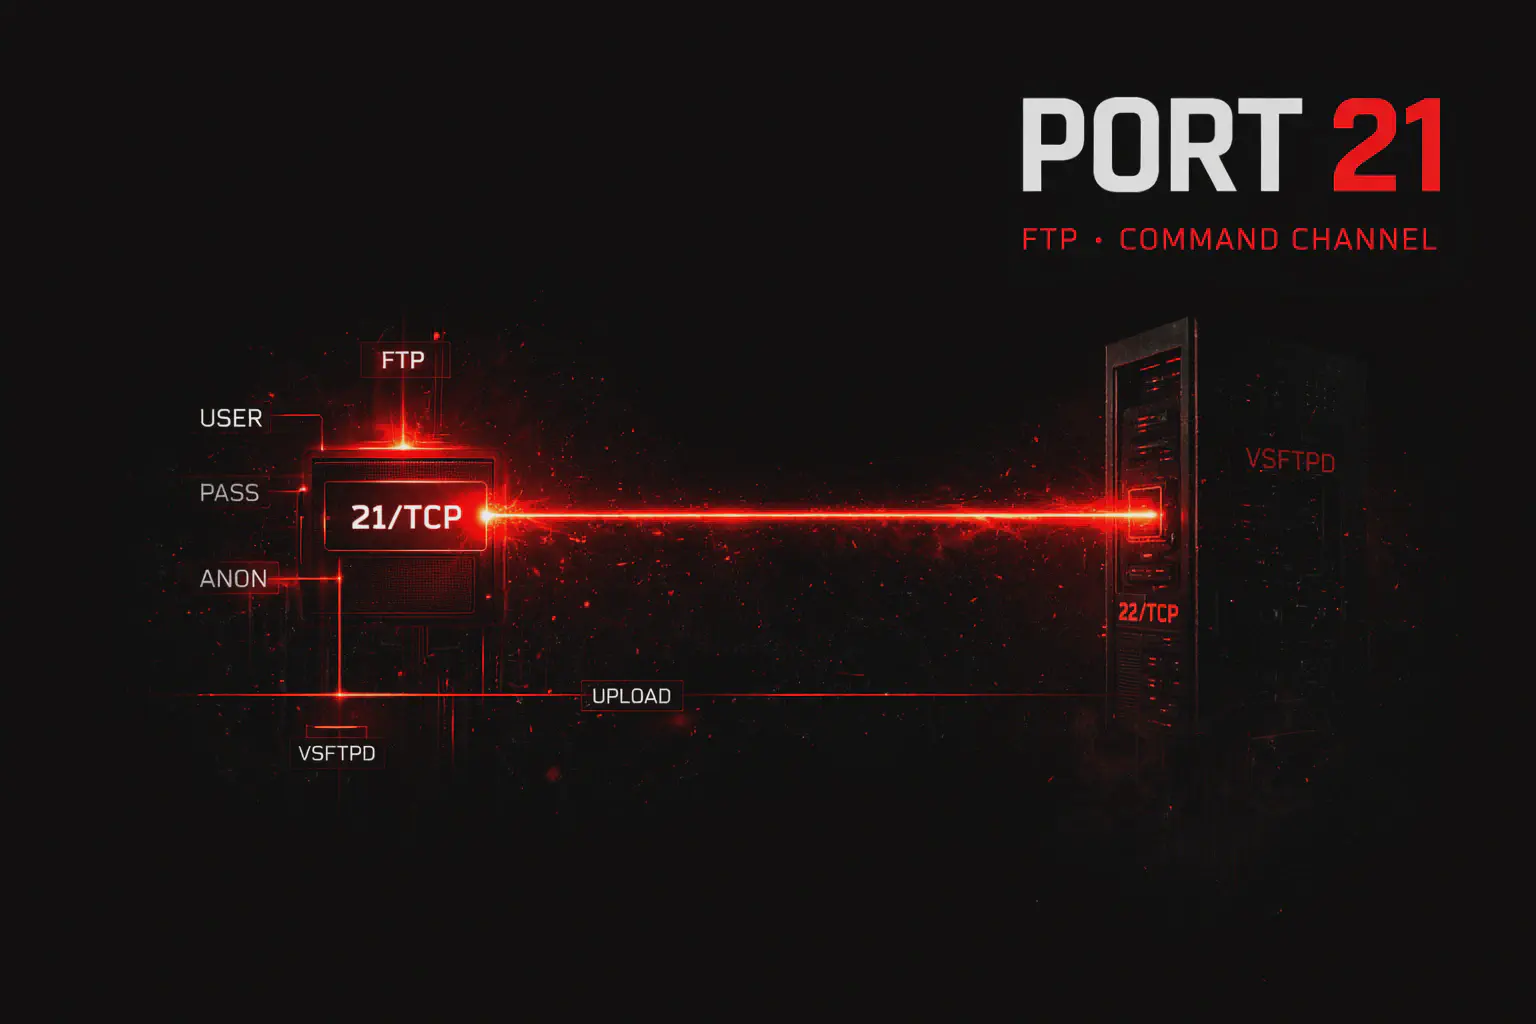
FTP port 21 remains a key pentest target: discover enumeration, anonymous login, brute force, file uploads, vsftpd and ProFTPD exploits, detection, and practical hardening.
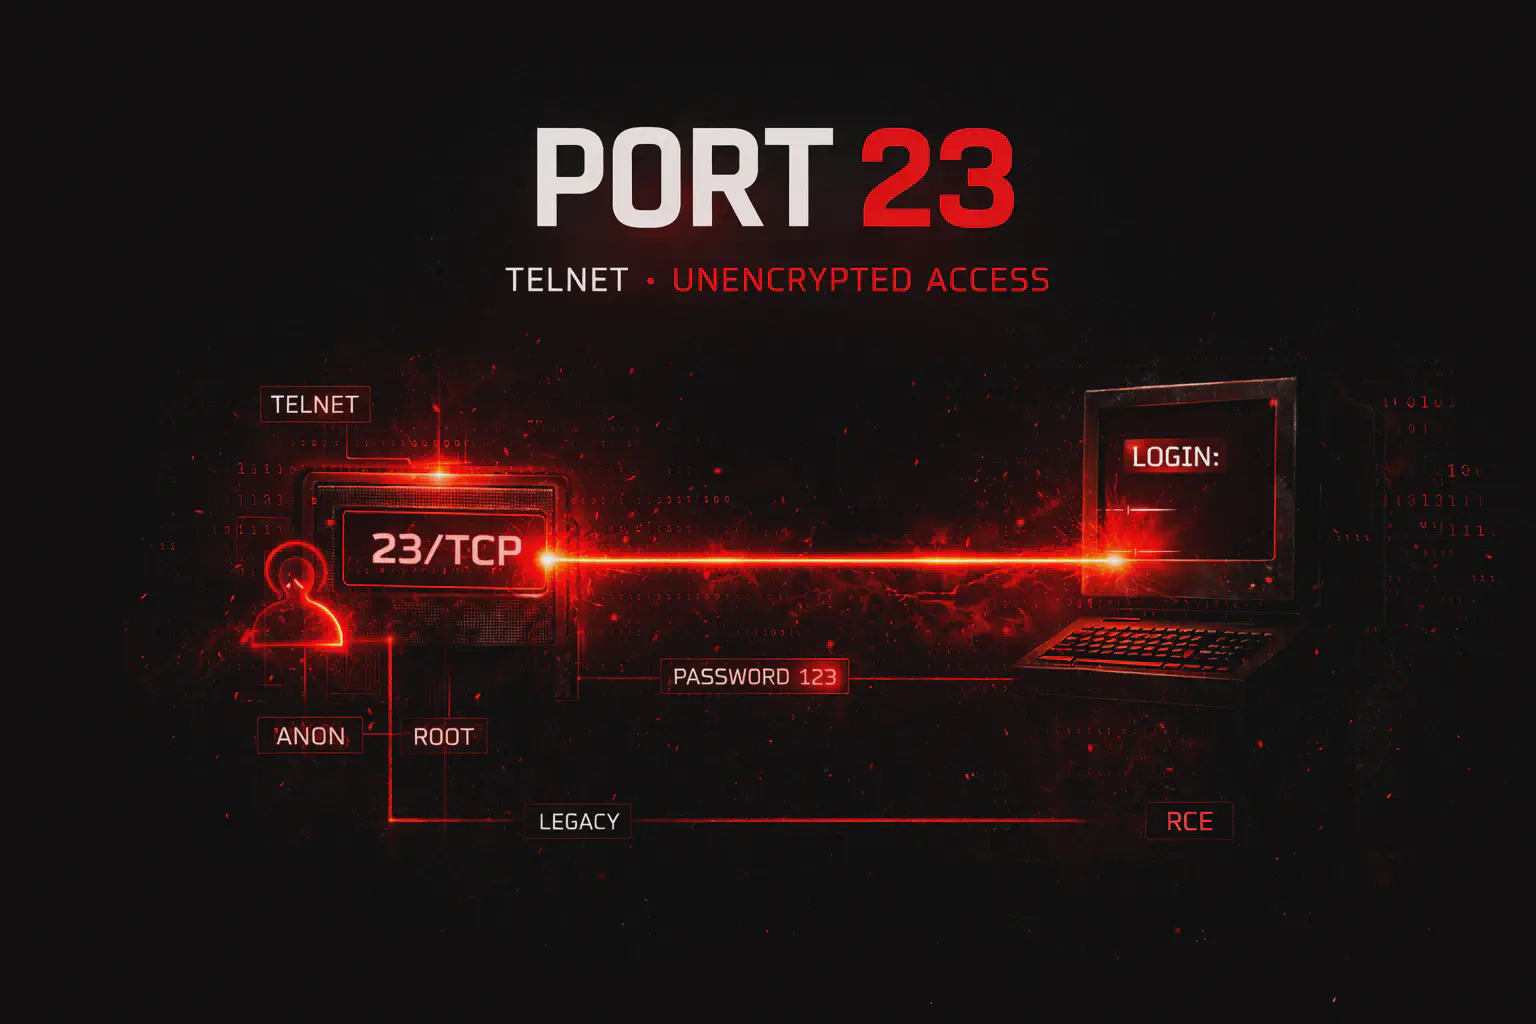
Telnet port 23 is an immediate critical finding: it transmits credentials in clear text, facilitating brute force, sniffing, and insecure remote access. Learn how to enumerate, attack, and secure it.
Learn what port 1025 is in MS RPC, why it correlates with the endpoint mapper on 135, and how dynamic RPC ports depend on the Windows version: 1025-5000 on legacy systems, 49152-65535 from Windows Vista/Server 2008 onwards.
Learn what port 912 is associated with apex-mesh and why it might indicate a remote management platform like MeshCentral: centralized access to endpoints, remote agents, and high-impact surface area for the entire managed network.
Learn what port 990 ftps is, how it relates to port 989 ftps-data, and why anonymous logins, weak credentials, and exposed backups remain the primary risks of TLS-protected file transfers.
Learn what POP3S port 995 is, why POP3 over TLS uses implicit encryption on the email channel, and how weak credentials, mailbox access, and sensitive content still make POP3S a relevant target.
Learn what port 880 is associated with legacy or custom Kerberos admin services, how it relates to kadmin and kpasswd, and why password policies, principals, and KDC configuration are valuable for Kerberos enumeration.
Learn what VMware port 902 is, used in core communications between vCenter Server and ESXi, and why identifying a host with vmware-authd is a high-impact surface for your entire virtual infrastructure.
Learn what ftps-data port 989 is, how it relates to port 990 in implicit FTPS, and why certificates, TLS, and access permissions remain crucial to evaluating file transfer security.
Learn what LDAPS port 636 is, how LDAP over SSL can reveal your hostname, domain, and enterprise CA, and why LDAP signing and channel binding remain crucial for reducing Active Directory relay and exposure.
Learn what Rlogin port 513 is, how .rhosts and hosts.equiv work, why trust can open passwordless logins, and how to identify trust chains and lateral movement on legacy Unix systems.
Learn what RTSP port 554 is, how to detect paths from Hikvision, Dahua, and other vendors, and why CCTV, DVR, and NVR streams with weak or no authentication pose a real risk to video surveillance.
Find out what SMTP Submission port 587 is, how authenticated email sending works according to RFC 6409, and why STARTTLS and SMTP AUTH are crucial for evaluating the security of your email service.
Learn what http-rpc-epmap port 593 is, how ncacn_http works in a Microsoft environment, and why RPC over HTTP can expose endpoints, DCOM services, and useful information about the enterprise RPC surface.
Learn what port 623/UDP asf-rmcp is, how IPMI 2.0 works with RAKP, and why CVE-2013-4786 allows hash recovery from BMC responses, while cipher suite 0 support can drastically reduce remote management security.
Learn what IPP/CUPS port 631 is, how the Internet Printing Protocol over TCP and UDP 631 works, and why the 2024 cups-browsed vulnerability chain brought RCE, printer discovery, and Linux print server security back to the forefront.
Learn what HTTPS port 443 is for, how TLS, certificates, and virtual hosts work, and the risks it introduces, including exposed hostnames in SANs, TLS misconfigurations, sensitive files, admin panels, and web attack surfaces.
Learn what SMTPS port 465 is used for, how SMTP Submission over TLS works, and what risks it introduces, including user enumeration, open relay, brute force SMTP AUTH, and internal phishing with valid credentials.
ISAKMP port 500 in pentest: IPsec VPN enumeration, IKE fingerprinting, Aggressive Mode, PSK hash extraction, offline cracking, and tunneling to internal network.
Rexec Port 512: What it is, how it works, and how to test it in a pentest. Enumeration, cleartext credential sniffing, credential spraying, command execution, and risks of legacy Unix systems.
Learn what syslog port 514/UDP is, how to identify collectors and logging streams, what data can travel in the clear, and why syslog over TLS on 6514 reduces eavesdropping and spoofing.
Learn what LPD port 515 is, how the Line Printer Daemon defined in RFC 1179 works, and why print queues, Unix/Linux print servers, and legacy services can expose sensitive information and overlooked attack surfaces.
Learn what port 520/UDP used by RIP is, how RIPv1 and RIPv2 work, and why route advertisements can expose network topology and increase the risk of route poisoning, traffic redirection, and path manipulation.
Learn what IRC port 194 is for, why many servers use 6667 or 6697, how the protocol works, and the risks it introduces, including user enumeration, channels, internal hostname leaks, and vulnerable daemons.
Learn what SMUX port 199 does, how it connects SNMP subagents and master agents, what risks it introduces when exposed to the network, and how to analyze registrations, OIDs, and misconfigurations in legacy systems.
A practical guide to FTP (File Transfer Protocol) ports 20 and 21: the difference between control and data channels, active/passive mode, sniffing risks, FTP bounces, and common vulnerabilities in legacy servers and labs.
Learn what the SNMP Trap port 162 is used for, how the notification channel works compared to port 161, what risks it introduces with SNMPv1/v2c, and how to exploit it for reconnaissance, sniffing, and passive intelligence gathering.
Learn what BGP port 179 is used for, how Autonomous System peering works, what risks a misconfigured session introduces, and how to analyze enumeration, route injection, and hijacking in an authorized pentest/CTF.
Learn what Squid port 3128 is used for, how an HTTP/HTTPS forward proxy works, the risks a misconfigured open proxy introduces, and how to exploit or defend against it in pivoting, access to internal services, and ACL control.
Learn what RDP port 3389 is used for, how Remote Desktop, NLA, and CredSSP work, what risks service exposure introduces, and how to attack or defend against brute force, BlueKeep, and lateral movement.
Network Sniffing: How to Capture Traffic, Credentials, and Packet Data in Pentests
How VPNs work and what they are at a technical level: IPSec, OpenVPN, WireGuard, L2TP, and PPTP. Tunnel architecture, real-world attacks, misconfigurations, and pentest analysis.
Complete guide to Blind XSS: out-of-band detection, server callbacks, XSS Hunter, stealth payloads, admin injection points, and internal panel trigger analysis.
Learn how STP and RSTP work, what the Root Bridge, Spanning Tree Protocol, and how BPDU election occurs, and what real risks exist in pentesting: takeover, TCN floods, and layer 2 attacks.
Complete guide to TCP: three-way handshake, flags, sequence number, windowing, port scanning with Nmap, session hijacking, SYN flood and traffic analysis.
TLS/SSL Pentesting Guide 2026: Handshakes, Weak Cipher Suites, ECH, Post-Quantum, Heartbleed, POODLE, and 15+ Vulnerabilities to Test with testssl.sh.
Learn how VLANs and 802.1Q work, the difference between access and trunk, native VLANs, inter-VLAN routing, DTP, double tagging, and VLAN hopping techniques in pentests.
Learn how VRRP, HSRP, and CARP work, how gateway failover occurs, and why takeover, priority abuse, and MITM are real risks in network pentesting.
The Complete Guide to 802.11 Wi-Fi: Wireless Frames, Monitor Mode, WPA2/WPA3, Four-Way Handshake, PMKID, Deauthentication, Evil Twin, and Real-World Pentesting Risks.
PPP Explained Well: How the Point-to-Point Protocol Works, the Differences Between PAP and CHAP, PPPoE, PPTP, MS-CHAPv2, Real-World Attacks, and Their Impact on Modern Pentesting.
QUIC explained clearly: what it is, how it works with HTTP/3, 0-RTT risks, UDP 443 inspection gap, logging bypass, and real-world implications for pentesting.
SCTP What is it: how it works, four-way handshake, multi-streaming, multi-homing, scanning with Nmap, risks on SIGTRAN, Diameter and 4G/5G networks.
SNMP: what it is, how it works, OID, public/private community string, snmpwalk, brute force, write access, and real risks in an enterprise pentest.
UDP explained clearly: headers, differences with TCP, UDP scanning with Nmap, critical services like DNS, SNMP and NTP, amplification attacks and real risks in pentesting.
Learn what GRE is, how Generic Routing Encapsulation tunneling works, why it's risky in enterprise environments, and how to exploit or defend against it in a pentest.
Learn how IPSec works and why it is crucial in enterprise VPN pentesting: IKEv1/IKEv2, ESP, tunnel mode, aggressive mode, weak PSK, ike-scan, and defenses.
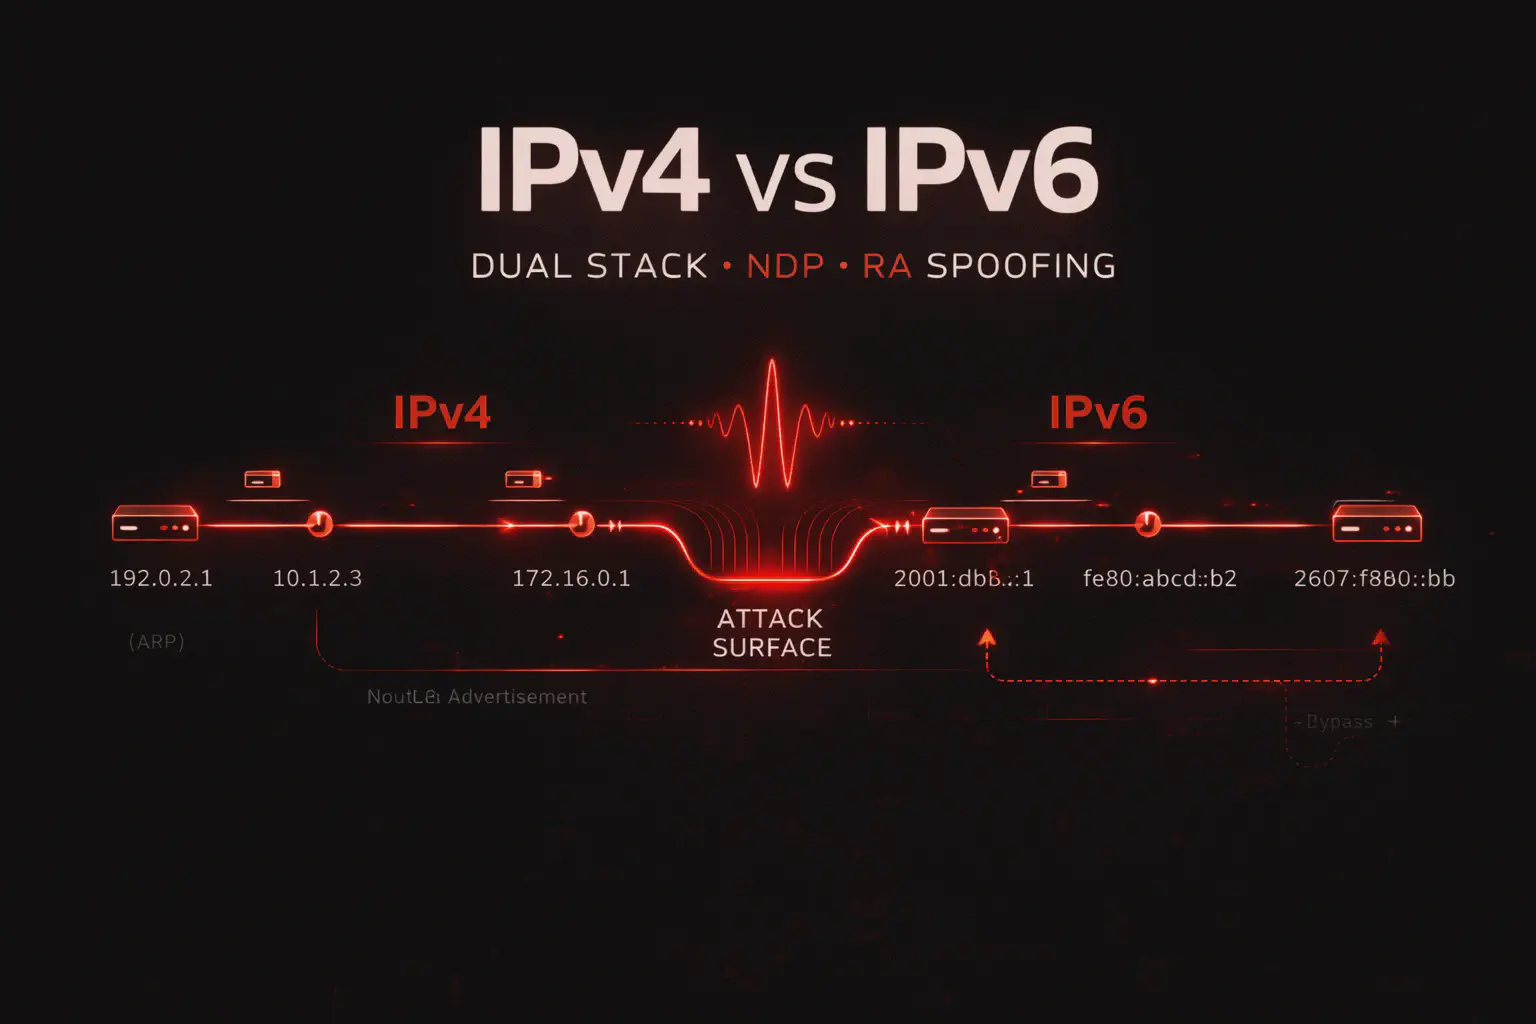
Learn the differences between IPv4 and IPv6 and why they matter in pentesting: SLAAC, NDP, RA spoofing, IPv6 scanning, dual-stack, control bypass, and defenses.
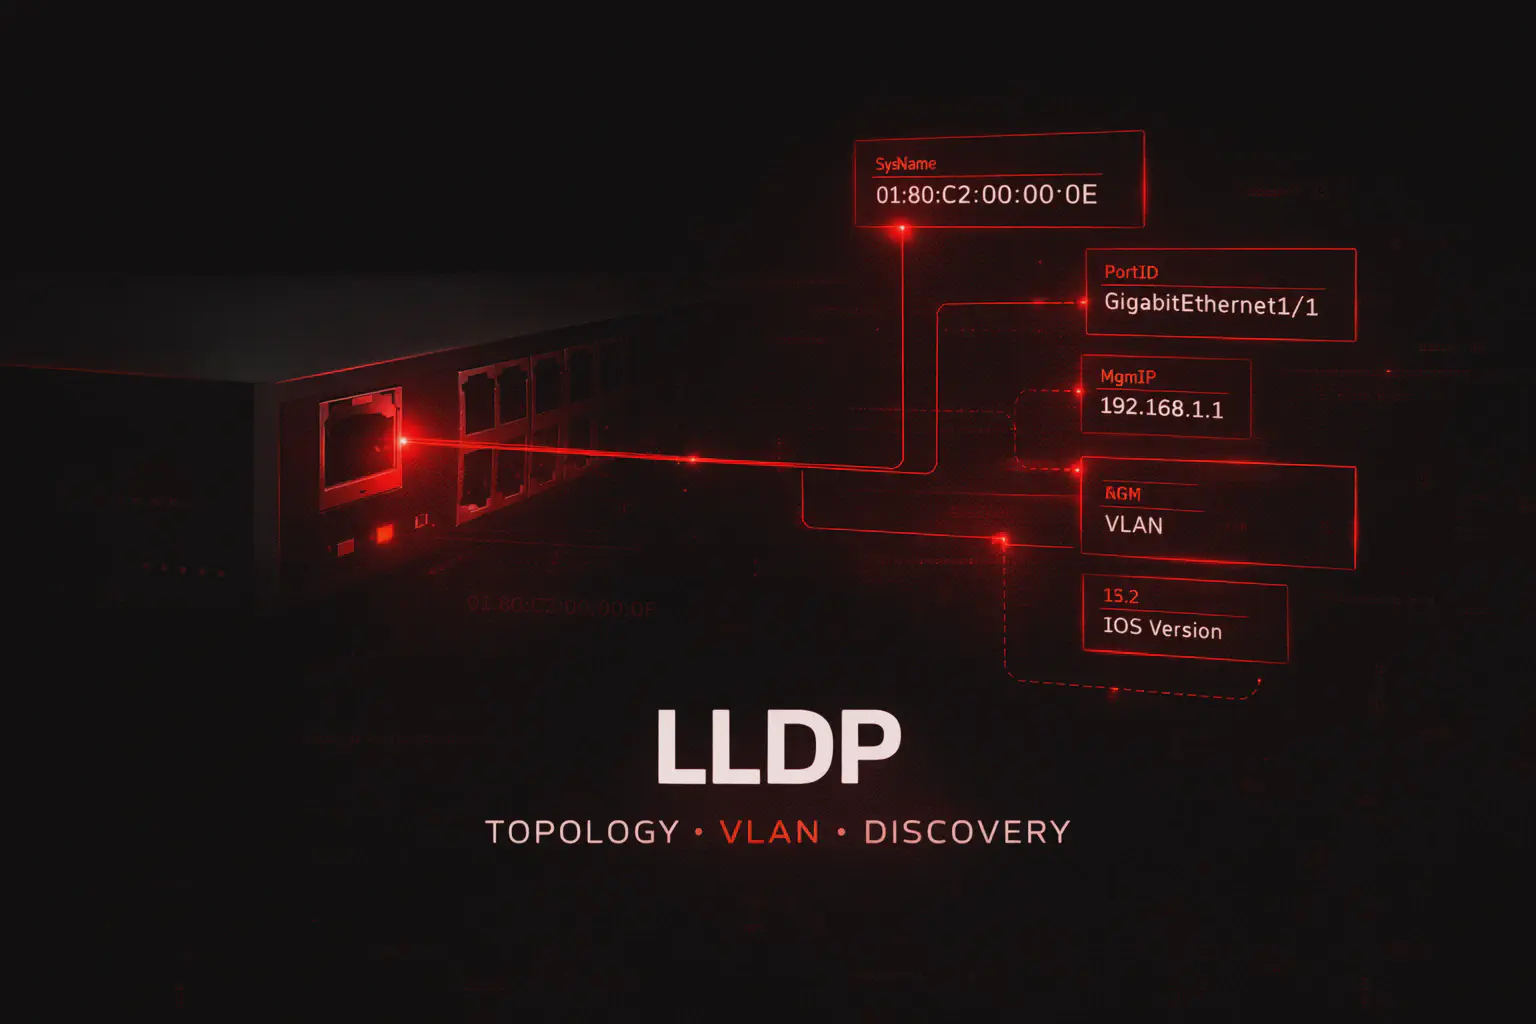
Learn what LLDP is, how it works, and why it's useful in pentesting: passive discovery, neighbor tables, VLANs, IP management, LLDP-MED, spoofing, and defenses.
Learn what NTP is, how it works, and why it's critical in pentesting: monlists, DDoS amplification, rogue NTP servers, time skew, Kerberos, TLS, logs, and defenses.
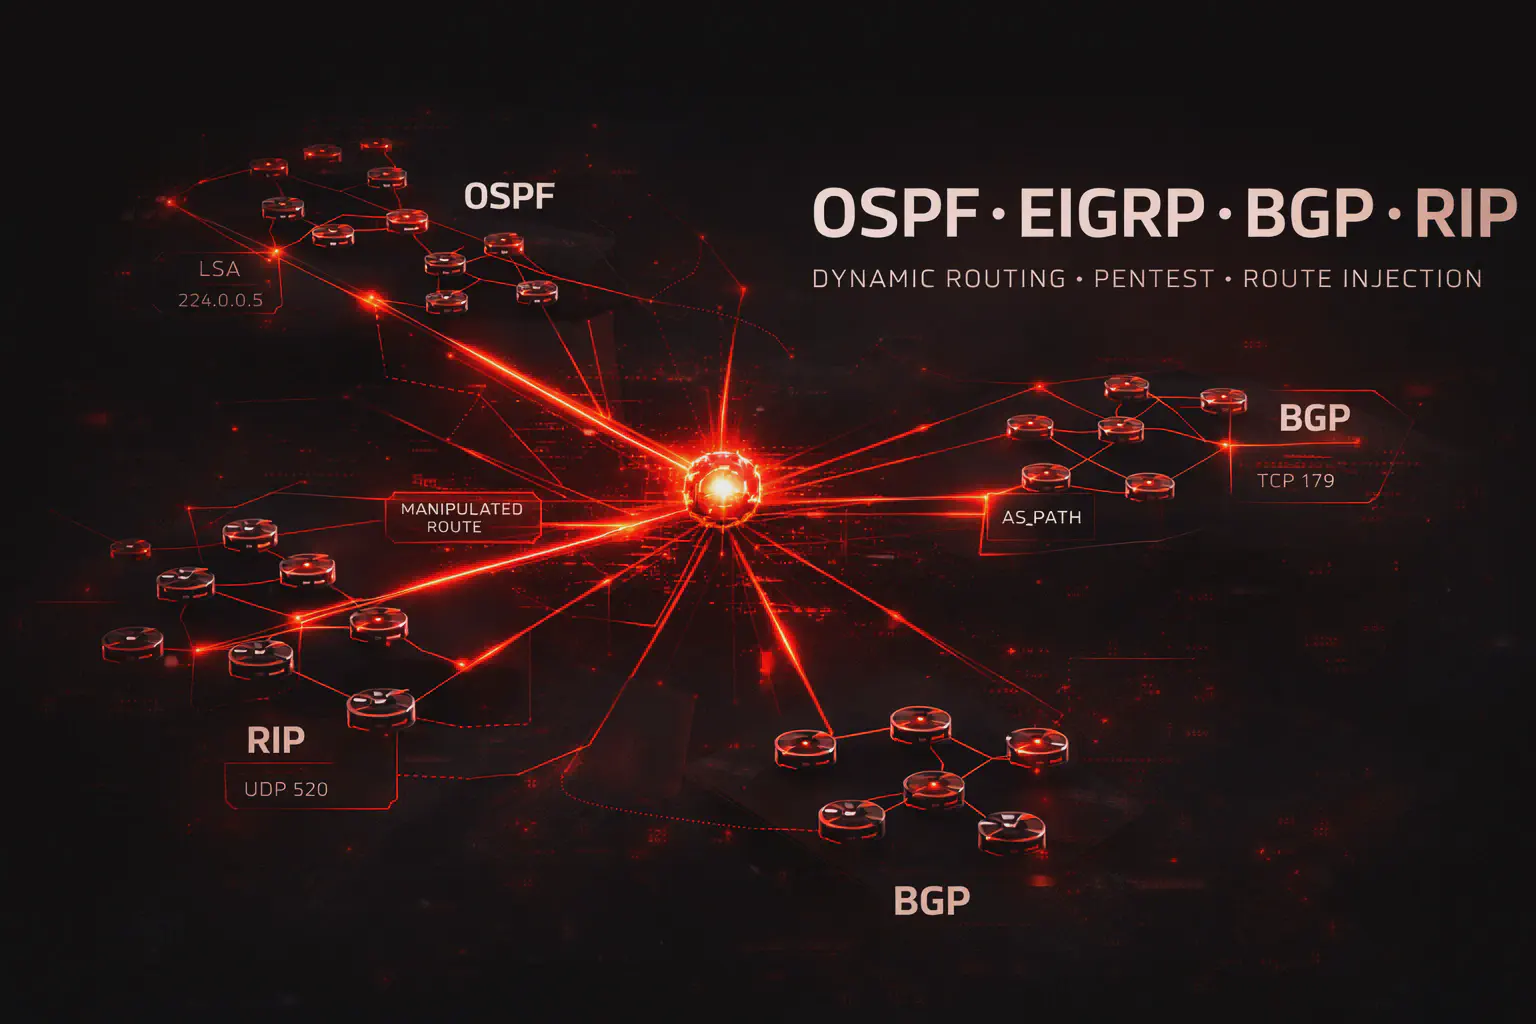
A complete guide to OSPF, EIGRP, BGP, and RIP: how they work, their differences, route injection, BGP hijacking, fake LSAs, MITMs, and defenses for dynamic routing protocols.
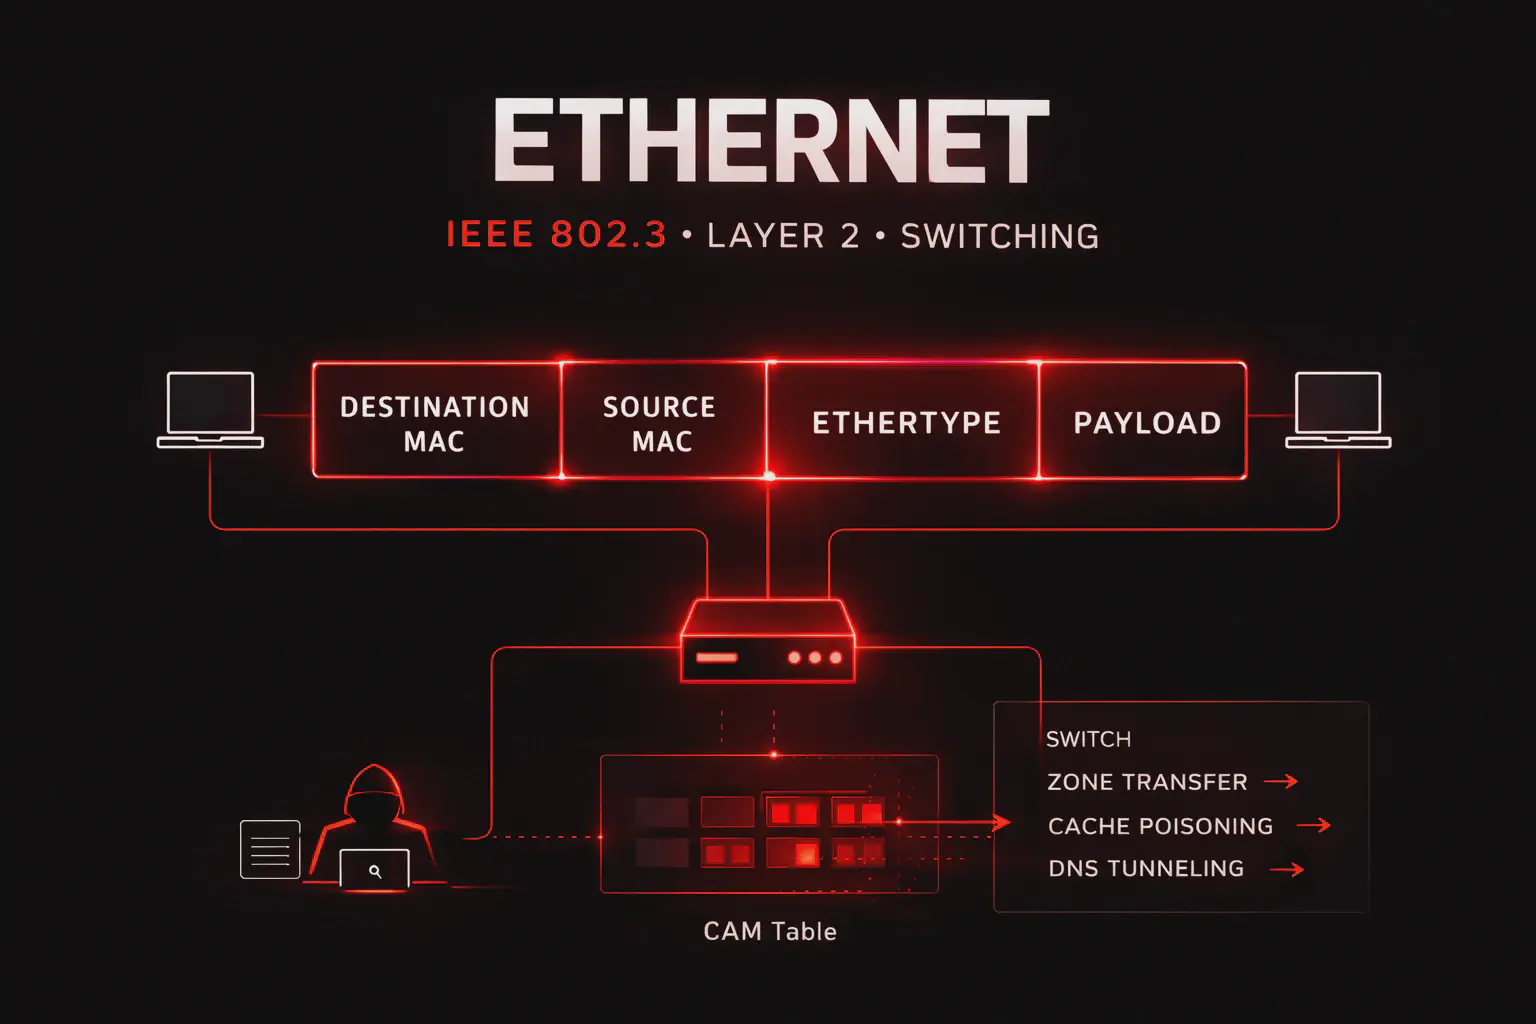
Learn what Ethernet is, how an 802.3 frame works, and why it's essential in pentesting: MAC address, switches, CAM table overflow, sniffing, spoofing, and defenses.
Learn what HTTP is, how HTTPS works, and why it's essential in web pentesting: methods, headers, cookies, status codes, fingerprinting, enumeration, and real-world attacks.
Learn what ICMP is, how ping and traceroute work, and why it's crucial in pentesting: host discovery, ICMP tunneling, redirection, fingerprinting, detection, and defenses.
Learn what IGMP is, how multicast works, and why it's useful in pentesting: host discovery, membership reporting, IGMP snooping, reconnaissance, DoS, and security.
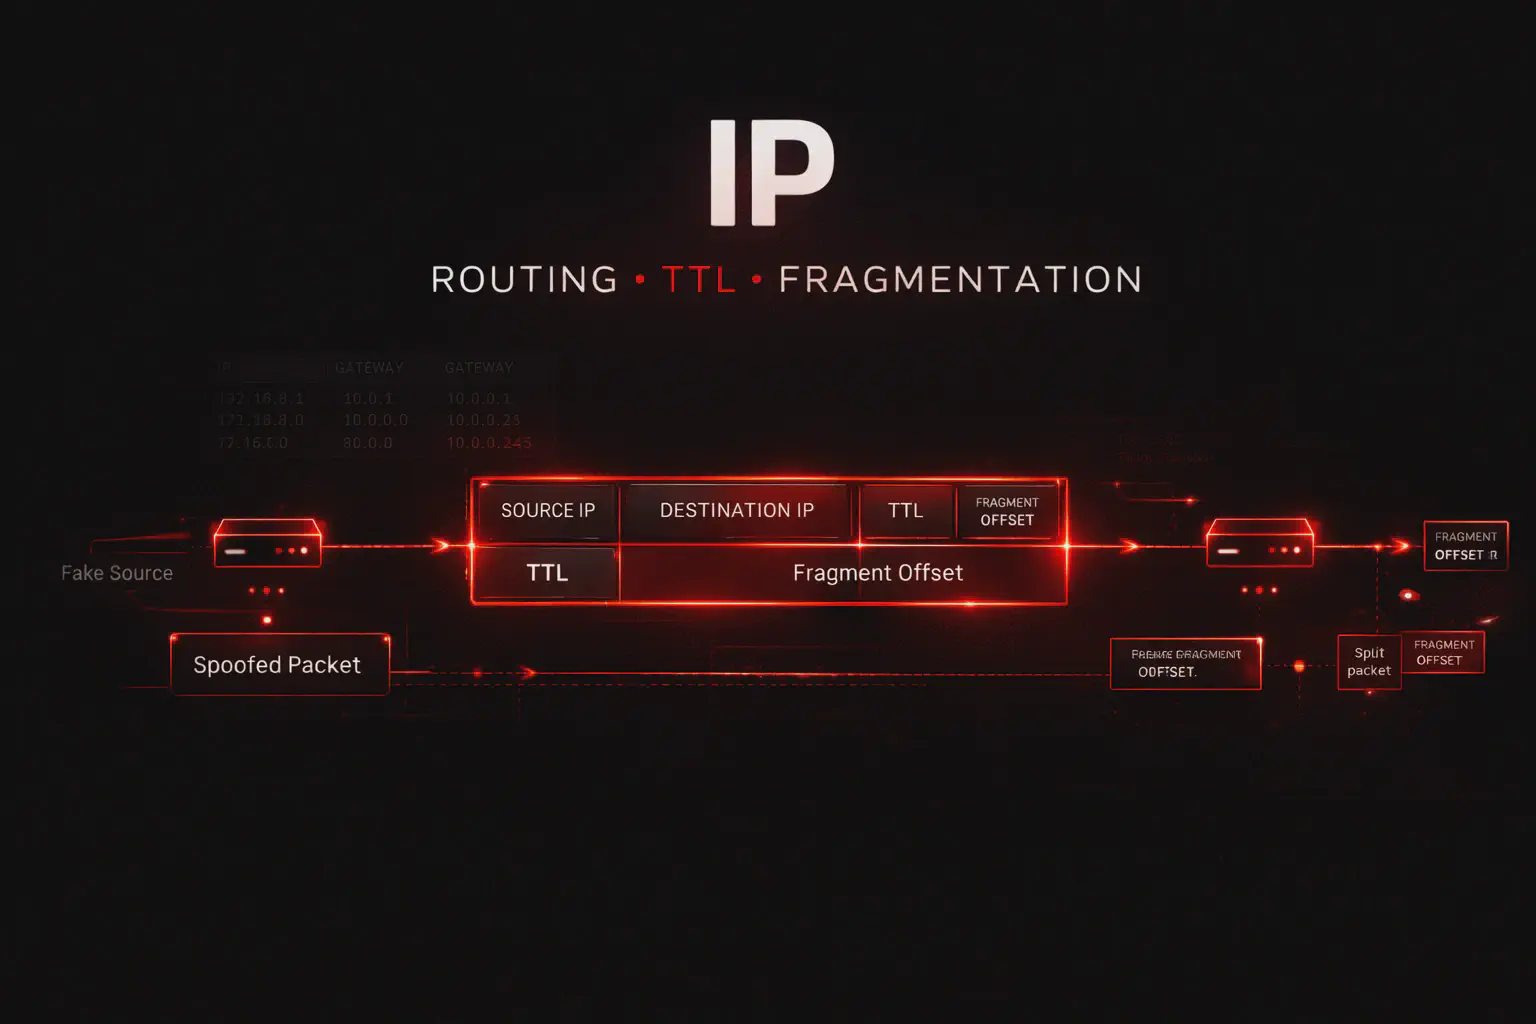
Learn what IP is, how headers, TTLs, routing, and fragmentation work, and why it's essential in pentesting: IP spoofing, evasion, reconnaissance, and defenses.
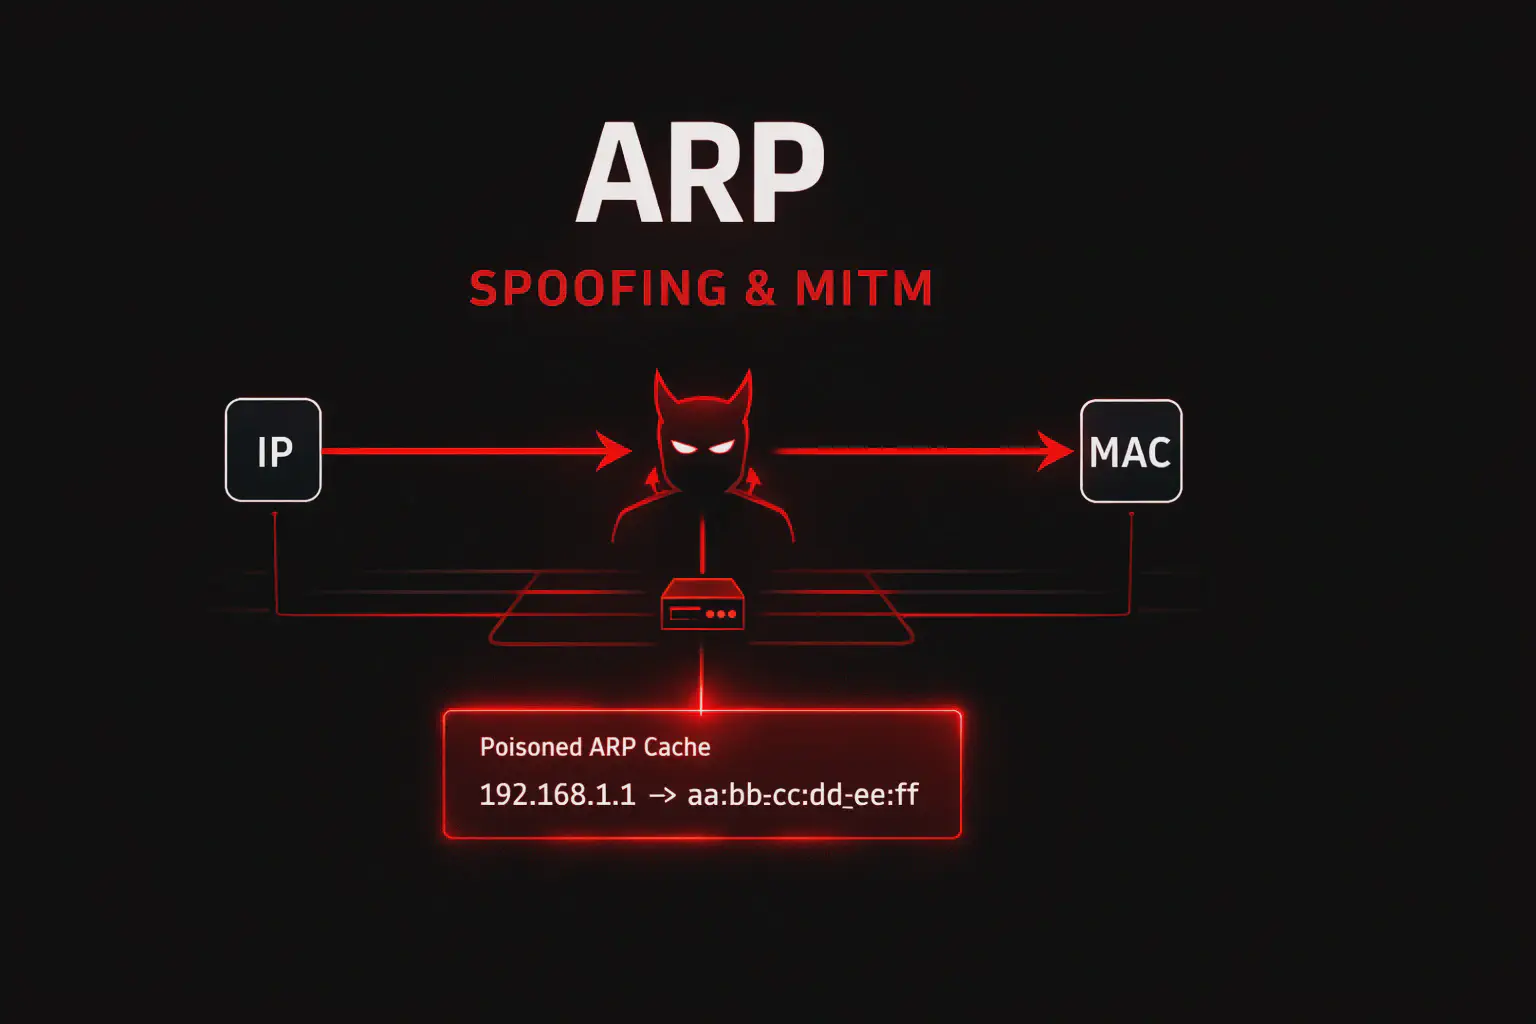
Learn what ARP is, how it actually works, and how it's exploited in pentesting: ARP cache, gratuitous ARP, spoofing, MITM, detection, defenses, and practical tools.
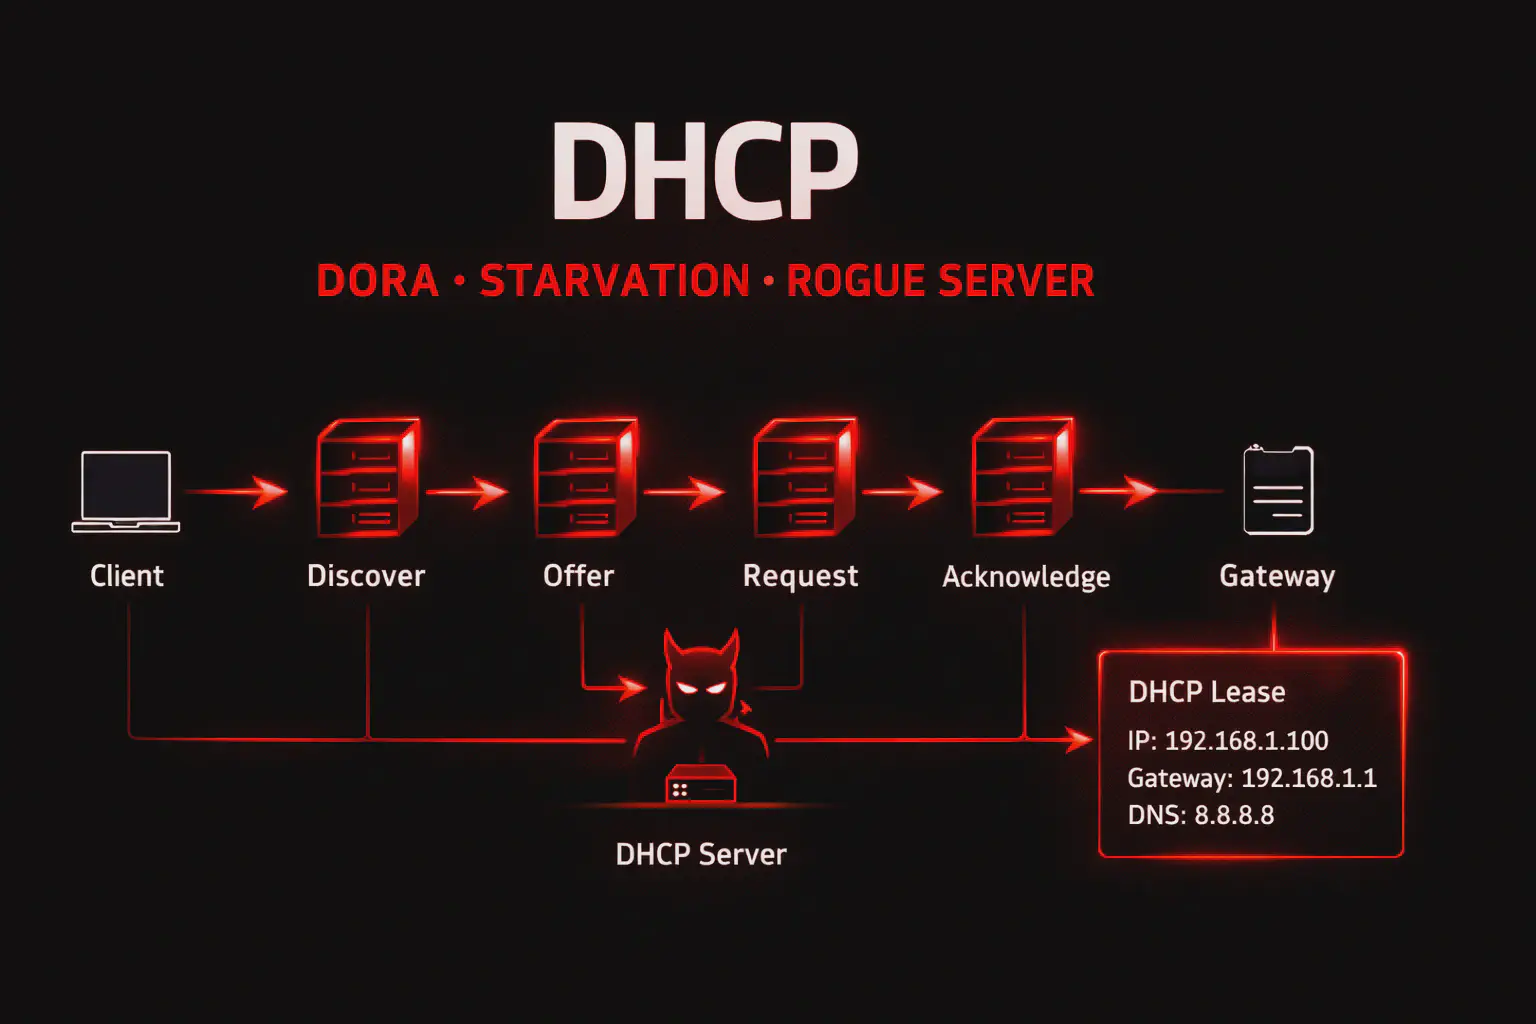
Learn what DHCP is, how the DORA process works, and how to exploit it in a pentest: starvation, rogue DHCP servers, WPAD injection, option 121, and real-world defenses.
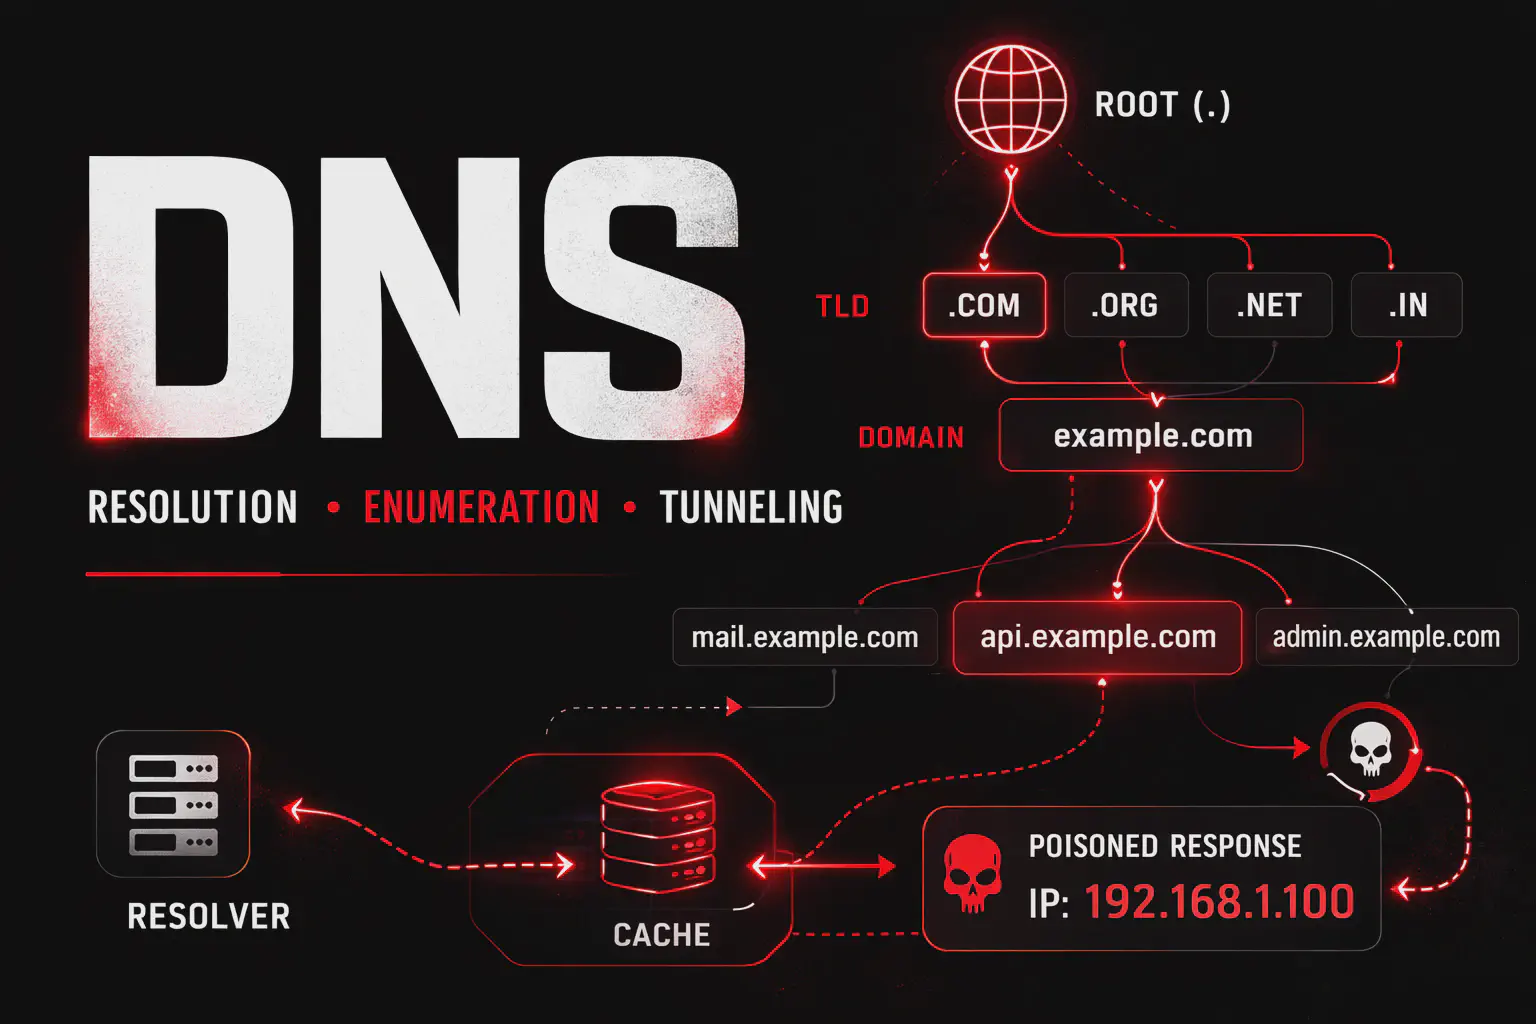
Learn what DNS is, how name resolution works, and how to leverage it in a pentest: zone transfer, subdomain enumeration, cache poisoning, tunneling, and defenses.
Learn about SSH port 22, one of the most common pentest targets: discover enumeration, brute force, user enumeration, stolen keys, SSH tunneling, and effective hardening of the Secure Shell protocol.
Port 8080 often hosts Apache Tomcat and Jenkins, two key targets in web pentesting. Learn about enumeration, Tomcat Manager, Jenkins RCE, and the most useful tests for the most critical web vulnerabilities.
Port 5985 exposes WinRM over HTTP, the Microsoft service used by PowerShell Remoting. Learn about enumeration, access with Evil-WinRM, Pass-the-Hash, lateral movement, and hardening in Active Directory environments.
MySQL port 3306: a practical pentest guide with brute force credentials, database dumps, LOAD_FILE, webshell via INTO OUTFILE, UDF for RCE, and escalation techniques.
Socat for advanced networking: relay, port forwarding, reverse shell, and encrypted tunnels. The Swiss Army Knife for network connections in pentesting.
Shodan: Practical dorks for MongoDB, IoT, ICS and CVE, advanced filters, CLI, API, InternetDB and complete cheat sheet for passive reconnaissance and pentesting (2026).
RSH: Clear Text Remote Shell on Unix Systems
RevSocks creates a reverse SOCKS proxy between the attacker and the compromised target, allowing pivoting and access to internal networks in authorized pentests.
NBTSscan is a lightweight NetBIOS enumeration tool for Windows networks. It identifies hostnames, domains, and MAC addresses via NetBIOS queries.
ProxyChains: A practical guide to anonymizing traffic and chaining proxies in penetration testing. Configuration, SOCKS5, and tool integration.
SSHuttle: A complete guide to creating VPNs over SSH for penetration testing. Pivoting, tunneling, and accessing internal networks without configuration.
Pentest Rsync on port 873: enumerates rsyncd and modules, verifies anonymous and write access, analyzes exposed files and possible attack paths.
Learn how to exploit Telnet on port 23 during a pentest: enumeration, banner grabbing, credentials, privilege escalation, pivoting, and lateral movement.
Latest CVE

CVE-2026-20079: Critical authentication bypass (CVSS 10.0) in Cisco Secure FMC, KEV CISA, and exploited by Sandworm and Qilin. Root cause, IOC, remediation.
CVE-2026-82329: Authentication bypass in JFrog Artifactory via empty join key. Root cause, exploit chain, working PoC, detection, and remediation.
CVE-2026-31431 Technical Analysis: How the algif_aead bug works, AF_ALG + splice() chain, practical step-by-step PoC. Every Linux since 2017 is vulnerable.
noPac on Active Directory: Exploits CVE-2021-42278 and CVE-2021-42287 to impersonate a Domain Controller, perform DCSync, and gain Domain Admin
Latest Walkthroughs

Walkthrough of Hack The Box Monitors: SQLi in Cacti (CVE-2020-14295), deserialization in OFBiz (CVE-2020-9496), and container escape via kernel module.
Hack The Box Sink write-up: HTTP Request Smuggling, CVE-2019-18277, HAProxy, Gunicorn, Gitea, Ligolo-ng, AWS LocalStack, KMS, and Secrets Manager.
Hack The Box Schooled Write-Up: from Stored XSS on Moodle to webshell, MySQL credentials and privilege escalation to root on FreeBSD via pkg.
Full HTB Mango walkthrough: NoSQL injection login bypass on MongoDB, credential extraction with $regex, and privilege escalation via SUID on jjs.
Hack The Box Unattended full writeup: NGINX alias bug, double SQL injection, LFI, session poisoning, cron poisoning and privilege escalation to root.
Write-Up of TryHackMe's Bolt machine: enumeration, credential discovery, RCE authenticated to Bolt CMS via session hijacking and privesc to root.
Complete Hack The Box: Help write-up. GraphQL enumeration, bypass file upload to HelpDeskZ with vulnerable PHP code analysis, privesc kernel to root.
Hack The Box's Falafel Machine Write-Up: User Enumeration, Blind SQL Injection, PHP Login Bypass, RCE Upload, and Linux Privilege Escalation.
Hack The Box Shibuya Write-up: Enumerate users via Kerberos, extract NTLM hashes from WIM backups, and leverage RemotePotato0 and ADCS ESC1 up to Domain Admin.
Complete WriteUp of Hack The Box Redelegate: Anonymous FTP, KeePass, MSSQL, ForceChangePassword, SeEnableDelegationPrivilege, S4U, DCSync and Domain Admin.
Hack The Box Giddy full write-up: SQL Injection, NTLMv2 hash capture, WinRM access, AV Bypass and privilege escalation to SYSTEM via CVE-2016-6914.
Write-Up HTB Love, Easy VM: SQLi time-based, NTLM attempt on Responder, SSRF towards 5000, and privesc with AlwaysInstallElevated. Every dead end explained.
WriteUp Hack The Bpx Eighteen: MSSQL impersonation, cracking hash Werkzeug PBKDF2, privilege escalation with BadSuccessor (CVE-2025-53779) on Windows Server 2025
Voleur's full walkthrough of Hack The Box: targeted Kerberoasting, AD Recycle Bin abuse, DPAPI chaining, and privilege escalation via WSL to Administrator.
Complete WriteUp at Hack The Box Scepter: NFS, PFX/PEM certificates, ADCS ESC9, ESC14, altSecurityIdentities and final DCSync.
Complete walkthrough of Hack The Box Anubis (Insane, Windows): ASP SSTI for shell in Docker, CVE-2021-28079 on Jamovi for foothold on host, and privilege escalation via ADCS ESC4 with GenericAll on certificate template.
HTB Haze Writeup: CVE-2024-36991 on Splunk, credential decryption with splunksecrets, GMSA abuse, Shadow Credentials on AD and RCE up to SYSTEM.
Complete writeup of HTB Search: foothold via credentials in an image, Kerberoasting, GMSA abuse, and two distinct paths to Domain Admin.
HTB Scrambled Writeup: Kerberoasting, Silver Ticket on MSSQL and RCE via BinaryFormatter insecure deserialization. Static analysis with dnSpy and ysoserial.net
HTB Sekhmet Insane,WriteUp Complete: insecure deserialization in node-serialize, bypass ModSecurity with Unicode encoding, ZipCrypto, Kerberos on Linux and DPAPI on Active Directory.
HTB ProLab Dante review: lab structure, strengths of pivoting, real-world issues with older OSes and unintended CVEs. Who really needs it and when to skip it.
HTB Hathor Walkthrough: AppLocker Bypass, DLL Hijacking over SMB, Code Signing with a Stolen Certificate, and DCSync Without NTLM. Insane Windows Machine
Walkthrough Osaka – OffSec Proving Grounds: format string → ASLR bypass, ROP chain with VirtualAlloc → DEP bypass, shellcode and SeDebugPrivilege → SYSTEM.
Latest Tools
OpenSSL for TLS, X.509, RSA, and ECDSA certificates, PKI, s_client, and encryption. Practical commands for Linux, Windows, troubleshooting, and pentesting.
Discover Dradis Framework: import findings from Nessus, Nmap, and Burp, organize evidence, and generate consistent pentest reports. A practical guide.
What is JTAG and how does it work? Learn about pins, JTAGulator, OpenOCD, firmware dumps, and the risks of an exposed JTAG interface in hardware pentesting.
Nessus Guide: Installation, Nessus Essentials, vulnerability scans, credentialed scans, policies, tuning, and reporting. The complete vulnerability assessment workflow.
Configure Sliver C2 for Red Team: installation, mTLS/HTTP/DNS listener, implant, beacons and sessions, Armory, BOF, pivoting, OPSEC, detection and cleanup.
Learn how Cobalt Strike works in the Red Team: Team Server architecture, Beacon, listener, Malleable C2, post-exploitation and main detection techniques.
Use DirBuster on Kali to find hidden directories and files: GUI and headless configuration, wordlist, recursion, soft-404, and comparison with ffuf and feroxbuster.
Use ngrok in penetration testing to create TCP/HTTPS tunnels behind NATs and firewalls, receive reverse shells with Netcat or Metasploit, and evaluate OPSEC limits.
Practical guide to XSSer for testing XSS vulnerabilities: installation, GET/POST scanning, payload, fuzzing, encoding, WAF bypass and results reporting.
A practical guide to WPScan for WordPress pentesting: installation, scanning, plugin, theme, and user enumeration, vulnerabilities, API tokens, and brute force.
Guide to impacket-renameMachine to change the sAMAccountName of account computers and understand the NoPac chain with CVE-2021-42278 and CVE-2021-42287.
Impacket-ticketer guide to forge Golden and Silver Kerberos Tickets with NTLM hashes or AES keys, customize PAC, and save ticket ccache.
A guide to impacket-smbserver for creating an SMB share on Kali, transferring files, registering NTLM authentication, and managing SMB2, logins, and logging.
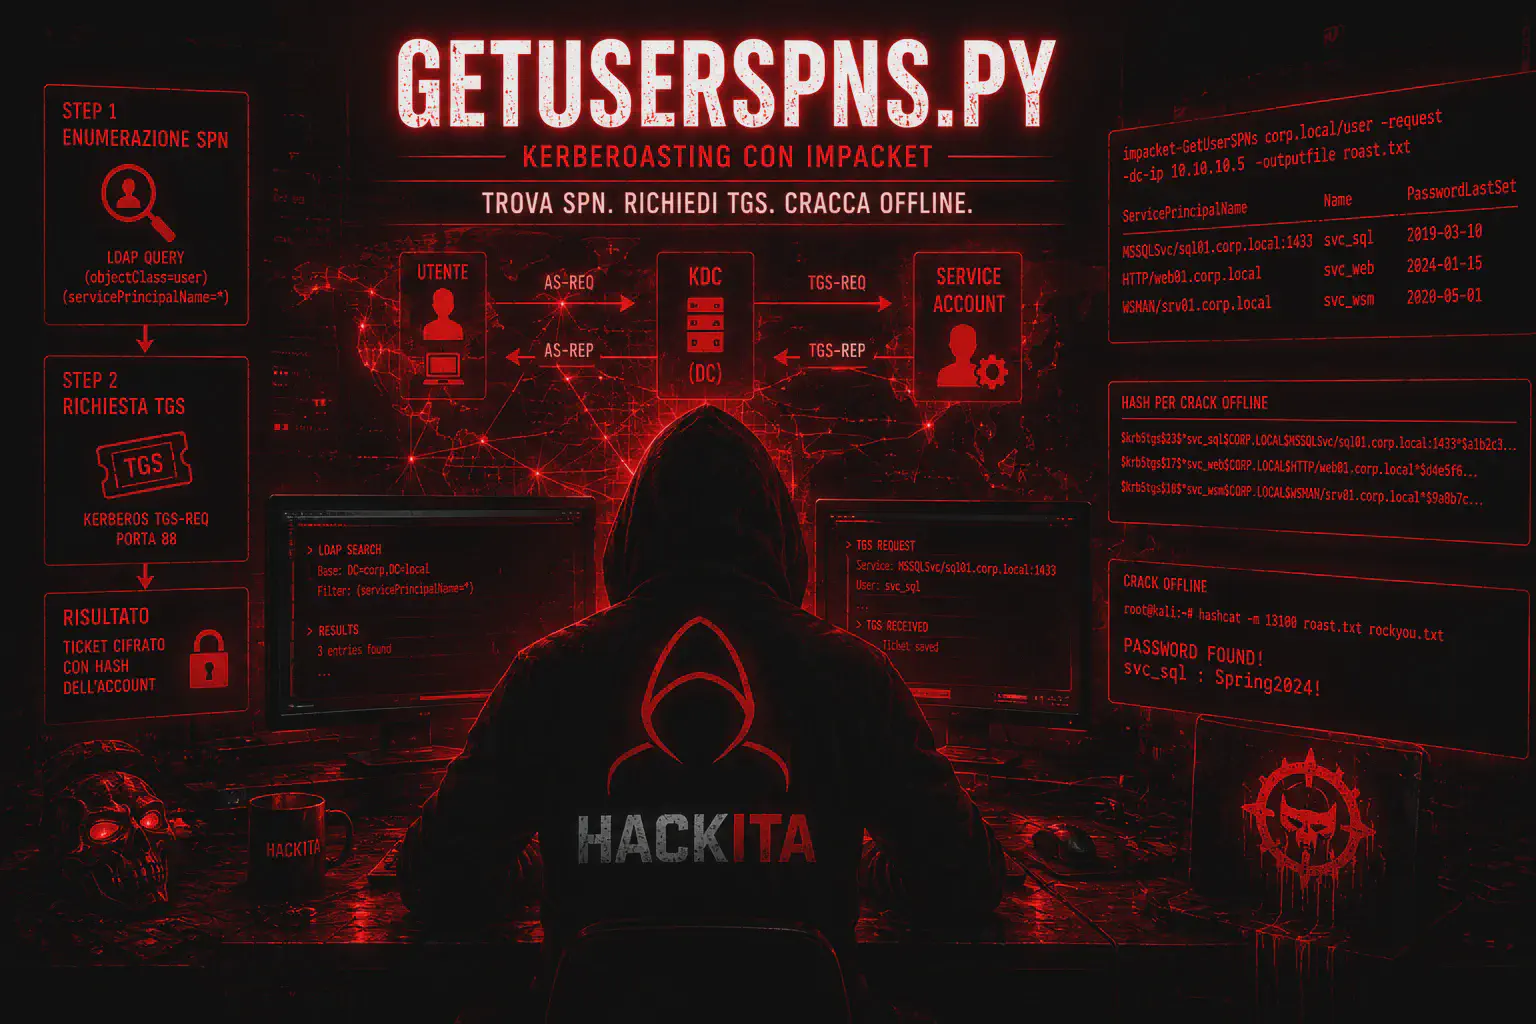
How to use impacket-GetUserSPNs to enumerate accounts with SPNs and request Kerberos TGS with passwords, NTLM hashes, caches, or AES keys for Windows Active Directory
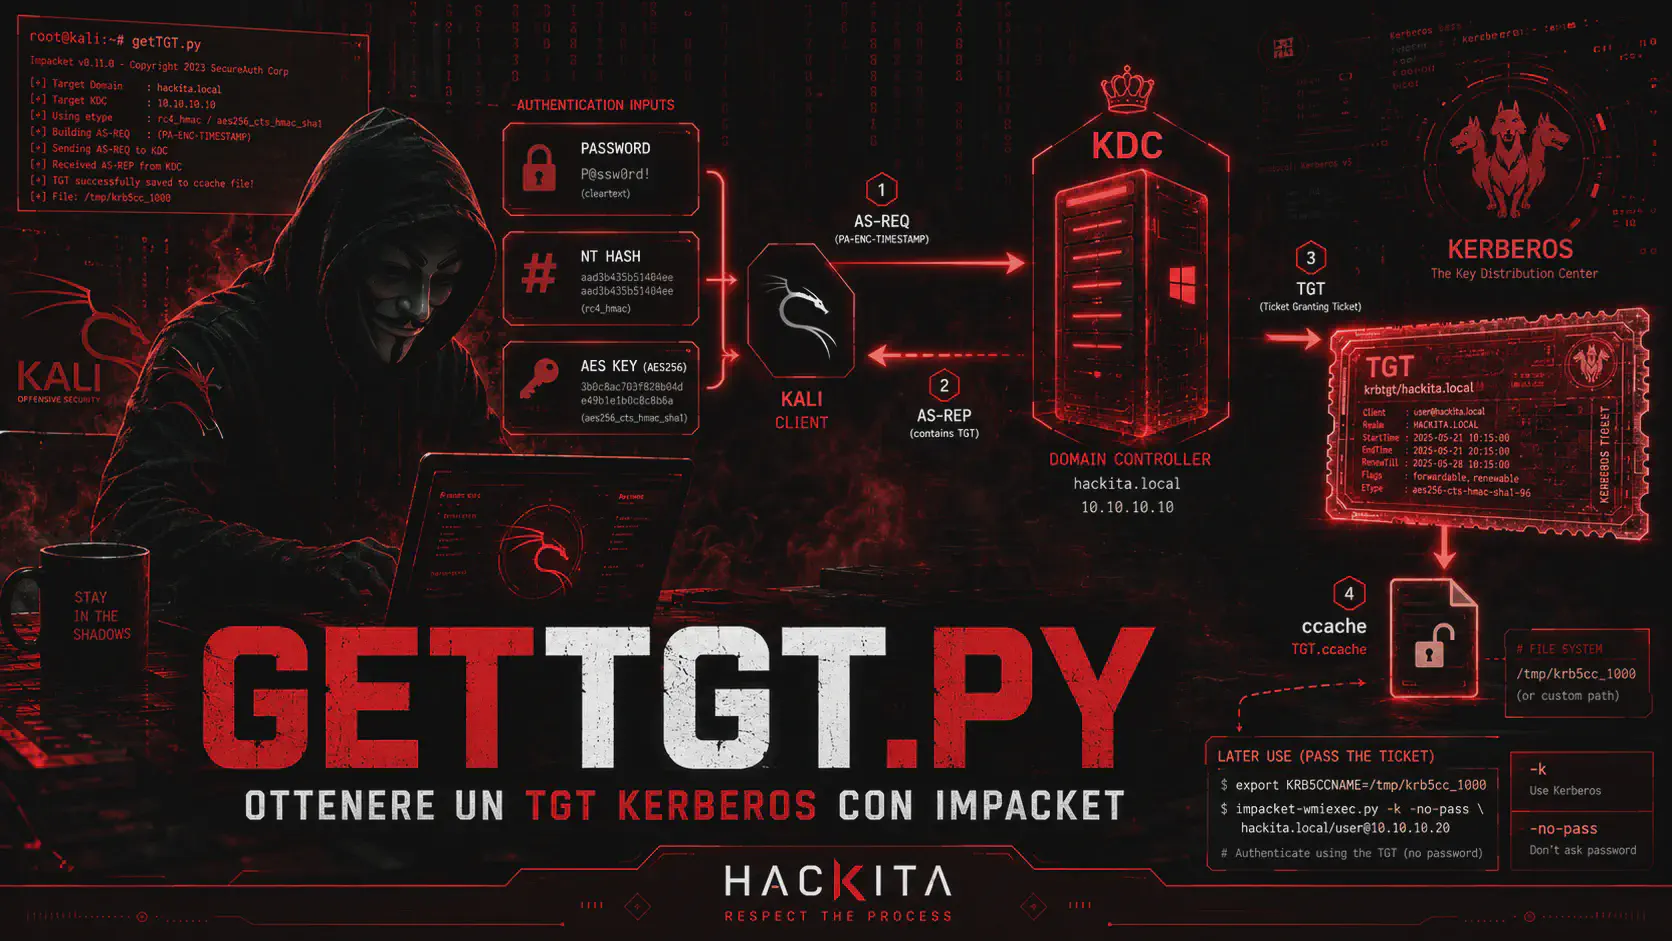
How to use impacket-getTGT to request a Kerberos TGT and save it in ccache format using a password, NTLM hash, or AES key in Active Directory.
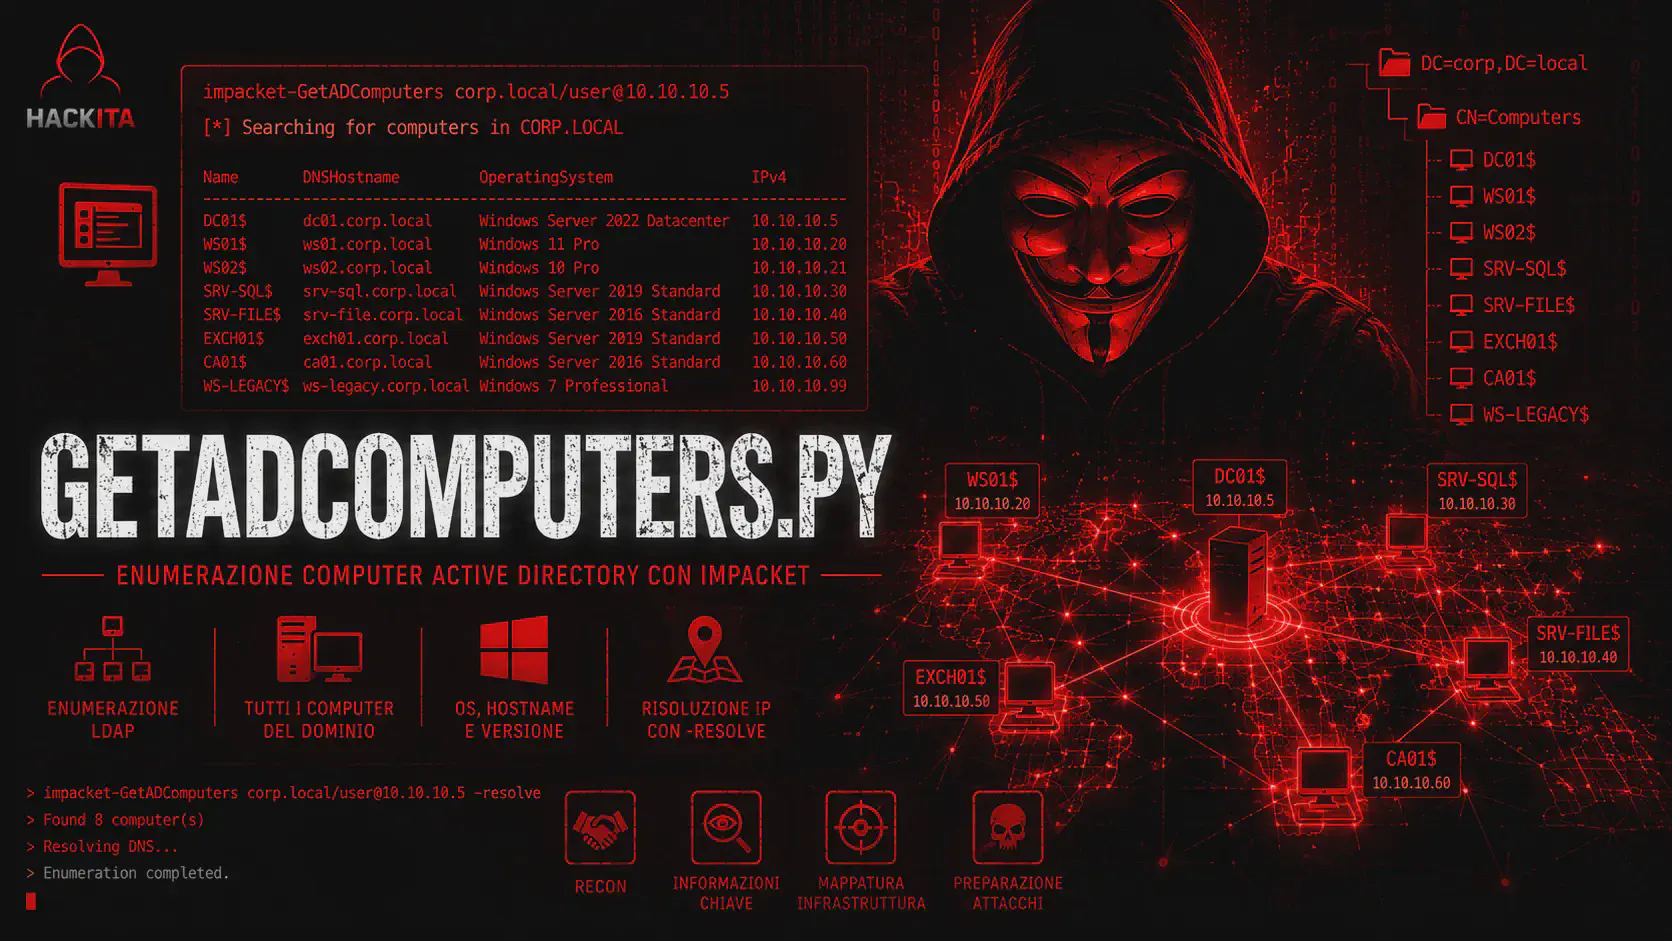
How to use impacket-GetADComputers to enumerate Active Directory computers via LDAP, -resolveIP ,auth with password, NTLM hash, Kerberos, ccache or AES keys.
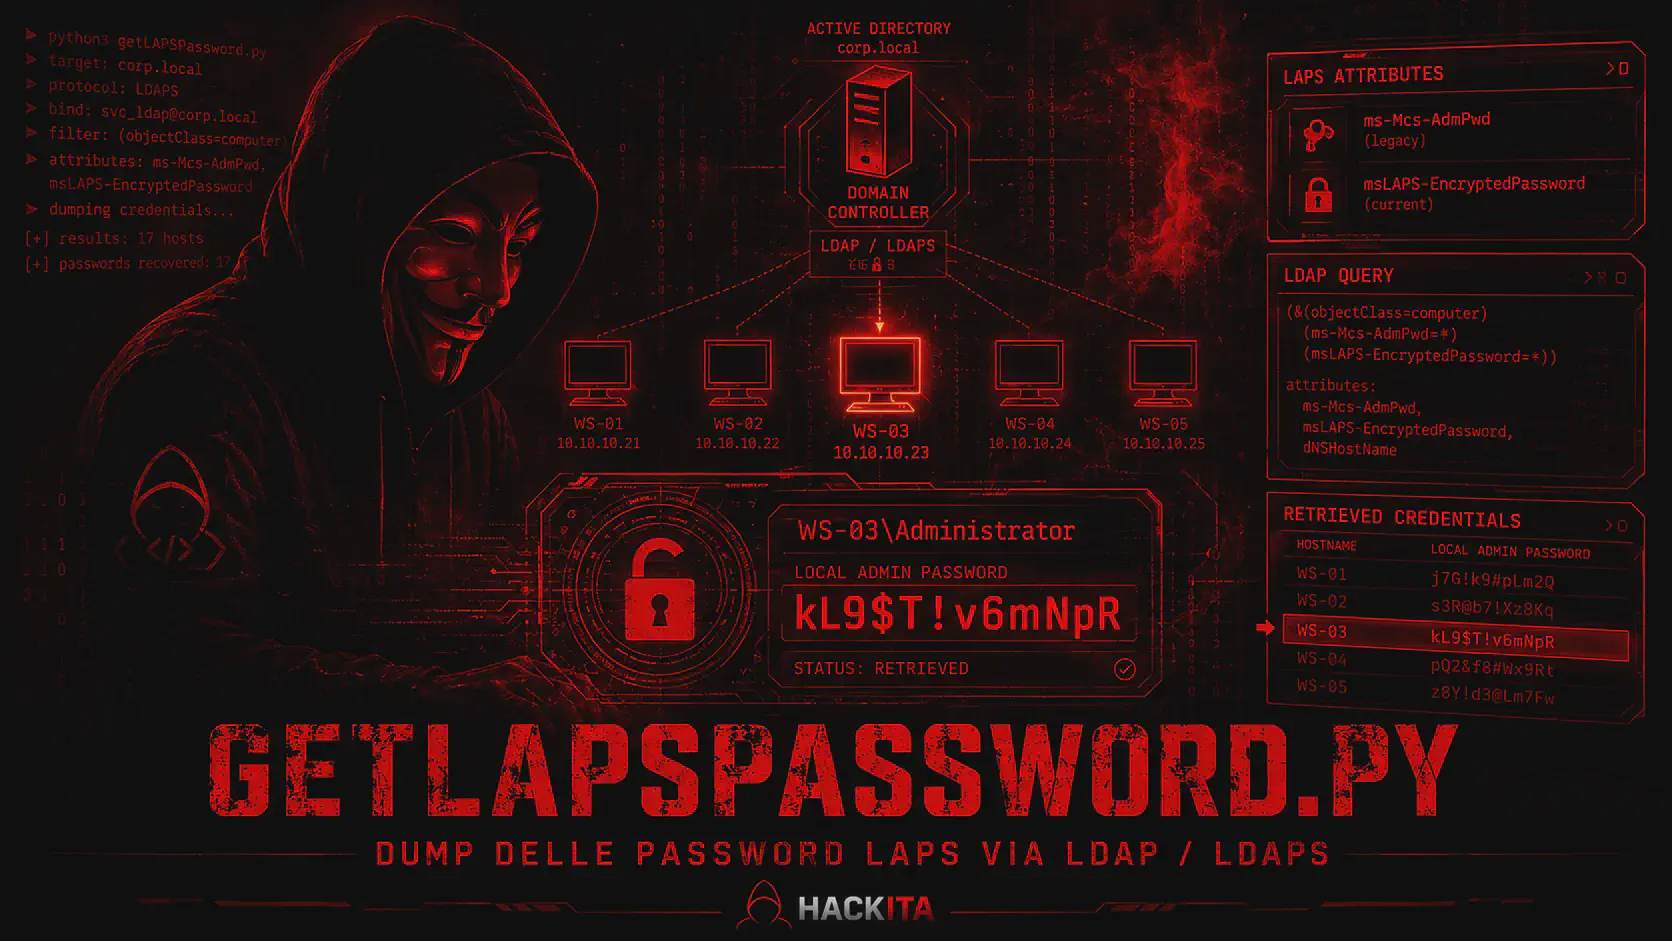
Impacket's GetLAPSPassword.py guide for recovering encrypted Legacy LAPS and Windows LAPS passwords from Active Directory with passwords, NTLM hashes, or Kerberos.
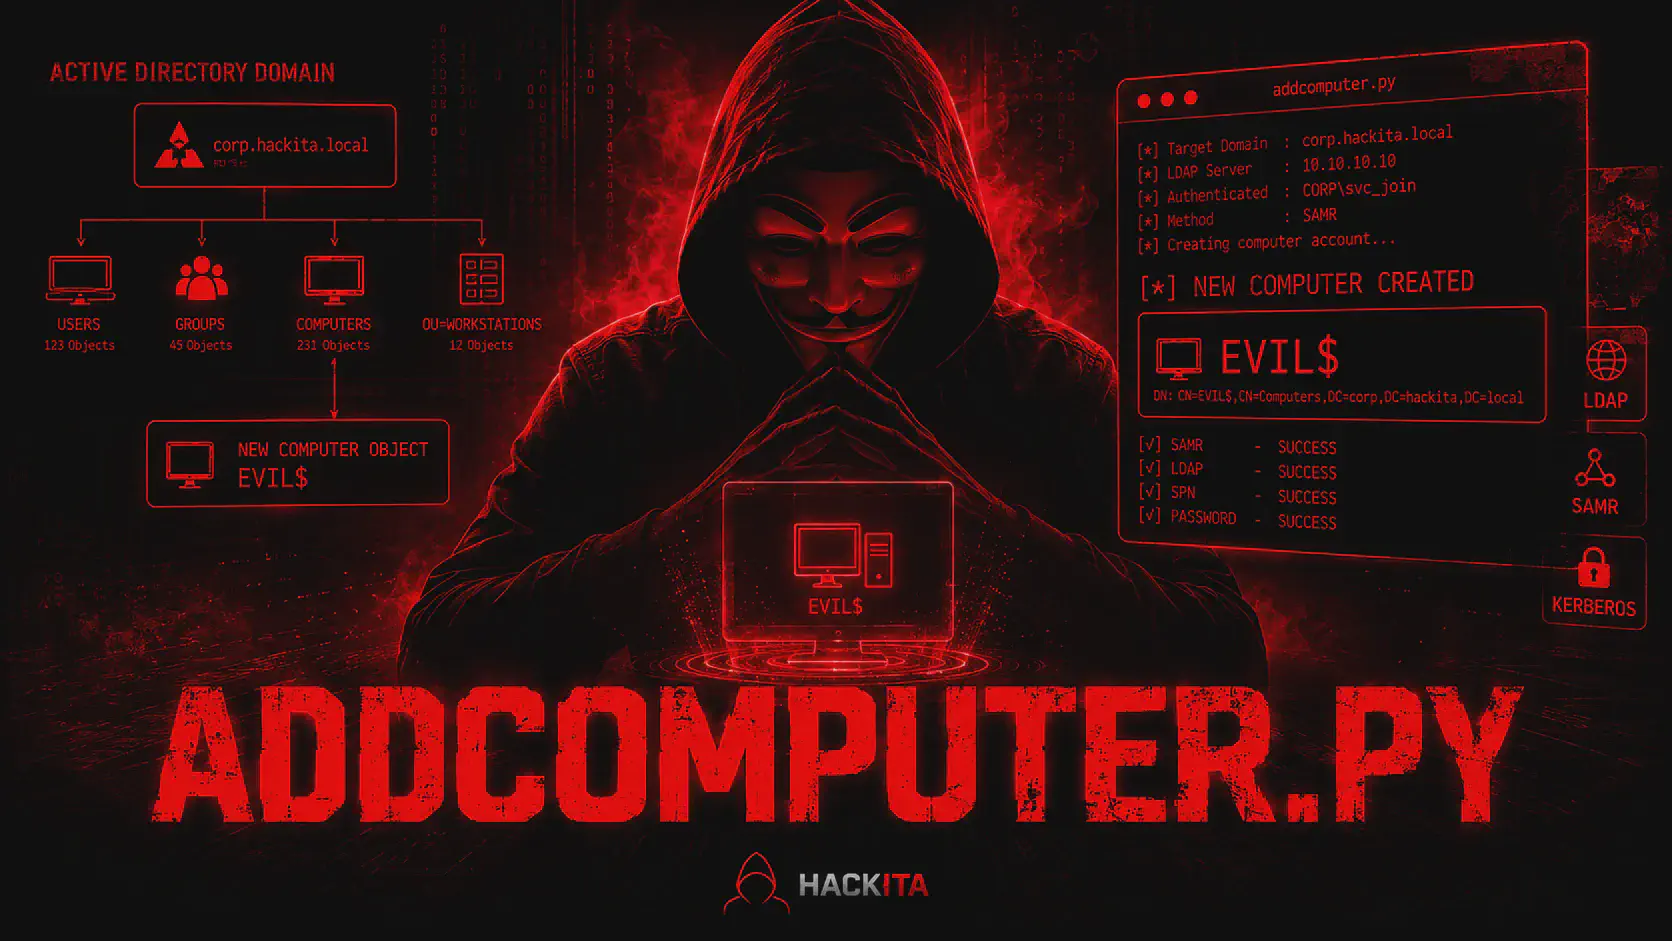
Impacket's addcomputer.py guide for creating Active Directory computer accounts via SAMR or LDAPS, verifying MachineAccountQuota, and using them in RBCD chains.
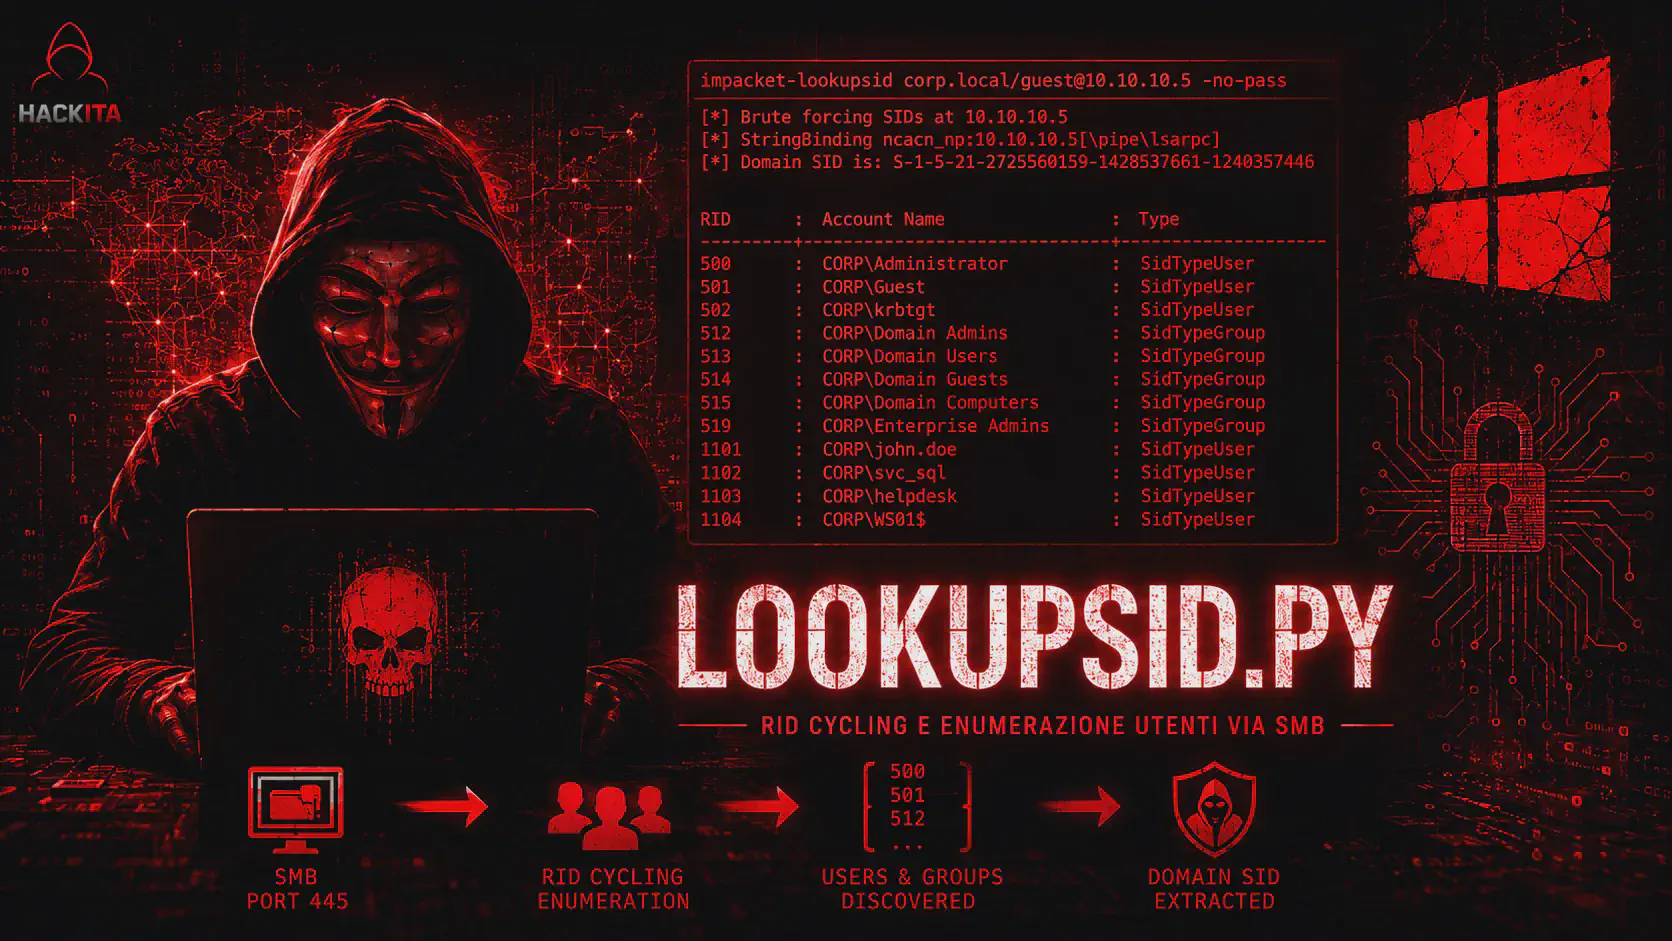
Guide to impacket-lookupsid to enumerate users, groups, and SIDs via MS-LSAT over SMB, using passwords, NTLM hashes, Kerberos, or anonymous sessions when allowed.
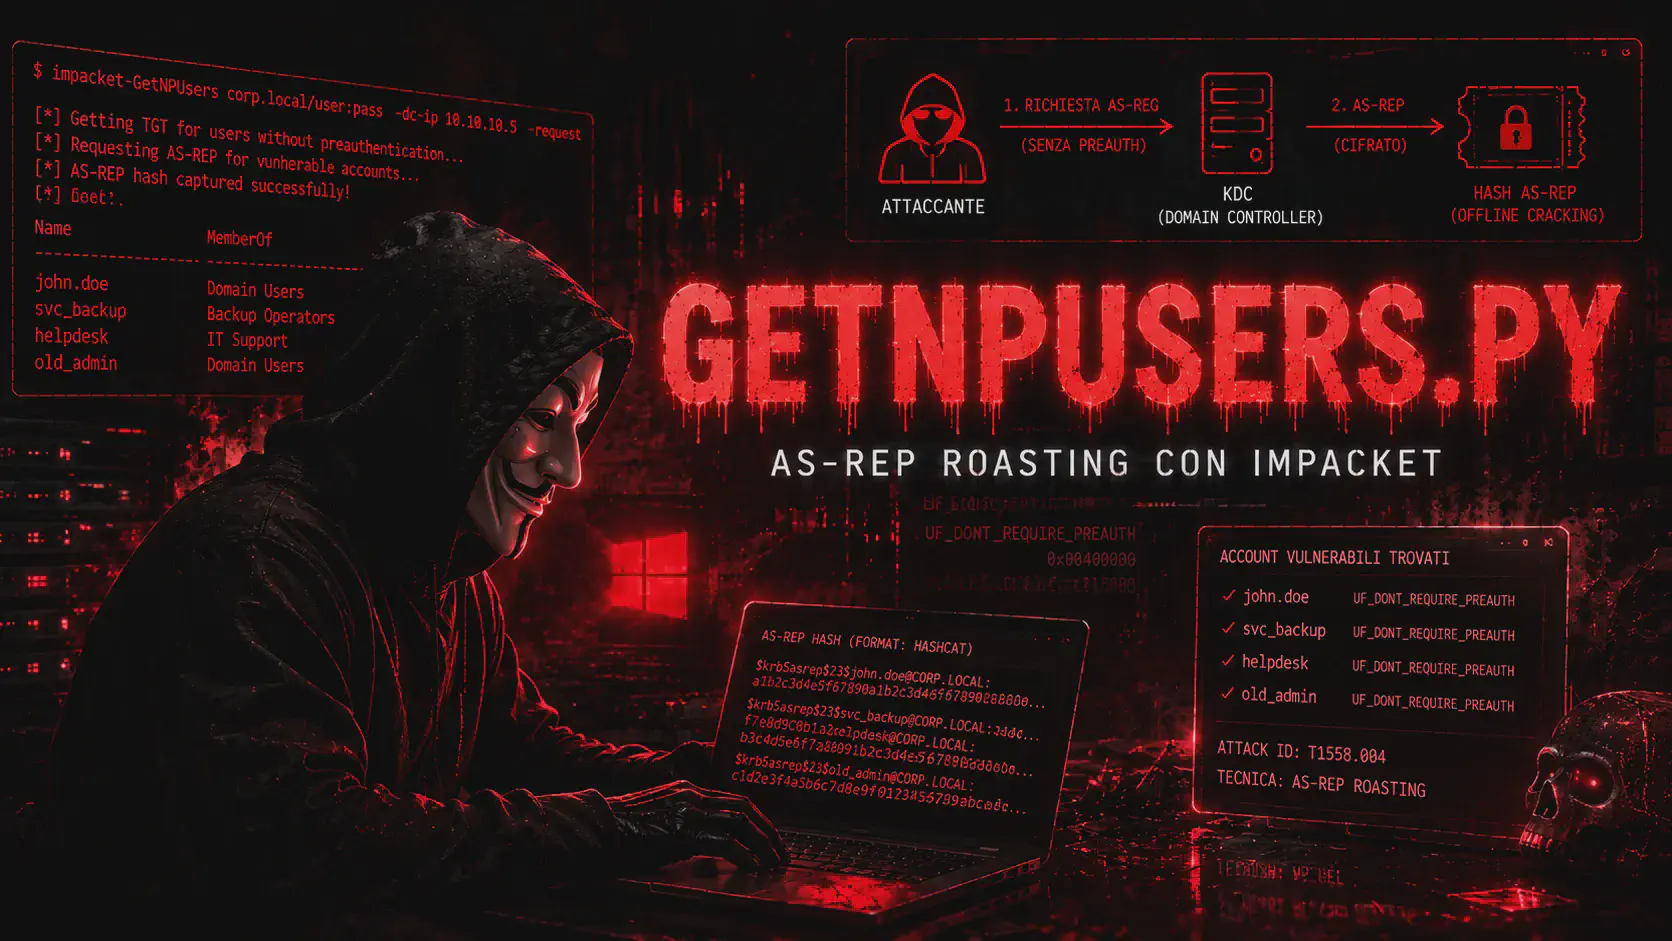
Impacket's GetNPUsers.py guide for finding accounts without Kerberos pre-authentication, extracting AS-REP hashes, and cracking them offline with Hashcat.
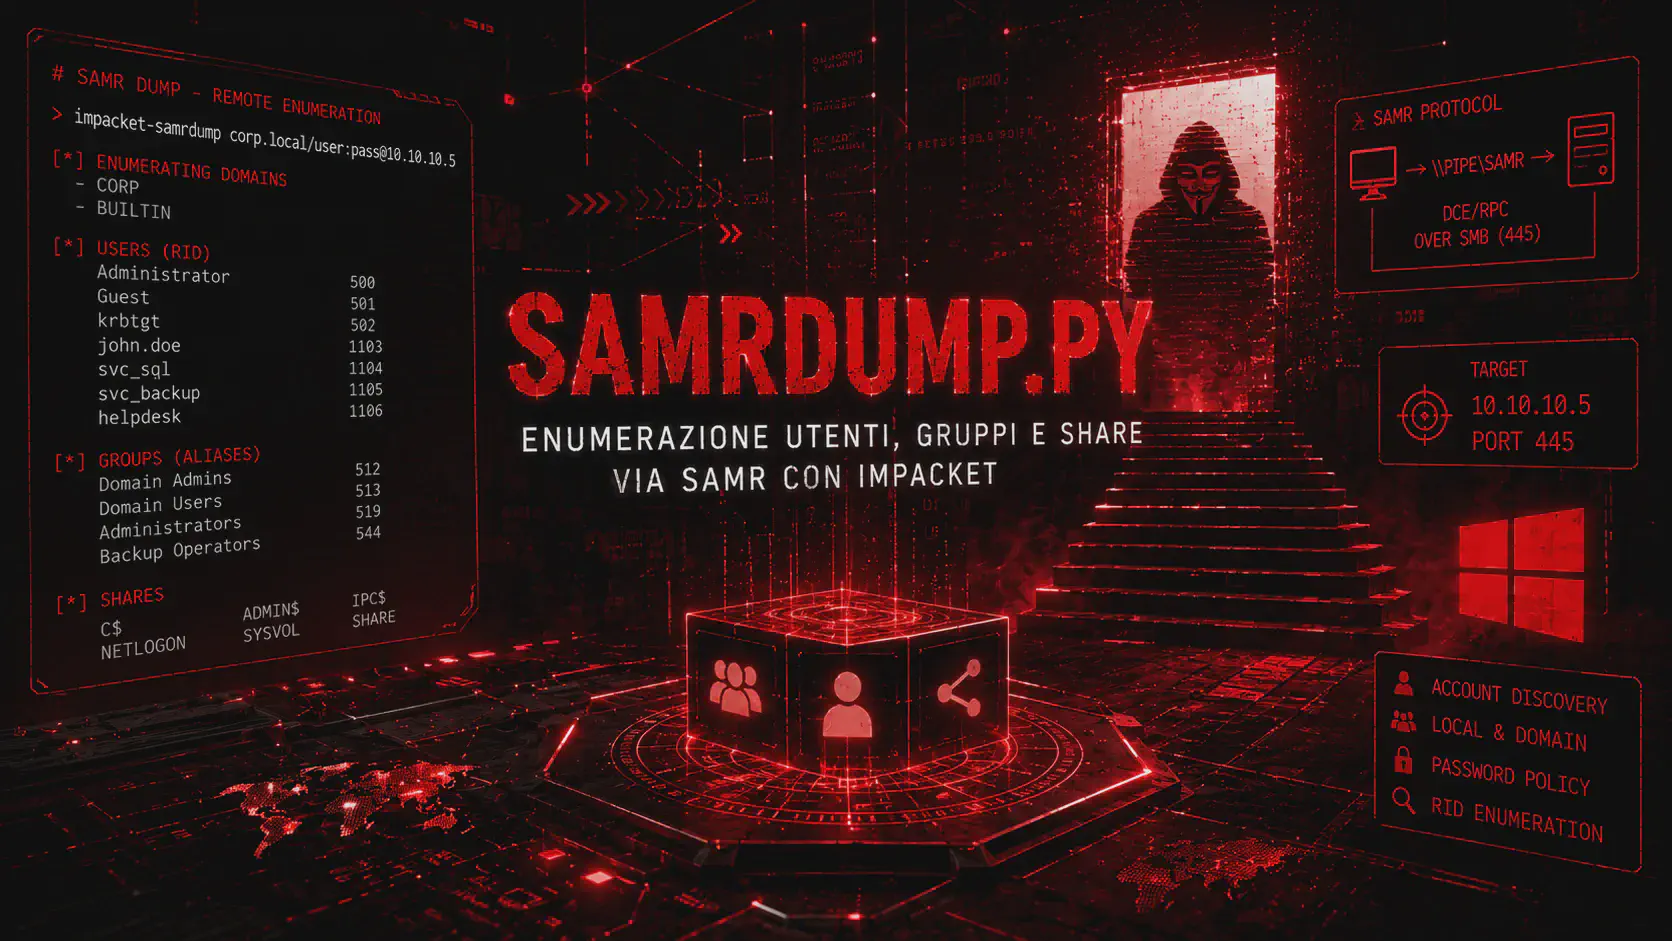
Impacket's samrdump.py guide to enumerate Windows users via MS-SAMR over SMB, get RID and account attributes with passwords, NTLM or Kerberos hashes.
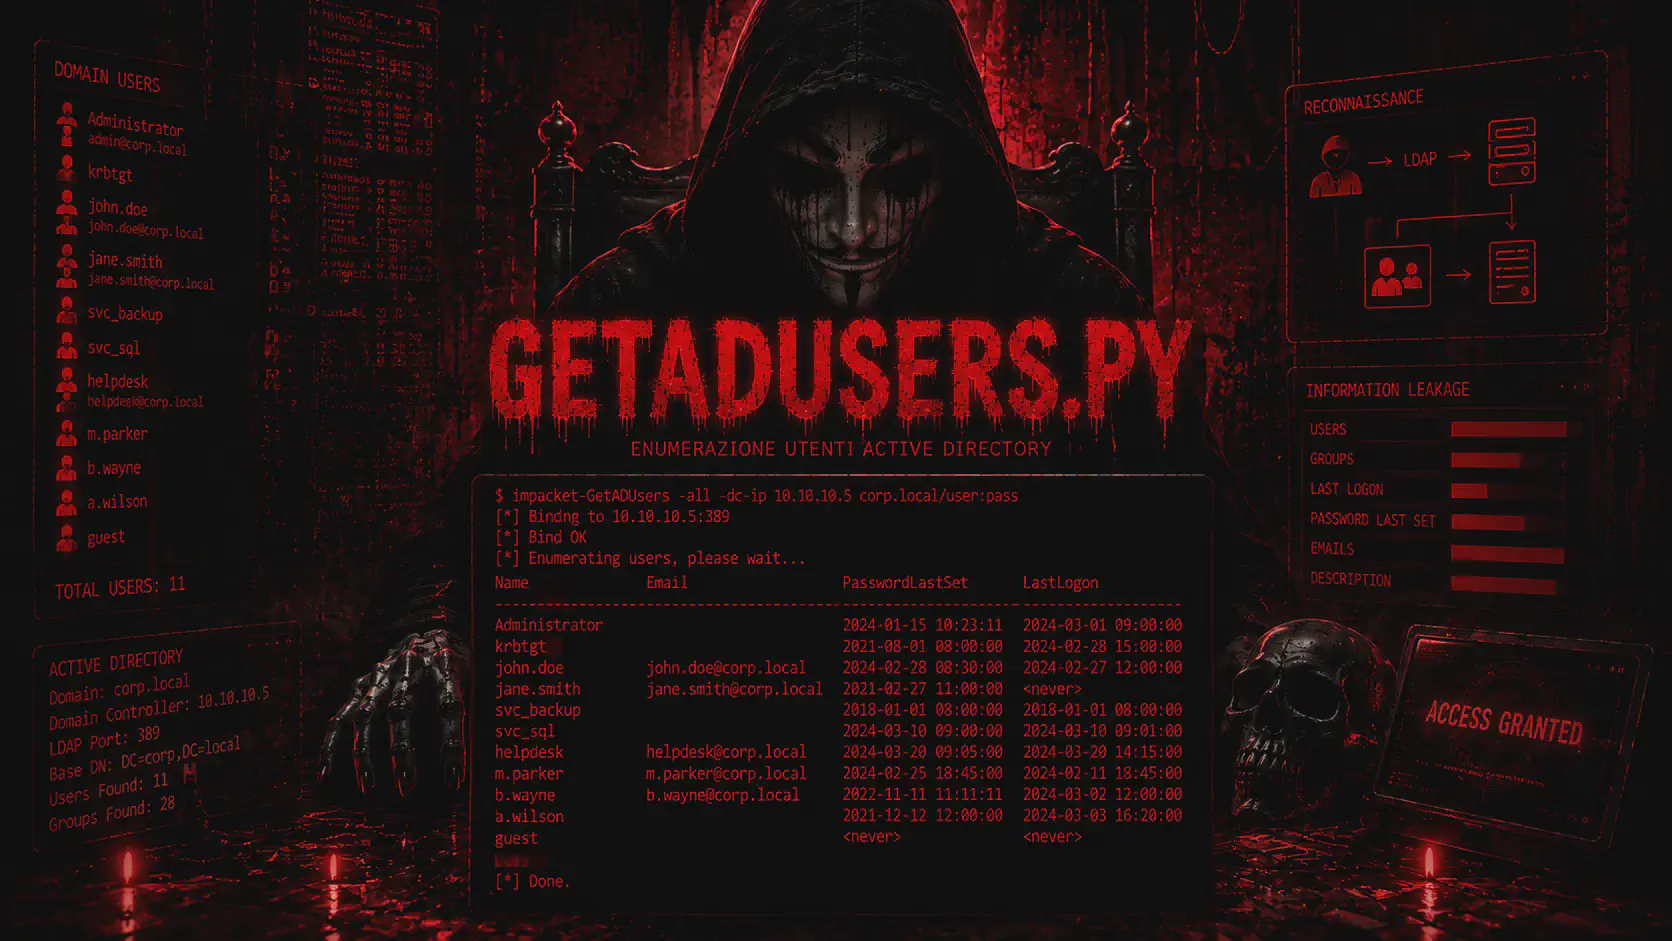
Impacket's GetADUsers.py guide to enumerate Active Directory users via LDAP with password, NTLM hash, AES or Kerberos key and parse pwdLastSet and lastLogon.
Impacket's getST.py guide for obtaining Kerberos Service Tickets with S4U2Self, S4U2Proxy, RBCD, and constrained delegation. Payload and errors for AD pentests.
A guide to Impacket's rpcdump.py for enumerating Windows RPC endpoints, UUIDs, named pipes, and dynamic ports. Practical commands and analysis for pentesting.
impacket-dcomexec How-To Guide: Remote Windows Execution via DCOM with ShellWindows, ShellBrowserWindow, and MMC20 Using NTLM Passwords or Hashes.
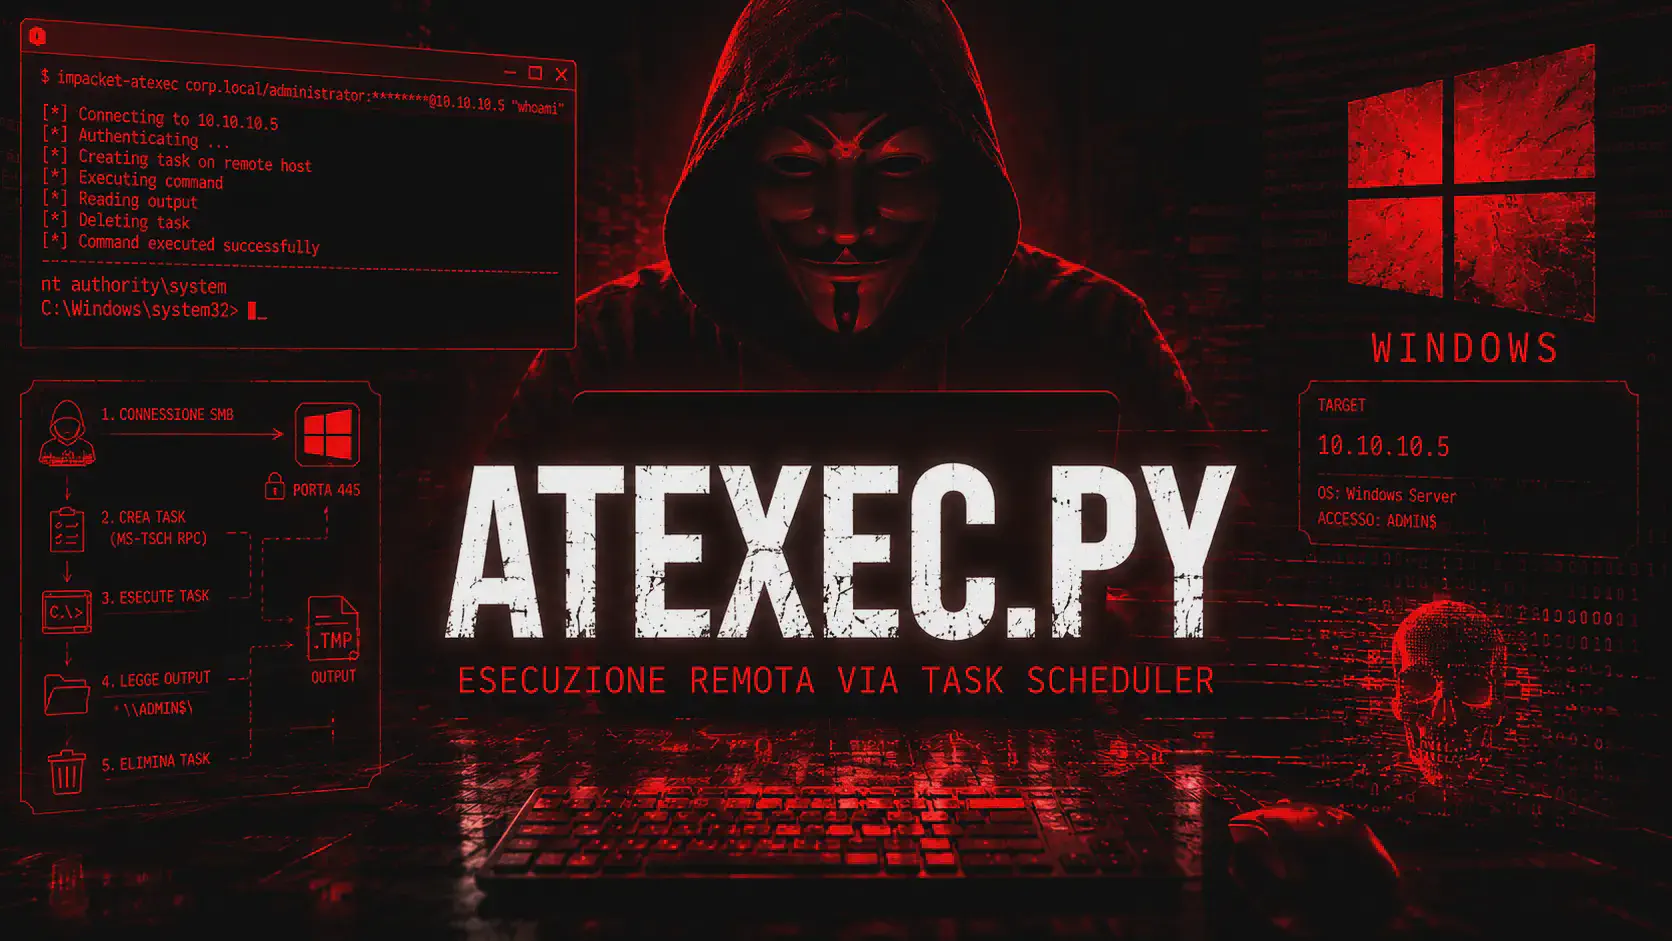
A Guide to Impacket-atexec: Remote Execution on Windows via Task Scheduler RPC with Password, Pass-the-Hash, Kerberos, and Lateral Movement over SMB.
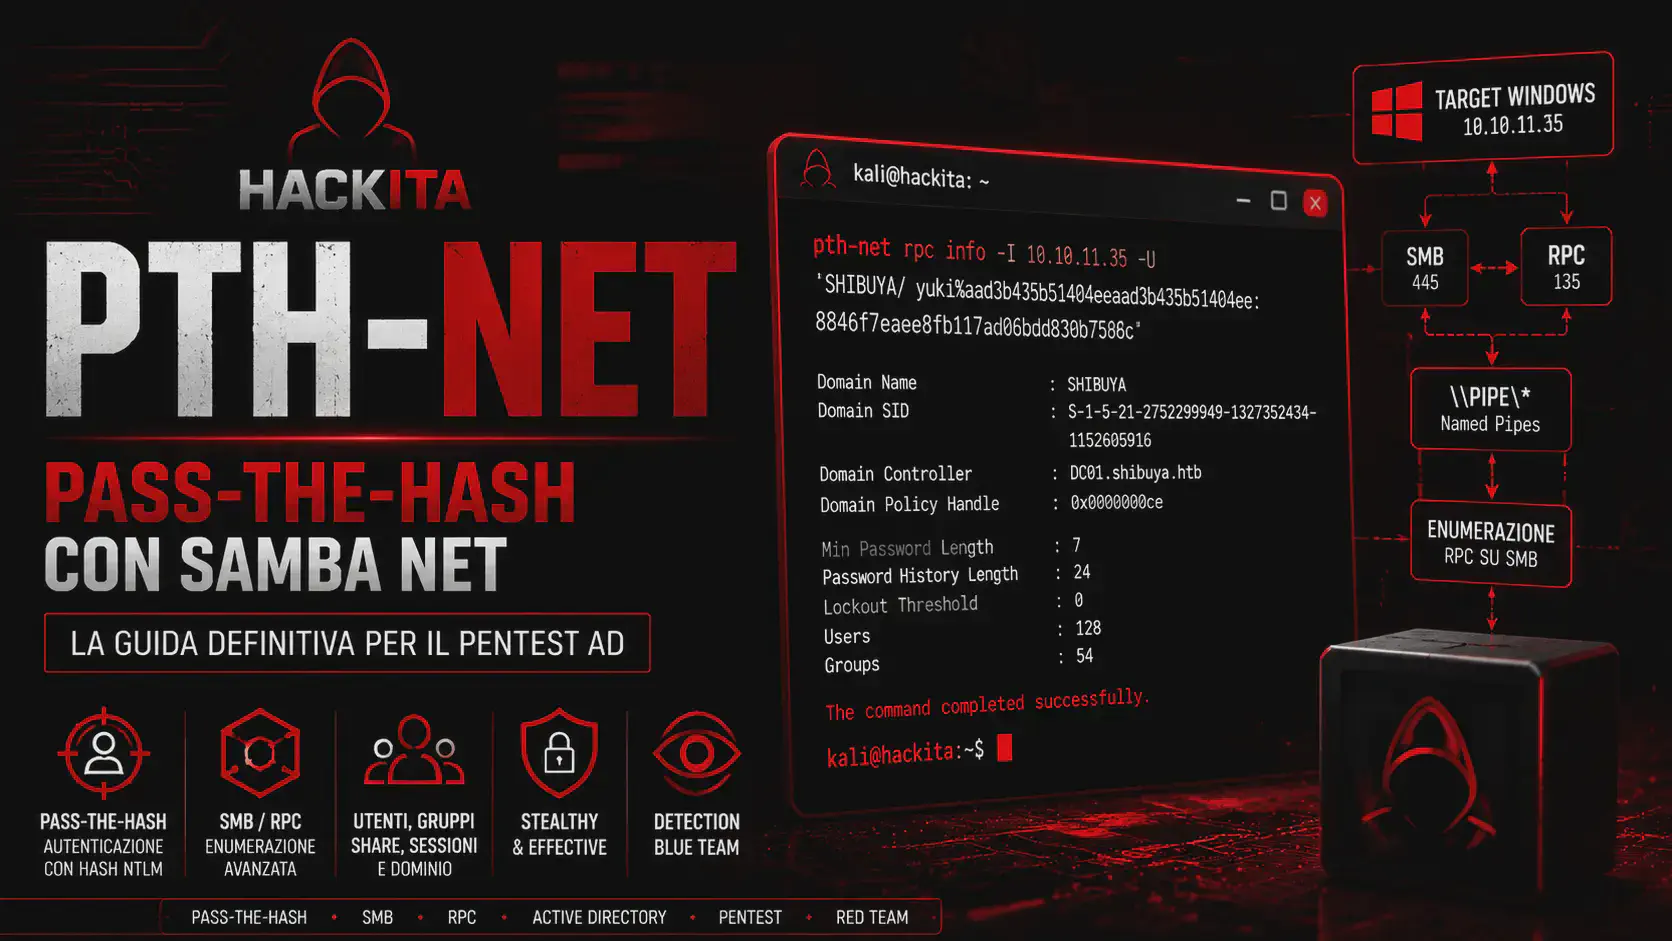
Use pth-net with NTLM hash to enumerate users, payloads, groups and shares via SMB/RPC in pentests, compare it with NetExec and Impacket and analyze PtH detection.
How to impacket-secretsdump: Remote and offline dump of NTLM hashes, SAM, LSA secrets, Kerberos keys, and NTDS.dit in Windows and Active Directory.
PowerView guide to enumerate Windows Active Directory: users, groups, computers, ACLs, sessions, GPOs, and trusts with PowerShell commands and practical examples.
PowerShell for Windows Pentesters: Commands, Downloads, Remoting, Active Directory Enumeration, Logging, AMSI, CLM, and Post-Exploitation Techniques.
SharpHound for BloodHound CE: Active Directory data collection, key flags, stealth options, and import to map escalation paths.
BloodyAD: PTH/PTT authentication, ACE abuse (GenericAll, WriteDACL, RBCD), Shadow Credentials, Bad Successor 2025 and autobloody.Pentest, payload, detection and bypass
Impacket reg.py: Query, add, delete, save, and backup the remote Windows registry via SMB/MS-RRP. SAM, LSA, WDigest, RDP, and WinRM keys for pentesting and hardening.
Complete guide to Certipy 5.1 to enumerate AD CS, locate ESC1-ESC17, request certificates, use PKINIT, relay, Shadow Credentials and Golden Certificate.
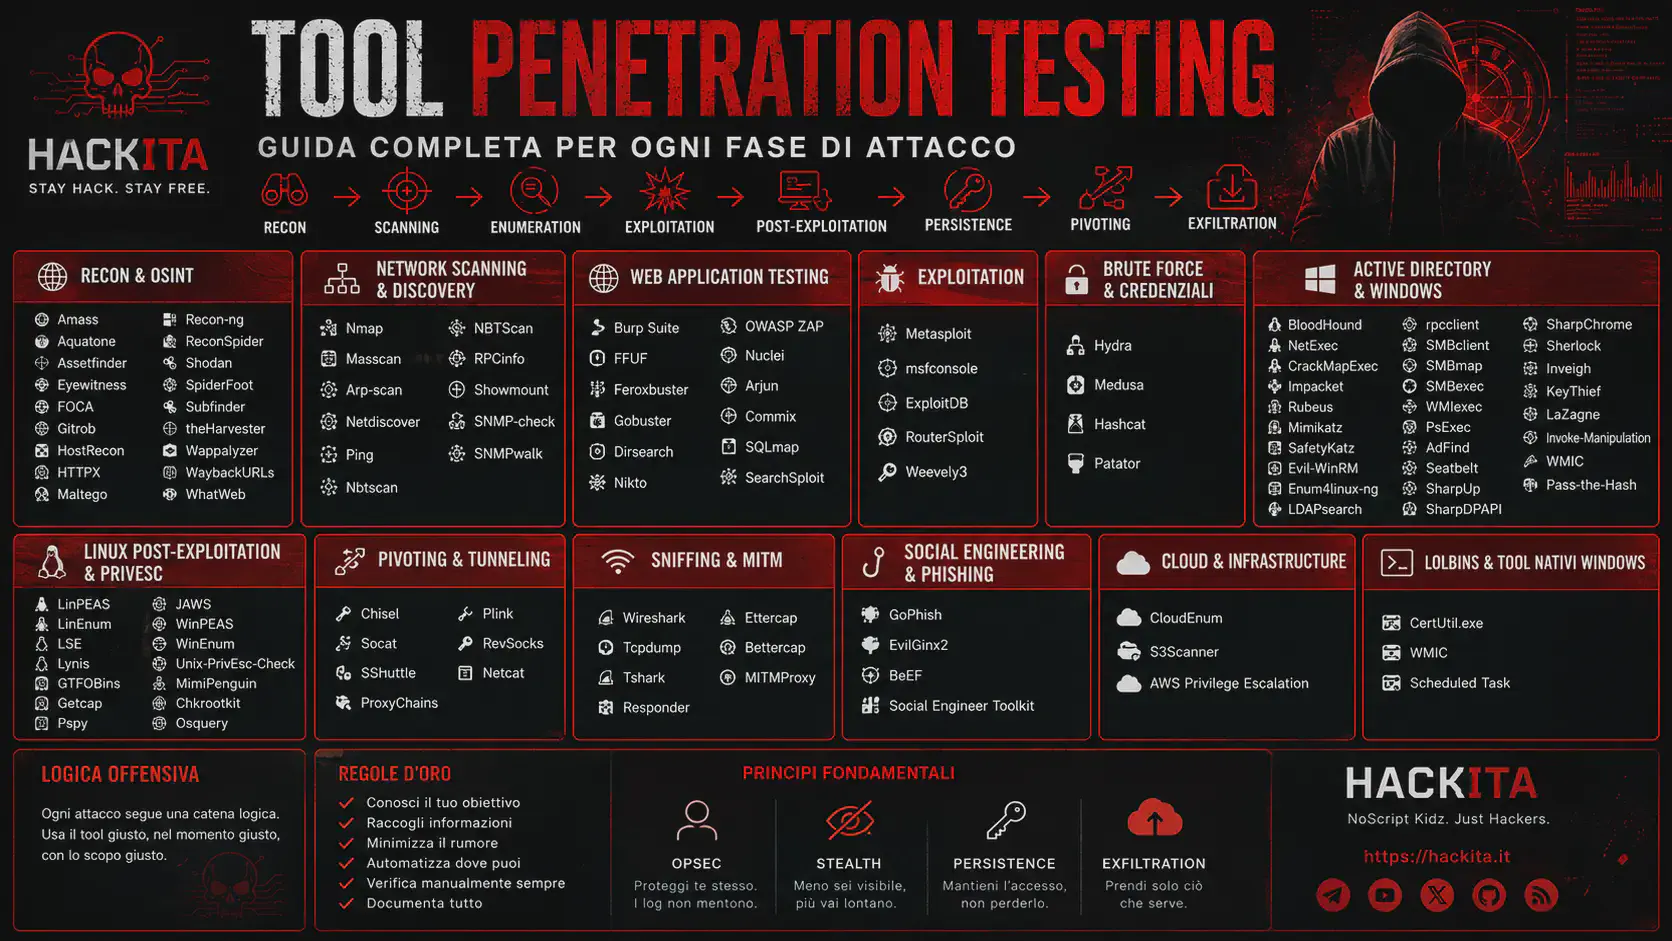
All offensive penetration testing tools organized by attack phase: recon, exploitation, post-exploitation, pivoting, AD. With real attack chains for CTF, OSCP, OSEP, and red teams.
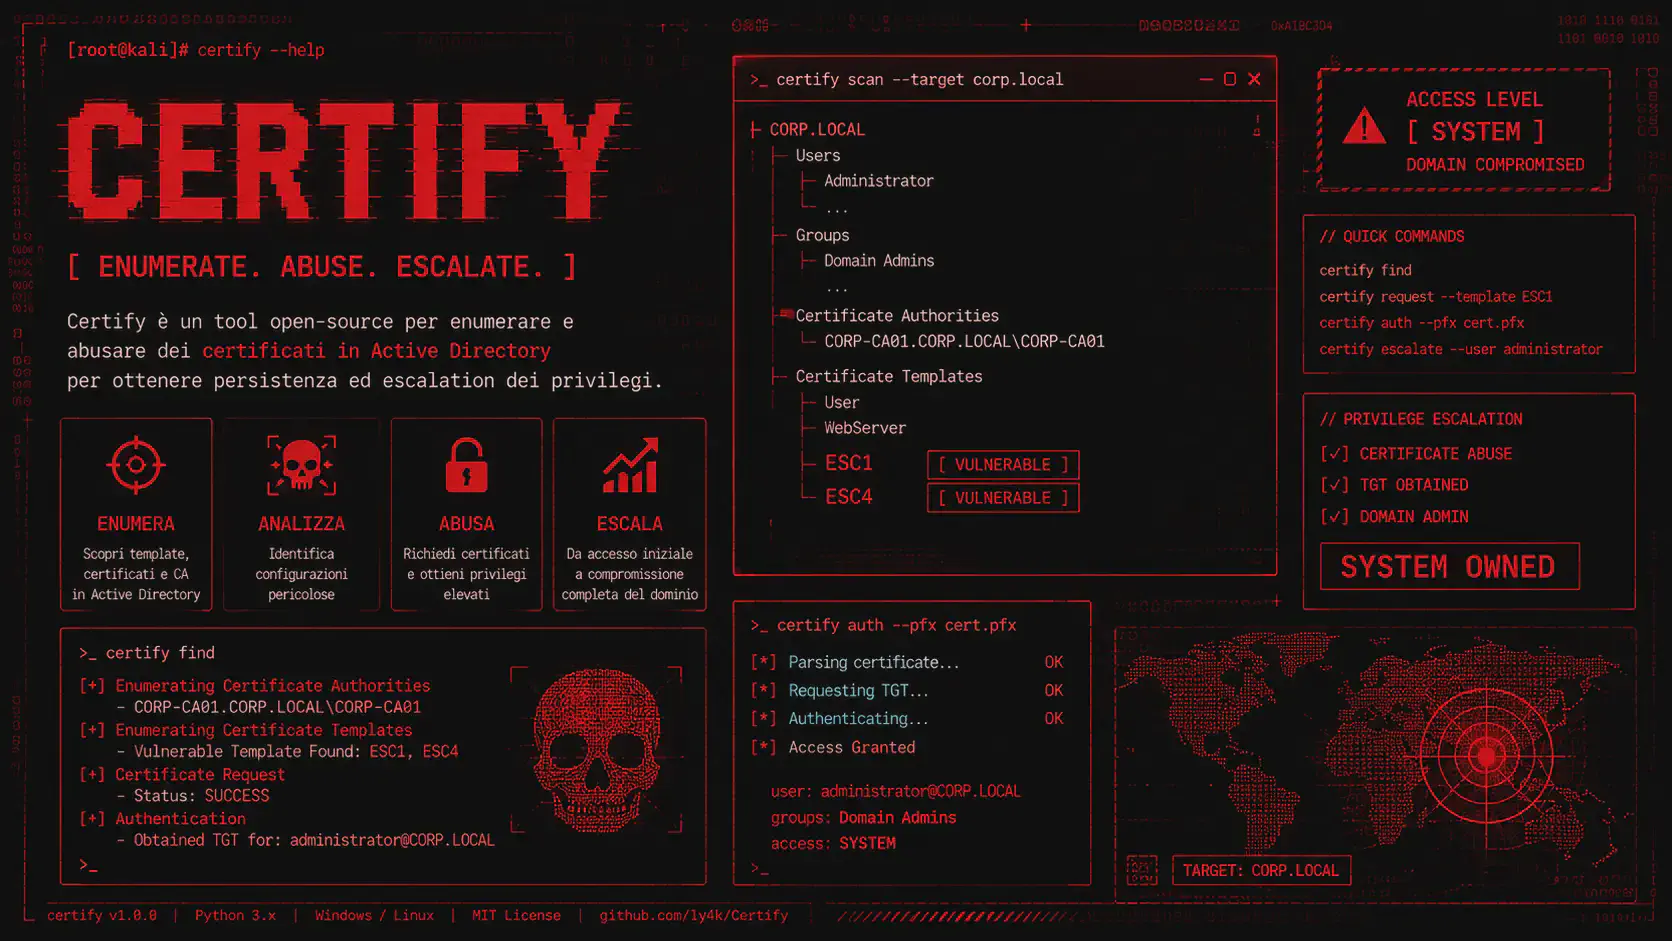
Certify is GhostPack's C# tool for enumerating and exploiting AD CS from Windows without Python dependencies. Learn how to use it to find vulnerable templates and request certificates for escalation to Domain Admin.
Complete guide to John the Ripper (Jumbo): Extract hashes from ZIP, SSH, KeePass, PDF, and Office with *2john; crack with wordlist and rules. Comparison with hashcat and final cheat sheet.
Learn how to use OWASP ZAP to intercept HTTP/HTTPS traffic, map web applications with spiders and AJAX Spiders, perform active scans, fuzzing, and authenticated tests, even in CI/CD with Docker and APIs.
Learn how to use Impacket's WMIExec and wmiexec.py for lateral movement on Windows with passwords, Pass-the-Hash, and Kerberos, reducing artifacts compared to PsExec and improving OPSEC.
Learn how to use Unix-PrivEsc-Check to detect misconfigurations, weak permissions, sudo abuse, and privilege escalation vectors on Unix/Linux systems, including legacy environments where modern tools fail.
A guide to Wappalyzer for detecting CMS, framework, CDN, analytics, and website versioning clues to guide targeted reconnaissance, fingerprinting, and scanning in pentesting.
Learn how to use Waybackurls to extract a domain's historical URLs from the Wayback Machine, find forgotten paths, exposed backups, and old endpoints useful for passive reconnaissance.
Learn how to use WhatWeb to identify a website's CMS, framework, web server, JavaScript libraries, and technologies to guide reconnaissance, fingerprinting, and targeted vulnerability scanning.
Complete guide to WinEnum for post-exploitation enumeration on Windows: PowerShell and Batch variants, privilege escalation checks, OPSEC, differences with WinPEAS, PowerUp, SharpUp, and Seatbelt.
WinPEAS for Windows privesc: Commands, enumeration, and output to detect vulnerable services, exposed credentials, and misconfigured privilege escalation.
Learn how to use WMIC for enumeration, remote execution, lateral movement, and WMI persistence on Windows. This includes the current status of the tool, practical commands, detection, hardening, and a comparison with PowerShell, CIM, and WinRM.
Learn how to use ssh-audit to verify SSH server and client configurations, identify weak algorithms, outdated ciphers, vulnerable versions, and find useful findings for authorized hardening or penetration testing.
SSH-KeyHunter automates the search for private SSH keys on Linux, detects unprotected files, owners, fingerprints, and targets from known_hosts: an ideal tool for post-exploitation and lateral movement in authorized pentests.
A guide to Sshuttle for creating a transparent tunnel over SSH, reaching internal subnets, routing DNS, and using a compromised host as a pivot during lateral movement and post-exploitation in authorized pentests.
Learn how to use Subfinder to find valid subdomains from passive sources, speed up web reconnaissance, and build a more effective recon pipeline with the ProjectDiscovery tool optimized for speed and stealth.
smbmap explained for pentests: SMB share enumeration, permissions, file access, and credential testing on Windows and Active Directory systems.
SMBExec is a remote command execution technique over SMB 445 without dropping persistent binaries. It's a stealthier alternative to PsExec in Active Directory environments.
SET is a framework for simulating social engineering in authorized environments: phishing, credential harvester, and client-side attacks.
RouterSploit is a framework for testing vulnerabilities on routers and IoT devices. It includes scanning, exploit, and brute-force modules.
Osquery allows you to query operating systems with SQL queries to analyze processes, users, files, and configurations for security monitoring purposes.
Patator: A Modular Brute-Force Authentication Testing Framework
Nmap for penetration testing and network recon: commands, host discovery, TCP/UDP port scanning, service detection, OS fingerprinting, NSE and enumeration.
How to download and use ncat.exe on Windows: listeners, connections, file transfer, SSL, reverse shell with -e cmd.exe, antivirus false positives and detection.
MSFvenom exploit for lab and pentest: syntax, staged and stageless payload, EXE, ELF, PHP, WAR and MSI formats, shellcode with bad characters, handler and detection.
LSE (Linux Smart Enumeration): Automated Linux Privilege Escalation Checklist
Medusa is a parallel tool for brute-forcing authentication over SSH, FTP, SMB, HTTP, and other services. Fast, scalable, and ideal for authorized password auditing.
Metasploit Framework is the most widely used penetration testing platform for exploits, payloads, and post-exploitation. A complete offensive workflow guide.
mitmproxy is an interactive proxy for analyzing and manipulating HTTP/HTTPS traffic. Ideal for API testing, debugging, and authorized security assessments.
LaZagne is an open-source tool for recovering saved passwords on Windows and Linux from browsers, email clients, and local software post-exploitation.
Ldapsearch is a CLI tool for querying LDAP and Active Directory from Linux. It's useful for enumerating users, groups, SPNs, and domain objects.
httpx is the HTTP probing tool for filtering active hosts, detecting technologies, status codes and screenshots in pipelines with subdomain enumeration.
Hydra is a brute force tool for testing credentials over SSH, FTP, RDP, HTTP, and other services during authorized penetration tests.
Impacket is a Python suite for interacting with network protocols (SMB, LDAP, Kerberos, RPC) and conducting AD attacks such as DCSync and Pass-the-Hash.
Invoke-Manipulation is a PowerShell module for obfuscating scripts and bypassing static checks during authorized red team operations.
HostRecon automates single-domain OSINT and reconnaissance: DNS, whois, subdomain, breach data, and exposure mapping in a single command.
Evil-WinRM: Remote PowerShell shell via WinRM for Windows post-exploitation. Pass-the-hash, Kerberos ticket, AMSI bypass, in-memory execution .NET assembly for lateral movement enterprise.
Cloud_enum is an OSINT tool for enumerating publicly exposed cloud resources on AWS, Azure, and GCP. It's useful during reconnaissance to map buckets, storage accounts, and assets related to a target domain.
Empire 5.0: A Complete Guide to C2 PowerShell: Stager, AMSI Bypass, Post-Exploitation, Lateral Movement, and Evasion Techniques. Cheat sheet included.
Evilginx2's practical guide to bypassing 2FA authentication: man-in-the-middle phishing, session hijacking, and credential theft. Advanced attacks against MFA.
Arjun is a tool for discovering hidden HTTP parameters in web applications during penetration testing. It automates the identification of undocumented GET and POST parameters useful for IDOR, XSS, and injection.
Assetfinder is an OSINT tool for enumerating subdomains from public sources during the reconnaissance phase. It's ideal for quickly mapping a domain's attack surface during penetration testing.
Commix is an automated tool for identifying and exploiting command injection vulnerabilities in web applications. It supports blind, time-based, and file-based techniques to obtain RCE during penetration testing.
Plink is the command-line version of PuTTY that allows SSH tunneling, port forwarding, and pivoting from Windows systems. A practical guide to its use in penetration testing and red teams.
Searchsploit is a terminal tool for searching for local exploits directly from the Exploit-DB database. A practical guide to identifying exploitable vulnerabilities during penetration testing.
How to Install Maltego for OSINT and Reconnaissance: Use Entity, Transform, Pivot, and Graph Analysis to Correlate Domains, IPs, Emails, People, and Infrastructure.
Masscan is a high-speed port scanner capable of analyzing millions of IP addresses in minutes. A practical guide to its use during reconnaissance and infrastructure mapping during penetration testing.
Discover SpiderFoot to automate OSINT and reconnaissance: modules, correlation, subdomain, IP, email, threat intelligence, and attack surface mapping.
Learn how to use TheHarvester to harvest emails and subdomains: installation, recon, OSINT sources, API keys, JSON/XML output, and verified troubleshooting.
KeeThief: How to extract master keys and credentials from KeePass during an authorized pentest. Memory dumps, .kdbx files, operational limitations, detection, and post-exploitation.
Weevely3: A practical guide to generating and managing stealthy PHP web shells in penetration testing. Tunneling, evasion, and post-exploitation.
Chisel's Practical Guide to Tunneling and Pivoting: TCP Tunneling over HTTP, SOCKS Proxy, and Port Forwarding Through Firewalls. Modern Pivoting for Pentesters.
LaZagne: password recovery tool for 87+ applications. Browser, WiFi, email, database, sysadmin tools. DPAPI decryption, credential harvesting post-exploitation Windows/Linux/macOS.
SafetyKatz is a Mimikatz wrapper for in-memory credential dumping from LSASS, without writing to disk. It supports EDR evasion, NTLM hash extraction, and integration with Cobalt Strike for post-exploitation in Active Directory.
FFUF is a fast Go web fuzzer for directory, vhost, and API testing. A practical guide with wordlists, filters, and pentest techniques.
Hashcat: GPU password cracking practical guide for NTLM, MD5, SHA, bcrypt hashes. Attack modes, mask patterns, wordlist rules and real techniques from CTF and pentest.
CrackMapExec (cme) to NetExec (nxc) Migration Guide: Translate CME commands to NXC, manage Kerberos, forms, file transfer, and see what's changing today.
ARP-Scan guide on Kali Linux to discover hosts on your local network: ARP scanning, IP, MAC, vendor, subnet, output, and network reconnaissance workflow.
Netdiscover is an essential tool for identifying active devices on the local network. It's ideal for silent recon via ARP in environments without DNS or DHCP.
Analyze network behavior with ping, fping, and hping3. ICMP reconnaissance, host discovery, and firewall testing techniques used in pentests.
Rpcinfo allows you to identify active RPC services on Unix/Linux hosts. It's essential for reconnaissance and analysis of potential remote attack vectors.
Showmount is the perfect tool for enumerating NFS shares. It's used in recons to identify accessible resources and entry points in Unix/Linux environments.
Snmp-check allows you to extract information from network devices using SNMP. Perfect for low-noise attacks, silent enumeration, and footprinting.
Snmpwalk is the ideal tool for querying SNMP agents and gathering detailed information about network devices. It's used for low-noise recon and targeted attacks.
Complete guide to enum4linux-ng for SMB and Active Directory enumeration: users, groups, shares, policies, SID/RID, authentication, and practical commands.
Complete Operation Guide to NetExec (nxc): SMB, LDAP, WinRM, RDP, advanced modules, credential dumping, vulnerability scan and lateral movement in Active Directory
With smbclient, you can access, read, and write files to SMB shares. Learn how to use it for pentesting, internal attacks, enumeration, and pivoting in AD.
BloodHound for privilege escalation on Active Directory: SharpHound, edge abuse, Shadow Credentials and ADCS. Italian guide to AD pentest towards Domain Admin.
ldapsearch for pentest: RootDSE, Base DN, LDAP bindings, users, groups, computers, SPN, LDAPS and Active Directory enumeration troubleshooting and cheat sheets
Guide to rpcclient on Kali Linux to enumerate users, groups, SIDs/RIDs, trusts, password policies, and SMB shares via SAMR, LSARPC, and SRVSVC, with practical commands.
What is Inveigh and how does it work? A guide to LLMNR, NBNS, and WPAD for capturing NetNTLM in Windows labs, using PowerShell, relay, troubleshooting, and detection.
A practical guide to mitmproxy: configure the proxy, intercept HTTPS, install the CA, filter and modify flows, save sessions, and troubleshoot common issues.
NBTScan on Linux: Learn how to scan Windows hosts, identify NetBIOS names, domains, workgroups, and useful information for network reconnaissance.
Learn how to use Netcat (nc) on Linux and Windows: practical commands, TCP/UDP listeners, port scanning, banner grabbing, file transfer, and reverse shell.
Responder for Linux: How to capture NTLM/NetNTLMv2 hashes with LLMNR, NBT-NS, and WPAD, crack and relay NTLM in penetration tests and secure Windows labs
What is Bettercap and how does it work? Discover the framework for network hacking and MITM: tutorials on Kali Linux, ARP spoofing, sniffing, network recon, PCAP, and proxies.
What is Ettercap and how does it work? A practical guide to MITM, ARP spoofing, and sniffing on Kali Linux, including installation, filters, packet capture, and commands.
What is tcpdump and how does it work? A guide to terminal network sniffing with packet capture, BPF filters, PCAP analysis, and pentesting commands.
What is TShark and how is it used? A guide to terminal network sniffing with packet capture, filters, PCAP analysis, statistics, and pentesting commands.
Wireshark for ethical hacking: advanced filters, NTLM, DNS, and TCP Stream. Learn how to isolate traffic, read sessions, and find useful indicators in labs and HTBs.
Latest Guides and Resources
Cybersecurity and information security: what it is, threats and defenses for businesses and individuals, ethical hacking, penetration testing, red teams, blue teams, SOCs, and analysis.
SEO poisoning: Malware, cloaking, and Gootloaders push fake pages to the top of Google. Recognize them and check if your site is compromised.
How a keylogger works and what it is, hardware and software, how to recognize it on Windows and what the law says, from the FTC case against the SpyFone app.
What is a RAT, how does a remote control Trojan work, how to tell if your PC is infected, how to remove it, and the history of Back Orifice and Blackshades.
Flipper Zero: what it is, how it works, and what it can do with RFID, NFC, Sub-GHz, and BadUSB. Learn about custom firmware and what's legal and illegal in Italy.
Kali Linux: what it is, what it's for, how to install it, how to learn, and the main tools for penetration testing, cybersecurity, forensics, and red teams.
Firewall: what it is, meaning, how it works, what it does, types (stateful, NGFW, WAF), basic rules, ufw and Windows commands and how a pentester sees it with Nmap.
Learn what a computer worm is, how it works and spreads, how it differs from viruses and ransomware, famous cases, and how to recognize an infection on the network.
Data breach: how it works and what it is, causes, real-world examples, the 72-hour rule, costs in 2026, and what to do if your data is stolen.
Trojans: how they spread, what damage they can cause, and how to recognize them. Comparison with viruses and worms, main types, and examples such as Zeus and Emotet.
What is a zero-day attack? Learn what zero-day vulnerabilities and exploits mean, the differences between n-day and CVE, real-world examples, and how to defend yourself in 2026.
GDPR: meaning, how it works and who it applies to, principles, rights, DPO, data breach in 72 hours and fines up to 20 million euros or 4% of turnover
Who are Anonymous, where the Guy Fawkes mask came from, their most famous operations (Chanology, Payback, Tunisia), and what they're still doing today in 2026.
The deep web explained simply: what it is, how to access it and how it works, examples, differences between the surface web and the dark web, whether Tor is needed, and whether it's legal to browse it.
Kevin David Mitnick, known as The Condor and The Darkside Hacker, was one of the most famous hackers: social engineering, arrest, career, and death in 2023.
What is a botnet, how a device becomes a remotely controlled zombie, how to recognize it, and the Mirai case that brought half the internet into crisis in 2016.
NIS2 explained simply: what the NIS 2 directive is, who it applies to, obligations, 24-hour incident reporting, fines up to €10 million, and 2026 deadlines.
Learn how spyware works, the signs you can spot on your phone and PC, how it differs from stalkerware, how to remove it, and what the Pegasus case revealed.
Were data centers in Basilicata hacked? Russian pages and Kraken indicate a hacker attack: what happened to the Basilicata Region, healthcare system, and hospitals?
Who are the 10 most famous and powerful hackers in history? From Kevin Mitnick to Anonymous: true stories, famous attacks, secrets and curiosities, and what they do today.
What is the dark web, how does it differ from the deep web and Tor, what criminal economy really operates there, and what's true about legends like the Red Rooms.
What distinguishes white hat, black hat, and grey hat, the origin of the term hacker/cracker, the legal risks of each, and what responsible disclosure is.
What is a computer virus, how it spreads, the main types, how to recognize and remove it, and how it differs from malware, worms, Trojans, and ransomware.
Who is an ethical hacker, what they do every day, what skills and tools they use, how much they earn in Italy, and how to become one step by step.
What is a hacker, the difference between a cracker and an ethical hacker, the types (white, black, grey hat), when hacking is a crime, and how to become an ethical hacker.
Revolut confirms a data breach: fake government request, passports and Bitcoin histories exposed. Data published online, 10.000 BTC ransom demanded.

Thomson Reuters: C-Track platform breached in US and Canadian courts. SSNs, health data, and court records sealed in 24 courts.
Vodafone 2026 scam: Did you receive the text message "Your 7415 Gold Starter points expire today"? Here's how to spot it, where the link goes, and what to do.
Automate secret scanning with Gitleaks pre-commit and TruffleHog in CI/CD: lock API keys and tokens, verify leaks, and remove secrets from Git history.
AWS Operational Pentesting: Enumerate IAM, S3, EC2, Lambda, and IMDS with AWS CLI, Pacu, ScoutSuite, and Prowler; find misconfigurations and privilege escalation paths.
Cloud security automation on AWS: Use Prowler, ScoutSuite, and AWS Config; integrate Checkov and tfsec into CI/CD; and detect drift and misconfiguration with EventBridge.
Learn which SecLists wordlists to use for directory fuzzing, password cracking, DNS and API, with paths on Kali Linux and custom lists created with CeWL and Crunch.
Database security for pentesters and defenders: misconfigurations, weak credentials, exposed services, and hardening of MSSQL, MySQL, and PostgreSQL.
Database Privilege Escalation Guide. Pentest for MSSQL, MySQL, PostgreSQL, and Oracle: Enumerate privileges and escalate from database access to RCE.
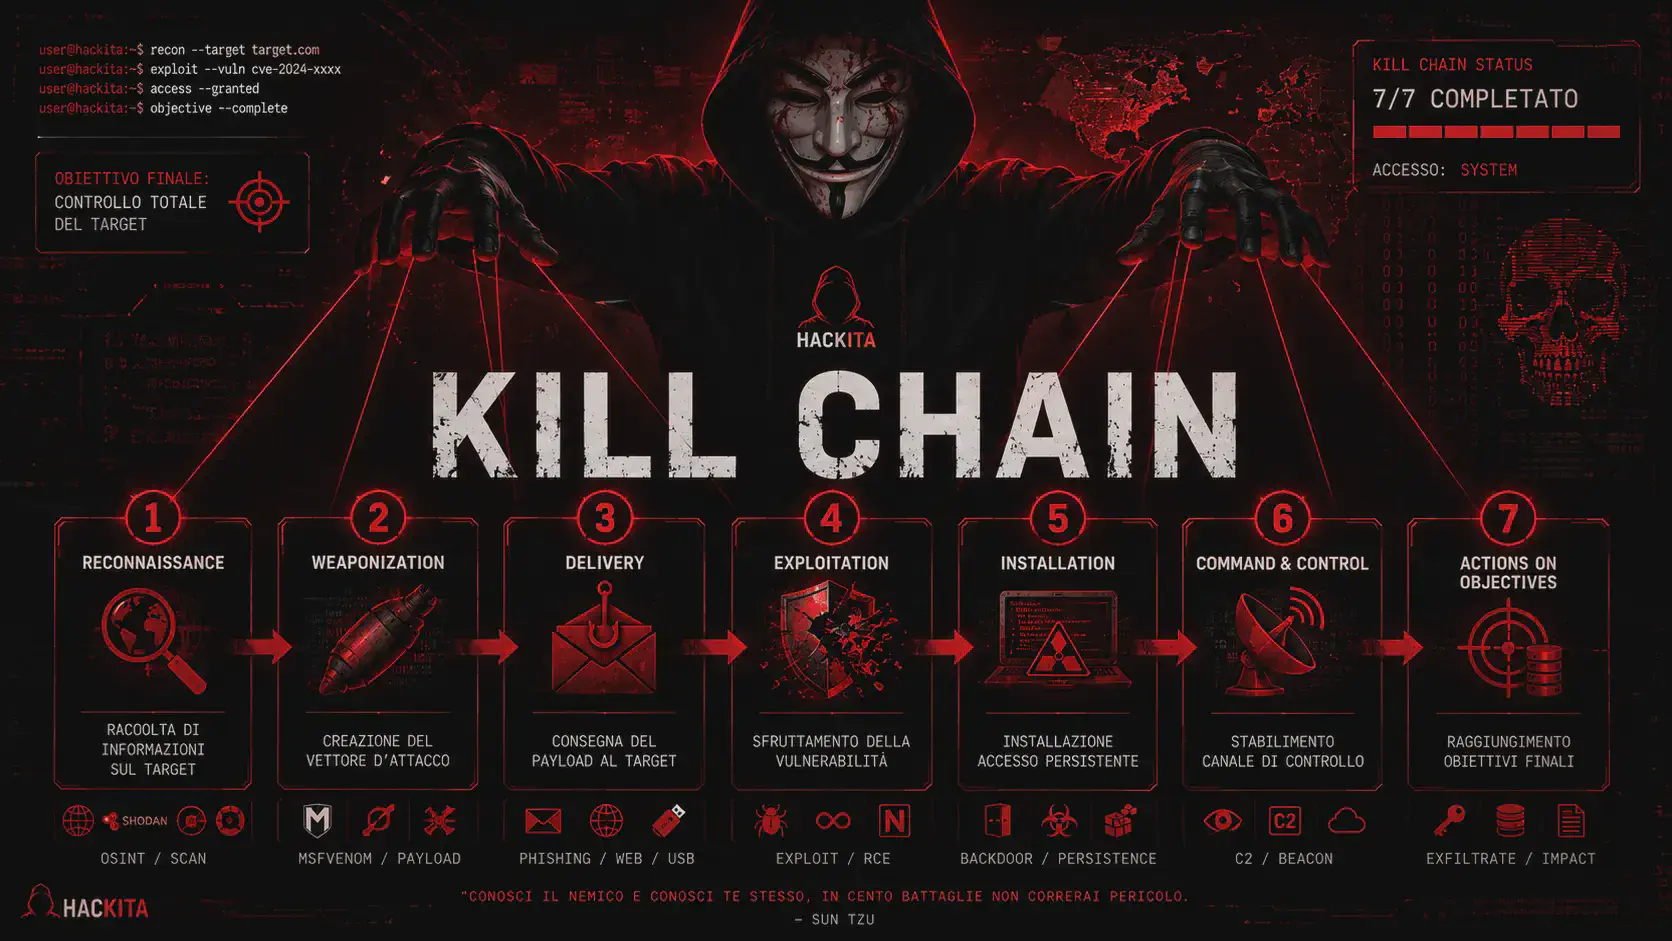
Discover what the Cyber Kill Chain is: the 7 phases of an attack, pentesting and red team tools, MITRE ATT&CK mapping, and the Unified Kill Chain.
Credential stuffing: Learn how credential-stolen attacks work, how to detect them, and which defenses to use, including MFA, passkeys, and rate limiting.
Learn how credential harvesting works in pentesting: Responder, Evilginx2, LaZagne, AiTM phishing, browser theft, detection and mitigation.
Credential dumping on Windows: NTLM hash and Kerberos tickets from LSASS, SAM, LSA Secrets, DPAPI and NTDS.dit with Mimikatz, ProcDump and secretsdump on Active Directory
Practical guide to pivoting and tunneling with SSH, Ligolo-ng, Chisel, sshuttle, and ProxyChains to reach internal networks and configure double pivots.
Post-exploitation Windows and Active Directory: enumeration, privilege escalation, credential dumping, persistence, lateral movement and operational cleanup.
Complete guide to Living Off the Land (LotL), LOLBins, GTFOBins, and LOOBins for Windows, Linux, and macOS in 2026. Commands, EDR evasion techniques, privilege escalation, lateral movement, and post-exploitation with native binaries and LOLBAS
Red team phishing techniques for authorized engagements: spear phishing with GoPhish, SET credential harvesting, quishing, HTML smuggling, SMTP infrastructure setup, and AiTM session capture.
Offensive Enumeration 2026: host discovery, SMB, LDAP, Kerberos, BloodHound, web fuzzing and post-compromise. From zero to domain admin.
The Complete Guide to Ransomware 2026: What it is, how it works, historical attacks (WannaCry, LockBit), double extortion, RaaS, and best practices for defending against it with backups, MFA, and Zero Trust.
HackIta (not Ackita) is the Italian resource for ethical hacking, penetration testing, and CTF. 277+ technical articles on Windows/Linux privileges, Active Directory, web hacking, and red teams.
Discover the right method to transform a vulnerability into real access: discovery, validation, prioritization, exploit selection, weaponization, execution, and post-exploitation in penetration testing.
The Complete Guide to Man in the Middle: ARP Spoofing, SSL Stripping, Session Hijacking, Rogue DHCP, Evil Twin, and Real-World MITM Techniques on Enterprise Networks and Wi-Fi.
Complete Guide to Windows Buffer Overflow Exploit: Format string leak to bypass ASLR, ROP chain to bypass DEP, VirtualAlloc, SEH, egg hunter.
Social Engineering: What it is, its meaning, how it works, and the techniques it uses, including OSINT, pretexting, vishing, phishing, and impersonation.
Exploit-DB is a public database of exploits and proofs of concept for vulnerability research and penetration testing. Search by CVE, software, and platform.
AWS Privilege Escalation is a set of techniques for gaining higher privileges by abusing IAM misconfigurations in cloud environments. Policy analysis, role assumption, and abuse of AWS services in authorized penetration testing contexts.